Rep. Alan Grayson: I Learn Much More About The NSA From The Press Than From Intelligence Briefings
By Mike Masnick | Techdirt | October 28, 2013
Rep. Alan Grayson has been among the most outspoken members of Congress about the NSA’s surveillance efforts, and his latest is an op-ed in the Guardian, in which he notes that Congressional “oversight” is really Congressional “overlook,” and that he learns much more about the NSA from the press than from the House intelligence briefings:
Despite being a member of Congress possessing security clearance, I’ve learned far more about government spying on me and my fellow citizens from reading media reports than I have from “intelligence” briefings. If the vote on the Amash-Conyers amendment is any indication, my colleagues feel the same way. In fact, one long-serving conservative Republican told me that he doesn’t attend such briefings anymore, because, “they always lie”.
Many of us worry that Congressional Intelligence Committees are more loyal to the “intelligence community” that they are tasked with policing, than to the Constitution. And the House Intelligence Committee isn’t doing anything to assuage our concerns.
We’ve covered in detail how House Intelligence chair Mike Rogers had blocked other Reps. from learning information about the spying program, refusing to answer questions or provide more access to certain Congressional Reps, as well as generally making sure that curious Reps can’t find out the answers to their questions. Grayson goes into more detail:
I’ve requested classified information, and further meetings with NSA officials. The House Intelligence Committee has refused to provide either. Supporters of the NSA’s vast ubiquitous domestic spying operation assure the public that members of Congress can be briefed on these activities whenever they want. Senator Saxby Chambliss says all a member of Congress needs to do is ask for information, and he’ll get it. Well I did ask, and the House Intelligence Committee said “no”, repeatedly. And virtually every other member not on the Intelligence Committee gets the same treatment.
Recently, a member of the House Intelligence Committee was asked at a town hall meeting, by his constituents, why my requests for more information about these programs were being denied. This member argued that I don’t have the necessary level of clearance to obtain access for classified information. That doesn’t make any sense; every member is given the same level of clearance. There is no legal justification for imparting secret knowledge about the NSA’s domestic surveillance activities only to the 20 members of the House Intelligence Committee. Moreover, how can the remaining 415 of us do our job properly, when we’re kept in the dark – or worse, misinformed?
This is even more important than just a few concerned Congressional Reps. Just recently, we wrote about the FISA Court’s defense of its latest renewal on the bulk metadata collection of phone records under Section 215 of the Patriot Act. A very key piece of that decision had to do with the FISA Court’s belief that Congress was well-informed about the programs when it voted to renew Section 215 — thus, arguing that Congress approves of such things. Grayson’s comments (along with those of many other House Representatives — not to mention the 207 Reps who voted for the Amash Amendment against such bulk collection) suggest that the FISA Court is simply wrong on this, but doesn’t seem to care enough to find out the truth.
Brazil to press for local Internet data storage after NSA spying
RT | October 29, 2013
Brazil is urging a plan to introduce local data storage for Internet giants like Facebook and Google in order to keep the information they get from Brazilian users safe –as part of a complex of measures to oppose US spying.
The new law could impact Google, Facebook, Twitter and other Internet global companies that operate in Brazil, Latin America’s biggest country and one of the world’s largest telecommunications markets.
The country’s president, Dilma Rousseff, is urging lawmakers to vote as early as this week on the law, according to Reuters who have seen the draft of the legislation.
“The government can oblige Internet service companies … to install and use centers for the storage, management and dissemination of data within the national territory,” the draft of the document read.
Rousseff’s calls come after surveillance leaks by the US in Brazil that went as far as tracking the personal phone calls and e-mails of the President herself.
Last month, Brazilian President Dilma Rousseff canceled a scheduled meeting at the White House after leaked documents showed the NSA spied on her country’s state oil company.
“We are not regulating the way information flows, just requiring that data on Brazilians be stored in Brazil so it is subject to the jurisdiction of Brazilian courts,” Rousseff spokesman Thomas Traumann said. “This has nothing to do with global communications.”
However, the companies disagree saying that the legislation will increase costs of services, and damage the economic activity connected with information.
Last week a coalition of business groups representing dozens of Internet companies including Facebook, Google, Microsoft and eBay sent a letter to Brazilian lawmakers.
“In-country data storage requirements would detrimentally impact all economic activity that depends on data flows,” the letter read, Reuters reported.
Many also threatened the law will scare the companies, while others, nevertheless, were of the opinion that the companies would comply if faced with no other options.
This week, Brazil is expected to vote on a cyber-security bill to create a state system to protect the country’s citizens from spying.
When the news on the bill emerged two weeks ago, Brazilian President Dilma Rousseff tweeted the news, stressing the need for greater security “to prevent possible espionage.”
The latest legislation project comes against a backdrop of Brazil set to host a conference next April to debate ways to guard Internet privacy from espionage.
The meeting is to be held by ICAAN, the body that manages web domain names. It is thought to be neutral and includes governments, civil society and industry.
Meanwhile, BRICS companies are working to create a “new Internet”.
In particular, Brazil has been reported to be building a “BRICS cable” that will create an independent link between Brazil, South Africa, India, China and Russia, in order to bypass NSA cables and avoid spying.
The cable is set to go from the Brazilian town of Fortaleza to the Russian town of Vladivostok via Cape Town, Chennai and Shantou.
The length of the fiber-optic cable will be almost 35,000 kilometers, making it one of the most ambitious underwater telecom projects ever attempted.
Last week, most of the BRICS countries joined talks to hammer out a UN resolution that would condemn “indiscriminate” and “extra-territorial” surveillance, and ensure “independent oversight” of electronic monitoring.
Russian Foreign Minister Sergey Lavrov said that “contacts [between Moscow and Washington] never stop,” when asked if the latest publication of secret files leaked by the former National Security Agency (NSA) contractor would affect relations between Russia and the US.
Also, Lavrov made it clear that the situation surrounding Snowden is irrelevant to Russia.
“We have formulated our position on Snowden and have said everything,” he said.
Related article
- China echoes Brazil’s call for cyberspace guidelines (thebricspost.com)
Palestinian Woman Arrested in Chicago
Committee to Stop FBI Repression | October 23, 2013
 A Palestinian woman, Rasmieh Odeh, was arrested at her home this morning, Oct. 22, by agents of the Department of Homeland Security.
She is charged with immigration fraud. Allegedly, in her application for citizenship, she didn’t mention that she was arrested in Palestine 45 years ago by an Israeli military court that detains Palestinians without charge – a court that has over 200 children in prison today and does not recognize the rights of Palestinians to due process.
The arrest today appears to be related to the case of the 23 anti-war activists subpoenaed to a grand jury in 2010. Well-known labor, community and international solidarity activists around the Midwest had their homes raided by the FBI when the U.S. attorney alleged that they had provided material support to foreign terrorist organizations in Palestine and Colombia.
Assistant U.S. Attorney Barry Jonas is leading the investigation against the 23. He was at the courtroom in Chicago this morning, consulting with the assistant U.S. attorney who was presenting the indictment to the judge. Jonas was also the prosecutor in the case of the Holy Land Five, the heads of the largest Muslim charity in the U.S. before 9/11. He was successful in getting prison sentences for as long as 65 years for the five men, who provided charity to children in Gaza.
The Committee to Stop FBI Repression (CSFR) denounces this attack as another example of the continuing repression of Palestinians and people who stand in solidarity with them. Homeland Security, the FBI, Immigration and Customs Enforcement and the U.S. Attorney’s office now are carrying out enforcement of the Israeli occupation of Palestine.
Odeh will appear in court in Detroit on Nov. 1, where she will be represented by Jim Fennerty of the National Lawyers Guild. CSFR urges people to attend the proceedings at the Federal Court in Detroit in her defense.
Snowden Rebuts Sen. Feinstein’s Claims That The NSA’s Metadata Collection Is ‘Not Surveillance’
By Tim Cushing | Techdirt | October 25, 2013
Ed Snowden has briefly stepped up to the mic to rebut Dianne Feinstein’s claims that the NSA’s bulk phone records collections are “not surveillance.” While he didn’t specifically name Feinstein, it’s pretty clear who his comments are directed towards, what with the senator putting in overtime over the past few weeks defending the agency’s cherished but useless Section 215 collections haystacks that are definitely not collections (according to the Intelligence Dictionary.)
“Today, no telephone in America makes a call without leaving a record with the NSA. Today, no Internet transaction enters or leaves America without passing through the NSA’s hands,” Snowden said in a statement Thursday.
“Our representatives in Congress tell us this is not surveillance. They’re wrong.”
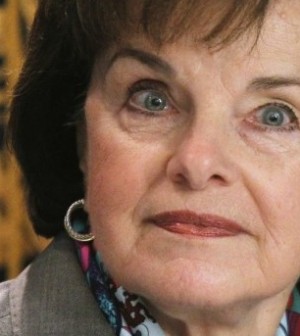 Her op-ed for the USA Today stated the following:
The call-records program is not surveillance.
Why is it not surveillance? Feinstein claimed, in direct contradiction to someone who’s seen most of the inner workings of the agency’s programs, that because it doesn’t sweep up communications or names, it isn’t surveillance. Also, she pointed out that surveillance or not, it’s legal. So there.
Maybe Feinstein considers the term “surveillance” to mean something closer to the old school interpretation — shadowy figures in unmarked vans wearing headphones and peering through binoculars.
Of course, this kind of surveillance contained many elements completely eliminated by the combination of the PATRIOT Act, the FISA Amendments Act, and a very charitable reading of the Third Party Doctrine. You know, the sort of stuff those shadowy men used to utilize: warrants, targeted investigations, reasonable suspicion, a grudging working relationship with the Fourth Amendment…
That’s all gone now. The courts have declared that sweeping up business records on millions of Americans is no more a violation of the Fourth Amendment than gathering metadata on a single person. The NSA has warped the definition of “surveillance” just as surely as they’ve warped the definition of “relevant.” The wholesale, untargeted gathering of millions of “transactions” from internet and phone activity doesn’t seem to resemble what anyone might historically think of as “surveillance,” but it’s surveillance nonetheless.
Sure, the NSA may not look at everything it gathers, but it has the capability to do so and it shows no interest in letting any of its dragnets be taken out of commission. The NSA’s defenders downplay the agency’s many intrusions by first playing the “legal” and “oversight” cards and, when those fail to impress, belittle their critics by trotting out condescending statements like, “The NSA isn’t interested in Grandma’s birthday phone call or the cat videos you email to your friends.”
Well, no shit. We’re hardly interested in that, either. We’re not worried about the NSA looking through tons of inane interactions. We know it doesn’t have the time or inclination to do so. We’re more concerned it’s looking at the stuff it finds interesting and amassing databases full of “suspicious” persons by relying on algorithms and keywords — a fallible process that robs everything of context and turns slightly pointed hay into the needles it so desperately needs to justify its existence.
What makes this even more frightening is that the agency then hands this unfiltered, untargeted, massive collection of data off to other agencies, not only in the US but in other countries, subjecting innocent Americans’ data to new algorithms, keywords and mentalities, increasing the possibility of false positives.
But what we’re mainly concerned about is the fact that an agency that claims its doing this to combat terrorism can’t seem to come up with much evidence that its programs are working. The NSA has deprived us of civil liberties while delivering next to nothing in terms of security. Americans have been sold out to a data-hungry beast, and even if it’s not officially “surveillance,” it’s still completely unacceptable.
TSA Runs Background Checks of U.S. Passengers before They Arrive at the Airport
By Noel Brinkerhoff and Danny Biederman | AllGov | October 23, 2013
The Transportation Security Administration (TSA) has broadened its screening of passengers before they arrive at the airport by using government and private databases revealing personal information.
The expanded screening, which used to apply only to people entering the United States, now affects domestic travelers, and can include TSA agents reviewing car registrations and employment information.
“It is unclear precisely what information the agency is relying upon to make these risk assessments, given the extensive range of records it can access, including tax identification number, past travel itineraries, property records, physical characteristics, and law enforcement or intelligence information,” Susan Stellin wrote for The New York Times.
TSA claims that the purpose of the expanded passenger data scans is to identify low-risk passengers in order to lighten their security screening at the airport and thus make actual searches more targeted. The agency’s goal is to be able to do that with 25% of all passengers by the end of 2014. Those designated low-risk travelers will get to move through a separate line and be able to keep their shoes and jackets on.
Privacy groups expressed concern over the TSA’s widening reach into people’s personal records.
Previously, the air travel background checks, called Secure Flight, only involved a comparison of a passenger’s name, gender and date of birth to terrorist watch list data. Now it is clearly much more.
“I think the best way to look at it is as a pre-crime assessment every time you fly,” Edward Hasbrouck, a consultant to the Identity Project, one of the groups that oppose the prescreening initiatives, told the Times. “The default will be the highest, most intrusive level of search, and anything less will be conditioned on providing some additional information in some fashion.”
TSA has not announced details of the program, but it reportedly has already been launched.
To Learn More:
Security Check Now Starts Long Before You Fly (by Susan Stellin, New York Times)
As TSA Expands beyond Airports, Concerns are Raised over Warrantless Searches (by Noel Brinkerhoff and Danny Biederman, AllGov)
TSA Spreads to Trains, Subways, Bus Terminals and Ferries (by Noel Brinkerhoff and David Wallechinsky, AllGov)
Tennessee First State to Allow TSA Highway Random Search Program (by David Wallechinsky and Noel Brinkerhoff, AllGov)
Clerical Blunder Reveals TSA Considers Airport Terrorist Attack Unlikely
By JACK BOUBOUSHIAN | Courthouse News | October 22, 2013
Classified TSA documents revealed by clerical error show that the agency does not think terrorists are plotting to attack airplanes, suggesting that nude body scans are unnecessary to protect passengers.
After Rapiscan developed “backscatter” body scanners using Advanced Imaging Technology in 2007, Jonathan Corbett sued the Transportation Security Administration three years later.
He claimed that the TSA procedures violated the Fourth Amendment’s prohibition against unreasonable searches in requiring agents to touch the passengers’ private areas and let them see clear images of the passengers’ nude bodies.
Corbett claimed that the “the abstract risk[s] of terrorism without a credible, specific threat” does not justify the unreasonable screening procedures, which are performed without probable cause or a search warrant.
“The nude body scanners serve to palpate every inch of skin, this time with electromagnetic radiation rather than fingers,” he wrote in a recent brief. “Every crevice, fold, and bump is turned into a picture of the traveler’s nude body. It is, essentially, the high-tech version of an invasive pat-down.”
After a federal judge found in 2011 that only federal courts of appeals can hear challenges to TSA orders, Corbett’s case is now pending before the 11th Circuit.
In the course of discovery, the TSA gave Corbett classified documents, which he incorporated into the brief that he filed under seal.
A clerk at the 11th Circuit somehow neglected to place the document under seal, however, allowing the public to see the redacted information.
This mistake revealed the TSA’s apparent admission that terrorists are unlikely to target airports in a subsequent attack.
“As of mid-2011, terrorist threat groups present in the Homeland are not known to be actively plotting against civil aviation targets or airports; instead, their focus is on fundraising, recruiting, and propagandizing,” the TSA said.
In addition, the brief states that “the government concedes that it would be difficult to have a repeat of 9/11 due to hardened cockpit doors and the willingness of passengers to challenge hijackers rather than assume a hijacking merely means a diversion to Cuba. The government also credits updated pre-flight security for that difficulty assessment, but the assessment was written before the en masse deployment of body scanners and before the update to the pat-down procedure. Further, the government admits that there have been no attempted domestic hijackings of any kind in the 12 years since 9/11.”
The nude body scanners are not very good at detecting explosives, and almost everything caught by the machine, such as guns, could be found using a traditional metal detector, Corbett says.
The only thing the scanners allegedly excel at over a metal detector is finding illegal drugs, which do not threaten the safety of passengers.
Because less intrusive, but equally effective, search methods exist, the TSA’s use of nude scanners and full pat-downs is unnecessary and unconstitutional, according to the brief Corbett filed pro se.
“The limited support that the TSA has for the nude body scanners and pat-down procedures in Congress, in the eyes of the public, and in the courts so far is a direct result of the TSA’s insistence that these devices are necessary to mitigate the threat of non-metallic explosives,” it states. “When given the choice between sacrificing some of their privacy or risk being blown up, many people – especially politicians who would not want to have the finger pointed at them for being ‘responsible’ for allowing the next terrorist attack to happen – choose the former.
“However, this is a false choice, and the TSA has deliberately misled the public, Congress, and the courts into concluding that no less invasive alternatives can ‘do the job.’ At least three other technologies are available to the TSA for the purpose of screening travelers for explosives, and a review of the administrative record shows that the TSA’s decision to use nude body scanners and pat-downs over these other technologies was arbitrary and capricious.”
Related article
NSA spied on 125bn phone calls in one month
Press TV – October 24, 2013
The US National Security Agency monitored nearly 125 billion phone calls from around the world in just one month, including around 3 billion calls from US soil, according to documents released by whistleblower Edward J. Snowden.
The sheer extent of the NSA’s data collection effort was compiled from multiple sources and organized on Wednesday by members of intelligence website Cryptome, which regularly publishes government documents and other information.
The majority of calls monitored by the NSA originated from Afghanistan and Pakistan, where 13.76 billion and 21.98 billion calls were respectively collected during January 2013, according to the Boundless Informant “heat map” revealed by the Guardian.
Billions of phone calls were also recorded from countries in the Middle East, including Iraq, Saudi Arabia, Egypt, Iran and Jordan.
Additionally, some 6.28 billion calls from India were collected. An estimated 3 billion US phone communications were also tapped by the NSA.
Perhaps the most controversial element of the NSA spying program is the effort to collect phone data from Western nations that have friendly relations with the US.
Germany, France and several other countries have expressed concerns about US spying after Snowden, former NSA contractor, revealed classified information about US surveillance programs.
The chairman of the US Joint Chiefs of Staff, Gen. Martin Dempsey, admitted in July that Snowden’s exposés have seriously damaged US ties with other countries. “There has been damage. I don’t think we actually have been able to determine the depth of that damage.”
Related articles
- NSA Spies on 500 Million Germany Data Connections Monthly (leaksource.wordpress.com)
- US spied on French diplomats- report (worldbulletin.net)
- Angela Merkel Calls Obama, Enquires Why Her Phone Was Spied On (eteknix.com)
Federal Appeals Court Rules Warrant Required for GPS Tracking
By Nathan Freed Wessler | ACLU | October 23, 2013
Today the Third Circuit Court of Appeals ruled that law enforcement agents must obtain a warrant based on probable cause to attach a GPS device to a car and track its movements. The case, United States v. Katzin, is the first in which a federal appeals court has explicitly held that a warrant is required for GPS tracking by police. The ACLU submitted an amicus brief in the case (joined by the ACLU of Pennsylvania, Electronic Frontier Foundation, and National Association of Criminal Defense Lawyers) and presented oral argument to the court in March.
In this case, police suspected three brothers, Harry, Mark, and Michael Katzin, of robbing several pharmacies. Without getting a warrant from a judge, FBI agents attached a GPS tracking device to Harry Katzin’s car in order to follow its movements. The government used the GPS device to track the Katzins as they drove to and from another pharmacy, and arrested them as they drove away. Before trial, the Katzins argued that police had violated their Fourth Amendment rights by using the GPS tracker without a warrant, and the district court agreed. Today’s ruling affirms that decision.
Last year, in United States v. Jones, the Supreme Court unanimously held that attaching a GPS tracker to a car to follow its movements is a search under the Fourth Amendment. The Court did not decide whether police need a warrant to conduct such a search, however, and the government argued in this case that an exception to the usual requirement of a warrant should apply. The Third Circuit rejected the government’s arguments, explaining that GPS tracking is a “vastly broader endeavor” than the kinds of limited searches that courts have allowed without warrants. In particular, the court held that the “automobile exception” to the warrant requirement does not apply to GPS tracking. The exception is designed to permit warrantless searches of cars to reveal contraband before the cars can drive away. But, as the court explained, that narrow exception does not “permit [police] to leave behind an ever-watchful electronic sentinel in order to collect future evidence” without judicial oversight.
The court also rejected a second argument made by the government: that the so-called “good faith” exception should permit use of evidence derived from the GPS tracking, even if it violated the Fourth Amendment. Because the GPS tracker was attached to the Katzins’ car before the Supreme Court decided Jones, and before the Third Circuit had addressed the issue, the government argued that FBI agents couldn’t have known that using a GPS device might raise questions under the Fourth Amendment, and therefore they acted in good faith by choosing not to seek a warrant. The court explained that this does not excuse police from the requirement of getting a warrant:
Where an officer decides to take the Fourth Amendment inquiry into his own hands, rather than to seek a warrant from a neutral magistrate — particularly where the law is as far from settled as it was in this case — he acts in a constitutionally reckless fashion. Here, law enforcement personnel made a deliberate decision to forego securing a warrant before attaching a GPS device directly to a target vehicle in the absence of binding Fourth Amendment precedent authorizing such a practice. . . . Excluding the evidence here will incentivize the police to err on the side of constitutional behavior and help prevent future Fourth Amendment violations.
Today’s opinion offers a full-throated defense of the Fourth Amendment, and installs an important safeguard against unjustified government surveillance. As courts around the country consider challenges to warrantless location tracking by police (whether using GPS devices or cell phone signals), they would do well to follow the Third Circuit’s lead.
NSA’s Italy op exposed: ‘Millions’ of private communications intercepted with govt awareness
RT | October 23, 2013
Everyday communications of Italians are also on the watch list of the US National Security Agency, a new report has revealed. While an Italian parliamentary committee seeks clarification of NSA activities, local security sources defend the snooping.
Italy’s spy watchdog COPASIR has recently learned details of large-scale monitoring of Italians by the US intelligence agency NSA, according to a report published by Corriere della Sera.
COPASIR stands for Parliamentary Committee for the Intelligence and Security Services and for State Secret Control, and is tasked with overseeing the activities of Italy’s own spy agencies. The body has free access to intelligence agencies’ offices and documents and has the authority to overcome judicial and banking secrecy.
In order to confirm the snooping on Italians, the committee members had to go to the United States and meet with US intelligence agency directors, as well as with congressional committee chairs.
A delegation of parliamentarians from the COPASIR confirmed their concerns regarding the extent of the NSA’s PRISM surveillance program during an official visit to the US three weeks ago, the media said. As part of the program, phone calls and computer communications of “millions of Italians” are reportedly being gathered.
Moreover, Corriere della Sera added that the implications extended to “a monitoring network that started years ago and is still active,” of which the Italian government and spy agencies might have been well aware of.
Such discoveries have prompted uneasy questions to officials, with leading members of COPASIR now seeking clarification from the government, and reportedly awaiting the junior minister for the intelligence services, Marco Minniti, to visit the committee’s offices on Wednesday afternoon.
Meanwhile, Italian intelligence sources quoted in the report rushed to justify the surveillance activities of their partners.
The acquisition of the sensitive private information “has as its sole aim the fight against terrorism,” one source was quoted as saying, while another denied that the NSA’s spying ever breached Italy’s sovereignty.
“We have never had any evidence that this kind of monitoring might have involved political spying on Italian public figures. All our investigations into any such eventuality have proved negative,” the source maintained.
However, such explanations did not satisfy COPASIR, nor did the NSA deputy director’s promise of “a complete overview of communications to and from the United States.”
According to the Italian media, the committee member Claudio Fava from Left Ecology Freedom (SEL) party, was “openly perplexed” as he commented on such statements.
“It’s a data trawling system based on various sensors. US intelligence experts explained that their main concern was to comply with American data protection laws and intervene to safeguard national security. Whether this conflicts with other countries’ laws is of no concern to them but it should be to us,” Fava was quoted as saying.
Another COPASIR member, Felice Casson of the Democratic Party (PD), said that the replies the committee received from top Italian intelligence officials were “far from reassuring.”
“It is clear that the United States has acquired information on individuals and institutions across Europe. What concrete elements exist to rule out that this has happened to politicians and institutions in Italy?” Casson questioned.
Leading Democratic Party (PD) politician Ettore Rosato also demanded an explanation from the government, saying that “a few months ago, when the first [NSA whistleblower Edward Snowden’s] revelations emerged, both the prime minister, Enrico Letta, and the foreign minister, Emma Bonino, professed astonishment at what came out.”
So far, the documents obtained by various world media from the former NSA contractor Snowden have revealed that the Italian embassy in Washington was subject to spying along with the diplomatic missions of other countries. Italian intelligence sources have been careful to deny the claims only “off the record,” Corriere della Sera says.
Right before the NSA scandal emerged, the collaboration between Italian and American intelligence services was “at its peak,” and, according to the media, included sharing of communications through the SIGINT interception system. However, such cooperation appeared to have been justified by the ongoing allied wars in Iraq and Afghanistan and the search for western hostages there, the media adds.
But in the wake of recent revelations on the US spying activities in France, which triggered a media frenzy and public outrage, the media speculates Italy may find it difficult to maintain the same “stance” towards the NSA programs.
Featured Video
Saudi Led Destruction of Yemen’s heritage
or go to
Aletho News Archives – Video-Images
From the Archives
Israel: Strategic Ally or Liability?
By Stephen Sniegoski | My Catbird Seat | June 12, 2010
The claim that Israel serves as a valuable ally for the United States is made by both pro-Zionists and much of the anti-war and anti-Zionist Left that is influenced by Noam Chomsky. As a result of the Gaza flotilla massacre, which has caused a world-wide uproar against Israel, the value of Israel to the United States is being publicly questioned in more mainstream foreign policy forums. … continue
Blog Roll
 Aletho News
- West’s death cult in a theater near you
- How the Yandex ‘Russian bots’ lie fell apart
- Burnham’s ‘Russia did Brexit’ ruse crumbles
- Estonia making movies and games to encourage war against Russia
- Four in five new UK jobs taken by foreigners – report
- Here’s what Trump’s latest U-turn really means for Russia and Ukraine
- The Houthis Are Not an Iranian Proxy
- Europe’s Energy Hypocrisy, Russian LNG Profits and US Dependence
- ICC ignored ‘very well-documented’ NATO crimes – ex-Libyan minister
- SNSC secretary dismisses US response to Iran’s conditions as ‘inadequate’
- If Americans Knew
- Activists Abused By Israel Return to New Freedom Flotilla Mission
- 60 Minutes won’t tell the full truth about Israeli settler violence
- Nearly 50,000 women, girls killed or severely injured in Gaza since October 2023: UN Women
- ADL is working with AI companies to suppress alleged ‘antisemitism’
- Israeli occupation forces using social media surveillance unit to target hundreds of Palestinians in the West Bank
- Israel’s New – and Terrifying – Security Doctrine
- Israeli Attacks Kill Five in Gaza, Including a four-year-old and a woman
- Air Force Major Who Called for Trump’s Impeachment Held in Solitary Confinement
- It’s a Genocide, I’m Into It’: Seinfeld Mocks Protest over Palestinian Children Killed
- Universities fire dozens amid pressure from Zionist billionaires
- No Tricks Zone
- New Study Suggests Large Regions Of The Pacific Ocean Have Been Cooling For The Last 80 Years
- Germany’s Green Energy Debacle: High Energy Costs Force Kahla Porzellan to Close After 182 Years!
- New Study: 50 Years Of The Most Aggressive ‘Net Zero’ Policies Can Only Affect The Global Climate By 0.03°C
- US September “Heat” Was No Record…Many Records Set Decades Ago
- Latest European Green Energy Debacle; Portugal’s Largest Flagship Solar Park Insolvent!
- Green Energy Debacle: German Expert Professor Fritz Vahrenholt Warns Of Severe Economic And Social Consequences
- Two More Paleo Reconstructions Affirm Meters-Higher Sea Levels Across Ireland, Brazil 7000-6000 Years Ago
- New Study: Earth And Venus Surface Warmth Largely Explained By Convection And Lapse Rate, Not CO2 Or Radiation
- 2025 Nature Paper Claiming Worsening Global Drought Gets RETRACTED …Heavily Flawed
- New Study: ‘Global Drought Shows No Detectable Recent Acceleration Under Climate Warming’

