Tragic Stories From Rafah: Students Mourn Their Future
By Fatima Abdallah | Al-Akhbar | September 20, 2013
At the Rafah border crossing with Egypt – Gaza’s only bridge to the outside world – a young Palestinian man cries profusely. He scrapes a passenger bus with his fingernails as it departs toward Egypt. He wants more than anything to stop the bus and get on it.
Mohammed al-Astal’s situation is shared by dozens of Palestinian students from Gaza studying abroad who wanted to spend their holidays with their families in the Gaza Strip. Unable to travel – Egyptian authorities have closed the border for a week now, citing security reasons – they have now missed the start of the academic year. If their absence continues, they will not be able to carry on with their studies.
Astal, a medical student at al-Mansoura University in Egypt, told Al-Akhbar: “For two weeks, I’ve been coming to the Rafah crossing every day at six in the morning, hoping I would be allowed to travel so I can go back to school, but to no avail.”
More than 2,000 people in Gaza are dreaming of traveling to Egypt today or tomorrow now that the Egyptian authorities have opened the crossing for two days. Egyptian authorities announced on Monday, September 16, the opening of the Rafah crossing on Wednesday and Thursday from 10 am to 2 pm at the request of the Palestinian Authority President Mahmoud Abbas.
Frustrated, the only thing those waiting can do is obstruct the buses full of travelers. Hamas security forces clash with individuals, pushing them back with batons until three buses manage to leave Rafah.
“All students have to come to the Rafah crossing again tomorrow morning. That is what the Palestinian embassy said in a piece of news posted yesterday,” said Hassan, a law student in Egypt. “Missing an entire month of the new semester means losing the whole semester.”
Hassan expressed his right to be on the list of passengers, along with medical patients and other urgent cases, especially after the Palestinian ambassador in Egypt, Barakat al-Farra, issued a statement on Tuesday requested that students come to Rafah after coordination with the embassy.
Maher Abu Sabha, director general of crossings at Egypt’s Interior Ministry, said: “Students stuck in Gaza do have a priority to travel, but there are also humanitarian cases of patients and people with residence permits that might expire at any moment. [These people] need to leave Gaza or else they will lose their lives outside the Strip.”
According to Abu Sabha, there are more than 4,500 Gazans registered on urgent travel lists. He pointed out that all of them can be considered humanitarian cases. They are patients, people with residence permits, and students.
Mufid al-Mukhalalati, health minister in the Hamas government, said at a press conference, “Closing the crossing has prevented more than a thousand patients from reaching Egyptian hospitals and receiving treatment and has also prevented foreign medical delegates from reaching the Gaza Strip.”
Egyptian authorities closed the crossing last Wednesday, September 11, after an armed attack was launched against the Egyptian military intelligence building in Rafah. The attack killed six Egyptian soldiers and injured 17 others.
Palestinians in Gaza continue to face increased difficulties at the Rafah crossing since the Egyptian army deposed former Egyptian president Mohamed Mursi on July 3. In the meantime, Egyptian authorities reduced working hours at the crossing to four hours daily. While thousands waited at the Rafah gate, only 250 were able to leave the Gaza Strip.
Surveillance at the United Nations
By Danny O’Brien and Katitza Rodriguez | EFF | September 17, 2013
The surveillance scandal has now reached the United Nation’s Human Rights Council, which opened its 24th session last week to a volley of questions about privacy and spying, many of them targeted at the United States and United Kingdom. (That’s perhaps not surprising, since U.N. representatives were among those listed as being monitored by the NSA and GCHQ).
The opening statement by the eminent South African human rights lawyer Navi Pillay (now the U.N.’s High Commissioner for Human Rights) warned of the “broad scope of national security surveillance in countries, including the United States and United Kingdom,” and urged all countries to “ensure that adequate safeguards are in place to prevent security agency overreach and to protect the right to privacy and other human rights.” On September 13, the German Ambassador Schumacher delivered a joint statement on behalf of Austria, Germany, Liechtenstein, Norway, Switzerland and Hungary expressing their concern about the consequences of “surveillance, decryption and mass data collection.”
One part of the potential solution to those concerns will be officially launched this Friday in a Human Rights Council side-meeting on digital privacy hosted by these same concerned countries: the International Principles on the Application of Human Rights to Communications Surveillance.
For over a year, EFF has been working with other civil liberties groups to develop these principles that spell out how existing human rights law applies to modern digital surveillance. The 13 Principles — which have been signed by 258 organizations across the world— also provide a benchmark that people around the world can use to evaluate and push for changes in their own surveillance laws. For this 24th session, EFF has joined RSF and APC in a joint written submission to the HRC, advocating for these checks and balances.
The Human Rights Council isn’t the only diplomatic venue at the United Nations where complaints about the United States’ surveillance practices are being heard. The Human Rights Committee is also set to scrutinize the United States on its compliance with Article 17 (right to privacy) of the International Coventant on Civil and Political Rights. The United States’ written response to Human Rights Committee has already laid out its diplomatic response in favor of the Patriot and FISA provisions. It notably dodges the key question that is emerging from other countries regarding these programs: if the U.S. government cannot rein in its domestic surveillance program, riven as it is with constitutional and statutory problems, just how much worse are the controls on the surveillance of non-US persons?
More directly relevant to the diplomatic community is a connected question: how can the United States accuse, with a straight face, other countries of undermining “Internet Freedom” through the use of malware and mass spying, when it seems that there are precious few internal limits to what its own security services are permitted to do in the same arena?
This is not just a matter of the United States’ international reputation. The greatest risk to the Internet in the international arena right now lies in the formation of an unholy alliance between countries who are already seeking excuses to spy and censor the net and those, like the United States, who have previously argued against such practices, but are now having to defend their own surveillance excesses with similar language.
Without promising substantive reform at home, the U.S. and the U.K. risk alienating their own allies at the United Nations, while granting a carte blanche for other countries to pursue a repressive Internet agenda abroad. The Western countries implicated in the NSA scandal should grab onto the full set of principles as a liferaft: a way that they can show a commitment to transparency and proportionality in a way that obliges other countries to follow the same standards. Otherwise, the U.S. and the U.K. will be seen as having started a race to the bottom of privacy standards: a race too many other countries will be happy to join.
Court Reveals ‘Secret Interpretation’ Of The Patriot Act, Allowing NSA To Collect All Phone Call Data
By Mike Masnick | Techdirt | September 17, 2013
The FISA Court (FISC) today released a heavily redacted version of its July ruling approving the renewal of the bulk metadata collection on all phone calls from US phone providers under Section 215 of the Patriot Act. This is part of the “secret interpretation” as to how the FISC interprets the Patriot Act’s “business records” or “tangible things” section to mean that the government can order a telco to turn over pretty much all records — even as the very author of the law says it was written specifically to not allow this interpretation.
Much of the ruling is pretty much what you’d expect, given the way defenders of this program have been insisting that this is all very legal. It argues that Smith v. Maryland show that there are no privacy protections in data given to your telco. It goes on at length defending the third party doctrine, arguing that because some third party holds your data, you have no expectation of privacy. As many have argued, this is a ridiculous and antiquated view of the third party doctrine, not at all consistent with modern technology, but the FISC repeats it without question. While some have pointed out that even if single points of metadata might not be privacy violating, collecting all of them creates a new problem, the court rejects that entirely.
From there, there’s a big discussion of whether or not “there are reasonable grounds to believe that the tangible things sought are relevant to an authorized investigation.” This is a big part of where the concern lies. How can the government defend the claim that all records are “relevant to an authorized investigation.” Here, the court compares the order to the Stored Communications Act (SCA), which lets the government get access to records as well. And then the word games begin. Basically, it argues that because one law requires “specific and articulable facts” and that the information must be “material,” while the other (the PATRIOT Act) does not, then the government doesn’t need specific and articulable facts. Rather it just needs “a statement of facts showing there are reasonable grounds to believe that the records are relevant to the investigation.”
For non-content records production requests, such as the type sought here, Section 2703(c) provides a variety of mechanisms, including acquisition through a court order under Section 2703(d). Under this section, which is comparable to Section 215, the government must offer to the court “specific and articulable facts showing that there are reasonable grounds to believe that the records or other information sought, are relevant and material to an ongoing criminal investigation.” 2703(d) (emphasis added). Section 215, the comparable provision for foreign intelligence purposes, requires neither “specific and articulable facts” nor does it require that the information be “material.” Rather, it merely requires a statement of facts showing that there are reasonable grounds to believe that the records sought are relevant to the investigation. 50 U.S.C. That these two provisions apply to the production of the same type of records from the same type of providers is an indication that Congress intended this Court to apply a different, and in specific respects lower, standard to the government’s Application under Section 215 than a court reviewing a request under Section 2703(d). Indeed, the Act version of FISA’s business records provision required “specific and articulable facts giving reason to believe that the person to whom the records pertain is a foreign power or an agent of a foreign power.” 50 U.S.C. §1862(b)(2)(B) as it read on October 25, 2001. In enacting Section 215, Congress removed the requirements for “specific and articulable facts” and that the records pertain to “a foreign power or an agent of a foreign power.” Accordingly, now the government need not provide specific and articulable facts, demonstrate any connection to a particular suspect, nor show materiality when requesting business records under Section 215. To find otherwise would be to impose a higher burden — one that Congress knew how to include in Section 215, but chose to dispense with.
Also, it argues that since Section 215 allows recipients of the order to challenge them and no telco ever has that this lends it to believe there are no problems with the law.
Second, Section 2703(d) permits the service provider to file a motion with a court to “quash or modify such order, if the information or records requested are unusually voluminous in nature or compliance with such order otherwise would cause undue burden on such provider.” Congress recognized that, even with the higher statutory standard for a production order under Section 2703(d), some requests authorized by a court would be “voluminous” and provided a means by which the provider could seek relief using a motion. Under Section 215, however, Congress provided a specific and complex statutory scheme for judicial review of an Order from this Court to ensure that providers could challenge both the legality of the required production and the nondisclosure provisions of that Order. 50 U.S.C. §1861(f). This adversarial process includes the selection of a judge from a pool of FISC judges to review the challenge to determine if it is frivolous and to rule on the merits, provides standards that the judge is to apply during such review, and provides for appeal to the Foreign Intelligence Surveillance Court of Review and, ultimately, the U.S. Supreme Court. This procedure, as opposed to the motion process available under Section 2703(d) to challenge a production as unduly voluminous or burdensome, contemplates a substantial and engaging adversarial process to test the legality of this Court’ Orders under Section 215. This enhanced process appears designed to ensure that there are additional safeguards in light of the lower threshold that the government is required to meet for production under Section 215 as opposed to Section 2703(d). To date, no holder of records who has received an Order to produce bulk telephony metadata has challenged the legality of such an Order. Indeed, no recipient of any Section 215 Order has challenged the legality of such an Order, despite the explicit statutory mechanism for doing so.
Basically, the court says “why of course there’s an adversarial process” to protect users’ privacy. It just depends on Verizon or AT&T taking up the fight on behalf of their users, and they haven’t done so, so let’s just assume everyone’s okay with this. That’s kind of crazy when you think about it. Admittedly, the public should be up in arms that Verizon and AT&T appear to have no interest in challenging these broad collections of data, but that hardly makes them constitutional.
From there we move onto the interpretation of how this massive data collection could possibly be seen as “relevant.” First, it notes (as mentioned above) that the government doesn’t need to prove that the data is actually relevant. Just that it has reasonable grounds to believe that they are relevant.
As an initial matter and as a point of clarification, the government’s burden under Section 215 is not to prove that the records sought are, in fact, relevant to an authorized investigation. The explicit terms of the statute require “a statement of facts showing that there are reasonable grounds to believe that the tangible things sought are relevant.
Then it basically says that because the NSA can sniff out terrorists within a giant database, that makes the entire database relevant. Really.
This Court has previously examined the issue of relevance for bulk collections. See; [REDACTED] While those matters involved different collections from the one at issue here, the relevance standard was similar…. (“[R]elevant to an ongoing investigation to protect against international terrorism….”). In both cases, there were facts demonstrating that information concerning known and unknown affiliates of international terrorist organizations was contained within the non-content metadata the government sought to obtain. As this Court noted in 2010, the “finding of relevance most crucially depended on the conclusion that bulk collection is necessary for NSA to employ tools that are likely to generate useful investigative leads to help identify and track terrorist operatives.” [REDACTED] Indeed, in [REDACTED] this Court noted that bulk collections such as these are “necessary to identify the much smaller number of [international terrorist] communications.’ [REDACTED] As a result, it is this showing of necessity that led the Court to find that “the entire mass of collected metadata is relevant to investigating [international terrorist groups] and affiliated persons.” [REDACTED]
It then applies those previous, redacted-named rulings, to this case, repeating the DOJ’s own filing saying “all of the metadata collected is thus relevant, because the success of this investigative tool depends on bulk collections.”
That’s ridiculous and tautological. You could argue that the “success” of a program designed to stop crimes “depends on” putting cameras inside everyone’s home, but that doesn’t make it any less a violation of privacy. It also hardly makes the collection of all such data “relevant.”
The FISC continues to tap dance on the grave of the 4th Amendment:
The government depends on this bulk collection because if production of the information were to wait until the specific identifier connected to an international terrorist group were determined, most of the historical connections (the entire purpose of this authorization) would be lost. The analysis of past connections is only possible “if the Government has collected and archived a broad set of metadata that contains within it the subset of communications that can later be identified as terrorist-related.” Because the subset of terrorist communications is ultimately contained within the whole of the metadata produced, but can only be found after the production is aggregated and then queried using identifiers determined to be associated with identified international terrorist organizations, the whole production is relevant to the ongoing investigation out of necessity.
Once again, that makes no sense. First off, just because you can put together all this aggregate data and use it to find criminals and terrorists doesn’t automatically make it legal. Once again, I’m sure that having cameras in everyone’s homes would allow similar capturing of illegal behavior. But that doesn’t make it legal. Second, the argument that without this metadata collection the information would be “lost” is clearly untrue. As was just revealed a few weeks ago, AT&T has employees embedded with the DEA who are willing, ready and able to do deep dive searches on decades worth of phone records (even beyond AT&T). The data isn’t lost. They’re available via AT&T employees who are working right alongside government employees.
Incredibly, the FISC then claims that the mere claim that terrorists use the phone system is enough to show that all phone records are relevant.
The government must demonstrate “facts showing that there are reasonable grounds to believe that the tangible things sought are relevant to an authorized investigation.” The fact that international terrorist operatives are using telephone communications, and that it is necessary to obtain the bulk collection of a telephone company’s metadata to determine those connections between known and unknown international terrorist operatives as part of authorized investigations, is sufficient to meet the low statutory hurdle set out in Section 215 to obtain a production of records.
Except, almost nothing there makes sense. It’s not true that it is necessary to obtain bulk collection of the metadata to find those connections. And just because terrorists live in houses, we don’t say that it’s okay for law enforcement to search every house. Take this same argument and apply it to anything else and the 4th Amendment goes away entirely.
In short, this shows the serious problems with these efforts being non-adversarial. The FISC more or less buys the government’s argument at every single turn, even though there are multiple arguments for why the government’s position is either not true or, at the very least, misleading.
Related article
Swiss take obligatory army service to referendum
RT | September 18, 2013
On Sunday, the Swiss are voting on a proposal to abolish military conscription in favor of a voluntary army. The country with no clear foes and a long tradition of neutrality could find better ways of spending money than playing at war, proponents say.
Switzerland, once a proud supplier of mercenaries for numerous wars in Europe, has maintained a policy of armed neutrality for the last five centuries. It isn’t a member of any defense pacts and wasn’t even member of the United Nations until 2002. But it has an army of 150,000, the size of Austria’s, Belgium’s, Norway’s, Finland’s and Sweden’s armies combined.
Under Swiss law, all able-bodied males must take part in compulsory military service between the ages of 18 and 34. This comprises 18 to 21 weeks of basic training and further yearly refresher courses lasting 19 days. Senior officers may have to serve up to the age of 50 and spend more than twice as much time on army duty than ordinary recruits.
Boot camp is praised by advocates as a character-building experience, which teaches working in a team under stress and gives a chance to develop leadership skills. It also serves as a kind of glue for Swiss society, with connections made in the service lasting on in civilian life. For a country with four different language groups, it is seen by many Swiss as crucial for national unity.
The military is also the cornerstone of the Swiss militia, which has a role similar to the National Guard in the US. Those in the army help civilian authorities and respond to natural disasters and other major events. Many continue helping society as volunteers after retiring from the service by joining the fire service, participating in local politics. or serving other public duties.
An anachronism that costs too much
However, there are plenty who see military traditions as an expensive anachronism, which is no longer necessary. The pacifist Group for Switzerland without an Army (GSoA) has gathered the 100,000 signatures necessary to put their abolition proposal to a national referendum.
Referenda are essential to Switzerland’s direct form of democracy and are held several times a year at national, regional and local levels. An initiative must win support from a majority of voters and a majority of cantons to be passed and made law.
GSoA, which has been campaigning against obligatory army service since 1982, argues that the country located in the heart of Europe doesn’t need big military firepower to protect itself and that a purely voluntary force would suffice. It criticizes conscription, which excludes Swiss women and disrupts study and work for men, costing an estimated $4.3 billion to the economy annually.
“Not everyone has time to play war,” declares the GSoA campaign poster.
The group has pushed unsuccessfully for several referendums in the past, trying to scrap the military, preventing the procurement of American fighter jets, banning all arms exports from Switzerland, and stopping the Swiss tradition of conscripts keeping their assault rifles at home after initial training.
Sunday’s vote is not expected to go in favor of the GSoA. A survey by Swiss television in August revealed that 40 per cent of respondents would reject the initiative, with another 17 per cent leaning that way. The support for the military is particularly strong in the older generations, with 68 per cent of those over 65 opposing the initiative. Less than a third of Swiss people support the proposal.
“Switzerland needs an army,” says Jakob Büchler of the Christian Democrat Party (CVP), a member of the National Council, which rejected the initiative as cited by The Local. “We are a small country, we are a neutral country, and we are a country that isn’t in any defense alliances. We have to therefore organize our own defense and security ourselves, and that’s why we need an army.”
Opponents of the initiative fear that there won’t be enough volunteers for military service and Switzerland would then have to start a costly change to a professional army.
Globalization advancing
Lately, GSoA reasoning has found support from an increasing number of multinational firms who are not happy to see local staff being sent to boot camps, reports Reuters. The contact-building aspect of the military is diminishing too, with Swiss companies being infiltrated by foreigners – just six of the CEOs at Switzerland’s top 20 companies hold Swiss nationality – and of course females are climbing the corporate ladder, too. Meanwhile young men nowadays have other options such as internships abroad.
While the GSoA proposal is likely to be thrown out, they are still hoping for a strong showing of support for their stance as they continue their fight. “The more ‘yes’ votes we receive, the greater the pressure will be to reform the army,” says Seraina Patzen, a spokeswoman for the group.
The Swiss military are not objecting to undergoing reform. They have already shrunk the number of troops considerably. In the late 1980s Switzerland had 800,000 soldiers and officers, but by 2003 the number had dropped to 350,000. The plan is to reduce the current army of 150,000 to 100,000 in coming years.
Conscription rules were made less strict. Since 1996 conscientious objectors may serve an extended period in the civil service as an alternative to joining the military.
But the Defense Ministry maintains that a conscripted military is necessary for the country. During a recent media tour of barracks, Defense Minister Ueli Maurer said Switzerland may not face an enemy in the field, but may become, for example, a target of a cyber attack disrupting the transport network. In order for the army to respond to national emergencies, it needs to be able to draw on the best IT specialists, engineers and technicians the country has to offer.
NY Times Doesn’t Think That NSA Sharing Raw Communications With Israel Is Newsworthy
By Mike Masnick | Techdirt | September 16, 2013
Last week, we were among those who wrote about the latest revelations via the Guardian about how the NSA was sharing raw communications it had collected with Israeli intelligence. This is a big story for any number of reasons, but apparently the NY Times doesn’t think so. When Public Editor Margaret Sullivan asked why, the managing editor basically said the story wasn’t newsworthy:
He told me that The Times had chosen not to follow the story because its level of significance did not demand it.
“I didn’t think it was a significant or surprising story,” he said. “I think the more energy we put into chasing the small ones, the less time we have to break our own. Not to mention cover the turmoil in Syria.”
So, I asked him, by e-mail, was this essentially a question of reporting resources? After all, The Times could have published an article written by a wire service, like Reuters or The Associated Press.
“I’d say resources and news judgment,” he responded.
The resources issue is one I can understand totally. Here at Techdirt, we probably cover about one quarter to one third the number of stories we’d like to (which is also why I have about a thousand open tabs of stories I’m “hoping” to get to one of these days). But to claim that it’s not “significant” or “surprising” or somehow newsworthy is pretty crazy. This is a major part of the story — where the NSA keeps insisting that it is exceptionally careful with the data it collects, yet here it is handing off a ton of communications, including those of Americans, off to a foreign intelligence agency with basically no oversight. If the NY Times doesn’t think that’s newsworthy, the NY Times needs to recalibrate its newsworthy scale.
Related article
UK new forced conscription bill: a look
Press TV – September 16, 2013
The British government has launched a new debate on reintroducing mandatory National Service, or conscription, for the 18 to 26-year-olds, 50 years after the last conscripted British soldier ended his service.
The bill was tabled by Conservative MP Philip Hollobone, who said the service can inspire young people with “self-respect, personal reliance, discipline and behavior.”
The legislation was introduced to the parliament for debate on June 24, which is considered its first reading though no debate took place at that stage.
MPs are expected to hold a second reading debate on the bill on February 28, 2014.
The bill predicts the introduction of a year-long charitable or military service that could involve care for the elderly or the disabled, work for the emergency services or service in the armed forces with a necessary “residential element” that requires participants to live away from their homes.
“Every individual who has attained the age of 18 years, and who has not attained the age of 26 years, shall be liable to serve one year of national service at some point between these years unless exempt,” the bill reads.
“Regulations shall provide that the scheme must extend the scope of the National Citizen Service and include the following elements,” it adds.
The bill, if voted into law, makes it a criminal offense to skip National Service.
The reference in the text of the proposed law to the National Citizen Service (NCS), which was introduced by Prime Minister David Cameron for the 16 and 17-year-olds in 2010, raises suspicion that the Conservative-Liberal Democrat coalition government has been planning to reintroduce the long-forgotten National Service early after taking office.
NCS is now in full swing in England and offers voluntary short-time tours for individuals to take part in team projects away from home to help their community.
London first introduced conscription during the First World War in 1916, which lasted until 1919.
Another forced service was launched in 1939 at the beginning of the Second World War, continuing until 1960, with the last conscripted soldiers ending their service in 1963.
The recruitment was named War Service or Military Service during the wars and National Service, as formulated by the National Service Act 1948, between 1948 and 1960.
The second national service period that started in 1939 lasted beyond the World War II (1939-1945) partly because of Britain’s involvement in the Korean War of the 1950’s.
That could be adequate precedence for the British public to fear a decade of military adventurism, including the wars in Afghanistan, Iraq and Libya – not to mention the saber-rattling against Syria — has triggered the renewed call for a national service.
Indeed, the public opposition to the bill emerged from the very onset after an e-petition was launched demanding the government to “stop the National Service Bill 2013-2014”. The petition has already collected over 27,000 signatures.
It rejects the mandatory service as “unacceptable”, calling on the government to reject the bill “in its entirety” and “reassure us that non voluntary service and any residential or military style training, or service, will always be a freedom of choice”.
Under the Coalition agreement any e-petition attracting more than 100,000 signatures becomes eligible for a Commons debate.
The public concern over the new initiative has been clearly reflected in the e-petition.
“We do not want our children and grandchildren to fight and die in wars, or in training that they or we have no control over,” the petition says.
There are also concerns that the forced conscription is against the idea of a free society as compulsory recruits will have to spend a year in service with minimum wage at the end of their high school or college, when they could rather start a job or begin university education in anticipation of a difficult future amid Britain’s economic woes.
Related articles
NYC Tracking E-ZPass Tags All Over The City, Without Telling Drivers
By Mike Masnick | Techdirt | September 13, 2013
New York, and many states in the northeast and midwest, use an RFID toll-paying solution called E-ZPass (the system works in multiple states — but not all, which is why, for example, you can’t use the E-ZPass on California’s Fastrak system). Ever since E-ZPass came into existence, some have expressed concerns that the tags would be used for tracking, rather than just for more convenient and efficient toll-paying. And, in fact, the toll-paying records have been used in a variety of legal cases, from catching an official who falsified time sheets to being used as evidence in divorce cases. But all of those still involved using the records at the actual tolls, where everyone knows the tags are being read.
However, it turns out that New York City has had an ongoing program to surreptitiously scan the tags in a variety of places supposedly for monitoring traffic. Indeed, you could see how that sort of traffic information might be useful, though these days with many other forms of traffic monitoring systems out there, it’s probably a lot less necessary than before. But this was only discovered because a hacker going by the name Puking Monkey (one assumes this was not his given name) got suspicious and hacked up an E-ZPass to light up and make a sound whenever it was read. Then he drove around Manhattan, and voila, the tag kept going off.
As Kash Hill’s article at Forbes notes, this has been going on for years, though, the various agencies involved have been rather quiet about it, and (perhaps most importantly) this type of usage does not appear to be disclosed in the terms and conditions for the E-ZPass. Oops.
The technology company that makes the devices insists that it’s not being used for any surveillance:
“The tag ID is scrambled to make it anonymous. The scrambled ID is held in dynamic memory for several minutes to compare with other sightings from other readers strategically placed for the purpose of measuring travel times which are then averaged to develop an understanding of traffic conditions,” says TransCore spokesperson Barbara Catlin by email. “Travel times are used to estimate average speeds for general traveler information and performance metrics. Tag sightings (reads) age off the system after several minutes or after they are paired and are not stored because they are of no value. Hence the system cannot identify the tag user and does not keep any record of the tag sightings.”
Of course, even if that is true today, that doesn’t mean it will always be true. We’re already well aware of how the NYPD is known for the extreme lengths it will go in terms of surveillance, including the fact that it’s set up its own intelligence division that many say rivals the intelligence operations of entire nations. Since the folks behind E-ZPass didn’t seem to think it was necessary to tell people that their devices would be used for traffic monitoring, how likely is it that anyone would be told if it was used for surveillance as well?
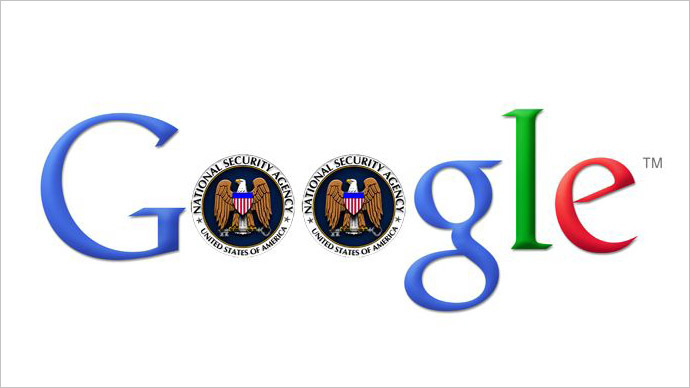
NSA masqueraded as Google to spy on web users – report
RT | September 13, 2013
The NSA used ‘man in the middle’ hack attacks to impersonate Google and fool web users, leaks have revealed. The technique circumvents encryption by redirecting users to a copycat site which relays all the data entered to NSA data banks.
Brazilian television network Globo News released a report based on classified data divulged by former CIA worker Edward Snowden on Sunday. The report itself blew the whistle on US government spying on Brazilian oil giant Petrobras, but hidden in amongst the data was information the NSA had impersonated Google to get its hands on user data.
Globo TV showed slides from a 2012 NSA presentation explaining how the organization intercepts data and re-routes it to NSA central. One of the convert techniques the NSA uses to do this is a ‘man in the middle’ (MITM) hack attack.
This particular method of intercepting internet communications is quite common among expert hackers as it avoids having to break through encryption. Essentially, NSA operatives log into a router used by an internet service provider and divert ‘target traffic’ to a copycat MITM site, whereupon all the data entered is relayed to the NSA. The data released by Edward Snowden and reported on by Globo News suggests the NSA carried out these attacks disguised as Google.
When the news broke about the NSA gathering information through internet browsers, tech giants such as Google and Yahoo denied complicity, maintaining they only handover data if a formal request is issued by the government.
“As for recent reports that the US government has found ways to circumvent our security systems, we have no evidence of any such thing ever occurring. We provide our user data to governments only in accordance with the law,” said Google spokesperson Jay Nancarrow to news site Mother Jones.
Google, along with Microsoft, Facebook and Yahoo, has filed a lawsuit against the Foreign Intelligence Surveillance Court (FISA) to allow them to make public all the data requests made by the NSA.
“Given the important public policy issues at stake, we have also asked the court to hold its hearing in open rather than behind closed doors. It’s time for more transparency,” Google’s director of law enforcement and information security, Richard Salgado, and the director of public policy and government affairs, Pablo Chavez, wrote in a blog post on Monday.
The tech giants implicated in NSA’s global spying program have denied criticism that they could have done more to resist NSA spying. Marissa Mayer, CEO of Yahoo, claimed that speaking out about the NSA’s activities would have amounted to ‘treason’ at a press conference in San Francisco on Wednesday.
In Yahoo’s defense, she argued that the company had been very skeptical of the NSA’s requests to disclose user data and had resisted whenever possible. Mayer concluded that it was more realistic to work within the system,” rather than fight against it.
What Convinced Obama to Reverse His Position on NSA Surveillance?
By Jennifer Hoelzer | September 11, 2013
 Since details of the NSA’s surveillance programs started coming to light in early June – and President Obama’s been forced to publicly answer for its activities – the president has repeatedly reminded us that he came into office with a “healthy skepticism about these programs.” But, after careful evaluation, he determined “that on, you know, net, it was worth doing.”
Some of these programs I had been critical of when I was in the Senate. When I looked through specifically what was being done, my determination was that the two programs in particular that had been at issue, 215 and 702, offered valuable intelligence that helps us protect the American people and they’re worth preserving. (From his August 9th Press Conference.)
It’s a rhetorical strategy intended to win his critics’ trust by demonstrating that he understands our concerns because he used to share them. The message he wants us to take away is: if we had been in his shoes and saw the evidence he saw when he got into office, we would have signed off on these programs too.
Well, yesterday we got a glimpse of some of the evidence he saw when he assumed office – at least in connection to the NSA’s collection of U.S. phone call records — and, it begs the question, what exactly changed his mind about the NSA’s domestic surveillance programs? What did the President see that led him to the conclusion that everything he had previously said on the topic was wrong because allowing the NSA to collect everyone’s phone call records really is a constitutionally-supported, great idea?
Because, according to the documents the ODNI released yesterday, when President Obama took office, the NSA’s “telephony metadata” program wasn’t getting stellar reviews. In fact, we now know that days prior to Obama’s inauguration, the NSA reported that it had repeatedly violated the court-ordered rules limiting its use of the data it was collecting. A little over a month later, a judge on the Foreign Intelligence Surveillance Court found that, “Since January 15 [five days before Obama’s inauguration] it has finally come to light that the FISC’s authorizations of this vast collection program have been premised on a flawed depiction of how the NSA uses” the phone call data.
Not only had the Intelligence Community been misrepresenting its program to the court, the judge, Reggie B. Walton, went on to write:
The minimization procedures proposed by the government in each successive application and approved and adopted as binding by the orders of the FISC have been so frequently and systemically violated that it can fairly be said that this critical element of the overall BR regime has never functioned effectively.
And,
To approve such a program, the Court must have every confidence that the government is doing its utmost to ensure that those responsible for implementation fully comply with the Court’s orders. The Court no longer has such confidence.
The judge also implied that – other than hypothetical examples of how this data might provide intelligence of “immense value to the government” – the government had yet to provide the court with concrete evidence that the program was actually providing that value.
This program has been ongoing for nearly three years. The time has come for the government to describe to the Court how, based on the information collected and analyzed during that time, the value of the program to the nation’s security justifies the continued collection and retention of massive quantities of U.S. person information.
Again, Judge Walton reached these conclusions based on evidence that was available to him at the very same time that I imagine President Obama and his team were evaluating these programs. Plus, I’m assuming the president considered Judge Walton’s opinion in his evaluation, right?
So, what exactly convinced President Obama that this was “worth doing?” Because as the president explained last month, the prospect that something could happen isn’t the same as actual evidence that it has or ever will.
Featured Video
Saudi Led Destruction of Yemen’s heritage
or go to
Aletho News Archives – Video-Images
From the Archives
Israel: Strategic Ally or Liability?
By Stephen Sniegoski | My Catbird Seat | June 12, 2010
The claim that Israel serves as a valuable ally for the United States is made by both pro-Zionists and much of the anti-war and anti-Zionist Left that is influenced by Noam Chomsky. As a result of the Gaza flotilla massacre, which has caused a world-wide uproar against Israel, the value of Israel to the United States is being publicly questioned in more mainstream foreign policy forums. … continue
Blog Roll
 Aletho News
- Declassified UK exposes British man who fought for ‘Israel’ in Gaza
- West’s death cult in a theater near you
- How the Yandex ‘Russian bots’ lie fell apart
- Burnham’s ‘Russia did Brexit’ ruse crumbles
- Estonia making movies and games to encourage war against Russia
- Four in five new UK jobs taken by foreigners – report
- Here’s what Trump’s latest U-turn really means for Russia and Ukraine
- The Houthis Are Not an Iranian Proxy
- Europe’s Energy Hypocrisy, Russian LNG Profits and US Dependence
- ICC ignored ‘very well-documented’ NATO crimes – ex-Libyan minister
- If Americans Knew
- An error has occurred; the feed is probably down. Try again later.
- No Tricks Zone
- New Study Suggests Large Regions Of The Pacific Ocean Have Been Cooling For The Last 80 Years
- Germany’s Green Energy Debacle: High Energy Costs Force Kahla Porzellan to Close After 182 Years!
- New Study: 50 Years Of The Most Aggressive ‘Net Zero’ Policies Can Only Affect The Global Climate By 0.03°C
- US September “Heat” Was No Record…Many Records Set Decades Ago
- Latest European Green Energy Debacle; Portugal’s Largest Flagship Solar Park Insolvent!
- Green Energy Debacle: German Expert Professor Fritz Vahrenholt Warns Of Severe Economic And Social Consequences
- Two More Paleo Reconstructions Affirm Meters-Higher Sea Levels Across Ireland, Brazil 7000-6000 Years Ago
- New Study: Earth And Venus Surface Warmth Largely Explained By Convection And Lapse Rate, Not CO2 Or Radiation
- 2025 Nature Paper Claiming Worsening Global Drought Gets RETRACTED …Heavily Flawed
- New Study: ‘Global Drought Shows No Detectable Recent Acceleration Under Climate Warming’

