How the Department of Homeland Security Created a Deceptive Tale of Russia Hacking US Voter Sites
By Gareth Porter | Consortium News | August 28, 2018
The narrative of Russian intelligence attacking state and local election boards and threatening the integrity of U.S. elections has achieved near-universal acceptance by media and political elites. And now it has been accepted by the Trump administration’s intelligence chief, Dan Coats, as well.
But the real story behind that narrative, recounted here for the first time, reveals that the Department of Homeland Security (DHS) created and nurtured an account that was grossly and deliberately deceptive.
DHS compiled an intelligence report suggesting hackers linked to the Russian government could have targeted voter-related websites in many states and then leaked a sensational story of Russian attacks on those sites without the qualifications that would have revealed a different story. When state election officials began asking questions, they discovered that the DHS claims were false and, in at least one case, laughable.
The National Security Agency and special counsel Robert Mueller’s investigating team have also claimed evidence that Russian military intelligence was behind election infrastructure hacking, but on closer examination, those claims turn out to be speculative and misleading as well. Mueller’s indictment of 12 GRU military intelligence officers does not cite any violations of U.S. election laws though it claims Russia interfered with the 2016 election.
A Sensational Story
On Sept. 29, 2016, a few weeks after the hacking of election-related websites in Illinois and Arizona, ABC News carried a sensational headline: “Russian Hackers Targeted Nearly Half of States’ Voter Registration Systems, Successfully Infiltrated 4.” The story itself reported that “more than 20 state election systems” had been hacked, and four states had been “breached” by hackers suspected of working for the Russian government. The story cited only sources “knowledgeable” about the matter, indicating that those who were pushing the story were eager to hide the institutional origins of the information.
Behind that sensational story was a federal agency seeking to establish its leadership within the national security state apparatus on cybersecurity, despite its limited resources for such responsibility. In late summer and fall 2016, the Department of Homeland Security was maneuvering politically to designate state and local voter registration databases and voting systems as “critical infrastructure.” Such a designation would make voter-related networks and websites under the protection a “priority sub-sector” in the DHS “National Infrastructure Protection Plan, which already included 16 such sub-sectors.
DHS Secretary Jeh Johnson and other senior DHS officials consulted with many state election officials in the hope of getting their approval for such a designation. Meanwhile, the DHS was finishing an intelligence report that would both highlight the Russian threat to U.S. election infrastructure and the role DHS could play in protecting it, thus creating political impetus to the designation. But several secretaries of state—the officials in charge of the election infrastructure in their state—strongly opposed the designation that Johnson wanted.
On Jan. 6, 2017—the same day three intelligence agencies released a joint “assessment” on Russian interference in the election—Johnson announced the designation anyway.
Media stories continued to reflect the official assumption that cyber attacks on state election websites were Russian-sponsored. Stunningly, The Wall Street Journal reported in December 2016 that DHS was itself behind hacking attempts of Georgia’s election database.
The facts surrounding the two actual breaches of state websites in Illinois and Arizona, as well as the broader context of cyberattacks on state websites, didn’t support that premise at all.
In July, Illinois discovered an intrusion into its voter registration website and the theft of personal information on as many as 200,000 registered voters. (The 2018 Mueller indictments of GRU officers would unaccountably put the figure at 500,000.) Significantly, however, the hackers only had copied the information and had left it unchanged in the database.
That was a crucial clue to the motive behind the hack. DHS Assistant Secretary for Cyber Security and Communications Andy Ozment told a Congressional committee in late September 2016 that the fact hackers hadn’t tampered with the voter data indicated that the aim of the theft was not to influence the electoral process. Instead, it was “possibly for the purpose of selling personal information.” Ozment was contradicting the line that already was being taken on the Illinois and Arizona hacks by the National Protection and Programs Directorate and other senior DHS officials.
In an interview with me last year, Ken Menzel, the legal adviser to the Illinois secretary of state, confirmed what Ozment had testified. “Hackers have been trying constantly to get into it since 2006,” Menzel said, adding that they had been probing every other official Illinois database with such personal data for vulnerabilities as well. “Every governmental database—driver’s licenses, health care, you name it—has people trying to get into it,” said Menzel.
In the other successful cyberattack on an electoral website, hackers had acquired the username and password for the voter database Arizona used during the summer, as Arizona Secretary of State Michele Reagan learned from the FBI. But the reason that it had become known, according to Reagan in an interview with Mother Jones, was that the login and password had shown up for sale on the dark web—the network of websites used by cyber criminals to sell stolen data and other illicit wares.
Furthermore, the FBI had told her that the effort to penetrate the database was the work of a “known hacker” whom the FBI had monitored “frequently” in the past. Thus, there were reasons to believe that both Illinois and Arizona hacking incidents were linked to criminal hackers seeking information they could sell for profit.
Meanwhile, the FBI was unable to come up with any theory about what Russia might have intended to do with voter registration data such as what was taken in the Illinois hack. When FBI Counterintelligence official Bill Priestap was asked in a June 2017 hearing how Moscow might use such data, his answer revealed that he had no clue: “They took the data to understand what it consisted of,” said the struggling Priestap, “so they can affect better understanding and plan accordingly in regards to possibly impacting future elections by knowing what is there and studying it.”
The inability to think of any plausible way for the Russian government to use such data explains why DHS and the intelligence community adopted the argument, as senior DHS officials Samuel Liles and Jeanette Manfra put it, that the hacks “could be intended or used to undermine public confidence in electoral processes and potentially the outcome.” But such a strategy could not have had any effect without a decision by DHS and the U.S. intelligence community to assert publicly that the intrusions and other scanning and probing were Russian operations, despite the absence of hard evidence. So DHS and other agencies were consciously sowing public doubts about U.S. elections that they were attributing to Russia.
DHS Reveals Its Self-Serving Methodology
In June 2017, Liles and Manfra testified to the Senate Intelligence Committee that an October 2016 DHS intelligence report had listed election systems in 21 states that were “potentially targeted by Russian government cyber actors.” They revealed that the sensational story leaked to the press in late September 2016 had been based on a draft of the DHS report. And more importantly, their use of the phrase “potentially targeted” showed that they were arguing only that the cyber incidents it listed were possible indications of a Russian attack on election infrastructure.
Furthermore, Liles and Manfra said the DHS report had “catalogued suspicious activity we observed on state government networks across the country,” which had been “largely based on suspected malicious tactics and infrastructure.” They were referring to a list of eight IP addresses an August 2016 FBI “flash alert” had obtained from the Illinois and Arizona intrusions, which DHS and FBI had not been able to attribute to the Russian government.

Manfra: No doubt it was the Russians. (C-SPAN)
The DHS officials recalled that the DHS began to “receive reports of cyber-enabled scanning and probing of election-related infrastructure in some states, some of which appeared to originate from servers operated by a Russian company.” Six of the eight IP addresses in the FBI alert were indeed traced to King Servers, owned by a young Russian living in Siberia. But as DHS cyber specialists knew well, the country of ownership of the server doesn’t prove anything about who was responsible for hacking: As cybersecurity expert Jeffrey Carr pointed out, the Russian hackers who coordinated the Russian attack on Georgian government websites in 2008 used a Texas-based company as the hosting provider.
The cybersecurity firm ThreatConnect noted in 2016 that one of the other two IP addresses had hosted a Russian criminal market for five months in 2015. But that was not a serious indicator, either. Private IP addresses are reassigned frequently by server companies, so there is not a necessary connection between users of the same IP address at different times.
The DHS methodology of selecting reports of cyber incidents involving election-related websites as “potentially targeted” by Russian government-sponsored hackers was based on no objective evidence whatever. The resulting list appears to have included any one of the eight addresses as well as any attack or “scan” on a public website that could be linked in any way to elections.
This methodology conveniently ignored the fact that criminal hackers were constantly trying to get access to every database in those same state, country and municipal systems. Not only for Illinois and Arizona officials, but state electoral officials.
In fact, 14 of the 21 states on the list experienced nothing more than the routine scanning that occurs every day, according to the Senate Intelligence Committee. Only six involved what was referred to as a “malicious access attempt,” meaning an effort to penetrate the site. One of them was in Ohio, where the attempt to find a weakness lasted less than a second and was considered by DHS’s internet security contractor a “non-event” at the time.
State Officials Force DHS to Tell the Truth
For a year, DHS did not inform the 21 states on its list that their election boards or other election-related sites had been attacked in a presumed Russian-sponsored operation. The excuse DHS officials cited was that it could not reveal such sensitive intelligence to state officials without security clearances. But the reluctance to reveal the details about each case was certainly related to the reasonable expectation that states would publicly challenge their claims, creating a potential serious embarrassment.
On Sept. 22, 2017, DHS notified 21 states about the cyber incidents that had been included in the October 2016 report. The public announcement of the notifications said DHS had notified each chief election officer of “any potential targeting we were aware of in their state leading up to the 2016 election.” The phrase “potential targeting” again telegraphed the broad and vague criterion DHS had adopted, but it was ignored in media stories.
But the notifications, which took the form of phone calls lasting only a few minutes, provided a minimum of information and failed to convey the significant qualification that DHS was only suggesting targeting as a possibility. “It was a couple of guys from DHS reading from a script,” recalled one state election official who asked not to be identified. “They said [our state] was targeted by Russian government cyber actors.”
A number of state election officials recognized that this information conflicted with what they knew. And if they complained, they got a more accurate picture from DHS. After Wisconsin Secretary of State Michael Haas demanded further clarification, he got an email response from a DHS official with a different account. “[B]ased on our external analysis,” the official wrote, “the WI [Wisconsin] IP address affected belongs to the WI Department of Workforce Development, not the Elections Commission.”
California Secretary of State Alex Padilla said DHS initially had notified his office “that Russian cyber actors ‘scanned’ California’s Internet-facing systems in 2016, including Secretary of State websites.” But under further questioning, DHS admitted to Padilla that what the hackers had targeted was the California Department of Technology’s network.
Texas Secretary of State Rolando Pablos and Oklahoma Election Board spokesman Byron Dean also denied that any state website with voter- or election-related information had been targeted, and Pablos demanded that DHS “correct its erroneous notification.”
Despite these embarrassing admissions, a statement issued by DHS spokesman Scott McConnell on Sept. 28, 2017 said the DHS “stood by” its assessment that 21 states “were the target of Russian government cyber actors seeking vulnerabilities and access to U.S. election infrastructure.” The statement retreated from the previous admission that the notifications involved “potential targeting,” but it also revealed for the first time that DHS had defined “targeting” very broadly indeed.
It said the category included “some cases” involving “direct scanning of targeted systems” but also cases in which “malicious actors scanned for vulnerabilities in networks that may be connected to those systems or have similar characteristics in order to gain information about how to later penetrate their target.”
It is true that hackers may scan one website in the hope of learning something that could be useful for penetrating another website, as cybersecurity expert Prof. Herbert S. Lin of Stanford University explained to me in an interview. But including any incident in which that motive was theoretical meant that any state website could be included on the DHS list, without any evidence it was related to a political motive.
Arizona’s further exchanges with DHS revealed just how far DHS had gone in exploiting that escape clause in order to add more states to its “targeted” list. Arizona Secretary of State Michele Reagan tweeted that DHS had informed her that “the Russian government targeted our voter registration systems in 2016.” After meeting with DHS officials in early October 2017, however, Reagan wrote in a blog post that DHS “could not confirm that any attempted Russian government hack occurred whatsoever to any election-related system in Arizona, much less the statewide voter registration database.”
What the DHS said in that meeting, as Reagan’s spokesman Matt Roberts recounted to me, is even more shocking. “When we pressed DHS on what exactly was actually targeted, they said it was the Phoenix public library’s computers system,” Roberts recalled.
In April 2018, a CBS News “60 Minutes” segment reported that the October 2016 DHS intelligence report had included the Russian government hacking of a “county database in Arizona.” Responding to that CBS report, an unidentified “senior Trump administration official” who was well-briefed on the DHS report told Reuters that “media reports” on the issue had sometimes “conflated criminal hacking with Russian government activity,” and that the cyberattack on the target in Arizona “was not perpetrated by the Russian government.”
NSA Finds a GRU Election Plot
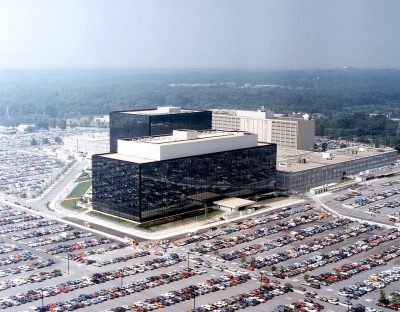
National Security Agency headquarters in Fort Meade, Md. (Wikimedia)
NSA intelligence analysts claimed in a May 2017 analysis to have documented an effort by Russian military intelligence (GRU) to hack into U.S. electoral institutions. In an intelligence analysis obtained by The Intercept and reported in June 2017, NSA analysts wrote that the GRU had sent a spear-phishing email—one with an attachment designed to look exactly like one from a trusted institution but that contains malware design to get control of the computer—to a vendor of voting machine technology in Florida. The hackers then designed a fake web page that looked like that of the vendor. They sent it to a list of 122 email addresses NSA believed to be local government organizations that probably were “involved in the management of voter registration systems.” The objective of the new spear-phishing campaign, the NSA suggested, was to get control of their computers through malware to carry out the exfiltration of voter-related data.
But the authors of The Intercept story failed to notice crucial details in the NSA report that should have tipped them off that the attribution of the spear-phishing campaign to the GRU was based merely on the analysts’ own judgment—and that their judgment was faulty.
The Intercept article included a color-coded chart from the original NSA report that provides crucial information missing from the text of the NSA analysis itself as well as The Intercept’s account. The chart clearly distinguishes between the elements of the NSA’s account of the alleged Russian scheme that were based on “Confirmed Information” (shown in green) and those that were based on “Analyst Judgment” (shown in yellow). The connection between the “operator” of the spear-phishing campaign the report describes and an unidentified entity confirmed to be under the authority of the GRU is shown as a yellow line, meaning that it is based on “Analyst Judgment” and labeled “probably.”
A major criterion for any attribution of a hacking incident is whether there are strong similarities to previous hacks identified with a specific actor. But the chart concedes that “several characteristics” of the campaign depicted in the report distinguish it from “another major GRU spear-phishing program,” the identity of which has been redacted from the report.
The NSA chart refers to evidence that the same operator also had launched spear-phishing campaigns on other web-based mail applications, including the Russian company “Mail.ru.” Those targets suggest that the actors were more likely Russian criminal hackers rather than Russian military intelligence.
Even more damaging to its case, the NSA reports that the same operator who had sent the spear-phishing emails also had sent a test email to the “American Samoa Election Office.” Criminal hackers could have been interested in personal information from the database associated with that office. But the idea that Russian military intelligence was planning to hack the voter rolls in American Samoa, an unincorporated U.S. territory with 56,000 inhabitants who can’t even vote in U.S. presidential elections, is plainly risible.
The Mueller Indictment’s Sleight of Hand
The Mueller indictment of GRU officers released on July 13 appeared at first reading to offer new evidence of Russian government responsibility for the hacking of Illinois and other state voter-related websites. A close analysis of the relevant paragraphs, however, confirms the lack of any real intelligence supporting that claim.
Mueller accused two GRU officers of working with unidentified “co-conspirators” on those hacks. But the only alleged evidence linking the GRU to the operators in the hacking incidents is the claim that a GRU official named Anatoly Kovalev and “co-conspirators” deleted search history related to the preparation for the hack after the FBI issued its alert on the hacking identifying the IP address associated with it in August 2016.
A careful reading of the relevant paragraphs shows that the claim is spurious. The first sentence in Paragraph 71 says that both Kovalev and his “co-conspirators” researched domains used by U.S. state boards of elections and other entities “for website vulnerabilities.” The second says Kovalev and “co-conspirators” had searched for “state political party email addresses, including filtered queries for email addresses listed on state Republican Party websites.”

Mueller: Don’t read the fine print. (The White House/Wikimedia)
Searching for website vulnerabilities would be evidence of intent to hack them, of course, but searching Republican Party websites for email addresses is hardly evidence of any hacking plan. And Paragraph 74 states that Kovalev “deleted his search history”—not the search histories of any “co-conspirator”—thus revealing that there were no joint searches and suggesting that the subject Kovalev had searched was Republican Party emails. So any deletion by Kovalev of his search history after the FBI alert would not be evidence of his involvement in the hacking of the Illinois election board website.
With this rhetorical misdirection unraveled, it becomes clear that the repetition in every paragraph of the section of the phrase “Kovalev and his co-conspirators” was aimed at giving the reader the impression the accusation is based on hard intelligence about possible collusion that doesn’t exist.
The Need for Critical Scrutiny of DHS Cyberattack Claims
The DHS campaign to establish its role as the protector of U.S. electoral institutions is not the only case in which that agency has used a devious means to sow fear of Russian cyberattacks. In December 2016, DHS and the FBI published a long list of IP addresses as indicators of possible Russian cyberattacks. But most of the addresses on the list had no connection with Russian intelligence, as former U.S. government cyber-warfare officer Rob Lee found on close examination.
When someone at the Burlington, Vt., Electric Company spotted one of those IP addresses on one of its computers, the company reported it to DHS. But instead of quietly investigating the address to verify that it was indeed an indicator of Russian intrusion, DHS immediately informed The Washington Post. The result was a sensational story that Russian hackers had penetrated the U.S. power grid. In fact, the IP address in question was merely Yahoo’s email server, as Rob Lee told me, and the computer had not even been connected to the power grid. The threat to the power grid was a tall tale created by a DHS official, which the Post had to embarrassingly retract.
Since May 2017, DHS, in partnership with the FBI, has begun an even more ambitious campaign to focus public attention on what it says are Russian “targeting” and “intrusions” into “major, high value assets that operate components of our Nation’s critical infrastructure”, including energy, nuclear, water, aviation and critical manufacturing sectors. Any evidence of such an intrusion must be taken seriously by the U.S. government and reported by news media. But in light of the DHS record on alleged threats to election infrastructure and the Burlington power grid, and its well-known ambition to assume leadership over cyber protection, the public interest demands that the news media examine DHS claims about Russian cyber threats far more critically than they have up to now.
Gareth Porter is an independent investigative journalist and winner of the 2012 Gellhorn Prize for journalism. His latest book is Manufactured Crisis: The Untold Story of the Iran Nuclear Scare.
The 10 Main Holes in the Official Narrative on the Salisbury Poisonings: #5 – The Feeding of the Ducks
By Rob Slane | The Blog Mire | August 27, 2018
In the previous piece, I began to focus on the official timeline of events on March 4th, as stated by The Metropolitan Police on 17th March, noting that there is a missing 4 hours in the morning, which investigators were very anxious to receive information on at the time, but which they have been conspicuously silent on since. Not only have they failed to update the timeline with information about the Skripals movements on the morning of 4th March, but they have failed to do so despite now having that information. How can I be sure they have it? Because both Sergei and Yulia Skripal have been awake and talking for months now.
But in this piece, I want to focus on something even more important. Something that is crucial for two reasons:
- Firstly, the Metropolitan Police do not mention it in their timeline, even though it absolutely did happen and is vital.
- Secondly, it completely demolishes the theory that the Skripals were poisoned by touching a nerve agent on the handle of Mr Skripal’s front door.
The incident in question is the duck feed. But before I come on to it, let’s just remind ourselves of the official timeline once more, so that we can then see where this incident fits in:
Saturday 3rd March
14.40hrs on Saturday 3 March: Yulia arrives at Heathrow Airport on a flight from Russia.
Sunday 4th March
09.15hrs on Sunday, 4 March: Sergei’s car is seen in the area of London Road, Churchill Way North and Wilton Road.
13.30hrs: Sergei’s car is seen being driven down Devizes Road, towards the town centre.
13:40hrs: Sergei and Yulia arrive in Sainsbury’s upper level car park at the Maltings. At some time after this, they go to the Bishops Mill Pub in the town centre.
14.20hrs: They dine at Zizzi Restaurant.
15:35hrs: They leave Zizzi Restaurant.
16.15hrs: Emergency services receive a report from a member of the public and police arrive at the scene within minutes, where they find Sergei and Yulia extremely ill on a park bench near the restaurant.
One of the things that is immediately obvious about this timeline is its astonishing vagueness in certain places. For instance, Mr Skripal’s car was apparently seen in three different areas — London Road, Churchill Way North and Wilton Road — at 9:15. Presumably it was seen on CCTV cameras in these locations, and presumably these cameras all have time and date stamps. In which case, why could the timeline not be more precise than suggesting that Mr Skripal’s car was at three locations at the same time?
But the vagueness of the time and location of the car in the morning really is small fry compared to the time and location given at 13:40hrs:
“Sergei and Yulia arrive in Sainsbury’s upper level car park at the Maltings. At some time after this, they go to the Bishops Mill Pub in the town centre.”
At some time after this? What exactly is that supposed to mean? Were there not CCTV cameras in The Maltings and in The Mill that could give a more precise timeline? The unnerving thing – given that this is one of the biggest and most important investigations Britain has ever seen – is that yes indeed there were. And yet what these cameras show has either been ignored in the timeline altogether, or incorporated into it in some sort of vague and nebulous way that – and I don’t know how else to process it – frankly looks very suspect.
I’ll come on to the bit about The Mill in the next piece, but before we get there, perhaps we can jog the memories of investigators by reminding them of a piece of CCTV footage that they certainly do have, which is time stamped, and which shows clearly where Sergei Skripal and Yulia were at a particular time.
After parking the car, at 1:40pm, the two of them were seen near the Avon Playground, in The Maltings, feeding ducks with some local boys. This was at 1:45pm and has been confirmed to me by one of the boys’ mothers, who was shown the CCTV footage by the police, which she said was really clear. She also confirmed to me that Mr Skripal was wearing jeans and a leather jacket, and that Yulia Skripal had a red bag.
The Metropolitan Police apparently don’t think the duck feeding incident important enough to include in their timeline, and so after the parking of the car, we are treated to the vague statement that, “at some time after this, they go to the Bishops Mill Pub.”
But it is incredibly important, for the following reason: it totally, completely and comprehensively debunks the idea that Mr Skripal was poisoned at his home, after his hand came into contact with a deadly nerve agent on the handle of his front door. Why?
BECAUSE HE HANDED BREAD TO THE BOYS, AND NONE OF THEM BECAME CONTAMINATED, THAT’S WHY!
Think about it. Zizzis has remained shut since the incident, because it was apparently contaminated, and the table that the Skripals ate their meal at “had to be destroyed” because of the apparently high concentration of nerve agent there. Likewise, The Mill has been closed ever since. And of course the bench too had to be destroyed, since it was apparently contaminated.
But these were all places visited by the Skripals AFTER the feeding of the ducks.
And so we are asked to believe the following preposterous notion: That Sergei and Yulia Skripal’s hands were contaminated with “military grade nerve agent” at the door of Mr Skripal’s house, so much so that certain places they visited on that afternoon had to undergo months of decontamination, and certain items they touched had to be destroyed.
And yet in between getting the nerve agent on their hands at the door, and the visits to those locations, Mr Skripal was seen on CCTV, at 1:45pm, handing bread to local boys to give to the ducks. With his contaminated hands, apparently. And one of those boys even ate a piece. And yet none of those boys managed to become contaminated the by the “military grade nerve agent” on Mr Skripal’s hands?
No amount of “they might have been wearing gloves” will do. Firstly, the temperature was actually quite warm (8-9 degrees) and so it’s unlikely that they were wearing gloves; secondly, who actually tears bread from a loaf whilst wearing gloves (probably nobody, is my guess); but thirdly, gloves apparently weren’t enough protection to prevent D.S. Bailey from becoming contaminated, allegedly at the door handle.
No, there is no way out of this. The duck feeding incident leaves the “nerve agent on the door handle” theory in tatters. If the duck feed happened – which it did – then the “Skripals becoming contaminated with nerve agent on the door handle” did not happen. To continue to believe that it did, in the light of Mr Skripal handing bread to boys, not one of whom became contaminated, is to cast off all reason and enter a twilight world of the absurd.
But it does at least explain why the incident doesn’t make it onto the timeline!
The 10 Main Holes in the Official Narrative on the Salisbury Poisonings: #1 – The Motive
The 10 Main Holes in the Official Narrative on the Salisbury Poisonings: #2 – The Intent
The 10 Main Holes in the Official Narrative on the Salisbury Poisonings: #3 – The Capability
The 10 Main Holes in the Official Narrative on the Salisbury Poisonings: #4 – The Missing Four Hours
The 10 Main Holes in the Official Narrative on the Salisbury Poisonings: #6 – The Meal and The Drink
Skripals – When the BBC Hide the Truth
By Craig Murray | August 27, 2018
On 8 July 2018 a lady named Kirsty Eccles asked what, in its enormous ramifications, historians may one day see as the most important Freedom of Information request ever made. The rest of this post requires extremely close and careful reading, and some thought, for you to understand that claim.
Dear British Broadcasting Corporation,
1: Why did BBC Newsnight correspondent Mark Urban keep secret from the licence payers that he had been having meetings with Sergei Skripal only last summer.
2: When did the BBC know this?
3: Please provide me with copies of all correspondence between yourselves and Mark Urban on the subject of Sergei Skripal.
Yours faithfully,
Kirsty Eccles
The ramifications of this little request are enormous as they cut right to the heart of the ramping up of the new Cold War, of the BBC’s propaganda collusion with the security services to that end, and of the concoction of fraudulent evidence in the Steele “dirty dossier”. This also of course casts a strong light on more plausible motives for an attack on the Skripals.
Which is why the BBC point blank refused to answer Kirsty’s request, stating that it was subject to the Freedom of Information exemption for “Journalism”.
10th July 2018
Dear Ms Eccles
Freedom of Information request – RFI20181319
Thank you for your request to the BBC of 8th July 2018, seeking the following information under the
Freedom of Information Act 2000:
1: Why did BBC Newsnight correspondent Mark Urban keep secret from the licence payers that he
had been having meetings with Sergei Skripal only last summer.
2: When did the BBC know this?
3: Please provide me with copies of all correspondence between yourselves and Mark Urban on the
subject of Sergei Skripal.
The information you have requested is excluded from the Act because it is held for the purposes of
‘journalism, art or literature.’ The BBC is therefore not obliged to provide this information to you. Part VI
of Schedule 1 to FOIA provides that information held by the BBC and the other public service broadcasters
is only covered by the Act if it is held for ‘purposes other than those of journalism, art or literature”. The
BBC is not required to supply information held for the purposes of creating the BBC’s output or
information that supports and is closely associated with these creative activities.
The BBC is of course being entirely tendentious here – “journalism” does not include the deliberate suppression of vital information from the public, particularly in order to facilitate the propagation of fake news on behalf of the security services. That black propaganda is precisely what the BBC is knowingly engaged in, and here trying hard to hide.
I have today attempted to contact Mark Urban at Newsnight by phone, with no success, and sent him this email:
To: mark.urban@bbc.co.uk
Dear Mark,
As you may know, I am a journalist working in alternative media, a member of the NUJ, as well as a former British Ambassador. I am researching the Skripal case.
I wish to ask you the following questions.
1) When the Skripals were first poisoned, it was the largest news story in the entire World and you were uniquely positioned having held several meetings with Sergei Skripal the previous year. Yet faced with what should have been a massive career break, you withheld that unique information on a major story from the public for four months. Why?
2) You were an officer in the Royal Tank Regiment together with Skripal’s MI6 handler, Pablo Miller, who also lived in Salisbury. Have you maintained friendship with Miller over the years and how often do you communicate?
3) When you met Skripal in Salisbury, was Miller present all or part of the time, or did you meet Miller separately?
4) Was the BBC aware of your meetings with Miller and/or Skripal at the time?
5) When, four months later, you told the world about your meetings with Skripal after the Rowley/Sturgess incident, you said you had met him to research a book. Yet the only forthcoming book by you advertised is on the Skripal attack. What was the subject of your discussions with Skripal?
6) Pablo Miller worked for Orbis Intelligence. Do you know if Miller contributed to the Christopher Steele dossier on Trump/Russia?
7) Did you discuss the Trump dossier with Skripal and/or Miller?
8) Do you know whether Skripal contributed to the Trump dossier?
9) In your Newsnight piece following the Rowley/Sturgess incident, you stated that security service sources had told you that Yulia Skripal’s telephone may have been bugged. Since January 2017, how many security service briefings or discussions have you had on any of the matter above.I look forward to hearing from you.
Craig Murray
I should very much welcome others also sending emails to Mark Urban to emphasise the public demand for an answer from the BBC to these vital questions. If you have time, write your own email, or if not copy and paste from mine.
To quote that great Scot John Paul Jones, “We have not yet begun to fight”.
US not ready for substantive dialogue with Russia on cybersecurity – Lavrov
RT | August 28, 2018
The US has not yet provided any evidence of ‘Russian hackers’ interfering in the 2016 presidential election, Russian Foreign Minister Sergey Lavrov said Tuesday.
“For the second year we have been proposing that a bilateral working group on cybersecurity should be created to discuss and remove mutual concerns, including those related to influence on electoral processes in [the US and Russia],” he told the Slovak newspaper Pravda.
However, Washington is avoiding a “professional exchange of views,” he said.
It is only surprising “how easily it was possible to put a discussion of this unfounded theme at the center of the intra-American socio-political discussion,” Lavrov noted.
5 timely reminders that the media think you are an idiot…

By Kit | OffGuardian | August 28, 2018
The corporate media think we are stupid. All of us. They have as much respect for our intellect or ability to reason as they do for the truth. This is displayed, in size 20 font, on the front page of every newspaper every single day. They paint a picture of an absurd world, and expect us all to nod along with it, blithely accepting their stories as true, no matter what laws of reason – or even physics – they bend to suit their purpose.
The world in the newspaper and on the television is not real in any true sense of the word. Merely a crazy fun-house mirror reflection of the truth. Important features shrunk to nothing, tiny flaws blown up out of proportion. Apparently solid shapes that – on inspection – are nothing but strange plays of light and shadow.
With that in mind, let’s remind ourselves of the kind of completely bonkers things we’re all expected to believe.
1. The Inherent silliness of “ISIS”
This section was going to be more specific, but as I looked back over recent history, there was no single absurdity that highlighted how stupid the ISIS story was.
ISIS was, and is, silly. A few bullet points to demonstrate this – and a reminder that these are not exaggerated in any way. These are, supposedly, facts:
- They were making $1-$3 million PER DAY smuggling oil out of Syria, in convoys kilometres long that the US air force either couldn’t find or wouldn’t bomb because of “risks to civilians”. How they had the technical expertise to extract and process this oil was never explained.
- They minted their own currency.
- They published end-of-year reports, like a business, and kept detailed accounts on flash drives and USB sticks. Despite this, no ISIS bank accounts were ever seized, monitored or shut down.
- They had multiple social media accounts, YouTube channels – often described as “ISIS linked social media accounts” – these accounts weren’t locked, blocked or deleted. The registered owners weren’t arrested. They had their own twitter app which was impossible to block and created their own social network.
- They had their own TV channel, with an animated logo, a waving flag, in the corner of their videos. Think on this – somebody, somewhere, made that logo.
- They had fleets of Toyotas, which we’re supposed to believe they just sort of… acquired. They are all clean, new and undamaged. They are all colour-matched too, of course. There are red ones, white ones, black ones and tan ones. With and without logos painted on the hood. They deployed these trucks in photo-shoots and “viral” videos, the theoretical production of which simply boggles the mind. A bunch of black Toyota’s crossing the desert doesn’t look like much, but think about the actual logistics of making the video. They had to drive up to this spot, drop off the camera crew and equipment, drive back over the horizon, properly time their entrance by synchronizing all the driving and spacing the trucks out evenly, drive past the camera crew waving their flags… then drive back and pick up the camera men and equipment. All of this in the middle of a war zone.
- Of course all their videos had the same music, the ISIS theme, which was Arabic voices singing in close harmony. We’re supposed to believe that – somewhere in the heart of their war-torn empire – a bunch of crazy zealots gathered round a microphone to sing a capella melodies about “death to the west”, while a frustrated technician muttered to himself about “levels” and how Muhammad is flat on the high note. This spawned their own genre of music, which NME did a story on.
It’s so… stupid. And yet the media says it, and expects us to believe it.
ISIS – the all-powerful death cult, the existential threat to Western democracy, on the verge of “regional dominance”. There was a map and everything – world domination by 2020.
Despite all this, ISIS – the untouchable hydra of evil – completely fell apart as a force in the region just months after Russia and Iran got involved in the Syrian war.
Why was this?
Could it be that ISIS were just a media creation – the PR arm of the CIA’s jihadist proxy army – and, in truth, barely existed as fighting force? Existing, rather, to give Western powers an excuse to conduct air strikes on Syrian territory?
Or could it be that the MSM realised that 10,000 insane, bloodthirsty zealots taking time out of their devout holy war to have design meetings about coinage, or shoot music videos in Dune buggies, rings rather hollow?
It’s all a bit silly isn’t it?
2. The Syrian government Is collectively suicidal
Several times, in the last couple of years, Western leaders have made remarkably prescient statements – something along the lines of “We will not tolerate the use of chemical weapons on civilians”, or “We will act if chemical weapons are used”. In fact, in just the last few days both the US and France have reissued these warnings.
Despite these warnings, and though it offers him literally zero strategic advantages of any kind, Assad keeps deploying his super-secret chemical weapons against civilians… just because. He’s winning the war, it’s pretty much over, the only thing that could swing it against him is NATO, and he keeps deliberately inciting them to attack him.
There’s only 2 explanations for that – either he, and his government, are low-key suicidal, or it never happened, and the propagandists in the media truly believe we are completely stupid.
Then there’s the photographs.
Syria knows they have been in America’s crosshairs for years, since well before the start of the Arab spring. They are aware of Israel’s designs on Syrian land, and more than familiar with the US modus operandi re: “humanitarianism”. They KNOW the worst thing they could do is give America, and their NATO allies, even the whisper of a war crime to get indignant about.
… and yet we’re supposed to believe, not only that the regime tortured and executed tens of thousands of “peaceful protestors” for absolutely no reason, but they also kept a carefully photographed and catalogued record of their crimes.
This was brought up in the Guardian today, the famous “Caesar Photographs”, photos of 11,000 people the Assad government tortured and killed, all properly catalogued and numbered and then – conveniently – leaked by some unknown “former guard” and displayed in London like some morbid art exhibition.
The identity of the “leaker” remains a mystery, and there is literally zero evidence the photographs are a) from Syria or b) real.
Does this version of events sound even slightly reasonable?
3. Amnesty International used echolocation to recreate a Syrian prison
They really did. They have some guys claiming to be Syrian resistance members who were held in one of Assad’s “torture prisons”, but they were either blindfolded or in darkness the whole time, so in order to map out the interior of the prison… Amnesty International played sounds to them, to see if they sounded the same. I truly wish I was joking:
Inmates were constantly blindfolded or forced to kneel and cover their eyes when guards entered their cells, so sound became the key sense by which they navigated and measured their environment – and therefore one of the chief tools with which the Forensic team could reconstruct the prison layout. Using a technique of “echo profiling”, sound artist Lawrence Abu Hamdan was able to determine the size of cells, stairwells and corridors by playing different reverberations and asking witnesses to match them with sounds they remembered hearing in the prison.
There’s no reports as to why exactly the men were locked up, how they got away, why they were released and not executed like everyone else OR – indeed – where they acquired their bat-like super hearing.
… But we do now have a 3D model of Assad’s “torture prison”. We even know which room is the crematorium too, because it looked like the snow on the roof had melted in one satellite photo… and the only thing that makes a roof hot is the burning corpses of dissidents.
The whole process is part of a completely made up recently developed field known as “forensic architecture”. In simple terms, it seems “forensic architecture” is looking at the outside of a building – or indeed a photograph of the outside of a building – and guessing what’s inside. While this might seem difficult, pointless, or even insane to most people… to the mainstream media it is worth of thousands of words of coverage and, indeed, winning media awards.
Does any of that really make any sense to you?
4. Jeremy Corbyn hates the Jews
Jeremy Corbyn is soft – maybe, arguably – too soft for the job that history has violently hoisted on to his shoulders, but soft none the less. He rides his bike to work, wears cardigans, is a vegetarian. He has campaigned for peace and against war his entire life. He was arrested for protesting apartheid whilst Margaret Thatcher was calling Nelson Mandela a terrorist, he spoke out against Pinochet while the General was a darling on both sides of the Atlantic.
He has won two international peace prizes.
The idea that, during a public career dedicated to the socialist ideals of decency and fairness, he was secretly thinking “Bloody Jews!” the whole time is completely absurd. Insultingly absurd, and there is not a single piece of evidence to suggest otherwise. There is nothing more to be said on the matter.
5. Russiagate
This is the big one, currently. The grand-daddy of the nothingburgers. Russiagate never happened. There was no collusion, no cheating or vote hacking or pay-offs. They have found literally zero evidence anything ever took place, seizing upon tiny anecdotal scraps and blaring them out in FULL CAPS HEADLINES to make a case in the court of public opinion that would never stand in an actual court.
Where “Russiagate” is different from most invented media schlock however, is the sheer weight of counter evidence. For most media fiction you can say “Well, there’s very little evidence to support that” (see Corbyn = anti-Semite as a classic example). With Russiagate you can go even further: There is a ton – A TON – of evidence to the contrary, clear-cut evidence that Russia (and Putin) have nothing to do with Trump being President. The media refuse to acknowledge this evidence, directly and contemptuously challenging the public’s ability to reason.
Below is a list of unchallenged, non-controversial facts about Russiagate:
- The only proven, admitted, wrong-doing in the 2016 Presidential election was carried out by the DNC, who rigged the primaries so Clinton would be the democratic candidate. This was later admitted to by members of the DNC.
- The e-mails which first brought this to light were published by WikiLeaks, there is no proven link between WikiLeaks and the Russian government.
- Julian Assange, founder of WikiLeaks claimed the e-mails were from an internal leak, not the result of a hack.
- The “Trump-Russia” dossier, a collection of (possibly fabricated) dirt put together by British ex-spy Christopher Steele, was paid for by the DNC and Clinton’s campaign.
These facts, alone, should bring Russiagate down… but there’s more. Since becoming President, Donald Trump has:
- Armed the Ukrainian coup government.
- Bombed Syria.
- Torn up the Iran deal.
- Sanctioned Russia over the Skripal case.
- Sanctioned Russia over “election interference”.
- Expelled Russian diplomats.
- Killed over 200 Russian “mercenaries” in Syria.
These are policies that not only run counter to ALL of Russia’s interests, but very nearly brought us to the brink of World War 3.
And yet we’re told, over and over, to ignore our own logical minds and believe that Trump is Putin’s “puppet”. That Trump is “soft” on Russia.
Why would a product of Russian collusion pursue policies harmful to Russia? How many Russians need to die before we accept that Trump is anything but soft?
The media line on this issue is insane, and dangerous. In refusing to acknowledge the actual truth – that the US Deep State is pushing for conflict with Russia – the media are dragging us toward apocalypse, smiling happily to themselves as they go.
They are either all delusional morons, think WE are all delusional morons, or – most probably – both.
The inmates are running the asylum, declaring the rest of us insane because none of us are hearing voices.
This is why the media is in decline, why the BBC is losing its audience and the newspapers have plummeting readership, because people are tired of being treated like idiots and herded like cattle. We’ve made a collective decision to cut the bullshit out of our lives. The world is heading towards a split, two parallel universes running together – the real world, where reasonable pragmatic people get on with the struggles of life, and the media world, where fake people write about pretend events in newspapers nobody reads.
The media has become that manipulative spouse who lies and cheats and tells you it’s all your fault. A narcissistic gaslighter who just will not change.
It’s time to make a clean break.
The 10 Main Holes in the Official Narrative on the Salisbury Poisonings: #4 – The Missing Four Hours
By Rob Slane | The Blog Mire | August 25, 2018
According to the Metropolitan Police investigation into the poisoning of Sergei and Yulia Skripal, the official timeline of their movements on the weekend of the incident is as follows:
Saturday 3rd March
14.40hrs on Saturday 3 March: Yulia arrives at Heathrow Airport on a flight from Russia.
Sunday 4th March
09.15hrs on Sunday, 4 March: Sergei’s car is seen in the area of London Road, Churchill Way North and Wilton Road.
13.30hrs: Sergei’s car is seen being driven down Devizes Road, towards the town centre.
13:40hrs: Sergei and Yulia arrive in Sainsbury’s upper level car park at the Maltings. At some time after this, they go to the Bishops Mill Pub in the town centre.
14.20hrs: They dine at Zizzi Restaurant.
15:35hrs: They leave Zizzi Restaurant.
16.15hrs: Emergency services receive a report from a member of the public and police arrive at the scene within minutes, where they find Sergei and Yulia extremely ill on a park bench near the restaurant.
Whilst fully realising that such a timeline does not necessarily need to include every detail, such as the time that Yulia arrived in Salisbury on the Saturday afternoon, nevertheless, there are some serious problems with this account, which are broadly as follows:
- Firstly, it omits crucial information from the morning of 4th March.
- Secondly, it ignores a very important incident on the afternoon of 4th March.
- Thirdly, it is, I believe, incorrect in the sequence of events it presents.
In this piece, I want to concentrate on the first one of these — the morning — and then cover the second and third in subsequent pieces.
When the timeline above was released by the Metropolitan Police on 17th March, the whereabouts of the Skripals on the morning of 4th March was unknown. At the press conference in which the timeline was released, Deputy Assistant Commissioner, Neil Basu, who is in charge of the investigation, appealed for information about their movements on the morning of 4th March:
“We believe that at around 9.15am on Sunday 4 March, Sergei’s car may have been in the areas of London Road, Churchill Way North and Wilton Road. Then at around 1.30pm it was seen being driven down Devizes Road, towards the town centre.
We need to establish Sergei and Yulia’s movements during the morning, before they headed to the town centre. Did you see this car, or what you believe was this car, on the day of the incident? We are particularly keen to hear from you if you saw the car before 1.30pm. If you have information, please call the police on 101″ [my emphasis].
Although the Skripals’ movements were unknown, it had been thought that they visited the cemetery on London Road, since there were apparently fresh flowers on the grave of Mr Skripals wife, Liudmila. But there was one very important piece of information that was known, which was extremely interesting. According to The Times:
“The Russian spy and his daughter poisoned by nerve agent turned off the GPS tracking on their mobile telephones for four hours on the day they were attacked, it was reported yesterday.”
That piece of information alone is enough to make those missing four hours in the morning vital to any investigation. There must have been a reason for the Skripals to make their phones untraceable during that time and – with apologies for stating the blindingly obvious – it was clearly because they did not want their movements at that time to be known. The most plausible explanation for this would seem to be that they had some kind of meeting that morning, a meeting which was important and secret enough for them not to want certain other people knowing where they were and what they were doing.
It is entirely understandable that the Metropolitan Police did not include details of the Skripals’ movements on the morning of 4th March in the timeline they released on 17th March, since they did not know them at that time. And given that the Skripals had made their phones untraceable, it is also entirely understandable why the Metropolitan Police desperately wanted people to come forward with information about the four hour time period.
But here’s the thing: More than five months later, and this timeline has not been updated. Not only this, but the Metropolitan Police have gone mysteriously quiet about this part of the timeline. Why mysterious? Simply because Sergei and Yulia Skripal have been awake and talking for months, and unless they have steadfastly refused to tell investigators what they were doing on that morning – which is frankly inconceivable – then the Metropolitan Police must know where they were and what they were doing on that morning. And yet they’ve stopped talking about it and have not updated their timeline since 17th March.
Which raises the following questions:
- Where were Sergei and Yulia Skripal on the morning of 4th March?
- What were they doing?
- Why did they feel the need to turn off the GPS tracking on their phones?
- Were they meeting someone, and if so who?
- Why has the Metropolitan Police not updated its timeline to include the Skripals’ whereabouts that morning, since it must by now be well aware of them?
The 10 Main Holes in the Official Narrative on the Salisbury Poisonings: #1 – The Motive
The 10 Main Holes in the Official Narrative on the Salisbury Poisonings: #2 – The Intent
The 10 Main Holes in the Official Narrative on the Salisbury Poisonings: #3 – The Capability
The 10 Main Holes in the Official Narrative on the Salisbury Poisonings: #4 – The Missing Four Hours
The 10 Main Holes in the Official Narrative on the Salisbury Poisonings: #6 – The Meal and The Drink
Russophobia digest part 6: Evidence is optional as alleged anti-vaxx Russian bots go phishing
RT | August 24, 2018
Alleged Russian bots have been at the forefront of another week of Russophobia, with a new but familiar pattern emerging. Scare stories and accusations are made, before a later admission that no actual evidence is available.
RT takes a look at the last seven days or so of Russophobia.
Democrats’ security chief missed the memo
One of the real values of Russophobia is that it means thought and proof are rarely, if ever, needed anymore. Why find out what really happened when there is a decent conclusion to jump to?
For example, this week Bob Lord, the Democratic National Committee’s chief security officer, claimed that the organization’s US voter database had been hacked. Only, he later had to admit it was actually a ‘phishing test.’
Yep, nobody told the security chief about the security test, and he didn’t bother asking either, because it’s much easier to simply insinuate that Russians did it. To be fair to Lord, he didn’t appear to overtly use the ‘R’ word, but almost every media report on the non-incident seasoned its coverage liberally with accusations against Russia.
Microsoft’s marketing dept jumps on Russophobia bandwagon
Staying in the murky world of unsubstantiated cyber-claims, Microsoft said it has also thwarted phishing attacks on political targets by a group “widely associated” with Russia (Fancy Bear, in case you’re interested). It backed up its claims in the now-time-honored fashion of admitting there is “no evidence” that the dodgy domains detected were used in any successful attacks — and there’s no evidence “to indicate the identity of the ultimate targets.”
So, why is Microsoft getting involved? Because it’s got a brand new product maybe? Bill Gates’ boys have come up with anti-hacking software ‘AccountGuard’ as part of its ‘Defending Democracy Program.’
It provides “state-of-the-art cybersecurity protection at no extra cost to all candidates and campaign offices at the federal, state and local level, as well as think tanks and political organizations we now believe are under attack.”
And they claim the Russians are dangerous!?
Pro-pox bots
Those busy little alleged Russian bots are also driving the online anti-vaccine debate in the US, apparently, according to research in the US. No surprise there really, Russian bots real or imagined are accused of driving every online debate these days.
David Broniatowski from the George Washington School of Engineering and Applied Science said: “… many anti-vaccine tweets come from accounts whose provenance is unclear. These might be bots, human users or ‘cyborgs’ – hacked accounts that are sometimes taken over by bots. Although it’s impossible to know exactly how many tweets were generated by bots and trolls …”
“Impossible to know,” “provenance unclear.” So again, no real evidence, so it must be the Russians, mustn’t it?
Someone better check whether Jenny McCarthy and Jim Carrey are Russian bots too, because they’re not too keen on vaccinations either. Apparently neither is Donald Trump, but you can hardly accuse him of… Oh.
Manafort: Conviction without collusion
Russophobes were jumping for joy at the conviction of Trump’s former election chief Paul Manafort this week. He was sent down for tax fraud, and bank fraud, and hiding bank accounts. What he definitely wasn’t sent down for was colluding with Russia, which is really a little strange considering the man responsible for sending him to court was Special Counsel Robert Mueller, who was only appointed to investigate exactly that. As we’ve seen, though, evidence is optional when Russians are the target.
In the wise words of America’s commander-in-chief: “This has nothing to do with Russian collusion. This started as Russian collusion. This has absolutely nothing to do [with it].” Say what you want about Donald Trump…
Read more:
Germany Can’t Give Up on Cooperation With Russia in Oil and Gas – Merkel
Sputnik – 24.08.2018
Germany has greenlighted the Nord Stream 2 project to bring Russian gas to Europe and is under strong pressure from the US, which warns that the project is making Germany dependent on Russia. Berlin insists that the project is entirely commercial.
A planned sub-sea pipeline that will bring gas directly from Russia under the Baltic Sea will not make Germany dependent on Russia for energy, Chancellor Angela Merkel told university students in the Georgian capital Tbilisi on Friday, on the second day of her trip to the Caucasus.
Angela Merkel described continued Russian oil and natural gas supplies to Germany as an important factor in ensuring the country’s energy security.
”We have a decades-long history of economic cooperation with Russia, including on CO2 emissions. We have consistently been reducing our use of coal and we need natural gas coming to us via Belarus, Ukraine and Poland, that’s why we support Nord Stream 1 and 2,” Merkel noted.
She noted that Germany wanted to make sure that Russia continued delivering some gas via Ukraine even after the Nord Stream 2 pipeline was finished.
Mentioning the importance of expanding the so-called “Southern Corridor” for natural gas supplies also from Azerbaijan, she still pointed out that buying gas from Russia was cheaper than buying it elsewhere.
“Europe and Russia, then the Soviet Union, had very close energy cooperation during the Cold War. We can’t afford giving up on cooperation with Russia in oil and gas. Of course, we can have natural gas coming from Azerbaijan, but the truth is that it will not be available at the price we are paying for Russian gas,” Merkel said.
Some countries that are afraid of losing revenues from Russian gas transit, above all Ukraine, are opposed to Nord Stream 2.
The project is also facing opposition from the United States, which has ambitious plans of LNG exports to Europe.
Russia has repeatedly urged its European partners not to perceive the Nord Stream pipeline as an instrument of influence insisting that the project is an entirely economic one.
AfD MP: ‘We Refuse to Support the US Gas Industry at Germany’s Expense’
Sputnik – August 24, 2018
Despite opposition to the Nord Stream II pipeline from some Eastern Europe states, the consortium of energy companies involved in the joint venture are going ahead with the project.
Sputnik reporter Suliman Mulhem spoke to Christian Blex, a representative of the Alternative for Germany (AfD) Party in the Bundestag, about the proposed pipeline and the untapped potential of bilateral EU-Russia trade.
Europe’s Dilemma
Europe’s growing demand for natural gas, coupled with falling production in many longstanding European natural gas exporters, such as Norway, has put the region on course to face an energy deficit unless it swiftly alters its energy mix or builds the necessary midstream infrastructure to import more natural gas from Russia.
A move away from natural gas is unlikely to happen, as it is unrivaled by most alternatives in terms of affordability, abundance, and is significantly more eco-friendly than other fossil fuels, such as coal.
Alternatively, Europe could look to make up its energy shortfall by importing US liquefied natural gas (LNG), though, as Dr. Blex explained, this course of action is riddled with drawbacks and is not in Germany’s interests.
“The position of the AfD is that Germany should make an interest-based policy and due to the current economic climate and the German government’s recent policies, we must focus on importing. As Russia currently supplies the cheapest option in the form of natural gas, it is only logical that we import from them,” Dr. Blex told Sputnik on Friday.
“Since the US cannot currently compete in terms of both price and infrastructure, the idea of seriously switching to US gas is a pipe dreams. In addition, the AfD refuses to support the US gas industry at the expense of Germany, or to solely serve Washington’s geostrategic interests.”
Baseless Prophecies
Dr. Blex expressed his support for Nord Stream II, insisting that it will benefit Germany and the wider European economy, dismissing concerns that Moscow could use Europe’s reliance on Russian natural gas as leverage over the continent.
“Despite all the prophecies of doubts about the danger of a Russian monopoly position and the associated blackmail potential, as well as its alleged political uncertainty as a partner, Russia has always reliably adhered to its supply contracts with Germany over the past 30 years, which is why we regard Russia to be a reliable partner. As long as this remains so, I see no need to orient ourselves elsewhere,” Dr. Blex said.
In fact, this is more likely to be an issue if Europe swapped out Russian natural gas for US LNG, as the Trump administration has repeatedly showed itself to be an unreliable partner, with President Trump withdrawing from the Iran nuclear deal and recklessly imposing tariffs against several key US trade partners in 2018.
In virtually every case of opposition to Nord Stream II, the critic has a vested interest in preventing the pipeline’s completion; Russian natural gas is perhaps the single largest barrier to US LNG taking over Europe’s energy market, while some European states are keen to hinder the project to ensure their revenue streams from existing Russian gas transit deals aren’t slashed.
Undisputed Potential & Future Relations
Although Europe maintains a fruitful partnership with Russia in the energy sector, sanctions and the contemporary political climate have inhibited both sides from exploring new avenues and benefiting from the untapped economic potential an amicable relationship offers.
Dr. Blex noted this “tremendous potential,” and voiced concerns of German and other European businesses being adversely affected by the sanctions, saying, “It is undisputed that trade between the European Union and Russia has tremendous potential. German companies in the automotive, chemical and electronic industries suffered losses due to sanctions. Normalization of relations is therefore of Russian as well as European and German interest.”
EU farmers have often protested against the sanctions, dumping their produce on the streets, as they’ve been hit hard by the sanctions.
“The AfD advocates ending the sanctions,” the German MP added.
Moreover, the Bundestag member called for a “pan-European policy” that fosters better political and economic relations with Russia, but said the current German federal government is unlikely to adopt such an approach.
“A pan-European policy that strengthens economic relations with Russia would be desirable. Unfortunately, the political will for this geostrategic reasoning does not yet exist; the Merkel government is against it.”
However, Dr. Blex described himself as optimistic “that the steady increase in power of the AfD” will shift Germany’s stance and lead to a more productive relationship with Russia.
“I therefore hope that in the long term, throughout the EU, there will be a recognition that Russia must be seen as a partner rather than an enemy,” Dr. Blex concluded.
The 10 Main Holes in the Official Narrative on the Salisbury Poisonings: #3 – The Capability
By Rob Slane | The Blog Mire | August 23, 2018
Once again I return to Theresa May’s statement of 26th May, in which she stated the following:
“In conclusion, as I have set out, no other country has a combination of the capability, the intent and the motive to carry out such an act.”
She then went on to claim:
“We have been led by evidence not by speculation.”
However, as I showed in Part 1 and Part 2, her statement to the Commons contained no actual evidence of motive or intent. Claims and assertions, but nothing more.
But what of capability? Looking through the statement, here are the key passages that might be said to fall into this category:
“As I set out for the House in my statements earlier this month, our world-leading experts at the Defence Science and Technology Laboratory at Porton Down positively identified the chemical used for this act as a Novichok – a military-grade nerve agent of a type developed by the Soviet Union.”
“And we have information indicating that within the last decade, Russia has investigated ways of delivering nerve agents probably for assassination – and as part of this programme has produced and stockpiled small quantities of Novichoks.”
Her evidence, such that it is, therefore falls into two categories: firstly, capability with regard to the weapon allegedly used to poison the Skripals; secondly, capability with regard to method of delivery of the weapon.
There are three things to say with regard to the first category. To begin with, it is not quite the case that Porton Down scientists had “positively identified the chemical” as a “Novichok”. In the evidence presented to the High Court between 20th – 22nd March, here is how the Porton Down Chemical and Biological Analyst described the substance:
“Blood samples from Sergei Skripal and Yulia Skripal were analysed and the findings indicated exposure to a nerve agent or related compound. The samples tested positive for the presence of a Novichok class nerve agent or closely related agent [my emphasis].”
As you will notice, there is a degree of ambiguity in this statement which is not present in Mrs May’s statement made a few days later. Ought she not to have recognised this?
Secondly, it has been conclusively shown that a number of other countries either have produced, or know how to produce substances within the class of nerve agents that Mrs May referred to as “Novichoks”. The Czech Government has admitted producing a small quantity of the closely related substance, A-230; Iran has produced it, in compliance with the OPCW in 2016; The German Intelligence Agency, BND, was given the formula back in the 1990s, and they shared it with a number of other NATO countries, including the US and UK. The Edgewood Chemical and Biological Defense Command in Maryland, USA, recorded the formula back in 1998.
The point of this is not to point the finger at any of those countries. Merely to say that knowledge of and production of “Novichok” is by no means confined to one country. And in any case, according to one of the world’s leading experts in organic chemistry, David Collum, Professor of Organic Chemistry at Cornell University, it doesn’t even require a State party. He asserts that “any credible organic chemist could make Novichok nerve agents.”
The fact that other countries know how to produce “Novichoks”, and in some cases have produced it, shows the claim that its apparent use in Salisbury proves Russian culpability to be complete nonsense. It’s as silly as saying that a poisoning using VX points to Britain because VX is a type of nerve agent developed by Britain.
And thirdly, if the British Government did indeed have information that the Russian Government had a secret programme investigating ways of delivering nerve agents, and had produced and stockpiled small quantities of Novichoks, then it had an obligation to inform the OPCW under the Chemical Weapons Convention, which it apparently failed to do. Furthermore, as a State Party to the Convention, it should have raised objections in 2017, when the OPCW’s Director-General, Ahmet Üzümcü, declared the following:
“The completion of the verified destruction of Russia’s chemical weapons programme is a major milestone in the achievement of the goals of the Chemical Weapons Convention. I congratulate Russia and I commend all of their experts who were involved for their professionalism and dedication. I also express my appreciation to the States Parties that assisted the Russian Federation with its destruction program and thank the OPCW staff who verified the destruction.”
So much for Mrs May’s evidence of capability regarding the weapon, what of her evidence regarding the delivery?
When she stated that her Government had information that the Russian Government had investigated ways of delivering nerve agents, she was, I believe, referring to the alleged “assassin’s manual”, which the Government says it possesses, but will not show because it is classified, and which apparently contains information showing that Russian agents were trained in putting poison on door handles.
Three brief points about this:
1. It really is utter nonsense. Smearing poison on a door handle would be a frankly ludicrous way to target someone for assassination, since you could never be sure that your target would actually touch it (you never know, maybe a postman or a milkman or the man from Amazon might get there first).
2. Salisbury was treated to dozens of guys in Hazmat gear decontaminating certain parts of the city, since the substance in question was apparently so lethal that, according to Alastair Hay, Professor of Environmental Toxicology at the University of Leeds:
“A few millilitres would be sufficient to probably kill a good number of people.”
Are we really supposed to believe that the Russians have either:
a) Developed ways of putting this stuff on door handles without the requisite chemical protection and perhaps just a pair of Marigolds, or
b) Have people stupid enough to try.
3. But the biggest problem is this: The British Government was starting to point the finger at the Russian Government within a few days of the poisoning, and it was later stated that one of the reasons for this was the manual that they apparently possessed. But if they did indeed have this manual, and it was the reason for their apportioning of blame as early as 12th March:
a) Why was the door handle not the focus of the investigation from the very start?
b) When are those police officers who stood within feet of that door, and those who no doubt went in and out of the house using the door handle, going to sue Her Majesty’s Government for negligence and their failure to act on the intelligence they apparently had?
If there is indeed such a manual, my guess is that it was put together by a chap named Steele.
The 10 Main Holes in the Official Narrative on the Salisbury Poisonings: #1 – The Motive
The 10 Main Holes in the Official Narrative on the Salisbury Poisonings: #2 – The Intent
The 10 Main Holes in the Official Narrative on the Salisbury Poisonings: #3 – The Capability
The 10 Main Holes in the Official Narrative on the Salisbury Poisonings: #4 – The Missing Four Hours
The 10 Main Holes in the Official Narrative on the Salisbury Poisonings: #6 – The Meal and The Drink
Featured Video
EUROPE FEARS RUSSIA’S NEXT MOVE / Ian Proud
or go to
Aletho News Archives – Video-Images
New Book
New Book: No Autoimmunity The Body Doesn’t Attack Itself
Lies are Unbekoming | September 24, 2026
 The label for Humira, once the best-selling drug in the world, lists its risks in plain print. One of them, in the label’s own words, is new “autoimmune” disease.
A drug prescribed for a condition labelled autoimmune carries a warning that it can cause a condition labelled autoimmune. That contradiction sits in every box, on a folded paper almost nobody reads.
My new book starts there.
No Autoimmunity: The Body Doesn’t Attack Itself
For seventy years, “your body is attacking itself, and we don’t know why” has ended the conversation for people diagnosed with multiple sclerosis, lupus, rheumatoid arthritis, Hashimoto’s, Type 1 diabetes, Crohn’s and psoriasis. More than eighty conditions now carry the autoimmune label. The diagnosis comes with a prescription for life. It almost never comes with a question about cause.
This book asks the question and answers it from the framework’s own records: its drug labels, its journals, its regulatory filings, and its own experiments. … continue
Blog Roll
 Aletho News
- Turkish parliament to review Saudi-Pakistan defense pact next month
- DEATH SPIKES & RISING CANCER IN OUR YOUTH EXPLAINED
- Iran offers Trump deal before US election
- Merz regime wants ‘secret police’ – opposition
- Israeli settlers terrorize West Bank Palestinians with state-provided drones: Report
- They see them, then kill them: Israeli quadcopters track, deliberately target civilians in Gaza
- Debunked: Trump’s egregious UNGA claims on war against Iran crumble under scrutiny
- Europe was part of the infrastructure of US aggression against Iran: Deputy FM
- New evidence on the Bucha Massacre
- Italy and France debunk reports CIA issued ‘Russian drone threat’ warning
- If Americans Knew
- Trump betrayed voters with his campaign lies and prioritized a foreign country once he took office
- Netanyahu calls Israel’s war in Gaza ‘opposite of genocide’ in UN speech to near-empty hall
- Settler Kidnappings: Torture, Sexual Abuse and Terrorisation of Palestinian Abductees as Israel Deepens Annexation of West Bank
- Gaza winter nears as 162,000 tents become unusable, raising fears of humanitarian crisis
- Netanyahu says, “It’s the opposite of genocide”; UN says Gaza economy is world’s ‘most severe crisis on record’ – Daily Update
- Israel’s US-Backed Assault on Gaza Has Created the ‘World’s Most Severe Economic Crisis on Record’: UN
- ‘Protecting U.S. Citizens’… From Israel
- ‘This is where I live now, the back of a truck’: a day in the life of a grandmother in Gaza
- In UN Speech, Iran’s President Displays Pictures of Children Killed by US, Brings Attention to Israel’s Nuclear Arsenal
- Israel displaces hundreds of Palestinians amid wave of demolitions in West Bank
- No Tricks Zone
- New Study: Earth And Venus Surface Warmth Largely Explained By Convection And Lapse Rate, Not CO2 Or Radiation
- 2025 Nature Paper Claiming Worsening Global Drought Gets RETRACTED …Heavily Flawed
- New Study: ‘Global Drought Shows No Detectable Recent Acceleration Under Climate Warming’
- Economic Masterminds: German Socialists Suggest Taxing Productivity Gains Stemming From Using AI
- The South China Sea Has Not Been Cooperating With The Climate Change Narrative
- Energy Crisis: Germany Enters Heating Season With Historically Low Gas Reserve Fill Levels
- New Study: The Antarctic Ice Sheet Gained Mass From 2020-2024 Due To Staggering Snow And Ice Accumulation
- Study: Ocean Heating Rates From Thousands Of Years Ago ‘Dwarf’ Modern Ocean Heating Rates
- Climate Extremists Target, Attack Large-Scale Power Grid Infrastructure In Germany!
- New Study: Antarctic Ice Melt Has Contributed Less Than 1 Centimeter To Sea Level Rise In The Last 30 Years

