NY Times Doesn’t Think That NSA Sharing Raw Communications With Israel Is Newsworthy
By Mike Masnick | Techdirt | September 16, 2013
Last week, we were among those who wrote about the latest revelations via the Guardian about how the NSA was sharing raw communications it had collected with Israeli intelligence. This is a big story for any number of reasons, but apparently the NY Times doesn’t think so. When Public Editor Margaret Sullivan asked why, the managing editor basically said the story wasn’t newsworthy:
He told me that The Times had chosen not to follow the story because its level of significance did not demand it.
“I didn’t think it was a significant or surprising story,” he said. “I think the more energy we put into chasing the small ones, the less time we have to break our own. Not to mention cover the turmoil in Syria.”
So, I asked him, by e-mail, was this essentially a question of reporting resources? After all, The Times could have published an article written by a wire service, like Reuters or The Associated Press.
“I’d say resources and news judgment,” he responded.
The resources issue is one I can understand totally. Here at Techdirt, we probably cover about one quarter to one third the number of stories we’d like to (which is also why I have about a thousand open tabs of stories I’m “hoping” to get to one of these days). But to claim that it’s not “significant” or “surprising” or somehow newsworthy is pretty crazy. This is a major part of the story — where the NSA keeps insisting that it is exceptionally careful with the data it collects, yet here it is handing off a ton of communications, including those of Americans, off to a foreign intelligence agency with basically no oversight. If the NY Times doesn’t think that’s newsworthy, the NY Times needs to recalibrate its newsworthy scale.
Related article
The NSA Is Also Grabbing Millions Of Credit Card Records
By Tim Cushing | Techdirt | September 16, 2013
In addition to everything else it’s collecting, the NSA also has millions of international credit card transactions stashed away in its databases, according to documents viewed by Spiegel.
The information from the American foreign intelligence agency, acquired by former NSA contractor and whistleblower Edward Snowden, show that the spying is conducted by a branch called “Follow the Money” (FTM). The collected information then flows into the NSA’s own financial databank, called “Tracfin,” which in 2011 contained 180 million records. Some 84 percent of the data is from credit card transactions.
On one hand, what the NSA is doing is exactly what the NSA should be doing: tracing the money flow of terrorist organizations.
Their aim was to gain access to transactions by VISA customers in Europe, the Middle East and Africa, according to one presentation. The goal was to “collect, parse and ingest transactional data for priority credit card associations, focusing on priority geographic regions.”
This is part of the Terrorist Finance Tracking Program, which was set up shortly after the 9/11 attacks and gave the US government access to the SWIFT (Society for Worldwide Interbank Financial Telecommunication) database. This, in and of itself, is not news, having been exposed in 2006. Documents uncovered then showed the program had been in place since 2002, with permission extended to the CIA and the Treasury Dept. as part of Bush’s “Global War on Terror.”
What is new, however, is the fact that the NSA is targeting transactions from major credit card companies, like VISA. This has quite a bit more potential for misuse than SWIFT, which records only banking transactions. VISA responded to this new information with the same quasi-denial we’ve seen from several other companies whose links to the NSA have been exposed.
“We are not aware of any unauthorized access to our network. Visa takes data security seriously and, in response to any attempted intrusion, we would pursue all available remedies to the fullest extent of the law. Further, its Visa’s policy to only provide transaction information in response to a subpoena or other valid legal process.”
Of course, this isn’t “unauthorized” access, not when gathered with a court order or subpoena. But this isn’t as tightly controlled as the spokesperson makes it appear. If pursuing data for “counterterrorism” purposes, the NSA is allowed to skirt the protections of the Right to Financial Privacy Act, thanks to an amendment in the PATRIOT Act. But even with these legal options, it appears the NSA would still rather pursue this in an extralegal fashion in order to circumvent the warrant process.
NSA analysts at an internal conference that year described in detail how they had apparently successfully searched through the US company’s complex transaction network for tapping possibilities.
Whatever’s happening now appears to be the NSA grabbing more data simply because it can. It’s not as if it didn’t already have access copious amounts of financial data, thanks to the government’s fully legal (and fully public) collection of bulk financial records through SWIFT.
Remember: in addition to stealing the data, Treasury also gets it via a now-public agreement. The former CEO of SWIFT Leonard Schrank and former Homeland Security Czar, Juan Zarate actually boasted in July, in response to the earliest Edward Snowden revelations, about how laudable Treasury’s consensual access to the data was.
“The use of the data was legal, limited, targeted, overseen and audited. The program set a gold standard for how to protect the confidential data provided to the government. Treasury legally gained access to large amounts of Swift’s financial-messaging data (which is the banking equivalent of telephone metadata) and eventually explained it to the public at home and abroad.
It could remain a model for how to limit the government’s use of mass amounts of data in a world where access to information is necessary to ensure our security while also protecting privacy and civil liberties.”
Never mind that by the time they wrote this, an EU audit had showed the protections were illusory, in part because the details of actual queries were oral (and therefore the queries weren’t auditable), in part because Treasury was getting bulk data. But there was a legitimate way to get data pertaining to the claimed primary threat at hand, terrorism. And now we know NSA also stole data.
Even when the government has an advantageous agreement to collect bulk data with little oversight, its agencies can’t help but exploit this even further. The collection via “oral queries” is another indicator of these agencies’ (FBI, NSA, CIA) unwillingness to follow even the most minimal of rules. (See also the administration’s 2010 ruling that made the FBI’s warrantless wiretapping legal, which occurred after the agency’s process had slid from issuing tons of National Security Letters to simply calling up the telcos and requesting records.)
The untargeted collection of financial data has raised concerns from those on the “collection” side.
[E]ven intelligence agency employees are somewhat concerned about spying on the world finance system, according to one document from the UK’s intelligence agency GCHQ concerning the legal perspectives on “financial data” and the agency’s own cooperations with the NSA in this area. The collection, storage and sharing of politically sensitive data is a deep invasion of privacy, and involved “bulk data” full of “rich personal information,” much of which “is not about our targets,” the document says.
When even the spies are concerned about about how much data their spy programs are netting, that’s a pretty good sign a bulk records collections effort has gone too far. And it has deeper implications than simply a massive amount of privacy violations. As Marcy Wheeler points out, even the then-Fed chairman Alan Greenspan expressed his concerns about the breadth of the SWIFT collections.
If the world’s financiers were to find out how their sensitive internal data was being used, he acknowledged, it could hurt the stability of the global banking systems.
That’s a scary thought, considering the “global banking system” isn’t all that stable to begin with. A lack of targeting will leave the NSA open to more accusations of economic espionage, something clearly not related to its supposed “national security” agenda.
Related article
NYC Tracking E-ZPass Tags All Over The City, Without Telling Drivers
By Mike Masnick | Techdirt | September 13, 2013
New York, and many states in the northeast and midwest, use an RFID toll-paying solution called E-ZPass (the system works in multiple states — but not all, which is why, for example, you can’t use the E-ZPass on California’s Fastrak system). Ever since E-ZPass came into existence, some have expressed concerns that the tags would be used for tracking, rather than just for more convenient and efficient toll-paying. And, in fact, the toll-paying records have been used in a variety of legal cases, from catching an official who falsified time sheets to being used as evidence in divorce cases. But all of those still involved using the records at the actual tolls, where everyone knows the tags are being read.
However, it turns out that New York City has had an ongoing program to surreptitiously scan the tags in a variety of places supposedly for monitoring traffic. Indeed, you could see how that sort of traffic information might be useful, though these days with many other forms of traffic monitoring systems out there, it’s probably a lot less necessary than before. But this was only discovered because a hacker going by the name Puking Monkey (one assumes this was not his given name) got suspicious and hacked up an E-ZPass to light up and make a sound whenever it was read. Then he drove around Manhattan, and voila, the tag kept going off.
As Kash Hill’s article at Forbes notes, this has been going on for years, though, the various agencies involved have been rather quiet about it, and (perhaps most importantly) this type of usage does not appear to be disclosed in the terms and conditions for the E-ZPass. Oops.
The technology company that makes the devices insists that it’s not being used for any surveillance:
“The tag ID is scrambled to make it anonymous. The scrambled ID is held in dynamic memory for several minutes to compare with other sightings from other readers strategically placed for the purpose of measuring travel times which are then averaged to develop an understanding of traffic conditions,” says TransCore spokesperson Barbara Catlin by email. “Travel times are used to estimate average speeds for general traveler information and performance metrics. Tag sightings (reads) age off the system after several minutes or after they are paired and are not stored because they are of no value. Hence the system cannot identify the tag user and does not keep any record of the tag sightings.”
Of course, even if that is true today, that doesn’t mean it will always be true. We’re already well aware of how the NYPD is known for the extreme lengths it will go in terms of surveillance, including the fact that it’s set up its own intelligence division that many say rivals the intelligence operations of entire nations. Since the folks behind E-ZPass didn’t seem to think it was necessary to tell people that their devices would be used for traffic monitoring, how likely is it that anyone would be told if it was used for surveillance as well?
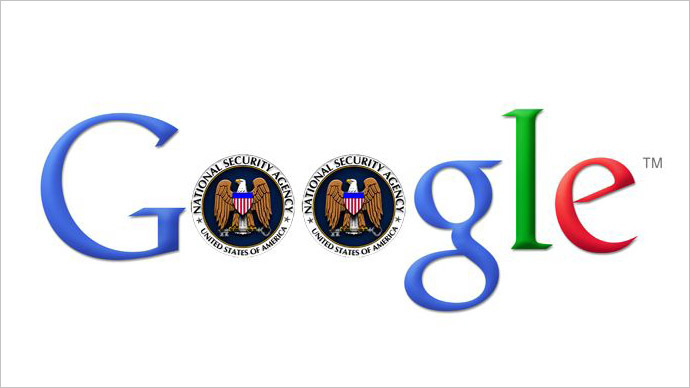
NSA masqueraded as Google to spy on web users – report
RT | September 13, 2013
The NSA used ‘man in the middle’ hack attacks to impersonate Google and fool web users, leaks have revealed. The technique circumvents encryption by redirecting users to a copycat site which relays all the data entered to NSA data banks.
Brazilian television network Globo News released a report based on classified data divulged by former CIA worker Edward Snowden on Sunday. The report itself blew the whistle on US government spying on Brazilian oil giant Petrobras, but hidden in amongst the data was information the NSA had impersonated Google to get its hands on user data.
Globo TV showed slides from a 2012 NSA presentation explaining how the organization intercepts data and re-routes it to NSA central. One of the convert techniques the NSA uses to do this is a ‘man in the middle’ (MITM) hack attack.
This particular method of intercepting internet communications is quite common among expert hackers as it avoids having to break through encryption. Essentially, NSA operatives log into a router used by an internet service provider and divert ‘target traffic’ to a copycat MITM site, whereupon all the data entered is relayed to the NSA. The data released by Edward Snowden and reported on by Globo News suggests the NSA carried out these attacks disguised as Google.
When the news broke about the NSA gathering information through internet browsers, tech giants such as Google and Yahoo denied complicity, maintaining they only handover data if a formal request is issued by the government.
“As for recent reports that the US government has found ways to circumvent our security systems, we have no evidence of any such thing ever occurring. We provide our user data to governments only in accordance with the law,” said Google spokesperson Jay Nancarrow to news site Mother Jones.
Google, along with Microsoft, Facebook and Yahoo, has filed a lawsuit against the Foreign Intelligence Surveillance Court (FISA) to allow them to make public all the data requests made by the NSA.
“Given the important public policy issues at stake, we have also asked the court to hold its hearing in open rather than behind closed doors. It’s time for more transparency,” Google’s director of law enforcement and information security, Richard Salgado, and the director of public policy and government affairs, Pablo Chavez, wrote in a blog post on Monday.
The tech giants implicated in NSA’s global spying program have denied criticism that they could have done more to resist NSA spying. Marissa Mayer, CEO of Yahoo, claimed that speaking out about the NSA’s activities would have amounted to ‘treason’ at a press conference in San Francisco on Wednesday.
In Yahoo’s defense, she argued that the company had been very skeptical of the NSA’s requests to disclose user data and had resisted whenever possible. Mayer concluded that it was more realistic to work within the system,” rather than fight against it.
What Convinced Obama to Reverse His Position on NSA Surveillance?
By Jennifer Hoelzer | September 11, 2013
 Since details of the NSA’s surveillance programs started coming to light in early June – and President Obama’s been forced to publicly answer for its activities – the president has repeatedly reminded us that he came into office with a “healthy skepticism about these programs.” But, after careful evaluation, he determined “that on, you know, net, it was worth doing.”
Some of these programs I had been critical of when I was in the Senate. When I looked through specifically what was being done, my determination was that the two programs in particular that had been at issue, 215 and 702, offered valuable intelligence that helps us protect the American people and they’re worth preserving. (From his August 9th Press Conference.)
It’s a rhetorical strategy intended to win his critics’ trust by demonstrating that he understands our concerns because he used to share them. The message he wants us to take away is: if we had been in his shoes and saw the evidence he saw when he got into office, we would have signed off on these programs too.
Well, yesterday we got a glimpse of some of the evidence he saw when he assumed office – at least in connection to the NSA’s collection of U.S. phone call records — and, it begs the question, what exactly changed his mind about the NSA’s domestic surveillance programs? What did the President see that led him to the conclusion that everything he had previously said on the topic was wrong because allowing the NSA to collect everyone’s phone call records really is a constitutionally-supported, great idea?
Because, according to the documents the ODNI released yesterday, when President Obama took office, the NSA’s “telephony metadata” program wasn’t getting stellar reviews. In fact, we now know that days prior to Obama’s inauguration, the NSA reported that it had repeatedly violated the court-ordered rules limiting its use of the data it was collecting. A little over a month later, a judge on the Foreign Intelligence Surveillance Court found that, “Since January 15 [five days before Obama’s inauguration] it has finally come to light that the FISC’s authorizations of this vast collection program have been premised on a flawed depiction of how the NSA uses” the phone call data.
Not only had the Intelligence Community been misrepresenting its program to the court, the judge, Reggie B. Walton, went on to write:
The minimization procedures proposed by the government in each successive application and approved and adopted as binding by the orders of the FISC have been so frequently and systemically violated that it can fairly be said that this critical element of the overall BR regime has never functioned effectively.
And,
To approve such a program, the Court must have every confidence that the government is doing its utmost to ensure that those responsible for implementation fully comply with the Court’s orders. The Court no longer has such confidence.
The judge also implied that – other than hypothetical examples of how this data might provide intelligence of “immense value to the government” – the government had yet to provide the court with concrete evidence that the program was actually providing that value.
This program has been ongoing for nearly three years. The time has come for the government to describe to the Court how, based on the information collected and analyzed during that time, the value of the program to the nation’s security justifies the continued collection and retention of massive quantities of U.S. person information.
Again, Judge Walton reached these conclusions based on evidence that was available to him at the very same time that I imagine President Obama and his team were evaluating these programs. Plus, I’m assuming the president considered Judge Walton’s opinion in his evaluation, right?
So, what exactly convinced President Obama that this was “worth doing?” Because as the president explained last month, the prospect that something could happen isn’t the same as actual evidence that it has or ever will.
Ex-FBI counsel implicated in surveillance abuses nominated to crucial federal bench
RT | September 11, 2013
The former top lawyer at the FBI deeply implicated in surveillance abuses revealed before and by Edward Snowden’s leaks was confirmed as a federal judge in a top court for terrorism cases this week.
The US Senate voted 73-24 on Monday in approving Valerie Caproni, Federal Bureau of Investigation general counsel from 2003 to 2011, to the Southern District of New York, one of the country’s most important federal courts for terrorism cases.
Caproni has received bipartisan criticism for allowing and defending surveillance abuses both found to be overbroad during her tenure and those not disclosed when she was counsel but later revealed to be inappropriate or illegal. For example, the Snowden leaks showed Caproni mischaracterized the limits of the Patriot Act during her term.
A 2010 report by the Department of Justice revealed the FBI inappropriately used non-judicial subpoenas called “exigent letters” to gather phone numbers of over 5,550 Americans until 2006.
“The FBI broke the law on telephone records privacy and the general counsel’s office, headed by Valerie Caproni, sanctioned it and must face consequences,” said John Conyers in April 2010 as chairman of the House Judiciary Committee.
Conyers called for Caproni’s firing at the time over the use of the non-judicial subpoenas, according to the Guardian.
“It’s not in the Patriot Act. It never has been. And its use, perhaps coincidentally, began in the same month that Ms Valerie Caproni began her work as general counsel,” Conyers said in 2010.
Caproni told House lawmakers in 2008 if phone numbers — acquired from telephone companies by the FBI via the non-judicial subpoenas evidently sanctioned in the Patriot Act — were not related to a “currently open investigation, and there was no emergency at the time we received the records, the records are removed from our files and destroyed.”
Yet revelations found in documents supplied by Snowden outlined how the National Security Agency stores phone records on all Americans for up five years no matter if they are associated with an open investigation or not. In addition, it’s been found that the NSA has the capability to feed the FBI phone records if there is a “reasonable articulable suspicion” they are related to terrorism.
“Caproni knew that the Bush administration could use or was using the Section 215 provision in the Patriot Act to obtain Americans’ phone records on a broad scale, an issue that has recently been documented by the whistleblower material first printed in the Guardian,” Lisa Graves, a former deputy assistant attorney general who dealt with Caproni while working on national security issues for the ACLU, told the Guardian.
In 2007, DOJ’s Inspector General Glenn Fine found the FBI was serially abusing National Security Letters — a demand regarding national security independent of legal subpoenas– to obtain business records, including “unauthorized collection of telephone or internet email transactional records.” While the larger collection of phone records was still not exposed at the time, Caproni called the inappropriate collection a “colossal failure on our part.”
“Government officials that secretly approved of overbroad surveillance programs the public is only seeing now because of leaks, and whose testimony on the issue obscured rather than revealed these abuses, should be held to account for their actions in a public forum,” former FBI agent Mike German told the Guardian.
Caproni’s nomination to the federal bench had some bipartisan opposition, but not enough to block her appointment.
“She is a woman with impeccable credentials,” Sen. Kirsten Gillibrand (D-N.Y.) said on the Senate floor Monday. “This country needs more women like her.”
NSA, no way! Anti-spying sentiments on the rise amid steady stream of disclosures
RT | September 11, 2013
The National Security Agency isn’t making many friends, apparently: a new poll published this week suggests that a majority of Americans continue to have complaints with the NSA’s surveillance practices amid a myriad of recent disclosures.
According to the results of survey released this week by the Associated Press and the NORC Center for Public Affairs Research, anti-NSA sentiment remains rampant in the United States more than three months after former intelligence contractor Edward Snowden first began disclosing top-secret documents exposing the inner-workings of a vast surveillance apparatus operated by America’s premier spy agency. Meanwhile, concerns regarding those practices are growing amid members of Congress and even independent coalitions.
Polling conducted by the AP and NORC last month and released on Tuesday suggest that 56 percent of Americans surveyed oppose the NSA’s collection of telephone records, and 54 percent said they were against the practices that put Internet metadata into the hands of federal investigators.
A confused poll earlier this year in July by the PEW Research Center found that 44 percent of Americans disapproved of the NSA program, with half of the country not opposing the surveillance methods.
Now only 34 percent — or roughly one-third of those polled — say they are okay with the dragnet collection of metadata, or raw information including information on the sender and recipient, time and location pertaining to emails and phone calls. Additionally, 53 percent of Americans polled from a group of 1,008 adults say the federal government is doing a good job of ensuring freedom, a drop in seven percentage points since 2011. That earlier study concluded that 40 percent of Americans thought the government was doing a good job of protecting privacy, and today that number is down to 34 percent.
The AP poll also concluded that an overwhelming 71 percent of those asked opposed US officials eavesdropping on calls without warrant, and 62 percent said they were against the monitoring of email content.
Results from the latest poll were published on Tuesday, one day before the UK’s Guardian newspaper published the latest top-secret document in a series of classified leaks attributed to Snowden since early June. On Wednesday morning, the Guardian published a NSA memo from 2009 in which it’s revealed how US intelligence officials have shared raw data collected from American persons with Israeli counterparts without domestic agents even analyzing that information before it changes hands.
Commenting to the AP, Trevor Timm of the Electronic Frontier Foundation suggested the recent NSA disclosures undoubtedly have influenced the public’s perception of the US intelligence community and the way it conducts itself.
“For the first time, the public is able to see what’s going on behind closed doors and it’s changing minds,” Timm told the AP.
The EFF, along with the American Civil Liberties Union and more than two dozen other entities, are named as plaintiffs in a collection of lawsuits challenging the Obama administration’s surveillance programs. Attorneys for the EFF are representing plaintiffs in the matter of First Unitarian Church of Los Angeles v. NSA, which grew in size this week when five new organizations signed on to sue the White House. The EFF announced on Tuesday this week that Acorn Active Media, the Charity and Security Network, the National Lawyers Guild, Patient Privacy Rights and The Shalom Center have all signed on to the suit, which attorneys say challenges the government’s surveillance alleged abuse of Section 215 of the Patriot Act to collect bulk telephone metadata — an activity first disclosed on June 5 after Snowden leaked documents to the Guardian and Washington Post.
“The First Amendment guarantees the freedom to associate and express political views as a group,” EFF legal director Cindy Cohn said in a statement. “The NSA undermines that right when it collects, without any particular target, the phone records of innocent Americans and the organizations in which they participate. In order to advocate effectively, these organizations must have the ability to protect the privacy of their employees and members.”
Also signing on in support of NSA reform is US Rep. Darrell Issa (R-California), who only this week announced he’d be seeking changes in the way America conducts surveillance operations. Issa previously voted against a measure proposed by colleague Rep. Justin Amash (R-Michigan) which would have aimed to thwart the NSA’s now-infamous practices, but this week wrote a letter to Congress saying lawmakers on Capitol Hill should debate those policies once again as leaks continue to raise concerns.
“Now that it has been publicly acknowledged that the communications of Americans were included in the NSA’s data collection program, likely violating their Fourth Amendment rights, Congress must respond in a manner that both increases the transparency of the agency’s programs and reinforces the constitutional protections of our citizens,” Issa wrote in a letter first published by Politico.
“We’re very pleased that Chairman Issa supports our amendment,” Amash spokesman Will Adams told US News & World Report. “If the Amash amendment does get taken up by the House and it does pass this fall, it will put pressure on the committees to start passing comprehensive reforms.”
The Amash Amendment would have barred the NSA from using the PATRIOT Act provision at the center of First Unitarian Church of Los Angeles v. NSA to collect the phone records of all Americans. It was defeated in the House last month by a 12 vote margin.
Related articles
Another Reason The NSA Needs To Go: It’s Been Doing What It Explicitly Was Told Not To Do
By Mike Masnick | Techdirt | September 10, 2013
One of the key things that people quickly realized after last week’s revelation about the NSA putting backdoors into encryption, was that this was exactly what the federal government had tried to do with the Clipper Chip back in the 90s, and after a public debate, it was rejected. The battle over the Clipper Chip was one of the key legal/tech battles of the 1990s.
And then the NSA went and did it anyway.
Jack Shafer, over at Reuters, points out that there’s this pattern of the NSA not taking no for an answer, discussing the attempts to stop PGP and also the infamous Total Information Awareness program:
Zimmerman and his allies eventually won the PGP showdown, as did privacy advocates in the mid-1990s, defeating the government’s proposal for the “Clipper chip,” which would allow easy surveillance of telephone and computer systems, and again after 9/11, when Congress cut funding for the Defense Department office in charge of the Total Information Awareness (TIA) program, a massive surveillance database containing oceans of vital information about everybody in the United States.
But the journalistic record proves we can’t trust government’s white flag of surrender. In the case of TIA, the government abandoned the program’s name but preserved the operation, as Shane Harris and others reported seven years ago, giving it new code names and concealing it in places like the NSA. The documents Snowden stole from the NSA show the government capturing and analyzing much of what TIA sought in the first place.
Basically, this suggests that even if the NSA is told to stop doing the various things it’s doing, it’s only a matter of time until they do them anyway. One response to this — which many are taking seriously — is to look into re-architecting the internet to see what can be built, ground-up with security in mind, specifically making sure that the NSA can’t weasel its way in.
But there’s a separate issue as well. How do we stop basic government overreach after it’s been made clear that they don’t have a mandate to do what they’re doing? Yes, government officials and NSA defenders like to pretend that they did have a mandate here, and will point to the FISA Court or other aspects to argue that it’s perfectly fine — but when they’re explicitly doing exactly what they were denied a decade or more ago, those arguments ring hollow. But, if they’re allowed to get away with it, without any response, then they’ll never stop. No matter what they’re told not to do, they’ll just keep doing anyway, because what’s the worst that happens? People complain about it?
So it seems that there needs to be a very different system in place — on that involves real oversight, not the pathetic joke that is the Intelligence Committees of both houses of Congress and the FISA Court. And, frankly, it should be over a new organization. It seems clear at this point that you can’t reform the NSA. It’s rotten to its core. Yes, signals intelligence and other intelligence activities can be important and necessary, but it really seems like we need to breakup the NSA, and restructure the whole thing such that it can be built in a manner where there’s actual oversight, rather than having it do whatever it wants and pretending everything is fine any time anyone accuses them of anything.
The Most Awkward G20 Summit Ever
By Dan Beeton | CEPR Americas Blog | September 5, 2013
President Obama is in St. Petersburg, Russia to participate in the G20 Summit today and tomorrow, amidst a time of heightened tensions between the U.S. and several G20 member nations. Looming over the summit are the Obama administration’s plans for a possible military attack on Syria, while Russian President Vladimir Putin has said that a U.S. military response without U.N. Security Council approval “can only be interpreted as an aggression” and UNASUR – which includes G20 members Argentina and Brazil, issued a statement that “condemns external interventions that are inconsistent with the Charter of the United Nations.”
New revelations of NSA spying on other G20 member nation presidents – Dilma Rousseff of Brazil and Enrique Peña Nieto of Mexico – leaked by NSA whistle-blower Edward Snowden and first reported in Brazil’s O Globo, have also created new frictions. Rousseff is reportedly considering canceling a state visit to Washington next month over the espionage and the Obama administration’s response to the revelations, and reportedly has canceled a scheduled trip to D.C. next week by an advance team that was to have done preparations for her visit. The Brazilian government has demanded an apology from the Obama administration. In an interview with Reuters on Wednesday, an anonymous senior Brazilian official underscored the gravity of the situation:
[T]he official, who declined to be identified due to the sensitivity of the episode, said Rousseff feels “patronized” by the U.S. response so far to the Globo report. She is prepared to cancel the visit as well as take punitive action, including ruling out the purchase of F-18 Super Hornet fighters from Chicago-based Boeing Co, the official said.
“She is completely furious,” the official said.
“This is a major, major crisis …. There needs to be an apology. It needs to be public. Without that, it’s basically impossible for her to go to Washington in October,” the official said.
Other media reports suggest that Brazil may implement measures to channel its Internet communications through non-U.S. companies. But when asked in a press briefing aboard Air Force One this morning, Deputy National Security Advisor for Strategic Communications Ben Rhodes did not suggest that such an apology would be forthcoming:
Q The Foreign Minister said he wanted an apology.
MR. RHODES: Well, I think — what we’re focused on is making sure the Brazilians understand exactly what the nature of our intelligence effort is. We carry out intelligence like just about every other country around the world. If there are concerns that we can address consistent with our national security requirements, we will aim to do so through our bilateral relationship.
Such responses are not likely to go far toward patching things up with Brazil. It is conspicuously dishonest to suggest that the U.S. government “carr[ies] out intelligence like just about every other country around the world,” as no other country is known to have the capacity for the level of global spying that the NSA and other agencies conduct, and few countries are likely to have the intelligence budgets enjoyed by U.S. agencies – currently totaling some $75.6 billion, according to documents leaked by Snowden and reported by the Washington Post.
There are also signs that the Washington foreign policy establishment is troubled by the Obama administration’s dismissive attitude toward Brazil’s understandable outrage. On Tuesday, McClatchy cited Peter Hakim of the Inter-American Dialogue – essentially the voice of the Latin America policy establishment in Washington:
Peter Hakim, the president emeritus of the Inter-American Dialogue, a Washington-based policy group, noted that Secretary of State John Kerry had visited Brasilia last month to patch things up after the initial NSA leaks but “really did not do a very good job. He just brushed it off.”
Hakim said he believed the O Globo report, and he added that “snooping at presidents is disrespectful and offensive.”
Rousseff and Pena Nieto had to issue strong statements, Hakim said. “Both have to show they are not pushovers, that they can stand up to the U.S.,” he said.
The ongoing revelations made by Snowden have affected U.S. relations with other countries as well. As the Pan-American Post points out, Peña Nieto may continue to reduce intelligence sharing with the U.S.; he also said yesterday that “he may discuss the issue with President Barack Obama at the summit.” U.S.-Russian relations, of course, have also recently become tense following Russia’s granting of temporary political asylum to Snowden.
The G20 Summit also comes just after the IMF, at the direction of the U.S. Treasury Department, changed its plan to support the Argentine government in its legal battle with “vulture funds” – meaning that U.S.-Argentine relations may also be relatively cool.
Related article
Featured Video
or go to
Aletho News Archives – Video-Images
Book Review
The Maidan Killings and the False-Flag Case
By Freddie Ponton | 21st Century Wire | September 5, 2026
Before the killings that helped bring down Ukraine’s president in February 2014, American diplomats were discussing who should enter its government. In a leaked telephone call, senior State Department official Victoria Nuland told US ambassador Geoffrey Pyatt, “I think Yats is the guy,” referring to opposition leader Arseniy Yatseniuk. Washington had clear preferences and was working to advance them. Later that month, Yatseniuk became prime minister.
Ivan Katchanovski’s The Maidan Massacre in Ukraine examines the violence that preceded that transfer of power. Drawing on television footage, witness testimony, forensic examinations and Ukrainian court proceedings, he argues that elements of the opposition shot protesters and police in a false-flag operation. His case centres on evidence of protesters being shot from opposition-controlled locations, including Hotel Ukraina, overlooking the killing ground. … continue
Blog Roll
 Aletho News
- In August Hanning Treason Case- All Signs Point To Tel Aviv.
- France cleared dozens of military sales to Israel between May and September: Report
- France projects nuclear power as Macron pushes arsenal expansion
- The fallacy of US delusions about Iran’s economic collapse
- What changes with Lula or Flávio?
- Britain leads Western media’s demise through ‘fear porn’ narrative
- The Maidan Killings and the False-Flag Case
- Georgia’s Largest Healthcare System Will Fire Employees Who Refuse Flu Vaccine
- The Five-Year Fuel Crisis: Why the World Economy Is Paying for a War It Thinks Is Ending
- Trump’s Big Bluff on Iran
- If Americans Knew
- CIA Report Warns Israel Could Head Toward Civil War, Total Collapse
- Banker Who Exposed Howard Lutnick’s Ties to Epstein Warned of ‘Retaliation’ and ‘Personal Consequences’ in Last Post Before Suicide
- Israeli Attacks Kill Two Palestinians in Gaza
- Gaza genocide at 3: Israeli-U.S. cruelty and the smart, deep resistance to it are changing the world
- As genocide is about to enter 3rd year, little of Gaza remains– Daily Update
- “We See Our Homes Now From A Satellite, Like Strangers”
- Watch “Gaza: Doctors Under Attack”, originally censored by BBC
- NAZA: Israeli embassies in UK and US promote rival documentary to challenge Gaza genocide allegations
- David Ellison appoints Israeli to lead merged Paramount-Warner studios
- Turkish Red Crescent helps elderly Gaza man walk again after Israel confiscates his prosthetic limb
- No Tricks Zone
- Latest European Green Energy Debacle; Portugal’s Largest Flagship Solar Park Insolvent!
- Green Energy Debacle: German Expert Professor Fritz Vahrenholt Warns Of Severe Economic And Social Consequences
- Two More Paleo Reconstructions Affirm Meters-Higher Sea Levels Across Ireland, Brazil 7000-6000 Years Ago
- New Study: Earth And Venus Surface Warmth Largely Explained By Convection And Lapse Rate, Not CO2 Or Radiation
- 2025 Nature Paper Claiming Worsening Global Drought Gets RETRACTED …Heavily Flawed
- New Study: ‘Global Drought Shows No Detectable Recent Acceleration Under Climate Warming’
- Economic Masterminds: German Socialists Suggest Taxing Productivity Gains Stemming From Using AI
- The South China Sea Has Not Been Cooperating With The Climate Change Narrative
- Energy Crisis: Germany Enters Heating Season With Historically Low Gas Reserve Fill Levels
- New Study: The Antarctic Ice Sheet Gained Mass From 2020-2024 Due To Staggering Snow And Ice Accumulation

