Palestinians schools must adopt Israeli narrative of the conflict
MEMO | January 7, 2014
Israel is to tell the Palestinian Authority to change the history syllabus used in its schools as a condition ahead of negotiating final status issues. According to a specialist in Israeli studies, Saleh Al-Na’ami, Israel’s defence minister has said that Palestinian schools must teach the Israeli narrative of events before and since 1948, when what Palestinians call the Nakba (Catastrophe) of the creation of the state of Israel took place.
“They [the PA] need to cancel the Palestinian narrative of the history of the Palestinian-Israeli conflict,” Moshe Ya’alon is alleged to have said.
Haaretz reported that the weekly ministerial meeting on Sunday included a discussion about such a change in the Palestinian school syllabus. Ya’alon is also reported to be insisting on an end to Palestinians using speeches in mosques to “incite” the population against the Israeli occupation.
Related article

Court Decision Exempts Secret Memo From FOIA, Sets Stage For Future Secret Laws To Go Unchallenged
By Tim Cushing | Techdirt | January 6, 2014
The “most transparent administration” received another win for continued secrecy, thanks to an appeals court decision that allowed it to continue to withhold a DOJ memo that created an exploitable loophole in consumer data privacy protections.
The document at issue is a classified memo issued by the Office of Legal Counsel on Jan. 8, 2010. A report later that year by the Justice Department’s inspector general at the time, Glenn A. Fine, disclosed the memo’s existence and its broad conclusion that telephone companies may voluntarily provide records to the government “without legal process or a qualifying emergency,” notwithstanding the Electronic Communications Privacy Act.
The EFF has been engaged with the government over the release of this document since 2011, when a district court judge ruled the document was exempt from FOIA requests because it was part of executive branch “internal deliberations.” In other words, despite the fact that the OLC memos can be considered legally binding (and exempt those following the memos’ advice or instructions from legal repercussions), the memo is not considered “working law.” The EFF has argued that these memos are not “deliberative,” but are rather secret laws deployed in such a fashion as to avoid being exposed by FOIA requests.
The presiding judge explained his decision with this reasoning.
“Even if the O.L.C. opinion describes the legal parameters of what the F.B.I. is permitted to do, it does not state or determine the F.B.I.’s policy,” Judge Harry T. Edwards wrote in the decision on Friday. “The F.B.I. was free to decline to adopt the investigative tactics deemed legally permissible in the O.L.C. opinion.”
According to the FBI, it did decline to follow the memo’s parameters.
The bureau, which has abandoned exigent letters, said that it did not employ the legal theory outlined in the memo when using the letters, and that it had no plans to use it in the future.
But the DOJ’s arguments for keeping the memo secret calls the FBI’s assertion into question.
During the litigation, the Justice Department also told the court that parts of the memo contained classified information, “highly specific in nature and known to very few individuals,” about a secret intelligence-gathering technique that the F.B.I. is using against “hostile entities.”
Either the FBI is utilizing the memo’s legal theories or the memo covers so much ground that the FBI is using something entirely unrelated, making the first statement truthful as far as it extends to exigent letters only.
Judge Edwards’ rationale gives the government every reason to utilize the Office of Legal Counsel to provide it with the legal justification it needs to deploy questionable tactics and programs. (Previous OLC memos were used to justify warrantless wiretaps and “brutal questioning of detainees.”) The ruling makes it easier for any OLC memo to be exempted from FOIA requests, providing for even more government secrecy.
David Sobel, a lawyer for the EFF, called the ruling “troubling,” describing the office’s memos as a body of “secret law” that the public has a right to know about. He said he hoped the ruling would reinvigorate efforts among some lawmakers to enact a law opening such memos to greater scrutiny outside the executive branch.
“It’s kind of hard to imagine how a different case in the D.C. Circuit is likely to have a different outcome in light of this opinion,” he said.
Because the document remains a secret, its true significance remains a source of speculation. The New York Times says the memo is most likely the legal basis for the CIA’s voluntary agreement with AT&T, which allows the agency to search its massive database of international calls (and tip local numbers to the FBI for further investigation). And it’s not as if this secret memo is the only tool the government has for demanding data. The FBI may have abandoned “exigent letters” but it’s still using National Security Letters to obtain data without a court order. (No mention is made of the FBI’s exigent Post-It notes or over-the-shoulder database searches.)
The DOJ is understandably pleased with this decision as it plays to its obfuscatory tendencies. This is also a dubious win for this administration — and those that follow. Having an in-house agency on tap that can create new laws and interpretations of existing statutes without having to risk having its legally-binding memos scrutinized by the public will be a tool too powerful for many to ignore.
Related articles


NSA More Or Less Admits To Spying On Congress
By Mike Masnick | Techdirt | January 6, 2014
On Friday, we noted that Senator Bernie Sanders had asked the NSA if it spied on members of Congress. He was very explicit in how he defined “spying” such that the NSA couldn’t legitimately deny it — since the definition included collecting metadata on their calls — something the NSA absolutely does. In response to press requests, it appears that the NSA has issued a statement to a variety of publications, basically admitting that of course it spies on Congress, because it collects everyone’s data.
NSA’s authorities to collect signals intelligence data include procedures that protect the privacy of US persons. Such protections are built into and cut across the entire process. Members of Congress have the same privacy protections as all US persons. NSA is fully committed to transparency with Congress. Our interaction with Congress has been extensive both before and since the media disclosures began last June.
We are reviewing Senator Sanders’s letter now, and we will continue to work to ensure that all members of Congress, including Senator Sanders, have information about NSA’s mission, authorities, and programs to fully inform the discharge of their duties.
The key line: “Members of Congress have the same privacy protections as all US persons.” Meaning, basically, that they have no privacy protections when it comes to the NSA collecting data.
France-UAE satellite deal shaky after US spy tech discovered onboard – report
RT | January 6, 2014
The sale of two intelligence satellites to the UAE by France for nearly a billion dollars could go south after they were found to contain American technology designed to intercept data transmitted to the ground station.
The equipment, costing 3.4 billion dirhams ($930 million), constitutes two high-resolution Pleiades-type Falcon Eye military intelligence satellites, which a top UAE defense source has said contain specific US-made components designed to intercept the satellites’ communications with their accompanying ground station, Defensenews.com said in a report.
“The discovery [of the US-made components] was reported to the deputy supreme commander [Sheikh Mohamm ed Bin Zayed] in September,” an unnamed defense source said. “We have requested the French to change these components and also consulted with the Russian and Chinese firms.”
“If this issue is not resolved, the UAE is willing to scrap the whole deal,” said the source, adding that the incident has seen an increase in talks with Moscow, which – along with Beijing – has also been a frequent defense tech supplier to the Gulf state.
However, it is not clear whether the US equipment can be taken off of the French satellites.
The satellites come courtesy of prime contractor Airbus Defence and Space and payload manufacturer Thales Alenia, neither of whom could be reached for comment.
The system, comprised of satellites and a ground station, will require 20 trained engineers to operate. Under the July 22 deal, signed by Sheikh Mohammed, Crown Prince of Dubai and deputy supreme commander of the armed forces, and French Defense Minister Jean-Yves Le Drian, delivery of the satellites and the ground station was to be made sometime in 2018.
A total of 11 international bidders were competing in the Flacon Eye race for more than a decade to ship their technologies to the UAE, which in late 2012 announced that they had chosen to go with the French and the Americans.
According to the source, the French won because of the filters which their rival Americans imposed on the use of the equipment – a policy dubbed “shutter control.” The US government restricts sale of commercial high resolution satellite images from spacecraft it licenses, if they are deemed a threat to its national security.
One French defense specialist found it surprising that France had had US spy technology on board its equipment, especially when France’s use of the Pleiades surveillance system is considered to be of critical importance to its national security.
According to Defensenews, UAE threats to call off the deal are seen by some commentators as a way to secure a better bargain from the French, because “the satellites would be part of a big package deal… it’s not surprising the UAE drives a hard bargain. They’re using it as a layer of power.”
The unnamed defense specialist referred to the possibility that the Emirates may wish to drive the price down for other equipment, such as the Dessault Aviation Rafale fighter jet.
When Your Phone Is Not Your Friend
By Peter Lee | China Matters | January 2, 2014
Gadzooks! They’ve cracked the iPhone!?
Newly leaked documents from the National Security Agency highlight Dropout Jeep, a piece of software that could target one of the country’s most popular devices — the iPhone.
According to documents published by the German news website Spiegel Online and dated Oct. 1, 2008, Dropout Jeep would give the NSA the ability to retrieve contact information, read through text messages, listen to voicemails and even turn on the iPhone camera and microphone.
The document goes on to say that while Drop Jeep was currently limited to installation through “close access methods,” the NSA would research ways to install the program remotely in future versions.
If you’re wondering how the NSA developed this fiendish capability, fingers are being pointed at Apple, but a trip through the Wayback machine suggests another possible culprit:
From a 2011 article by Mark Elgan at Computerworld:
Cellphone users say they want more privacy, and app makers are listening.
No, they’re not listening to user requests. They’re literally listening to the sounds in your office, kitchen, living room and bedroom.
A new class of smartphone app has emerged that uses the microphone built into your phone as a covert listening device — a “bug,” in common parlance.
…
The issue was brought to the world’s attention recently on a podcast called This Week in Tech. Host Leo Laporte and his panel shocked listeners by unmasking three popular apps that activate your phone’s microphone to collect sound patterns from inside your home, meeting, office or wherever you are.
…
The new apps are often sneakier about it [than older apps, which were activated by users in order to identify a song that was playing, etc.–CH]. The vast majority of people who use the Color app, for example, have no idea that their microphones are being activated to gather sounds.Welcome to the future.
…
[M]arketers love cellphones, which are viewed as universal sensors for conducting highly granular, real-time market research.Of course, lots of apps transmit all kinds of private data back to the app maker. Some send back each phone’s Unique Device Identification (UDI), the number assigned to each mobile phone, which can be used to positively identify it. Other apps tell the servers the phone’s location. Many apps actually snoop around on your phone, gathering up personal information, such as gender, age and ZIP code, and zapping it back to the company over your phone’s data connection.
Methinks it would behoove consumers wondering how the NSA might get into their iPhones to hie themselves to their local App Store.
A little further back in the Wayback machine brings us to the analog era, my favorite, when all that was needed to turn your home phone into a microphone was some fiddling at the telco switch. From Bloomberg in 1999:
It’s hardly a secret that phone taps are a favorite ploy of industrial spies as well as law-enforcement agencies. What isn’t well-known is that the phone doesn’t even have to be off the hook to be tapped. It’s possible to activate a hung-up phone remotely and use it to eavesdrop. This techno-trick recently came to light as a result of a drug dealer’s court case in the Netherlands–but it is said that the technique will work on virtually any phone anywhere.
I remember reading somewhere that this was a much-cherished technology for various British intelligence outfits working through British Telecom and its previous incarnation, Post Office Telecommunications.
And from Mark Bowden’s book on the US-assisted manhunt for Pablo Escobar in the early 1990s, Killing Pablo, here is a nugget from the analog cell phone era which, I expect, still applies today:
There was another nifty secret feature to Centra Spike’s capability [a US Army sigint outfit that, unlike the NSA, was tasked with providing tactical intelligence to special operations–CH]. So long as their target left the battery in his cell phone, Centra Spike could remotely turn it on whenever they wished. Without triggering the phone’s lights or beeper, the phone could be activated so that it emitted a low-intensity signal, enough for the unit to get a fix on its general location…
With this background, the extravagant cybercaution of Brookings China wonk Kenneth Lieberthal is understandable:
When Kenneth G. Lieberthal, a China expert at the Brookings Institution, travels to that country, he follows a routine that seems straight from a spy film.
He leaves his cellphone and laptop at home and instead brings “loaner” devices, which he erases before he leaves the United States and wipes clean the minute he returns. In China, he disables Bluetooth and Wi-Fi, never lets his phone out of his sight and, in meetings, not only turns off his phone but also removes the battery, for fear his microphone could be turned on remotely. He connects to the Internet only through an encrypted, password-protected channel, and copies and pastes his password from a USB thumb drive. He never types in a password directly, because, he said, “the Chinese are very good at installing key-logging software on your laptop.”
I have a feeling that Mr. Lieberthal’s countermeasures are informed both by awareness of PRC perfidy, and knowledge of the immense penetration and surveillance capabilities the industrial-security partnership has brought to the telecom and networking game around the world.
If you’re in China–or anywhere else–that phone in your pocket: it’s not your friend.
Court Says Border Searches Of Your Computer Are Okay Because You Shouldn’t Keep Important Info On Your Computer
By Mike Masnick | Techdirt | December 31, 2013
This one is hardly a surprise, given how many (though not all) courts have ruled concerning searches of computing devices at the border. The government’s general theory is that there is no 4th Amendment right at the border, and thus customs officials can search anything. The argument that they’re trying to prevent “bad stuff” from getting into the country really doesn’t make much sense though. If bad stuff is “on a computer” it could easily be sent digitally across the border with no intervention from a customs official. Furthermore, making border searches of laptops and phones even more troubling is the nature of how information is stored. When we pack for a trip we deliberately choose what to include in our suitcase — so we know what’s coming with us. However, on our electronic devices, we pretty much store absolutely everything. Arguing that these are subject to a full search seems problematic — but many courts have found otherwise.
And, now there’s another one. A judge in NY has dismissed a challenge to the searches brought by the ACLU. The judge, Edward Korman, repeatedly quotes former head of Homeland Security, Michael Chertoff, who now makes money by hyping up the threats the country faces, so it’s not like he’s the most unbiased of folks to be relying on for how important these border searches really are. Judge Korman claims that the defendants have no standing to bring the case in the first place. There is one individual (a PhD. student) who actually had his computer searched, and then some professional organizations who worried about their members having their computers searched. The judge is simply not impressed by their arguments… at all. He notes that Customs and Border Patrol appears to search so few laptops that it’s highly unlikely that any individual will have theirs searched — and thus these groups can’t really allege a likely harm. He points out that it’s wrong to use a declaratory judgment case to address “a claim of alleged injury based on speculation as to conduct which may or may not occur at some unspecified future date.”
As for the one guy, Pascal Abidor, who did have his laptop searched, Judge Korman is also not impressed, noting that he’s not suing over that particular search, but the possibility of future searches. The judge seems a bit perplexed by this decision, but notes that it takes away his ability to get standing:
Abidor could have established standing in this case by adding a cause of action for damages based on his claim that he was subject to an unreasonable search. Such a cause of action would have provided the occasion for a trial or a motion for summary judgment that would have fully developed the record with respect to both the initial quick look search and subsequent forensic search. No such action is alleged.
But, as Judge Korman notes, if he can’t show any real likelihood of future harm, he can’t show standing.
Even after dismissing for lack of standing, the judge decides to take on the issue anyway, and this is where he starts to get really insulting to anyone who thinks that perhaps they should have some privacy rights at the border. He openly mocks the plaintiffs for arguing for the need for a “reasonable suspicion” standard for searches, noting that this bar is so low that it’s not like they’d get much more privacy out if it anyway:
Plaintiffs must be drinking the Kool-Aid if they think that a reasonable suspicion threshold of this kind will enable them to “guarantee” confidentiality to their sources.
He goes on to suggest that since traveling internationally involves going into other countries, these same people would probably have even less privacy over their data, since other countries may be even more willing to search their computers. He even cites the situation of David Miranda having his electronics searched in the UK.
Surely, Pascal Abidor cannot be so naive to expect that when he crosses the Syrian or Lebanese border that the contents of his computer will be immune from searches and seizures at the whim of those who work for Bassar al-Assad or Hassan Nasrallah. Indeed, the New York Times recently reported on the saga of David Michael Miranda who was detained for nine hours by British authorities “while on a stop in London’s Heathrow airport during a trip from Germany to Brazil.”
While the judge’s point is correct that other countries are unlikely to protect the privacy of travelers as well, and that means that any information on a laptop may be inherently unsafe, it seems like a bit of a weak copout to argue that since other countries have no respect for your electronic privacy, that the US shouldn’t either.
He goes even further, arguing that because there’s a “special need” at the border to stop bad people, that it’s perfectly fine to ignore things like probable cause or reasonable suspicion — again quoting Michael Chertoff to suggest that border laptop searches have stopped “bad people” from entering the US.
But then he argues that since everyone knows they may be searched at the border, there isn’t really an invasion of privacy:
The invasion of privacy occasioned by such a border search, however, like the search of luggage, briefcases, and even clothing worn by a person entering the United States, is mitigated by other factors….. As Professor LaFave observes, because “the individual crossing a border is on notice that certain types of searchers are likely to be made, his privacy is less invaded by those searches.” …. Thus, “[t]he individual traveler determines the time and place of the search by his own actions, and he thus has ample opportunity to diminish the impact of that search by limiting the nature and character of the effects which he brings with him.”… Indeed, because of the large number of laptop computers (close to a million per year) that are lost by travelers–numbers that far exceed the comparative handful of laptops that are searched at the border–the sensible advice to all travelers is to “[t]hink twice about the information you carry on your laptop,” and to ask themselves: “Is it really necessary to have so much information accessible to you on your computer.”
This seems problematic on multiple levels. First, if we go by the idea that there’s less of a privacy violation because you know it’s coming, then that gives the government the right to ignore the 4th Amendment so long as it tells you ahead of time that it’s going to ignore the 4th Amendment. Even the Supreme Court in Smith v. Maryland — the infamous case concerning the 3rd party doctrine — states that such a scenario is ridiculous, and that just because you know that you’re going to be searched, it doesn’t automatically make the search reasonable.
As for the suggestion that you shouldn’t store stuff on your computers, I’m sure that’s great in theory, but I’d like judges to make decisions based in reality. This suggestion is basically “don’t use your computer for what it’s designed for, because we might search it.” That’s not exactly compelling.
Again, given past precedents, and the specific facts of this case, it’s not entirely surprising. That doesn’t mean it’s not disappointing to see yet another middle finger given to the 4th Amendment to close out the year.
Related articles
- Lawsuit Challenging Laptop Searches at US Border Is Dismissed by Federal Judge (dissenter.firedoglake.com)
- RT: Constitution ‘exemption’ zone spans 100 miles inland of US border – judg (jhaines6.wordpress.com)
NSA Unit Intercepts Computer Shipments for Secret Access Modifications
By Noel Brinkerhoff | AllGov | January 1, 2014
Sophisticated as it is with myriad forms of electronic spying at its disposal, the National Security Agency (NSA) sometimes resorts to old-fashioned, hands-on methods of breaking into someone’s computer system.
In rare instances when the agency can’t hack its way into a network, the NSA employs a special group of “plumbers” to gain access.
These specialists intercept computer shipments ordered by a targeted person and reroute the boxes to secret workshops. There, the packages are opened, and either software or hardware are implanted into the equipment to allow the NSA full access to the system once it’s operational by the target. The packages are then carefully resealed and sent on their way to the unsuspecting customers.
This type of old-school procedure, referred to by NSA as “interdiction,” is considered by the agency to be one of its “most productive operations,” a method that gives the NSA access to computer networks “around the world.”
These interceptions are just one of the many sneaky tasks performed by the NSA’s Office of Tailored Access Operations (TAO), which is also skilled at electronic snooping.
According to NSA documents obtained by the German newspaper Der Spiegel, TAO handles jobs involving counterterrorism, cyber attacks and traditional espionage.
Matthew Aid, a historian who specializes in NSA history, told Spiegel that TAO is “akin to the wunderkind of the US intelligence community,” adding that within the NSA, the unit is known for “getting the ungettable.”
TAO’s work has extended around the globe, reaching more than 250 targets in nearly 90 countries. It has been projected that about 85,000 computers worldwide were infiltrated by NSA specialists as of the end of 2013. Most of the “implants” were accomplished via the Internet by TAO teams.
“Indeed, TAO specialists have directly accessed the protected networks of democratically elected leaders of countries,” Spiegel wrote. “They infiltrated networks of European telecommunications companies and gained access to and read mails sent over Blackberry’s BES email servers, which until then were believed to be securely encrypted.”
The unit’s successes have given the NSA reason to expand its size and locations since first establishing TAO in 1997.
TAO offices now operate out of Wahiawa, Hawaii; Fort Gordon, Georgia; Buckley Air Force Base near Denver, Colorado; Lackland Air Force Base in San Antonio, Texas; and Fort Meade, Maryland (NSA headquarters).
The San Antonio unit alone is expected to grow from 60 to 270 specialists by 2015.
To Learn More:
Inside TAO: Documents Reveal Top NSA Hacking Unit (Der Spiegel)
Shopping for Spy Gear: Catalog Advertises NSA Toolbox (by Jacob Appelbaum, Judith Horchert and Christian Stöcker, Der Spiegel)
Computer Security Firm Accepted $10 Million Payoff to Give NSA Backdoor Access (by Noel Brinkerhoff, AllGov)
NSA’s Personal Propagandist For CBS Officially Takes Counterterrorism Job Everyone Knew He Was Getting
By Mike Masnick | Techdirt | December 30, 2013
When 60 Minutes did its hack PR job for the NSA a few weeks ago, lots of people called out the fact that the reporter who handled the segment, John Miller, wasn’t just a former intelligence official working for the Office of the Director of National Intelligence (which oversees the NSA), but that he was widely rumored to have worked out a deal for a new job for the NYPD, heading up “counterterrorism.” Even though there were multiple reports at the time, including one that claimed it was a “99.44% done deal,” when asked about it, Miller lied. He told a reporter, “you know as much about this as I do.”
That was clearly Miller lying — something that Miller has had an issue with in the past — as the “rumor” is now confirmed and Miller has accepted his job doing “counterterrorism” for the NYPD. And while some might say that doing counterterrorism for a city police force is different than working for national intelligence, that’s only because you’re not familiar with the NYPD, which has set up something of a shadow NSA/CIA to do all sorts of activities not normally associated with a police force.
And, of course, since the press was clearly familiar with Miller’s expected role, it raises serious questions about why 60 Minutes allowed the puff piece to move forward with a seriously conflicted “journalist.” While Miller has lashed out at critics, rather than respond to a single point raised, the brand that comes out worst in all this is clearly CBS and 60 Minutes — which basically let an intelligence official do an entire propaganda piece on the NSA. 60 Minutes used to be about hard hitting journalism. Now, apparently, they think it’s “journalism” to shill for the surveillance state.
Israeli forces shoot photographer in Bilin demonstrations
Ma’an – 29/12/2013
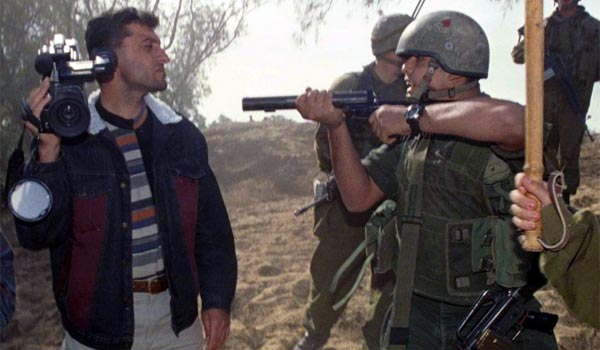
RAMALLAH – A photographer was injured and dozens suffered from excessive tear gas inhalation as Israeli forces dispersed a demonstration in Bilin near Ramallah.
Israeli forces fired rubber-coated steel bullets, tear gas and stun grenades at demonstrators as they neared their lands close to the wall.
Photographer Mohammad Yassin, 20, was hit with a rubber coated steel bullet during the protests.
The demonstration was held in celebration of Christmas and the release of Samer Issawi, and in protest of Israeli settlement activity and the separation wall.
Participants, some of whom wore Santa Claus costumes, raised Palestinian flags and chanted songs for unity and resistance.
Since 2005, Bilin villagers have protested on a weekly basis against the Israeli separation wall that runs through their village on land confiscated from local farmers.
Previous protests by Bilin activists have forced the Israeli authorities to re-route the wall, but large chunks of the village lands remain inaccessible to residents because of the route.
Related article
NSA collects data from undersea cables

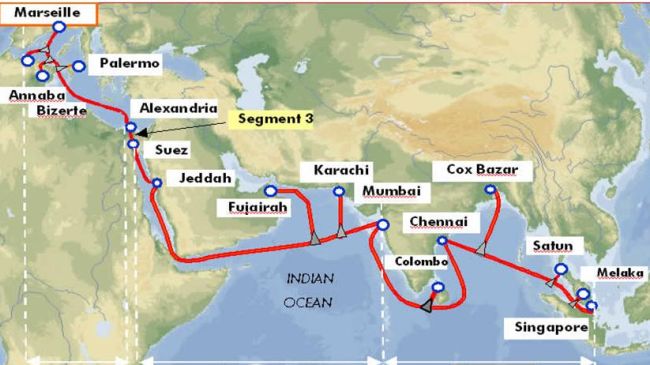
South East Asia–Middle East–Western Europe 4 (SEA-ME-WE 4) optical fiber submarine communications cable
Press TV – December 29, 2013
The US National Security Agency (NSA) has collected sensitive data on key undersea optical fiber telecommunications cables between Europe, North Africa and Asia.
Citing classified documents labeled “top secret” and “not for foreigners”, German news magazine Der Spiegel reported on Sunday that the NSA spied on the so-called “South East Asia-Middle East-West Europe 4” also known as “Sea-Me-We 4” undersea cable system.
The German magazine said NSA specialists had hacked an internal website belonging to the operator consortium to mine documents about technical infrastructure including circuit mapping and network management information. “More operations are planned in the future to collect more information about this and other cable systems.” Spiegel quoted the NSA documents, dating from February, as saying.
According to the website of the project “the South East Asia-Middle East-West Europe 4 project is a next generation submarine cable system linking South East Asia to Europe via the Indian Sub-Continent and Middle East. The project aims to take these regions to the forefront of global communication by significantly increasing the bandwidth and global connectivity of users along its route between Singapore and France.”
Spiegel reports that “Among the companies that hold ownership stakes in it are France Telecom, now known as Orange and still partly government-owned, and Telecom Italia Sparkle.”
In March 2004, a consortium of 16 international telecommunications companies signed construction and maintenance agreements for the new optical fiber submarine cable system linking South East Asia to Europe via the Indian Sub-Continent and Middle East with Terminal Stations in Singapore, Malaysia, Thailand, Bangladesh, India, Sri Lanka, Pakistan, United Arab Emirates, Saudi Arabia, Egypt, Italy, Tunisia, Algeria and France. The contract is being awarded jointly to Alcatel Submarine Networks, France and Fujitsu Ltd., Japan and the estimated project cost is of the order of $500 million.
The submarine cable system is approximately 20,000km long. It consists of the main backbone across the Eastern and Western worlds plus the extension links in various countries. The project seeks to support telephone, internet, multimedia and various broadband data applications.
It seems the method was employed by the NSA’s elite hacking unit (TAO) via incorporating routers and servers from non-NSA networks into its covert network by infecting these networks with “implants” that then allow the government hackers to control the computers remotely.
The document leaked by Der Spiegel proudly says that, on Feb. 13, 2013, TAO “successfully collected network management information for the SEA-Me-We Undersea Cable Systems (SMW-4).” With the help of a “website masquerade operation,” the agency managed to “gain access to the consortium’s management website and collected Layer 2 network information that shows the circuit mapping for significant portions of the network.”
The US government claims that its spying operations that are taking place both at home and abroad are vital for fighting terrorism.
A federal judge ruled Friday that the NSA’s bulk collection of millions of Americans’ telephone and Internet records is legal. US District Judge William Pauley also concluded that the operation is an important part of America’s effort to combat the threat of terrorism.
NSA spies on millions of telephone and Internet records that are routed through American networks on daily basis. According to some estimates, NSA spies on 380 million cellphones in the US.
Prior to Pauley’s ruling, another US District Court Judge, Richard Leon, had described the massive NSA spying program “Almost Orwellian”.
“I cannot imagine a more ‘indiscriminate’ and ‘arbitrary invasion’ than this systematic and high-tech collection and retention of personal data on virtually every single citizen,” Judge Leon wrote.
Is Anything Left of the US Constitution or Privacy Rights?

Vying for a Supreme Court appointment? US District Judge William H. Pauley III ruled that the NSA’s massive spying program is legal.
By Franklin Lamb | Fig Trees and Vineyards | December 28, 2013
The answer to this question is being pondered across America in light of two seemingly contradictory federal court decisions handed down this month from two separate courts, one in Washington, the other in New York.
Since the Bush Administration’s “war of terrorism” was launched, civil liberties advocates have voiced growing alarms about the erosion of Constitutional guarantees. Yet with the disclosures by whistle blower Edward Snowden, concerns about what protections Americans have remaining—protections from governmental intrusions into their privacy as well as home or office invasions by police forces—have rapidly gained new impetus. Because of Snowden’s leaks, legal challenges have been brought against the National Security Agency; without the leaks, no challenge could have been mounted.
Now all of a sudden two US Federal District Courts, with identical powers under the US Constitution, have reached seemingly opposite conclusions on the same legal issue, i.e. the right of the NSA to conduct “metadata” searches and store the information of scores of millions of unknowing Americans. This means, given that appeals have been filed in both cases, that the issue is likely going to be decided by the US Supreme Court.
Civil libertarians were encouraged earlier this month when Federal Judge Richard Leon of the United States District Court for the District of Columbia ruled on December 16 that the NSA’s bulk collection of cell phone data of Americans (everyone you called, when you called them, and where you were when you called them) violates the Fourth Amendment to the Constitution. Calling the data gathering “Orwellian,” Judge Leon reasoned that we now use our smartphones for a wide variety of personal activities in which we have the expectation of privacy, that probably we have more expectation of privacy from cell phones now than we did, say, from a pay phone in the 1980s. And he also noted, crucially, that cell phones today make it possible to determine the caller’s GPS location. “It’s one thing to say that people expect phone companies to occasionally provide information to law enforcement; it is quite another to suggest that our citizens expect all phone companies to operate what is effectively a joint intelligence-gathering operation with the Government,” Leon wrote.

US District Judge Richard Leon
The judge then focused on whether the massive NSA surveillance violates the Fourth Amendment, which guarantees, “the right of the people to be secure in their persons, houses, papers, and effects, against unreasonable searches and seizures, shall not be violated, and no warrants shall issue, but upon probable cause, supported by oath or affirmation, and particularly describing the place to be searched, and the persons or things to be seized.”
He writes:
“The threshold issue that I must address, then, is whether plaintiffs have a reasonable expectation of privacy that is violated when the Government indiscriminately collects their telephony metadata along with the metadata of hundreds of millions of other citizens without any particularized suspicion of wrongdoing, retains all of that metadata for five years, and then queries, analyzes and investigates that data without prior judicial approval of the investigative targets. If they do – and a Fourth Amendment search has thus occurred– then the next step of the analysis will be to determine whether such a search is ‘reasonable.’”
Judge Leon found that the NSA, when demanding citizens’ telephone metadata, is conducting a search, and that it is most likely an unreasonable search under the Fourth Amendment, given there is no specific suspicion of wrongdoing by any individual whose records are demanded.
In his ruling he granted the request for an injunction against the collection of the plaintiffs’ phone data, ordering the government to destroy any of their records that have been gathered. But the judge stayed action on his ruling pending a government appeal, recognizing in his 68-page opinion what he termed as the “significant national security interests at stake in this case and the novelty of the constitutional issues.”
But no sooner had Judge Leon’s decision been published, bringing hope to civil libertarians, than US District Judge William H. Pauley III in New York issued what looks almost like a diametrically antithetical ruling, making for the latest in a contentious debate that has also seen a presidential commission weighing in on certain aspects of NSA spying as well. On December 27, Pauley ruled that the NSA’s collection of vast oceans of data on private phone calls is legal—meaning that in a period of just 11 days the two judges, along with the presidential panel, had reached “the opposite of consensus on every significant question before them, including the intelligence value of the program, the privacy interests at stake and how the Constitution figures in the analysis,” as the New York Times reported it.
The case in New York was brought by the American Civil Liberties Union, which said it would appeal.
Judges Leon and Pauley have starkly differing understandings on how valuable the NSA program is. Echoing arguments made recently by former FBI director Robert S. Mueller III and other senior government officials, Pauley, whose courtroom is not far from where the World Trade Center towers stood, said he believed the program might have caught the 9/11 hijackers had it been in place at the time. “While robust discussions are underway across the nation, in Congress and at the White House, the question for this court is whether the government’s bulk telephony metadata program is lawful,” Pauley wrote. “This court finds it is.”
The finding stands in stark contrast to Leon’s ruling in Washington:
“The government does not cite a single instance in which analysis of the N.S.A.’s bulk metadata collection actually stopped an imminent attack, or otherwise aided the government in achieving any objective that was time-sensitive in nature,” Judge Leon wrote.
What these conflicting decisions leave us in is a profound quandary with respect to the issues raised by Edward Snowden. In a Christmas address that was carried by British Channel 4 and widely aired on the Internet, the former NSA contractor expressed the legitimate concern of all people who value individual liberty and privacy. A child born today, he said, might “never know what it means to have a private moment to themselves, an unrecorded, unanalyzed thought.” He added that people are essentially walking around with a tracking device in their pockets, noting that this disappearance of privacy is important because privacy “is what allows us to determine who we are and who we want to be.”
Featured Video
Anthrax War – CBC The Passionate Eye
or go to
Aletho News Archives – Video-Images
Book Review
Shattered Dreams: The HPV Vaccine Exposed (2019)
By Christina England – 30 Q&As – Book Review & Summary
Lies are Unbekoming | September 4, 2026
… Gardasil received FDA fast-track approval in 2006, Cervarix followed in 2009, and Gardasil 9 was approved in December 2014 with more than double the aluminium adjuvant content of the original. The commercial context is specific. Merck was about to lose patent protection on Zocor and faced $18 billion in Vioxx injury claims from a cardiovascular drug the company had marketed while suppressing its own data showing a five-times increase in heart attacks. Analysts projected the global HPV vaccine market at $4 billion by 2011, contingent on government-funded national programs for teenage girls. The 1986 National Childhood Vaccine Injury Act had already granted manufacturers complete liability immunity. By 2013, Japan had withdrawn its HPV vaccine recommendation after cataloguing severe adverse reactions in hundreds of girls. No Western government followed. The establishment position across the UK, US, Australia, and most of Europe held, and still holds, that the vaccines are safe and effective, that reported injuries are coincidental, and that cervical cancer prevention justifies the program. The book was published into this position, not against a vacuum.
Shattered Dreams sits alongside Mary Holland’s The HPV Vaccine On Trial and Viera Scheibner’s foundational vaccination work as part of the documented record on what has been done to a generation of teenage girls under the banner of cancer prevention. The full summary unpacks three specific findings: that Merck used the aluminium adjuvant itself as the “placebo” control in 92.5% of trial subjects, making it structurally impossible to detect excess reactions from the adjuvant; that Dr. Sin Hang Lee found HPV DNA fragments bound to aluminium in every one of sixteen Gardasil samples tested, and in the blood and spleen of a New Zealand girl six months after her third dose; and that in every country with high vaccination coverage, including Australia, the UK, Norway, and Sweden, cervical cancer rates have stopped declining and started rising specifically in the vaccinated cohort. Martínez-Lavín’s 2017 calculation puts the number needed to seriously harm with Gardasil 9 at 140, and the number needed to vaccinate to prevent one case at 1,757. Thirteen young women are seriously harmed for every one who benefits. The vaccine was approved on the basis of trials that could not detect what the trials were supposed to detect, and it is still being given to twelve-year-olds today. … Read full review
Blog Roll
 Aletho News
- The Maidan Killings and the False-Flag Case
- Georgia’s Largest Healthcare System Will Fire Employees Who Refuse Flu Vaccine
- The Five-Year Fuel Crisis: Why the World Economy Is Paying for a War It Thinks Is Ending
- Trump’s Big Bluff on Iran
- Swiss scammed out of millions by Ukraine-linked call centers – media
- Germany facing potential ‘violent conflict’ with Russia – spy chief
- Ukraine’s EU neighbors reject new plea from Kiev – Politico
- British Transport Police Facial Recognition Trial Scanned 926,912 People With Zero Arrests
- House Bill Would Ban Federal Use of Flock ALPR Data
- Can a Spice Rival a Drug? 10 Head-to-Head Trials Put It to the Test.
- If Americans Knew
- “We See Our Homes Now From A Satellite, Like Strangers”
- Watch “Gaza: Doctors Under Attack”, originally censored by BBC
- NAZA: Israeli embassies in UK and US promote rival documentary to challenge Gaza genocide allegations
- David Ellison appoints Israeli to lead merged Paramount-Warner studios
- Turkish Red Crescent helps elderly Gaza man walk again after Israel confiscates his prosthetic limb
- Four Palestinians Killed in Israeli Attacks in Gaza
- Two Palestinian youths killed and village razed as Israeli attacks on West Bank continue
- Two more Christian women victims of Israeli raids on Gaza
- Cruelty, Deprivation, Indignity: A Journalist’s 22 Months in Israeli Prison
- New IDF Website Frames Slain Gaza Journalists as Terrorists
- No Tricks Zone
- Latest European Green Energy Debacle; Portugal’s Largest Flagship Solar Park Insolvent!
- Green Energy Debacle: German Expert Professor Fritz Vahrenholt Warns Of Severe Economic And Social Consequences
- Two More Paleo Reconstructions Affirm Meters-Higher Sea Levels Across Ireland, Brazil 7000-6000 Years Ago
- New Study: Earth And Venus Surface Warmth Largely Explained By Convection And Lapse Rate, Not CO2 Or Radiation
- 2025 Nature Paper Claiming Worsening Global Drought Gets RETRACTED …Heavily Flawed
- New Study: ‘Global Drought Shows No Detectable Recent Acceleration Under Climate Warming’
- Economic Masterminds: German Socialists Suggest Taxing Productivity Gains Stemming From Using AI
- The South China Sea Has Not Been Cooperating With The Climate Change Narrative
- Energy Crisis: Germany Enters Heating Season With Historically Low Gas Reserve Fill Levels
- New Study: The Antarctic Ice Sheet Gained Mass From 2020-2024 Due To Staggering Snow And Ice Accumulation

