How Europe’s Fight with Google Over Privacy Ignores Real Privacy
By Alfredo Lopez | This Can’t Be Happening | April 10, 2013
Last week the governments of France, Germany, Italy, the Netherlands, Spain, and the United Kingdom fired a warning shot at Google and it appears they’re reloading the gun with real ammunition.
This past December, about a year after the Internet behemoth announced a new privacy policy, a working group of representatives from these countries called the policy grossly abusive of people’s privacy and said Google had four months to bring itself into compliance with European law. Google dismissed the ultimatum: “Our privacy policy,” it said, “respects European law and allows us to create simpler, more effective services.” The European countries response was that they will take actions, based on their national laws and in coodination with each other, by the Fall.
These government/corporation tiffs are frequent and their rhetorical fire normally turns into quickly dissipated smoke. This one could be different. It comes at a time when the world’s powerful are trying to decide how much privacy we people will have and what the term privacy actually means, and this squabble’s outcome will affect that and, of course, our freedom. That alone makes it worth watching.
But there’s something deeper here that transcends this conflict. Privacy is, in fact, a core component of democracy and any infringement on complete privacy is an obscene attack on the possibility of having a free and democratic society. As important as the outcome of this show-down might be, the most important and frightening development is that it’s taking place at all.
The political shoot-out began a year ago when Google announced that it was unifying about 60 privacy policy agreements, covering its myriad services, into one big one. The company explained that lumping together these “agreements” (the things you’re asked to read before pressing the “I Accept” button on a website) was a matter of efficiency and transparency. There’s a logic to that: how many privacy policies have you read on the Internet? One would assume that if you don’t read one, you can hardly be expected to read 60.
That, however, is a corporate shell game. Google made this move not to make our reading easier but to make gathering information about us more efficient. Google is a marketing company and nothing makes a marketing company more powerful and valuable to advertisers than having pertinent information on hundreds of millions of people all over the world. Its privacy policy is fitted to that purpose. It says that, once you sign up and begin using these services as an identified user, you give up that right of refusal. So, because people don’t read that privacy policy, they don’t realize that it effectively eliminates their privacy.
For a very long time, Google has known who uses each of its services and how, but now it knows which combination of services you use and how they interact with each other in your daily life. It also knows cities or towns of residence (and, in many cases, addresses) of its registered users, the IP addresses of their computers, their names (and often the names of their family members and friends), what they do on the Internet every day, what they buy and consider buying and, for those using Gmail, who they write to and what they write. It can hone in a your specific physical location with Goodgle Maps and will store that info if you map it. In fact, all this info is stored on Google’s databases with members’ tacit approval and Google’s complete understanding of what all this means.
“If you have something that you don’t want anyone to know, maybe you shouldn’t be doing it in the first place,” Google CEO Eric Schmidt said in 2009. “If you really need that kind of privacy, the reality is that search engines — including Google — do retain this information for some time and it’s important, for example, that we are all subject in the United States to the Patriot Act and it is possible that all that information could be made available to the authorities.”
The information Google holds rivals and in some cases surpasses the information most governments have on their own citizens. So when Google released this new policy which permits it to combine that information and use it for evaluation, marketing and advertising, these governments commissioned France’s CNIL to investigate.
That selection, in itself, is striking. The CNIL is an independent, government-supported authority that specializes in data privacy law enforcement. France has among the strongest data collection restrictions in the world and, while CNIL has often been criticized by advocates for being too sheepish in its advocacy, data protection “sheepishness” in France would be considered ferocity in many other countries.
Like a trained bulldog, CNIL investigated all the Google data policies for nine months and then presented its report. It was devastating, accusing Google of policies and mechanisms that effectively violate privacy laws in most European countries. Based on that report, 24 of the EU’s 27 data regulators wrote Google a letter last December proposing about a dozen changes: among them that Google shouldn’t collect information on users without their consent, combine information from different services without additional consent or use the data it collects for advertising.
The four months passed. “Google did not provide any precise and effective answers,” CNIL said last week. “In this context, the EU data protection authorities are committed to act and continue their investigations. Therefore, they propose to set up a working group, led by the CNIL, in order to coordinate their reaction, which should take place before summer.”
In the diplomatic jargon of international regulation, those are fighting words. “Coordinate their reaction” is something the European Union’s countries seldom do (witness their financial crisis) and they almost never make threats around technology. Action against Google in Europe could affect the company’s relationship with one of its largest markets and a critical marketing link in the world-wide chain that is the Internet. Google could be crippled. That’s what that statement threatens.
But let’s not kid ourselves. A capitalist government, like those in Europe, has a system to protect and, to do the protecting, its police agencies routinely use data collected on the Internet about its citizens. As Google’s Schmidt put it in 2010: “In a world of asynchronous threats it is too dangerous for there not to be some way to identify you. We need a [verified] name service for people. Governments will demand it.”
So the issue here isn’t really how to protect people’s privacy; it’s how to balance the various approaches to impinging on it. Google says it needs information about you to match its marketing to what you buy; governments say they need information about you to monitor and control what you do the rest of the time. They’re trying to work out how these two approaches to information gathering can co-exist and not conflict with each other.
If, for example, a particular policy draws too much public attention to this issue or provokes a large lawsuit or gets people asking why their government isn’t — or is — doing something, that’s a problem. The government will then find its own privacy policies in the spotlight. That’s only one way this balance can become unbalanced, but in any case balance is the issue being disputed. There is really no debate about whether or not you have a right to privacy on the Internet. As far as both sides are concerned, you don’t, and both sides are most pleased if you’re not paying much attention to that fact.
It’s persistently perplexing how little most people care about this issue. Even many of the most politically conscious will often just shrug and say “there’s nothing that can be done about it”. After decades of increasing surveillance (oiled by a government-encouraged paranoia about terrorism) we expect the powerful of our society to know everything about us and, apparently, most of us can live with that. Some of us appear to think we can’t live without it.
But that battering of our democratic consciousness has not only lowered our guard against violations of our privacy; it has actually fostered a distorted understanding of what privacy actually is. Or better put: it’s convinced many of us that a small part of the privacy debate is the entire debate.
For purposes of the Internet, privacy is your ability to communicate with other people excluding anyone you want from that conversation and your ability to say what you want to those people (and listen to what they have to say) excluding people you don’t want listening.
Sure, what you say to your family or which websites you visit or what you consider buying on the Internet should, in a sane society, be your business and taking a snapshot of all this is a horrible personal violation. But the more dangerous violation is that, in establishing the means to eavesdrop on your life and honing the ability to store and analyze that information, powerful forces are systematically limiting what the Internet can be about.
What humanity created as a tool of freedom and, in many cases, struggle has been taken over by corporations and governments wielding lawsuits, imprisonment and largely unnoticed anti-freedom laws to pervert its original intent.
“When the Internet began… it was seen largely as a non-commercial oasis,” free-speech advocate and writer Robert McChesney told Democracy Now in a recent interview. “It was a place where people could go and be equal and be empowered as citizens to take on concentrated economic and political power, to battle propaganda… And there was no surveillance. People could do what they wanted and not be tracked.
“What’s been taking place… is that on a number of different fronts, extraordinarily large, monopolistic corporations have emerged: AT&T, Verizon, Comcast, at the access level; Google, Facebook, Apple, Amazon, at the application and use level. And these firms have changed the nature of the Internet dramatically… (and) they work closely with the government and the national security state and the military. They really walk hand in hand collecting this information, monitoring people, in ways that by all democratic theory are inimical to a free society.”
“Privacy” isn’t primarily individual and privacy laws aren’t in place only to address individual activities. In fact, you can’t be individually private on the Internet because then you wouldn’t be using the Internet. The privacy laws are there to make sure people can function in our exercise of free speech, exchange of information and association. They are, and always have been, a way to protect us from government inquiry and inquisition. Those laws that say a cop can’t just walk into your house and search it without a warrant or question you and those with you or keep close tabs on everything you do and who you do it with — those are privacy laws. They protect our collaborative activity from
government repression.
That collaborative activity is what the Internet has deepened and broadened. It lets us communicate with people all over the world involved in activities emanating from issues and concerns similar to ours. It lets people who are fighting for their rights in a country where such activity can get you jailed or killed talk to people world-wide who can support them. It permits coordination of struggles going on in vastly different environments in far-away countries. It cuts through our media’s lies about other countries with solid truth we learn from people in those countries. It helps unify us and helps us support each other in a rapid, almost immediate, way.
It’s what humanity needs and it’s the reason why the Internet now reaches two billion people.
But if the privacy is taken away, if a government or a corporation can read your email or follow you around as you visit and use websites, your use of the Internet for its most important political purpose becomes stored information that can be used to oppose and repress you.
Privacy, viewed that way, is the litmus test of a free environment. In that context, Google is a monster and the governments that are challenging it on such restricted grounds aren’t much better.
Yes, the progressive response to the European initiative on Google privacy should be to encourage it but with an understanding of its pitfalls and a loud outcry about them. Even if Europe has its way, the outcome will still be an erosion of our privacy and a further empowerment of those who would, in some situations, repress our movements for change.
So right now, those of us who are truly concerned about the future of this society and the world, need to place Internet privacy among our most prominent issues.
FBI Sued for Info on Supersnooping Program
By RYAN ABBOTT | Courthouse News | April 10, 2013
WASHINGTON – The FBI refuses to provide information on a massive biometric identification database that can identify noncriminal civilians through iris scans, DNA, and facial and voice recognition, a watchdog claims in court.
The Electronic Privacy Information Center, or EPIC, sued the FBI in Federal Court, claiming that the bureau identified more than 7,000 pages of responsive records, but won’t release them.
EPIC claims the FBI began posting details on its website about its biometric identification system, known as Next Generation Identification (NGI), in 2009.
“When completed, the NGI system will be the largest biometric database in the world,” EPIC says in its complaint. “The vast majority of records contained in the NGI database will be of U.S. citizens.”
EPIC claims the NGI system will be able to identify people through fingerprints, iris scans, DNA profiles, voice identification profiles, palm prints and photographs, and will through facial recognition.
“The NGI database will include photographic images of millions of individuals who are neither criminals nor suspects,” the complaint states.
The Department of Homeland Security has spent “hundreds of millions of dollars” into the system, and wants to integrate it into state and local surveillance systems that may use other surveillance technology, giving the government the capability of real-time matching of live feeds from surveillance cameras, EPIC claims.
There are an estimated 30 million surveillance cameras in the United States, but not all of them will be used for law enforcement purposes, EPIC says in the complaint.
It claims private entities will also have access to the system.
EPIC claims the Orwellian system already is up and running in New York City, where police have been scanning irises of arrestees since 2010 and using a handheld device that “allows officers patrolling the streets to scan irises and faces of individuals and match them against biometric databases.”
At least 11 other states participate in the program: Arizona, Hawaii, Kansas, Maryland, Michigan, Missouri, Nebraska, New Mexico, Ohio, South Carolina and Tennessee, according to the complaint.
EPIC claims it submitted two FOIA request in 2012, seeking records on the FBI’s contracts with private contractors Lockheed Martin, IBM, Accenture, BAE Systems Information Technology, Global Science & Technology, Innovation Management & Technology Services, Platinum Solutions, the National Center for State Courts, and any other entities involved with the program.
The FBI said it found 7,380 pages of potentially responsive records but has failed to disclose a single agency record, the complaint states.
EPIC wants to see the records, and wants its FOIA fees waived.
It is represented by house counsel Ginger McCall.
Related article
New Documents Suggest IRS Reads Emails Without a Warrant
By Nathan Freed Wessler | ACLU | April 10, 2013
Everyone knows the IRS is our nation’s tax collector, but it is also a law enforcement organization tasked with investigating criminal violations of the tax laws. New documents released to the ACLU under the Freedom of Information Act reveal that the IRS Criminal Tax Division has long taken the position that the IRS can read your emails without a warrant—a practice that one appeals court has said violates the Fourth Amendment (and we think most Americans would agree).
Last year, the ACLU sent a FOIA request to the IRS seeking records regarding whether it gets a warrant before reading people’s email, text messages and other private electronic communications. The IRS has now responded by sending us 247 pages of records describing the policies and practices of its criminal investigative arm when seeking the contents of emails and other electronic communications.
So does the IRS always get a warrant? Unfortunately, while the documents we have obtained do not answer this question point blank, they suggest otherwise. This question is too important for the IRS not to be completely forthright with the American public. The IRS should tell the public whether it always gets a warrant to access email and other private communications in the course of criminal investigations. And if the agency does not get a warrant, it should change its policy to always require one.
The IRS and Email: Reading Between the Lines
The federal law that governs law enforcement access to emails, the Electronic Communications Privacy Act (ECPA), is hopelessly outdated. It draws a distinction between email that is stored on an email provider’s server for 180 days or less, and email that is older or has been opened. The former requires a warrant; the latter does not. Luckily, the Fourth Amendment still protects against unreasonable searches by the government. Accordingly, in 2010 the Sixth Circuit Court of Appeals decided in United States v. Warshak that the government must obtain a probable cause warrant before compelling email providers to turn over messages.
However, the IRS hasn’t told the public whether it is following Warshak everywhere in the country, or only within the Sixth Circuit.
The documents the ACLU obtained make clear that, before Warshak, it was the policy of the IRS to read people’s email without getting a warrant. Not only that, but the IRS believed that the Fourth Amendment did not apply to email at all. A 2009 “Search Warrant Handbook” from the IRS Criminal Tax Division’s Office of Chief Counsel baldly asserts that “the Fourth Amendment does not protect communications held in electronic storage, such as email messages stored on a server, because internet users do not have a reasonable expectation of privacy in such communications.” Again in 2010, a presentation by the IRS Office of Chief Counsel asserts that the “4th Amendment Does Not Protect Emails Stored on Server” and there is “No Privacy Expectation” in those emails.
Other older documents corroborate that the IRS did not get warrants across the board. For example, the 2009 edition of the Internal Revenue Manual (the official compilation of IRS policies and procedures) explains that “the government may obtain the contents of electronic communication that has been in storage for more than 180 days” without a warrant.
Then came Warshak, decided on December 14, 2010. The key question our FOIA request seeks to answer is whether the IRS’s policy changed after Warshak, which should have put the agency on notice that the Fourth Amendment does in fact protect the contents of emails. The first indication of the IRS’s position, from an email exchange in mid-January 2011, does not bode well. In an email titled “US v. Warshak,” an employee of the IRS Criminal Investigation unit asks two lawyers in the IRS Criminal Tax Division whether Warshak will have any effect on the IRS’s work. A Special Counsel in the Criminal Tax Division replies: “I have not heard anything related to this opinion. We have always taken the position that a warrant is necessary when retrieving e-mails that are less than 180 days old.” But that’s just the ECPA standard. The real question is whether the IRS is obtaining warrants for emails more than 180 days old. Shortly after Warshak, apparently it still was not.
The IRS had an opportunity to officially reconsider its position when it issued edits to the Internal Revenue Manual in March 2011. But its policy stayed the same: the Manual explained that under ECPA, “Investigators can obtain everything in an account except for unopened e-mail or voice mail stored with a provider for 180 days or less using a [relevant-and-material-standard] court order” instead of a warrant. Again, no suggestion that the Fourth Amendment might require more.
The first indication that the IRS was considering the effect of Warshak came in an October 2011 IRS Chief Counsel Advice memorandum available on the IRS website but not provided in response to our FOIA request. An IRS employee sought guidance about whether it is proper to use an administrative summons, instead of a warrant, to obtain emails that are more than 180 days old. (The emails in question were located on an internet service provider’s (ISP) server somewhere in the territory covered by the Ninth Circuit Court of Appeals). The memo summarized the holding of Warshak and advised that “as a practical matter it would not be sensible” to seek older emails without a warrant. This is good advice, but the memo’s reasoning leaves much to be desired. The memo explained that Warshak applies only in the Sixth Circuit but that, because the ISP had informed the IRS that it did not intend to voluntarily comply with an administrative summons for emails, there was not “any reasonable possibility that the Service will be able to obtain the contents of this customer’s emails . . . without protracted litigation, if at all.” Any investigative leads contained in the emails would therefore be “stale” by the time the litigation could be concluded, making attempted warrantless access not worthwhile.
The memo misses another chance to declare that agents should obtain a warrant for emails because the Fourth Amendment requires it. Instead, the memo’s advice (which may not be used as precedent and is not binding in other IRS criminal investigations) is limited to situations in the Ninth Circuit where an ISP intends to challenge warrantless requests for emails. The IRS shouldn’t obey the Fourth Amendment only when it faces the inconvenience of protracted litigation; it should recognize that the Fourth Amendment requires warrants for the contents of emails at all times.
Finally, to the present: has the IRS’s position changed this tax season? Apparently not. The current version of the Internal Revenue Manual, available on the IRS website, continues to explain that no warrant is required for emails that are stored by an ISP for more than 180 days. Apparently the agency believes nothing of consequence has changed since ECPA was enacted in 1986, or the now-outdated Surveillance Handbook was published in 1994.
The IRS Owes the American Public an Explanation—and a Warrant Requirement
Let’s hope you never end up on the wrong end of an IRS criminal tax investigation. But if you do, you should be able to trust that the IRS will obey the Fourth Amendment when it seeks the contents of your private emails. Until now, that hasn’t been the case. The IRS should let the American public know whether it obtains warrants across the board when accessing people’s email. And even more important, the IRS should formally amend its policies to require its agents to obtain warrants when seeking the contents of emails, without regard to their age.
(We also sent FOIA requests to the FBI and other components of the Department of Justice—we will be receiving records from those offices in the coming weeks).
Related articles
- Like rest of the feds, the IRS can get your e-mails with no problem (arstechnica.com)
- When a Secretive Stingray Cell Phone Tracking “Warrant” Isn’t a Warrant (alethonews.wordpress.com)
Palestinian Cameraman Shot In The Face In Bethlehem
By Saed Bannoura | IMEMC & Agencies | April 08, 2013
 Bethlehem, Monday April 8, 2013, Palestinian medical sources reported that a Palestinian cameraman was shot in the face, on Monday evening, by a rubber-coated metal bullet, in the Aida refugee camp in the West Bank city of Bethlehem.
The Palestine News Network (PNN) has reported that Mohammad Waleed Al-Azza was shot during clashes that took place between Israeli soldiers invading the camp and local youths who hurled stones at them.
PNN added that Al-Azza, who works at the Refugee Media Center in addition to freelancing for PNN and other agencies, was deliberately shot in the face by the soldiers who tried to stop him from documenting the invasion.
The soldiers tried to push him away, and when he refused to leave, one of the soldiers pointed his gun at him and shot him from a relatively close range.
Al-Azza’s medical condition was described as moderate; he was moved to the Bethlehem Arab Society for Rehabilitation, in Bethlehem, where he will undergo surgery.
The camp has been witnessing an extended wave of escalation since several months now, due to repeated Israeli invasions and attacks against the residents, PNN said.
Several reporters have been injured in recent clashes between the soldiers and the Palestinians in different parts of the occupied West Bank, and occupied East Jerusalem.
Supporters Say All The Wrong Things to Try and Pass CISPA
By Mark M. Jaycox | EFF | April 8, 2013
Ever since reintroducing CISPA, the so-called “cybersecurity bill,” its supporters promote the bill with craftily worded or just plain misleading claims. Such claims have been lobbed over and over again in op-eds, at hearings, and in press materials. One “fact sheet” by Rep. Rogers and Ruppersberger titled “Myth v. Fact” is so dubious that we felt we had to comment.
Here are some of the statements supporters of CISPA are pushing and why they’re false:
Supporters of CISPA say, “There are no broad definitions”
Supporters are keen to note that the bill doesn’t have broad definitions. In the “Myth v. Fact” sheet, the authors of CISPA specifically point to the definition of “cyber threat information.” Cyber threat information is information about an online threat that companies can share with each other and with any government agency—including the NSA. In hearings, experts have said that they don’t need to share personally identifiable information to combat threats. But the definition in the bill allows for any information related to a perceived threat or vulnerability—including sensitive personal information—to be shared. Cyber threat information should be a narrowly defined term.
Another example of a broad (or missing) definition is the term “cybersecurity system.” Companies can use a “cybersecurity system” to “identify or obtain” information about a potential threat (“cyber threat information”). The definition is critical to understanding the bill, but is circular. CISPA defines a “cybersecurity system” as “a system designed or employed” for a cybersecurity purpose (i.e. to protect against vulnerabilities or threats). The language is not limited to network security software or intrusion detection systems, and is so broadly written that one wonders if a “system” involving a tangible item—e.g., locks on doors—could be considered a “cybersecurity system.” In practical terms, it’s unclear what is exactly covered by such a “system,” because the word “system” is never defined.
The best example of a dangerous undefined term in the bill is found within the overly broad legal immunity for companies. The clause grants a company who acts in “good faith” immunity for “any decisions made” based off of the information it learns from the government or other companies. Does this cover decisions to violate other laws, like computer crime laws? Or privacy laws intended to protect users? Companies should not be given carte blanche immunity to violate long-standing computer crime and privacy law. And it is notoriously hard to prove that a company acted in bad faith, in the few circumstances where you would actually find out your privacy had been violated.
Supporters of CISPA say, “The bill is not a government surveillance program”
Supporters are adamant CISPA doesn’t create a wide-ranging “government surveillance program.” It’s true the bill doesn’t create such a surveillance program like the one described in the ongoing warrantless wiretapping lawsuits.
But the trick here is what is meant by “government surveillance.” We think that if the bill aims at having our information flow to the government, it’s tantamount to government surveillance, whether or not the government initially collected the information.
The bill creates a loophole in the privacy laws that prevented companies from disclosing your information to the government and gives companies broad legal immunity for sharing information with the government. As a result, CISPA makes it more likely that companies will surveil their own users and then disclose that information. The sly wording dodges the key issue: that CISPA encourages companies to conduct surveillance on their networks and hand “cyber threat information” to the government. In short, the bill encourages a de facto private spying regime, with the same end result.
Supporters of CISPA say, “The government can’t read your private email”
Reps. Rogers and Ruppersberger are adamant CISPA doesn’t grant the government access to read private emails. The claim was recently repeated by James Lewis, a fellow at the Center for Strategic and International Studies. But the broad definitions do allow for personal information to be gathered by companies and then sent to the government without any mandatory minimization of personal information. And under the vague definitions an aggressive company could claim that private messages are related to the threat, obtain them, and share then with the government. If Reps. Rogers and Ruppersberger did want content of emails disclosed under CISPA, it would be easy enough to exclude them explicitly.
Supporters say, “CISPA follows advice from privacy and civil liberty advocates”
In his introduction of the bill, Rep. Rogers assured the audience that he has listened to the privacy and civil liberties community.
This year’s CISPA does contain some language added after privacy and civil liberties advocates complained in 2012. But those changes didn’t address some big issues that were raised last year, and this year’s privacy and civil liberties complaints about CISPA remain unaddressed.
Let’s Stop CISPA
Reps. Rogers and Ruppersberger are on a strong publicity offensive to make sure the bill passes. The American public deserves full explanations and clear meanings about what CISPA can do and the extent to which it can do it. The public doesn’t need carefully worded messaging materials that obfuscate and mislead a discussion on CISPA. The issues at stake—like the broad legal immunity and new spying powers that allow for companies to collect private, and sensitive, user information—are too serious.
To stop this type of misinformation—and to stop CISPA—we urge you to tell your members of Congress to stand up for privacy.
Related articles
Israeli military court sentences cartoonist to five months in jail
Palestine Information Center – 06/04/2013
 JENIN — The Israeli military court in Salem, north of Jenin, has sentenced Palestinian cartoonist Mohammed Sabana to five months imprisonment on the charge of contacting “hostile parties”.
Family members told the PIC reporter on Saturday that the court passed the sentence on Friday and charged Sabana with making such contacts during his visit to Jordan.
They said that the charges were unfounded, adding that the sentence was illegal and proved the summary trials conducted against Palestinian citizens.
The relatives affirmed that Sabana was not involved with any political party or organization and was just an activist who employs his cartoons in exposing the Israeli occupation’s crimes.
Sabana was arrested on his return from Jordan last February and held for interrogation. His brother, Thamer, was also detained for his pro-prisoners’ activities.
Related articles
- Israel detains Palestinian cartoonist, family says (alethonews.wordpress.com)
- Palestinian Journalists jailed by Israelis (english.pravda.ru)
Report Details Government’s Ability to Analyze Massive Aerial Surveillance Video Streams
By Jay Stanley | ACLU | April 5, 2013
Yesterday I wrote about Dayton Ohio’s plan for an aerial surveillance system similar to the “nightmare scenario” ARGUS wide-area surveillance technology. Actually, ARGUS is just the most advanced of a number of such “persistent wide-area surveillance” systems in existence and development. They include Constant Hawk, Angel Fire, Kestrel (used on blimps in Afghanistan), and Gorgon Stare.
One of the problems created by these systems—which have heretofore been used primarily in war zones—is that they tend to generate a deluge of video footage. A 2010 article says that American UAVs in Iraq and Afghanistan produced 24 years’ worth of video in 2009, and that that number was expected to increase 30-fold (which would be 720 years’ worth) in 2011. Who knows what that’s up to this year, or where it will be by, say, 2025. The human beings who operate these systems can’t possibly analyze all that footage.
In an attempt to solve this problem, Lawrence Livermore Labs has created a system for the military called “Persistics.” It can be used in conjunction with drone (or manned) camera systems such as ARGUS to help manage the vast oceans of video data that are now being generated. The system is
designed to help the Department of Defense and other agencies monitor tens of square kilometers of terrain from the skies, with sufficiently high resolution for tracking people and vehicles for many hours at a time.
That’s from a May 2011 report that I recently came across with the faintly ominous title “From Video to Knowledge.” Produced by Livermore Labs, it contains a lot of interesting detail about Persistics and the problems and solutions involved in massive aerial video surveillance.
The Persistics system consists of algorithms that “analyze the streaming video content to automatically extract items of interest.”
Its analysis algorithms permit surveillance systems to “stare” at key people, vehicles, locations, and events for hours and even days at a time while automatically searching with unsurpassed detail for anomalies or preselected targets.
With Persistics, the report boasts, “analysts can determine the relationships between vehicles, people, buildings, and events.” Among the capabilities touted in the report are:
- “Seamless stitching” together of images from multiple cameras to create “a virtual large-format camera.”
- Stabilizing video (“essential for accurate and high-resolution object identification and tracking”).
- Eliminating parallax (the difference in how an object appears when viewed from slightly different angles).
- Differentiating moving objects from the background.
- The ability to automatically follow moving objects such as vehicles.
- Creating a “heat map” representation of traffic density in order to “automatically discern if the traffic pattern changes.”
- Comparing images taken at different times and automatically detecting any changes that have taken place.
- Super-high “1,000-times” video compression.
- The ability to provide all the locations a particular vehicle was spotted within a given time frame.
- The ability to provide all the vehicles that were spotted at a particular location within a given time frame.
Technologically, according to the report, the Persistics program relies heavily on the explosion in the power of consumer Graphics Processing Units (GPUs) used in video games and the like.
The report also says that the system “is being further enhanced” to work with ARGUS, and includes new details about that system:
Persistics can simultaneously and continuously detect and track the motion of thousands of targets over the ARGUS-IS coverage area of 100 square kilometers. ARGUS-IS can generate several terabytes of data per minute, hundreds of times greater than previous-generation sensors.
Previous reports said that ARGUS could cover 15 square miles; here it reports 100 square kilometers, which is 38.6 square miles. (I suppose we should expect Moore’s Law-like expansion in the capabilities of these systems.)
Of course, the system is designed to store and retrieve all the records and data about everything that it surveils:
Persistics supports forensic analyses. Should an event such as a terrorist attack occur, the archival imagery of the public space could be reviewed to determine important details such as the moment a bomb was placed or when a suspect cased the targeted area. With sufficiently high-resolution imagery, a law-enforcement or military user could one day zoom in on an individual face in a heavily populated urban environment, thus identifying the attacker.
As with every privacy-invading technology designed and/or sold as helping foil terrorists, we have to wonder how long it will be before it’s applied to tracking peace activists.
Future work on Persistics is focused on the kind of behavioral analytics that have been discussed in the context of programs such as “Trapwire.” Livermore scientists, according to the report, are now working on automated methods for identifying “patterns of behavior” that could indicate “deviations from normal social and cultural patterns” and “networks of subversive activity.”
Also under development are efforts to allow the three-dimensional viewing of targets, as well as “methods to overlay multiple sensor inputs—including infrared, radar, and visual data—and then merge data to obtain a multilayered assessment.”
Of course, much of this is unobjectionable from a domestic civil liberties point of view when it’s used as originally intended: on foreign battlefields. The problem comes when the government brings the technology home and turns it inward upon the American people. In fact, at the close of the report, Livermore contemplates exactly that:
Unmanned aircraft have demonstrated their ISR [intelligence, surveillance, and reconnaissance] value for years in Afghanistan and Iraq. As U.S. soldiers return home, the role of overhead video imagery aided by Persistics technology is expected to increase. Persistics could also support missions at home, such as monitoring security at U.S. borders or guarding ports and energy production facilities. Clearly, with Persistics, video means knowledge—and strengthened national security.
Among the federal agencies most interested in the technology, the report says, is DHS.
Related article
- Drone ‘Nightmare Scenario’ Now Has A Name: ARGUS (alethonews.wordpress.com)
Until Today, If You Were 17, It Could Have Been Illegal To Read Seventeen.com Under the CFAA
By Dave Maass and Kurt Opsahl and Trevor Timm | EFF | April 3, 2013
If you are 17 or under, a federal prosecutor could have charged you with computer hacking just for reading Seventeen magazine online—until today.
It’s not because the law got any better. Earlier today, we wrote about news sites that alarmingly prohibit their youth audiences from accessing the news and the potential criminal consequences under the Computer Fraud and Abuse Act. In response, the Hearst Corporation modified the terms of service across its family of publications, including the Hearst Teen Network, which notably includes titles like Seventeen, CosmoGirl, Teen and MisQuince.
Seventeen highlights the absurdity of giving terms of service the force of law under the CFAA. It boasts a readership of almost 4.5 million teen readers with an average age of 16 and a half, and yet, until today, the average reader was legally banned from visiting Seventeen.com. That’s right, for a magazine dedicated to teen fashion, the publisher’s terms explicitly restricted online access to readers 18 and older. What’s worse, the Justice Department could choose to bring the might of the government to enforce this contract against a Seventeen reader who may never have even seen the agreement.
Federal prosecutors have argued in court that accessing a website in violation of terms of service is a crime. If the website’s terms, like Seventeen magazine’s previous version, explicitly state that you must be an adult to visit their sites or participate in their interactive features, then teenagers accessing the site “without authorization” under the CFAA and could be doing jail time, according to the DOJ.
Hearst removed the following line from the terms for publications ranging from the Houston Chronicle to the San Francisco Chronicle, from Popular Mechanics to Seventeen:
YOU MAY NOT ACCESS OR USE THE COVERED SITES OR ACCEPT THE AGREEMENT IF YOU ARE NOT AT LEAST 18 YEARS OLD.
The revisions are dated “April 23, 2013,” but presumably they meant April 3. Thank you Hearst, we appreciate your prompt response. But the real problem is the CFAA, which allows prosecutors to use these silly terms to manufacture computer crimes. And prosecutors have plenty of opportunities, as ridiculous terms of service abuond throughout the Internet.
We also previously reported on a variety of other websites—including the New York Times, Boston Globe, and NPR—that have similar terms of service that restrict people 12-and-under from reading the news. Atlantic Wire expanded on our blog post by pointing to even more news sites that do the same thing. While these terms weren’t as absurd as Hearst’s, Atlantic Wire also highlighted the law’s farcical implications using photos showing which of Shaquille O’Neal’s children were allowed to visit a lengthy list of news sites.
Thankfully, the Ninth and Fourth Circuits have rejected the government’s aggressive interpretation of the CFAA (with amicus help from EFF), but the Justice Department has shown no signs that it has given up on aggressive interpretations. The vague language of the law could turn virtually every Internet user into a potential criminal, allowing the Justice Department to use their discretion to go after any citizen they don’t like, rather than only harmful criminals the bill was intended to stop.
Hearst changed its terms of use within a matter of hours and a couple of mouse clicks. Unfortunately, fixing the CFAA won’t be as simple. If the absurdity is getting to you, now would be the time to write your members of Congress, demanding they get on board with CFAA reform and reject the House Judiciary Committee proposal that would make this bad law worse.
Related articles
We don’t spy on US citizens, just anti-government groups, says fusion center director
PrivacySOS – 03/28/2013

The Arkansas State Fusion Center
An official from an Arkansas State Fusion Center recently spoke to the press to clear up what he called “misconceptions” about what his office actually does, with depressingly hilarious results. (For some background on fusion centers, click here.)
“The misconceptions are that we are conducting spying operations on US citizens, which is of course not the fact. That is absolutely not what we do,” fusion center director Richard Davis told the local press.
Fusion center employees are in a tight spot to justify the existence of their operations after multiple congressional reports over the past year took them to task for being poorly run, duplicative of other counterterrorism efforts, privacy violative wastes of money, or some combination of the three.
So what does Mr. Davis’ fusion center do, then? Why does it exist?
The Arkansas fusion center director, after having flatly denied that his office spies on US citizens, told the reporter the following:
“I do what I do because of what happened on 9/11,” Davis says. “There’s this urge and this feeling inside that you want to do something, and this is a perfect opportunity for me.”
Davis says Arkansas hasn’t collected much information about international plots, but they do focus on groups closer to home.
“We focus a little more on that, domestic terrorism and certain groups that are anti-government,” he says. “We want to kind of take a look at that and receive that information.“
So the fusion center does in fact spy on US citizens! Among them, “groups that are anti-government.” But maybe I’m getting ahead of myself here: perhaps Mr. Davis thinks that people who hold “anti-government” views should not be treated as US citizens?
The fact is, in the United States, holding “anti-government” views is protected by the First Amendment. And everyone in the United States, not just its citizens, is protected by the First Amendment and the rest of the Bill of Rights.
Disliking the government isn’t a crime. But that’s not stopping many fusion centers from associating dissent with terrorism.
Here in Boston we learned that the Boston police intelligence unit spied on anti-war and other activist groups for years, filing “intelligence reports” on activists at its fusion center, the Boston Regional Intelligence Center. Fusion centers in other states have reported on people for high crimes like putting political stickers up in restrooms, or participating in anti-death penalty organizing.
Activists in Los Angeles have brought their concerns about inappropriate political spying straight to the fusion center itself. Perhaps people in Arkansas should tell Mr. Davis how they feel about their tax dollars supporting shadowy surveillance of so-called “anti-government” groups. Then again, they might not want to be listed as “anti-government.”
When a Secretive Stingray Cell Phone Tracking “Warrant” Isn’t a Warrant
By Hanni Fakhoury | EFF | March 28, 2013
An Arizona federal court this afternoon will be the battleground over the government’s use of a “Stingray” surveillance device in a closely watched criminal case, United States v. Rigmaiden. And in an important development, new documents revealed after an ACLU of Northern California Freedom of Information Act (FOIA) request should leave the government with some explaining to do.
“Stingray” is the brand name of an International Mobile Subscriber Identity locator, or “IMSI catcher.” A Stingray acts as a fake cell-phone tower, small enough to fit in a van, allowing the government to route all network traffic to the fake tower. We’ve warned that Stingrays are dangerous because they have the capability to obtain the contents of electronic and wire communications while necessarily sucking down data on scores of innocent people along the way.
The Fourth Amendment requires searches be “reasonable,” generally meaning they must be accompanied by a warrant. To get a warrant, the government must show there is probable cause to believe the place they want to search will have evidence of a crime. And it means the judge must ensure the warrant is “particular,” or limited to only allow searches into areas where the evidence is most likely to be found. The only way a judge can make these tough decisions is with the government being forthright about what it’s doing.
But when it comes to Stingrays the government has been extremely secretive about its use, withholding documents in FOIA requests, failing to explain (or even understand) the technology to a Texas federal judge and in Rigmaiden, misleading the court about the fact it’s even using one at all.
Daniel David Rigmaiden is charged with a variety of tax and wire fraud crimes. Hoping to pinpoint Rigmaiden’s precise location within an apartment complex, federal agents applied for an order requesting the court to order Verizon to help the agents pinpoint the physical location of a wireless broadband access card and cell phone they believed Rigmaiden was using. The order is clearly directed towards Verizon:
The Court therefore ORDERS, pursuant to Federal Rule of Criminal Procedure 41(b); Title 18, United States Code, Sections 2703 and 3117; and Title 28, United States Code, Section 1651, that Verizon Wireless, within ten (10) days of the signing of this Order and for a period not to exceed 30 days, unless extended by the Court, shall provide to agents of the FBI data and information obtained from the monitoring of transmissions related to the location of the Target Broadband Access Card/Cellular Telephone…
Ultimately, it turns out the government did not just get Verizon to give it the data. It also used a Stingray device to find Rigmaiden, sucking up loads of other data from other electronic devices in the complex as well, which it deleted.
When Rigmaiden filed a motion to suppress the Stingray evidence as a warrantless search in violation of the Fourth Amendment, the government responded that this order was a search warrant that authorized the government to use the Stingray. Together with the ACLU of Northern California and the ACLU, we filed an amicus brief in support of Rigmaiden, noting that this “order” wasn’t a search warrant because it was directed towards Verizon, made no mention of an IMSI catcher or Stingray and didn’t authorize the government—rather than Verizon—to do anything. Plus to the extent it captured loads of information from other people not suspected of criminal activity it was a “general warrant,” the precise evil the Fourth Amendment was designed to prevent.
The FOIA documents bolster our argument that this isn’t a warrant. The documents are a series of internal emails from DOJ attorneys in the United States Attorney’s Office for the Northern District of California, the district where the order in Rigmaiden’s case was issued. The emails make clear that U.S. Attorneys in the Northern California were using Stingrays but not informing magistrates of what exactly they were doing. And once the judges got wind of what was actually going on, they were none too pleased:
As some of you may be aware, our office has been working closely with the magistrate judges in an effort to address their collective concerns regarding whether a pen register is sufficient to authorize the use of law enforcement’s WIT technology (a box that simulates a cell tower and can be placed inside a van to help pinpoint an individual’s location with some specificity) to locate an individual. It has recently come to my attention that many agents are still using WIT technology in the field although the pen register application does not make that explicit.
While we continue work on a long term fix for this problem, it is important that we are consistent and forthright in our pen register requests to the magistrates…
These emails, combined with the text of the disputed order itself, suggest agents obtained authorization to use a pen register without indicating they also planned to use a Stingray. Either at the time of the application or after the fact, the government attempted to transform that order into a warrant that authorized the use of a Stingray.
Judicial superivison of searches is most needed when the government uses new technologies to embark into new and unknown privacy intrusions. But when the government hides what it’s really doing, it removes this important check on government power. We hope the court sees its been duped, and makes clear to the government that honesty and a warrant are requirements to using a Stingray.
Journalists detained in Hebron, leading to two arrests and threats to restrict Palestinian movement
International Solidarity Movement | March 24, 2013
Hebron, Occupied Palestine – In the afternoon of the 24th March, two Palestinian Al Jazeera journalists arrived into Hebron to interview a Palestinian family living near the illegal Israeli settlement in the area of Tel Rumeida. When they arrived, settlers called the Israeli military and police, who arrived and confiscated the journalists’ ID cards, despite having seen their press credentials. The Al Jazeera reporters had their ID cards returned after around an hour, but two Hebron Palestinians who attempted to intervene on their behalf with police were arrested and removed in a police car. Their status is currently unknown and no reason was given for their arrest.
After the journalists were apprehended, police and settlers arrived into the area with rolls of barbed wire, informing another Palestinian resident that his primary access to the main road would be closed. Hashem Azzeh and his family live underneath the Tel Rumeida settlement, with their access to the main road running directly next to the settlement. This path has been repeatedly closed by the Israeli authorities since 2000, and was only opened most recently in late 2012 after extensive legal battles in the Israeli courts.
The police and settlers claimed today that the path would be closed because unapproved people had been walking along it. According to the Israeli authorities, only Hashem, his family and guests walking with them have permission to use the path. Hashem states that he has no knowledge of strangers using this route to access his house.
Without the path, Hashem and his family have to travel a much longer, rock-strewn and hazardous route to leave their home. Hashem said today, “I think they will close my access now, they will say it is for security reasons.” He thinks that the settlers used the arrival of the journalists and the subsequent confusion as a pretext to close his path and restrict his family’s movement, in further attempts to drive them from their home – they already face regular hassle from Israeli authorities and attacks from the settlers, including on Hashem’s young children.
Related articles
- 9 Year old Palestinian boy attacked by settlers (alethonews.wordpress.com)
- Stranded in Shuhada: Hebron’s Qurtuba school (alethonews.wordpress.com)
Featured Video
Armando Mema: Finland Used as New Frontline Against Russia
or go to
Aletho News Archives – Video-Images
From the Archives
MI5 plotted assassination of Irish PM in 1985 – Ulster Volunteer Force
RT | December 29, 2017
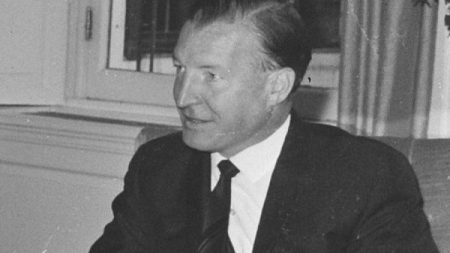
Former Irish Prime Minister Charles Haughey was warned by loyalist paramilitaries that they were once tasked with murdering him in an assassination plot purportedly dreamt up by the British secret service.
The sensational disclosure was sent in a letter to the Irish government, newly released under the Public Records Act, which requires documents of historical value to be published by the National Archives within 30 years.
Written on Ulster Volunteer Force (UVF) signature paper, the warning claims the terrorist organization was asked by an MI5 operative about the prospect of carrying out an attack on Republic of Ireland leader Haughey in 1985.
At the time, Haughey would have been in opposition as head of political party Fianna Fáil, but details of the solicitation did not become known to Irish authorities until 1987.
“In 1985 we were approached by a M15 officer attached to the Northern Ireland Office and based in Lisburn, Alex Jones was his supposed name,” the letter reads, according to the Irish Times. “He asked us to execute you.”… continue
Blog Roll
 Aletho News
- Armando Mema: Finland Used as New Frontline Against Russia
- Gestapo 2.0? Germany grants spy agencies sweeping new powers
- Franco-Palestinian group seeks court ban on Israeli real estate fair in Paris
- How British foreign policy is frozen in the ruins of empire
- EU risks investor exodus over Russian assets – Euroclear chief
- Moscow warns NATO over troop buildup
- EU leaders prolonging Ukraine conflict to stay in power – Swiss journalist
- Moscow car bombing injures former aide to Ukraine’s ex-PM Azarov
- Yemeni forces make major advances, complete Aden encirclement
- Trita Parsi: Trump’s Swiss Cheese Iran Plan & U.S. Break with Israel?
- If Americans Knew
- An error has occurred; the feed is probably down. Try again later.
- No Tricks Zone
- New Study: Barents Sea Temperatures Were Warmer And Sea Ice Less Extensive In The 1700s Than Today
- German Authorities Start Initiative To Evaluate Public Register For Climate “Disinformation” Spreaders!
- Zonal Asymmetry of Temperature Change in the Antarctic Circumpolar Current
- New Study: The Net Fossil Fuel Contribution To Rising Atmospheric CO2 Has Been Zero For 500 Years
- Germany’s Green Energy Transition Becoming Increasingly Expensive…Another 6 Trillion Euros!
- Sudden Stratospheric Warming, Powerful El Niño Combination May Lead To Extreme Europe Cold, Energy Crisis!
- Two New Studies Find Thwaites Glacier Melt Cannot Be Driven By Human Activity Or A Warming Ocean
- E-Cars Reduce CO2 Emissions By Only 41% Compared To Internal Combustion Engine Vehicles
- Predictions Made By Renowned Climate Professor Over Past Decades Have Been Proven To Be Poor
- New Study Suggests Large Regions Of The Pacific Ocean Have Been Cooling For The Last 80 Years

