The ‘Lying’ Mainstream Press and Media in Canada
Part one
By Robin Mathews | American Herald Tribune | January 18, 2020
More and more… reasonably informed Canadians believe ‘the Main Stream Press and Media’ constitutes a ‘lie factory’, a ‘manipulator of public response’ in the service of real power in the country. Canada’s MSPM, that is, exists to help ‘the Deep State’. To help the Corporatocracy. To help the Imperial Master. To help the people Stephen Harper’s group governed for … and the same people the Justin Trudeau group governs for with, perhaps, a little more ‘panache’… and cover-up.
Stark proof of Canadians’ dark and suspicious belief about the MSPM was provided in the first election Justin Trudeau won … and after. The Globe and Mail beat the drums to keep the corrupt Conservative Party of Stephen Harper in power … fighting up to the last hour. And … now … that one of Harper’s worst, rabbit-skinned hatchet-men, makers of ugly, anti-democracy legislation is running for leader, you may be sure no one in the Mainstream Press and Media (MSPM) will review his ugly past doings. Not even Andrew Coyne, star commentator for the Globe and Mail who – in a large recent advertisement tells readers “I can just write what I really think”.
What Canadians face with the likes of Andrew Coyne … and all the rest, I allege … is not only (as we will see) ‘fudging’ of stories to protect the Corporate Rich, but outright failure to surface and deal with “facts”, “news”, “information” Canadians have a right to have (and need to have) in order to act positively for the country.
How is it (for instance) that (unreported/uncommented upon) Canadian publishing that flowered in the post 1968 period to become a major economic and cultural activity (as it should be) in Canada …. is now DESTROYED, without as much as a mournful sigh from the (sold out) representatives of the MSPM, let alone full dress reporting to Canadians of the facts.
Today, fewer than 5% of non-fiction books that Canadians buy are produced by Canadian publishers! Canada’s whole book trade is – for all intents and purposes – a branch activity of foreign (mostly Imperial U.S.) publishers. “We will tell Canadians what they may read.” (and who will profit from it.) Think about that …. (Where is Andrew Coyne?)
WHY, for instance, is there no genuinely fact-informed argument for Canada to get out of NATO. NATO is an arm of U.S. Imperial Policy: period. Why… in addition … do we hear nothing – ever – about Canada’s despicable and repressive role (over decades) in Haiti? Silence. Why does no reasonably intelligent and informed commentator cut through the wholesale truckload of lies about the voracious, calculated, perverse U.S. assault on Venezuela [and any other Central and South American country that seeks real democracy and independence]. And especially … why is there no attack on Canada’s sad and shameful backing of the U.S. in every vicious act against those countries? Why does no “mainstream” Canadian newsdealer ever even mention that the extermination of Palestinians is being pursued … a slow and steady program is being pursued…?
Andrew Coyne writes (“what (he) really thinks”) – a column in support of NATO, (Jan 11, 2020, p.02) ringing all the False Bells, accepting U.S. hegemony, liking it, taking for granted an unbrokenly divided world. He chooses, of course, to forget the ‘non U.N.- approved’ murderous “NATO” actions in the old Yugoslavia; to forget Canada’s shameful part in the wholesale murder and relentless destruction of the country with the highest standard of living in Africa, Libya … in the erasure and gruesome murder of the leader of that country moving his people to decent life. Twelve hundred Libyan students were studying in Canada when Muammar Gaddafi was murdered … to the public gloating joy of Hilary Clinton and (may we assume?) Andrew Coyne …?
Why is there never news about the failure of the Bank of Canada to restore its special lending powers to make possible necessary infrastructure, low-cost housing, hospital and educational building … and more? That policy paid for the Second World War, the building, after it, in Canada … and much more… without significant debt! ! It was trashed by Pierre Elliot Trudeau in 1974 at the instancing of the Bank of International Settlements. (For the meaning of that name read: the U.S. hegemony over all Western nations/NATO nations after the 1944 meetings to lay out power distribution in the after-war-world, held at Bretton Woods, New Hampshire.)
Why is there almost never informed, inclusive, critical comment about ANY of the shared (or unshared) Defence, Policing, Private Corporation Activities, Environmental Actions, Foreign Aid, and Military Hardware sales where Canada and the U.S.A. impinge on one another Canadians are kept almost completely ignorant of major matters concerning … Canada.
Especially … why are Canadians kept in the dark (purposefully) about the gigantic subject of large Canadian corporations acting abroad … and, indeed, about any profit-seeking activity … whether the Pirate-Looting by cell-phone-plus suppliers in Canada or the untenable treatment of workers and the bribery of corrupt others in foreign locations around the globe…? Where is the MSPM??
Andrew Coyne writes about a foreign-acting Canadian corporation, SNC Lavelin (Dec. 21, 2019, p. 02,”SNC’s GUILTY PLEA…”) on tip-toe (so-to-speak), missing, many would say, the point absolutely. But why not? As he says in the his big ad: “I can just write what I really think….” Or, perhaps, it would be better to say “I can just write what the wealthy owners of my job really think….”
We will look at Andrew Coyne’s efforts to “think” (in Part Two of The Lying Mainstream Press and Media in Canada) and see if we can show the strange, guileful, warm, charming, slippery, open-hearted process of completely misleading Canadians … by its Mainstream Press and Media (which includes the Castrated Broadcasting Corporation).
Before leaving Part One… think about the fact that the Castrated Broadcasting Corporation NEVER touches Palestinian Extermination; Haiti; Sell-out of Canadian publishing; “the NATO Question”; the “takeover” (by the Bank of International Settlements) of the Bank of Canada; Canada’s shameful me-too foreign policy in the suppression and devastation by the U.S.A. of Central and South American countries and people; or the behaviour of Canadian Corporations overseas …. Think about … that… and add your own contribution to the list of endless failures “achieved” by Canada’s Mainstream Press and Media.
DHS Head Claims Russia Seeks to ‘Undermine American Way of Life’, Expects US 2020 Voter Interference
Sputnik – 18.01.2020
Acting Secretary of the US Department of Homeland Security (DHS) Chad Wolf has joined the ranks of US officials who observe the DC political creed that Russia interferes in US internal affairs.
Wolf, in his 17 January speech, most of which was dedicated to what he referred to as the “top threats facing the Homeland” – Iran, China and Russia, claimed that even though Moscow does not strive to diminish the US role in the international arena, the nation is nonetheless looking to disrupt and undermine the “American way of life”.
“Lastly, let me touch on Russia. Unlike China, Russia doesn’t seek to weaken our economy and surpass us on the world-stage; rather they focus on actions that disrupt and undermine the American way of life. As we saw in 2016, we fully expect Russia to attempt to interfere in the 2020 elections to sow public discord and undermine our democratic institutions”, Wolf, serving as DHS acting secretary since November 2019, said, during an event hosted by the Homeland Security Experts Group in Washington DC.The official claimed that the 2018 midterm elections were “the most secure elections in the modern era” as the US created “classified and unclassified election war rooms” that “connected election officials in all 50 states, political parties, social media companies and agencies across the US Government, including DOD, the FBI and the Intelligence Community”.
“Let me be clear: We are prepared,” Wolf said. “More importantly, the state and local officials who run our elections are prepared. We are working with our federal partners to make sure those officials on the front lines of our elections have the information and the tools they need to combat Russian interference.”
“In 2020, we’re doing this and more to prevent our adversaries from degrading faith in our democracy and election results”, Wolf said.The acting secretary acknowledged that “100 percent security is never realistic” and asserted that US federal government and intelligence agencies were “laser-focused” on securing the upcoming elections.
Russian Trail
US intelligence agencies and lawmakers have accused Moscow of meddling in US elections since Trump’s 2016 victory, a political event that provoked allegations of Trump’s cooperation with Moscow as a means spreading anti-opponent propaganda online.
The US Department of Justice at the time launched an investigation headed by US Special Prosecutor Robert Mueller but the report concluded that no sufficient evidence existed to prove the allegations.
Both Trump and Russian officials have together repeatedly denied claims that they worked together to influence the results of the election.
In December 2019, Russian Foreign Minister Sergey Lavrov said that he had not seen any proof in support of allegations that Russia interfered in US elections, arguing that “No one has given us this proof because simply it does not exist”, while noting that Moscow is prepared to exchange assurances with Washington on non-interference in each other’s domestic affairs.Besides the US, the narrative of Russian involvement in the internal affairs of other countries has been used by a variety of European nations, however, again, no proof has been furnished.
In November 2019, El Pais published several stories alleging Russian influence in Catalonia, according to Spanish intelligence officers, again without providing evidence. The Russian embassy in Spain responded by joking about the allegations.
“With regards to the tireless work of El Pais researchers on linking the source of the Catalan crisis to Russia, we would like to draw their attention to a revealing fact. There is a suspicious coincidence: the number of the alleged Russian unit, which is mentioned in the newspaper, ends with 155, which itself creates a new reality. So – [follow] the trail,” the embassy tweeted.Spain’s constitution contains Article 155, used by Madrid to suspend Catalonia’s autonomy and violently introduce direct rule in the wake of a 2017 independence declaration.
An American Oligarch‘s Dirty Tale of Corruption
By F. William Engdahl – New Eastern Outlook – 12.06.2015
Rarely does the world get a true look inside the corrupt world of Western oligarchs and the brazen manipulations they use to enhance their fortunes at the expense of the public good. The following comes from correspondence of the Hungarian-born billionaire, now naturalized American speculator, George Soros. The hacker group CyberBerkut has published online letters allegedly written by Soros that reveal him not only as puppet master of the US-backed Ukraine regime. They also reveal his machinations with the US Government and the officials of the European Union in a scheme where, if he succeeds, he could win billions in the plunder of Ukraine assets. All, of course, would be at the expense of Ukrainian citizens and of EU taxpayers.
What the three hacked documents reveal is a degree of behind-the-scene manipulation of the most minute details of the Kiev regime by the New York billionaire.
In the longest memo, dated March 15, 2015 and marked “Confidential” Soros outlines a detailed map of actions for the Ukraine regime. Titled, “A short and medium term comprehensive strategy for the new Ukraine,” the memo from Soros calls for steps to “restore the fighting capacity of Ukraine without violating the Minsk agreement.” To do the restoring, Soros blithely notes that “General Wesley Clark, Polish General Skrzypczak and a few specialists under the auspices of the Atlantic Council [emphasis added—f.w.e.] will advise President Poroshenko how to restore the fighting capacity of Ukraine without violating the Minsk agreement.”
Soros also calls for supplying lethal arms to Ukraine and secretly training Ukrainian army personnel in Romania to avoid direct NATO presence in Ukraine. The Atlantic Council is a leading Washington pro-NATO think tank.
Notably, Wesley Clark is also a business associate of Soros in BNK Petroleum which does business in Poland.
Clark, some might recall, was the mentally-unstable NATO General in charge of the 1999 bombing of Serbia who ordered NATO soldiers to fire on Russian soldiers guarding the Pristina International Airport. The Russians were there as a part of an agreed joint NATO–Russia peacekeeping operation supposed to police Kosovo. The British Commander, General Mike Jackson refused Clark, retorting, “I’m not going to start the Third World War for you.” Now Clark apparently decided to come out of retirement for the chance to go at Russia directly.
Naked asset grab
In his March 2015 memo Soros further writes that Ukrainian President Poroshenko’s “first priority must be to regain control of financial markets,” which he assures Poroshenko that Soros would be ready to assist in: “I am ready to call Jack Lew of the US Treasury to sound him out about the swap agreement.”
He also calls on the EU to give Ukraine an annual aid sum of €11 billion via a special EU borrowing facility. Soros proposes in effect using the EU’s “AAA” top credit rating to provide a risk insurance for investment into Ukraine.
Whose risk would the EU insure?
Soros details, “I am prepared to invest up to €1 billion in Ukrainian businesses. This is likely to attract the interest of the investment community. As stated above, Ukraine must become an attractive investment destination.” Not to leave any doubt, Soros continues, “The investments will be for-profit but I will pledge to contribute the profits to my foundations. This should allay suspicions that I am advocating policies in search of personal gain. “
Anyone familiar with the history of the Soros Open Society Foundations in Eastern Europe and around the world since the late 1980’s, will know that his supposedly philanthropic “democracy-building” projects in Poland, Russia, or Ukraine in the 1990’s allowed Soros the businessman to literally plunder the former communist countries using Harvard University’s “shock therapy” messiah, and Soros associate, Jeffrey Sachs, to convince the post-Soviet governments to privatize and open to a “free market” at once, rather than gradually.
The example of Soros in Liberia is instructive for understanding the seemingly seamless interplay between Soros the shrewd businessman and Soros the philanthropist. In West Africa George Soros backed a former Open Society employee of his, Liberian President Ellen Johnson Sirleaf, giving her international publicity and through his influence, even arranging a Nobel Peace Prize for her in 2011, insuring her election as president. Before her presidency she had been well-indoctrinated into the Western free market game, studying economics at Harvard and working for the US-controlled World Bank in Washington and the Rockefeller Citibank in Nairobi. Before becoming Liberia’s President, she worked for Soros directly as chair of his Open Society Initiative for West Africa (OSIWA).
Once in office, President Sirleaf opened the doors for Soros to take over major Liberian gold and base metals assets along with his partner, Nathaniel Rothschild. One of her first acts as President was to also invite the Pentagon’s new Africa Command, AFRICOM, into Liberia whose purpose as a Liberian investigation revealed, was to “protect George Soros and Rothschild mining operations in West Africa rather than champion stability and human rights.”
Naftogaz the target
The Soros memo makes clear he has his eyes on the Ukrainian state gas and energy monopoly, Naftogaz. He writes, “The centerpiece of economic reforms will be the reorganization of Naftogaz and the introduction of market pricing for all forms of energy, replacing hidden subsidies…”
In an earlier letter Soros wrote in December 2014 to both President Poroshenko and Prime Minister Yatsenyuk, Soros openly called for his Shock Therapy: “I want to appeal to you to unite behind the reformers in your government and give your wholehearted support to a radical, ‘big bang’ type of approach. That is to say, administrative controls would be removed and the economy would move to market prices rapidly rather than gradually… Naftogaz needs to be reorganized with a big bang replacing the hidden subsidies…”
Splitting Naftogaz into separate companies could allow Soros to take control of one of the new branches and essentially privatize its profits. He already suggested that he indirectly brought in US consulting company, McKinsey, to advise Naftogaz on the privatization “big bang.”
The Puppet-Master?
The totality of what is revealed in the three hacked documents show that Soros is effectively the puppet-master pulling most of the strings in Kiev. Soros Foundation’s Ukraine branch, International Renaissance Foundation (IRF) has been involved in Ukraine since 1989. His IRF doled out more than $100 million to Ukrainian NGOs two years before the fall of the Soviet Union, creating the preconditions for Ukraine’s independence from Russia in 1991. Soros also admitted to financing the 2013-2014 Maidan Square protests that brought the current government into power.
Soros’ foundations were also deeply involved in the 2004 Orange Revolution that brought the corrupt but pro-NATO Viktor Yushchenko into power with his American wife who had been in the US State Department. In 2004 just weeks after Soros’ International Renaissance Foundation had succeeded in getting Viktor Yushchenko as President of Ukraine, Michael McFaul wrote an OpEd for the Washington Post. McFaul, a specialist in organizing color revolutions, who later became US Ambassador to Russia, revealed:
Did Americans meddle in the internal affairs of Ukraine? Yes. The American agents of influence would prefer different language to describe their activities — democratic assistance, democracy promotion, civil society support, etc. — but their work, however labeled, seeks to influence political change in Ukraine. The U.S. Agency for International Development, the National Endowment for Democracy and a few other foundations sponsored certain U.S. organizations, including Freedom House, the International Republican Institute, the National Democratic Institute, the Solidarity Center, the Eurasia Foundation, Internews and several others to provide small grants and technical assistance to Ukrainian civil society. The European Union, individual European countries and the Soros-funded International Renaissance Foundation did the same.
Soros shapes ‘New Ukraine’
Today the CyberBerkut hacked papers show that Soros’ IRF money is behind creation of a National Reform Council, a body organized by presidential decree from Poroshenko which allows the Ukrainian president to push bills through Ukraine’s legislature. Soros writes, “The framework for bringing the various branches of government together has also emerged. The National Reform Council (NRC) brings together the presidential administration, the cabinet of ministers, the Rada and its committees and civil society. The International Renaissance Foundation which is the Ukrainian branch of the Soros Foundations was the sole financial supporter of the NRC until now…”
Soros’ NRC in effect is the vehicle to allow the President to override parliamentary debate to push through “reforms,” with the declared first priority being privatization of Naftogaz and raising gas prices drastically to Ukrainian industry and households, something the bankrupt country can hardly afford.
In his letter to Poroshenko and Yatsenyuk, Soros hints that he played a key role in selection of three key non-Ukrainian ministers—Natalia Jaresko, an American ex- State Department official as Finance Minister; Aivras Abromavicius of Lithuania as Economics Minister, and a health minister from Georgia. Soros in his December 2014 letter, referring to his proposal for a “big bank” privatization of Naftogaz and price rise, states, “You are fortunate to have appointed three ‘new Ukrainian’ ministers and several natives (sic) who are committed to this approach.”
Elsewhere Soros speaks about de facto creating the impression within the EU that the current government of Yatsenyuk is finally cleaning out the notorious corruption that has dominated every Kiev regime since 1991. Creating that temporary reform illusion, he remarks, will convince the EU to cough up the €11 billion annual investment insurance fund. His March 2015 paper says that, “It is essential for the government to produce a visible demonstration (sic) during the next three months in order to change the widely prevailing image of Ukraine as an utterly corrupt country.” That he states will open the EU to make the €11 billion insurance guarantee investment fund.
While saying that it is important to show Ukraine as a country that is not corrupt, Soros reveals he has little concern when transparency and proper procedures block his agenda. Talking about his proposals to reform Ukraine’s constitution to enable privatizations and other Soros-friendly moves, he complains, “The process has been slowed down by the insistence of the newly elected Rada on proper procedures and total transparency.”
Soros suggests that he intends to create this “visible demonstration” through his initiatives, such as using the Soros-funded National Reform Council, a body organized by presidential decree which allows the Ukrainian president to push bills through Ukraine’s legislature.
George Soros is also using his new European Council on Foreign Relations think-tank to lobby his Ukraine strategy, with his council members such as Alexander Graf Lambsdorff or Joschka Fischer or Karl-Theodor zu Guttenberg, not to mention former ECB head, Jean-Claude Trichet no doubt playing a subtle role.
George Soros, now 84, was born in Hungary as a Jew, George Sorosz. Soros once boasted in a TV interview that he posed during the war as a gentile with forged papers, assisting the Horthy government to seize property of other Hungarian Jews who were being shipped to the Nazi death camps. Soros told the TV moderator, “There was no sense that I shouldn’t be there, because that was–well, actually, in a funny way, it’s just like in markets–that if I weren’t there–of course, I wasn’t doing it, but somebody else would.”
This is the same morality apparently behind Soros’ activities in Ukraine today. It seems again to matter not to him that the Ukrainian government he helped bring to power in the February 2014 US coup d’etat is riddled with explicit anti-semites and self-proclaimed neo-Nazis from the Svoboda Party and Pravy Sektor. George Soros is clearly a devotee of “public-private-partnership.” Only here the public gets fleeced to enrich private investors like Mr. Soros and friends. Cynically, Soros signs his Ukraine strategy memo, “George Soros–A self-appointed advocate of the new Ukraine, March 12, 2015.”
Evidence suggests US lied about Iranian strikes on US facilities in Iraq
By Robert Inlakesh | Press TV | January 16, 2020
During the early morning hours of January 8, 2020, Iranian strategic missile units launched a precision attack, branded ‘Operation Martyr Soleimani’, against US forces at the American-operated section of the ‘Ain al-Asad’ air base in Iraq.
The response, coming in response to the illegal assassination of General Qassem Soleimani, was a high-observable attack using ballistic missile forces – as opposed to a low-observable attack using terrain-reading cruise missiles and suicide drones.
With US forces already having been in a heightened state of alert, American radar and satellite reconnaissance would have spotted the attack within a minute of it being launched (and a six hour pre-warning of an imminent attack before that), giving the US and other coalition troops present at the base time to seek cover in hardened shelter areas. This, however, did not prevent the success of the attack which, according to primary source evidence, destroyed highly-expensive US aviation assets.
THE RESULT – U.S. FORCES ASSET LOSSES
According to the evidence that has been made available to us at this point, it is obvious that the US is lying about the extent of the damage inflicted upon its assets and infrastructure at the Ain al-Asad base.
No American media group or official Pentagon report initially released the satellite pictures shown in this report, and probably for good reason. To downplay the event (as Trump did in his official address, as did the Pentagon in its later report), they simply dismissed the damaged equipment, referring to the destroyed assets as simple “tents, a parking lot and a damaged helicopter” (per the Department of Defense).
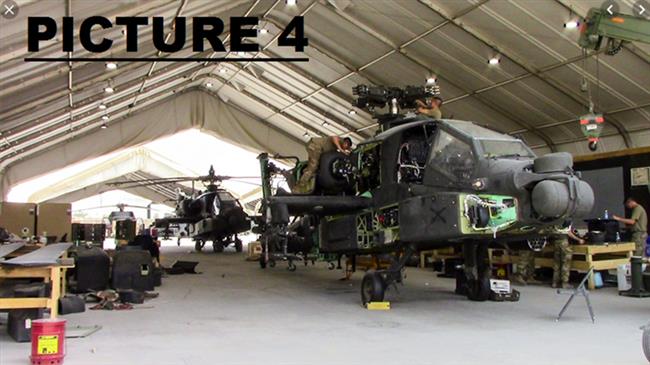
The Iranian missile attack for the most part targeted Apache (AH-64) attack helicopter shelters (refer to Picture 1). Refer to Picture 3 and Picture 4 to see what those “tent”-like Apache steel-frame shelters look like at ground level.
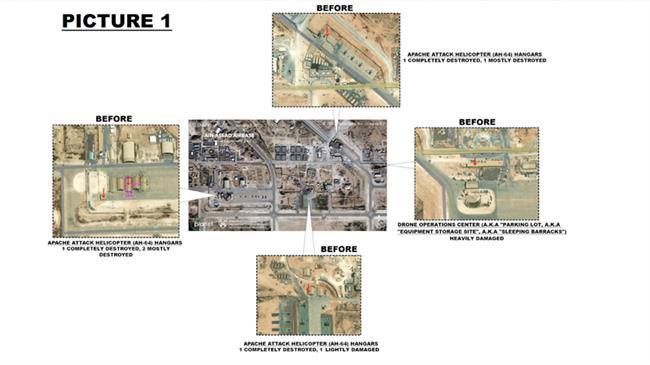
They are the standard steel-frame soft shelter design for US helicopter units based in overseas areas at second-rate airfields (such as the Ain al-Asad Base) – US helicopter units operating from old Afghan airfields are also housed in this kind of shelter design. Each one of those Apache attack helicopter shelters can house two such aircraft. With six structures of the type provably destroyed, demonstrated through the satellite images showing blackened scorch marks (suggesting assets inside them were destroyed with the shelter itself, refer to Picture 1) AND assuming each only had one Apache in them, it can be concluded that at least 6 Apache gunships were destroyed in the attack.
Recently, Danish media, citing a Danish coalition soldier who was present at the base at the time of the attack, admitted that multiple helicopters were destroyed to the point of being “split in half”.
Another Apache hangar (refer to Picture 2) was also directly struck, located to the far eastern end of the Ain al-Asad Base and destroyed. However, note that there is no scorch-blackened concrete underneath it, suggesting nothing was inside it that led to additional burning beyond the impact of the warhead itself.
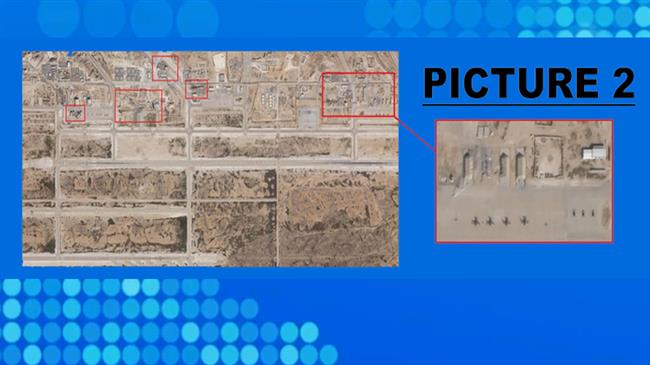
Indeed, just to the south of that destroyed hangar and the undamaged three hangars next to it, 4 Apache helicopters can be seen sitting out on the open tarmac. They were spared as they were, ironically, not being sheltered.
The official US story on the other structure targeted beyond the “tents” (i.e. Apache gunship hangars) has already changed twice – first it was called a parking lot, then an equipment storage area and now, apparently, a barracks for drone operators. Picture 1 (far right) shows the result of the attack on this structure.
It is hard to imagine that base zoning regulators within the US military would chose to place sleeping quarters right next to a strip alert (ready-to-go) aircraft parking area, itself right next to a major taxiway, given the constant noise that comes from these areas.
A more astute assessment would place this structure as an operations center, which lines up with the Iranian claim that the command site from which the Qassem Soleimani assassination operation had been coordinated, was targeted and destroyed in Iran’s retaliation strike.

Indeed, AFP recently released an exclusive report in which a US drone operator present at the Ain al-Asad Airbase, one First Sergeant Wesley Kilpatrick, admitted that airborne drones were rendered inoperable after a direct hit penetrated the base’s UAV operations center and destroyed the fiber lines which connect remote stations to satellite communication equipment(needed for drone control and visuals).
In all of this, one thing is obvious. US officials and media are stumbling over their own statements trying to cover up the extent of the damage dealt to the US-operated section of the Ain al-Asad base – in fact, going so far to cease calling the military site a US airbase (as it had been called for the last 16 years) to (all of a sudden) just an “Iraqi facility”.
THE WEAPONS USED BY IRAN
Short-range ballistic missiles (SRBM) of the upgraded Fateh-313 (range 500 km) and Qiam (range 800 km) types were launched from Western Iran towards the US-operated Ain al-Asad Base in Iraq.
Fateh-313s represent the majority of the missile type used for the attack. Their accuracy still seems to have been to within a matter of meters of their intended targets, except for two stray shots that hit the open tarmac area.
Whilst the Fateh-313 missiles use a combination of INS and electro-optical guidance, the Qiam missiles reportedly use a mix of INS, GPS and radar-mapping target acquisition. The latter method being the archaic predecessor version of DSMAC (imaging automatic target acquisition) terminal-phase guidance used in high-end ground-attack cruise missiles, such as the Tomahawk.
THE OPERATION –OTHER DETAILS
Satellite pictures show that some targeted sites were double-tapped (hit twice-over for good measure).
Initial reports from the Ain al-Asad Base claimed nearly 40 detonations in total despite the fact the number of actual warhead impacts was about fifteen, indicating that there were around two dozen cases of secondary explosions (fuel and ammo going off after being ignited).
In conclusion, according to the evidence we have available to us currently, there is no doubt that the United States has completely distorted the gravitude of Iran’s strikes. The mainstream media in the West have also seemingly refrained from acknowledging much of the damage, apart from on occasion.
Robert Inlakesh is a journalist, writer and political analyst, who has lived in and reported from the occupied Palestinian West Bank. He has written for publications such as Mint Press, Mondoweiss, MEMO, and various other outlets. He specializes in analysis of the Middle East, in particular Palestine-Israel. He also works for Press TV as a European correspondent.
Iraq denies report it has restarted joint military operations with US
Press TV – January 16, 2020
The Iraqi government has denied claims that the country’s military is resuming joint operations with the US-led coalition after Washington’s assassination of top Iranian and Iraqi commanders.
“The joint operations have not resumed and we have not given our authorization,” Major General Abdul Karim Khalaf, the spokesman for the commander-in-chief of the Iraqi armed forces, said on Thursday.
He added that the coalition did not have a permission from Baghdad to carry out any joint missions.
The remarks came after the New York Times, citing two American military officials, reported Thursday that the US had resumed the operations.
Khalaf said the Iraqi government had ordered the coalition to halt its joint operations following the US assassination of top Iranian anti-terror commander, Lieutenant General Qassem Soleimani, and Abu Mahdi al-Muhandis, the second-in-command of Popular Mobilization Units (PMU).
Last month, another US airstrike killed 25 members of PMU in the Arab country’s west.
On January 3, a US drone strike outside Baghdad airport killed General Soleimani and al-Muhandis.
Washington began the pause on January 5, two days after the strike, but furious Iraqi lawmakers voted to expel more than 5,000 US troops based in their country.
The Pentagon said it had no information with regard the the alleged resumption of joint operations with Iraqi troops.
The US-led coalition’s spokesman in Baghdad also declined to comment.
Burisma Hack Story: Attempt to Put ‘Trump’, ‘Russia’ & ‘Impeachment’ in the Same Headline?
Sputnik – January 16, 2020
The timing of the media fuss over the alleged “Russian hack” of Burisma coincides with the resumption of the impeachment process by the Senate, say American academics, suggesting that the story could be a mere distraction aimed at evoking the spectre of “Trump-Russia” collusion amid the 2020 election cycle.
Ukraine has kicked off an investigation into a suspected cyberattack by so-called “Russian military hackers” on the energy company Burisma requesting assistance from the FBI. As The New York Times claimed Monday, Fancy Bears or Advanced Persistent Threat (APT) 28, allegedly subjected the energy company to phishing attacks, citing a recent report by Area 1 Security, a California-based American cybersecurity firm.
Burisma entered the spotlight light during the Democrats-driven impeachment process against Donald Trump due to its connections with the son of presidential candidate and former Vice President Joe Biden, Hunter, who previously served on the company’s board of directors and is believed to have financially benefitted from the apparent nepotistic scheme.
Falling short of confirming whether the hackers obtained any information, the Area 1 report says that the timing of the alleged malicious activities in relation to the 2020 US elections “raises the spectre that this is an early warning of what we have anticipated since the successful cyberattacks undertaken during the 2016 US elections”, referring to unfounded allegations of Russia’s interference in the previous US presidential race and hacking of the Democratic National Committee (DNC).
Media Fuss Over Alleged Burisma Hack is ‘Distraction’
“The level of media attention given to this story in the United States is curious”, says Matthew Wilson, an associate professor of political science at Southern Methodist University. “Assuming that this hacking did, in fact, occur – and I have no reason to doubt that it did – nothing has yet come of it. No one in Russia (or elsewhere) has released anything about the Bidens gleaned from a hack of Burisma’s servers, and discussion of the motives behind the hack is entirely speculative”.
According to the professor, “one almost suspects that it is simply an attempt by some in the American media to get the words ‘Trump’, ‘Russia’, and ‘impeachment’ into the same headline” ahead of a Senate impeachment trial that is likely to commence very shortly.
For her part, Laura Wilson, a political science professor at the University of Indianapolis, does not rule out that the hacking allegations serve as distraction from two important events: the Trump impeachment and the US 2020 presidential elections.
“As the Senate takes up the question of removal of office after the House passed the impeachment resolution, and the parties and candidates prepare for the upcoming primary elections, these major events will undoubtedly play a significant role in shaping the future of our country and require attention and focus”, she says.
According to Wilson, “distractions in any way should be considered just that, distractions, and though other issues will come up, they need to be evaluated fairly and swiftly given their potential impact relative to the importance of the impeachment and election”.
It’s ‘Less Than Definitive’ That Fancy Bears Hacked Burisma
American monthly Wired noted Tuesday that “it’s still not entirely proven” that Fancy Bears did hack Burisma citing cybersecurity analysts who see Area 1’s evidence tying the alleged phishing campaign to the aforementioned hackers as “less than definitive”.
The media outlet quotes security firm ThreatConnect that shared its brief analysis of the phishing campaign’s features on Twitter concluding that “none of these characteristics are definitively indicative of APT28 activity” and that “we don’t have any specific information on how the domains have been operationalised”.
Wired added that in response to its request, Area 1 Security said it has more evidence to back up its findings but declined to share it publicly.
Area 1 Security’s belief that the hacking was conducted by “Russian military hackers” originates from earlier assumptions made by Crowdstrike, a former DNC contractor, that hacker group Fancy Bear, which supposedly broke into the DNC email servers in 2016, had something to do with Russia’s Main Intelligence Department (GRU). However, this connection has never been proven beyond a reasonable doubt. Furthermore, according to some cyber experts, the so-called “Fancy Bear” or Advanced Persistent Threat (APT) 28 could be nothing more than a collection of hacking tools originating from the dark web that can be used by virtually anyone.
On the other hand, Veteran Intelligence Professionals for Sanity (VIPS), a group of former officers from the United States Intelligence Community, has repeatedly stated that the leak of DNC files was an inside job and not an external breach into the committee’s system.
Who Targeted Ukraine Airlines Flight 752? Iran Shot It Down But There May Be More to the Story
By Philip Giraldi | American Herald Tribune | January 15, 2020
The claim that Major General Qassem Soleimani was a “terrorist” on a mission to carry out an “imminent” attack that would kill hundreds of Americans turned out to be a lie, so why should one believe anything else relating to recent developments in Iran and Iraq? To be sure, Ukraine International Airlines Flight 752 departing from Tehran’s Imam Khomeini International Airport on the morning of January 8th with 176 passengers and crew on board was shot down by Iranian air defenses, something which the government of the Islamic Republic has admitted, but there just might be considerably more to the story involving cyberwarfare carried out by the U.S. and possibly Israeli governments.
To be sure, the Iranian air defenses were on high alert fearing an American attack in the wake of the U.S. government’s assassination of Soleimani on January 3rd followed by a missile strike from Iran directed against two U.S. bases in Iraq. In spite of the tension and the escalation, the Iranian government did not shut down the country’s airspace. Civilian passenger flights were still departing and arriving in Tehran, almost certainly an error in judgment on the part of the airport authorities. Inexplicably, civilian aircraft continued to take off and land even after Flight 752 was shot down.
Fifty-seven of the passengers on the flight were Canadians of Iranian descent, leading Prime Minister Justin Trudeau to point the finger both at the Iranian government for its carelessness and also at Washington, observing angrily that the Trump Administration had deliberately and recklessly sought to “escalate tensions” with Iran through an attack near Baghdad Airport, heedless of the impact on travelers and other civilians in the region.
What seems to have been a case of bad judgements and human error does, however, include some elements that have yet to be explained. The Iranian missile operator reportedly experienced considerable “jamming” and the planes transponder switched off and stopped transmitting several minutes before the missiles were launched. There were also problems with the communication network of the air defense command, which may have been related.
The electronic jamming coming from an unknown source meant that the air defense system was placed on manual operation, relying on human intervention to launch. The human role meant that an operator had to make a quick judgment in a pressure situation in which he had only moments to react. The shutdown of the transponder, which would have automatically signaled to the operator and Tor electronics that the plane was civilian, instead automatically indicated that it was hostile. The operator, having been particularly briefed on the possibility of incoming American cruise missiles, then fired.
The two missiles that brought the plane down came from a Russian-made system designated SA-15 by NATO and called Tor by the Russians. Its eight missiles are normally mounted on a tracked vehicle. The system includes both radar to detect and track targets as well as an independent launch system, which includes an Identification Friend or Foe (IFF) system functionality capable of reading call signs and transponder signals to prevent accidents. Given what happened on that morning in Tehran, it is plausible to assume that something or someone deliberately interfered with both the Iranian air defenses and with the transponder on the airplane, possibly as part of an attempt to create an aviation accident that would be attributed to the Iranian government.
The SA-15 Tor defense system used by Iran has one major vulnerability. It can be hacked or “spoofed,” permitting an intruder to impersonate a legitimate user and take control. The United States Navy and Air Force reportedly have developed technologies “that can fool enemy radar systems with false and deceptively moving targets.” Fooling the system also means fooling the operator. The Guardian has also reported independently how the United States military has long been developing systems that can from a distance alter the electronics and targeting of Iran’s available missiles.
The same technology can, of course, be used to alter or even mask the transponder on a civilian airliner in such a fashion as to send false information about identity and location. The United States has the cyber and electronic warfare capability to both jam and alter signals relating to both airliner transponders and to the Iranian air defenses. Israel presumably has the same ability. Joe Quinn at Sott.net also notes an interested back story to those photos and video footage that have appeared in the New York Times and elsewhere showing the Iranian missile launch, the impact with the plane and the remains after the crash, to include the missile remains. They appeared on January 9th, in an Instagram account called ‘Rich Kids of Tehran‘. Quinn asks how the Rich Kids happened to be in “a low-income housing estate on the city’s outskirts [near the airport] at 6 a.m. on the morning of January 8th with cameras pointed at the right part of the sky in time to capture a missile hitting a Ukrainian passenger plane…?”
Put together the Rich Kids and the possibility of electronic warfare and it all suggests a premeditated and carefully planned event of which the Soleimani assassination was only a part. There have been riots in Iran subsequent to the shooting down of the plane, blaming the government for its ineptitude. Some of the people in the street are clearly calling for the goal long sought by the United States and Israel, i.e. “regime change.” If nothing else, Iran, which was widely seen as the victim in the killing of Soleimani, is being depicted in much of the international media as little more than another unprincipled actor with blood on its hands. There is much still to explain about the downing of Ukrainian International Airlines Flight 752.
Philip M. Giraldi is a former CIA counter-terrorism specialist and military intelligence officer who served nineteen years overseas in Turkey, Italy, Germany, and Spain. He was the CIA Chief of Base for the Barcelona Olympics in 1992 and was one of the first Americans to enter Afghanistan in December 2001. Phil is Executive Director of the Council for the National Interest, a Washington-based advocacy group that seeks to encourage and promote a U.S. foreign policy in the Middle East that is consistent with American values and interests.
Americans Beware! Russia Can Hack Your Brain, Make You Believe Joe Biden Unfit for Oval Office
By Robert Bridge | Strategic Culture Foundation | January 15, 2020
I suppose it is necessary, considering the bleak and humorless times we live in, to immediately start by acknowledging that the headline is meant as satire, what Webster defines as a form of “ridicule to expose and criticize people’s stupidity or vices, particularly in the context of contemporary politics and other topical issues.”
In other words, nyet, the Kremlin does not have a hotline to the American brain that can trigger card-carrying Democrats to enter a catatonic trance on Election Day and vote against Joe Biden, or any of the other flawless Democratic gems for that matter. By this time, especially following the release of the Mueller Report, you would think that conspiracy theories involving Russia and American democracy would have subsided; instead they’ve only escalated as the U.S. enters the hot end of the 2020 presidential election campaign.
Courtesy of Bloomberg :
“U.S. intelligence and law enforcement officials are assessing whether Russia is trying to undermine Joe Biden in its ongoing disinformation efforts with the former vice president still the front-runner in the race to challenge President Donald Trump, according to two officials familiar with the matter…
Part of the inquiry is to determine whether Russia is trying to weaken Biden by promoting controversy over his past involvement in U.S. policy toward Ukraine while his son worked for an energy company there.”
So how exactly does Russia, in a scene straight out of A Clockwork Orange, tap into the frontal lobe section of the U.S. electorate and cause them to lose all confidence in their political favorites?
“A signature trait of Russian President Vladimir Putin ‘is his ability to convince people of outright falsehoods,’ William Evanina, director of the National Counterintelligence and Security Center, said in a statement. ‘In America, [the Russians are] using social media and many other tools to inflame social divisions, promote conspiracy theories and sow distrust in our democracy and elections.’”
Yes, somehow those dastardly Russians have outsmarted the brightest and best-paid political strategists in Washington, D.C. by brandishing what amounts to some really persuasive memes over social media, and for just rubles on the dollar. The techies at Wired went so far as to call this epic assault on the fragile American cranium, “meme warfare to divide America.” By way of evidence, it cited a very creative meme that screamed, “F*CK THE ELECTIONS,” which was intended, as the ironclad argument goes, to cause a number of impressionable Americans to throw up their hands in a fit of collective exasperation and say, ‘Ok, that’s it. I’m staying at home on Election Day.’
Yes, it’s really that easy! Imagine all the money the Russians and their radical new political technologies could have saved guys like casino tycoon, Sheldon Adelson, who showered the Trump campaign with $100 million dollars.
Many of those divisive Russian messages wormed their way onto Facebook, purportedly, where God only knows how many voter brains’ turned to maggots and mush just staring at them. Yet one individual who actually recalls seeing one or two of these dangerous memes was Rob Goldman, former Vice President for Advertising on Facebook, who revealed via Twitter, another infected social media platform, some interesting information:
“Most of the coverage of Russian meddling involves their attempt to effect the outcome of the 2016 U.S. election. I have seen all of the Russian ads and I can say very definitively that swaying the election was *NOT* the main goal.”
Clearly, Goldman seems to have been under the sway of some folk Russian brainwashing technique, probably passed down from the time of Rasputin. In any case, Donald Trump himself took great satisfaction from that particular revelation, retweeting it to his millions of minions.
Incidentally, it may or may not be relevant, but Goldman retired from Facebook in October 2019 after seven years with the company.
Russia, the gift that keeps on giving
Not only have the Democrats been able to use the Russia bogeyman as their excuse for losing the White House in 2016, they are able to summon this distant nuclear power whenever they wish to curb internet freedoms, which is pretty much every day now.
Now, fun-loving memes are under attack and may soon go the way of the DoDo bird (“A small office of Russian trolls could derail 241 years of U.S. political history with a handful of dank memes and an advertising budget that would barely buy you a billboard in Brooklyn,” screamed insanely The Guardian ). At the same time, freedom of speech is getting destroyed by vapid accusations of ‘hate speech,’ which, unless used to incite violence, is a totally meaningless term used to eliminate any conversation that is undesirable to the elite.
Meanwhile, only the mainstream media these days are permitted to dabble in ‘conspiracy theories’ even as their own false narratives have contributed to the pulverization of entire nations, as was the case in Iraq, for example, which sustained a full-blown U.S. military invasion in 2003 following debunked claims that Saddam Hussein was harboring weapons of mass destruction. That was the mother of all conspiracy theories that was pushed unchallenged by the mainstream media.
So back to Joe Biden.
Do intelligent Americans really need help from Russia to prove that just maybe the former Vice President is mentally and physically unfit to stand for the White House? Probably not. From whispering sweet nothings into the ears of any female within groping distance, to sucking on his wife’s fingertips at a political rally, something just doesn’t seem altogether right upstairs with Joe Biden. So what is the real story for dragging Russia, once again, into the internal swamp pit known as Washington, D.C.?
The Bloomberg article provides a big hint: “This time around, the narrative about Biden and Ukraine is … well-publicized and being advanced by Trump, his personal attorney Rudy Giuliani and the president’s Republican allies in Congress.”
And that “narrative” has everything to do with not only the Democrats’ frozen impeachment proceedings against the U.S. leader, which promises to have major connections to Ukraine, Joe Biden and his son Hunter, and quite possibly dozens of other top Democrats. In other words, the Democrats understand that pushing ahead with impeachment could be their ultimate downfall.
Although few Americans seem to remember that back in May of 2019, Trump granted U.S. Attorney General William Barr “full and complete authority” to investigate exactly how claims that Trump was ‘conspiring with the Kremlin’ in the 2016 presidential election had originated, the Democrats certainly have not.
Their bogus ‘Russian collusion’ claim provided the rationale for a four-year-long ‘witch hunt’ that began when the Democrats, relying on the flimsy findings contained in the so-called ‘Steele dossier, managed to get approval from the FISA court to spy on the Trump campaign. Now, some top-ranking Democrats – never imagining Hillary Clinton would actually lose in 2016 – are understandably nervous as to what Barr and his assistant, federal attorney John Durham will divulge to the public in the coming months.
With so much riding on the line in 2020, is anyone surprised that Bloomberg, the news affiliate owned and operated by Democratic contender Michael Bloomberg, is now reporting “U.S. officials are warning that Russia’s election interference in 2020 could be more brazen than in the 2016 presidential race or the 2018 midterm election.”
In other words, the racist ploy used by Democrats to explain their monumental defeat in 2016 did not end with the Mueller Report. The conspiracy theory, promulgated by a media that is in effect just another branch of the Democratic National Committee, is being primed to explain not only possible criminal charges aimed at top Democrats in the coming months, but how Democrats, like Michael Bloomberg, failed once again to beat the seemingly unstoppable incumbent, Donald Trump.
Establishment Pundits Go Nuts Over New Russian Hacking Conspiracy

By Caitlin Johnstone | January 14, 2020
The New York Times reports that GRU operatives launched a successful “phishing attack” on the Ukrainian gas company at the heart of scandalous allegations about Joe Biden, and establishment pundits are falling all over themselves to tweet the hottest take on this exciting new Russia conspiracy.
The story itself fails the smell test on a number of fronts. It falsely claims that allegations of Biden’s corrupt dealings with Ukrainian officials as vice president have been “discredited”, and its only named source is a cybersecurity firm with foundational ties to the NSA and to Crowdstrike, which you may remember as the extremely shady Atlantic Council-tied company at the heart of the plot hole-riddled 2016 Russia hacking narrative (whose CEO is now a billionaire).
The article also of course lacks any hard evidence for its claims, and is of course completely silent on any details as to how the security firm knows that the alleged hackers were both (A) Russian and (B) tied to the Russian government. This is par for course with mass media news reporting on anything negative about Russia, where all journalistic standards have gone out the window and nobody suffers any professional consequences for even the most egregious misreporting on that nation.
And, naturally, liberal pundits are guzzling it down like Mike Pompeo left alone at the table with the gravy boat.
Thanks to editor of another establishment “news” organization for being so mindblowingly & transparently corrupt that even I can see through you.
Here our establishment errand boy warns that any true information about Joe & Hunter Biden’s corruption is Russian Disinformation https://t.co/YF3oLnScSd
— Jimmy Dore (@jimmy_dore) January 14, 2020
I don’t know if you’ve ever seen a man trying to run with an erection, but FYI it’s the most ridiculous-looking thing you can possibly ever witness. And the mad scramble of conservative Democrats to say something viral about this new angle on an entirely exhausted theme puts one in the mind of a whole platoon of men running completely tumescent at full sprint.
“I hope my fellow editors will think hard — really hard, a lot harder than they did in 2016 — before publishing any material hacked by the Russians,” tweeted editor-in-chief of The Daily Beast Noah Shachtman in response to the NYT report.
It is very revealing that the head of a major mainstream publication believes news outlets should sit on a story exposing the corruption of a leading presidential candidate–no matter how newsworthy–if it’s believed to have come from “the Russians”. How many major stories are being spiked for no other reason than a loyalty to the US government’s geopolitical agendas against noncompliant nations, exactly?
Yet sentiments identical to Shachtman’s are currently being bleated by like-minded pundits throughout the Twitterverse right now.
“Me and Oliver Darcy took at look at this a year ago… newsrooms hadn’t a lot to say about it. Not a lot of self-reflection, it seems,” tweeted CNN’s Donie O’Sullivan in response to Shachtman’s post. “Hackers could target the 2020 election. How will newsrooms respond if they release stolen data?”
“Russians working hard for President Trump’s reelection: mainstream media do not need to collaborate with the Russians again and breathlessly promote their non-newsworthy findings, as they did in 2016,” economist David Rothschild tweeted, without specifying his peculiar definition of “non-newsworthy”.
“Will the media run info from national security hacks as blockbuster stories like in 2016? That’s the million-dollar question,” tweeted Michigan Advance editor-in-chief Susan Demas.
This might be the most important news of the day. Russia could leak Burisma emails, and slip in some doctored emails, to harm Biden later on, if he is the Democratic nominee. The 2016 playbook all over again. https://t.co/w0p7pXjWgp
— Marshall Cohen (@MarshallCohen) January 13, 2020
A CNN reporter took it up even further, preemptively speculating based on literally nothing that any evidence of Biden’s corruption which emerges from the phishing campaign will have been “doctored” by Russia.
“Russia could leak Burisma emails, and slip in some doctored emails, to harm Biden later on, if he is the Democratic nominee,” tweeted CNN’s Marshall Cohen. “The 2016 playbook all over again.”
This insanity was seconded and then ratcheted up even further by MSNBC’s Malcolm Nance, whose main job seems to be to push the Overton window of Russia hysteria toward the craziest end of the spectrum.
“DNC 2.0,” Nance wrote. “To protect Trump the GRU will manufacture and insert Black propaganda, fake emails in a data base Burisma emails to implicate Biden and support Trump. They don’t care if you believe it … it’s all to get Trump to believe it. He’ll destroy America to win.”
DNC 2.0. To protect Trump the GRU will manufacture & insert Black propaganda, fake emails in a data base Burisma emails to implicate Biden & support Trump. They don’t care if you believe it … it’s all to get Trump to believe it. He’ll destroy America to win. #NoGreaterTraitor https://t.co/LgZeAwa9fK
— Malcolm Nance (@MalcolmNance) January 14, 2020
MSNBC analyst and former Obama administration official Richard Stengel, who has openly stated that he endorses the US government propagandizing its citizens, seized on the opportunity offered by this lawless feeding frenzy to advance a completely baseless Russiagate theory, because why the hell not?
“‘Russia, if you’re listening, hack Burisma.’ GRU has done same thing to this Ukrainian firm that they did to DNC,” tweeted Stengel. “If Trump asked Zelensky on a public call to investigate the Bidens, what do you suppose he asked Putin on a private call? Vlad, do me a favor.”
“More evidence that Putin fears Biden and is actively trying to help Trump,” added the Obama administration’s Michael McFaul. “Not good. All who believe in American sovereignty should denounce, Democrats and Republicans alike.”
“I’ll say it now: I don’t care WHAT the emails say. If he’s the guy, he’s got my vote. PERIOD,” tweeted popular #Resistance pundit Brooklyn Dad Defiant in what could generously be described as a very odd confession.
Here we go again, a Russian hacking playbook right out of 2016.
Russians hacked Burisma, and they’ll leak doctored emails on Biden if he’s the nominee.
I’ll say it now: I don’t care WHAT the emails say. If he’s the guy, he’s got my vote. PERIOD. https://t.co/qJhqNMecxR
— BrooklynDad_Defiant! (@mmpadellan) January 14, 2020
There is at this time no legitimate reason to believe that the GRU was involved in any kind of cyberattack on Burisma, let alone that it found anything worth publishing. At the moment the only information we’ve gleaned from this incident is more insight into the fact that the news media environment of the most powerful nation on earth is deeply, profoundly unhealthy, and so are the individuals operating within it.
These are the people who shape the dominant narrative. These are the thought leaders, who really do lead the way a very large sector of the population thinks. We need to bring more consciousness to how wildly dysfunctional this is.
2020 has been wild already. And all signs indicate that it’s only going to get a whole lot crazier.
How an Israeli Spy-Linked Tech Firm Gained Access to the US Gov’t’s Most Classified Networks
Graphic by Claudio Cabrera
By Whitney Webb | MintPress News | January 14, 2020
If the networks of the U.S. military, the U.S. intelligence community and a slew of other U.S. federal agencies were running the software of a company with deep ties, not only to foreign companies with a history of espionage against the U.S. but also foreign military intelligence, it would — at the very least — garner substantial media attention. Yet, no media reports to date have noted that such a scenario exists on a massive scale and that the company making such software recently simulated the cancellation of the 2020 election and the declaration of martial law in the United States.
Earlier this month, MintPress News reported on the simulations for the U.S. 2020 election organized by the company Cybereason, a firm led by former members of Israel’s military intelligence Unit 8200 and advised by former top and current officials in both Israeli military intelligence and the CIA. Those simulations, attended by federal officials from the FBI, DHS and the U.S. Secret Service, ended in disaster, with the elections ultimately canceled and martial law declared due to the chaos created by a group of hackers led by Cybereason employees.
The first installment of this three part series delved deeply into Cybereason’s ties to the intelligence community of Israel and also other agencies, including the CIA, as well as the fact that Cybereason stood to gain little financially from the simulations given that their software could not have prevented the attacks waged against the U.S.’ electoral infrastructure in the exercise.
Also noted was the fact that Cybereason software could be potentially used as a backdoor by unauthorized actors, a possibility strengthened by the fact that the company’s co-founders all previously worked for firms that have a history of placing backdoors into U.S. telecommunications and electronic infrastructure as well as aggressive espionage targeting U.S. federal agencies.
The latter issue is crucial in the context of this installment of this exclusive MintPress series, as Cybereason’s main investors turned partners have integrated Cybereason’s software into their product offerings. This means that the clients of these Cybereason partner companies, the U.S. intelligence community and military among them, are now part of Cybereason’s network of more than 6 million endpoints that this private company constantly monitors using a combination of staff comprised largely of former intelligence operatives and an AI algorithm first developed by Israeli military intelligence.
Cybereason, thus far, has disclosed the following groups as lead investors in the company: Charles River Ventures (CRV), Spark Capital, Lockheed Martin and SoftBank. Charles River Ventures (CRV) was among the first to invest in Cybereason and has been frequently investing in other Israeli tech start-ups that were founded by former members of the elite Israeli military intelligence Unit 8200 over the last few years. Spark Capital, based in California, appears to have followed CRV’s interest in Cybereason since the venture capitalist who co-founded Spark and led its investment in Cybereason is a former CRV partner who still has close ties to the firm.
While CRV and Spark Capital seem like just the type of investors a company like Cybereason would attract given their clear interest in similar tech start-ups coming out of Israel’s cyber sector, Cybereason’s other lead investors — Lockheed Martin and SoftBank — deserve much more attention and scrutiny.
Cybereason widely used by US Government, thanks to Lockheed
“A match made in heaven,” trumpeted Forbes at the news of the Lockheed Martin-Cybereason partnership, first forged in 2015. The partnership involved not only Lockheed Martin becoming a major investor in the cybersecurity company but also in Lockheed Martin becoming the largest conduit providing Cybereason’s software to U.S. federal and military agencies.
Indeed, as Forbes noted at the time, not only did Lockheed invest in the company, it decided to integrate Cybereason’s software completely into its product portfolio, resulting in a “model of both using Cybereason internally, and selling it to both public and private customers.”
Cybereason CEO and former offensive hacker for Israeli military intelligence — Lior Div — said the following of the partnership:
Lockheed Martin invested in Cybereason’s protection system after they compared our solution against a dozen others from the top industry players. The US firm was so impressed with the results they got from Cybereason that they began offering it to their own customers – among them most of the top Fortune 100 companies, and the US federal government. Cybereason is now the security system recommended by LM to its customers for protection from a wide (sic) malware and hack attacks.”
Rich Mahler, then-director of Commercial Cyber Services at Lockheed Martin, told Defense Daily that the company’s decision to invest in Cybereason, internally use its software, and include the technology as part of Lockheed Martin’s cyber solutions portfolio were all “independent business decisions but were all coordinated and timed with the transaction.”
How independent each of those decisions actually was is unclear, especially given the timing of Lockheed Martin’s investment in Cybereason, whose close and troubling ties to Israeli intelligence as well as the CIA were noted in the previous installment of this investigative series. Indeed, about a year prior to their investment in the Israeli military intelligence-linked Cybereason, Lockheed Martin opened an office in Beersheba, Israel, where the IDF has its “cyberhub”. The office is focused not on the sales of armaments, but instead on technology.
Marilyn Hewson, Lockheed Martin’s CEO, said the following during her speech that inaugurated the company’s Beersheba office:
The consolidation of IDF Technical Units to new bases in the Negev Desert region is an important transformation of Israel’s information technology capability… We understand the challenges of this move. Which is why we are investing in the facilities and people that will ensure we are prepared to support for these critical projects. By locating our new office in the capital of the Negev we are well positioned to work closely with our Israeli partners and stand ready to: accelerate project execution, reduce program risk and share our technical expertise by training and developing in-country talent.”
Beersheba not only houses the IDF’s technology campus, but also the Israel National Cyber Directorate, which reports directly to Israel’s Prime Minister, as well as a high-tech corporate park that mostly houses tech companies with ties to Israel’s military intelligence apparatus. The area has been cited in several media reports as a visible indicator of the public-private merger between Israeli technology companies, many of them started by Unit 8200 alumni, and the Israeli government and its intelligence services. Lockheed Martin quickly became a key fixture in the Beersheba-based cyberhub.
Not long before Lockheed began exploring the possibility of opening an office in Beersheba, the company was hacked by individuals who used tokens tied to the company, RSA Security, whose founders have ties to Israel’s defense establishment and which is now owned by Dell, a company also deeply tied to the Israeli government and tech sector. The hack, perpetrated by still unknown actors, may have sparked Lockheed’s subsequent interest in Israel’s cybersecurity sector.
Soon after opening its Beersheba office, Lockheed Martin created its Israel subsidiary, Lockheed Martin Israel. Unlike many of the company’s other subsidiaries, this one is focused exclusively on “cybersecurity, enterprise information technology, data centers, mobile, analytics and cloud” as opposed to the manufacture and design of armaments.
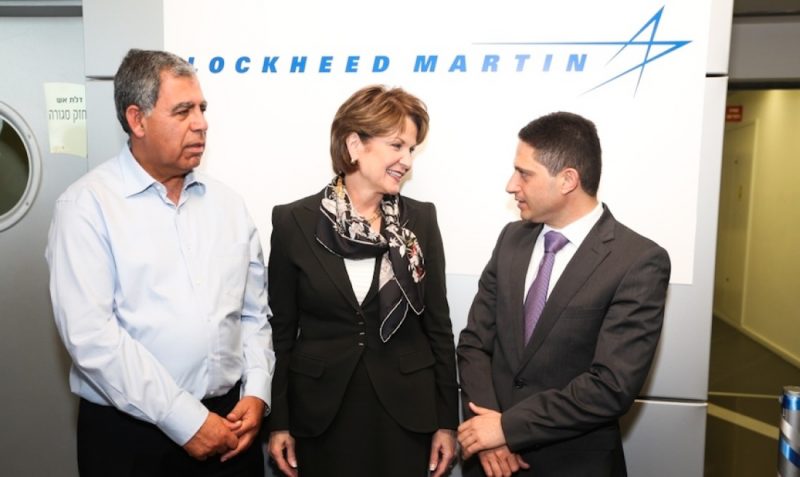
Marillyn Hewson, center, poses with Israeli gov. officials at the opening of Lockheed Martin’s facility in Beersheba. Photo | Diego Mittleberg
Haden Land, then-vice president of research and technology for Lockheed Martin, told the Wall Street Journal that the creation of the subsidiary was largely aimed at securing contracts with the IDF and that the company’s Israel subsidiary would soon be seeking partnership and investments in pursuit of that end. Land oversaw the local roll-out of the company’s Israel subsidiary while concurrently meeting with Israeli government officials. According to the Journal, Land “oversees all of Lockheed Martin’s information-systems businesses, including defense and civilian commercial units” for the United States and elsewhere.
Just a few months later, Lockheed Martin partnered and invested in Cybereason, suggesting that Lockheed’s decision to do so was aimed at securing closer ties with the IDF. This further suggests that Cybereason still maintains close ties to Israeli military intelligence, a point expounded upon in great detail in the previous installment of this series.
Thus, it appears that not only does Lockheed Martin use Cybereason’s software on its own devices and on those it manages for its private and public sector clients, but it also decided to use the company’s software in this way out of a desire to more closely collaborate with the Israeli military in matters related to technology and cybersecurity.
The cozy ties between Lockheed Martin, one of the U.S. government’s largest private contractors, and the IDF set off alarm bells, then and now, for those concerned with U.S. national security. Such concern makes it important to look at the extent of Cybereason’s use by federal and military agencies in the United States through their contracting of Lockheed Martin’s Information Technology (IT) division. This is especially important considering Israeli military intelligence’s history of using espionage, blackmail and private tech companies against the U.S. government, as detailed here.
While the exact number of U.S. federal and military agencies using Cybereason’s software is unknown, it is widespread, with Lockheed Martin’s IT division as the conduit. Indeed, Lockheed Martin was the number one IT solutions provider to the U.S. federal government up until its IT division was spun off and merged with Leidos Holdings. As a consequence, Leidos is now the largest IT provider to the U.S. government and is also directly partnered with Cybereason in the same way Lockheed Martin was. Even after its IT division was spun off, Lockheed Martin continues to use Cybereason’s software in its cybersecurity work for the Pentagon and still maintains a stake in the company.
The Leidos-Lockheed Martin IT hybrid provides a litany of services to the U.S. military and U.S. intelligence. As investigative journalist Tim Shorrock noted for The Nation, the company does “everything from analyzing signals for the NSA to tracking down suspected enemy fighters for US Special Forces in the Middle East and Africa” and, following its merger with Lockheed and consequential partnership with Cybereason, became “the largest of five corporations that together employ nearly 80 percent of the private-sector employees contracted to work for US spy and surveillance agencies.” Shorrock also notes that these private-sector contractors now dominate the mammoth U.S. surveillance apparatus, many of them working for Leidos and — by extension — using Cybereason’s software.
Leidos’ exclusive use of Cybereason software for cybersecurity is also relevant for the U.S. military since Leidos runs a number of sensitive systems for the Pentagon, including its recently inked contract to manage the entire military telecommunications infrastructure for Defense Information Systems Agency (DISA). In addition to maintaining the military telecom network, Cybereason is also directly partnered with World Wide Technologies (WWT) as of this past October. WWT manages cybersecurity for the U.S. Army, maintains DISA’s firewalls and data storage as well as the U.S. Air Force’s biometric identification system. WWT also manages contracts for NASA, itself a frequent target of Israeli government espionage, and the U.S. Navy. WWT’s partnership is similar to the Lockheed/Leidos partnership in that Cybereason’s software is now completely integrated into its portfolio, giving the company full access to the devices on all of these highly classified networks.
Many of these new partnerships with Cybereason, including its partnership with WWT, followed claims made by members of Israel’s Unit 8200 in 2017 that the popular antivirus software of Kaspersky Labs contained a backdoor for Russian intelligence, thereby compromising U.S. systems. The Wall Street Journal was the first to report on the alleged backdoor but did not mention the involvement of Unit 8200 in identifying it, a fact revealed by the New York Times a week later.
Notably, none of the evidence Unit 8200 used to blame Kaspersky has been made public and Kaspersky noted that it was actually Israeli hackers that had been discovered planting backdoors into its platform prior to the accusation levied against Kaspersky by Unit 8200. As the New York Times noted:
Investigators later discovered that the Israeli hackers had implanted multiple back doors into Kaspersky’s systems, employing sophisticated tools to steal passwords, take screenshots, and vacuum up emails and documents.”
Unit 8200’s claims ultimately led the U.S. government to abandon Kaspersky’s products entirely in 2018, allowing companies like Cybereason (with its own close ties to Unit 8200) to fill the void. Indeed, the very agencies that banned Kaspersky now use cybersecurity software that employs Cybereason’s EDR system. No flags have been raised about Cybereason’s own collaboration with the very foreign intelligence service that first pointed the finger at Kaspersky and that previously sold software with backdoors to sensitive U.S. facilities.
SoftBank, Cybereason and the Vision Fund
While its entry into the U.S. market and U.S. government networks is substantial, Cybereason’s software is also run throughout the world on a massive scale through partnerships that have seen it enter into Latin American and European markets in major ways in just the last few months. It has also seen its software become prominent in Asia following a partnership with the company Trustwave. Much of this rapid expansion followed a major injection of cash courtesy of one of the company’s biggest clients and now its largest investor, Japan’s SoftBank.
SoftBank first invested in Cybereason in 2015, the same year Lockheed Martin initially invested and partnered with the firm. It was also the year that SoftBank announced its intention to invest in Israeli tech start-ups. SoftBank first injected $50 million into Cybereason, followed by an additional $100 million in 2017 and $200 million last August. SoftBank’s investments account for most of the money raised by the company since it was founded in 2012 ($350 million out of $400 million total).
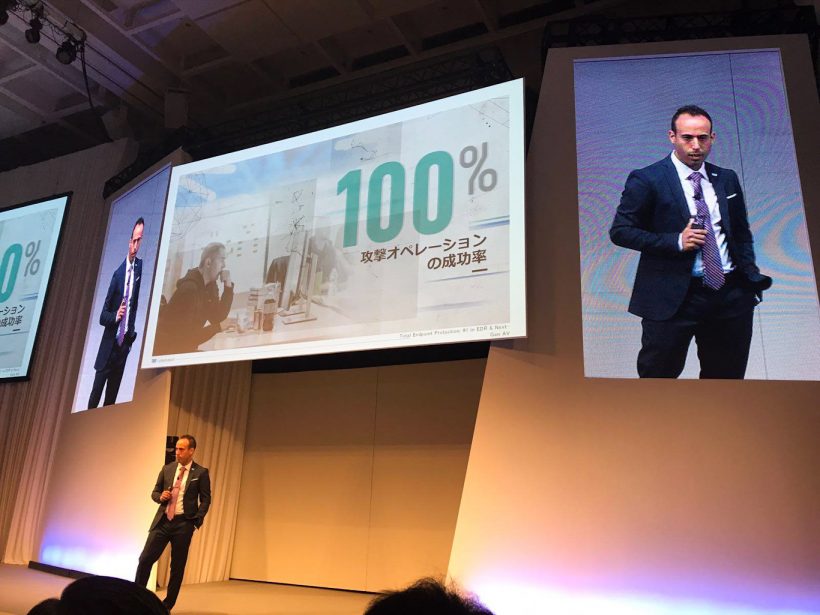
Cybereason CEO Lior Div speaks at a SoftBank event in Japan, July 21, 2017. Photo | Cybereason
Prior to investing, Softbank was a client of Cybereason, which Ken Miyauchi, president of SoftBank, noted when making the following statement after Softbank’s initial investment in Cybereason:
SoftBank works to obtain cutting edge technology and outstanding business models to lead the Information Revolution. Our deployment of the Cybereason platform internally gave us firsthand knowledge of the value it provides, and led to our decision to invest. I’m confident Cybereason and SoftBank’s new product offering will bring a new level of security to Japanese organizations.”
SoftBank — one of Japan’s largest telecommunications companies — not only began to deploy Cybereason internally but directly partnered with it after investing, much like Lockheed Martin had done around the same time. This partnership resulted in SoftBank and Cybereason creating a joint venture in Japan and Cybereason creating partnerships with other tech companies acquired by SoftBank, including the U.K.’s Arm, which specializes in making chips and management platforms for Internet of Things (IoT) devices.
SoftBank’s interest in Cybereason is significant, particularly in light of Cybereason’s interest in the 2020 U.S. election, given that SoftBank has significant ties to key allies of President Trump and even the president himself.
Indeed, SoftBank’s Masayoshi Son was among the first wave of international business leaders who sought to woo then-president-elect Trump soon after the 2016 election. Son first visited Trump Tower in December 2016 and announced, with Trump by his side in the building’s lobby, that SoftBank would invest $50 billion in the U.S. and create 50,000 jobs. Trump subsequently claimed on Twitter that Son had only decided to make this investment because Trump had won the election.
Son told reporters at the time that the investment would come from a $100 billion fund that would be created in partnership with Saudi Arabia’s sovereign wealth fund as well as other investors. “I just came to celebrate his new job. I said, ‘This is great. The US will become great again,’” Son said, according to reports.
Then, in March of 2017, Son sent top SoftBank executives to meet with senior members of Trump’s economic team and, according to the New York Times, “the SoftBank executives said that because of a lack of advanced digital investments, the competitiveness of the United States economy was at risk. And the executives made the case, quite strongly, that Mr. Son was committed to playing a major role in addressing this issue through a spate of job-creating investments.” Many of SoftBank’s investments and acquisitions in the U.S. since then have focused mainly on artificial intelligence and technology with military applications, such as “killer robot” firm Boston Dynamics, suggesting Son’s interest lies more in dominating futuristic military-industrial technologies than creating jobs for the average American.
After their initial meeting, Trump and Son met again a year later in June 2018, with Trump stating that “His [Son’s] $50 billion turned out to be $72 billion so far, he’s not finished yet.” Several media reports have claimed that Son’s moves since Trump’s election have sought to “curry favor” with the President.
Through the creation of this fund alongside the Saudis, SoftBank has since become increasingly intertwined with Saudi Crown Prince Muhammad bin Salman (MBS), a key ally of President Trump in the Middle East known for his authoritarian crackdowns on Saudi elites and dissidents alike. The ties between Saudi Arabia and SoftBank became ever tighter when MBS took the reins in the oil kingdom and after SoftBank announced the launch of the Vision Fund in 2016. SoftBank’s Vision Fund is a vehicle for investing in hi-tech companies and start-ups and its largest shareholder is the Public Investment Fund of Saudi Arabia. Notably, Son decided to launch the Vision Fund in Riyadh during President Trump’s first official visit to the Gulf Kingdom.
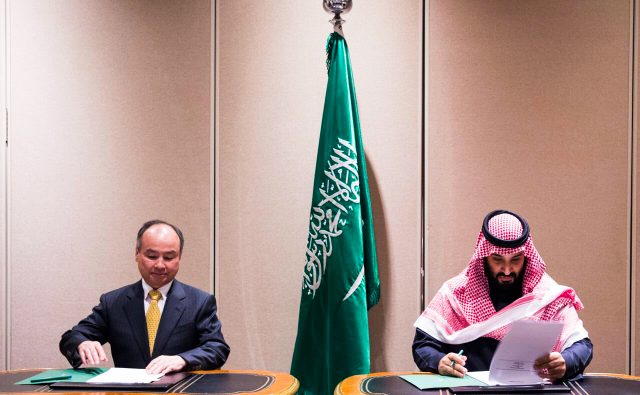
Masayoshi Son, left, signs a deal related to the Vision Fund with Bin Salman in March 2018. Photo | SPA
In addition, the Mubadala Investment Company, a government fund of the United Arab Emirates (UAE), gave $15 billion to the Vision Fund. UAE leadership also share close ties to the Trump administration and MBS in Saudi Arabia.
As a consequence, SoftBank’s Vision Fund is majority funded by two Middle Eastern authoritarian governments with close ties to the U.S. government, specifically the Trump administration. In addition, both countries have enjoyed the rapid growth and normalization of ties with the state of Israel in recent years, particularly following the rise of current Saudi Crown Prince Muhammad bin Salman and Jared Kushner’s rise to prominence in his father-in-law’s administration. Other investments in the Vision Fund have come from Apple, Qualcomm and Oracle’s Larry Ellison, all tech companies with strong ties to Israel’s government.
The Saudi and Emirati governments’ links to the Vision Fund are so obvious that even mainstream outlets like the New York Times have described them as a “front for Saudi Arabia and perhaps other countries in the Middle East.”
SoftBank also enjoys close ties to Jared Kushner, with Fortress Investment Group lending $57 million to Kushner Companies in October 2017 while it was under contract to be acquired by SoftBank. As Barron’s noted at the time:
When SoftBank Group bought Fortress Investment Group last year, the Japanese company was buying access to a corps of seasoned investors. What SoftBank also got is a financial tie to the family of President Donald Trump’s senior advisor and son-in-law, Jared Kushner.”
According to The Real Deal, Kushner Companies obtained the financing from Fortress only after its attempts to obtain funding through the EB-5 visa program for a specific real estate venture were abandoned after the U.S. Attorney and the Securities and Exchange Commission began to investigate how Kushner Companies used the EB-5 investor visa program. A key factor in the opening of that investigation was Kushner Companies’ representatives touting Jared Kushner’s position at the White House when talking to prospective investors and lenders.
SoftBank also recently came to the aid of a friend of Jared Kushner, former CEO of WeWork Adam Neumann. Neumann made shocking claims about his ties to both Kushner and Saudi Arabia’s MBS, even asserting that he had worked with both in creating Kushner’s long-awaited and controversial Middle East “peace plan” and claimed that he, Kushner and MBS would together “save the world.” Neumann previously called Kushner his “mentor.” MBS has also discussed on several occasions his close ties with Kushner and U.S. media reports have noted the frequent correspondence between the two “princelings.”
Notably, SoftBank invested in Neumann’s WeWork using money from the Saudi-dominated Vision Fund and later went on to essentially bail the company out after its IPO collapse and Neumann was pushed out. SoftBank’s founder, Masayoshi Son, had an odd yet very close relationship with Neumann, perhaps explaining why Neumann was allowed to walk with $1.7 billion after bringing WeWork to the brink of collapse. Notably, nearly half of SoftBank’s approximately $47 billion investments in the U.S. economy since Trump’s election, went to acquiring and then bailing out WeWork. It is unlikely that such a disastrous investment resulted in the level of job creation that Son had promised Trump in 2016.
Given that it is Cybereason’s top investor and shareholder by a large margin, SoftBank’s ties to the Trump administration and key allies of that administration are significant in light of Cybereason’s odd interest in 2020 U.S. election scenarios that end with the cancellation of this year’s upcoming presidential election. It goes without saying that the cancellation of the election would mean a continuation of the Trump administration until new elections would take place.
Furthermore, with Cybereason’s close and enduring ties to Israeli military intelligence now well-documented, it is worth asking if Israeli military intelligence would consider intervening in 2020 if the still-to-be-decided Democratic contender was strongly opposed to Israeli government policy, particularly Israel’s military occupation of Palestine. This is especially worth considering given revelations that sexual blackmailer and pedophile Jeffrey Epstein, who targeted prominent U.S. politicians, mostly Democrats, was in the employ of Israeli military intelligence.
Notably, Cybereason’s doomsday election scenarios involved the weaponization of deep fakes, self-driving cars and the hacking Internet of Things devices, with all of those technologies being pioneered and perfected — not by Russia, China or Iran — but by companies directly tied to Israeli intelligence, much like Cybereason itself. These companies, their technology and Cybereason’s own work creating the narrative that U.S. rival states seek to undermine the U.S. election in this way, will all be discussed in the conclusion of MintPress’ series on Cybereason and its outsized interest in the U.S. democratic process.
Whitney Webb is a MintPress News journalist based in Chile. She has contributed to several independent media outlets including Global Research, EcoWatch, the Ron Paul Institute and 21st Century Wire, among others. She has made several radio and television appearances and is the 2019 winner of the Serena Shim Award for Uncompromised Integrity in Journalism.
Iran Jet Disaster Setup
By Soraya Sepahpour-Ulrich and Finian Cunningham – Sputnik – 13.01.2020
The 19-second video published by the New York Times last week showing the moment an Iranian missile hit a passenger jet has prompted much social media skepticism.
Questions arise about the improbable timing and circumstances of recording the precise moment when the plane was hit.
The newspaper ran the splash story on January 9, the day after a Ukrainian airliner was brought down near Tehran. It was headlined: ‘Video Shows Ukrainian Plane Being Hit Over Iran’. All 176 people onboard were killed. Two days later, the Iranian military admitted that one of its air defense units had fired at the plane in the mistaken belief that it was an incoming enemy cruise missile.
“A smoking gun” was how NY Times’ journalist Christiaan Triebert described the video in a tweet. Triebert works in the visual investigations team at the paper. In the same tweet, he thanked – “a very big shout out” – to an Iranian national by the name of Nariman Gharib “who provided it [the video] to the NY Times, and the videographer, who would like to remain anonymous”.
The anonymous videographer is the person who caught the 19-second clip which shows a missile striking Flight PS752 shortly after take-off from Tehran’s Imam Khomenei airport at around 6.15 am. This person, who remains silent during the filming while smoking a cigarette (the smoke briefly wafts over the screen), is standing in the suburb of Parand looking northwest. His location was verified by the NY Times using satellite data. The rapid way the newspaper’s technical resources were marshaled raises a curious question about how a seemingly random video submission was afforded such punctilious attention.
But the big question which many people on social media are asking is: why was this “videographer” standing in a derelict industrial area outside Tehran at around six o’clock in the morning with a mobile phone camera training on a fixed angle to the darkened sky? The airliner is barely visible, yet the sky-watching person has the camera pointed and ready to film a most dramatic event, seconds before it happened. That strongly suggests, foreknowledge.
Given that something awful has just been witnessed it is all the more strange that the person holding the camera remains calm and unshaken. There is no audible expression of shock or even the slightest disquiet.
Turns out that Nariman Gharib, the guy who received the video and credited by the NY Times for submitting it, is a vociferous anti-Iranian government dissident who does not live in Iran. He ardently promotes regime change in his social media posts.
Christiaan Triebert, the NY Times’ video expert, who collaborated closely with Gharib to get the story out within hours of the incident, previously worked as a senior investigator at Bellingcat. Bellingcat calls itself an independent online investigative journalism project, but numerous critics accuse it of being a media adjunct to Western military intelligence. Bellingcat has been a big proponent of media narratives smearing the Russian and Syrian governments over the MH17 shoot-down in Ukraine in 2014 and chemical weapons attacks.
In the latest shoot-down of the airliner above Tehran, the tight liaison between a suspiciously placed anonymous videographer on the ground and an expatriate Iranian dissident who then gets the prompt and generous technical attention of the NY Times suggests a level of orchestration, not, as we are led to believe, a random happenstance submission. More sinisterly, the fateful incident was a setup.
It seems reasonable to speculate that in the early hours of January 8 a calamitous incident was contrived to happen. The shoot-down occurred only four hours after Iran attacked two US military bases in Iraq. Those attacks were in revenge for the American drone assassination on January 3 of Iran’s top military commander, Maj. General Qassem Soleimani.
Subsequently, Iranian air-defense systems were on high alert for a possible counter-strike by US forces. Several reports indicate that the Iranian defense radars were detecting warnings of incoming enemy warplanes and cruise missiles on the morning of 8 January. It does seem odd why the Iranian authorities did not cancel all commercial flights out of Tehran during that period. Perhaps because civilian airliners can normally be differentiated by radar and other signals from military objects.
However, with the electronic warfare (EW) technology that the United States has developed in recent years it is entirely feasible for enemy military radars to be “spoofed” by phantom objects. One such EW developed by the Pentagon is Miniature Air-Launched Decoy (MALD) which can create deceptive signals on enemy radar systems of incoming warheads.
What we contend therefore is this: the Americans exploited a brink-of-war scenario in which they anticipated Iranian air-defense systems to be on a hair-trigger. Add to this tension an assault by electronic warfare on Iranian military radars in which it would be technically feasible to distort a civilian airliner’s data as an offensive target. The Iranian military has claimed this was the nature of the shoot-down error. It seems plausible given the existing electronic warfare used by the Pentagon.
It’s a fair, albeit nefarious, bet that the flight paths out of Tehran were deliberately put in an extremely dangerous position by the malicious assault from American electronic warfare. A guy placed on the ground scoping the outward flight paths – times known by publicly available schedules – would be thus on hand to catch the provoked errant missile shot.
The shoot-down setup would explain why Western intelligence were so quick to confidently assert what happened, contradicting Iran’s initial claims of a technical onboard plane failure.
The disaster has gravely undermined the Iranian government, both at home and around the world. Protests have erupted in Iran denouncing the authorities and the Islamic Revolutionary Guards Corp for “lying” about the crash. Most of the 176 victims were Iranian nationals. The anger on the streets is being fueled by the public comments of Western leaders like Donald Trump, who no doubt see the clamor and recriminations as an opportunity to push harder for regime change in Iran.
Fishy Findings: 100% Replication Failure
Eight fish studies were double-checked. Not one was accurate.

By Donna Laframboise | Big Picture News | January 13, 2020
Science proves… Science says… Research shows…
Every week, the above phrases are employed by TV personalities, newspaper journalists, coworkers, friends, and family. When these phrases are uttered, certain ideas get elevated above the fray, enthroned on a pedestal.
Science has spoken. Who are you to be arguing with SCIENCE?
The problem, of course, is that scientific research is conducted by human beings. Who not only make mistakes, but are susceptible to peer pressure, group think, intellectual fads, and noble cause corruption.
The fallibility of ‘science’ is splendidly illustrated by a paper published last week in Nature. It concludes that not one, not two, but eight previously published studies about how climate change affects the behaviour of coral reef fish are unsound.
When a second team of researchers conducted the same experiments, the results were startlingly different. Here’s a quote from the abstract in Nature:
we comprehensively and transparently show that… ocean acidification levels have negligible effects on important behaviours of coral reef fishes… we additionally show that … [results] that have been reported in several previous studies are highly improbable. [bold added]
Extending back to 2010, many of these studies were highly publicized at the time they appeared. Physicist Peter Ridd points out they were all produced by Australia’s James Cook University. Ridd, remember, was fired by James Cook after raising concerns about research quality.
Responsibility appears to lie squarely with ecologist Philip Mundy, who investigates “the effects of climate change on reef fish populations” via “a range of laboratory and field-based experiments.” Thanks to Mundy’s team, a good chunk of what the world thinks it knows about coral reef fish and climate change has now been shown to be dead wrong.
Zero out of eight. How many other James Cook research papers should we be taking seriously?
To be continued…
Featured Video
Can the U.S. Afford to Annihilate Iran?
or go to
Aletho News Archives – Video-Images
Book Review
The Genetic Deception — now in paperback (Second Edition)
Lies are Unbekoming | October 2, 2026
The genes the field promised were never there.
The genetic story of disease is a cover story.
The twenty-first century runs on it. Paediatric clinics. Cancer centres. Forensic laboratories. Family-planning counsel. It is used to explain illness, to assign blame, to foreclose questions. It protects the industries whose products and practices are what actually caused the harm.
It isn’t true.
In 2010, Jonathan Latham and Allison Wilson looked at over seven hundred genome-wide association studies covering some eighty common diseases. The genes the field had promised were not there. The field invented a term, “missing heritability”, to explain the absence, and has quietly worked to bury the finding ever since.
The Genetic Deception is a book about what Latham and Wilson found. What the field did with it. And what the public was told instead. … continue
Blog Roll
 Aletho News
- US increasing Middle East military buildup – AP
- Flydubai scenario: Netanyahu’s plot to drag US to war with Iran, stay in power
- The Genetic Deception — now in paperback (Second Edition)
- Can the U.S. Afford to Annihilate Iran? /Seyed M. Marandi
- Elmo Sold mRNA Jabs to Your Toddler. Now They Are “Off-Label.”
- British state targets Palestine Action with yet another crooked trial
- Americans are paying the price to preserve Israel’s nuclear hegemony
- Resistance factions are necessary to ensure a permanent US Iraq withdrawal
- How Israel destabilizes the Middle East: Denying sovereignty and the right to exist
- Europe’s Establishment Is Embracing War – and Losing Voters
- If Americans Knew
- Israeli Soldiers Abduct At Least 22 Across Occupied West Bank
- Eight Palestinians Killed in Israeli Attacks on Gaza
- Israeli former leaders and security chiefs threaten legal action over ‘Jewish terrorism’
- Israel map in LA Times ad includes all land from the river to the sea
- Inside Lebanon’s 200-page dossier on Israeli war crimes
- Flydubai, genocide, settler violence, Trump abuse of power to deport – Daily Update
- Counting Antisemitic Incidents: What the ADL Audit Reveals — and Obscures
- Mamdani releases plan to combat antisemitism and hate crimes in New York City
- Iran’s Revolutionary Guards Publish Letter to the American People
- DMFI launches $1 million ad campaign supporting Virginia’s Elaine Luria
- No Tricks Zone
- Green Energy Debacle: German Expert Professor Fritz Vahrenholt Warns Of Severe Economic And Social Consequences
- Two More Paleo Reconstructions Affirm Meters-Higher Sea Levels Across Ireland, Brazil 7000-6000 Years Ago
- New Study: Earth And Venus Surface Warmth Largely Explained By Convection And Lapse Rate, Not CO2 Or Radiation
- 2025 Nature Paper Claiming Worsening Global Drought Gets RETRACTED …Heavily Flawed
- New Study: ‘Global Drought Shows No Detectable Recent Acceleration Under Climate Warming’
- Economic Masterminds: German Socialists Suggest Taxing Productivity Gains Stemming From Using AI
- The South China Sea Has Not Been Cooperating With The Climate Change Narrative
- Energy Crisis: Germany Enters Heating Season With Historically Low Gas Reserve Fill Levels
- New Study: The Antarctic Ice Sheet Gained Mass From 2020-2024 Due To Staggering Snow And Ice Accumulation
- Study: Ocean Heating Rates From Thousands Of Years Ago ‘Dwarf’ Modern Ocean Heating Rates

