Pro-Israel news outlets ran ‘deepfake’ op-eds in ‘new disinformation frontier’
MEMO | July 20, 2020
Pro-Israel news agencies have run “deepfake” op-eds, in what is said to be “a new disinformation frontier”. Details of the “hyper-realistic forgery” were uncovered by a Reuters report this week, which uncovered the mystery around the identity of Oliver Taylor.
Taylor has been writing for a number of well-known publications, including Israel National News, the Jerusalem Post, and the Times of Israel. However, his article in the US Jewish newspaper the Algemeiner, which accused a London based academic Mazen Masri and his wife, Palestinian rights campaigner Ryvka Barnard, of being “known terrorist sympathizers”, exposed his true identity.
Mystified by Taylor’s accusation, Masri and Barnard alerted Reuters to their suspicion over the anti-Palestinian writer. The senior lecturer in law said when he pulled up Taylor’s profile photo, he couldn’t put his finger on it, but he explained that something about the young man’s face “seemed off”.
It seems as though Masri had drawn the ire of Taylor over his work in late 2018 when the lecturer helped launch a lawsuit against the Israeli surveillance company NSO on behalf of alleged Mexican victims of the company’s phone hacking technology. The spyware company has been accused of being “deeply involved” in carrying out mobile phone hacks of 1,400 of its users.
Taylor’s identity was finally uncovered. Rather than being a real person, Taylor appears to be a “deepfake”, or a hyper-realistic forgery, created in part to criticise Mazen. Reuters interviewed six experts who conclude that it had the characteristics of forgery that would not be detectable to the naked eye.
In their report raising concerns over “the marriage of deepfakes and disinformation”, the Reuters report warned deepfakes like Taylor are “dangerous” because they undermined public discourse.
Taylor is just one of several deepfakes. Earlier this month, the Daily Beast, reported that 46 conservative news outlets, including some reporting on the Jewish community, were duped into publishing Middle East “hot takes” by 19 non-existent authors as part of a massive propaganda campaign that appears to have started in July 2019.
Only a few of the news outlets covering Israel are said to have removed articles that later turned out to be deepfakes.
Powell & Iraq—Regime Change, Not Disarmament: The Fundamental Lie
By Scott Ritter – Consortium News – July 18, 2020
The New York Times Magazine has published a puff piece soft-peddling former Secretary of State Colin Powell’s role in selling a war on Iraq to the UN Security Council using what turned out to be bad intelligence. “Colin Powell Still Wants Answers” is the title of the article, written by Robert Draper. “The analysts who provided the intelligence,” a sub-header to the article declares, “now say it was doubted inside the CIA at the time.”
Draper’s article is an extract from a book, To Start a War: How the Bush Administration Took America into Iraq, scheduled for publication later this month. In the interest of full disclosure, I was approached by Draper in 2018 about his interest in writing this book, and I agreed to be interviewed as part of his research. I have not yet read the book, but can note that, based upon the tone and content of his New York Times Magazine article, my words apparently carried little weight.
Regime Change, Not WMD
I spent some time articulating to Draper my contention that the issue with Saddam Hussein’s Iraq was never about weapons of mass destruction (WMD), but rather regime change, and that everything had to be viewed in the light of this reality—including Powell’s Feb. 5, 2003 presentation before the UN Security Council. Based upon the content of his article, I might as well have been talking to a brick wall.
Powell’s 2003 presentation before the council did not take place in a policy vacuum. In many ways, the March 2003 U.S.-led invasion and subsequent occupation of Iraq was a continuation of the 1991 Gulf War, which Powell helped orchestrate. Its fumbled aftermath was again, something that transpired on Powell’s watch as the chairman of the Joint Chiefs of Staff in the administration of George H. W. Bush.
Powell was part of the policy team that crafted the post-Gulf War response to the fact that Iraq’s president, Saddam Hussein, survived a conflict he was not meant to. After being labeled the Middle East equivalent of Adolf Hitler whose crimes required Nuremburg-like retribution in a speech delivered by President Bush in October 1990, the Iraqi President’s post-conflict hold on power had become a political problem for Bush 41.
Powell was aware of the CIA’s post-war assessment on the vulnerability of Saddam’s rule to continued economic sanctions, and helped craft the policy that led to the passage of Security Council resolution 687 in April 1991. That linked Iraq’s obligation to be disarmed of its WMD prior to any lifting of sanctions and the reality that it was U.S. policy not to lift these sanctions, regardless of Iraq’s disarmament status, until which time Saddam was removed from power.
Regime change, not disarmament, was always the driving factor behind U.S. policy towards Saddam Hussein’s Iraq. Powell knew this because he helped craft the original policy.
I bore witness to the reality of this policy as a weapons inspector working for the United Nations Special Commission (UNSCOM), created under the mandate of resolution 687 to oversee the disarming of Iraq’s WMD. Brought in to create an intelligence capability for the inspection team, my remit soon expanded to operations and, more specifically, how Iraq was hiding retained weapons and capability from the inspectors.
SCUDS
One of my first tasks was addressing discrepancies in Iraq’s accounting of its modified SCUD missile arsenal; in December 1991 I wrote an assessment that Iraq was likely retaining approximately 100 missiles. By March 1992 Iraq, under pressure, admitted it had retained a force of 89 missiles (that number later grew to 97).
After extensive investigations, I was able to corroborate the Iraqi declarations, and in November 1992 issued an assessment that UNSCOM could account for the totality of Iraq’s SCUD missile force. This, of course, was an unacceptable conclusion, given that a compliant Iraq meant sanctions would need to be lifted and Saddam would survive.
The U.S. intelligence community rejected my findings without providing any fact-based evidence to refute it, and the CIA later briefed the Senate that it assessed Iraq to be retaining a force of some 200 covert SCUD missiles. This all took place under Powell’s watch as chairman of the Joint Chiefs.
I challenged the CIA’s assessment, and organized the largest, most complex inspection in UNSCOM’s history to investigate the intelligence behind the 200-missile assessment. In the end, the intelligence was shown to be wrong, and in November 1993 I briefed the CIA Director’s senior staff on UNSCOM’s conclusion that all SCUD missiles were accounted for.
Moving the Goalposts
The CIA’s response was to assert that Iraq had a force of 12-20 covert SCUD missiles, and that this number would never change, regardless of what UNSCOM did. This same assessment was in play at the time of Powell’s Security Council presentation, a blatant lie born of the willful manufacture of lies by an entity—the CIA—whose task was regime change, not disarmament.
Powell knew all of this, and yet he still delivered his speech to the UN Security Council.
In October 2002, in a briefing designed to undermine the credibility of UN inspectors preparing to return to Iraq, the Defense Intelligence Agency trotted out Dr. John Yurechko, the defense intelligence officer for information operations and denial and deception, to provide a briefing detailing U.S. claims that Iraq was engaged in a systematic process of concealment regarding its WMD programs.
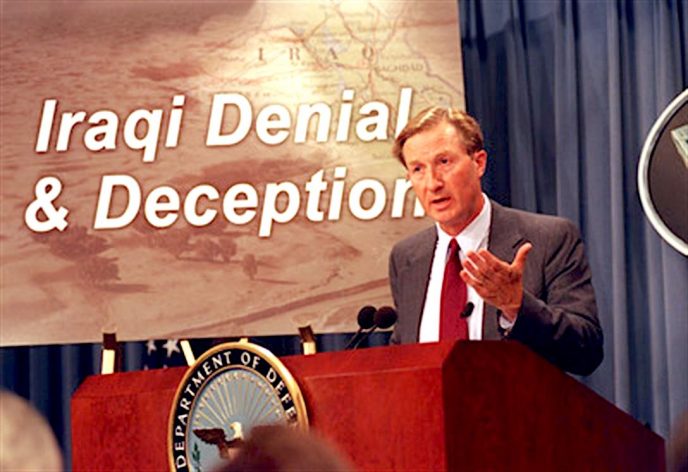
John Yurechko, of the Defense Intelligence Agency, briefs reporters at the Pentagon on Oct. 8, 2002 (U.S. Defense Dept.)
According to Yurechko, the briefing was compiled from several sources, including “inspector memoirs” and Iraqi defectors. The briefing was farcical, a deliberate effort to propagate misinformation by the administration of Bush 43. I know—starting in 1994, I led a concerted UNSCOM effort involving the intelligence services of eight nations to get to the bottom of Iraq’s so-called “concealment mechanism.”
Using innovative imagery intelligence techniques, defector debriefs, agent networks and communications intercepts, combined with extremely aggressive on-site inspections, I was able, by March 1998, to conclude that Iraqi concealment efforts were largely centered on protecting Saddam Hussein from assassination, and had nothing to do with hiding WMD. This, too, was an inconvenient finding, and led to the U.S. dismantling the apparatus of investigation I had so carefully assembled over the course of four years.
It was never about the WMD—Powell knew this. It was always about regime change.
Using UN as Cover for Coup Attempt
In 1991, Powell signed off on the incorporation of elite U.S. military commandos into the CIA’s Special Activities Staff for the purpose of using UNSCOM as a front to collect intelligence that could facilitate the removal of Saddam Hussein. I worked with this special cell from 1991 until 1996, on the mistaken opinion that the unique intelligence, logistics and communications capability they provided were useful to planning and executing the complex inspections I was helping lead in Iraq.
This program resulted in the failed coup attempt in June 1996 that used UNSCOM as its operational cover—the coup failed, the Special Activities Staff ceased all cooperation with UNSCOM, and we inspectors were left holding the bag. The Iraqis had every right to be concerned that UNSCOM inspections were being used to target their president because, the truth be told, they were.
Nowhere in Powell’s presentation to the Security Council, or in any of his efforts to recast that presentation as a good intention led astray by bad intelligence, does the reality of regime change factor in. Regime change was the only policy objective of three successive U.S. presidential administrations—Bush 41, Clinton, and Bush 43.
Powell was a key player in two of these. He knew. He knew about the existence of the CIA’s Iraq Operations Group. He knew of the successive string of covert “findings” issued by U.S. presidents authorizing the CIA to remove Saddam Hussein from power using lethal force. He knew that the die had been cast for war long before Bush 43 decided to engage the United Nations in the fall of 2002.
Powell Knew
Powell knew all of this, and yet he still allowed himself to be used as a front to sell this conflict to the international community, and by extension the American people, using intelligence that was demonstrably false. If, simply by drawing on my experience as an UNSCOM inspector, I knew every word he uttered before the Security Council was a lie the moment he spoke, Powell should have as well, because every aspect of my work as an UNSCOM inspector was known to, and documented by, the CIA.
It is not that I was unknown to Powell in the context of the WMD narrative. Indeed, my name came up during an interview Powell gave to Fox News on Sept. 8, 2002, when he was asked to comment on a quote from my speech to the Iraqi Parliament earlier that month in which I stated:
“The rhetoric of fear that is disseminated by my government and others has not to date been backed up by hard facts that substantiate any allegations that Iraq is today in possession of weapons of mass destruction or has links to terror groups responsible for attacking the United States. Void of such facts, all we have is speculation.”
Powell responded by declaring,
“We have facts, not speculation. Scott is certainly entitled to his opinion but I’m afraid that I would not place the security of my nation and the security of our friends in the region on that kind of an assertion by somebody who’s not in the intelligence chain any longer… If Scott is right, then why are they keeping the inspectors out? If Scott is right, why don’t they say, ‘Anytime, any place, anywhere, bring ‘em in, everybody come in—we are clean?’ The reason is they are not clean. And we have to find out what they have and what we’re going to do about it. And that’s why it’s been the policy of this government to insist that Iraq be disarmed in accordance with the terms of the relevant UN resolutions.” (emphasis added, Aletho News )
Of course, in November 2002, Iraq did just what Powell said they would never do—they let the UN inspectors return without preconditions. The inspectors quickly exposed the fact that the “high quality” U.S. intelligence they had been tasked with investigating was pure bunk. Left to their own devices, the new round of UN weapons inspections would soon be able to give Iraq a clean bill of health, paving the way for the lifting of sanctions and the continued survival of Saddam Hussein.
Powell knew this was not an option. And thus he allowed himself to be used as a vehicle for disseminating more lies—lies that would take the U.S. to war, cost thousands of U.S. service members their lives, along with hundreds of thousands of Iraqis, all in the name of regime change.
Back to Robert Draper. I spent a considerable amount of time impressing upon him the reality of regime change as a policy, and the fact that the WMD disarmament issue existed for the sole purpose of facilitating regime change. Apparently, my words had little impact, as all Draper has done in his article is continue the false narrative that America went to war on the weight of false and misleading intelligence.
Draper is wrong—America went to war because it was our policy as a nation, sustained over three successive presidential administrations, to remove Saddam Hussein from power. By 2002 the WMD narrative that had been used to support and sustain this regime change policy was weakening.
Powell’s speech was a last-gasp effort to use the story of Iraqi WMD for the purpose it was always intended—to facilitate the removal of Saddam Hussein from power. In this light, Colin Powell’s speech was one of the greatest successes in CIA history. That is not the story, however, Draper chose to tell, and the world is worse off for that failed opportunity.
Scott Ritter is a former Marine Corps intelligence officer who served in the former Soviet Union implementing arms control treaties, in the Persian Gulf during Operation Desert Storm, and in Iraq overseeing the disarmament of WMD.
White Helmets co-founder stole aid money destined for Syria – report
RT | July 17, 2020
As Western governments opened their checkbooks for the White Helmets – a controversial ‘rescue organization’ in Syria – their co-founder used the cash to top up his wage and even finance his wedding, according to a Dutch report.
Days before he plunged from a window in Istanbul to his death last year, White Helmets co-founder and British mercenary James Le Mesurier admitted to defrauding Mayday Rescue, an organization that fundraised for the anti-government rescue group in Syria.
According to documents seen by Dutch newspaper De Volkskrant, Le Mesurier told an accountant sent to audit the charity’s books that he forged receipts for $50,000, pretending that it was sent to finance an evacuation operation in Syria. Instead, the money was paid to Le Mesurier himself. In addition to paying himself a salary of €24,000 ($27,414) per month, Le Mesurier dipped into company cash to finance a lavish wedding in Istanbul in 2018, and to issue loans to his new wife, former diplomat Emma Winberg, the report claims.
The accountant sent to investigate Mayday found that “tens of thousands of dollars in cash” were withdrawn to pay for the “fairytale wedding.”
Meanwhile, governments across the Western world were lining up to support Mayday, and channel money to the White Helmets. According to a 2018 report by the Dutch Ministry of Foreign Affairs, the organization took in $127 million between 2014 and 2018, with only $19 million of this haul coming from non-state donors. The government of the Netherlands paid out almost $11.5 million in this period, while similar donations flowed in from Germany, Great Britain, Canada, Qatar, and others.
Despite being hailed as fearless rescue workers, the White Helmets have been accused of partnering with Al-Qaeda. Operating exclusively in rebel-held territory, the group’s members have been photographed posing with jihadists and have been accused of staging chemical weapons attacks to draw in Western forces against Syrian President Bashar Assad.
Le Mesurier’s death was deemed a suicide by Turkish authorities. Shortly afterwards, a number of countries that had donated to Mayday demanded an accountant have another look over the organization’s books. According to De Volkskrant, this probe found that most of Mayday’s financial records are “missing.” Donations were not just handed to the organization in Amsterdam and forwarded to Syria, but distributed through a network of commercial organizations in Turkey and Dubai.
In a letter to donors, Le Mesurier admitted to swindling them out of their cash, but maintained the fraud wasn’t committed on purpose. After these donors discovered their cash had disappeared, they kept the inquiry into Mayday secret, De Volkskrant reported.
The Dutch government pulled its funding from Mayday Rescue almost a year before Le Mesurier admitted the fraud and killed himself. The government in The Hague will not transfer a final subsidy of more than €57,000 ($65,200) to the organization, while Germany is attempting to claim nearly €50,000 ($57,200) back. Cor Vrieswijk, Mayday’s new administrator, told De Volkskrant that the charity will be dissolved in the coming months.
President Assad claimed last November that Le Mesurier’s death was no accident, stating in an interview that the former soldier and mercenary may have been killed because he “knew major secrets.” What Le Mesurier may or may not have known is anyone’s guess, but his death and the subsequent investigation into Mayday has not dried up the White Helmets’ funding.
The group is reportedly receiving subsidies from Western governments through other organizations. At present its members are occupied with fighting the coronavirus outbreak in Syria. However, that hasn’t stopped its leadership from lobbying the US government against Assad and pressing for the maintenance of sanctions, even amid the pandemic.
The Russians are coming, again! Poorly understood cybercrimes play perfectly into political agendas
By Helen Buyniski | RT | July 16, 2020
Foreign hackers are determined as ever to steal technology, meddle in elections and skew foreign policy, but fear not! The CIA has apparently been authorized to deliver preemptive cyber-strikes based on partisan mythmaking.
US, UK and Canadian intelligence dropped a 16-page report on Thursday accusing “Russian hackers” – specifically APT29, the “Cozy Bear” hacking group of ‘Russiagate’ fame – of targeting unspecified entities involved in developing the (increasingly controversial) Covid-19 vaccine.
However, the report is fraught with the same factual pitfalls plaguing previous unsubstantiated “Russian hacking” tales, seemingly designed to capitalize on the general population’s ignorance about cyber-attacks – or vaccines, for that matter. While Democrat-linked cybersecurity firm CrowdStrike specializes in attributing state actors to malware attacks, more reputable companies avoid doing so based solely on the malware used, since hacking groups often exchange tools or even collaborate.
The best, or just best-funded hackers are able to not only cover their tracks effectively but create a fake trail leading to someone else. The WikiLeaks Vault 7 release in 2017 exposed the disturbing tools the CIA has at its disposal for simulating foreign cyberattacks, tools that allow the agency to make it seem like Moscow or Tehran is behind a hack when the real culprits are in Langley, Virginia.
Russia is far from the only country to be accused of such behavior, of course – China was accused of attempting to steal coronavirus vaccine research back in May, while US and UK intelligence agencies warned that same month that other “threat groups” were “actively targeting” local governments, pharmaceutical and research firms, healthcare facilities, and universities for virus-related hacking.
Nor is this latest outbreak of finger-pointing limited to the pandemic. On Thursday, UK foreign minister Dominic Raab denounced “Russian actors” for “almost certainly” seeking to meddle in the 2019 election – not by actually breaking any laws, but by “amplifying” documents leaked by other people on Reddit and circulated around social media in the run-up to December’s contest
Raab didn’t name any of the Russians responsible for circulating the material, perhaps mindful of the embarrassment that befell his ideological brother-in-arms, Atlantic Council bot-hunter Ben Nimmo, who accused several real people of being “Russian bots.” Further covering his bases, Raab in the same statement acknowledged that there was “no evidence of a broad-spectrum Russian campaign against the General Election.”
Even the most nonspecific shrieking about Russian hackers plotting to steal vaccine data, however, distracts from the inconvenient reality that the vaccines under development in the UK and US are performing abysmally. Neither the US company Moderna – initially hailed as the frontrunner despite never having brought a vaccine to market before – nor the UK’s collaboration between Oxford University and pharma giant AstraZeneca have produced any encouraging results in their clinical trials.
That didn’t stop the US from ordering 300 million doses of the Oxford jab, though the Trump administration’s coronavirus czar Anthony Fauci has already begun lamenting the “general anti-science, anti-authority, anti-vaccine feeling among some people in this country” he fears will keep Americans away from the needle.
With regard to hacking, however, the world might be more concerned about the CIA than the Russians – especially following Wednesday’s Yahoo News report that the agency had received carte blanche from Trump to wage preemptive (i.e. unjustified) cyber-warfare against any individual or organization it could link to a “handful of adversarial countries.”
According to several former US officials, the CIA has been wielding unprecedented offensive powers against American civilians only tenuously connected to Washington’s geopolitical rivals since 2018, checking off at least 12 cyber-attacks on its “wish list” already. Liberated from the tiresome need to provide “years of signals and dozens of pages of intelligence” justifying raining computer-borne chaos and destabilization on its victims, the CIA has wrought “a combination of destructive things – stuff is on fire and exploding – and also public dissemination of data: leaking or things that look like leaking.”
News of the CIA being given carte blanche appears at the same point in the US election cycle as the 2018 report about a similar measure that freed the hands of the Pentagon to conduct its own cyberattacks without interference from the State Department or any intelligence agencies.
With a hotly anticipated election coming up in November, it’s not hard to imagine how a few well-placed “leaks” or “destructive things” might convince voters to put aside their concerns about the administration’s response to the pandemic – or to place it front and center, depending on whether the CIA has decided it can live with four more years of Trump.
One thing is certain: the “Russian meddling” narrative isn’t going away anytime soon.
Helen Buyniski is an American journalist and political commentator at RT. Follow her on Twitter @velocirapture23
The Real ‘Russian Playbook’ Is Written in English
By Patrick Armstrong | Strategic Culture Foundation | July 17, 2020
I hadn’t given The Russian Playbook much attention until Susan Rice, Obama’s quondam security advisor, opined a month ago on CNN that “I’m not reading the intelligence today, or these days — but based on my experience, this is right out of the Russian playbook“. She was referring to the latest U.S. riots.
Once I’d seen this mention of The Russian Playbook (aka KGB, Kremlin or Putin’s Playbook), I saw the expression all over the place. Here’s an early – perhaps the earliest – use of the term. In October 2016, the Center for Strategic and International studies (“Ranked #1“) informed us of the “Kremlin Playbook” with this ominous beginning:
There was a deeply held assumption that, when the countries of Central and Eastern Europe joined NATO and the European Union in 2004, these countries would continue their positive democratic and economic transformation. Yet more than a decade later, the region has experienced a steady decline in democratic standards and governance practices at the same time that Russia’s economic engagement with the region expanded significantly.
And asks:
Are these developments coincidental, or has the Kremlin sought deliberately to erode the region’s democratic institutions through its influence to ‘break the internal coherence of the enemy system’?
Well, to these people, to ask the question is to answer it: can’t possibly be disappointment at the gap between 2004’s expectations and 2020’s reality, can’t be that they don’t like the total Western values package that they have to accept, it must be those crafty Russians deceiving them. This was the earliest reference to The Playbook that I found, but it certainly wasn’t the last.
I found headlines such as these: Former CIA Director Outlines Russian Playbook for Influencing Unsuspecting Targets (May 2017); Fmr. CIA op.: Don Jr. meeting part of Russian playbook (Jul 2017); Americans Use Russian Playbook to Spread Disinformation (Oct 2018); Factory of Lies: The Russian Playbook (Nov 2018); Shredding the Putin Playbook: Six crucial steps we must take on cyber-security—before it’s too late. (Winter 2018); Trump’s spin is ‘all out of the KGB playbook’: Counterintelligence expert Malcolm Nance (May 2019).
Of course, all these people are convinced Moscow interfered in the 2016 presidential election. Somehow. To some effect. Never really specified but the latest outburst of insanity is this video from the Lincoln Project. As Anatoly Karlin observes: “I think it’s really cool how we Russians took over America just by shitposting online. How does it feel to be subhuman?” He has a point: the Lincoln Project, and the others shrieking about Russian interference, take it for granted that American democracy is so flimsy and Americans so gullible that a few Facebook ads can bring the whole facade down. A curious mental state indeed.
So let us consider The Russian Playbook. It stands at the very heart of Russian power. It is old: at least a century old. Why, did not Tolstoy’s 1908 Letter to a Hindu inspire Gandhi to bring down the British Indian Empire and win the Great Game for Moscow? The Tolstoy-Putin link is undeniable as we are told in A Post-Soviet ‘War and Peace’: What Tolstoy’s Masterwork Explains About Putin’s Foreign Policy: “In the early decades of the nineteenth century, Napoleon (like Putin after him) wanted to construct his own international order…”. Russian novelists: adepts of The Playbook every one. So there is much to consider about this remarkable Book which has had such an enormous – hidden to most – role in world history. Its instructions on how to swing Western elections are especially important: the 2016 U.S. election; Brexit; “100 years of Russian electoral interference“; Canada; France; the European Union; Germany and many more. The awed reader must ask whether any Western election since Tolstoy’s day can be trusted. Not to forget the Great Hawaiian Pizza Debate the Russians could start at any moment.
What can we know about The Playbook? For a start it must be written in Russian, a language that those crafty Russians insist on speaking among themselves. Secondly such an important document would be protected the way that highly classified material is protected. There would be a very restricted need to know; underlings participating in one of the many plays would not know how their part fitted into The Playbook; few would ever see The Playbook itself. The Playbook would be brought to the desk of the few authorised to see it by a courier, signed for, the courier would watch the reader and take away the copy afterwards. The very few copies in existence would be securely locked away; each numbered and differing subtly from the others so that, should a leak occur, the authorities would know which copy read by whom had been leaked. Printed on paper that could not be photographed or duplicated. As much protection as human cunning could devise; right up there with the nuclear codes.
So, The Russian Playbook would be extraordinarily difficult to get hold of. And yet… every talking head on U.S. TV has a copy at his elbow! English copies, one assumes. Rachel Maddow has comprehended the complicated chapter on how to control the U.S. power system. Others have read the impenetrably complex section on how to control U.S. voting machines or change vote counts. Many are familiar with the lists of divisions in American society and directions for exploiting them. Adam Schiff has mastered the section on how to get Trump to give Alaska back. Susan Rice well knows the chapter “How to create riots in peaceful communities”.
And so on. It’s all quite ridiculous: we’re supposed to believe that Moscow easily controls far-away countries but can’t keep its neighbours under control.
There is no Russian Playbook, that’s just projection. But there is a “playbook” and it’s written in English, it’s freely available and it’s inexpensive enough that every pundit can have a personal copy: it’s named “From Dictatorship To Democracy: A Conceptual Framework for Liberation” and it’s written by Gene Sharp (1928-2018). Whatever Sharp may have thought he was doing, whatever good cause he thought he was assisting, his book has been used as a guide to create regime changes around the world. Billed as “democracy” and “freedom”, their results are not so benign. Witness Ukraine today. Or Libya. Or Kosovo whose long-time leader has just been indicted for numerous crimes. Curiously enough, these efforts always take place in countries that resist Washington’s line but never in countries that don’t. Here we do see training, financing, propaganda, discord being sown, divisions exploited to effect regime change – all the things in the imaginary “Russian Playbook”. So, whatever he may have thought he was helping, Sharp’s advice has been used to produce what only the propagandists could call “model interventions“; to the “liberated” themselves, the reality is poverty, destruction, war and refugees.
The Albert Einstein Institution, which Sharp created in 1983, strongly denies collusion with Washington-sponsored overthrows but people from it have organised seminars or workshops in many targets of U.S. overthrows. The most recent annual report of 2014, while rather opaque, shows 45% of its income from “grants” (as opposed to “individuals”) and has logos of Euromaidan, SOSVenezuela, Umbrellamovement, Lwili, Sunflowersquare and others. In short, the logos of regime change operations in Ukraine, Venezuela, Hong Kong, Burkina Faso and Taiwan. (And, ironically for today’s USA, Black Lives Matter). So, clearly, there is some connection between the AEI and Washington-sponsored regime change operations.
So there is a “handbook” but it’s not Russian.
Reading Sharp’s book, however, makes one wonder if he was just fooling himself. Has there ever been a “dictatorship” overthrown by “non-violent” resistance along the lines of what he is suggesting? He mentions Norwegians who resisted Hitler; but Norway was liberated, along with the rest of Occupied Europe, by extremely violent warfare. While some Jews escaped, most didn’t and it was the conquest of Berlin that saved the rest: the Nazi state was killed. The USSR went away, together with its satellite governments in Europe but that was a top-down event. He likes Gandhi but Gandhi wouldn’t have lasted a minute under Stalin. Otpor was greatly aided by NATO’s war on Serbia. And, they’re only “non-violent” because the Western media doesn’t talk much about the violence; “non-violent” is not the first word that comes to mind in this video of Kiev 2014. “Colour revolutions” are manufactured from existing grievances, to be sure, but with a great deal of outside assistance, direction and funding; upon inspection, there’s much design behind their “spontaneity”. And, not infrequently, with mysterious sniping at a expedient moment – see Katchanovski’s research on the “Heavenly Hundred” of the Maidan showing pretty convincingly that the shootings were “a false flag operation” involving “an alliance of the far right organizations, specifically the Right Sector and Svoboda, and oligarchic parties, such as Fatherland”. There is little in Sharp’s book to suggest that non-violent resistance would have had much effect on a really brutal and determined government. He also has the naïve habit of using “democrat” and “dictator” as if these words were as precisely defined as coconuts and codfish. But any “dictatorship” – for example Stalin’s is a very complex affair with many shades of opinion in it. So, in terms of what he was apparently trying to do, one can see it only succeeding against rather mild “dictators” presiding over extremely unpopular polities. With a great deal of outside effort and resources.
His “playbook” is useful to outside powers that want to overthrow governments they don’t like. Especially those run by “dictators” not brutal enough to shoot the protesters down. It’s not Russian diplomats that are caught choosing the leaders of ostensibly independent countries. It’s not Russians who boast of spending money in poor countries to change their governments. It’s not Russian diplomats who meet with foreign opposition leaders. Russia doesn’t fabricate a leader of a foreign country. It’s not Russia that invents a humanitarian crisis, bombs the country to bits, laughs at its leader’s brutal death and walks away. It’s not Russia that sanctions numerous countries. It’s not Russia that gives fellowships to foreign oppositionists. Even the Washington Post (one of the principals in sustaining Putindunnit hysteria) covered “The long history of the U.S. interfering with elections elsewhere“; but piously insisted “the days of its worst behavior are long behind it”. Whatever the pundits may claim about Russia, the USA actually has an organisation devoted to interfering in other countries’ business; one of whose leading lights proudly boasted: “A lot of what we do today was done covertly 25 years ago by the CIA.”
The famous “Russian Playbook” is nothing but projection onto Moscow of what Washington actually does: projection is so common a feature of American propaganda that one may certain that when Washington accuses somebody else of doing something, it’s a guarantee that Washington is doing it.
Inconclusive investigations and psychological trauma cultivate Israel’s impunity

Protesters hold banners in solidarity with the martyr Iyad Hallaq an autistic Palestinian man shot dead by Israeli police in the West Bank city of Bethlehem on 2 June 2020 [Abedalrahman Hassan/ApaImages]
By Ramona Wadi | MEMO | July 16, 2020
In May, Israeli security forces killed Eyad Al-Hallaq, a 32-year-old Palestinian man with special needs, on suspicion that he had a weapon. He was on his way to the special school in Jerusalem which he attended, when he was chased by Israeli security forces, cornered and shot, despite being accompanied by his teacher who repeatedly called out to the aggressors that he was autistic. No weapon was discovered on Hallaq after this unwarranted extrajudicial killing.
Less than two months after Israeli Defence Minister Benny Gantz issued a perfunctory, patronising apology in which he stated, “I am sure this subject will be investigated swiftly and conclusions will be reached,” recent reports attest to how rapidly Israel invokes its own impunity to cover up its crimes.
Eyad Al-Hallaq was killed in a heavily securitised area in Jerusalem’s Old City; security cameras monitoring the indigenous population are everywhere. However, Israel’s Justice Ministry has confirmed that there is no CCTV footage of the killing. It went on to assert that, despite the presence of cameras where the shooting took place, the cameras “were not connected at the relevant time and didn’t document” the incident.
This lacks even a shard of credibility, yet it is not unusual in Israel, which goes to great lengths to safeguard its own institutions and uniformed criminals from scrutiny and prosecution. The Hallaq family is now left with no recourse for justice, because Israel has created its own travesty of justice that is concerned solely with manufacturing impunity for those responsible for the 32-year-old’s death. The investigation is close to reaching a conclusion, according to a Haaretz report, and there is no doubt that the bereaved family will be left to face a multitude of questions on its own, with the additional psychological trauma of knowing that the exact circumstances of their son’s murder are unresolved and the perpetrators still roam free. In Israel’s typical style, it will be an inconclusive end to a concluded investigation. The family’s lawyer, meanwhile, is requesting an in-depth investigation because there is a “very strong suspicion” that the police are concealing evidence in this case.
This is not the first time that Israel has refused to release evidence that would provide both context and corroboration. A case that springs to mind is that of Ibrahim Abu Thurayyah, a double amputee killed by a shot to the head in December 2017 during the Great Return March protests in the Gaza Strip. Israeli investigations concluded there was no evidence that one of its snipers had directly targeted Thurayyah while he was in his wheelchair.
Concealing evidence is a clear indication of culpability. For Israel, however, the practice is dissociative and is reflective of how colonial violence against Palestinians sustains itself. There is no need to deny culpability if action is taken to prevent any discussion of the crime. Indeed, in this case it is easier for Israeli government officials to exploit the victim and the grieving family, since the evidence of the events leading up to Eyad Al-Hallaq’s killing has been eliminated.
For the Hallaq family, as it was for other families whose relatives have been murdered by Israeli occupation forces, the killing and subsequent cover-up is a personal rupture. Politically, Israel is replicating the impunity generated since the Nakba on a different scale, relying upon separate episodes of inflicted trauma to prevent a collective Palestinian narrative from emerging as a unified front against its colonial violence.
The Maxwell Family Business: Espionage

July 15, 2020
Many were surprised to learn earlier this month that the key co-conspirator in Jeffrey Epstein’s intelligence-linked sexual blackmail operation, Ghislaine Maxwell, had been in hiding in New England since Epstein’s arrest and subsequent “suicide” last summer. Her recent arrest, of course, has returned attention to the Epstein scandal and to Ghislaine’s ties to the entire operation, in which she played a central and crucial role, arguably more so than Epstein himself.
Ghislaine was first reported to be living in New England at the mansion of her alleged boyfriend Scott Borgeson on August 14th of last year. Though Maxwell is believed to have stayed there until purchasing the nearby New Hampshire home where she was arrested, attention from her presence on the East Coast was immediately and sensationally re-directed to the West Coast when, a day later on August 15th, the New York Post published a picture allegedly depicting Maxwell reading a book on “CIA operatives” at an In-N-Out Burger in Los Angeles, California. The photo was later revealed to have been photoshopped and a fake, but ultimately served its purpose in distracting from her actual location in New England.
While the media frenziedly covered the fake In-N-Out Burger photo, the appearance of an unexpected visitor nearby Borgeson’s mansion succeeded in largely slipping under the radar. On August 18th, Ghislaine’s sister Christine was spotted “packing up a number of bags” into a SUV just a few miles from Borgeson’s “secluded beachfront” home. Christine, who currently lives and works in Dallas, Texas, declined to comment on why she was visiting the exact area where Ghislaine was allegedly hiding at the time.
Out of the seven Maxwell siblings, Ghislaine Maxwell has undoubtedly received the bulk of media scrutiny both in recent years and arguably ever since the suspected homicide of the family patriarch, Robert Maxwell, in 1991. In the years since his death, Robert Maxwell’s close ties to Israeli intelligence and links to other intelligence agencies have been documented by respected journalists and investigators including Seymour Hersh and Gordon Thomas, among others.
While Ghislaine’s own ties to intelligence have since come to light in relation to her critical role in facilitating the Jeffrey Epstein sexual blackmail operation. Little, if any attention, has been paid to her siblings, particularly Christine and her twin sister Isabel, despite them having held senior roles at the Israeli intelligence front company that facilitated their father’s greatest act of espionage on Israel’s behalf, the sale of the bugged PROMIS software to the U.S. national laboratories at the heart of the country’s nuclear weapons system.
Not only that, but Christine and Isabel later became directly involved with technology-based business ventures that directly involved Ghislaine during the very period she worked with Epstein on behalf of Israeli and U.S. intelligence to ensnare powerful U.S. political and public figures in a sexual blackmail scheme involving minors. At the time, Ghislaine described her profession to a number of newspapers as “an internet operator.” Then, after this venture’s multi-million dollar sale to a competitor, Christine and Isabel became involved with successors to the PROMIS software scandal that were closely tied to U.S. intelligence and Israeli intelligence, respectively.
Ghislaine herself also became involved in these affairs, as did Jeffrey Epstein following his first arrest, as they began courting the biggest names in the U.S. tech scene, from Silicon Valley’s most powerful venture capital firms to its most well-known titans. This also dovetailed with Epstein’s investments in Israeli intelligence-linked tech firms and his claims of having troves of blackmail on prominent tech company CEOs during this same period.
With Ghislaine’s name and her ties to intelligence now inking their way back into the media sphere, detailing the decades-long course of these technology-focused espionage operations and their persistent ties to the Maxwell sisters demands the attention it deserves, as the need to air out the real Maxwell family business – espionage – is now greater than ever before.
Trap doors and Treason
One of the most brazen and successful operations conducted by Israeli intelligence on a global scale is undeniably its sale of a bugged software program to governments, corporations and major financial and scientific institutions around the world. That software program, known as the Prosecutor’s Information Management System or by its acronym PROMIS, was originally created and marketed by Inslaw Inc., a company created by former NSA official Bill Hamilton and his wife Nancy.
In 1982, Inslaw leased its revolutionary PROMIS software to the U.S. Justice Department, then headed by arch neocon Edwin Meese III, Ronald Reagan’s most trusted advisor and who would later go on to advise Donald Trump following the 2016 election. The success of the software, which allowed integration of separate databases and information analysis on a previously unimaginable scale, eventually caught the attention of Rafi Eitan, the notorious and legendary Israeli spymaster and handler of the “most damaging spy” in American history, Jonathan Pollard. Eitan, at the time, was serving as the then-head of the now defunct Israel intelligence service known as Lekem, which focused specifically on espionage related to scientific and technical information and discoveries.
Eitan had first learned of PROMIS from Earl Brian. Brian was a long-time associate of Ronald Reagan who had previously worked for the CIA in covert operations and had been in charge of Reagan’s healthcare program when Reagan was governor of California. Brian often bragged of the nickname he had acquired in overseeing that health care initiative – “the man who walked over the dead.” In 1982, however, Brian was attempting to build a business empire, in which then-AG Ed Meese’s wife was a major investor, and he had first met Eitan while attempting to sell a healthcare system in Iran.
Brian divulged the efficacy of PROMIS, but – instead of praising its revolutionary approach to data analysis – expressed his frustration that the software enabled U.S. federal investigators to successfully track and target money laundering and other financial crimes. He also expressed frustration that he had been left out of the profits on PROMIS, the development of which he had followed closely for several years.
As their conversation wore on, Eitan and Brian hatched a plan to install a “trapdoor”, today more often referred to as a back door, into the software. They would then market PROMIS throughout the world, providing Israeli intelligence and allied elements of U.S. intelligence with a direct window into the operations of its enemies and allies while also netting Eitan and Brian massive profits for the sale of the software. Brian, of course, would also be able to use PROMIS to circumvent authorities investigating financial crimes.
According to the testimony of ex-Mossad official Ari Ben-Menashe, after PROMIS was obtained by Israel’s military intelligence through direct collusion with the U.S. Department of Justice, Ben-Menashe contacted an Israeli American programmer living in California on Eitan’s orders. That programmer then planted a “trapdoor” or back door into the software that would allow Lekem covert access to any database connected to a device on which the software was installed.
Once the back door was present, Brian attempted to use his company Hadron Inc to market the bugged PROMIS software around the world, though he first had tried to buy out Inslaw to do so. Unsuccessful, Brian turned to his close friend, then-Attorney General Ed Meese, and the Justice Department then abruptly refused to make the payments to Inslaw that had been stipulated by the contract, essentially using the software for free, which Inslaw claimed to be theft.
Meese’s actions would force Inslaw into bankruptcy and Inslaw subsequently sued the Justice Department, with a US court later finding that the Meese-led department “took, converted, stole” the software through “trickery, fraud and deceit.” With Inslaw out of the way, Brian sold the bugged software to Jordan’s and Iraq’s intelligence services, a major boon for Israel, and to a handful of companies. Despite this, Eitan was unsatisfied with Brian and Hadron and he quickly turned to the person he thought could most effectively market and sell PROMIS to governments of interest all over the world, Robert Maxwell.
First recruited as an asset of Israeli intelligence in the early 1960s, Maxwell’s standing with Israeli intelligence would strengthen considerably beginning in the early 1980s, when he purchased a web of Israeli companies, many of which were official “service providers” for the Mossad. One of these companies, a computer firm called Degem, had been used for years to provide cover to Mossad assassins that conducted kidnappings and murders in Latin America and Africa.
Through Degem and other Maxwell-owned companies based in Israel and elsewhere, Maxwell marketed PROMIS so successfully that Israeli intelligence soon had access to the innermost workings of innumerable governments, corporations, banks and intelligence services around the world. Many of Maxwell’s biggest successes came in selling PROMIS to dictators in Eastern Europe, Africa and Latin America. Following the sale and after Maxwell collected a handsome paycheck, PROMIS’ unparalleled ability to track and surveil anything – from cash flows to human movement – were used by these governments to commit financial crimes with greater finesse and used to hunt down and disappear dissidents. Israeli intelligence, of course, watched it all play out in real time.
In Latin America, for instance, Maxwell sold PROMIS to military dictatorships in Chile and Argentina, which were used to facilitate the mass murder that characterized Operation Condor as the friends and families of dissidents and so-called subversives were easily identified using PROMIS. PROMIS was so effective for this purpose that, just days after Maxwell sold the software to Guatemala, its US-backed dictatorship rounded up 20,000 “subversives” who were never heard from again. Of course, thanks to the back door in PROMIS, Israeli intelligence knew the identities of Guatemala’s disappeared before the victim’s own families. Israel was also intimately involved in the arming and training of many of the same Latin American dictatorships that had been sold the bugged PROMIS software.
Though Israeli intelligence found obvious use for the steady stream of sensitive and classified information, their biggest prize was yet to come – top secret government laboratories in the United States. Eitan tasked Maxwell with selling PROMIS to US labs in the Los Alamos complex, including Sandia National Laboratory, which was and is at the core of the US nuclear weapons system. Notably, the eventual sale of PROMIS to these laboratories by Maxwell occurred during the same period in 1984 when Eitan tasked one of Israel’s top experts in nuclear targeting with supervising Jonathan Pollard’s espionage of U.S. nuclear secrets on Israel’s behalf.
In order to plot how he would accomplish such a feat, Maxwell would meet with none other than Henry Kissinger, who told him that – in order to sell PROMIS to these sensitive laboratories – he needed to enlist the services of then-Senator for Texas John Tower, who was the head of the Senates’ Armed Services Committee at the time. Maxwell quickly struck a deal with Tower and then, using Mossad money, paid Tower $200,000 for his services, which included opening doors – not just to the Los Alamos complex, but also to the Reagan White House. Tower would arrange a trip for Maxwell to travel to Sandia National Laboratory, where he would market PROMIS. Unlike most other PROMIS sales, this one would not be handled by Degem, but a US-based company called Information on Demand.
It is worth noting that, despite Tower’s obvious and treasonous actions with respect to U.S. national security, another long-time “source” of Robert Maxwell, George H.W. Bush, would attempt to nominate Tower to serve as U.S. Secretary of Defense. When the Senate refused to confirm Tower, only then did Bush nominate Dick Cheney, who would then head the Pentagon and oversee the U.S.’ role in the First Gulf War. Not long after his failure to secure the nomination as Pentagon chief, Tower died in a suspicious plane crash soon after the equally suspicious death of Robert Maxwell.
Front Companies and FBI Cover-ups
Robert Maxwell purchased Information on Demand from its founder, Sue Rugge – a former librarian, through the Pergamon Group in 1982 – the very year plans were made by Rafi Eitan and Earl Brian to subvert PROMIS. Its offices were just a few doors down from the home of Isabel Maxwell and her first husband Dale Djerassi, son of the scientist credited with creating the birth control pill.
According to FBI files obtained by Inslaw Inc. via a FOIA request in the 1990s, San Francisco’s FBI opened an investigation into Information on Demand a year later in October 1983 and subsequently interviewed Rugge about the business and its activities. She told the FBI that the company’s sources “include over 250 computer data bases” and that company uses these to “locate single facts as well as provide answers to complex questions dealing with such areas as comprehensive marketing research, custom data summaries, sophisticated literature searching, current awareness service and global information capability.
One of these databases included Lockheed’s Dialog database and “the Defense Technical Center which is connected to the Department of Defense (DOD) which contains classified information.” She asserted, however, that the company “has no password for access and further no need for access.” Elsewhere in the document, it notes that Information on Demand claimed not have any access to classified information “to the best of their knowledge” and “includes information concerning government and various available means of tapping government information databases.”
The FBI asked Rugge about one client of the company in particular, whose name and identifying information is redacted in its entirety, but notes that this mysterious client had worked with Information on Demand since at least 1973. Subsequent efforts by Inslaw Inc. and others to learn the identity of the redacted client have been unsuccessful since 1994.
Notably, just one month before the FBI opened an investigation into Information on Demand and interviewed Sue Rugge, another related Maxwell-owned firm, Pergamon International Information Corporation, had sent a letter to then-CIA Director Bill Casey, offering to provide the agency with access to patent databases. The only redacted portion of the letter is the identity of PIIC’s Executive Vice President, who had written the letter to Casey.
After Rugge had been interviewed, FBI interest in Information on Demand peaked soon after in June 1984, when a formal investigation was opened. This took place after two employees of Sandia National Laboratory who worked in technology transfer approached the Bureau over Information on Demand’s efforts to sell PROMIS to the laboratory. Those employees were compelled to contact the FBI after obtaining information from employees of the National Security Agency (NSA) regarding “the purchase of Information on Demand Inc. by one Robert Maxwell, the owner of Pergamon International.” The specific information on this purchase from the NSA is included in the report but redacted in its entirety. Two months later, one of the Sandia employees followed up with the Bureau, suggesting that the NSA and FBI jointly investigate Information on Demand, but was essentially stonewalled and told to take it up with FBI headquarters.
The FBI case file is coded as a foreign counter-intelligence investigation specifically, suggesting that the case was opened because the FBI was made aware of the alleged involvement of a foreign intelligence service in some aspect of Information on Demand’s activities that related specifically to the “dissemination, marketing or sale of computer software systems, including but not limited to the PROMIS computer software product.” It also noted that Maxwell himself had previously been the subject of a “security investigation” conducted by the FBI from 1953 until 1961, the year Maxwell was formally recruited as an Israeli intelligence asset.
In early August 1984, FBI headquarters and other higher-ups in the Ed Meese-led Department of Justice, which itself was complicit in the whole sordid PROMIS affair, ordered the New Mexico office to halt its investigation into Information on Demand, Maxwell and PROMIS. The cover-up, oddly enough, continues today, with the FBI still refusing to release documents pertaining to Robert Maxwell and his role in the PROMIS scandal.
Several months following the shuttering of the FBI investigation into Information on Demand, Robert Maxwell again returned to Sandia National Laboratories in February 1985, signing the contract for the sale of PROMIS and listing himself as President and CEO of Information on Demand. A few months later, he passed that role on to his daughter Christine, who served as the company’s president and CEO up until her father’s death in 1991, according to her résumé. Upon the collapse of his business empire shortly after his demise, which also resulted in the closure of Information on Demand, Christine created a company called Research on Demand that offered similar services and specialized “in Internet- and Big Data analytics-related market studies for companies in the Telecoms.”
In addition, Isabel Maxwell, who lived in close proximity to the company’s offices in Berkely, CA, told Haaretz that she had also worked for Information on Demand, which she refers to as “her sister’s company,” following her 1989 divorce from Dale Djerassi.
Recreating their Father’s Legacy
After the death of Robert Maxwell, in what most of his family and many of his biographers regard as a murder conducted by Israeli intelligence, his children began to pick up the pieces and sought to rebuild their father’s empire. Of his seven children, five took on different aspects of their father’s vast portfolio.
Kevin and Ian Maxwell took over much of his business (and the associated fall-out) and his murky network of interlocking companies, trusts and foundations spread throughout the world. Ghislaine, having already positioned herself in New York at her father’s behest to anchor his efforts to expand his empire and operations into Manhattan, began a sexual blackmail operation on behalf of Israeli intelligence alongside Jeffrey Epstein. Christine and Isabel, however, would take off where Maxwell’s intelligence-linked work with PROMIS and in technology had left off by cashing in on a new revolutionary technology, the Internet.
“We literally were trying to think about how to restart this whole business” that had collapsed after their father’s death, Christine Maxwell would later say of her decision to found, along with her husband Roger Malina, Isabel and Isabel’s then-husband David Hayden, their internet services company – the McKinley Group – in January 1992. Isabel would remember the decision similarly, telling Wired in 1999, that she and her sister had “wanted to circle the wagons and rebuild,” seeing McKinley as “a chance to recreate a bit of their father’s legacy.” In 2000, Isabel would tell The Guardian that her father would “love it [the internet] if he was still here.” “He was very prescient…. He’d be in his element, he’d be having a blast, I’m sure he’d be thrilled to know what I’m doing now,” she told the UK-based publication while “throwing back her head and laughing loudly.” Notably, at that time, Isabel was leading Israeli software company with ties to Israeli military intelligence and powerful Israeli political players, including some who had previously worked directly under her father.
It’s not hard to see why Christine and Isabel saw the internet as their chance to expand upon and rebuild upon Robert Maxwell’s “legacy.” As previously mentioned, Christine, right up until her father’s death, had been president and CEO of the Robert Maxwell-owned Israeli intelligence front company, Information on Demand, where Isabel had also worked. Upon his death, Christine had founded a related company called Research on Demand, which specialized in “internet and big data analytics” for telecommunications firms, and would later overlap with the McKinley Group’s work. McKinley began as a directory with a rating system for websites, later transitioning into the Magellan search engine, all of which Isabel Maxwell told Cnet in 1997 were all Christine’s idea.
McKinley created what became known as the Magellan online directory, remembered as “the first site to publish lengthy reviews and ratings of websites.” Magellan’s “value-added content” approach attracted several large corporations, resulting in “major alliances” with AT&T, Time Warner, IBM, Netcom and the Microsoft Network [MSN] that were negotiated by Isabel Maxwell. Microsoft’s major alliance with McKinley came in late 1995, when Microsoft announced that Magellan would power the search option for the company’s MSN service. Time Warner first chose Magellan for its early web portal called Pathfinder and Magellan was on the homepage of the internet browser Netscape for much of the 1990s.
However, McKinley’s fortunes were troubled as its efforts to be the first search engine to go public fell through, igniting a stand-off between Christine Maxwell and Isabel’s husband that also resulted in the company’s essentially falling behind other market leaders both missing the window for a second IPO attempt and lagging behind in adding ad revenue to their business model. Excite, which was later acquired by AskJeeves, ultimately bought the McKinley Group and Magellan for 1.2 million shares of Excite stock in 1996, which was then valued at $18 million. It was allegedly Isabel Maxwell who made the deal possible, with Excite’s CEO at the time, George Bell, claiming she alone salvaged their purchase of McKinley.
Despite the company’s lackluster end, the Maxwell sisters and other stakeholders in the company, Ghislaine Maxwell among them, not only obtained a multi-million dollar payout from the deal, but also forged close connections with Silicon Valley high-rollers. Upon McKinley/Magellan’s sale, the overt ties of Christine and Isabel Maxwell to intelligence in both the U.S. and Israel would grow considerably.
A Family Affair
While the company is often framed as being a venture between Christine and Isabel Maxwell, McKinley Group and Magellan were much more than just the twin sisters’ business. For instance, a November 2003 article in The Evening Standard notes that Christine and Isabel launched the company with considerable help from their brother, Kevin Maxwell who the article described as being “consumed by an overwhelming desire to be his ‘dad reincorporated’” according to confidants. Another Evening Standard article from March 2001 cited report that “Kevin played a major role” in the company’s affairs.
In addition, at the time, The Sunday Times noed in November 2000 that Ghislaine Maxwell “had a substantial interest in Magellan” and netted a considerable sum following its sale to Excite in 1996. It also noted that Ghislaine, throughout the 1990s, had “been discreetly building up a business empire as opaque as her father’s” and that “she is secretive to the point of paranoia and her business affairs are deeply mysterious.” However, she would nonetheless describe “herself as an ‘internet operator’” even though “her office in Manhattan refuses to confirm even the name or the nature of her business.” A separate article in The Scotsman from 2001 also notes that Ghislaine “is extremely secretive about her affairs and describes herself as an internet operator.”
Exactly how involved Ghislaine Maxwell was involved in the McKinley Group and Magellan is unclear, though her decision to describe herself as an “internet operator” and her documented “substantial interest” in the company suggest that it was more than superficial. What is notable, however, is that Ghislaine’s time as an “internet operator” and her business interests in Magellan overlap directly with her time working alongside Jeffrey Epstein in an Israeli intelligence-linked sexual blackmail operation.
During this period of time, Ghislaine Maxwell and Jeffrey Epstein frequently had considerable overlap in their finances, with press reports from the time often asking whether Ghislaine’s expenses were paid by Epstein or through her access to the “lost Maxwell millions” that had been hidden in a web of murky, untraceable financial entities and allegedly “disappeared” following his 1991 death.
The latter is certainly a possibility as it was Ghislaine who was the first to walk into her late father’s office on the Lady Ghislaine following his death, where she “shredded all incriminating documents onboard,” according to journalist John Jackson who witnessed the scene. This would likely mean that she was quickly able to distinguish which documents were “incriminating” and was intimately aware of his more unsavory business activities. In addition, prior to his death, Robert Maxwell had provided Ghislaine with a “tailor-made” New York corporation called Maxwell Corporate Gifts, of which little is known. The corporation was reportedly intended to aid her in establishing a foothold in New York’s power base for Robert Maxwell’s planned expansion into New York society, a plan first set into motion following his purchase of the New York Daily News.
Notably, an article from The Evening Standard in 2001 makes an odd comment about a major source of income from Epstein during the 1990s, stating that “has made many millions out of his business links with the likes of Bill Gates, Donald Trump and Ohio billionaire Leslie Wexner, whose trust he runs.” In addition, Epstein victim Maria Farmer noted in an interview that she overheard Ghislaine and Epstein discuss Bill Gates as though they knew him well in 1995. However, these mentions of Bill Gates here defy the official narrative about the Epstein-Gates relationship, which claims they first met in 2011. Given the “major alliance” between McKinley/Magellan and Microsoft that was forged in 1995-1996, it is certainly possible that Epstein’s pre-2001 “business links” with Bill Gates were, in fact, related to Ghislaine’s involvement and stake in Magellan. This is also supported by the fact that, as will be shown in Part 2 of this report, Magellan co-founder Isabel Maxwell had a personal relationship with Bill Gates and that he put her subsequent company, Israel-based CommTouch, “on the map” after a major investment that had been brokered between Gates and Isabel personally. Part 2 will also show how both Isabel and Christine’s overt involvement, with Israeli and U.S. intelligence, respectively, deepened after Magellan was sold to Excite in 1996.
How an Israeli Spy-Linked Tech Firm Gained Access to the US Gov’t’s Most Classified Networks
By Whitney Webb |
Unlimited Hangout| July 15, 2020
If the networks of the U.S. military, the U.S. intelligence community and a slew of other U.S. federal agencies were running the software of a company with deep ties, not only to foreign companies with a history of espionage against the U.S. but also foreign military intelligence, it would — at the very least — garner substantial media attention. Yet, no media reports to date have noted that such a scenario exists on a massive scale and that the company making such software recently simulated the cancellation of the 2020 election and the declaration of martial law in the United States.
Earlier this month, MintPress News reported on the simulations for the U.S. 2020 election organized by the company Cybereason, a firm led by former members of Israel’s military intelligence Unit 8200 and advised by former top and current officials in both Israeli military intelligence and the CIA. Those simulations, attended by federal officials from the FBI, DHS and the U.S. Secret Service, ended in disaster, with the elections ultimately canceled and martial law declared due to the chaos created by a group of hackers led by Cybereason employees.
The first installment of this three part series delved deeply into Cybereason’s ties to the intelligence community of Israel and also other agencies, including the CIA, as well as the fact that Cybereason stood to gain little financially from the simulations given that their software could not have prevented the attacks waged against the U.S.’ electoral infrastructure in the exercise.
Also noted was the fact that Cybereason software could be potentially used as a backdoor by unauthorized actors, a possibility strengthened by the fact that the company’s co-founders all previously worked for firms that have a history of placing backdoors into U.S. telecommunications and electronic infrastructure as well as aggressive espionage targeting U.S. federal agencies.
The latter issue is crucial in the context of this installment of this exclusive MintPress series, as Cybereason’s main investors turned partners have integrated Cybereason’s software into their product offerings. This means that the clients of these Cybereason partner companies, the U.S. intelligence community and military among them, are now part of Cybereason’s network of more than 6 million endpoints that this private company constantly monitors using a combination of staff comprised largely of former intelligence operatives and an AI algorithm first developed by Israeli military intelligence.
Cybereason, thus far, has disclosed the following groups as lead investors in the company: Charles River Ventures (CRV), Spark Capital, Lockheed Martin and SoftBank. Charles River Ventures (CRV) was among the first to invest in Cybereason and has been frequently investing in other Israeli tech start-upsthat were founded by former members of the elite Israeli military intelligence Unit 8200 over the last few years. Spark Capital, based in California, appears to have followed CRV’s interest in Cybereason since the venture capitalist who co-founded Spark and led its investment in Cybereason is a former CRV partnerwho still has close ties to the firm.
While CRV and Spark Capital seem like just the type of investors a company like Cybereason would attract given their clear interest in similar tech start-ups coming out of Israel’s cyber sector, Cybereason’s other lead investors — Lockheed Martin and SoftBank — deserve much more attention and scrutiny.
Cybereason widely used by US Government, thanks to Lockheed
“A match made in heaven,” trumpeted Forbes at the news of the Lockheed Martin-Cybereason partnership, first forged in 2015. The partnership involved not only Lockheed Martin becoming a major investor in the cybersecurity company but also in Lockheed Martin becoming the largest conduit providing Cybereason’s software to U.S. federal and military agencies.
Indeed, as Forbes noted at the time, not only did Lockheed invest in the company, it decided to integrate Cybereason’s software completely into its product portfolio, resulting in a “model of both using Cybereason internally, and selling it to both public and private customers.”
Cybereason CEO and former offensive hacker for Israeli military intelligence — Lior Div — said the following of the partnership:
Lockheed Martin invested in Cybereason’s protection system after they compared our solution against a dozen others from the top industry players. The US firm was so impressed with the results they got from Cybereason that they began offering it to their own customers – among them most of the top Fortune 100 companies, and the US federal government. Cybereason is now the security system recommended by LM to its customers for protection from a wide (sic) malware and hack attacks.”
Rich Mahler, then-director of Commercial Cyber Services at Lockheed Martin, told Defense Daily that the company’s decision to invest in Cybereason, internally use its software, and include the technology as part of Lockheed Martin’s cyber solutions portfolio were all “independent business decisions but were all coordinated and timed with the transaction.”
How independent each of those decisions actually was is unclear, especially given the timing of Lockheed Martin’s investment in Cybereason, whose close and troubling ties to Israeli intelligence as well as the CIA were noted in the previous installment of this investigative series. Indeed, about a year prior to their investment in the Israeli military intelligence-linked Cybereason, Lockheed Martin opened an office in Beersheba, Israel, where the IDF has its “cyberhub”. The office is focused not on the sales of armaments, but instead on technology.
Marilyn Hewson, Lockheed Martin’s CEO, said the following during her speech that inaugurated the company’s Beersheba office:
The consolidation of IDF Technical Units to new bases in the Negev Desert region is an important transformation of Israel’s information technology capability… We understand the challenges of this move. Which is why we are investing in the facilities and people that will ensure we are prepared to support for these critical projects. By locating our new office in the capital of the Negev we are well positioned to work closely with our Israeli partners and stand ready to: accelerate project execution, reduce program risk and share our technical expertise by training and developing in-country talent.”
Beersheba not only houses the IDF’s technology campus, but also the Israel National Cyber Directorate, which reports directly to Israel’s Prime Minister, as well as a high-tech corporate park that mostly houses tech companies with ties to Israel’s military intelligence apparatus. The area has been cited in several media reports as a visible indicator of the public-private merger between Israeli technology companies, many of them started by Unit 8200 alumni, and the Israeli government and its intelligence services. Lockheed Martin quickly became a key fixture in the Beersheba-based cyberhub.
Not long before Lockheed began exploring the possibility of opening an office in Beersheba, the company was hacked by individuals who used tokens tied to the company, RSA Security, whose founders have ties to Israel’s defense establishment and which is now owned by Dell, a company also deeply tied to the Israeli government and tech sector. The hack, perpetrated by still unknown actors, may have sparked Lockheed’s subsequent interest in Israel’s cybersecurity sector.
Soon after opening its Beersheba office, Lockheed Martin created its Israel subsidiary, Lockheed Martin Israel. Unlike many of the company’s other subsidiaries, this one is focused exclusively on “cybersecurity, enterprise information technology, data centers, mobile, analytics and cloud” as opposed to the manufacture and design of armaments.
Haden Land, then-vice president of research and technology for Lockheed Martin, told the Wall Street Journal that the creation of the subsidiary was largely aimed at securing contracts with the IDF and that the company’s Israel subsidiary would soon be seeking partnership and investments in pursuit of that end. Land oversaw the local roll-out of the company’s Israel subsidiary while concurrently meeting with Israeli government officials. According to the Journal, Land “oversees all of Lockheed Martin’s information-systems businesses, including defense and civilian commercial units” for the United States and elsewhere.
Just a few months later, Lockheed Martin partnered and invested in Cybereason, suggesting that Lockheed’s decision to do so was aimed at securing closer ties with the IDF. This further suggests that Cybereason still maintains close ties to Israeli military intelligence, a point expounded upon in great detail in the previous installment of this series.
Thus, it appears that not only does Lockheed Martin use Cybereason’s software on its own devices and on those it manages for its private and public sector clients, but it also decided to use the company’s software in this way out of a desire to more closely collaborate with the Israeli military in matters related to technology and cybersecurity.
The cozy ties between Lockheed Martin, one of the U.S. government’s largest private contractors, and the IDF set off alarm bells, then and now, for those concerned with U.S. national security. Such concern makes it important to look at the extent of Cybereason’s use by federal and military agencies in the United States through their contracting of Lockheed Martin’s Information Technology (IT) division. This is especially important considering Israeli military intelligence’s history of using espionage, blackmail and private tech companies against the U.S. government, as detailed here.
While the exact number of U.S. federal and military agencies using Cybereason’s software is unknown, it is widespread, with Lockheed Martin’s IT division as the conduit. Indeed, Lockheed Martin was the number one IT solutions provider to the U.S. federal government up until its IT division was spun off and merged with Leidos Holdings. As a consequence, Leidos is now the largest IT provider to the U.S. government and is also directly partnered with Cybereason in the same way Lockheed Martin was. Even after its IT division was spun off, Lockheed Martin continues to use Cybereason’s software in its cybersecurity work for the Pentagon and still maintains a stake in the company.
The Leidos-Lockheed Martin IT hybrid provides a litany of services to the U.S. military and U.S. intelligence. As investigative journalist Tim Shorrock noted for The Nation, the company does “everything from analyzing signals for the NSA to tracking down suspected enemy fighters for US Special Forces in the Middle East and Africa” and, following its merger with Lockheed and consequential partnership with Cybereason, became “the largest of five corporations that together employ nearly 80 percent of the private-sector employees contracted to work for US spy and surveillance agencies.” Shorrock also notes that these private-sector contractors now dominate the mammoth U.S. surveillance apparatus, many of them working for Leidos and — by extension — using Cybereason’s software.
Leidos’ exclusive use of Cybereason software for cybersecurity is also relevant for the U.S. military since Leidos runs a number of sensitive systems for the Pentagon, including its recently inked contract to manage the entire military telecommunications infrastructure for Defense Information Systems Agency (DISA). In addition to maintaining the military telecom network, Cybereason is also directly partnered with World Wide Technologies (WWT) as of this past October. WWT manages cybersecurity for the U.S. Army, maintains DISA’s firewalls and data storage as well as the U.S. Air Force’s biometric identification system. WWT also manages contracts for NASA, itself a frequent target of Israeli government espionage, and the U.S. Navy. WWT’s partnership is similar to the Lockheed/Leidos partnership in that Cybereason’s software is now completely integrated into its portfolio, giving the company full access to the devices on all of these highly classified networks.
Many of these new partnerships with Cybereason, including its partnership with WWT, followed claims made by members of Israel’s Unit 8200 in 2017 that the popular antivirus software of Kaspersky Labs contained a backdoor for Russian intelligence, thereby compromising U.S. systems. The Wall Street Journal was the first to report on the alleged backdoor but did not mention the involvement of Unit 8200 in identifying it, a fact revealed by the New York Times a week later.
Notably, none of the evidence Unit 8200 used to blame Kaspersky has been made public and Kaspersky noted that it was actually Israeli hackers that had been discovered planting backdoors into its platform prior to the accusation levied against Kaspersky by Unit 8200. As the New York Times noted:
Investigators later discovered that the Israeli hackers had implanted multiple back doors into Kaspersky’s systems, employing sophisticated tools to steal passwords, take screenshots, and vacuum up emails and documents.”
Unit 8200’s claims ultimately led the U.S. government to abandon Kaspersky’s products entirely in 2018, allowing companies like Cybereason (with its own close ties to Unit 8200) to fill the void. Indeed, the very agencies that banned Kaspersky now use cybersecurity software that employs Cybereason’s EDR system. No flags have been raised about Cybereason’s own collaboration with the very foreign intelligence service that first pointed the finger at Kaspersky and that previously sold software with backdoors to sensitive U.S. facilities.
SoftBank, Cybereason and the Vision Fund
While its entry into the U.S. market and U.S. government networks is substantial, Cybereason’s software is also run throughout the world on a massive scale through partnerships that have seen it enter into Latin American and European markets in major ways in just the last few months. It has also seen its software become prominent in Asia following a partnership with the company Trustwave. Much of this rapid expansion followed a major injection of cash courtesy of one of the company’s biggest clients and now its largest investor, Japan’s SoftBank.
SoftBank first invested in Cybereason in 2015, the same year Lockheed Martin initially invested and partnered with the firm. It was also the year that SoftBank announced its intention to invest in Israeli tech start-ups. SoftBank first injected $50 million into Cybereason, followed by an additional $100 million in 2017 and $200 million last August. SoftBank’s investments account for most of the money raised by the company since it was founded in 2012 ($350 million out of $400 million total).
Prior to investing, Softbank was a client of Cybereason, which Ken Miyauchi, president of SoftBank, noted when making the following statement after Softbank’s initial investment in Cybereason:
SoftBank works to obtain cutting edge technology and outstanding business models to lead the Information Revolution. Our deployment of the Cybereason platform internally gave us firsthand knowledge of the value it provides, and led to our decision to invest. I’m confident Cybereason and SoftBank’s new product offering will bring a new level of security to Japanese organizations.”
SoftBank — one of Japan’s largest telecommunications companies — not only began to deploy Cybereason internally but directly partnered with it after investing, much like Lockheed Martin had done around the same time. This partnership resulted in SoftBank and Cybereason creating a joint venture in Japan and Cybereason creating partnerships with other tech companies acquired by SoftBank, including the U.K.’s Arm, which specializes in making chips and management platforms for Internet of Things (IoT) devices.
SoftBank’s interest in Cybereason is significant, particularly in light of Cybereason’s interest in the 2020 U.S. election, given that SoftBank has significant ties to key allies of President Trump and even the president himself.
Indeed, SoftBank’s Masayoshi Son was among the first wave of international business leaders who sought to woo then-president-elect Trump soon after the 2016 election. Son first visited Trump Tower in December 2016 and announced, with Trump by his side in the building’s lobby, that SoftBank would invest $50 billion in the U.S. and create 50,000 jobs. Trump subsequently claimed on Twitter that Son had only decided to make this investment because Trump had won the election.
Son told reporters at the time that the investment would come from a $100 billion fund that would be created in partnership with Saudi Arabia’s sovereign wealth fund as well as other investors. “I just came to celebrate his new job. I said, ‘This is great. The US will become great again,’” Son said, according to reports.
Then, in March of 2017, Son sent top SoftBank executives to meet with senior members of Trump’s economic team and, according to the New York Times, “the SoftBank executives said that because of a lack of advanced digital investments, the competitiveness of the United States economy was at risk. And the executives made the case, quite strongly, that Mr. Son was committed to playing a major role in addressing this issue through a spate of job-creating investments.” Many of SoftBank’s investments and acquisitions in the U.S. since then have focused mainly on artificial intelligence and technology with military applications, such as “killer robot” firm Boston Dynamics, suggesting Son’s interest lies more in dominating futuristic military-industrial technologies than creating jobs for the average American.
After their initial meeting, Trump and Son met again a year later in June 2018, with Trump stating that “His [Son’s] $50 billion turned out to be $72 billion so far, he’s not finished yet.” Several media reports have claimed that Son’s moves since Trump’s election have sought to “curry favor” with the President.
Through the creation of this fund alongside the Saudis, SoftBank has since become increasingly intertwined with Saudi Crown Prince Muhammad bin Salman (MBS), a key ally of President Trump in the Middle East known for his authoritarian crackdowns on Saudi elites and dissidents alike. The ties between Saudi Arabia and SoftBank became ever tighter when MBS took the reins in the oil kingdom and after SoftBank announced the launch of the Vision Fund in 2016. SoftBank’s Vision Fund is a vehicle for investing in hi-tech companies and start-ups and its largest shareholder is the Public Investment Fund of Saudi Arabia. Notably, Son decided to launch the Vision Fund in Riyadh during President Trump’s first official visit to the Gulf Kingdom.
In addition, the Mubadala Investment Company, a government fund of the United Arab Emirates (UAE), gave $15 billion to the Vision Fund. UAE leadership also share close ties to the Trump administration and MBS in Saudi Arabia.
As a consequence, SoftBank’s Vision Fund is majority funded by two Middle Eastern authoritarian governments with close ties to the U.S. government, specifically the Trump administration. In addition, both countries have enjoyed the rapid growth and normalization of ties with the state of Israel in recent years, particularly following the rise of current Saudi Crown Prince Muhammad bin Salman and Jared Kushner’s rise to prominence in his father-in-law’s administration. Other investments in the Vision Fund have come from Apple, Qualcomm and Oracle’s Larry Ellison, all tech companies with strong ties to Israel’s government.
The Saudi and Emirati governments’ links to the Vision Fund are so obvious that even mainstream outlets like the New York Times have described them as a “front for Saudi Arabia and perhaps other countries in the Middle East.”
SoftBank also enjoys close ties to Jared Kushner, with Fortress Investment Group lending $57 million to Kushner Companies in October 2017 while it was under contract to be acquired by SoftBank. As Barron’s noted at the time:
When SoftBank Group bought Fortress Investment Group last year, the Japanese company was buying access to a corps of seasoned investors. What SoftBank also got is a financial tie to the family of President Donald Trump’s senior advisor and son-in-law, Jared Kushner.”
According to The Real Deal, Kushner Companies obtained the financing from Fortress only after its attempts to obtain funding through the EB-5 visa program for a specific real estate venture were abandoned after the U.S. Attorney and the Securities and Exchange Commission began to investigate how Kushner Companies used the EB-5 investor visa program. A key factor in the opening of that investigation was Kushner Companies’ representatives touting Jared Kushner’s position at the White House when talking to prospective investors and lenders.
SoftBank also recently came to the aid of a friend of Jared Kushner, former CEO of WeWork Adam Neumann. Neumann made shocking claims about his ties to both Kushner and Saudi Arabia’s MBS, even asserting that he had worked with both in creating Kushner’s long-awaited and controversial Middle East “peace plan” and claimed that he, Kushner and MBS would together “save the world.” Neumann previously called Kushner his “mentor.” MBS has also discussed on several occasions his close ties with Kushner and U.S. media reports have noted the frequent correspondence between the two “princelings.”
Notably, SoftBank invested in Neumann’s WeWork using money from the Saudi-dominated Vision Fund and later went on to essentially bail the company out after its IPO collapse and Neumann was pushed out. SoftBank’s founder, Masayoshi Son, had an odd yet very close relationship with Neumann, perhaps explaining why Neumann was allowed to walk with $1.7 billion after bringing WeWork to the brink of collapse. Notably, nearly half of SoftBank’s approximately $47 billion investments in the U.S. economy since Trump’s election, went to acquiring and then bailing out WeWork. It is unlikely that such a disastrous investment resulted in the level of job creation that Son had promised Trump in 2016.
Given that it is Cybereason’s top investor and shareholder by a large margin, SoftBank’s ties to the Trump administration and key allies of that administration are significant in light of Cybereason’s odd interest in 2020 U.S. election scenarios that end with the cancellation of this year’s upcoming presidential election. It goes without saying that the cancellation of the election would mean a continuation of the Trump administration until new elections would take place.
Furthermore, with Cybereason’s close and enduring ties to Israeli military intelligence now well-documented, it is worth asking if Israeli military intelligence would consider intervening in 2020 if the still-to-be-decided Democratic contender was strongly opposed to Israeli government policy, particularly Israel’s military occupation of Palestine. This is especially worth considering given revelations that sexual blackmailer and pedophile Jeffrey Epstein, who targeted prominent U.S. politicians, mostly Democrats, was in the employ of Israeli military intelligence.
Notably, Cybereason’s doomsday election scenarios involved the weaponization of deep fakes, self-driving cars and hacking Internet of Things devices, with all of those technologies being pioneered and perfected — not by Russia, China or Iran — but by companies directly tied to Israeli intelligence, much like Cybereason itself. These companies, their technology and Cybereason’s own work creating the narrative that U.S. rival states seek to undermine the U.S. election in this way, will all be discussed in the conclusion of MintPress’ series on Cybereason and its outsized interest in the U.S. democratic process.
Israeli Proxies Profit from U.S. Coronavirus Funding
By Philip Giraldi • Unz Review • July 14, 2020
Washington D.C. is surely one of the most corrupt places on earth. Money talks and nearly everyone into the game sometimes referred to as politics has his or her hand out and expects to end up a millionaire. Given that, it should surprise no one to learn that a large chunk of the CARES Business Assistance Program’s trillions of dollars recently doled out for coronavirus relief, sold to the public as intended to help small businesses survive, has instead gone to those who are politically connected through lobbyists and other special interests.
A recent Time magazine article describes what it calls “a familiar lobbying bonanza.” To be sure, the details regarding who got the cash makes for depressing reading, though there is a familiar smell to it in light of the many boondoggled programs to make America “safe” over the past twenty years. The Paycheck Protection Program (PPP) has provided no less than 663,000 loans over $150,000, but much of the money has gone to “billionaires, country clubs, lobbyists, political allies, Wall Street, and big business,” all of which have better access to government than does the small business owner.
Recipients included 600 mostly large equity and asset management firms that were actually ineligible because of their involvement in “investment or speculation.” Cash rich law firms also benefited with more than 45 of top firms receiving at least $210 million in PPP loans while companies owned in whole or part by nine congressmen also received funds. A business partially owned by Paul Pelosi, husband of Speaker Nancy Pelosi, obtained a loan as did a real estate project run by the family of Jared Kushner.
Other decidedly questionable recipients include Planned Parenthood, the Church of Scientology, and rapper Kanye West, up until recently a Trump favorite, who, with his wife Kim Kardashian, owns a shoe and clothing company worth an estimated $3 billion.
Given the apparent fact that obtaining a loan was largely a matter of who you know, it is perhaps not surprising that the state of Israel and its myriad supporting entities in the United States were in front of the line when the money was passed out.
I recently wrote about the apparent holocaust scam run out of Israel whereby gullible foreigners have been receiving emails and seeing media solicitations regarding how Jewish survivors of World War 2 currently in Israel are living in squalor and starving due to the impact of the coronavirus. Readers commented that there are similar ads running on television in the U.S. soliciting money from “Christians and Jews” to help relieve the suffering. There have recently been allegations of fraud regarding the millions of dollars that have been raised by Christian groups in the United States. As Israel is a wealthy, socialist state with world class medical and social services systems in part paid for by the U.S. taxpayer, as well as pensions provided mostly by Germany for all survivors, the entire business definitely has a bad smell to it.
If so-called holocaust survivors are actually suffering, the fault should be firmly placed where it belongs: the Jewish “charitable” organizations and the state of Israel itself, which are custodians for the money coming from Europe and elsewhere. Professor Norman Finkelstein has demonstrated in his book The Holocaust Industry: Reflections on the Exploitation of Jewish Suffering how all the billions of dollars extorted by Israel and Jewish groups has been diverted and rarely reaches those who might actually have suffered.
A review of the Finkelstein book notes “…that very little of the recently extracted ‘compensation’ has reached its nominal beneficiaries. Instead, the industry’s concern today lies with winning compensation for law firms, consultants, politicians, Holocaust organizations, and industry elites. ‘When Jewish elites rob Jewish survivors no ethical issues arise; it’s just about the money…’”
In the current economic and healthcare crisis, some of these groups including Israeli start-up companies and proxy groups that lobby in the United States are eligible to received PPP under the multi-trillion dollar CARES Business Assistance Program as long as they have some salaried U.S. employees. The loans can be up to two and a half times the cost of wages actually paid to employees up to a total of $10 million and are issued at 1% interest that is repayable within two years, with a six-month grace period before payments are due. The loan would be converted into a grant if the company can demonstrate that the money was actually spent on salaries that prevented terminating employees.
Predictably, Israeli connected law firms in the U.S. were immediately out of the starting gates. “’In this program, it’s all about being first to the prize,’ said Attorney Oz Halabi, a partner and head of the U.S. taxation department at the New York office of law firm Pearl Cohen Zedek Latzer Baratz and a former senior official at the Israel Tax Authority. ‘It is very important to submit applications as soon as possible and to understand that the program is relevant to 99% of Israeli startups.’”
Because Israeli companies are well wired into political and financial power brokers in Washington and New York, they inevitably have had insider help applying early and obtaining immediate approvals for loans that struggling American small businesses will not receive. Reportedly 1,000 Jewish and Israel linked groups have already received $500 million but then proceeded to lay off employees anyway after they received their money. There has been, of course, no reciprocity of tax breaks or loans for U.S. companies operating in Israel.
The full measure of PPP spending has yet to be appreciated, but Grant Smith at the Institute for Research: Middle East Policy (IRMEP) has described a C-Span interview that reveals the extent to which Israel has taken advantage of CARES. Smith reports that “Israel lobby organizations such as the Zionist Organization of America ($2-5 million), Friends of the IDF ($2-5 million) and the Israeli American Council ($1-2 million) are grabbing huge loans from the CARES Act PPP program. According to SBA data, Israel’s Bank Leumi has doled out a quarter to a half billion dollars under the program, despite being called out for operating in the occupied West Bank. It has given sweetheart deals to the Israeli company Oran Safety Glass (which defrauded the U.S. Army on bulletproof glass contracts) and Energix, which operates power plants in the occupied Golan Heights and West Bank.”
Grant has also identified PPP money going to the Jewish Institute for National Security of America (JINSA), which inter alia arranges “terrorism” training for American police; the Jewish National Fund, which supports Israel’s illegal settlements; and the Israel on Campus Coalition, which has harassed students critical of the Jewish state on American campuses. Several of the organizations being supported with American taxpayer money are little more than front organizations promoting Israeli interests in the U.S. They should be required to be registered under the Foreign Agents Registration Act (FARA) of 1938 but the Justice Department never does anything about Israeli government fronts active in the United States.
Note that an Israeli bank has somehow been able to grant as much as a half billion dollars of U.S. taxpayer money under the program, all of it apparently going to Israeli businesses and other Israel-linked entities. One wonder what the screening process was like, if there even was one. And note that the Zionist Organization of America is essentially an Israeli lobbying group. It too gets the cash, as does the similar Israeli America Bank. Oran Safety Glass, which “won” a Pentagon contract for bulletproof glass for U.S. Army vehicles even though it could not produce the glass, also gets money.
But the most outrageous grant is to the Friends of the Israel Defense Forces (FIDF), an organization that raises money in the U.S. for the Israeli military. It held a gala event in Hollywood in 2017 that raised $53.8 million while one in New York City in the same year promoted as a “A Night of Heroes” raised $35 million, so it clearly does not need the money but took it anyway. Donations to FIDF are tax deductible as the organization is registered with the U.S. Treasury as a 501(c)3 educational and charitable non-profit foundation. One might well ask how it is possible that the American taxpayer should subsidize a foreign military organization that is regularly accused of war crimes in its ongoing brutal and genocidal occupation of the Palestinian West Bank and East Jerusalem? Where are the screams of outrage from Congress and the media, which are silent even as an estimated 100,000 American small businesses meanwhile go bust?
The multitude of gifts to Israel come at a time when the cover provided by the coronavirus and the BLM disruption have hidden from sight the expansion of the Israeli-American national security state. Writing at MintPress in an article entitled “The Merging of US and Israeli National Security States is Accelerating Amid COVID-19,” Raul Diego reports that:
“A two-pronged initiative by the U.S. Chamber of Commerce and the Department of Homeland Security is set to substantially increase Israel’s already significant role in America’s digital health, artificial intelligence (AI), critical health infrastructure, as well as law enforcement, public and border protection and other key sectors. Citing ‘health challenges’ posed by COVID-19, the U.S.-Israel Business Initiative (USIBI), a venture of the U.S. Chamber of Commerce, is advancing a new eight-point policy framework to facilitate a ‘more robust bilateral collaboration’ between Israeli and American companies to realize the ‘potential’ of technologies emerging out of Israel relating to telehealth, robotic diagnostics and AI-powered applications in healthcare.”
Diego also observes how “In a recent article, investigative reporter Whitney Webb uncovered the deep Israeli military roots of virtually every ‘health’ tech startup to emerge in the wake of the COVID-19 pandemic and their extensive relationships with the U.S. government at both the federal and state level. Regarding the policy framework, Webb stated that it was likely ‘part of a broader effort aimed at using the coronavirus crisis to facilitate the integration of Israeli tech companies, particularly in the “digital health” sector, into the U.S. technology ecosystem. Many, if not the vast majority, of these companies’, she continued, ‘were either founded by ex-members of Israeli intelligence or military intelligence, but also serve as contractors to Israel’s government or its military.’”
Inevitably, the rape of America and its remaining resources by Israel will accelerate with hardly a peep out of politicians or the media. The U.S. Chamber of Commerce U.S.-Israel Business Initiative only works in one direction, delivering money and jobs to Israel as it simultaneously makes Americans poorer and unemployed. The joint projects also enable the stealing of U.S. technology to advance the Jewish state’s own high-tech sector at no cost. There will also be major national security implications as the Israelis will be able to access every telephone to confront “health challenges” while monitoring the movement of Americans as they also record classified conversations to send the “take” back to Jerusalem.
And it all starts with the presumption that Israel is some kind of friend, which it is not. Fake charities and various schemes to otherwise defraud and impoverish the U.S. taxpayer is the name of the game and Israel goes on from there to become a “business arrangement” and “health initiative partner” plus “national security asset.” When will it ever end? Ask your congressman. He or she will not reply. Or write a letter to the Washington Post or New York Times. They will not print it.
Philip M. Giraldi, Ph.D., is Executive Director of the Council for the National Interest, a 501(c)3 tax deductible educational foundation (Federal ID Number #52-1739023) that seeks a more interests-based U.S. foreign policy in the Middle East. Website is https://councilforthenationalinterest.org, address is P.O. Box 2157, Purcellville VA 20134 and its email is inform@cnionline.org.
A Busy Hurricane Season? Maybe, But It Won’t Be Due To Global Warming
Today’s fake news from the BBC
By Paul Homewood | Not A Lot Of People Know That | July 12, 2020

Tropical Storm Fay brought strong winds, heavy rain and local flooding to north eastern states of the USA in the last few days.
It was the earliest “F” named storm on record and follows fast on the heels of the earliest “E” – Edouard – which formed earlier in the week.
And we may be looking at more to come. In an update to their hurricane season forecast, which includes all storms which are given a name, specialists at Colorado State University are now predicting there could be 20 named storms – up from 16 in their previous forecast. The long term average is 12.
And when it comes specifically to hurricanes – storms with winds of more than 74mph – that’s gone up too, from eight to nine. The forecast for the number of major hurricanes – Category 3 or above – stays at four.
This is the sixth consecutive year that has seen named tropical storms before the official start of the hurricane season on 1 June. Arthur and Bertha formed in May, also marking the first time since 2012 that two storms formed in that month. Cristobal, Edouard and Fay became, respectively, the earliest third, fifth and sixth named storms on record.
None of these storms became particularly large, which may have had something to do with the unusually large amounts of Saharan dust – a hurricane inhibitor – across the Atlantic.
It may well be that this year will see an above average number of storms – that is what averages are all about.
But the idea that this year, and indeed recent years, are anything special is ludicrous. This is, of course, the implication from the claim that there could be 20 named storms – up from 16 in their previous forecast. The long term average is 12.
The average of 12 is based on 1968 to 2018, but in the early days it was still common to miss many short lived storms out in the middle of the Atlantic, even as recently as the 1990s.
A comparison of 1968 and 2018 shows clearly how very few mid Atlantic storms were picked up in 1968, despite the early beginnings of satellite monitoring.


https://www.aoml.noaa.gov/hrd/hurdat/DataByYearandStorm.html
And even when they struck the US, they were not even given names all of the time:


https://www.aoml.noaa.gov/hrd/hurdat/uststorms.html
The only meaningful trends that can be drawn are for US landfall storms in the last 30 years, and HURDAT data shows clearly that tropical storms and hurricanes have become much less frequent in the last decade:

https://www.aoml.noaa.gov/hrd/hurdat/uststorms.html
So far this summer, three tropical storms have hit the US, so there is no sign that this summer will end up being unusual.
The BBC article ends:

The three factors are :
- A warm Atlantic
- Thunderstorms in Central Africa
- La Nina
Weasel words indeed! The actual data, of course, shows that there has been no long term trend in Atlantic hurricanes, which rather puts paid to the BBC’s climate stirring.
In the past the BBC have had to retract claims that climate change was making hurricanes worse, following my complaints. Having had their fingers burned once, they have obviously decided to be more circumspect!
Featured Video
Dan Dicks with James Corbett on Solutions Watch
or go to
Aletho News Archives – Video-Images
From the Archives
$1.5bn up in smoke: US THAAD missile stockpile dries up defending Israel against Iran
By Ivan Kesic | Press TV | July 2, 2025
According to American media, defense news outlets, and independent analysts, the 12-day Israeli military aggression against Iran significantly depleted the US stockpile of THAAD (Terminal High Altitude Area Defense) interceptor missiles.
Citing official sources, American magazine Newsweek reported on Friday that the US transferred a substantial portion of its advanced missile defense capabilities to support the Israeli regime, an effort with questionable results and a critical impact on US strategic reserves.
THAAD, developed by Lockheed Martin arms manufacturing company, is a key component of Israel’s multi-layered air defense architecture. It is designed to intercept medium-range ballistic missiles, including those launched from Iran and Yemen.
The US-made system is capable of targeting short-, medium-, and intermediate-range ballistic missiles during their terminal phase, whether inside or outside Earth’s atmosphere.
THAAD uses a “hit-to-kill” method, relying on kinetic energy rather than explosive warheads to destroy incoming threats, intercepting at altitudes of up to 150 km and ranges between 150-200 km.
Operated exclusively by American personnel, the US military maintains eight THAAD batteries with an estimated 350–400 interceptors in total. The eighth battery was activated during the June 20 Israeli aggression against Iran and is capable of intercepting hypersonic missiles. … continue
Blog Roll
 Aletho News
- Zionist Bought Senate Blocks Information About American Citizens Killed By Israel
- While Gaza dominates the UN, these are the people keeping it alive
- New Report: “Scholasticide and Genocide in Gaza: Assessment, Testimonies and Legal Analysis”
- ‘THAAD Delusion’: Iran war exposes US missile shield limits – The Atlantic
- Moscow issues warning to NATO over Russian exclave
- Yes, the Iran war has destroyed Trump’s presidency
- The fallacy of US delusions about Iran’s economic collapse
- Hezbollah denies Syria cell link, warns of Israeli plan to sow discord
- The legacy of US sanctions, war, and occupation in Iraq
- Iraqi resistance group rejects disarmament, vows to maintain support for Lebanon
- If Americans Knew
- Mamdani releases plan to combat antisemitism and hate crimes in New York City
- Iran’s Revolutionary Guards Publish Letter to the American People
- DMFI launches $1 million ad campaign supporting Virginia’s Elaine Luria
- US Senate blocks resolution seeking report on Americans killed by Israel
- Israeli Attacks Kill Ten Palestinians in Gaza
- Massacre at Minab: The School That Became a Grave
- Israeli media: The IDF Shows It Doesn’t Turn a Blind Eye; It Actively Emboldens Settler Havoc
- As settlers ravage West Bank, Israeli forces kill 10 in Gaza – Daily Update
- New Report: “Scholasticide and Genocide in Gaza: Assessment, Testimonies and Legal Analysis”
- Ex-Biden officials are desperate for a Gaza scapegoat
- No Tricks Zone
- Green Energy Debacle: German Expert Professor Fritz Vahrenholt Warns Of Severe Economic And Social Consequences
- Two More Paleo Reconstructions Affirm Meters-Higher Sea Levels Across Ireland, Brazil 7000-6000 Years Ago
- New Study: Earth And Venus Surface Warmth Largely Explained By Convection And Lapse Rate, Not CO2 Or Radiation
- 2025 Nature Paper Claiming Worsening Global Drought Gets RETRACTED …Heavily Flawed
- New Study: ‘Global Drought Shows No Detectable Recent Acceleration Under Climate Warming’
- Economic Masterminds: German Socialists Suggest Taxing Productivity Gains Stemming From Using AI
- The South China Sea Has Not Been Cooperating With The Climate Change Narrative
- Energy Crisis: Germany Enters Heating Season With Historically Low Gas Reserve Fill Levels
- New Study: The Antarctic Ice Sheet Gained Mass From 2020-2024 Due To Staggering Snow And Ice Accumulation
- Study: Ocean Heating Rates From Thousands Of Years Ago ‘Dwarf’ Modern Ocean Heating Rates

