Cybereason Announces New Plans to “Accelerate” Access to US Govt Networks Ahead of 2020 Election
By Whitney Webb | The Last American Vagabond | July 27, 2020
A cybersecurity firm tied to Israeli intelligence’s Unit 8200 that simulated a series of terrorist attacks occurring on the U.S. 2020 election has announced a new hire with deep ties to the U.S. intelligence and defense communities with the goal of gaining greater access to U.S. government networks.
A cybersecurity company tied to Israeli intelligence and a series of unnerving simulations regarding cyber-terrorist attacks on the upcoming U.S. elections has recently announced a new hire who plans to aid the company in further penetrating the U.S. public sector. Last Wednesday, the company Cybereason announced that it had hired Andrew Borene as its Managing Director for its recently launched U.S. public sector business. Borene, who boasts longstanding ties to the U.S. intelligence community and the Pentagon, “will accelerate Cybereason’s partner and customer presence in the U.S. public sector,” according to a Cybereason press release.
“My goal is to build a strong business for Cybereason within the U.S. public sector and I am planning to recruit a group of direct support executives, veterans and alumni of the elite [U.S.] military units and agencies that have defended our nation in the information age. I’ll also work to establish a network of the best channel and delivery partners for federal, state and local governments,” Borene said per the press release.
Eric Appel, Cybereason’s General Manager for North American Sales, stated that “We’re excited about Andrew joining Cybereason and the opportunity in the U.S. public sector for Cybereason to make a profound impact on helping the nation’s federal civilian, military, state and local government agencies…”
Borene will likely be successful in his ability to recruit a sales team of prominent alumni from the U.S. intelligence and defense communities to market Cybereason’s products throughout the U.S. government. Prior to joining Cybereason, Borene was a senior advisor to the Intelligence Advanced Research Projects Activity (IARPA), the intelligence community’s “DARPA” equivalent that is housed within the Office of the Director of National Intelligence (ODNI). He served in that capacity on behalf of intelligence contractor Booz Allen Hamilton. Prior to that, Borene served as Associate Deputy General Counsel to the Pentagon and was previously a military intelligence officer for the U.S. Marine Corps.
Borene’s private sector experience is also significant, as he was a senior executive at IBM. Notably, the current Chief Information Officer for the CIA, Juliane Gallina, had served alongside Borene as a top IBM executive prior to taking her current position at the agency. In addition, Borene also boasts ties to Wall Street as a veteran of Wells Fargo’s investment banking division.
In addition, Borene has deep ties to Washington’s foreign policy establishment as a “life member” of the Council on Foreign Relations (CFR) and to the national security-think tank nexus through his senior fellowship at the National Security Institute (NSI). NSI’s board includes former NSA directors, Keith Alexander and Michael Hayden (also a former CIA director); former Deputy Defense Secretary and “architect” of the Iraq War, Paul Wolfowitz; former director of the Defense Intelligence Agency, David Shedd; and a variety of other former top intelligence and defense officials as well as Silicon Valley executives and venture capitalists.
Notably, Borene is the latest addition to Cybereason with ties to the U.S. intelligence and defense communities as the company’s advisors include Robert Bigman, former Chief Information Security Officer for the CIA as well as Peter Sherlock, the former Chief Operating Officer of MITRE corporation, a major intelligence and defense contractor connected to the Ptech-9/11 controversy.
Cybereason: a front for Israeli Military Intelligence
Cybereason’s announcement of its hire of Andrew Borene coincided with its launch of its new “U.S. public sector business,” meaning that Cybereason now seeks to have its cybersecurity software running on even more of the U.S. government’s most classified networks. Cybereason, for years, has already been running on several sensitive U.S. government networks through its partnerships with IT contractors for intelligence and defense, such as Lockheed Martin (also a Cybereason investor), WWT and Leidos. However, Borene’s hire and this new publicly announced pivot towards the U.S. public sector clearly demonstrates the company’s interest in further deepening its presence on U.S. government networks.
Cybereason’s pivot is concerning for several reasons. First, its co-founders are alumni of Israel’s Unit 8200, an elite unit of the Israeli Intelligence corps that is part of the IDF’s Directorate of Military Intelligence and is involved mainly in signal intelligence, surveillance, cyberwarfare and code decryption. It is also well-known for its surveillance of Palestinian civilians and for using intercepted communications as blackmail in order to procure informants among Palestinians living under occupation in the West Bank.
In addition, all three Cybereason co-founders, after leaving Unit 8200, went on to work for two private Israel-based tech/telecom companies with a notorious history of aggressive espionage against the U.S. government: Amdocs and Comverse Infosys (the latter is now known as Verint Systems Inc.). This raises the possibility that Cybereason software could potentially be used as a backdoor by unauthorized actors, given that the company’s co-founders all previously worked for firms that have a history of placing backdoors into U.S. telecommunications and electronic infrastructure as well as aggressively spying on U.S. federal agencies.
Also notable is the fact that the company’s current CEO and co-founder Lior Div was much more than the average Unit 8200 officer during his time in the unit, as he “served as a commander [in Unit 8200] and carried out some of the world’s largest cyber offensive campaigns against nations and cybercrime groups. For his achievements, he received the Medal of Honor, the highest honor bestowed upon Unit 8200 members,” according to his biography. Troublingly, in an interview that Div gave to TechCrunch last year, Div stated that his work at Cybereason is “the continuation of the six years of training and service he spent working with the Israeli army’s 8200 Unit.”
This is particularly noteworthy given that Israel’s government has openly admitted that an on-going intelligence operation, first initiated in 2012 – the year Cybereason was founded, involves Israeli military intelligence and intelligence operations that had previously done “in house” (i.e. as part of Unit 8200, Mossad, etc.) being spun off into private companies, specifically start-ups in the “cyber” realm.
This operation is part of Israeli Prime Minister Benjamin Netanyahu’s “deliberate policy” to have former members of Israel’s “military and intelligence units … merge into companies with local partners and foreign partners” in order to make it all but impossible for major corporations and foreign governments to boycott Israel and to also to ensure that Israel becomes the world’s dominant “cyber power.”
One notable report on this policy, published by Israeli outlet Calcalist Tech, interviewed dozens of Israeli military, intelligence and government officials and noted that “since 2012, cyber-related and intelligence projects that were previously carried out in-house in the Israeli military and Israel’s main intelligence arms are transferred to companies that in some cases were built for this exact purpose.” The article also states that beginning in 2012, Israel’s intelligence and military intelligence agencies began to outsource “activities that were previously managed in-house, with a focus on software and cyber technologies.”
“Simulating” the Cancellation of the 2020 Election
In light of Cybereason’s background and the “acceleration” of their presence on U.S. government networks, the timing of their redoubled efforts to court the U.S. public sector add additional layers of concern given that it precedes the U.S. 2020 election by a matter of months. Since last year, Cybereason has conducted multiple simulations focused on the 2020 election, which were attended by federal officials from the FBI, DHS and the U.S. Secret Service and all of which ended in disaster. In those simulations, the 2020 election was ultimately canceled and martial law was then declared due to the chaos created by a group of hackers led by Cybereason employees.
Notably, Cybereason stood to gain nothing financially from the simulations given that their software could not have prevented the attacks waged against the U.S.’ electoral infrastructure in the exercise and the company framed their hosting of the simulations as merely “altruistic” because of their professed desire to help “protect” U.S. election infrastructure. The attacks conducted in the simulations by Cybereason employees included creating power grid blackouts, the use of deep fakes to sow confusion, creating havoc with municipal sewage systems and crashing self-driving cars into voters waiting in line to cast their ballots, killing 32 and injuring over a hundred people.
In the months since I first wrote about Cybereason and their 2020 “doomsday” simulations back in January, U.S. government officials and mass media alike have been warning that these same types of attacks that Cybereason simulated are likely to come to pass on this upcoming election day, scheduled for November 3rd of this year. More recently, in less than a week, headlines like “Election Security Experts Expect ‘Chaos’ Unless Action Taken,” “New York’s Pandemic Voting ‘Chaos’ Set to Go Nationwide in November,” and “Foreign adversaries ‘seeking to compromise’ presidential campaigns, intel warns,” among others, have been published in major U.S. media outlets.
While these narratives have asserted that China, Russia and/or Iran will be to blame for such attacks, it is worth noting that a tight-knit web of Israeli state-owned and private companies tied to Israeli military intelligence now run the software controlling key parts of the power grid in New York, California and elsewhere in the U.S.; are the main global producers of deep fakes; and the main providers of “security” software for self-driving and semi-self-driving cars, the quantity of which on U.S. streets has grown dramatically as a result of the coronavirus crisis.
With Cybereason’s newly announced push to run its software on critical U.S. government networks at both the federal and state levels, the company’s history of simulating terror attacks on critical U.S. infrastructure and their openly admitted and on-going ties to Israeli military intelligence deserve more scrutiny than ever as the U.S. election draws closer.
Israeli duplicity about 2014 invasion ‘Operation Brothers Keeper’
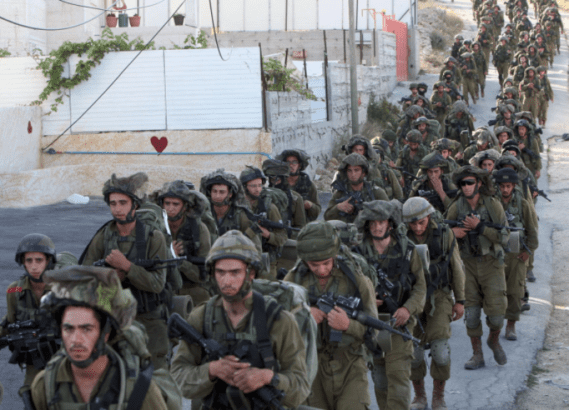
Operation Brothers Keeper, an Israeli initiative supposedly launched to rescue three Jewish Israeli teenagers who had been kidnapped.
By Kathryn Shihadah | If Americans Knew | July 15, 2020
“Operation Brothers Keeper” has a nice ring to it, but the name represents months of duplicity by Israeli leaders, not only toward their own people, but toward the world, in order to perpetrate injustices on the people of Palestine.
The summer of 2014, when Operation Brothers Keeper emerged, was an exceptionally violent season in a decades-long stretch of violence in Israel and the occupied Palestinian territories – a conflict defined by the Palestinian struggle for self-determination and against confiscation of their land; a conflict that has consistently seen many times more Palestinian casualties than Israelis.
Palestinians took to the streets that summer for much the same reason they always had: to struggle against oppression. The Israeli military came out to defend Israel’s status as oppressors.
Some context
Operation Brothers Keeper (OBK) was an invasion of the Palestinian West Bank, launched after the kidnapping of three Jewish Israeli teenagers. (This presaged its massive July invasion of Gaza, “Operation Protective Edge.”)
Perhaps, in the Israeli consciousness, the West Bank invasion was an isolated event – but for Palestinians, OBK was another in a long line of oppressive tactics within a framework of illegal occupation and injustice.
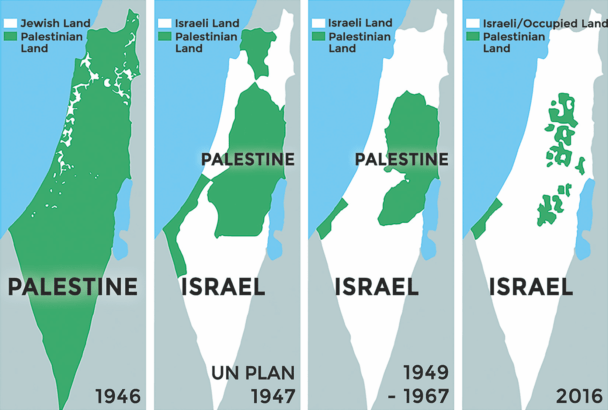
Maps show Palestinian loss of land from Israel’s 1948 creation through the present
In the early 20th century, massive Jewish immigration had caused concern among the indigenous Palestinians in the land; by 1948, 750,000 Palestinians were forced from their homes and land, most to never return as it became part of a new Jewish state. 1967 saw the occupation of all remaining Palestinian territories; 2008-9 had witnessed Israel’s devastating invasion of Gaza that killed 1,400 Palestinians (and 9 Israelis). In between these events, Israel had kept the Palestinian people under constant oppression – and the Palestinian people had resisted.
In late 2012, Israel had invaded the Palestinian Gaza Strip in a conflict that lasted 8 days before a ceasefire was put in place.
At that time, Israel promised to end its attacks on Gaza by land, sea, and air, stop assassinations of Gazan officials, and lift its blockade of Gaza, then in its 5th year; Hamas leaders in Gaza vowed to end rocket fire toward Israel (rockets that had killed 21 Israelis in 12 years).
Gaza held up its end of the deal: throughout 2013, rockets from Gaza were few and far between, and just one Israeli was killed in the vicinity. (5 more Israelis were killed elsewhere.)
Israel did not keep its promises: its military invaded Gaza and shot at Palestinian farmers and fishermen; the blockade remained in place, keeping food, medicine, and other staples out of the hands of those who needed them desperately. (Read here about the “period of calm” during the first 3 months after the 2012 ceasefire, during which Israelis experienced calm, but Palestinians were attacked on a daily basis.)
Nine Gazans were killed in 2013, over 30 other Palestinians were killed elsewhere. In the first 5 months of 2014 – before the Israeli teens were kidnapped – dozens of Palestinians, some of them teens, and 2 Israelis, were killed.
The Israeli blockade of Gaza remained in place (it is still in place today).
Kidnapping
On June 12th, the three Israelis, aged 16 – 19, were kidnapped while hitchhiking.
All three were yeshiva (Jewish religious school) students, and would have almost certainly become soldiers in the Israeli Defense Forces (IDF). Israel practices universal conscription of both males and females at age 18 – although it is possible to delay or even avoid military service by continuing religious education after high school, as was likely the case with the older kidnapping victim. (Go here to read about religious extremism in some Israeli yeshivot.)
One of the teens called an emergency number for help. Along with his voice, the call also recorded shouting in Arabic and several gunshots.
Several hours later, parents of one of the boys reported him missing, at which point the police began to make the connection with the emergency call, which they originally believed to be a prank.
Netanyahu at press conference with DM Moshe Ya’alon during Operation Brothers Keeper (AFP)
Deception and brutality
The Forward reports that the Israeli government “had known almost from the beginning that the boys were dead. It maintained the fiction that it hoped to find them alive as a pretext to dismantle Hamas’ West Bank operations.”
The prime suspects, Palestinians, were identified within hours of the incident, and known to be rogue, with “a reputation for attacking Israeli civilian targets” and regularly acting “counter to the policies being advocated by [Hamas].” Their family disclosed within a day of the kidnapping that the men had disappeared.
Instead of broadcasting photos of the suspects and preparing the country for the inevitable locating of bodies rather than hostages, Israeli PM Benjamin Netanyahu immediately imposed a gag order on the media.
Even the parents of the kidnapped teens were led to believe that the boys were still alive.
Publicly, Netanyahu consistently claimed that he knew “for a fact” that Hamas was behind the kidnapping – in fact, at no point did any evidence point to Hamas’ participation in the incident; its leaders consistently denied involvement.
Meanwhile, ironically, the Israeli police cautioned the public against “spreading rumors on social media.”
On June 15th, Netanyahu launched Operation Brothers Keeper, characterizing it as a “hostage rescue operation.” Behind the scenes, however, he commissioned 2,500 Israeli soldiers, plus special forces, on a rampage through the West Bank in search not of hostages, but of Hamas members. According to The Nation :
Israel arrested approximately 800 Palestinians without charge or trial, killed nine civilians and raided nearly 1,300 residential, commercial and public buildings.
The operation kept 300,000 Palestinians under curfew; movement was restricted for another 600,000 – a form of illegal collective punishment.
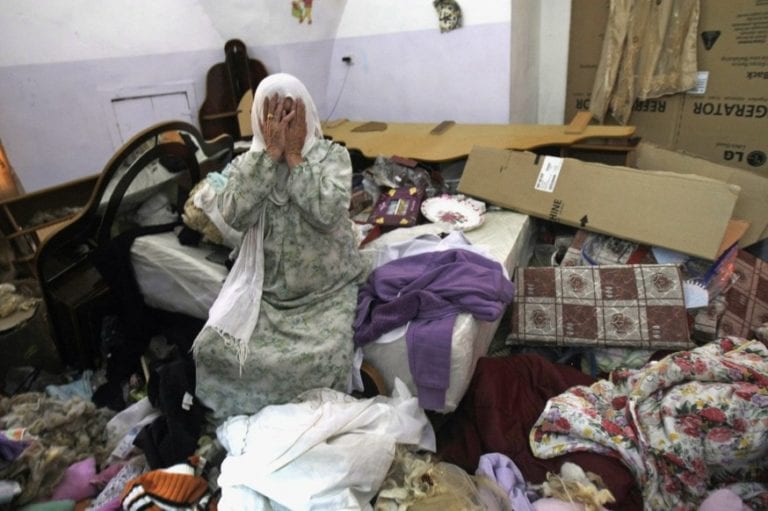
A Palestinian woman cries in her home after a raid by Israeli troops as part of Operation Brothers Keeper, Sunday, June 22,2014. (AP Photo/Nasser Ishtayeh)
As far as Israeli citizens knew, the killers could be anyone, anywhere; the vast majority were therefore supportive of whatever measures their leaders chose to take. All over Israel, and in Jewish communities around the world, rallies and prayer meetings sought – in vain – the boys’ safe return – even while the Israeli government knew they were already dead.
In Gaza – where Hamas is the duly elected governing party – Hamas leaders watched as Israel used them as a pretext for the spate of arrests. Hamas had restrained itself and other resistance factions since the end of the 2012 conflict, waiting for Israel to fulfill its promise to end the blockade. But now, Israel was blaming Hamas for the kidnappings, re-arresting Hamas prisoners who had been freed, and maintaining the blockade. Hamas began allowing rockets to fly out of Gaza again.
United Nations
On June 17th, the Israeli Ambassador to the UN, Ron Prosor, spoke to the Security Council. In his speech, he blamed Hamas for the kidnapping (without proof) and demanded international pressure on Hamas to release the boys. Prosor displayed the hashtag that Israel and its partisans all over the world were using to draw attention to the fabricated crisis: #BringBackOurBoys.
On June 21st, Netanyahu repeated his canard to U.N. Secretary-General Ban Ki-moon: “the information in Israel’s hands unequivocally indicates that Hamas is responsible for the abduction of the youths”; Netanyahu went on to falsely link the Palestinian resistance with ISIS when he said “we are witnessing the unrestrained brutality of Islamic terrorism, both in Israel and around us.”
On June 23rd, the U.N. Security Council attempted unsuccessfully to pass a resolution condemning the kidnapping of the Israeli teens: some countries wanted to add strong language condemning Israel’s violent security sweep; the US insisted that it would not sign any statement that included a reference to Israeli actions.
On June 24th, the mother of one of the kidnapped boys addressed the U.N. Human Rights Council (UNHRC), pleading for international assistance in bringing the boys back. (Her trip was paid for by UN Watch, a group that monitors what it calls “the continuing discriminatory treatment of Israel in the UN system” and pushes for “the removal of UN personnel who are considered critical of Israel.”)
In the same UNHRC session, many delegates and representatives from human rights organizations criticized Israel’s human rights record, especially its recent crackdown.
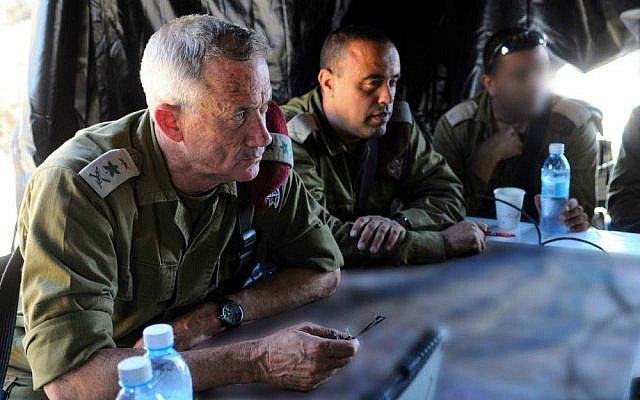
Then IDF Chief of Staff Benny Gantz visits soldiers as they take part in Operation Brothers Keeper to locate three kidnapped Israeli teens, June 24, 2014. (IDF Spokesperson/Flash90)
Kidnapped boys’ bodies found
On June 30th, 15 days after the Israeli leadership started its deceptive “campaign” to bring the boys back alive, the bodies were located ten minutes away from where they had last been seen.
The discovery was made not by the thousands of Israeli military or police – they were as much as 130 miles away, still ransacking Palestinian homes and arresting Palestinians – but by a volunteer search party.
The shallow grave was on the property of one of the suspects, whose identity had also been known for weeks, and whose property should have been considered suspect.
Within hours, Israeli forces demolished the family homes of the two suspects, an illegal but common practice in Israel.
The next day, July 1st, a funeral was held for the three teens. PM Netanyahu eulogized,
A deep and wide moral abyss separates us from our enemies. They sanctify death while we sanctify life. They sanctify cruelty while we sanctify compassion. This is the secret of our strength; it is the foundation of our unity.
This fraudulent profession of Israeli innocence flew in the face of facts that Mr. Netanyahu surely knew: the Israeli army had killed 19 Palestinians in the first quarter of 2014, and more in May and June. (Before the deaths of the three teens, two Israelis had been killed in 2014.)
Netanyahu’s eulogy also ignored the fact that Palestinians – specifically, Hamas – had been relatively subdued since 2012. As The Forward stated in “How Politics and Lies Triggered an Unintended War,” “The staged agony of the kidnap search created, probably unintentionally, what amounts to a mass, worldwide attack of post-traumatic stress flashback.”
Christian Peacemaker Teams (CPT) reported that late on July 1st, after the bodies were found, several Palestinians were killed. Israeli settlers also started constructing two new illegal outposts. Some settlers (and politicians) believe “the settlement enterprise is the most appropriate response to Palestinian terror… Our enemies will incite and we will establish” – not making the connection that building on stolen Palestinian land is incitement itself.
Incitement
From the moment the bodies of the missing teens were discovered, Israeli leaders incited their people to revenge, as described by Electronic Intifada :
Israeli Prime Minister Benjamin Netanyahu led the pack, calling the killers of the youths “human animals” and stating “Hamas is responsible. Hamas will pay.”
Former Israeli lawmaker Michael Ben-Ari posted a video and a statement…”We are living in a “jungle,” Ben-Ari said, calling Palestinian children “little terrorists”…
(Elsewhere, Ben-Ari called on Israel to “kill terrorists in public hangings.”)
Housing minister Uri Ariel called for the extrajudicial executions of leaders of Hamas and for Israel to “start a wave of construction in the settlements in response to the murder of the abductees”…
Tzipi Hotovely, another Likud lawmaker and deputy minister, wrote that “Israel must declare a war of annihilation of Hamas, which is responsible for the murder, and return to the assassination policy.”
Economy minister Naftali Bennett, leader of the ultra-anti-Palestinian Jewish Home party, declared “Murderers of children and those who direct them cannot be forgiven. Now is a time for actions, not words.”
With this highly visible incitement, it came as no surprise that after the funeral, crowds of Israelis – including young children – chanted “Death to the Arabs.” Mobs marched through the streets, attacking Palestinians as they went.
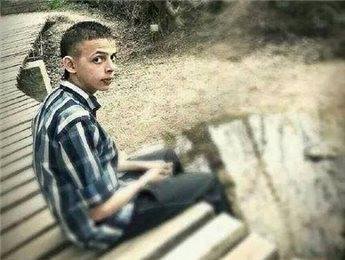
Mohammad Abukhdeir was killed by Jewish Israelis on July 2, 2014. (Facebook)
Revenge killing
On July 2nd, a Palestinian teenager named Mohammad Abukhdeir was kidnapped and burned alive near Jerusalem.
At first, Israel’s leaders imposed another gag order; meanwhile, Israeli police started rumors that Abukhdeir had been killed by his own family for being gay.
It wasn’t long before the truth had to come out: the torture/murder had been committed by three Jewish Israelis – two of them teenagers themselves. They eventually faced trial and in 2016 received sentences from 21 years to life. Their family homes were not demolished.
PM Netanyahu’s condolences to the Abukhdeir family condemned the murder and promised justice; then he went on to address his constituents, again claiming Israeli innocence:
I know that in our society, the society of Israel, there is no place for such murderers. And that’s the difference between us and our neighbors. They consider murderers to be heroes. They name public squares after them. We don’t. [editor’s note: this is false.] We condemn them and we put them on trial and we’ll put them in prison.
Al Jazeera reminded its readers that Abukhdeir’s abduction was not an isolated incident: “for Palestinians, the detention of their children, running into thousands, is experienced as kidnapping at an Israeli-state level.” The vast majority of these events – which frequently include torture – go unpunished.
In 2014, Israel’s military kidnapped 6,059 Palestinians. A spokesman for the Palestinian Commission of Detainees and Ex-Detainees stated on December 29th, 2014,
“There hasn’t been a single day that did not witness the abduction of Palestinians. On average, the army has kidnapped 505 Palestinians each month; approximately 17 a day.”
Since 1967, Israel has detained more than 50,000 Palestinian children; the Palestinian government has never detained an Israeli child. Additionally, a total of over 2,400 Palestinian children and 139 Israeli children have been killed since 2000.
Israeli teens’ killers tracked down
On August 5th, one suspect in the kidnapping and killing of the Israeli teens was arrested.
On September 23rd, the primary suspects were surrounded by Israeli military forces in a building in Hebron. An IDF spokesperson later stated, “We opened fire, they returned fire and they were killed in the exchange.”
At that point, Operation Brothers Keeper was officially closed.
Stay tuned for “war”
On July 8th, the Israel launched an incursion into Gaza, which in 50 days would bring about the deaths of 73 Israelis (9% civilians) and 2,250 Palestinians (65% civilians, 501 children). This travesty will be discussed in an upcoming post.
RELATED READING:
Blinken reveals how Obama & Biden helped Israel’s 2014 Gaza massacre
Israel arrests child with one-third of his skull missing, then lies about it
Remembering Mohammad Abukhdeir, 6 years on
The Staggering Cost of Israel to Americans: The Facts
Israeli airstrikes vs Palestinian rockets: Facts & Stats on air attacks
Trump-Kushner “Peace” Plan ignores elephants in the room: Israel created this mess
What Secrets Do Foreign US Bio Labs Hold?
By Vladimir Platov – New Eastern Outlook – 26.06.2020
Secret US bio laboratories are strewn across multiple countries in Africa, Asia, and even Europe. This is a global problem that is the attention of various media outlets as of late. More and more frequently, the numerous articles published on this issue voice questions such as: what secret programs (even supported by the country they are located in) are these US military bases pursuing? What if they are concocting a biological weapon to be used on their opposition, and they are the ones behind this entire coronavirus pandemic in the first place?
Emerging from recent discussions on whether the coronavirus is natural or artificially altered, comes information that CDC biologists from the US have been conducting unstable experiments on bats, which nearly all sources agree, trace back to the origin of the virus. They were raising and incubating entire colonies of bats, infecting them with deadly viruses, to study how the carriers of many infections handled them, and how infections can spread. The NCBI website has actually published three scientific works on the experiments carried out by CDC biologists involving infected bats, who have significant populations in South Africa, Egypt, Turkey, and across Asia. The first scientific work on this topic was published in 2015, while the latest – in 2020. In particular, these experiments by CDC biologists and the Pentagon were a joint effort involving colleagues from the Ministry of Defense (sic!) were conducted in 2017, while research on bats passing the infection to people was partially mentioned in March 2020. The results of completed experiments were similar: bats carry viruses, never get sick themselves, but can pass them on to humans.
We know that the USAID’s (which has undeniable ties with the Pentagon and CIA) EPT program was launched in 2009. It was to support US monitoring and laboratory opportunities in the chosen nations for studying wildlife and people coming in contact with animals, to discover new and already known virus agents, that can present a serious threat to people’s health. In Asia especially this program took root in Thailand, Cambodia, Indonesia, Laos, Vietnam, and China. In China, for instance, partners of this program were chosen by the government program of the Wuhan institute of virology, and the American non-government organization – EcoHealth Alliance. The specifics of what the Americans were into in Wuhan can be partially found in several scientific works posted on the NCBI website. Of course, the true secrets behind such deals are never made public. Thus, China became a complete doormat for American biologists testing viruses.
However, many countries have been manipulated in such a way. US military bio laboratories work on creating bacterial weapons in the Ukraine, stated Renat Kuzmin from the Oppositional Platform for Life. He thus confirmed, as did Ukrainian political figure Aleksander Lazarev the criminal activities of 15 bio labs sanctioned by the Pentagon on Ukrainian soil. Kuzmin noted that they are carrying out intelligence measures, as well as creating bacterial weapons and testing several harmful diseases on Ukrainians. Ukrainian MPs Victor Medvedchuk and Renat Kuzmin sent a formal complaint to the UN for US bacterial labs illegally functioning on Ukrainian soil. In a recently increasing wave of protests against the activities of US bio labs in Ukraine, experts note that in 2001, the US declined to sign an international protocol naming 33 microorganisms as potential agents of biological warfare, suddenly finding 37 articles that were not in the interests of the United States, obviously creating a loophole for themselves to continue secret bio weapon work on foreign soil.
The media has repeatedly published material proving a number of incidents with dangerous viruses and toxins, leading to the death of innocent citizens in countries unwittingly hosting secret US bio labs. A significant amount of such materials has been in a US bio laboratory named the Lugar Research center (Alekseevka, Tbilisi), confirming the concerns about illegal US activities in Georgia. Secret experiments are being conducted at the facility. Some research is even done on people, who are isolated in special units and subsequently infected with the most dangerous diseases. “The proof of this lies in the experiments carried out in this bio lab directed towards using insects as carriers for highly dangerous biological agents, and infections, as well as equipping weapons with poisonous substances and infected agents,” read a statement on the Ministry of Foreign Affairs of the Russian Federation’s website.
Since 2008, the Pentagon has created nearly a dozen bio labs in Armenia. Reports in local media reveal that the research involves pathogens that have long been studied by DARPA as potential bio weapons: anthrax, brucellosis, plague, African swine fever and tularemia. Armenia is a country that has witnessed sparks of mutating viruses over the past ten years, that have also spread through all of Transcaucasia, giving the Pentagon sufficient proof of concept of how bio weapons might work naturally, both on Russia’s southern border as well as in Iran. Pentagon bio laboratories in Armenia employ a number of US military contractors, the foremost of which being CH2M Hill, which has already spent $50 million from DTRA in 2018. CH2M Hill is famous for organizing bio labs in Georgia, Uganda, Tanzania, Iraq, Afghanistan and southeast Asian countries. CH2M Hill’s sub contractors have expressed significant interest in Black&Veach, which runs US bio labs in Ukraine, Germany, Azerbaijan, Cameroon, Thailand, Ethiopia, and Vietnam. Namely, the Battelle Memorial Institute and Southern Research Institute. Both companies are old partners of the Pentagon and CIA. Between 1952 and 1996, the Battelle Memorial Institute acquired 11 US army contracts and still conducts research and tests with the use of extremely toxic chemical substances and pathogenic bio active substances. One of Battelle’s joint operations with the CIA is Clear Vision in 1997 and 2000, while a low caliber bomb with anthrax was constructed as part of the operation to study the spreading principles of the virus after an explosion. This shines a light on the data from a partially classified presentation of the US Minister of Defense in 1981, where the economics of the three scenarios of possible biological attack in a big city are laid out. 16 simultaneous attacks using infected yellow fever mosquitoes through the air and aerosol attacks with spraying tularemia will lead to minimal losses. If 625,000 deaths occurred, the Pentagon would lose 29 cents per person.
This is why the activities of secret US bio labs located in numerous nations worldwide as well as proof of private company involvement such as CH2M Hill, Battelle, Metabiota and a number of others conducting research on dangerous anthrax bacteria, tularemia, hemorrhagic fever and a whole range of harmful viruses cannot go on unnoticed, and should be presented to the international public.
Denmark summons Saudi envoy over Riyadh’s support for anti-Iran terror group
Press TV – June 11, 2020
Denmark has called in the Saudi ambassador to Copenhagen to protest the kingdom’s support for a notorious terrorist group behind a 2018 deadly attack in Iran’s southwestern city of Ahvaz, among its other terrorist crimes against Iranians.
Riyadh’s envoy was summoned to the Danish Foreign Ministry on Wednesday after terrorism charges were leveled against three leaders of the anti-Iran al-Ahvaziya terror group based in Denmark.
Danish police said they were prosecuting “three people for financing and promoting terrorism in Iran, including in collaboration with a Saudi intelligence service.”
The suspects are believed to have received funds from Riyadh, which has been pursuing a highly hostile Iran policy under Crown Prince Mohammed bin Salman.
Meanwhile, Danish Security and Intelligence Service (PET) stressed that the trio worked for the Saudi regime between 2012 and 2018.
PET chief Finn Borch Andersen said it is “completely unacceptable” that Denmark is used “as a starting point to finance and support terrorism.”
“We will not accept such activities under any circumstances and our ambassador in Riyadh has repeated the same message directly to the Saudi authorities,” Danish Foreign Minister Jeppe Kofod said in a statement.
In February, Denmark said its intelligence service had arrested and charged three members of the Saudi-backed terror group for spying on behalf of the kingdom in the Scandinavian country.
Al-Ahvaziya has committed numerous crimes against Iranian targets over the past decades, among them bomb attacks in public places, abductions, assassinations, kidnapping for ransom, shooting at tourists and blowing up oil pipelines.
Formed a few years after the 1979 Islamic Revolution in Iran, the terror group was inspired back then by the Baath regime of Iraq’s ex-dictator Saddam Hussein.
Al-Ahvaziya has been after separating the southwestern province of Khuzestan — home to the country’s Arab population — from the rest of Iran through engaging in armed conflict against the Iranian government.
In September 2018, the Saudi-backed terror outfit claimed responsibility for a deadly attack on military parade in Ahvaz, Khuzestan’s provincial capital. The assault killed 25 people, including members of Iran’s Islamic Revolutionary Guard Corps (IRGC) and civilian bystanders, and injured 70 others.
Shortly after the attack, the London-based “Iran International” television channel funded by Saudi Arabia allowed the al-Ahvaziya spokesman to go live on air to defend the bloodshed.
In parallel, the Daesh Takfiri terrorist group also claimed responsibility for the Ahvaz attack.
In response, Iran launched missiles on gatherings of the ringleaders of the terror attack Ahvaz based in an area east of the Euphrates in Syria, killing and injuring a number of them and inflicting heavy losses on their stronghold.
Riyadh is widely viewed as a key sponsor of Takfiri terrorists, who are inspired by Wahhabism, an extremist ideology preached by Saudi clerics.
The Victims of MH17 Deserve More than the Shoddy Lies Perpetrated by Politicians and Media
By James O’Neill | Dissident Voice | June 7, 2020
The ABCs Insider program broadcast each Sunday morning is one of the ABCs most watched and most important programs. The three guests are drawn from the country’s mainstream media outlets. This is perhaps itself a limitation considering the broad range and frequently high standards of much political analysis in the country are non-mainstream outlets. The invited person subjected to questioning by the show’s host is almost invariably a politician drawn from either the Liberal or Labor parties.
One would be unwise to expect much more than a partisan view from the weekly political guest. It is, however, not unreasonable to think that the members of the panel might be expected to offer a factual analysis, albeit tempered by the political stance of their employee newspapers.
On the program broadcast on 7 June 2020 both the political guest, Labor deputy leader Richard Miles, and one of the panelists, the Sydney Morning Herald’s David Crowe offered an opinion that was stunning in its disregard for the body of information that is now available on the topic of the comment.
That topic was the shooting down of Malaysian airlines MH17 in July 2015 with the loss of life of 298 passengers and crew. The Dutch lost the largest proportion of the passengers, followed by Australia with 38 citizens and residents, then Malaysia and a smattering of citizens from a number of other countries.
An inquiry team was immediately established led by the Dutch, with other representatives coming from Australia, Belgium and Ukraine. There were three surprises in this contingent. The Dutch and Australians were not unexpected as having lost a significant number of their citizens. The inclusion of Belgium was puzzling and perhaps, in the light of subsequent events, only explicable in their role as the host of the NATO military alliance.
The second surprise was the inclusion of Ukraine. Although the tragedy occurred over Ukrainian territory it was clearly not an accident but the result of unfriendly criminal activity by a party or parties then unknown. Ukraine was at the very least a possible culprit.
The third surprise was the exclusion of Malaysia which as the owner and operator of the flight would normally be an automatic inclusion in any inquiry. Their exclusion was unexplained at the time. It was only later that it emerged that the four investigating countries had reached an agreement between themselves, the details of which have never been fully disclosed.
What is known however, is that part of the agreement provided that no statement on the investigation would be released without the unanimous agreement of all four members. To describe this as astonishing would be an understatement. It was one of the early clues that the investigation would not be an impartial investigation, but would in effect follow a political agenda. This has indeed proven to be the case.
What was also unknown at the time, but revealed relatively recently by the Malaysians, was that they had sent a team to the Ukraine immediately. Thanks to the assistance of Ukrainian rebels then (and now) engaged in a bitter war with the Kiev government, the plane’s black boxes had been retrieved. The rebels handed those over to the Malaysians who returned to Malaysia where they were examined before being in turn given to the British for further analysis.
It was with this information that the Malaysians then negotiated their entry into the inquiry team in late 2015. It was one of the features of this case that the Malaysian viewpoint has been almost entirely absent from the Dutch and Australian reporting of the case.
It did not take long for the Dutch, Australians and Ukrainians to blame Russia for the tragedy despite the fact, then and now, of anyone being able to offer even a remotely plausible reason for Russia to have shot down the civilian airliner of a friendly country. The improbability was compounded by the fact that the tragedy occurred over Ukrainian territory.
The implausibility of this version of events was enhanced when a British organisation known as Bellingcat published what they claimed to be pictures of a Russian missile firing weapon system returning to Russia from the area where the alleged missile had been fired from.
It is one of the telling features of this case that later evidence was disclosed, but not reported in the Australian media, that there were no Russian weapons capable of firing a BUK missile (the alleged weapon used) in the vicinity of the area it would have to be in to have fired the allegedly fatal missile. Neither for that matter was there any Ukrainian BUK missile facility within range, although the Ukrainians certainly possessed such missiles, a left over from the days when it was a part of the old Soviet Union and used Russian supplied weapons.
The other relevant point about the shoot down was the claim by then United States secretary of state John Kerry that United States satellites overhead at the time (observing what was a war zone) had seen exactly what had happened. There is no reason to doubt Mr Kerry’s claim. It is also likely that the Russians had overhead satellites, for exactly the same reason.
The important point, however, is that the United States has never produced that evidence to the Dutch led inquiry or anybody else. Given that such photos would in all probability be conclusive of the argument, their nonproduction leads to an irresistible inference. They do not support the Dutch-Ukrainian version. It is a safe assumption that if they did, we would have been inundated with those pictures, ad nauseam, ever since.
What the Russians and the Ukrainian rebels have said all along was that the plane was brought down by the actions of two Ukrainian jet fighters observed by independent eye witnesses at the time. The presence of multiple bullet holes in the plane’s recovered fuselage further confirms this interpretation of how MH17 came to its tragic end.
There is no obvious reason as to why the Ukrainians would shoot down a civilian airliner. The first of the three most likely possibilities are that it was a genuine accident, but if that was the case why not admit it, plead accident and pay appropriate compensation.
The second possibility is that it was a case of mistaken identity. It is known that a plane carrying Russia’s President Putin was in the general vicinity at that time, returning from an official trip to South America. Putin’s official plane carries very similar markings to Malaysian airlines.
The third possibility, which frankly is rather horrible to contemplate, is that it was a deliberate attempt to frame Russia, the major supporter of the Ukrainian rebel groups (overwhelmingly Russian speaking). It should not be forgotten also that the former Russian territory of Crimea (gifted to Ukraine by Khrushchev in Soviet days) had voted overwhelmingly to return to Russia. This had outraged the Ukrainian government who had vowed to retake Crimea by force. The United States also had plans to take over the Russian naval base on Crimea, thereby depriving Russia of a vital warm water port.
All of these facts make the rather ludicrous threat by then Australian prime minister Abbott of military action in support of Ukraine’s attempt to force Crimea back within its fold all the more ridiculous. More importantly, it makes the allegations of Messrs Marles and Crowe completely unsupportable. Australian government policy towards Ukraine, then as now, completely ignores the fact that it is a neo-fascist regime that came to power by violently overthrowing the legitimate Ukrainian government.
Both men ought to have known better. Indeed, it is probable both do know better but because Australia is a loyal supporter of the West’s official anti-Russian line, have gone along with helping perpetrate a manifest fiction, unsupported by the five years of evidence that have been accumulated in the interim. The Moscow based Australian journalist John Helmer is one of the very few to have consistently followed this Dutch led travesty and disclosed the evidence as it has emerged.
That the Australian mainstream media have chosen to ignore that evidence, to actively conceal the investigative role played by Australian forces in the early stages, and to perpetuate a gross falsehood does neither Mr Marles nor Mr Crowe or any organisation they represent any credit at all.
The families of the victims of this tragedy do not need the perpetuation of shoddy lies for geopolitical purposes. Messrs Marles and Crowe do neither themselves, their country, nor the organisations they represent any credit by helping to perpetuate a shameful lie.
James O’Neill is a Barrister at Law and geopolitical analyst. He can be contacted at joneill@qldbar.asn.au.
US Unable to Provide Extra Information on Missile Fired at Boeing MH17, Dutch Judge Says
Sputnik – 08.06.2020
US authorities have informed the Netherlands of being unable to provide additional information about a missile fired at the Malaysian Airlines Boeing, МН17, apart from a document sent in 2014, presiding judge Hendrik Steenhuis has stated at the resumed hearings in the MH17 case.
“The court asked whether classified satellite images of the missile launch, presented to Dutch special services, could be attached to the case … The prosecution said that the request had been sent to the US back in 2014, and in response a memorandum was sent. The Dutch prosecutor in charge of the fight against terrorism was able to check the accuracy of the memorandum … The prosecutor came to the conclusion that the memorandum was supported by other sources he had consultations with. He requested the conclusions be attached to the case. The US authorities said they could not provide any additional information regarding the missile launch in addition to the memorandum”, Steenhuis said.
Hearings in the 2014 MH17 crash case resumed on 8 June at the Schiphol Judicial Complex not far from Amsterdam. Earlier matters in the case of the MH17 crash in eastern Ukraine were heard in hearings on 9-10 March.
Russian nationals Igor Girkin, Sergey Dubinsky, and Oleg Pulatov, as well as Ukrainian national Leonid Kharchenko, are defendants in the case.
Russia has repeatedly demanded to provide data from Ukrainian radars and US satellites as part of an investigation into the MH17 crash.
MH17 Crash Case Details
Malaysia Airlines Flight MH17 crashed on 17 July 2014, in eastern Ukraine while en route from Amsterdam to Kuala Lumpur, killing all 298 people aboard. Most of the deceased were Dutch citizens. Kiev and the self-proclaimed republics in Ukraine’s east have exchanged blame for the downing of the plane.
The accident is being investigated by Dutch prosecutors and the JIT, which claim that the plane was hit by a Buk missile that belonged to the Russian armed forces. Moscow has repeatedly denied involvement in the incident and has called the JIT investigation biased, as Russia’s evidence showing that the plane had been shot down by a Ukrainian Buk missile has been ignored by investigators.
Russian President Vladimir Putin noted that the country has not been allowed to investigate the crash of the plane in eastern Ukraine, and Moscow can only accept the results of the investigation if it can fully participate in the probe. All missiles and the engine that were showed by the Dutch Commission for the investigation into the crash of the MH17, were disposed of after 2011, according to the Russian Defence Ministry.
OPCW head FALSELY described Syria whistleblower inspectors to discredit them, new documents show
RT | May 6, 2020
New documents leaked from the global chemical watchdog show that two inspectors blowing the whistle about the 2018 Douma incident in Syria were right, and the director seeking to discredit them was wrong.
Two inspectors with the Organization for the Prohibition of Chemical Weapons (OPCW) have challenged the organization’s final report on the April 2018 incident, which they say was altered to dismiss their findings and validate after the fact the US, UK and French missile strikes against the government in Damascus.
OPCW Director General Fernando Arias responded earlier this year by describing them as “rogue” inspectors who weren’t even members of the mission. Documents obtained by investigative journalist Aaron Mate at Greyzone, however, show that Arias’ statements were false or misleading.
Arias claimed that South African inspector Ian Henderson was “not a member” of the fact-finding mission (FFM) dispatched to Douma, and that he had played a “minor supporting role.” However, the documents from April 2018 obtained by the Grayzone show that OPCW directors were “happy” to have Henderson lead the visits to the most important locations in Douma: the hospital and the sites of alleged chlorine cylinder impact, for instance.
Another document, described as a sensitive security-planning memorandum known as CONOPS, lists Henderson as part of the FFM under the section “Mission Personnel.”
Last, but not least, the “F038” memorandum to the Syrian government lists Henderson as “part of the team conducting the technical secretariat visits,” notifying Damascus of his role. Henderson has previously explained publicly that he was on a mission in Nepal, and was assigned to Douma immediately upon his return.
Moreover, another OPCW document shows that Henderson took over the OPCW Damascus command post on May 3, 2018 – two days after returning from Douma. This goes directly against Arias’ version of events, according to which Henderson was already in Damascus, happened to play a minor role in the Douma mission, and then went “rogue” to sabotage the organization for reasons unknown.
Henderson and another whistleblower inspector – who remains anonymous – have said for months that they had not gone rogue, but were sidelined by OPCW because they produced evidence suggesting the Douma incident had been staged by the Army of Islam militants who controlled the area at the time. The final OPCW report, they contend, was doctored to retroactively justify the US, UK and French missile strikes and enable them to blame Damascus.
The OPCW responded to their revelations by painting them as disgruntled employees who breached confidentiality and lacked expertise and access to all the evidence. Their own documents now clearly show those statements to be false.
Syria: Fake Attack, Real Deaths
By Eric van de Beek – Sputnik – April 15, 2020
Two years ago the Syrian government was accused of a chemical attack in the Damascus suburb Douma. It has become clear now there never was such an attack. But still, people were found dead. Who were they? And how did they die?
On April 14th 2018, the US, France, and Great Britain launched missile strikes on Syria, in retribution for an alleged poison gas attack on the terrorist stronghold Douma for which they held the Syrian government responsible. Just before the attack, the Russian ambassador in Lebanon and the chief of Russia’s general staff warned Russia would respond to strikes on Syria if the lives of Russian servicemen were threatened, targeting any missiles and launchers involved. As Russian envoy to Organisation for the Prohibition of Chemical Weapons (OPCW), Alexander Shulgin, later put it: “There was a smell of gunpowder in the air“.
What could have led to World War III eventually ended with a hiss. No Russian targets were hit and for Syria, the damage from the attacks was limited, partly because Syria’s Soviet-era air defence systems intercepted many incoming missiles.
Rumours about a chemical attack had started with videos and photos disseminated on social media by Syrian Civil Defence, better known as The White Helmets, among others, of children being treated in a hospital with respiratory problems; of dead bodies in an apartment building; and of chlorine cylinders that looked as if they had been dropped from the sky, one laying on a roof terrace and the other on a bed under a hole in the roof.
On 16th April 2018, two days after the tripartite strike, British Middle East correspondent Robert Fisk interviewed a doctor from the Douma hospital. He stated that although the video of the children being treated in the hospital was real, and that the portrayed patients had been struggling with breathing problems, this was not the result of a poison gas attack, but of dust clouds caused by bombardments that had occurred earlier in the day.
While the patients were being brought in, there was a member of the White Helmets calling out “gas!” – which caused people to throw water over each other in panic.
Other witnesses, who told their story in The Hague on April 28th 2018, at a press conference organised by the Russian delegation to OPCW, roughly confirmed the statement of the doctor interviewed by Fisk. None of them, including several people who were seen in the video, said they hadn’t noticed anything of a poison gas attack.
In May 2019 a revealing document was leaked from OPCW about the two cylinders. The author, Ian Henderson, who in April 2018 had been sent to Douma to investigate the cylinders on behalf of the chemical watchdog, concluded that there was a “higher probability that both cylinders were manually placed at those two locations rather than being delivered from aircraft”. This seemed to be an understatement since the hole in the roof turned out to be smaller than the cylinder on the bed below.
Also “no organophosphorus nerve agents or their degradation products were detected, either in the environmental samples or in plasma samples from the alleged casualties”, the OPCW interim report on the Douma incident reads. The OPCW inspectors furthermore noted that the dead people in the photos and videos didn’t look like victims from “chlorine-containing choking or blood agents such as chlorine gas, phosgene or cyanogen chloride”.
And so, one important question remains unanswered: Who were the around 35 dead deceased, mostly women and children, that were filmed and photographed in the four-storey building in Douma, where one of the two cylinders was found on the roof? And how did they die?
Jaish al-Islam, the terrorist group that at that time occupied Douma, reportedly buried the bodies in an unmarked mass grave, before the OPCW inspectors had arrived at the scene. Raed Saleh, leader of the White Helmets, told Reuters he pinpointed the burial place to OPCW. Nevertheless, the chemical watchdog chose not to conduct exhumations.
And so I asked Al Saleh if he could tell me anything about the background of the victims and the location of their burial. Unfortunately, he left my questions unanswered. I also asked Dr. Ghassan Obeid of the mission of Syria to the OPCW if the Syrian authorities had made an effort to identify the deceased, but I received no reply from him either.
At a press conference of the Russian embassy in The Hague on July 12th 2019, that I attended, Maxim Grigoriev, director of the Russia-based Foundation for the Study of Democracy, showed interviews of people living in the apartment building and in its vicinity.
None of them recognised the deaths from the videos and photos, apart from one man who identified his brother, who had died, he said, from artillery shelling elsewhere. Some interviewees declared they had seen fighters bringing dead bodies into the building.
I invited the open-source and social media investigators of Bellingcat to debunk Grigoriev’s findings and to identify the ‘Douma victims’. I received no reply. Nevertheless, Bellingcat proved to be very quick in finding who was to blame: four days after the alleged chemical attack they concluded it was “highly likely the 34+ victims of the 19:30 attack on the apartment building near al-Shuhada Square were killed as a result of a gas cylinder filled with what is most likely chlorine gas being dropped from a Hip helicopter originating from Dumayr Airbase”.
And so here we are, two years after an attack that never happened, with around 35 dead people, still unidentified, and still buried in an unmarked grave.
Even more terrible: the management of OPCW, based in The Hague, The Netherlands, has suppressed the findings of its own inspectors who had conducted an investigation at the alleged crime scene in Douma, Syria.
The OPCW management is simply covering up for the criminal elements that have staged the Douma incident, and that could have triggered an all-out world war. For full information about this alarming fact, I recommend reading the presentation given by members of the Working Group on Syria, Media, and Propaganda among others in the House of Commons on January 22th 2020.
Mossad False Flag Attacks on Jews
Is anti-Semitism really increasing?
By Philip Giraldi • Unz Review • April 14, 2020
Even though distracted by the havoc resulting from the coronavirus, the United States and much of Europe is engaged in a frenzied search for anti-Semitism and anti-Semites so that what the media and chattering class are regarding as the greatest of all crimes and criminals can finally be extirpated completely. To be sure, there have recently been some horrific instances of ethnically or religiously motivated attacks on synagogues and individual Jews, but, as is often the case, however, quite a lot of the story is either pure spin or politically motivated. A Jewish student walking on a college campus who walks by protesters objecting to Israel’s behavior can claim to feel threatened and the incident is recorded as anti-Semitism, for example, and slurs written on the sides of buildings or grave stones, not necessarily the work of Jew-haters, are similarly categorized. In one case in Israel in 2017, the two street swastika artists were Jews.
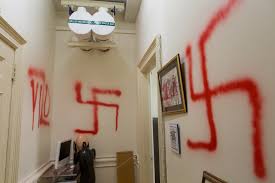 Weaponizing one point of view inevitably limits the ability of contrary views to be heard. The downside is, of course, that the frenzy that has resulted in the criminalization of free expression relating in any but a positive way to the activity of Jewish groups. It has also included the acceptance of the dishonest definition that any criticism of Israel is ipso facto anti-Semitism, giving that nation a carte blanche in terms of its brutal treatment of its neighbors and even of its non-Jewish citizens.
Jewish dominated Hollywood and the entertainment media have helped to create the anti-Semitism frenzy and continue to give the public regular doses of the holocaust story. Currently there are a number of television shows that depict in one form or another the persecution of Jews. Hunters on Amazon is about Jewish Americans tracking and killing suspected former Nazis living in New York City in the 1970s. The Plot to Destroy America on HBO is a retro history tale about how a Charles Lindbergh/Henry Ford regime installs a fascist government in the 1930s. One critic describes the televisual revenge feast “as one paranoid Jewish fantasy after another advocating murder as the solution to what they perceive as the problem of anti-Semitism.”
But, as always, nothing is quite so simple as such a black and white portrayal where there are evil Nazis and Jewish victims who are always justified when they seek revenge. First of all, as has been demonstrated, many recent so-called anti-Semitic attacks on Jews involve easily recognizable Hasidic Jews and are actually based on community tensions as established neighborhoods are experiencing dramatic changes with the newcomers using pressure tactics to force out existing residents. And after the Hasidim take over a town or neighborhood, they defund local schools to support their own private academies and frequently engage in large scale welfare and other social services fraud to permit them to spend all their days studying the Talmud, which, inter alia teaches that gentiles are no better than beasts fit only to serve Jews.
The recent concentration of coronavirus in Orthodox neighborhoods in New York as well as the eruption of measles cases last year have been attributed to the unwillingness of some conservative Jews to submit to vaccinations and normal hygienic practices. They also have persisted in illegal large gatherings at weddings and religious ceremonies, spreading the coronavirus within their own communities and also to outsiders with whom they have contact.
Regularly exposing anti-Semitism is regarded as a good thing by many Jewish groups because the state of perpetual victimization that it supports enables them to obtain special benefits that might otherwise be considered excessive in a pluralistic democracy. Holocaust education in schools is now mandatory in many jurisdictions and more than 90% of discretionary Department of Homeland Security funding goes to Jewish organizations. Jewish organizations are now lining up to get what they choose to believe is their share of Coronavirus emergency funding.
Claims of increasing anti-Semitism, and the citation of the so-called holocaust, are like having a perpetual money machine that regularly disgorges reparations from the Europeans as well as billions of dollars per year from the U.S. Treasury. Holocaust and anti-Semitism manufactured guilt are undoubtedly contributing factors to the subservient relationship that the United States enjoys with the state of Israel, most recently manifested in the U.S. Department of Defense’s gift of one million surgical masks to the Israel Defense Force in spite of there being a shortage of the masks in the United States (note how the story was edited after it first appeared by the Jerusalem Post to conceal the U.S. role but it still has the original email address and the photo cites the Department of Defense).
And then there is the issue of Jewish power, which is discussed regularly by Jews themselves but is verboten to gentiles. Jews wield hugely disproportionate power in all the Anglophone states as well as in France and parts of Eastern Europe and even in Latin America. If anti-Semitism is as rampant as has often been claimed it is odd that there are so many Jews prominent in politics and the professions, most especially financial services and the media. Either anti-Semitism is not really “surging” or the actual anti-Semities have proven to be particularly incompetent in making their case.
Further muddying the waters, there have been a number of instances in which Jews have themselves been responsible for what have been claimed to be anti-Semitic incidents. There has also been credible speculation that some of the incidents have been false flags staged by the Israeli government itself, presumably acting through its intelligence services. The objective would be to create sympathy among the public in Europe and the U.S. for Israel and to encourage diaspora emigration to the Jewish state. The recent tale of Israeli-American Michael Kadar, who has been credited with many of early 2017’s nearly two thousand bomb scares targeting Jewish community centers and synagogues worldwide, is illustrative.
Kadar, who holds both Israeli and American nationality, was arrested in Ashkelon Israel on March 2017 by Israeli police in response to the investigation carried out by the Federal Bureau of Investigation. Kadar’s American address was in New Lenox Illinois but he actually resided in Israel. Kadar’s defense was that he had a brain tumor that caused autism and was not responsible for his actions, but he was found to be fit for trial and was sentenced to 10 years in prison in June 2017. He was apparently subsequently quietly released from prison and returned to Illinois in mid-2018. In August 2019 he was arrested for violation of parole on a firearms and drugs offense.
The court in Tel Aviv convicted Kadar on counts including “extortion, disseminating hoaxes in order to spread panic, money laundering and computer hacking over bomb and shooting threats against community centers, schools, shopping malls, police stations, airlines, and airports in North America, Britain, Australia, New Zealand, Norway and Denmark.” It claimed that “As a result of 142 telephone calls to airports and airlines, in which he said bombs had been planted in passenger planes or they would come under attack, aircraft were forced to make emergency landings and fighter planes were scrambled.”
It was also claimed by the court that Kadar had gotten involved with the so-called restricted access “dark web” to make threats for money. He reportedly earned $240,000 equivalent worth of the digital currency Bitcoin. Kadar has reportedly refused to reveal the password to his Bitcoin wallet and its value is believed to have increased to more than $1 million.
The tale borders on the bizarre and right from the beginning there were many inconsistencies in both the Department of Justice case and in terms of Kadar’s biography and vital statistics. After his arrest and conviction, many of his public, private and social networking records were either deleted or changed, suggesting that a high-level cover-up was underway.
Most significant, the criminal complaint against Kadar included details of the phone calls that were not at all consistent with the case that he had acted alone. The threats were made using what is referred to as spoofing telephone services, used by marketers to hide the caller’s true number and identify, but the three cell phone numbers identified by the Department of Justice to make the spoofed calls were all U.S.-based and one of them was linked to a Jewish Chabad religious leader and one to the Church of Scientology’s counter-intelligence chief in California. In addition, some of the calls were made when Kadar was in transit between Illinois and Israel, suggesting that he had not initiated the calls.
DOJ’s criminal complaint also included information that the threat caller was a woman who had “a distinct speech impediment.” Michael Kadar’s mother has a distinct speech impediment. Oddly enough she has not been identified in any public documents and the Israelis claimed that Michael was disguising his voice, but she is believed to be Dr. Tamar Kadar, who resided in Ashkelon at the same address as Michael. Dr. Kadar is a chemical weapons researcher at the Mossad-linked Israel Institute for Biological Research (“IIBR”).
Michael appears to have U.S. birthright citizenship because he was born in Bethesda in 1990 while his mother was a visiting researcher at the U.S. Army Military Research Institute of Infectious Diseases (USAMRIID). While Dr. Kadar was at USAMRIID, anthrax went missing from the Army’s lab and may have been subsequently used in the 2001 anthrax letter attacks inside the U.S., which resulted in the deaths of five people. The FBI subsequently accused two USAMRIID researchers of the theft, but one was exonerated and the other committed suicide, closing the investigation.
So, there are some interesting issues raised by the Michael Kadar case. First of all, he appears to have been the fall guy for what may have been a Mossad directed false-flag operation actually run by his mother, who is herself an expert on biological weapons and works at an Israeli intelligence lab. Second, the objective of the operation may have been to create an impression that anti-Semitism is dramatically increasing, which ipso facto generates a positive perception of Israel and encourages foreign Jews to emigrate to the Jewish state. And third, there appears to have been a cover-up orchestrated by the Israeli and U.S. governments, evident in the disappearance of both official and non-official records, while Michael has been quietly released from prison and is enjoying his payoff of one million dollars in bitcoins. As always, whenever something involves promoting the interests of the state of Israel, the deeper one digs the more sordid the tale becomes.
Philip M. Giraldi, Ph.D., is Executive Director of the Council for the National Interest, a 501(c)3 tax deductible educational foundation (Federal ID Number #52-1739023) that seeks a more interests-based U.S. foreign policy in the Middle East. Website is councilforthenationalinterest.org, address is P.O. Box 2157, Purcellville VA 20134 and its email is inform@cnionline.org.
Why the US wouldn’t Ease Iran Sanctions
By Salman Rafi Sheikh – New Eastern Outlook – 09.04.2020
The past two weeks have seen US officials moving first from issuing an alert to their military commanders to make plans for a retaliatory strike against Iranian targets to talking about ‘easing’ sanctions on Iran if Iran ‘wants it.’ It’s obvious that there is no reason why the Iranians wouldn’t want to see sanctions against them being eased up. Yet, Trump’s desire for a formal request about this issue shows the latent intention of ignoring it, while using the whole scenario to its advantage i.e., let the situation exacerbate to an extent whereby the Iranian regime becomes unstable and incapable of rescuing its people from the virus, and thus collapse ultimately.
This would surely serve US interests, along with those of Saudi Arabia and Israel, which have been pushing hard to do a “regime change” in Tehran. In their calculation, the unprecedented crisis caused by the COVID-19 seems to have given them yet another opportunity to attain their ultimate objective.
Indeed, this was the intention when the US asked its military commanders to make plans for a retaliatory strike on Iran in response to an imaginary Iranian attack on US military bases—an attack that had neither been planned nor was it foreseen by anybody. But the fact that the US was going to ‘directly attack the Iranian forces’ in the wake of Iran supported militias attacking US troops shows that the intention was, as Trump himself said, to go “up the food chain”, thus creating a scenario that would be extremely difficult for Tehran to address.
Accordingly, as a part of US ‘war preparations’, the US military officials disclosed, seemingly on purpose, to the western media that Patriot air defence systems have been deployed to two Iraqi military bases and that the same systems were going to be deployed across two more bases.
While manufacturing a military crisis is one thing, executing it is another. Accordingly, even if the US ‘had a plan’, it doesn’t mean it was going to work due to multiple factors, including lack of support from US allies in Europe, who were already in the middle of operationalising Instex to start economic and financial transactions with Iran, bypassing US sanctions and showcasing their ‘independent’ approach towards Iran in the wake of widening gap between the US and Europe/NATO.
But the US sanctions are still intact; for easing sanctions will allow, in the US calculation, the Iranian regime to better tackle the COVID-19 crisis and thus stabilise itself politically and economically. This would thus undermine the very purpose of the US sanctions i.e., forcing the Iranian regime to implode and collapse.
Indeed, a collapse followed by a massive crisis in the Middle East, particularly one that involves Iran, is something that the US would welcome rather than desist. It shows why the US imposed new sanctions on Iran instead of removing the old ones.
It has happened recently when Iran, out of the necessity to cope with monetary shortfall, requested 5 billion dollars from the International Monetary Fund (IMF). While this was always obvious that the request will not be granted without US acquiescence, the US actually responded by announcing new sanctions on Iran’s oil industry, one of its very few remaining foreign exchange earners. The intention was to make life even more difficult for the Iranians.
Also, it explains why Washington has so far taken no serious steps to actually ease the sanctions on its own, even though sufficient conditions for doing so undoubtedly exist, including Iran’s response whereby they called for a halt to “warmongering during the coronavirus outbreak” and further warned that US military activities could create “instability and disaster”. On April 2, Foreign Minister Javad Zarif, addressing the US president, tweeted, “Don’t be misled by usual warmongers, AGAIN. Iran starts no wars, but teaches lessons to those who do.”
Notwithstanding the ‘progressive’ US rhetoric about easing sanctions if Iran asks for it, the fact of the matter remains that the US strategic aim in this part of the world remains a “regime change” in Iran, although it is also becoming clear with every day passing that this objective can never be achieved.
Europe has already started Instex, although it is yet to produce productive economic results and engage in economic and financial activity beyond the support for COVID-19. The Chinese have yet again come out against US war aggression, and the Russians remain a bulwark against any US adventure in the Middle East, particularly against Iran.
None of this, of course, means that the US will end its sanctions. On the other hand, it will continue to add more to the pool as it did a few days ago; after all, ‘Iranian crisis’ is the linchpin of the US military presence in the region and the key source of wealth for its military-industrial complex.
Salman Rafi Sheikh is a research-analyst of International Relations and Pakistan’s foreign and domestic affairs.
Featured Video
Houthis Keep Advancing as the Red Sea Crisis Deepens
or go to
Aletho News Archives – Video-Images
From the Archives
15 Saudi ‘hijackers’ were CIA agents working for US: Scholar
Press TV – April 13, 2016
Fifteen of the 9/11 “hijackers” from Saudi Arabia were CIA agents working for the United States government, which was seeking to destroy the Middle East for Israel and to double the American military budget, says Dr. Kevin Barrett, an American academic who has been studying the events of 9/11 since late 2003…. continue
Blog Roll
 Aletho News
- Damascus rejects Saudi request for Syrian fighters to counter Yemen: Report
- South Korea says will not send troops to join terrorist US war on Iran
- Russia Just Struck the Eyes of NATO’s War Machine in Ukraine
- Russia summons UK charge d’affaires over Kiev drone support
- NATO member warns bloc seeking pretext for war with Russia
- Macgregor: We Haven’t Seen the Worst of the Iran War Yet
- ‘We are not like everyone else’ laws that bind other nations do not apply to Israel, says Likud lawmaker
- Report: Saudi Arabia seeks allies’ assistance as missiles deplete amid war on Yemen
- Fuel Crisis Deepens: Pakistan Warns Tanker Attack in Red Sea Would Be an ‘Act of War’
- ‘Bucha massacre’ a false flag orchestrated by UK – Moscow
- If Americans Knew
- Robert Kraft: The Billionaire Friend of Netanyahu Pulling The Strings Behind the Macklemore/Ed Sheeran Blow Up
- Columbia Administered Fund Gives Big Money to Pro-Israel Groups
- Deportation Case of Palestinian Activist Salah Sarsour Tests First Amendment
- ‘We Will Not Forget’: Palestinians Mark 44 Years since Sabra and Shatila
- Why do we let Zionists decide what we can and can’t say?
- US welcomes Israeli, Iranian delegations to UN, but not Palestinians – Daily Update
- Biden’s Genocide Accomplices Targeted by New Accountability Campaign
- AIPAC’s Network Has Already Spent $67.2 Million to Shape the Midterm Elections
- Jewish Supremacist Manufacturing a Civilizational Threat to License Bigotry
- US bans Palestinian president from speaking at the UN
- No Tricks Zone
- New Study: ‘Global Drought Shows No Detectable Recent Acceleration Under Climate Warming’
- Economic Masterminds: German Socialists Suggest Taxing Productivity Gains Stemming From Using AI
- The South China Sea Has Not Been Cooperating With The Climate Change Narrative
- Energy Crisis: Germany Enters Heating Season With Historically Low Gas Reserve Fill Levels
- New Study: The Antarctic Ice Sheet Gained Mass From 2020-2024 Due To Staggering Snow And Ice Accumulation
- Study: Ocean Heating Rates From Thousands Of Years Ago ‘Dwarf’ Modern Ocean Heating Rates
- Climate Extremists Target, Attack Large-Scale Power Grid Infrastructure In Germany!
- New Study: Antarctic Ice Melt Has Contributed Less Than 1 Centimeter To Sea Level Rise In The Last 30 Years
- Fear Of Debate: Alarmist German Climate Scientist Calls On Mainstream Media To Discredit Skeptic Voices
- End-Of-August Arctic Sea Ice Extent Hasn’t Fallen In 20 Years, Official Data Show!
 Aletho News
