US Intel, Media Spread Fake Reports on Alleged Russian Election Meddling
Sputnik – 29.08.2018
WASHINGTON – US intelligence officials and the American mainstream media have been propagating false Russia meddling claims to undermine pro-Trump congressional candidates ahead of the midterm elections, analysts told Sputnik.
In particular, The New York Times reported on Friday, citing unnamed intelligence officials, that US sources in the Kremlin who had warned about Russian intervention in the US 2016 presidential election “had gone silent” and now the CIA is in the dark about Moscow’s plans vis-a-vis the upcoming congressional midterm elections.
In November, US voters go to the polls to elect lawmakers who will represent their respective states at the federal level. The midterm elections will determine whether Republicans maintain control of Congress and will be seen by many as a referendum on the sitting president’s performance.
US intelligence leaders, including Director of National Intelligence Dan Coats, without any evidence have been warning that Russia will likely interfere in the midterm elections. Coats and others have also claimed that Russia is waging an influence campaign via social media.
Former US Defense Department adviser Karen Kwiatkowski told Sputnik that she had doubts about the reliability of the New York Times report and intelligence community claims.
“Reading between the lines of this article, it seems as if politicized members of the US intelligence establishment — including people like Dan Coats — are hedging their bets,” she said.
Coats and his colleagues were getting on record their ‘concern’ about Russia interference in these upcoming elections in the event of an unexpected wave of support for President Donald Trump, Kwiatkowski explained.
The New York Times report, claiming that the United States had human sources inside the Kremlin appeared to be based on false assumptions and to be part of a wider strategy to try and convince US public opinion about a non-existent Russian plot to influence the elections, Kwiatkowski cautioned.
“In terms of this article, I suspect it is wrong in its assumptions, and is part of a larger domestic propaganda effort,” Kwiatkowski said.
Kwiatkowski pointed out the remarkable lack of evidence to support US allegations of Russia’s meddling in the 2018 midterm elections.
“The American intelligence apparatus is ‘concerned’ that the Russians are trying to pick and choose candidates in midterm elections — 435 Congressional elections and 33 plus Senate elections — but they don’t have any information about this activity that they ‘know’ is happening,” the former Pentagon aide said. “This isn’t how intelligence is done. It is however how agendas are pushed, and propaganda rejuvenated.”
Former CIA Director John Brennan, who was referred to in the New York Times article, lacked any credibility based on his documented record, Kwiatkowski noted.
“Brennan is an unreliable source, extremely biased, a known liar and he’s currently angrier than usual. With his clearance suspended, he may be receiving less information from his friends in the government, and maybe that’s what he is complaining about,” Kwiatkowski said.
Former Canadian diplomat Patrick Armstrong, who once served as a political official at Ottawa’s embassy in Moscow, told Sputnik that The New York Times report was written to try and sustain flagging interest and support the diminishing credibility of the fiction that Russia intervened in the 2016 US elections.
“The writers are trying to keep the conspiracy going in the hope that the Democrats will control the House and shut down all examination of what really happened,” Armstrong said.
Fake News
However, the fantasy that Russian involvement had cost the Democratic candidate Hillary Clinton the 2016 election was supported by no evidence whatsoever, Armstrong emphasized.
“This is nonsense on stilts and only can be twisted into a question if you believe — as New York Times consumers do as a matter of faith — that Russia ‘interfered’ in the first place,” Armstrong said.
No evidence has been produced other than the “fantasies” in the unsubstantiated dossier produced by former UK spy Christopher Steele.
The only plausible content in the New York Times story was the assertion that Moscow had expelled many of Washington’s intelligence assets in Russia, Armstrong observed.
Kwiatkowski pointed out that the real manipulation of US elections was done by countries that had a historically shared culture with the United States.
The UK’s MI6 and Israel’s Mossad, Kwiatkowski said, are far more active in US elections, at many levels, than the Russians could ever hope to be.
“It’s nice for The New York Times to be able not to talk about these risks — in part because Trump is not the candidate these two countries would prefer,” Kwiatkowski concluded.
In January 2017, a US intelligence community report that contained zero evidence claimed that Moscow tried to meddle in the US election process. Moscow has repeatedly denied interfering in US elections as such actions would run counter to the principles and practices of Russian foreign policy.
How the Department of Homeland Security Created a Deceptive Tale of Russia Hacking US Voter Sites
By Gareth Porter | Consortium News | August 28, 2018
The narrative of Russian intelligence attacking state and local election boards and threatening the integrity of U.S. elections has achieved near-universal acceptance by media and political elites. And now it has been accepted by the Trump administration’s intelligence chief, Dan Coats, as well.
But the real story behind that narrative, recounted here for the first time, reveals that the Department of Homeland Security (DHS) created and nurtured an account that was grossly and deliberately deceptive.
DHS compiled an intelligence report suggesting hackers linked to the Russian government could have targeted voter-related websites in many states and then leaked a sensational story of Russian attacks on those sites without the qualifications that would have revealed a different story. When state election officials began asking questions, they discovered that the DHS claims were false and, in at least one case, laughable.
The National Security Agency and special counsel Robert Mueller’s investigating team have also claimed evidence that Russian military intelligence was behind election infrastructure hacking, but on closer examination, those claims turn out to be speculative and misleading as well. Mueller’s indictment of 12 GRU military intelligence officers does not cite any violations of U.S. election laws though it claims Russia interfered with the 2016 election.
A Sensational Story
On Sept. 29, 2016, a few weeks after the hacking of election-related websites in Illinois and Arizona, ABC News carried a sensational headline: “Russian Hackers Targeted Nearly Half of States’ Voter Registration Systems, Successfully Infiltrated 4.” The story itself reported that “more than 20 state election systems” had been hacked, and four states had been “breached” by hackers suspected of working for the Russian government. The story cited only sources “knowledgeable” about the matter, indicating that those who were pushing the story were eager to hide the institutional origins of the information.
Behind that sensational story was a federal agency seeking to establish its leadership within the national security state apparatus on cybersecurity, despite its limited resources for such responsibility. In late summer and fall 2016, the Department of Homeland Security was maneuvering politically to designate state and local voter registration databases and voting systems as “critical infrastructure.” Such a designation would make voter-related networks and websites under the protection a “priority sub-sector” in the DHS “National Infrastructure Protection Plan, which already included 16 such sub-sectors.
DHS Secretary Jeh Johnson and other senior DHS officials consulted with many state election officials in the hope of getting their approval for such a designation. Meanwhile, the DHS was finishing an intelligence report that would both highlight the Russian threat to U.S. election infrastructure and the role DHS could play in protecting it, thus creating political impetus to the designation. But several secretaries of state—the officials in charge of the election infrastructure in their state—strongly opposed the designation that Johnson wanted.
On Jan. 6, 2017—the same day three intelligence agencies released a joint “assessment” on Russian interference in the election—Johnson announced the designation anyway.
Media stories continued to reflect the official assumption that cyber attacks on state election websites were Russian-sponsored. Stunningly, The Wall Street Journal reported in December 2016 that DHS was itself behind hacking attempts of Georgia’s election database.
The facts surrounding the two actual breaches of state websites in Illinois and Arizona, as well as the broader context of cyberattacks on state websites, didn’t support that premise at all.
In July, Illinois discovered an intrusion into its voter registration website and the theft of personal information on as many as 200,000 registered voters. (The 2018 Mueller indictments of GRU officers would unaccountably put the figure at 500,000.) Significantly, however, the hackers only had copied the information and had left it unchanged in the database.
That was a crucial clue to the motive behind the hack. DHS Assistant Secretary for Cyber Security and Communications Andy Ozment told a Congressional committee in late September 2016 that the fact hackers hadn’t tampered with the voter data indicated that the aim of the theft was not to influence the electoral process. Instead, it was “possibly for the purpose of selling personal information.” Ozment was contradicting the line that already was being taken on the Illinois and Arizona hacks by the National Protection and Programs Directorate and other senior DHS officials.
In an interview with me last year, Ken Menzel, the legal adviser to the Illinois secretary of state, confirmed what Ozment had testified. “Hackers have been trying constantly to get into it since 2006,” Menzel said, adding that they had been probing every other official Illinois database with such personal data for vulnerabilities as well. “Every governmental database—driver’s licenses, health care, you name it—has people trying to get into it,” said Menzel.
In the other successful cyberattack on an electoral website, hackers had acquired the username and password for the voter database Arizona used during the summer, as Arizona Secretary of State Michele Reagan learned from the FBI. But the reason that it had become known, according to Reagan in an interview with Mother Jones, was that the login and password had shown up for sale on the dark web—the network of websites used by cyber criminals to sell stolen data and other illicit wares.
Furthermore, the FBI had told her that the effort to penetrate the database was the work of a “known hacker” whom the FBI had monitored “frequently” in the past. Thus, there were reasons to believe that both Illinois and Arizona hacking incidents were linked to criminal hackers seeking information they could sell for profit.
Meanwhile, the FBI was unable to come up with any theory about what Russia might have intended to do with voter registration data such as what was taken in the Illinois hack. When FBI Counterintelligence official Bill Priestap was asked in a June 2017 hearing how Moscow might use such data, his answer revealed that he had no clue: “They took the data to understand what it consisted of,” said the struggling Priestap, “so they can affect better understanding and plan accordingly in regards to possibly impacting future elections by knowing what is there and studying it.”
The inability to think of any plausible way for the Russian government to use such data explains why DHS and the intelligence community adopted the argument, as senior DHS officials Samuel Liles and Jeanette Manfra put it, that the hacks “could be intended or used to undermine public confidence in electoral processes and potentially the outcome.” But such a strategy could not have had any effect without a decision by DHS and the U.S. intelligence community to assert publicly that the intrusions and other scanning and probing were Russian operations, despite the absence of hard evidence. So DHS and other agencies were consciously sowing public doubts about U.S. elections that they were attributing to Russia.
DHS Reveals Its Self-Serving Methodology
In June 2017, Liles and Manfra testified to the Senate Intelligence Committee that an October 2016 DHS intelligence report had listed election systems in 21 states that were “potentially targeted by Russian government cyber actors.” They revealed that the sensational story leaked to the press in late September 2016 had been based on a draft of the DHS report. And more importantly, their use of the phrase “potentially targeted” showed that they were arguing only that the cyber incidents it listed were possible indications of a Russian attack on election infrastructure.
Furthermore, Liles and Manfra said the DHS report had “catalogued suspicious activity we observed on state government networks across the country,” which had been “largely based on suspected malicious tactics and infrastructure.” They were referring to a list of eight IP addresses an August 2016 FBI “flash alert” had obtained from the Illinois and Arizona intrusions, which DHS and FBI had not been able to attribute to the Russian government.

Manfra: No doubt it was the Russians. (C-SPAN)
The DHS officials recalled that the DHS began to “receive reports of cyber-enabled scanning and probing of election-related infrastructure in some states, some of which appeared to originate from servers operated by a Russian company.” Six of the eight IP addresses in the FBI alert were indeed traced to King Servers, owned by a young Russian living in Siberia. But as DHS cyber specialists knew well, the country of ownership of the server doesn’t prove anything about who was responsible for hacking: As cybersecurity expert Jeffrey Carr pointed out, the Russian hackers who coordinated the Russian attack on Georgian government websites in 2008 used a Texas-based company as the hosting provider.
The cybersecurity firm ThreatConnect noted in 2016 that one of the other two IP addresses had hosted a Russian criminal market for five months in 2015. But that was not a serious indicator, either. Private IP addresses are reassigned frequently by server companies, so there is not a necessary connection between users of the same IP address at different times.
The DHS methodology of selecting reports of cyber incidents involving election-related websites as “potentially targeted” by Russian government-sponsored hackers was based on no objective evidence whatever. The resulting list appears to have included any one of the eight addresses as well as any attack or “scan” on a public website that could be linked in any way to elections.
This methodology conveniently ignored the fact that criminal hackers were constantly trying to get access to every database in those same state, country and municipal systems. Not only for Illinois and Arizona officials, but state electoral officials.
In fact, 14 of the 21 states on the list experienced nothing more than the routine scanning that occurs every day, according to the Senate Intelligence Committee. Only six involved what was referred to as a “malicious access attempt,” meaning an effort to penetrate the site. One of them was in Ohio, where the attempt to find a weakness lasted less than a second and was considered by DHS’s internet security contractor a “non-event” at the time.
State Officials Force DHS to Tell the Truth
For a year, DHS did not inform the 21 states on its list that their election boards or other election-related sites had been attacked in a presumed Russian-sponsored operation. The excuse DHS officials cited was that it could not reveal such sensitive intelligence to state officials without security clearances. But the reluctance to reveal the details about each case was certainly related to the reasonable expectation that states would publicly challenge their claims, creating a potential serious embarrassment.
On Sept. 22, 2017, DHS notified 21 states about the cyber incidents that had been included in the October 2016 report. The public announcement of the notifications said DHS had notified each chief election officer of “any potential targeting we were aware of in their state leading up to the 2016 election.” The phrase “potential targeting” again telegraphed the broad and vague criterion DHS had adopted, but it was ignored in media stories.
But the notifications, which took the form of phone calls lasting only a few minutes, provided a minimum of information and failed to convey the significant qualification that DHS was only suggesting targeting as a possibility. “It was a couple of guys from DHS reading from a script,” recalled one state election official who asked not to be identified. “They said [our state] was targeted by Russian government cyber actors.”
A number of state election officials recognized that this information conflicted with what they knew. And if they complained, they got a more accurate picture from DHS. After Wisconsin Secretary of State Michael Haas demanded further clarification, he got an email response from a DHS official with a different account. “[B]ased on our external analysis,” the official wrote, “the WI [Wisconsin] IP address affected belongs to the WI Department of Workforce Development, not the Elections Commission.”
California Secretary of State Alex Padilla said DHS initially had notified his office “that Russian cyber actors ‘scanned’ California’s Internet-facing systems in 2016, including Secretary of State websites.” But under further questioning, DHS admitted to Padilla that what the hackers had targeted was the California Department of Technology’s network.
Texas Secretary of State Rolando Pablos and Oklahoma Election Board spokesman Byron Dean also denied that any state website with voter- or election-related information had been targeted, and Pablos demanded that DHS “correct its erroneous notification.”
Despite these embarrassing admissions, a statement issued by DHS spokesman Scott McConnell on Sept. 28, 2017 said the DHS “stood by” its assessment that 21 states “were the target of Russian government cyber actors seeking vulnerabilities and access to U.S. election infrastructure.” The statement retreated from the previous admission that the notifications involved “potential targeting,” but it also revealed for the first time that DHS had defined “targeting” very broadly indeed.
It said the category included “some cases” involving “direct scanning of targeted systems” but also cases in which “malicious actors scanned for vulnerabilities in networks that may be connected to those systems or have similar characteristics in order to gain information about how to later penetrate their target.”
It is true that hackers may scan one website in the hope of learning something that could be useful for penetrating another website, as cybersecurity expert Prof. Herbert S. Lin of Stanford University explained to me in an interview. But including any incident in which that motive was theoretical meant that any state website could be included on the DHS list, without any evidence it was related to a political motive.
Arizona’s further exchanges with DHS revealed just how far DHS had gone in exploiting that escape clause in order to add more states to its “targeted” list. Arizona Secretary of State Michele Reagan tweeted that DHS had informed her that “the Russian government targeted our voter registration systems in 2016.” After meeting with DHS officials in early October 2017, however, Reagan wrote in a blog post that DHS “could not confirm that any attempted Russian government hack occurred whatsoever to any election-related system in Arizona, much less the statewide voter registration database.”
What the DHS said in that meeting, as Reagan’s spokesman Matt Roberts recounted to me, is even more shocking. “When we pressed DHS on what exactly was actually targeted, they said it was the Phoenix public library’s computers system,” Roberts recalled.
In April 2018, a CBS News “60 Minutes” segment reported that the October 2016 DHS intelligence report had included the Russian government hacking of a “county database in Arizona.” Responding to that CBS report, an unidentified “senior Trump administration official” who was well-briefed on the DHS report told Reuters that “media reports” on the issue had sometimes “conflated criminal hacking with Russian government activity,” and that the cyberattack on the target in Arizona “was not perpetrated by the Russian government.”
NSA Finds a GRU Election Plot
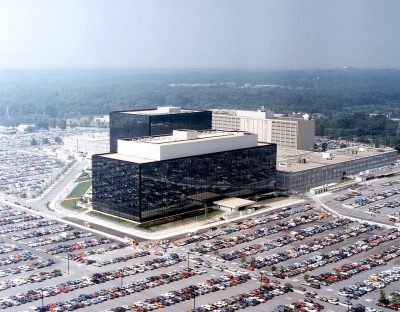
National Security Agency headquarters in Fort Meade, Md. (Wikimedia)
NSA intelligence analysts claimed in a May 2017 analysis to have documented an effort by Russian military intelligence (GRU) to hack into U.S. electoral institutions. In an intelligence analysis obtained by The Intercept and reported in June 2017, NSA analysts wrote that the GRU had sent a spear-phishing email—one with an attachment designed to look exactly like one from a trusted institution but that contains malware design to get control of the computer—to a vendor of voting machine technology in Florida. The hackers then designed a fake web page that looked like that of the vendor. They sent it to a list of 122 email addresses NSA believed to be local government organizations that probably were “involved in the management of voter registration systems.” The objective of the new spear-phishing campaign, the NSA suggested, was to get control of their computers through malware to carry out the exfiltration of voter-related data.
But the authors of The Intercept story failed to notice crucial details in the NSA report that should have tipped them off that the attribution of the spear-phishing campaign to the GRU was based merely on the analysts’ own judgment—and that their judgment was faulty.
The Intercept article included a color-coded chart from the original NSA report that provides crucial information missing from the text of the NSA analysis itself as well as The Intercept’s account. The chart clearly distinguishes between the elements of the NSA’s account of the alleged Russian scheme that were based on “Confirmed Information” (shown in green) and those that were based on “Analyst Judgment” (shown in yellow). The connection between the “operator” of the spear-phishing campaign the report describes and an unidentified entity confirmed to be under the authority of the GRU is shown as a yellow line, meaning that it is based on “Analyst Judgment” and labeled “probably.”
A major criterion for any attribution of a hacking incident is whether there are strong similarities to previous hacks identified with a specific actor. But the chart concedes that “several characteristics” of the campaign depicted in the report distinguish it from “another major GRU spear-phishing program,” the identity of which has been redacted from the report.
The NSA chart refers to evidence that the same operator also had launched spear-phishing campaigns on other web-based mail applications, including the Russian company “Mail.ru.” Those targets suggest that the actors were more likely Russian criminal hackers rather than Russian military intelligence.
Even more damaging to its case, the NSA reports that the same operator who had sent the spear-phishing emails also had sent a test email to the “American Samoa Election Office.” Criminal hackers could have been interested in personal information from the database associated with that office. But the idea that Russian military intelligence was planning to hack the voter rolls in American Samoa, an unincorporated U.S. territory with 56,000 inhabitants who can’t even vote in U.S. presidential elections, is plainly risible.
The Mueller Indictment’s Sleight of Hand
The Mueller indictment of GRU officers released on July 13 appeared at first reading to offer new evidence of Russian government responsibility for the hacking of Illinois and other state voter-related websites. A close analysis of the relevant paragraphs, however, confirms the lack of any real intelligence supporting that claim.
Mueller accused two GRU officers of working with unidentified “co-conspirators” on those hacks. But the only alleged evidence linking the GRU to the operators in the hacking incidents is the claim that a GRU official named Anatoly Kovalev and “co-conspirators” deleted search history related to the preparation for the hack after the FBI issued its alert on the hacking identifying the IP address associated with it in August 2016.
A careful reading of the relevant paragraphs shows that the claim is spurious. The first sentence in Paragraph 71 says that both Kovalev and his “co-conspirators” researched domains used by U.S. state boards of elections and other entities “for website vulnerabilities.” The second says Kovalev and “co-conspirators” had searched for “state political party email addresses, including filtered queries for email addresses listed on state Republican Party websites.”

Mueller: Don’t read the fine print. (The White House/Wikimedia)
Searching for website vulnerabilities would be evidence of intent to hack them, of course, but searching Republican Party websites for email addresses is hardly evidence of any hacking plan. And Paragraph 74 states that Kovalev “deleted his search history”—not the search histories of any “co-conspirator”—thus revealing that there were no joint searches and suggesting that the subject Kovalev had searched was Republican Party emails. So any deletion by Kovalev of his search history after the FBI alert would not be evidence of his involvement in the hacking of the Illinois election board website.
With this rhetorical misdirection unraveled, it becomes clear that the repetition in every paragraph of the section of the phrase “Kovalev and his co-conspirators” was aimed at giving the reader the impression the accusation is based on hard intelligence about possible collusion that doesn’t exist.
The Need for Critical Scrutiny of DHS Cyberattack Claims
The DHS campaign to establish its role as the protector of U.S. electoral institutions is not the only case in which that agency has used a devious means to sow fear of Russian cyberattacks. In December 2016, DHS and the FBI published a long list of IP addresses as indicators of possible Russian cyberattacks. But most of the addresses on the list had no connection with Russian intelligence, as former U.S. government cyber-warfare officer Rob Lee found on close examination.
When someone at the Burlington, Vt., Electric Company spotted one of those IP addresses on one of its computers, the company reported it to DHS. But instead of quietly investigating the address to verify that it was indeed an indicator of Russian intrusion, DHS immediately informed The Washington Post. The result was a sensational story that Russian hackers had penetrated the U.S. power grid. In fact, the IP address in question was merely Yahoo’s email server, as Rob Lee told me, and the computer had not even been connected to the power grid. The threat to the power grid was a tall tale created by a DHS official, which the Post had to embarrassingly retract.
Since May 2017, DHS, in partnership with the FBI, has begun an even more ambitious campaign to focus public attention on what it says are Russian “targeting” and “intrusions” into “major, high value assets that operate components of our Nation’s critical infrastructure”, including energy, nuclear, water, aviation and critical manufacturing sectors. Any evidence of such an intrusion must be taken seriously by the U.S. government and reported by news media. But in light of the DHS record on alleged threats to election infrastructure and the Burlington power grid, and its well-known ambition to assume leadership over cyber protection, the public interest demands that the news media examine DHS claims about Russian cyber threats far more critically than they have up to now.
Gareth Porter is an independent investigative journalist and winner of the 2012 Gellhorn Prize for journalism. His latest book is Manufactured Crisis: The Untold Story of the Iran Nuclear Scare.
Skripals – When the BBC Hide the Truth
By Craig Murray | August 27, 2018
On 8 July 2018 a lady named Kirsty Eccles asked what, in its enormous ramifications, historians may one day see as the most important Freedom of Information request ever made. The rest of this post requires extremely close and careful reading, and some thought, for you to understand that claim.
Dear British Broadcasting Corporation,
1: Why did BBC Newsnight correspondent Mark Urban keep secret from the licence payers that he had been having meetings with Sergei Skripal only last summer.
2: When did the BBC know this?
3: Please provide me with copies of all correspondence between yourselves and Mark Urban on the subject of Sergei Skripal.
Yours faithfully,
Kirsty Eccles
The ramifications of this little request are enormous as they cut right to the heart of the ramping up of the new Cold War, of the BBC’s propaganda collusion with the security services to that end, and of the concoction of fraudulent evidence in the Steele “dirty dossier”. This also of course casts a strong light on more plausible motives for an attack on the Skripals.
Which is why the BBC point blank refused to answer Kirsty’s request, stating that it was subject to the Freedom of Information exemption for “Journalism”.
10th July 2018
Dear Ms Eccles
Freedom of Information request – RFI20181319
Thank you for your request to the BBC of 8th July 2018, seeking the following information under the
Freedom of Information Act 2000:
1: Why did BBC Newsnight correspondent Mark Urban keep secret from the licence payers that he
had been having meetings with Sergei Skripal only last summer.
2: When did the BBC know this?
3: Please provide me with copies of all correspondence between yourselves and Mark Urban on the
subject of Sergei Skripal.
The information you have requested is excluded from the Act because it is held for the purposes of
‘journalism, art or literature.’ The BBC is therefore not obliged to provide this information to you. Part VI
of Schedule 1 to FOIA provides that information held by the BBC and the other public service broadcasters
is only covered by the Act if it is held for ‘purposes other than those of journalism, art or literature”. The
BBC is not required to supply information held for the purposes of creating the BBC’s output or
information that supports and is closely associated with these creative activities.
The BBC is of course being entirely tendentious here – “journalism” does not include the deliberate suppression of vital information from the public, particularly in order to facilitate the propagation of fake news on behalf of the security services. That black propaganda is precisely what the BBC is knowingly engaged in, and here trying hard to hide.
I have today attempted to contact Mark Urban at Newsnight by phone, with no success, and sent him this email:
To: mark.urban@bbc.co.uk
Dear Mark,
As you may know, I am a journalist working in alternative media, a member of the NUJ, as well as a former British Ambassador. I am researching the Skripal case.
I wish to ask you the following questions.
1) When the Skripals were first poisoned, it was the largest news story in the entire World and you were uniquely positioned having held several meetings with Sergei Skripal the previous year. Yet faced with what should have been a massive career break, you withheld that unique information on a major story from the public for four months. Why?
2) You were an officer in the Royal Tank Regiment together with Skripal’s MI6 handler, Pablo Miller, who also lived in Salisbury. Have you maintained friendship with Miller over the years and how often do you communicate?
3) When you met Skripal in Salisbury, was Miller present all or part of the time, or did you meet Miller separately?
4) Was the BBC aware of your meetings with Miller and/or Skripal at the time?
5) When, four months later, you told the world about your meetings with Skripal after the Rowley/Sturgess incident, you said you had met him to research a book. Yet the only forthcoming book by you advertised is on the Skripal attack. What was the subject of your discussions with Skripal?
6) Pablo Miller worked for Orbis Intelligence. Do you know if Miller contributed to the Christopher Steele dossier on Trump/Russia?
7) Did you discuss the Trump dossier with Skripal and/or Miller?
8) Do you know whether Skripal contributed to the Trump dossier?
9) In your Newsnight piece following the Rowley/Sturgess incident, you stated that security service sources had told you that Yulia Skripal’s telephone may have been bugged. Since January 2017, how many security service briefings or discussions have you had on any of the matter above.I look forward to hearing from you.
Craig Murray
I should very much welcome others also sending emails to Mark Urban to emphasise the public demand for an answer from the BBC to these vital questions. If you have time, write your own email, or if not copy and paste from mine.
To quote that great Scot John Paul Jones, “We have not yet begun to fight”.
5 timely reminders that the media think you are an idiot…

By Kit | OffGuardian | August 28, 2018
The corporate media think we are stupid. All of us. They have as much respect for our intellect or ability to reason as they do for the truth. This is displayed, in size 20 font, on the front page of every newspaper every single day. They paint a picture of an absurd world, and expect us all to nod along with it, blithely accepting their stories as true, no matter what laws of reason – or even physics – they bend to suit their purpose.
The world in the newspaper and on the television is not real in any true sense of the word. Merely a crazy fun-house mirror reflection of the truth. Important features shrunk to nothing, tiny flaws blown up out of proportion. Apparently solid shapes that – on inspection – are nothing but strange plays of light and shadow.
With that in mind, let’s remind ourselves of the kind of completely bonkers things we’re all expected to believe.
1. The Inherent silliness of “ISIS”
This section was going to be more specific, but as I looked back over recent history, there was no single absurdity that highlighted how stupid the ISIS story was.
ISIS was, and is, silly. A few bullet points to demonstrate this – and a reminder that these are not exaggerated in any way. These are, supposedly, facts:
- They were making $1-$3 million PER DAY smuggling oil out of Syria, in convoys kilometres long that the US air force either couldn’t find or wouldn’t bomb because of “risks to civilians”. How they had the technical expertise to extract and process this oil was never explained.
- They minted their own currency.
- They published end-of-year reports, like a business, and kept detailed accounts on flash drives and USB sticks. Despite this, no ISIS bank accounts were ever seized, monitored or shut down.
- They had multiple social media accounts, YouTube channels – often described as “ISIS linked social media accounts” – these accounts weren’t locked, blocked or deleted. The registered owners weren’t arrested. They had their own twitter app which was impossible to block and created their own social network.
- They had their own TV channel, with an animated logo, a waving flag, in the corner of their videos. Think on this – somebody, somewhere, made that logo.
- They had fleets of Toyotas, which we’re supposed to believe they just sort of… acquired. They are all clean, new and undamaged. They are all colour-matched too, of course. There are red ones, white ones, black ones and tan ones. With and without logos painted on the hood. They deployed these trucks in photo-shoots and “viral” videos, the theoretical production of which simply boggles the mind. A bunch of black Toyota’s crossing the desert doesn’t look like much, but think about the actual logistics of making the video. They had to drive up to this spot, drop off the camera crew and equipment, drive back over the horizon, properly time their entrance by synchronizing all the driving and spacing the trucks out evenly, drive past the camera crew waving their flags… then drive back and pick up the camera men and equipment. All of this in the middle of a war zone.
- Of course all their videos had the same music, the ISIS theme, which was Arabic voices singing in close harmony. We’re supposed to believe that – somewhere in the heart of their war-torn empire – a bunch of crazy zealots gathered round a microphone to sing a capella melodies about “death to the west”, while a frustrated technician muttered to himself about “levels” and how Muhammad is flat on the high note. This spawned their own genre of music, which NME did a story on.
It’s so… stupid. And yet the media says it, and expects us to believe it.
ISIS – the all-powerful death cult, the existential threat to Western democracy, on the verge of “regional dominance”. There was a map and everything – world domination by 2020.
Despite all this, ISIS – the untouchable hydra of evil – completely fell apart as a force in the region just months after Russia and Iran got involved in the Syrian war.
Why was this?
Could it be that ISIS were just a media creation – the PR arm of the CIA’s jihadist proxy army – and, in truth, barely existed as fighting force? Existing, rather, to give Western powers an excuse to conduct air strikes on Syrian territory?
Or could it be that the MSM realised that 10,000 insane, bloodthirsty zealots taking time out of their devout holy war to have design meetings about coinage, or shoot music videos in Dune buggies, rings rather hollow?
It’s all a bit silly isn’t it?
2. The Syrian government Is collectively suicidal
Several times, in the last couple of years, Western leaders have made remarkably prescient statements – something along the lines of “We will not tolerate the use of chemical weapons on civilians”, or “We will act if chemical weapons are used”. In fact, in just the last few days both the US and France have reissued these warnings.
Despite these warnings, and though it offers him literally zero strategic advantages of any kind, Assad keeps deploying his super-secret chemical weapons against civilians… just because. He’s winning the war, it’s pretty much over, the only thing that could swing it against him is NATO, and he keeps deliberately inciting them to attack him.
There’s only 2 explanations for that – either he, and his government, are low-key suicidal, or it never happened, and the propagandists in the media truly believe we are completely stupid.
Then there’s the photographs.
Syria knows they have been in America’s crosshairs for years, since well before the start of the Arab spring. They are aware of Israel’s designs on Syrian land, and more than familiar with the US modus operandi re: “humanitarianism”. They KNOW the worst thing they could do is give America, and their NATO allies, even the whisper of a war crime to get indignant about.
… and yet we’re supposed to believe, not only that the regime tortured and executed tens of thousands of “peaceful protestors” for absolutely no reason, but they also kept a carefully photographed and catalogued record of their crimes.
This was brought up in the Guardian today, the famous “Caesar Photographs”, photos of 11,000 people the Assad government tortured and killed, all properly catalogued and numbered and then – conveniently – leaked by some unknown “former guard” and displayed in London like some morbid art exhibition.
The identity of the “leaker” remains a mystery, and there is literally zero evidence the photographs are a) from Syria or b) real.
Does this version of events sound even slightly reasonable?
3. Amnesty International used echolocation to recreate a Syrian prison
They really did. They have some guys claiming to be Syrian resistance members who were held in one of Assad’s “torture prisons”, but they were either blindfolded or in darkness the whole time, so in order to map out the interior of the prison… Amnesty International played sounds to them, to see if they sounded the same. I truly wish I was joking:
Inmates were constantly blindfolded or forced to kneel and cover their eyes when guards entered their cells, so sound became the key sense by which they navigated and measured their environment – and therefore one of the chief tools with which the Forensic team could reconstruct the prison layout. Using a technique of “echo profiling”, sound artist Lawrence Abu Hamdan was able to determine the size of cells, stairwells and corridors by playing different reverberations and asking witnesses to match them with sounds they remembered hearing in the prison.
There’s no reports as to why exactly the men were locked up, how they got away, why they were released and not executed like everyone else OR – indeed – where they acquired their bat-like super hearing.
… But we do now have a 3D model of Assad’s “torture prison”. We even know which room is the crematorium too, because it looked like the snow on the roof had melted in one satellite photo… and the only thing that makes a roof hot is the burning corpses of dissidents.
The whole process is part of a completely made up recently developed field known as “forensic architecture”. In simple terms, it seems “forensic architecture” is looking at the outside of a building – or indeed a photograph of the outside of a building – and guessing what’s inside. While this might seem difficult, pointless, or even insane to most people… to the mainstream media it is worth of thousands of words of coverage and, indeed, winning media awards.
Does any of that really make any sense to you?
4. Jeremy Corbyn hates the Jews
Jeremy Corbyn is soft – maybe, arguably – too soft for the job that history has violently hoisted on to his shoulders, but soft none the less. He rides his bike to work, wears cardigans, is a vegetarian. He has campaigned for peace and against war his entire life. He was arrested for protesting apartheid whilst Margaret Thatcher was calling Nelson Mandela a terrorist, he spoke out against Pinochet while the General was a darling on both sides of the Atlantic.
He has won two international peace prizes.
The idea that, during a public career dedicated to the socialist ideals of decency and fairness, he was secretly thinking “Bloody Jews!” the whole time is completely absurd. Insultingly absurd, and there is not a single piece of evidence to suggest otherwise. There is nothing more to be said on the matter.
5. Russiagate
This is the big one, currently. The grand-daddy of the nothingburgers. Russiagate never happened. There was no collusion, no cheating or vote hacking or pay-offs. They have found literally zero evidence anything ever took place, seizing upon tiny anecdotal scraps and blaring them out in FULL CAPS HEADLINES to make a case in the court of public opinion that would never stand in an actual court.
Where “Russiagate” is different from most invented media schlock however, is the sheer weight of counter evidence. For most media fiction you can say “Well, there’s very little evidence to support that” (see Corbyn = anti-Semite as a classic example). With Russiagate you can go even further: There is a ton – A TON – of evidence to the contrary, clear-cut evidence that Russia (and Putin) have nothing to do with Trump being President. The media refuse to acknowledge this evidence, directly and contemptuously challenging the public’s ability to reason.
Below is a list of unchallenged, non-controversial facts about Russiagate:
- The only proven, admitted, wrong-doing in the 2016 Presidential election was carried out by the DNC, who rigged the primaries so Clinton would be the democratic candidate. This was later admitted to by members of the DNC.
- The e-mails which first brought this to light were published by WikiLeaks, there is no proven link between WikiLeaks and the Russian government.
- Julian Assange, founder of WikiLeaks claimed the e-mails were from an internal leak, not the result of a hack.
- The “Trump-Russia” dossier, a collection of (possibly fabricated) dirt put together by British ex-spy Christopher Steele, was paid for by the DNC and Clinton’s campaign.
These facts, alone, should bring Russiagate down… but there’s more. Since becoming President, Donald Trump has:
- Armed the Ukrainian coup government.
- Bombed Syria.
- Torn up the Iran deal.
- Sanctioned Russia over the Skripal case.
- Sanctioned Russia over “election interference”.
- Expelled Russian diplomats.
- Killed over 200 Russian “mercenaries” in Syria.
These are policies that not only run counter to ALL of Russia’s interests, but very nearly brought us to the brink of World War 3.
And yet we’re told, over and over, to ignore our own logical minds and believe that Trump is Putin’s “puppet”. That Trump is “soft” on Russia.
Why would a product of Russian collusion pursue policies harmful to Russia? How many Russians need to die before we accept that Trump is anything but soft?
The media line on this issue is insane, and dangerous. In refusing to acknowledge the actual truth – that the US Deep State is pushing for conflict with Russia – the media are dragging us toward apocalypse, smiling happily to themselves as they go.
They are either all delusional morons, think WE are all delusional morons, or – most probably – both.
The inmates are running the asylum, declaring the rest of us insane because none of us are hearing voices.
This is why the media is in decline, why the BBC is losing its audience and the newspapers have plummeting readership, because people are tired of being treated like idiots and herded like cattle. We’ve made a collective decision to cut the bullshit out of our lives. The world is heading towards a split, two parallel universes running together – the real world, where reasonable pragmatic people get on with the struggles of life, and the media world, where fake people write about pretend events in newspapers nobody reads.
The media has become that manipulative spouse who lies and cheats and tells you it’s all your fault. A narcissistic gaslighter who just will not change.
It’s time to make a clean break.
Trump Is Right About “Flipping”
By Jacob G. Hornberger | FFF | August 27, 2018
In the wake of the federal criminal conviction of former Trump official Paul Manafort and the guilty plea in federal court of former Trump lawyer Michael Cohen, the mainstream press is singing the praises of special prosecutor (and former FBI Director) Robert Mueller and the Justice Department.
In the process, Trump’s critics are condemning his denunciation of “flipping,” the process by which federal prosecutors offer a sweet deal to criminal defendants in return for testifying against a “higher-up” who the feds are also prosecuting. The press and the anti-Trumpsters say that such a practice is part of the “rule of law” and essential to the proper administration of justice.
Nothing could be further from the truth. Whatever else might be said about Trump, he is absolutely right on this point. The process of offering sweetheart deals to people in return for their “cooperation” to get someone else convicted has long been one of the most corrupt aspects of the federal criminal-justice system, especially as part of the federal government’s much-vaunted (and much-failed) war on drugs.
Suppose a federal criminal defendant contacts a prospective witness in a case and offers him $50,000 in return for his “cooperation” in his upcoming trial. The money will be paid as soon as the trial is over. The defendant makes it clear that he wants the witness to “tell the truth” but that his “cooperation” when he testifies at trial would be greatly appreciated.
What would happen if federal officials learned about that communication and offer? They would go ballistic. They would immediately secure an indictment for bribery and witness tampering.
What if the defendant says, “Oh, no, I wasn’t tampering with the witness. I specifically told him that I wanted him to tell the truth when he took the witness stand. I was just seeking his friendly ‘cooperation’ with my $50,000 offer to him.”?
It wouldn’t make a difference. Federal prosecutors would go after him with a vengeance on bribery and witness-tampering charges. And it is a virtual certainty that they would get a conviction.
There is good reason for that. The law recognizes that the money could serve as an inducement for the witness to lie. Even though the defendant tells him to “tell the truth,” the witness knows that the fifty grand is being paid to him to help the defendant get acquitted, especially since it is payable after the trial is over. The temptation to lie, in return for the money, becomes strong, which is why the law prohibits criminal defendants from engaging in this type of practice.
Suppose a federal prosecutor says to a witness, “You are facing life in prison on the charges we have brought against you. But if you ‘cooperate’ with us to get John Doe, we will adjust the charges so that the most the judge can do is send you to jail for only 5 years at most. If you are really ‘cooperative,’ we will recommend that the judge give you the lowest possible sentence, perhaps even probation. Oh, one more thing, we want to make it clear that we do want you to tell the truth.”
Do you see the problem? The temptation to please the prosecutor with “cooperation” becomes tremendous. If the witness can help secure a conviction of Doe, he stands to get a much lighter sentence for his successful “cooperation.” The inducement to commit perjury oftentimes takes over, notwithstanding the prosecutor’s admonition to the witness to “tell the truth.”
Defenders of this corrupt process say that without it, prosecutors could never get convictions. That’s pure nonsense. For one thing, prosecutors can secure a conviction against the witness and then force him to testify once his case is over. That’s because a person whose case is over is unable to rely on the Fifth Amendment to avoid testifying in the case against John Doe.
Moreover, the prosecutor can give what is called “use immunity” to the witness, which then forces him to testify in the case against Doe. Use immunity is not full immunity from prosecution. It simply means that the prosecutor cannot use the witness’s testimony against Doe to convict the witness at his trial. The prosecutor must convict him with other evidence.
But even if it means that the prosecutor is unable to secure some convictions, the question has to be asked: Do we want prosecutors securing convictions in this way? After all, there is a related question that must be asked: How many innocent people are convicted by perjured testimony from a witness who is doing his best to “cooperate” with the prosecution in the hope of getting a lighter sentence?
Given all the accolades being accorded Mueller, it is a shame that he has chosen to go down the same corrupt road that all other federal prosecutors have traveled. He didn’t have to do that. He could have led the way out of this immoral morass by taking a firm and public stand against this corrupt procedure. The fact that he has chosen instead to participate in it is a shame, to say the least.
Time for media to tell Americans about the bills in Congress to give Israel $38 billion
If Americans Knew | August 24, 2018
Congress is currently considering legislation to give Israel a total of $38 billion over 10 years, the largest such aid package in U.S. history. Yet, U.S. media are not telling Americans about the legislation, which is before Congress right now…
Legislation to give Israel $38 billion over the next ten years is currently working its way through Congress. This is the largest military aid package in U.S. history.
Yet, while Israeli media are covering the legislation, virtually no U.S. news reports have informed American taxpayers about this proposed disbursement of their tax money.
The proposed military aid amounts to $23,000 per every Jewish Israeli family of four. (Aid to Israel has been on average about 7,000 times greater per capita than U.S. aid to others around the world.)
The proposed aid is divided between two bills. One has already passed, but the main bill is still before Congress.
1. The 2019 military spending bill contains a provision giving Israel 550 million dollars (i.e. $5.5 billion over 10 years). This has already passed both houses of Congress and was signed into law on August 16.
2. A second bill, “United States-Israel Security Assistance Authorization Act of 2018,” is slated to give rest of the package, approximately $33 billion, to Israel. The number is H.R.5141.
This bill has already passed the Senate, and is now being considered in two House committees: Armed Services and Science, Space, and Technology.[1] (Click on each committee to see its members.)
The reason that the bill was referred to the committee on space is because the bill mandates that NASA work with the Israel Space Agency, despite accusations of Israeli espionage against the U.S.
In 2015 a Caltech scientist revealed that the Chair of Israel’s National Committee for Space Research had illegally acquired classified U.S. information. The alleged espionage and theft largely took place at Caltech’s Jet Propulsion Laboratory, a top NASA research and development center.
The $38 billion package was originally negotiated by the Obama administration in 2014,[2] but must now be codified into law.
While U.S. media are inexplicably ignoring this massive aid legislation, Israeli media are covering it regularly, and Israel lobbying organizations are calling on their members to support it. (AIPAC, the American Israel Public Affairs Committee, reportedly pioneered the legislation.)
For example, while U.S. media covered the military spending bill, none of the reports seem to have mentioned the millions of dollars to Israel. This is exemplified by an in depth PBS examination of the bill, which discussed aid to Ukraine – which gets a fraction of the amount promised to Israel – but failed to mention the far larger money to Israel.
We could not find any news reports that tell about the current aid to Israel bill.
In other words, Israelis know about the proposed $38 billion legislation, Israeli partisans in the U.S. know about it and are pressuring Congress to pass it, but the large majority of American taxpayers have no idea the legislation is before Congress.
Indications are that U.S. media are not going to report on these bills unless Americans demand that they do so.
Any Americans who believe the media should report on how American tax money is spent, will need to contact the media, both national and local, and tell them that.
The House will be back in session on September 4th. It’s probable that the bill will move forward quickly at that point. It’s unlikely that the process will involve any public debate whatsoever, unless voters contact their Congressional representatives and demand this.[3]
1. A third House committee, the committee on Foreign Affairs, passed the bill on May 9 and recommended that the full House now consider it “Under Suspension of the Rules, by Unanimous Consent.” (“The purpose of considering bills under suspension is to dispose of non-controversial measures expeditiously.” )
2. The Obama administration’s Memorandum of Understanding gave Israel even more money than it seems to have expected. The Forward reported at the time: “When Yaakov Nagel, Israel’s acting national security adviser, was tasked with heading the team negotiating a new 10-year military aid package with the United States, Prime Minister Netanyahu set forth the guidelines: ‘If you reach $3.5 billion a year, you’ll get a gold medal,’ Nagel recalled Wednesday, hours before signing the agreement in Washington. ‘If you get $3.3 billion you’ll get a silver medal; and if you get $3.1 billion you’ll get the bronze.’” Israel got an MOU for $3.8 billion per year, the largest pledge of military assistance in U.S. history.
A memorandum of understanding (MOU) is a non-binding agreement between two or more parties outlining the terms and details of an understanding. The legislation currently before Congress seeks to make the Obama administration’s 2014 MOU into law.
3. The disbursement is problematic on at least three grounds: (1) the majority of Americans feel we already give Israel too much money, (2) the aid would violate U.S. laws – see below, and (3) it would fund Israeli violations of international law and human rights abuses, causing tragedy in the region and hostility to the U.S. This has been documented in reports by the Red Cross, Human Rights Watch, Defense for Children, Christian Aid, Amnesty International, Israeli human rights organizations, etc, but these numerous reports, like the current $38 billion legislation, are largely ignored by U.S. media, which consistently provide Israel-centric reporting and fail to give Americans the full picture.
For a timeline of Israelis and Palestinians of all ages killed since 2000 go here.
The aid would violate several U.S. laws:
• It would violate two amendments to the 1961 Foreign Assistance Act, known as the the Symington and Glenn Amendments, that ban support for countries engaged in clandestine nuclear programs. (More information here.)
• It would violate the Leahy Law, which prohibits aid to countries guilty of human rights violations (more info here).
In the past Israel has used U.S. aid in ways that violated the Arms Export Control Act (AECA), which prohibits re-export of U.S.-origin defense and dual-use technology, which Israel has repeatedly done. Israel has also been charged with using U.S. weaponry illegally.
Russophobia digest part 6: Evidence is optional as alleged anti-vaxx Russian bots go phishing
RT | August 24, 2018
Alleged Russian bots have been at the forefront of another week of Russophobia, with a new but familiar pattern emerging. Scare stories and accusations are made, before a later admission that no actual evidence is available.
RT takes a look at the last seven days or so of Russophobia.
Democrats’ security chief missed the memo
One of the real values of Russophobia is that it means thought and proof are rarely, if ever, needed anymore. Why find out what really happened when there is a decent conclusion to jump to?
For example, this week Bob Lord, the Democratic National Committee’s chief security officer, claimed that the organization’s US voter database had been hacked. Only, he later had to admit it was actually a ‘phishing test.’
Yep, nobody told the security chief about the security test, and he didn’t bother asking either, because it’s much easier to simply insinuate that Russians did it. To be fair to Lord, he didn’t appear to overtly use the ‘R’ word, but almost every media report on the non-incident seasoned its coverage liberally with accusations against Russia.
Microsoft’s marketing dept jumps on Russophobia bandwagon
Staying in the murky world of unsubstantiated cyber-claims, Microsoft said it has also thwarted phishing attacks on political targets by a group “widely associated” with Russia (Fancy Bear, in case you’re interested). It backed up its claims in the now-time-honored fashion of admitting there is “no evidence” that the dodgy domains detected were used in any successful attacks — and there’s no evidence “to indicate the identity of the ultimate targets.”
So, why is Microsoft getting involved? Because it’s got a brand new product maybe? Bill Gates’ boys have come up with anti-hacking software ‘AccountGuard’ as part of its ‘Defending Democracy Program.’
It provides “state-of-the-art cybersecurity protection at no extra cost to all candidates and campaign offices at the federal, state and local level, as well as think tanks and political organizations we now believe are under attack.”
And they claim the Russians are dangerous!?
Pro-pox bots
Those busy little alleged Russian bots are also driving the online anti-vaccine debate in the US, apparently, according to research in the US. No surprise there really, Russian bots real or imagined are accused of driving every online debate these days.
David Broniatowski from the George Washington School of Engineering and Applied Science said: “… many anti-vaccine tweets come from accounts whose provenance is unclear. These might be bots, human users or ‘cyborgs’ – hacked accounts that are sometimes taken over by bots. Although it’s impossible to know exactly how many tweets were generated by bots and trolls …”
“Impossible to know,” “provenance unclear.” So again, no real evidence, so it must be the Russians, mustn’t it?
Someone better check whether Jenny McCarthy and Jim Carrey are Russian bots too, because they’re not too keen on vaccinations either. Apparently neither is Donald Trump, but you can hardly accuse him of… Oh.
Manafort: Conviction without collusion
Russophobes were jumping for joy at the conviction of Trump’s former election chief Paul Manafort this week. He was sent down for tax fraud, and bank fraud, and hiding bank accounts. What he definitely wasn’t sent down for was colluding with Russia, which is really a little strange considering the man responsible for sending him to court was Special Counsel Robert Mueller, who was only appointed to investigate exactly that. As we’ve seen, though, evidence is optional when Russians are the target.
In the wise words of America’s commander-in-chief: “This has nothing to do with Russian collusion. This started as Russian collusion. This has absolutely nothing to do [with it].” Say what you want about Donald Trump…
Read more:
Russian hackers not found… again: DNC retracts claim voter database targeted by cyber-attack
RT | August 23, 2018
The latest alarming news on a sophisticated cyber-attack on the Democratic National Committee’s voter database may have cemented one’s worst fears over Russia hacking into the US elections… except it was really a “phishing test.”
Bob Lord, the committee’s chief security officer, raised the alarm on Wednesday after detecting a fake login page that mimicked the access page for Votebuilder, a program used by Democratic Party officials across that country that hosts the party’s voter database.
“This attempt is further proof that there are constant threats as we head into midterm elections and we must remain vigilant in order to prevent future attacks,” Lord said in a statement. However, within a few hours it became clear that blaming Moscow, no matter how tempting, would not be an option.
In a follow-up statement, Lord clarified that the fake login page was “built by a third party as part of a simulated phishing test.” He claimed that the security test was not authorized by the DNC.
“While we are extremely relieved that this wasn’t an attempted intrusion by a foreign adversary, this incident is further proof that we need to continue to be vigilant in light of potential attacks,” Lord’s anticlimactic clarification said.
It’s not uncommon for corporations or organizations to hire consultants to test for security weaknesses in their computer systems – although it’s unusual for it to be done without any knowledge of the organization, as Lord has insisted.
Still, even when reporting that the scary DNC hack was a false alarm, CNN made sure to remind its readers that Microsoft recently announced (citing no concrete evidence) that it had thwarted an attempt by hackers working for Russian military intelligence to target the US Senate and conservative think tanks that advocated for tougher policies against Moscow.
The Three Musketeers, Poison Gas, and Dead Schoolkids
By Michael Howard | American Herald Tribune | August 23, 2018
Winking and nodding to the “freedom fighters” hunkered down in the northwestern Syrian province of Idlib, the world’s schoolmarm (formally known as The West) has issued a stern warning to President Bashar al-Assad: don’t use chemical weapons “again,” or else. Said warning came via a joint statement from the US, UK and France (henceforth known as The Three Musketeers), as the Syrian government prepares its offensive to retake the country’s last remaining “rebel” stronghold. The three great and benevolent powers are “gravely concerned,” they said, about the upcoming military campaign, explaining:
We also underline our concern at the potential for further—and illegal—use of chemical weapons. We remain resolved to act if the Assad regime uses chemical weapons again. As we have demonstrated, we will respond appropriately to any further use of chemical weapons by the Syrian regime, which has had such devastating humanitarian consequences for the Syrian population.
Read it again, and take note of the crafty way in which the statement messes around with language to manipulate its target audience (us). The use of chemical weapons is accurately, and superfluously, described, and emphasized with em dashes, as “illegal,” as though there was a soul on this earth to whom this is news. Then, alluding to their coordinated missile strikes against Syria this past April, which were unleashed to much pomp and circumstance, The Three Musketeers pledge to “respond appropriately” to any such illegal action on the part of the Syrian government.
Since they insist on begging questions, we must insist on demanding answers. For instance, how “appropriate” was the aforesaid missile attack? Assuming that, in this context, a direct link exists between appropriate and legal (and only an outlaw could reject that assumption), there was certainly nothing “appropriate” about The Three Musketeers’ unilateral decision to use military force against a sovereign country last April. Quite the reverse.
The missile strike, like the one a year before, was carried out in flagrant violation of the law. There are a total of two circumstances in which the use of military force is legally justified: when greenlit by a UN Security Council resolution, or when done in self-defense, that is to say in response to a direct military attack. Neither condition was met when The Three Musketeers rocketed Syria. On the other hand, Syria is accorded the legal right under international law to strike back at its attackers, and moreover to form a coalition for that purpose. As Chapter VII Article 51 of the UN Charter states:
Nothing in the present Charter shall impair the inherent right of individual or collective self-defense if an armed attack occurs against a Member of the United Nations, until the Security Council has taken measures necessary to maintain international peace and security.
Mildly ironic, then—is it not?—that, in “appropriately” bombing the Syrian government, we granted it the legal right to bomb us back? It’s a crying shame: if only Assad and his allies were sufficiently nihilistic … we could’ve had another exhilarating World War on our hands—the third and last. To borrow a quote from of Trump’s favorite general: “Compared to war, all other forms of human endeavor shrink to insignificance. God help me, I do love it so.” On that note, I think it’s high time we substitute “War” for “God” in our Republic’s official motto. Who besides Rand Paul would vote against the proposal?
All of which is to say nothing of the fact that the alleged chemical attack in Douma, which served as the pretext for The Three Musketeers’ “appropriate” bombing raid, almost certainly didn’t happen. The first chink in the armor came in the form of Robert Fisk’s report, from the actual site of the alleged attack, that quotes a local doctor as saying:
There was a lot of shelling [by government forces] and aircraft were always over Douma at night—but on this night, there was wind and huge dust clouds began to come into the basements and cellars where people lived. People began to arrive here suffering from hypoxia, oxygen loss. Then someone at the door, a “White Helmet”, shouted “Gas!” and a panic began. People started throwing water over each other. Yes, the video was filmed here, it is genuine, but what you see are people suffering from hypoxia—not gas poisoning.
By his own count, Fisk interviewed more than twenty Douma residents; he was unable to find a single person “who showed the slightest interest in Douma’s role in bringing about the Western air attacks. Two actually told me they didn’t know about the connection.” Moreover, many of those he spoke with told him they “never believed in” the chemical weapons narratives promulgated by Western media.
Despite the fact that it squared with the Syrian Observatory For Human Rights’ (the West’s go-to authority on the Syrian conflict) assessment of the event, Fisk’s journalism was easy enough for Western ideologues to ignore or deride. He’s only one person, they countered, and he only spoke to a handful of residents and a single doctor, all of whom probably have a pro-Assad agenda. Therefore, his report is worthless and so is he.
This position grew a little less tenable when, a week after Fisk’s story was published, Russia presented to the Organization for the Prohibition of Chemical Weapons (OPCW), which was holding a conference in the Hague, seventeen eyewitnesses, a mix of residents and doctors, all of whom testified that there had been no chemical attack in Douma. As Jonathan Cook explained (yes, one had to visit his personal blog or some equally marginal source to read about this), “the US, UK and France boycotted the meeting, denouncing Russia for producing the witnesses and calling the event an ‘obscene masquerade’ and ‘theatre’”—not a very surprising reaction from a self-righteous party whose fabricated narrative is coming apart at the seams.
Then came the coup de grâce. On July 6, the OPCW published the conclusion of its fact-finding mission in Douma. Before quoting from it, I’ll jog your memory a bit. According to the Western version of events, Assad used both sarin and chlorine (or perhaps a physical mixture of the two, a nonsensical theory), in his attack on Douma—which, incidentally, had already effectively “fallen,” raising questions as to why Assad would feel compelled to use chemical weapons at all, apart from the sheer sadistic fun of it. Regardless, sarin and chlorine, said the West. Not so, said the OPCW:
OPCW designated labs conducted analysis of prioritized samples. The results show that no organophosphorous nerve agents or their degradation products were detected in the environmental samples or in the plasma samples taken from alleged casualties [my emphasis]. Along with explosive residues, various chlorinated organic chemicals were found in samples from two sites, for which there is full chain of custody. Work by the team to establish the significance of these results is on-going. The FFM team will continue its work to draw final conclusions.
Not a trace of sarin, in other words. Attempting to ascertain why “various chlorinated organic chemicals” were found at the site is a pointless exercise for someone, like myself, who knows nothing of chlorinated organic compounds. The most perfunctory research indicates that such chemicals are used for a variety of non-murderous applications, for example as solvents, and that they stick around for a long time after they’ve been introduced to an environment. The basic point, which hordes of media fixers promptly got to work obscuring, is that the Western narrative was false. The US government, in concert with its unctuous allies, lied. Go figure.
Of course, this isn’t the first time a supposed chemical attack in Syria has been called into question. Those curious about whether Assad used sarin to murder hundreds of civilians in the suburb of Ghouta in 2013, as was, and is, claimed by The West, would do well to read two essays by Seymour Hersh—“The Red Line and the Rat Line” and “Whose Sarin”—both published in the London Review of Books, both available online. Hersh also examined the chemical incident that took place in Khan Sheikhoun in April 2017—also used as a pretext for illegal US military action. This time, however, his reporting was too heretical even for the London Review of Books (not to mention the New Yorker), and so had to be published in Die Welt, which no one in the US has ever heard of, let alone read. That Hersh, the preeminent investigative journalist of his time, has been pushed into no man’s land speaks to how narrow the spectrum of permissible discourse has become in this, our great Republic. The schoolmarm is cracking her whip. At this rate Hersh will soon be relegated to the personal blog.
For other dissident views re: chemical weapons in Syria, do yourself a favor and consult the work of former UN weapons inspector Scott Ritter and MIT professor and munitions expert Theodore Postol, as well as the late journalist Robert Parry of Consortium News, all of whom have written extensively, and cogently, on the subject. Or you can keep reading the Washington Post. You’re free to decide.
But what exactly did The Three Musketeers have in mind when they broadcast their latest threat? It’s a fair question to ask. On its face, the statement appears to reflect a genuine aversion to poison gas, and a genuine hope that the Syrian government will refrain from using any in Idlib. Fair enough. Having said that, how averse could they really be, given that gas attacks provide for them the only remotely plausible excuse to lob more cruise missiles out of the Mediterranean—an activity from which they, and their media sidekicks, derive the utmost pleasure? They are, after all, incorrigible hawks. It must cut them to the bone to have to stand by and watch from the sidelines as a perfectly good war winds down, handcuffed, helpless to effect the desired outcome. How pitiable the plight of the poor impotent imperialist! Flaming warmongers need love too.
Anyway, call me schizophrenic, but when I read the words of The Three Musketeers, I couldn’t help but pick up the faint sound of a dog whistle—aimed straight at the “moderate rebels” holding down the fort in Idlib. Read between the lines, the statement is an assurance to one party dressed up as a warning to another. If there’s a “chemical incident,” we will attack: you have our word. That’s the message sent to, and received by, al-Qaeda (I don’t know what they’re calling themselves these days, and I care less) and its various affiliates. Make no mistake: The Three Musketeers have just invited, oh-so-subtly, bin-Laden’s foot soldiers to stage a chemical atrocity in Idlib (God knows how many “various chlorinated organic chemicals” they’ve got on hand there), the resulting pictures of which will duly splash across every television screen in America so as to whip up … well, you’ve heard this song before.
So here’s a new one: a bunch of kids walk onto a school bus in Yemen. As the bus steers through a crowded marketplace, Saudi Arabia drops a bomb on it, killing forty small children and injuring scores more. The bomb is later identified as a “laser-guided” precision missile (precision being the operative word), manufactured by our very own Lockheed Martin, while the mangled school bus is described by Col. Turki al-Maliki, spokesman for the Saudi-led coalition, as a “legitimate target.” Meanwhile, back in illustrious Washington, Pentagon bureaucrat Rebecca Rebarich is asked to comment on the “legitimate” massacre of forty schoolkids.
“The US has worked with the Saudi-led coalition to help them improve procedures and oversight mechanisms to reduce civilian casualties,” she says. “While we do not independently verify claims of civilian casualties in which we are not directly involved, we call on all sides to reduce such casualties, including those caused via ballistic missile attacks on civilian population centers in Saudi Arabia.”
Translated from vapid officialese: “I don’t really give a shit.”
On the bright side, we’re “gravely concerned” about the coming battle for Idlib, where the babies are beautiful and, most importantly, the bombs that kill them are un-American.
Russia rejects Facebook’s allegations of disinformation campaign
RT | August 22, 2018
Russia on Wednesday rejected allegations from Facebook that the country’s GRU military intelligence service had been using the social media site to run disinformation campaigns.
Facebook, Twitter, and Alphabet Inc collectively removed hundreds of accounts tied to an alleged Iranian propaganda operation on Tuesday, while Facebook took down a second campaign it said was linked to Russia, Reuters reports.
According to Kremlin spokesman Dmitry Peskov, Facebook’s Russia-related allegations made no sense to Moscow and said they looked similar to previous groundless allegations from other sources like Microsoft.
“They are all trying to outdo one another with their statements which all look like carbon copies of one another,” the spokesman said. “We do not understand on what they are based,” he said, adding that the allegations lack “supporting explanation.”
Featured Video
Seyed M. Marandi: US-Iran War Inevitable: Kuwait and Bahrain May Fall
or go to
Aletho News Archives – Video-Images
From the Archives
Oil and the Israel Lobby
Reknowned economist M. Shahid Alam offers this excellent critique of Noam Chomsky’s defective analysis of the relative influence of Oil versus the Israel lobby over US foreign policy: … continue
Blog Roll
 Aletho News
- ICC ignored ‘very well-documented’ NATO crimes – ex-Libyan minister
- SNSC secretary dismisses US response to Iran’s conditions as ‘inadequate’
- Sanaa says Taiz roads open, secure for residents, warns Saudi forces
- Iraqi resistance group urges Saudi leadership to admit defeat, lift Yemen siege
- Trump’s Retreat: How Al-Aqsa Flood Took Down the US Empire
- Israel’s Military Actions in Lebanon Grossly Violate International Law — Lavrov
- Seyed M. Marandi: US-Iran War Inevitable: Kuwait and Bahrain May Fall
- Leaders Condemn Ansarallah Attack on Saudi Arabia While Ignoring Illegal War Against Yemen
- Leaked: Britain’s Covert Iraqi Psyops Network
- Yemeni Armed Forces Warn Airlines Against Using Saudi Airports, Exempt Mecca and Medina
- If Americans Knew
- How Israel Conquered the Latin American Right
- Agents search Rep. Omar’s Washington home in criminal probe as she vows she won’t ‘be silenced’
- “The Rule Was: ‘Shoot Everyone You See'”
- Israel goes ballistic over Nobel Laureate Navi Pillay
- U.S. May Join Yet Another Middle Eastern War — TCN
- Yellow Line moves again as Israel closes in on trapped Gazans – Daily Update
- Israeli Attacks Kill Seven Palestinians in Gaza Including Six-year-old Girl
- Gaza: Ceasefire Anniversary Marks Year of Failed Promises
- The American Conservative: Mike Huckabee Should Resign
- A C-Section in Shackles: A Palestinian Woman’s Harrowing Birth in Israeli Detention
- No Tricks Zone
- Germany’s Green Energy Debacle: High Energy Costs Force Kahla Porzellan to Close After 182 Years!
- New Study: 50 Years Of The Most Aggressive ‘Net Zero’ Policies Can Only Affect The Global Climate By 0.03°C
- US September “Heat” Was No Record…Many Records Set Decades Ago
- Latest European Green Energy Debacle; Portugal’s Largest Flagship Solar Park Insolvent!
- Green Energy Debacle: German Expert Professor Fritz Vahrenholt Warns Of Severe Economic And Social Consequences
- Two More Paleo Reconstructions Affirm Meters-Higher Sea Levels Across Ireland, Brazil 7000-6000 Years Ago
- New Study: Earth And Venus Surface Warmth Largely Explained By Convection And Lapse Rate, Not CO2 Or Radiation
- 2025 Nature Paper Claiming Worsening Global Drought Gets RETRACTED …Heavily Flawed
- New Study: ‘Global Drought Shows No Detectable Recent Acceleration Under Climate Warming’
- Economic Masterminds: German Socialists Suggest Taxing Productivity Gains Stemming From Using AI

