How the Pro-War “Left” Fell for the Kurds in Syria
By Max Parry • Unz Review • December 22, 2019
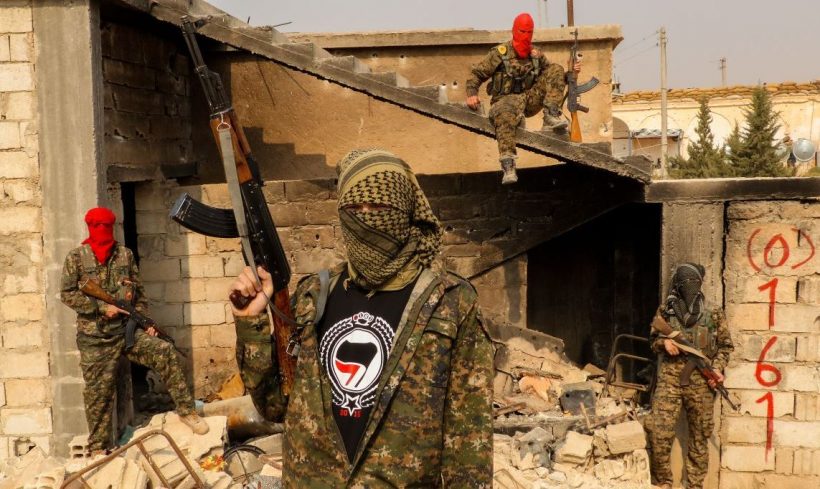
The October decision by U.S. President Donald Trump to withdraw American troops from northeastern Syria did not only precipitate the Turkish offensive, codenamed ‘Operation Peace Spring’, into Kurdish-held territory which followed. It also sparked an outcry of hysteria from much of the so-called “left” that has been deeply divided during the 8-year long conflict over its Kurdish question. Despite the fact that the Syrian Democratic Forces (SDF) were objectively a U.S. proxy army before they were “abandoned” by Washington to face an assault by its NATO ally, the ostensibly “progressive” politics of the mostly-Kurdish militants duped many self-identified people on the left into supporting them as the best option between terrorists and a “regime.” Apparently, everyone on earth except for the Kurds and their ‘humanitarian interventionist’ supporters saw this “betrayal” coming, which speaks to the essential naiveté of such amateurish politics. However, there is a historical basis to this political tendency that should be interrogated if a lesson is to be learned by those misguided by it.
Turkey initially went all-in with the West, Israel, and Gulf states in a joint effort to depose Syrian President Bashar al-Assad by stoking the flames of the country’s Arab Spring in 2011 into a full blown uprising. With Istanbul serving as the base for the opposition, Kurdish nationalists hoping to participate were not at all pleased that the alliance had based its government-in-exile in Turkey and naturally considered Ankara’s role to be detrimental to their own interests in establishing an autonomous ethnonationalist state. Likewise, Turkish President Recep Tayyip Erdoğan did not bargain on the conflict facilitating such a scenario, with the forty year war with the Kurdistan Workers Party (PKK) in southeastern Turkey still ongoing. When the PKK-linked People’s Protection Units (YPG) militias took control of northern Syrian towns and established a self-governing territory after boycotting the opposition, it was done only after negotiations between Damascus and Kurdish leaders. The Syrian government willingly and peacefully ceded the territory to them, just as we were told that the Baathists were among their oppressors.
The Rojava front opened up when the Kurds came under attack from the most radical jihadist militants in the opposition, some of which would later merge with the Islamist insurgency in western Iraq to form ISIS. Yet we now know for a fact that the rise of Islamic State was something actually desired by the U.S.-led coalition in the hopes of bringing down Assad, as revealed in a declassified 2012 Defense Intelligence Agency report. Shortly after clarifying that the opposition is “backed by the West, Gulf countries and Turkey”, the memo states:
“If the situation unravels there is the possibility of establishing a declared or undeclared Salafist principality in eastern Syria (Hasaka and Der Zor), and this is exactly what the supporting powers to the opposition want, in order to isolate the Syrian regime, which is considered the strategic depth of the Shia expansion (Iraq and Iran).”
Meanwhile, it was the Kurds themselves who divulged Ankara’s support for Daesh, frequently retrieving Turkish-issued passports from captured ISIS fighters. Even Emmanuel Macron said as much at the recent NATO summit in London, prompting a row between France and Turkey that took a backseat to the more ‘newsworthy’ Trump tantrum over a hot mic exchange between the French President and his Canadian and British counterparts. Then there was the disclosure that the late Senator John McCain had crossed the border from Turkey into Syria in mid-2013 to meet with leaders of the short-lived Free Syrian Army (FSA), dubbed as “moderate rebels”, which just a short time later would decline after its members joined better armed, more radical groups and the ISIS caliphate was proclaimed. One of the rebel leaders pictured with McCain in his visit is widely suspected to be the eventual chosen leader of ISIS, Abu Bakr al-Baghdadi, who was allegedly killed in a U.S. raid in Idlib this October. Ironically, many of the Turkish-backed FSA militias are now assisting Ankara in its assault on the Kurds while those who supported arming them feign outrage over the US troop removal.
Henry Kissinger reportedly once remarked, “America has no permanent friends or enemies, only interests.” Given that the U.S. was at the very least still using Daesh as a strategic asset, it seems inexplicable that the Kurdish leadership could trust Washington. The SDF had only a few skirmishes with the Syrian army during the entire war— if they wanted to defeat ISIS, why not partner with Damascus and Moscow? To say nothing of the U.S.’s long history of backing their oppression, from its support of Saddam Hussein during the Iran-Iraq War in the 1980s to the arming of Turkey’s brutal crackdown against the PKK which ended with the capture of its cultish leader, Abdullah Öcalan, in 1999. Did they really think after enlisting them for its cosmetic ‘fight’ against ISIS that the U.S. would continue to side with them against Ankara? Even so, Kurdish gains against Daesh would pale in comparison to those by the Syrian army with Russian air support. More perplexing is why anyone on the left would choose to back a group being used as a cat’s paw for imperialism, regardless of whatever ideals they claim to hold.
Perhaps the U.S. would not have reneged on its implicit pledge to help with the foundation of a Kurdish state had their “Assad must go” policy been successful, but the U.S. pullout appears to be the final nail in the coffin for both Washington’s regime change plans in Syria and an independent Kurdistan. The YPG’s makeover as the SDF was done at the behest of the U.S. but this did nothing to to diminish the objections of Ankara (or many ‘leftists’ from supporting them), who insisted the YPG was already an extension and rebranding of the PKK, a group Washington itself designates as a terrorist organization. Any effort to create a buffer state in the enclave was never going to be tolerated by Turkey but it nonetheless enabled the U.S. to illegally occupy northern Syria and facilitate the ongoing looting of its oil. Unfortunately for Washington, the consequence was that it eventually pushed Ankara closer toward the Kremlin, as Turkey went from shooting down Russian jets one year to purchasing the S-400 weapon system from Moscow the next. After backing a botched coup d’etat attempt against Erdoğan in 2016, any hope of Washington bringing Turkey back into its fold would be to discard the Kurds as soon as their usefulness ran out, if it wasn’t too late to repair the damage already.
Why would the U.S. risk losing its geo-strategic alliance with Turkey? To put it simply, it’s ‘special relationship’ with Israel took greater precedence. Any way you slice it, Washington’s foray into the region has been as much about Zionism as imperialism and its backing of the Kurds is no exception. Despite the blowback, the invasion of Iraq and destruction of Libya took two enormous sources of support for the Palestinian resistance off the chessboard. It may have strengthened Iran in the process, but that is all the more reason for the U.S. to sell a regime change attempt in Tehran in the future. Regrettably for Washington, when it tried to do the same in Syria, Russia intervened and emerged as the new peace broker in the Middle East. It comes as no surprise that following the Turkish invasion of northern Syria amid the U.S. withdrawal, the Kurds have finally struck a deal with Damascus and Moscow, a welcome and inevitable development that should have occurred years ago.
One of the main reasons for the Kurds joining the SDF so willingly has the same explanation as to why Washington was prepared to put its relationship with Ankara in jeopardy by supporting them: Israel. The cozy relationship between the Zionist state and the various Kurdish groups centered at the intersection of Turkey, Iran, Iraq and Syria goes back as far as the 1960s, as Jerusalem has consistently used them to undermine its enemies. It is not by chance that their respective interests overlap to a near tee, between the founding of a Kurdish protectorate and the Zionist plan for a ‘Greater Israel’ in the Middle East which includes a balkanization of Syria. Mossad has openly provided the Kurds with training and they have learned much in the ways of the ethnic cleansing of Arabs from the Jewish state in order to carve out a Syrian Kurdistan. One can certainly have sympathy for the Kurds as the largest ethnic group in the world at 40 million people without a state, but the Israel connection runs much deeper than geopolitical interests to the very ideological basis of their militancy which calls all of their stated ideals into question.
The ties between the YPG and the PKK are undeniable, as both groups follow jailed leader Abdullah Öcalan’s teachings which merge Kurdish nationalism with the theories of ‘democratic confederalism’ from the influential Jewish-American anarchist philosopher, Murray Bookchin. While the PKK may have been initially founded as a ‘Marxist-Leninist’ organization in the early 70s, a widespread misconception is that it still follows that aim when its ideology long-ago shifted to that of a self-professed and contradictory ‘libertarian socialism’ theorized by Bookchin who was actually a zealous anti-communist. Not coincidentally, the Western anarchist icon was also an avowed Zionist who often defended Israel’s war crimes and genocide of Palestinians while demonizing its Arab state opponents as the aggressors, including Syria. Scratch an anarchist and a neo-conservative will bleed, every time.
Many on the pseudo-left who have pledged solidarity with the Kurds have attempted to base their reasoning on a historically inaccurate analogy comparing the Syrian conflict with the Spanish Civil War of the 1930s. You would think ISIS would be the obvious first choice for the fascists in the Syrian war, but journalist Robert Mackey of popular “progressive” news site The Intercept even tried to cast the Syrian government as Francisco Franco’s Nationalists in an article comparing the 1937 bombing of Guernica by the Condor Legion to the 2018 chemical attack in Douma which remains in dispute regarding its perpetrator. One wonders if Mackey will retract his absurd comparison now that dozens of inspectors from the Organization for the Prohibition of Chemical Weapons (OPCW) have dissented in emails published by WikiLeaks showing that the OPCW engaged in a cover-up with the Trump administration to pin blame for the attacks on the Syrian government instead of the opposition, but don’t hold your breath.
In this retelling of the Spanish Civil War, the Kurds are generally seen in the role of the Trotskyite Workers’ Party of Marxist Unification (POUM) and the anarchist trade union National Confederation of Labour (CNT). In the midst of the conflict between the Nazi-supported Nationalists and Soviet-backed Republicans that was a prelude to World War II, the mobilization effort of all anti-fascist forces into a unified Popular Front was obstructed by the ultra-left and intransigent POUM and CNT who were then expelled from the coalition for their sectarianism. While the government was still fighting the Francoists, the POUM and CNT then attacked the Republicans but were put down in a failed insurrection. Although this revolt did not directly cause the loyalist defeat, it nevertheless sapped the strength from the Popular Front and smoothed the path for the generalissimo’s victory.
In the years since, Trotskyists have attempted to rewrite history by alleging that a primary historical text documenting the POUM’s sabotage of the Republicans — a 1938 pamphlet by journalist Georges Soria, the Spanish correspondent for the French Communist Party newspaper L’Humanite — is a forgery. On the Marxists Internet Archive website, an ‘editor’s note’ is provided as a preface to the text citing a single quote from Soria with the claim he admitted the work in its entirety was “no more than a fabrication”, but his words are selectively cropped to give that impression. While the author did admit accusations that the POUM‘s leadership were literal agents of Franco were a sensationalized exaggeration, the source of the full quote states the following:
“On the one hand, the charge that the leaders of POUM, among them Andrés Nin, ‘were agents of the Gestapo and Franco’, was no more than a fabrication because it was impossible to adduce the slightest evidence. On the other hand, although the leaders of POUM were neither agents of Franco or agents of the Gestapo, it is true that their relentless struggle against the Popular Front played the game nolens volens (like it or not/willingly or unwillingly) of the Caudillo (General Franco).”
In other words, Soria did not say the whole work was counterfeit like the editor’s note misleadingly suggests and reiterated that the POUM’s subversion helped Franco. (The Marxists Internet Archive does not hide its pro-Trotsky bias in its FAQ section.)
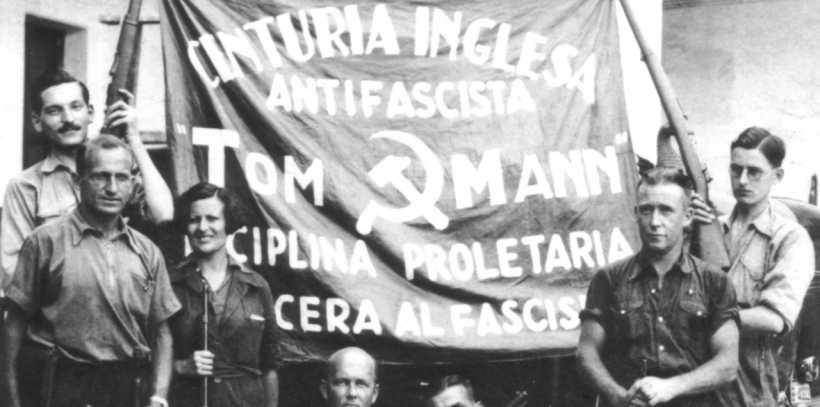
Marxist historian Eric Hobsbawm summarized the inherent contradictions of the Spanish Civil War and the role ultra-leftism played in the demise of the Republic in one of his later essays:
“Of course, the posthumous polemics about the Spanish war are legitimate, and indeed essential — but only if we separate out debate on real issues from the parti pris of political sectarianism, cold-war propaganda and pure ignorance of a forgotten past. The major question at issue in the Spanish civil war was, and remains, how social revolution and war were related on the republican side. The Spanish civil war was, or began as, both. It was a war born of the resistance of a legitimate government, with the help of a popular mobilisation, against a partially successful military coup; and, in important parts of Spain, the spontaneous transformation of the mobilisation into a social revolution. A serious war conducted by a government requires structure, discipline and a degree of centralisation. What characterises social revolutions like that of 1936 is local initiative, spontaneity, independence of, or even resistance to, higher authority — this was especially so given the unique strength of anarchism in Spain.”
Murray Bookchin also wrote at length about the Spanish Civil War but celebrated the decentralized anarchist tactics which incapacitated the Popular Front. The anarcho-syndicalist theorist championed the ‘civil war within the civil war’ as a successful example of his antithetical vision of ‘libertarian socialism’, while his emphasis on the individualist aspects of the former half of his oxymoronic and anti-statist theory often bears a striking resemblance to neoliberal talking points about self-regulating free markets. This would explain why he actually regarded right-wing libertarians to be his natural allies over the the socialist left, whom he considered ‘totalitarian’ as he told the libertarian publication Reason magazine in an interview in 1979. His reactionary demonization of the Soviet Union and dismissal of the accomplishments of all other socialist revolutions was recalled by Michael Parenti in Blackshirts and Reds:
“Left anticommunists remained studiously unimpressed by the dramatic gains won by masses of previously impoverished people under communism. Some were even scornful of such accomplishments. I recall how in Burlington Vermont, in 1971, the noted anticommunist anarchist, Murray Bookchin, derisively referred to my concern for “the poor little children who got fed under communism” (his words).”
Like the International Brigades consisting of foreign volunteers to assist the Spanish Republic in the 1930s, there is an ‘International Freedom Battalion’ currently fighting with the Kurds in Syria. Unfortunately, its live-action role playing ‘leftist’ mercenaries missed the part about the original International Brigades having been backed by the Comintern, not the U.S. military.
Meanwhile, Western media usually hostile to any semblance of radical politics have heavily promoted the Rojava federation as a feminist ‘direct democracy’ utopia, particularly giving excessive attention to the all-female Women’s Protection Units (YPJ) militia while ignoring the female regiments fighting for the secular Syrian government. As a result of the media’s exoticized portrayal of the Kurds and their endorsement by prominent misleaders on the left, from Slavoj Žižek to Noam Chomsky, many have been fooled into supporting them.
If the Spanish Civil War was a dress rehearsal for WWII, it remains to be seen if Syria proves to be a run-through for another global conflict. Then again, what has emerged from its climax is an increasingly multipolar world with the resurgence of Moscow as a deterrent to the mutually assured destruction between the U.S. and China.
Leftists today wishing to continue the legacy of those who fought for the Spanish Republic should have thrown their support behind the Syrian patriots bravely defending their country from terrorism and imperialism, not left opportunism. Thankfully, this time the good guys have prevailed while the Kurds have paid the price for betraying their fellow countrymen. Liberals shedding crocodile tears about Rojava should take comfort in the fact that they can always play the latest Call of Duty: Modern Warfare video game featuring the YPG fighting alongside the U.S. military if they need to fulfill their imperial fantasies.
Yes, that’s right, the latest installment of the popular first-person shooter franchise features a storyline inspired by the SDF. It’s too bad for them that in real life all of Syria will be returned to where it rightfully belongs under the Syrian Arab Republic.
Max Parry is an independent journalist and geopolitical analyst. His writing has appeared widely in alternative media. Max may be reached at maxrparry@live.com
NSA has been ‘lying to the courts all along,’ says whistleblower, as judges give warrantless surveillance the thumbs-up
National Security Agency (NSA) headquarters in Ft. Meade, Maryland © Reuters / Larry Downing
RT | December 21, 2019
The National Security Agency can gather the data of US citizens without a warrant – as long as it gathers this data by mistake, a court has ruled. However, this suits the agency just fine, whistleblower William Binney told RT.
The NSA is permitted to gather data on US citizens abroad, or “foreign connected” Americans at home. The dragnet surveillance operation necessary to gather this information also sucks up data on millions of Americans with no foreign contacts, a process critics say is unconstitutional.
On Wednesday, the 2nd Court of Appeals in New York declared this “incidental collection” of information permissible. The NSA has maintained that it is incapable of separating properly and improperly gathered data, but former NSA Technical Director William Binney told RT that this is simply untrue.
“They’ve been lying to the courts all along,” Binney said. “They’ve had the capability to sort that stuff out. It’s just that they don’t want to.”
“This gives them power over everyone, the ability to look into political opponents like they did with President Trump,” he continued.
While the court ruling gives the NSA free rein to suck up data on Americans’ phone and internet communications, it did not authorize the US’ other intelligence and law enforcement agencies to dig through this data. However, according to a Foreign Intelligence Surveillance Act (FISA) court ruling issued last year, the FBI accessed this data trove some 3.1 million times in 2017.
US State Department ‘firmly opposes’ ICC probe into Israeli war crimes allegations, insisting court lacks jurisdiction
RT | December 21, 2019
US Secretary of State Mike Pompeo has voiced “firm” opposition to a bid in the International Criminal Court (ICC) to investigate alleged war crimes committed by Israel in the occupied Palestinian territories.
After nearly four years of preliminary investigation, the ICC’s top prosecutor Fatou Bensouda said on Friday that the war crimes probe would be expanded into a full-scale inquiry, looking into whether Israel has carried out atrocities in the occupied West Bank and East Jerusalem, as well as Gaza. In a statement echoing earlier remarks by Israeli Prime Minister Benjamin Netanyahu, Pompeo said the case had no merit.
“We firmly oppose this and any other action that seeks to target Israel unfairly,” Pompeo said on Friday, arguing that because Palestine does not qualify as a “sovereign state” and is not a party to the ICC’s founding charter, the Rome Statute, it cannot bring cases before the court.
The top US diplomat also reiterated a “long standing objection” to any claim that the ICC has jurisdiction over non-member states, such as Israel and the United States, “absent a referral from the UN Security Council” or explicit cooperation from the nation in question. While then-President Bill Clinton signed the Rome Statute in 2000, it was never formally ratified by the Senate. Israel, too, was an early signer to the statute, but also never finalized its membership in the organization.
PM Netanyahu made a nearly identical argument to Pompeo’s earlier on Friday, insisting the court had no jurisdiction and that Palestine had not achieved statehood – a goal Palestinians have pursued for decades despite tooth-and-nail opposition from both Tel Aviv and its American benefactor.
While Palestine has yet to achieve statehood, the quasi-governmental Palestinian Authority was accepted into the ICC in 2015. Nonetheless, Bensouda signaled that she will convene with the court to confirm exactly how far its jurisdiction extends before moving ahead with the investigation.
Tel Aviv has been accused repeatedly over the years of carrying out war crimes against Palestinians, including the demolition and shelling of civilian homes and other structures, forcible relocation of residents and the use of live ammunition on unarmed demonstrators. Many of the allegations stem from Israel’s settlement project in the occupied territories.
In November, Pompeo declared that Israeli settlements in the occupied West Bank were legitimate under international law, overturning long-standing US policy on the question. Palestinians and their advocates argue the settlements make the long-sought statehood project increasingly unlikely, as Israel’s Jewish-only housing units sprawl across Palestinian land and tie up important resources. Much of the international community and the UN have long considered the settlements illegal and continue to do so, despite the American about-face.
Did John Brennan’s CIA Create Guccifer 2.0 and DCLeaks?
By Larry C Johnson | Sic Semper Tyrannis | December 20, 2019
Special Counsel Robert Mueller’s report insists that Guccifer 2.0 and DCLeaks were created by Russia’s military intelligence organization, the GRU, as part of a Russian plot to meddle in the U.S. 2016 Presidential Election. But this is a lie. Guccifer 2.0 and DCLeaks were created by Brennan’s CIA and this action by the CIA should be a target of U.S. Attorney John Durham’s investigation. Let me explain why.
Let us start with the January 2017 Intelligence Community Assessment aka ICA. Only three agencies of the 17 in the U.S. intelligence community contributed to and coordinated on the ICA–the FBI, the CIA and NSA. In the preamble to the ICA, you can read the following explanation about methodology:
When Intelligence Community analysts use words such as “we assess” or “we judge,” they are conveying an analytic assessment or judgment
To be clear, the phrase,“We assess”, is intel community jargon for “opinion”. If there was actual evidence or source material for a judgment the writer of the assessment would state, “According to a reliable source” or “knowledgeable source” or “documentary evidence.”
Pay close attention to what the analysts writing the ICA stated about the GRU and Guccifer 2.0 and DCLeaks:
We assess with high confidence that the GRU used the Guccifer 2.0 persona, DCLeaks.com, and WikiLeaks to release US victim data obtained in cyber operations publicly and in exclusives to media outlets.
- Guccifer 2.0, who claimed to be an independent Romanian hacker, made multiple contradictory statements and false claims about his likely Russian identity throughout the election. Press reporting suggests more than one person claiming to be Guccifer 2.0 interacted with journalists.
- Content that we assess was taken from e-mail accounts targeted by the GRU in March 2016 appeared on DCLeaks.com starting in June.
We assess with high confidence that the GRU relayed material it acquired from the DNC and senior Democratic officials to WikiLeaks. Moscow most likely chose WikiLeaks because of its self-proclaimed reputation for authenticity. Disclosures through WikiLeaks did not contain any evident forgeries.
Not one piece of corroborating intelligence. It is all based on opinion and strong belief. There was no human source report or electronic intercept pointing to a relationship between the GRU and the two alleged creations of the GRU–Guccifer 2.0 persona and DCLeaks.com.
Now consider the spin that Robert Mueller put on this opinion in his report on possible collusion between the Trump campaign and the Russians. Mueller bluffs the unsuspecting reader into believing that it is a proven fact that Guccifer 2.0 and DCLeaks were Russian assets. But he is relying on a mere opinion from a handpicked group of intel analysts working under the direction of then CIA Director John Brennan.Here’s Mueller’s take (I apologize for the lengthy quote but it is important that you read how the Mueller team presents this):
DCLeaks
“The GRU began planning the releases at least as early as April 19, 2016, when Unit 26165 registered the domain dcleaks.com through a service that anonymized the registrant.137 Unit 26165 paid for the registration using a pool of bitcoin that it had mined.138 The dcleaks.com landing page pointed to different tranches of stolen documents, arranged by victim or subject matter. Other dcleaks.com pages contained indexes of the stolen emails that were being released (bearing the sender, recipient, and date of the email). To control access and the timing of releases, pages were sometimes password-protected for a period of time and later made unrestricted to the public.
Starting in June 2016, the GRU posted stolen documents onto the website dcleaks.com, including documents stolen from a number of individuals associated with the Clinton Campaign. These documents appeared to have originated from personal email accounts (in particular, Google and Microsoft accounts), rather than the DNC and DCCC computer networks. DCLeaks victims included an advisor to the Clinton Campaign, a former DNC employee and Clinton Campaign employee, and four other campaign volunteers.139 The GRU released through dcleaks.com thousands of documents, including personal identifying and financial information, internal correspondence related to the“Clinton Campaign and prior political jobs, and fundraising files and information.140
GRU officers operated a Facebook page under the DCLeaks moniker, which they primarily used to promote releases of materials.141 The Facebook page was administered through a small number of preexisting GRU-controlled Facebook accounts.142
GRU officers also used the DCLeaks Facebook account, the Twitter account @dcleaks__, and the email account dcleaksproject@gmail.com to communicate privately with reporters and other U.S. persons. GRU officers using the DCLeaks persona gave certain reporters early access to archives of leaked files by sending them links and passwords to pages on the dcleaks.com website that had not yet become public. For example, on July 14, 2016, GRU officers operating under the DCLeaks persona sent a link and password for a non-public DCLeaks webpage to a U.S. reporter via the Facebook account.143 Similarly, on September 14, 2016, GRU officers sent reporters Twitter direct messages from @dcleaks_, with a password to another non-public part of the dcleaks.com website.144
The dcleaks.com website remained operational and public until March 2017.”
Guccifer 2.0
On June 14, 2016, the DNC and its cyber-response team announced the breach of the DNC network and suspected theft of DNC documents. In the statements, the cyber-response team alleged that Russian state-sponsored actors (which they referred to as “Fancy Bear”) were responsible for the breach.145 Apparently in response to that announcement, on June 15, 2016, GRU officers using the persona Guccifer 2.0 created a WordPress blog. In the hours leading up to the launch of that WordPress blog, GRU officers logged into a Moscow-based server used and managed by Unit 74455 and searched for a number of specific words and phrases in English, including “some hundred sheets,” “illuminati,” and “worldwide known.” Approximately two hours after the last of those searches, Guccifer 2.0 published its first post, attributing the DNC server hack to a lone Romanian hacker and using several of the unique English words and phrases that the GRU officers had searched for that day.146
That same day, June 15, 2016, the GRU also used the Guccifer 2.0 WordPress blog to begin releasing to the public documents stolen from the DNC and DCCC computer networks.
The Guccifer 2.0 persona ultimately released thousands of documents stolen from the DNC and DCCC in a series of blog posts between June 15, 2016 and October 18, 2016.147 Released documents included opposition research performed by the DNC (including a memorandum analyzing potential criticisms of candidate Trump), internal policy documents (such as recommendations on how to address politically sensitive issues), analyses of specific congressional races, and fundraising documents. Releases were organized around thematic issues, such as specific states (e.g., Florida and Pennsylvania) that were perceived as competitive in the 2016 U.S. presidential election.
Beginning in late June 2016, the GRU also used the Guccifer 2.0 persona to release documents directly to reporters and other interested individuals. Specifically, on June 27, 2016, Guccifer 2.0 sent an email to the news outlet The Smoking Gun offering to provide “exclusive access to some leaked emails linked [to] Hillary Clinton’s staff.”148 The GRU later sent the reporter a password and link to a locked portion of the dcleaks.com website that contained an archive of emails stolen by Unit 26165 from a Clinton Campaign volunteer in March 2016.149 “That the Guccifer 2.0 persona provided reporters access to a restricted portion of the DCLeaks website tends to indicate that both personas were operated by the same or a closely-related group of people.150
The GRU continued its release efforts through Guccifer 2.0 into August 2016. For example, on August 15, 2016, the Guccifer 2.0 persona sent a candidate for the U.S. Congress documents related to the candidate’s opponent.151 On August 22, 2016, the Guccifer 2.0 persona transferred approximately 2.5 gigabytes of Florida-related data stolen from the DCCC to a U.S. blogger covering Florida politics.152 On August 22, 2016, the Guccifer 2.0 persona sent a U.S. reporter documents stolen from the DCCC pertaining to the Black Lives Matter movement.153”
Wow. Sounds pretty convincing. The documents referencing communications by DCLeaks or Guccifer 2.0 with Wikileaks are real. What is not true is that these entities were GRU assets.
In October 2015 John Brennan reorganized the CIA. As part of that reorganization he created a new directorate–DIRECTORATE OF DIGITAL INNOVATION. Its mission was to “manipulate digital footprints.” In other words, this was the Directorate that did the work of creating Guccifer 2.0 and DCLeaks. One of their specialties, creating Digital Dust.
We also know, thanks to Wikileaks, that the CIA was using software specifically designed to mask CIA activity and make it appear like it was done by a foreign entity. Wikipedia describes the Vault 7 documents:
Vault 7 is a series of documents that WikiLeaks began to publish on 7 March 2017, that detail activities and capabilities of the United States’ Central Intelligence Agency to perform electronic surveillance and cyber warfare. The files, dated from 2013–2016, include details on the agency’s software capabilities, such as the ability to compromise cars, smart TVs,[1] web browsers (including Google Chrome, Microsoft Edge, Mozilla Firefox, and Opera Software ASA),[2][3][4] and the operating systems of most smartphones (including Apple’s iOS and Google’s Android), as well as other operating systems such as Microsoft Windows, macOS, and Linux[5][6
One of the tools in Vault 7 carries the innocuous name, MARBLE. Hackernews explains the purpose and function of MARBLE:
Dubbed “Marble,” the part 3 of CIA files contains 676 source code files of a secret anti-forensic Marble Framework, which is basically an obfuscator or a packer used to hide the true source of CIA malware.
The CIA’s Marble Framework tool includes a variety of different algorithm with foreign language text intentionally inserted into the malware source code to fool security analysts and falsely attribute attacks to the wrong nation.Marble is used to hamper[ing] forensic investigators and anti-virus companies from attributing viruses, trojans and hacking attacks to the CIA,” says the whistleblowing site.
“… for example by pretending that the spoken language of the malware creator was not American English, but Chinese, but then showing attempts to conceal the use of Chinese, drawing forensic investigators even more strongly to the wrong conclusion,” WikiLeaks explains.
So guess what gullible techies “discovered” in mid-June 2016? The meta data in the Guccifer 2.0 communications had “Russian fingerprints.”
We still don’t know who he is or whether he works for the Russian government, but one thing is for sure: Guccifer 2.0—the nom de guerre of the person claiming he hacked the Democratic National Committee and published hundreds of pages that appeared to prove it—left behind fingerprints implicating a Russian-speaking person with a nostalgia for the country’s lost Soviet era.
Exhibit A in the case is this document created and later edited in the ubiquitous Microsoft Word format. Metadata left inside the file shows it was last edited by someone using the computer name “Феликс Эдмундович.” That means the computer was configured to use the Russian language and that it was connected to a Russian-language keyboard. More intriguing still, “Феликс Эдмундович” is the colloquial name that translates to Felix Dzerzhinsky, the 20th Century Russian statesman who is best known for founding the Soviet secret police. (The metadata also shows that the purported DNC strategy memo was originally created by someone named Warren Flood, which happens to be the name of a LinkedIn user claiming to provide strategy and data analytics services to Democratic candidates.)
Just use your common sense. If the Russians were really trying to carry out a covert cyberattack, do you really think they are so sloppy and incompetent to insert the name of the creator of the Soviet secret police in the metadata? No. The Russians are not clowns. This was a clumsy attempt to frame the Russians.
Why would the CIA do this? The CIA knew that Podesta’s emails had been hacked and were circulating on the internet. But they had no evidence about the identity of the culprit. If they had such evidence, they would have cited it in the 2017 ICA.
The U.S. intelligence community became aware around May 26, 2016 that someone with access to the DNC network was offering those emails to Julian Assange and Wikileaks. Julian Assange and people who spoke to him indicate that the person was Seth Rich. Whether or not it was Seth, the Trump Task Force at CIA was aware that the emails, which would be embarrassing to the Clinton campaign, would be released at some time in the future. Hence the motive to create Guccifer 2.0 and pin the blame on Russia.
It is essential to recall the timeline of the alleged Russian intrusion into the DNC network. The only source for the claim that Russia hacked the DNC is a private cyber security firm, CrowdStrike. Here is the timeline for the DNC “hack.”
Here are the facts on the public record. They are at odds with the claims of the Intelligence Community:
- It was 29 April 2016, when the DNC claims it became aware its servers had been penetrated. No claim yet about who was responsible. And no claim that there had been a prior warning by the FBI of a penetration of the DNC by Russian military intelligence.
- According to CrowdStrike founder, Dimitri Alperovitch, his company first supposedly detected the Russians mucking around inside the DNC server on 6 May 2016. A CrowdStrike intelligence analyst reportedly told Alperovitch that:
- Falcon had identified not one but two Russian intruders: Cozy Bear, a group CrowdStrike’s experts believed was affiliated with the FSB, Russia’s answer to the CIA; and Fancy Bear, which they had linked to the GRU, Russian military intelligence.
- The Wikileaks data shows that the last message copied from the DNC network is dated Wed, 25 May 2016 08:48:35.
- 10 June 2016–CrowdStrike waited until 10 June 2016 to take concrete steps to clean up the DNC network. Alperovitch told Esquire’s Vicky Ward that: ‘Ultimately, the teams decided it was necessary to replace the software on every computer at the DNC. Until the network was clean, secrecy was vital. On the afternoon of Friday, June 10, all DNC employees were instructed to leave their laptops in the office.”
- On June 14, 2016, Ellen Nakamura, a Washington Post reporter who had been briefed by computer security company hired by the DNC—Crowdstrike–, wrote:
- Russian government hackers penetrated the computer network of the Democratic National Committee and gained access to the entire database of opposition research on GOP presidential candidate Donald Trump, according to committee officials and security experts who responded to the breach.
- The intruders so thoroughly compromised the DNC’s system that they also were able to read all email and chat traffic, said DNC officials and the security experts.
- The intrusion into the DNC was one of several targeting American political organizations. The networks of presidential candidates Hillary Clinton and Donald Trump were also targeted by Russian spies, as were the computers of some Republican political action committees, U.S. officials said. But details on those cases were not available.
- 15 June, 2016, an internet “personality” self-described as Guccifer 2.0 surfaces and claims to be responsible for the hacks but denies being Russian. The people/entity behind Guccifer 2.0:
- Used a Russian VPN service provider to conceal their identity.
- Created an email account with AOL.fr (a service that exposes the sender’s IP address) and contacted the press (exposing his VPN IP address in the process).
- Contacted various media outlets through this set up and claimed credit for hacking the DNC, sharing copies of files purportedly from the hack (one of which had Russian error messages embedded in them) with reporters from Gawker, The Smoking Gun and other outlets.
- Carried out searches for terms that were mostly in English, several of which would appear in Guccifer 2.0’s first blog post. They chose to do this via a server based in Moscow. (this is from the indictment,
“On or about June 15, 2016, the Conspirators logged into a Moscow-based server used and managed by Unit 74455”) - Created a blog and made an initial blog post claiming to have hacked the DNC, providing links to various documents as proof.
- Carelessly dropped a “Russian Smiley” into his first blog post.
- Managed to add the name “Феликс Эдмундович” (which translates to Felix Dzerzhinsky, also known as “Iron Felix”) to the metadata of several documents. (Several sources went beyond what the evidence shows and made claims about Guccifer 2.0 using a Russian keyboard, however, these claims are just assumptions made in response to the presence of cyrillic characters.)
The only thing that the Guccifer 2.0 character did not do to declare its Russian heritage was to take out full page ads in the New York Times and Washington Post. But the “forensic” fingerprints that Guccifer 2.0 was leaving behind is not the only inexplicable event.
Time for the common sense standard again. Crowdstrike detected the Russians on the 6th of May, according to CEO Dimitri Alperovitch, but took no steps to shutdown the network, eliminate the malware and clean the computers until 34 days later, i.e., the 10th of June. That is 34 days of inexcusable inaction.
It is only AFTER Julian Assange announces on 12 June 2016 that WikiLeaks has emails relating to Hillary Clinton that DCLeaks or Guccifer 2.0 try to contact Assange.
The actions attributed to DCLeaks and Guccifer 2.0 should be priority investigative targets for U.S. Attorney John Durham’s team of investigators. This potential use of a known CIA tool, developed under Brennan with the sole purpose to obfuscate the source of intrusions, pointing to another nation, as a false flag operation, is one of the actions and issues that U.S. Attorney John Durham should be looking into as a potential act of “Seditious conspiracy. It needs to be done. To quote the CIA, I strongly assess that the only intelligence agency that evidence indicates was meddling via cyber attacks in the 2016 Presidential election was the CIA, not the GRU.
Panama: A Grieving People Recalls 30 Years of the US Invasion
teleSUR | December 20, 2019
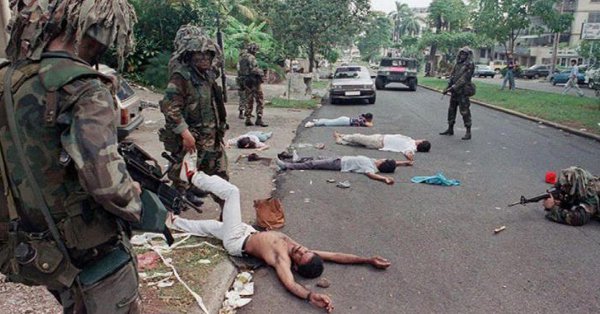
For the first time over the last 30 years, Panamanian authorities agreed to declare “National Day of Mourning” on December 20, which is the date on which the United States invaded Panama in 1989.
“The government acknowledges declaring December 20 as a day of national mourning to honor Panamanians and all the innocents who lost their lives and defended our territory’s integrity,” President Laurentino Cortizo tweeted on Wednesday.
On Dec. 20, 1989, President George H.W. Bush ordered “Operation Just Cause” and deployed some 26,000 soldiers to overthrow General Manuel Antonio Noriega.
Until then, he had been one of the most faithful collaborators of the Central Intelligence Agency (CIA) and the Drug Enforcement Administration (DEA).
Noriega fueled the Bush administration’s hostility when he requested the closure of “The School of the Americas,” where the U.S. had trained thousands of Latin American military since 1946. Upon losing Washington’s support, however, the U.S. Department of Justice accused him of drug trafficking.
Official declassified documents, which were published by Panama Files for the first time this week, indicate that 202 civilians and 314 militaries were killed during Operation Just Cause.
In an unofficially recognized manner, historians, activists, and families argue that the U.S. invasion killed up to 4,000 civilians.
“El Chorillo neighborhood, where the Panamanian Defense Forces central headquarters were located, was razed during the battle,” local outlet El Siglo recalls.
Mirta Guevara, who was a Public Prosecutor at the time, remembers that nobody imagined what the U.S. was planning to do. She was studying court records on the night of December 19 when her husband came in and told her, “Close those files. They are going to invade us.”
“I was shocked because, although one sees such things at the movies, I had never imagined it. I think that no Panamanian imagined that they were going to invade us,” Guevara recalls and now says that such an action had no justification. “Many people died.”
Of what happened in Panama not only oral accounts remained. A year after the invasion, a documentary showed a woman who asked the U.S.-imposed government to recognize whether what happened was “war, invasion or liberation.” They replied to her that it was a “government of democracy and justice.”
“Democracy for whom? Justice for whom? For those who are in the mass graves or for those who are in the government? For those of us who go hungry or for those who have everything?” the woman said without fear of the repression that was lived in the country.
In another documentary called “Unjust Cause,” which was made by the Panamanian filmmaker Rafael Vergara, scenes of brutal aggression are reported, one of which happened when U.S. troops bombarded a civil building because their inhabitants did not want to leave.
To resist the invasion, the Panamanians organized themselves in the “Battalions of Dignity”, which were groups of guerrilla fighters who were persecuted by the invasion-born government, which was led by Guillermo Endara, to whom a judge gave the presidency secretly the night before the invasion.
“Those who seized power mounted on the invading tanks remain silent,” a witness told Prensa Latina.
“After 30 years, the curtains, which hid the worst massacre experienced by Panama and the largest U.S. military deployment after Vietnam, begin to fall.”
In his chronicle “The Panama Invasion: A Heroine of the Little Hiroshima,” Colombian journalist Hernando Calvo described what happened in El Chorrillo neighborhood through the testimony of Ana.
She recalled a Dantesque scenario in which invading troops prevented helping injured family members, tanks hit dead or alive people lying on the street, and flamethrowers burned dead bodies at the beach.
Turkey vows to retaliate if US imposes sanctions on Russian gas pipeline
RT | December 20, 2019
Turkish President Recep Tayyip Erdogan has hit back against US threats to impose sanctions on the TurkStream pipeline that is set to deliver Russian gas to Turkey and further to southern and southeastern Europe starting next year.
“Now they [the US] say ‘we will impose sanctions on TurkStream,’” Erdogan told reporters on Friday in Malaysia. “This is a complete violation of our rights,” he said, adding that Ankara would retaliate against such a step.
The TurkStream project was created as an alternative to the South Stream pipeline. The project to deliver Russian gas to southern Europe was blocked by Bulgaria in 2014 under pressure from the US.
TurkStream is a two-string pipeline that will go from Russia along the bottom of the Black Sea to the European part of Turkey and will have a throughput capacity of 31.5 billion cubic meters. The official launch of the pipeline is scheduled for January 8, when Russian President Vladimir Putin comes to Turkey to met Erdogan.
Earlier this week, the US Senate adopted the 2020 National Defense Authorization Act, which stipulates sanctioning vessels that engaged in pipe-laying for the TurkStream project as well as punitive measures against companies working to complete the Nord Stream 2 natural gas pipeline from Russia to Germany. The bill is now on the way to the White House where President Donald Trump is set to sign it into law.
The bill also sanctions Turkey for its acquisition of the Russian-made S-400 air defense system and implies prohibiting the transfer of F-35 jets to the country. Addressing the matter, the Turkish leader said these issues are “closed” and warned against treating Ankara as a “tribal nation.”
Inside Journalist Tareq Haddad’s Spectacular Departure from Newsweek

A photo of Tareq Haddad is shown from his Twitter profile: @Tareq_Haddad
By Alan Macleod | MintPress News | December 20, 2019
It’s Manufacturing Consent meets Operation Mockingbird; in a long exposé essay that doubles as a goodbye to the profession, Newsweek journalist Tareq Haddad explained why he was very publicly quitting his job at the New York-based magazine. “Journalism is quickly dying. America is regressing because it lacks the truth,” he wrote.
The trigger for his decision was management suppressing his story on the bombshell news that the Organization for the Prohibition of Chemical Weapons (OPCW) hid a mountain of evidence suggesting the 2018 Douma Attack was staged, thus paving the way for more military intervention in Syria. But below the surface, it was about far more than that; Haddad’s essay described how journalists are worked to the bone and how media drives the public towards war, coordinating smears against politicians who stand against it. But most spectacularly of all, he alleges that there is a network of hundreds of government assets working as high-level editors in newsrooms across America, even naming the one at Newsweek.
Haddad knew the consequences of speaking out:
In the end, that decision was rather simple, all be it I understand the cost to me will be undesirable. I will be unemployed, struggle to finance myself and will likely not find another position in the industry I care about so passionately. If I am a little lucky, I will be smeared as a conspiracy theorist, maybe an Assad apologist or even a Russian asset—the latest farcical slur of the day,” he wrote.
MintPress News reached out to him for comment. He responded that he was certain that there were more capable and well-meaning reporters like him that could come forward. “Hopefully, those journalists will have the courage to push the issue with their editors or face the embarrassment the industry will experience when the truth of the matter is revealed to all,” he stated.
Newsweek was not alone in failing to report on the OPCW revelations. Virtually the entirety of the mainstream press (with the exception of Tucker Carlson) ignored or downplayed the findings that cast the Syrian Civil War in a considerably different light. In contrast, MintPress News, with a tiny budget compared to corporate media, has covered the story closely. Unsurprisingly, they have shown little interest in Haddad’s exposé of their corruption either.
“In any functioning democracy the Tareq Haddad affair should occupy mainstream media for weeks” Oliver Boyd-Barrett, Professor Emeritus of Bowling Green State University (Department of Journalism and Communications) told MintPress News. However, he noted, “We have neither a fully functioning democracy nor the uncontaminated information ecosystem that would enable such a thing.” Newsweek, for the record, claimed that the matter was much more mundane: “The writer pitched a conspiracy theory rather than an idea for objective reporting. Editors rejected the pitch,” it said in a statement.
The “conspiracy theory” referenced is that multiple whistleblowers have come forward to publicly accuse the OPCW of suppressing their evidence in order to reach a predetermined conclusion about the Douma attacks– one that supported military intervention. On the new evidence, former head of the OPCW Dr. Jose Bustani said it “confirmed doubts and suspicions I already had” about the incoherent report, claiming that “the picture is clearer now, although very disturbing.”
Truth, Haddad wrote, is “the most fundamental pillar of this modern society we so often take for granted,” claiming that, despite going into the profession after reading radical critiques of the media like Herman and Chomsky’s Manufacturing Consent, and knowing others (like Chris Hedges) had been fired for opposing war, “I believed that honest journalism could be done. Nothing I read, however, came close to the dishonesty and deception I experienced while at Newsweek.”
He spoke of constantly self-censoring and modifying his language as to not rock the boat and how staff were totally overworked. Haddad himself wrote an average of four articles per day on complicated topics he admitted he often had no experience with whatsoever. This is a phenomenon called “churnalism” by academics, where reporters are turned into cogs in giant news machines, churning out vapid and shallow writing or copying corporate press releases for the profit of the outlet. This is one reason why trust in media has been falling since the 1970s, and particularly in the last few years.
He also discusses how the media manufactured public consent for military intervention in Syria. One example of this was his boss’s refusal to publish another of his stories questioning the legitimacy of Bana Alabed, the youthful face of the pro-intervention movement. Meanwhile, those who stand up against war are smeared as assets of foreign powers. He condemns what he describes as coordinated attacks launching “preposterous accusations” against antiwar voices such as Hawaii Congresswoman Tulsi Gabbard.
Academics found the case remarkable, but not particularly unusual. When asked for comment by MintPress News, Tabe Bergman, Lecturer in Journalism at Xi’an Jiaotong-Liverpool University, Suzhou, China replied,
“Sadly, the resignation of Tareq Haddad is merely the latest in a long series of dedicated journalists quitting their job at mainstream news organizations that try to squeeze every penny out of the ‘news product’ while placating the powers that be.”
Operation Mockingbird 2.0
Perhaps the most truly alarming claim Haddad makes in his tell-all treatise is that there is a network of hundreds of deep state assets placed into newsrooms across the country, working to control what the public sees and hears, planting stories and quashing others. As he says:
“The U.S. government, in an ugly alliance with those that profit the most from war, has its tentacles in every part of the media — imposters, with ties to the U.S. State Department, sit in newsrooms all over the world. Editors, with no apparent connections to the member’s club, have done nothing to resist. Together, they filter out what can or cannot be reported. Inconvenient stories are completely blocked.”
Dr. Boyd-Barrett compared his revelations to Operation Mockingbird, a widespread CIA infiltration of hundreds of agenda-setting news outlets throughout the United States during the 20th century, placing agents in key positions or persuading existing reporters to work with them. “The use of journalists has been among the most productive means of intelligence‑gathering employed by the CIA,” wrote the legendary investigative journalist Carl Bernstein, who broke the story for Rolling Stone in 1977. As such, Boyd-Barrett told us there is “nothing essentially new” with Haddad’s exposé:
“Discerning critics have long assumed the wholesale penetration of our media ecosystem and universities by intelligence agencies and other special interests and every so often something emerges accidentally to confirm their worst fears.”
While initially fearing he might never work in the profession again, Haddad said that he is still weighing his options and is considering crowdfunding as a model to finance new investigations as an independent journalist.
“There are numerous stories that haven’t had the attention they deserve in the mainstream press and they are well worth investigating further. Also, it’s worth noting that because of my initial piece, several journalists have reached out to me with information I wasn’t previously aware of so there are several threads to be investigated more,” he revealed.
Haddad’s exposé of the corruption and collusion at the heart of modern journalism is something long-discussed by academics such as Bergman and Boyd-Barrett, but rarely does such a clear example present itself. His account undermines the credibility of the entire for-profit corporate model of news that prevails across the world, precisely the reason why you are unlikely to hear about it on CNN or in the New York Times.
Alan MacLeod is a MintPress Staff Writer as well as an academic and writer for Fairness and Accuracy in Reporting. His book, Bad News From Venezuela: Twenty Years of Fake News and Misreporting was published in April.
The 12 Strongest Arguments That Douma Was A False Flag
By Caitlyn Johnstone | December 20, 2019
There have been many US military interventions that were based on lies. This is not a conspiracy theory. It is not some kooky blogger’s opinion. It is an extensively documented and indisputable fact.
Nothing has ever been done to address this extensively documented and indisputable fact. No laws were ever changed. No war crimes tribunals were ever held. No policies or procedures were ever revised. No one was ever even fired. No changes were implemented to prevent the Iraq deception from happening again, and, when it happened again, no changes were implemented to prevent the Libya deception from happening again.
When you make a mistake, you take measures afterward to ensure that you never make the same mistake again. When you do something on purpose, and you intend on doing it again, you do not take any such measures.
There is a large and growing body of evidence that we have been lied to about Syria to an extent and to a level of sophistication that may be historically unprecedented. One particular aspect of the US-centralized empire’s military involvement in that nation, the 2018 airstrikes by the US/UK/France alliance and the alleged chemical weapons incident which preceded it, has been subject to intense scrutiny ever since it took place. And with good reason: there are many pieces of evidence indicating that the Douma incident was staged to falsely implicate the Syrian government.
I don’t claim to know exactly who would have been involved in such a staging and to what extent. It is technically possible, as the UK’s Admiral Lord West speculated at the time, that it was perpetrated independently by the vicious al-Qaeda-linked Jaysh al-Islam forces who’d been occupying Douma, a last-ditch attempt to provoke a western military response that might save them from the brink of defeat at the hands of the surging Syrian Arab Army. Jaysh al-Islam has an established record of deliberately massacring civilians, and of using civilians as military leverage by locking them in cages on rooftops in strategic Douma locations to prevent airstrikes. The narrative management operation known as the White Helmets would also have been involved to some extent, and it’s very possible that Saudi Arabia, who backs Jaysh al-Islam, was involved as well.
Any number of other allied intelligence agencies could have also been involved to some degree (perhaps with the more expanded goal of ensuring continued US military commitment in Syria during an administration that is vocally opposed to it), and it’s unknown if anyone involved would have had direct contact with any part of any US government agency regarding any of this. All we know for sure is that there’s a growing mountain of evidence that the Syrian government was not involved, and that this raises extremely important questions about (A) who really killed those civilians in Douma and (B) how seriously any future demands for military action should be taken from the US power alliance.
That mountain of evidence includes the following 12 items. Taken individually they are reason enough to be skeptical of the narratives that are being promoted by a government with a known history of using lies, propaganda and false flags to advance preexisting military agendas. Taken together, and looked at with intellectual honesty, they are enough to obliterate anyone’s trust in what we’ve been told about Douma.
1. A leaked OPCW Engineering Assessment concluded that the gas cylinders on the scene were manually placed there.
The Organisation for the Prohibition of Chemical Weapons (OPCW) is a purportedly neutral and international watchdog group dedicated to eliminating the use of chemical weapons around the world. In May of this year, a leaked internal OPCW document labeled “Engineering Assessment of Two Cylinders Observed at the Douma Incident” was published by the Working Group on Syria, Propaganda and Media. The Engineering Assessment was signed by a South African ballistics expert named Ian Henderson, whose name is seen listed in expert leadership positions on OPCW documents from as far back as 1998 and as recently as 2018, and its authenticity was quickly confirmed by the OPCW in a statement sent to multiple journalists that it was “conducting an internal investigation about the unauthorised release of the document in question.”
Henderson ran some experiments and found no scientifically grounded theory for how the cylinders could possibly have been dropped vertically from the air while being found in the condition and locations that they were found in, concluding instead that they were manually placed on the scene. This is a huge difference, since the Assad coalition was the only side with aircraft and Jaysh al-Islam were the only forces on the ground.
“The dimensions, characteristics and appearance of the cylinders, and the surrounding scene of the incidents, were inconsistent with what would have been expected in the case of either cylinder being delivered from an aircraft,” Henderson wrote. “In each case the alternative hypothesis produced the only plausible explanation for observations at the scene.”
“In summary, observations at the scene of the two locations, together with subsequent analysis, suggest that there is a higher probability that both cylinders were manually placed at those two locations rather than being delivered from aircraft,” Henderson concludes.
This is unsurprising, since the hypothetical physics of the empire’s airdrop narrative make no sense to anyone with any understanding of how material objects move. To get a simple explanation of this, watch the breakdown in this three-minute animation. For a more in-depth look, check out this long Twitter thread by Climate Audit’s Stephen McIntyre.
The existence of Henderson’s report was kept secret from the public by the OPCW, which might make more sense after we get through #2 on this list.
2. US officials reportedly pressured the OPCW to find evidence of Assad’s guilt.
https://twitter.com/MaxBlumenthal/status/1196246809070444545?s=20
In addition to whoever leaked the Henderson report in May, a second whistleblower going by the pseudonym of “Alex” emerged in October to give a presentation before the whistleblower’s advocacy group Courage Foundation exposing far more plot holes in the official Douma narrative. This same whistleblower also spoke with award-winning British journalist Jonathan Steele, who published a bombshell report on Alex’s revelations in CounterPunch last month.
Among the most stunning revelations in Steele’s article was Alex’s report that US officials attempted to pressure OPCW inspectors during the Organisation’s drafting of its Interim Report on their Douma investigation in July 2018, and that this intercession was facilitated by an OPCW official named Bob Fairweather.
“On July 4 there was another intervention,” Steele writes. “Fairweather, the chef de cabinet, invited several members of the drafting team to his office. There they found three US officials who were cursorily introduced without making clear which US agencies they represented. The Americans told them emphatically that the Syrian regime had conducted a gas attack, and that the two cylinders found on the roof and upper floor of the building contained 170 kilograms of chlorine. The inspectors left Fairweather’s office, feeling that the invitation to the Americans to address them was unacceptable pressure and a violation of the OPCW’s declared principles of independence and impartiality.”
It’s unknown what forces were at play that enabled the US government to insert itself into into an ostensibly impartial OPCW investigation with the help of an OPCW official, but it wouldn’t be the first time the US government leveraged the Organisation into facilitating preexisting regime change agendas against a disobedient Middle Eastern nation. In 2002 Mother Jones reported that the US government, spearheaded by John Bolton, had used the threat of withdrawing its disproportionately high percentage of funding from the Organisation if it didn’t oust its then-Director General Jose Bustani. The popular Bustani, who’d previously been unanimously re-elected to his position, had been hurting the case for war with his successful negotiations with Saddam Hussein’s Iraq. In March 2018, after Bolton was selected as Trump’s National Security Advisor, The Intercept revealed that the campaign to remove Bustani had also included Bolton personally threatening his children.
Bolton was operating at the highest levels of the Trump White House throughout the entire duration of the OPCW’s Douma investigation. He was Trump’s National Security Advisor from April 9, 2018 to September 10, 2019. The OPCW’s Fact-Finding mission didn’t arrive in Syria until April 14 2018 and didn’t begin its investigation in Douma until several days after that, with its final report being released in March of 2019.
3. Levels of chlorinated organic chemicals didn’t indicate any chlorine gas attack took place.
“The main point is that chlorine gas degrades rapidly in the air,” Jonathan Steele told Tucker Carlson last month detailing what was told to him by Alex. “So coming in two weeks later, you wouldn’t find anything. What you would find is that the gas contaminates or affects other chemicals in the natural environment. So-called chlorinated organic chemicals [COCs]. The difficulty is they exist anyway in the natural environment and water. So the crucial thing is the levels: were there higher levels of chlorinated organic chemicals found after the alleged gas attack than there would have been in the normal environment?”
“When they got back to the Netherlands, to The Hague where the OPCW has its headquarters, samples were sent off to designated laboratories, then there was a weird silence developed,” Steele continued. “Nobody told the inspectors what the results of the analysis was. It was only by chance that the inspector found out through accident earlier the results would come in and there were no differences at all. There were no higher levels of chlorinated organic chemicals in the areas where the alleged attack had happened where there is some suspicious cylinders had been found by opposition activists. So it didn’t seem possible that there could have been a gas attack because the levels were just the same as in the natural environment.”
“[Alex] got sight of the results which indicated that the levels of COCs were much lower than what would be expected in environmental samples,” Steele reported in CounterPunch. “They were comparable to and even lower than those given in the World Health Organisation’s guidelines on recommended permitted levels of trichlorophenol and other COCs in drinking water. The redacted version of the report made no mention of the findings.”
“Had they been included, the public would have seen that the levels of COCs found were no higher than you would expect in any household environment”, Alex told Steele.
This inconvenient fact was omitted from both the OPCW’s Interim Report in July 2018 and its Final Report in March 2019.
4. Many signs and symptoms of alleged chlorine gas poisoning weren’t consistent with chlorine gas poisoning.
https://twitter.com/caitoz/status/1187001753192919041?s=20
The OPCW’s Final Report on Douma in March 2019 assures us that the team found “reasonable grounds that the use of a toxic chemical as a weapon took place. This toxic chemical contained reactive chlorine. The toxic chemical was likely molecular chlorine.” A leaked internal OPCW email, featuring an inspector voicing objections to the aforementioned Bob Fairweather over vital information being omitted from the developing Interim Report on Douma, contradicts this assurance, saying observed symptoms weren’t consistent with chlorine gas poisoning.
“In this case the confidence in the identity of chlorine or any choking agent is drawn into question precisely because of the inconsistency with the reported and observed symptoms,” the email reads. “The inconsistency was not only noted by the FFM [Fact-Finding Mission] team but strongly noted by three toxicologists with expertise in exposure to CW [Chemical Weapons] agents.”
So the OPCW’s investigative team as well as three toxicologists said what was observed didn’t match chlorine gas poisoning symptoms. This information was, of course, hidden from us by the OPCW.
A leaked first draft of the Interim Report on Douma, before OPCW officials started cutting out chunks which didn’t suit the US narrative, gives more detail. Here are some excerpts (emphases mine):
“Some of the signs and symptoms described by witnesses and noted in photos and video recordings taken by witnesses, of the alleged victims are not consistent with exposure to chlorine-containing choking or blood agents such as chlorine gas, phosgene or cyanogen chloride. Specifically, the rapid onset of heavy buccal and nasal frothing in many victims, as well as the colour of the secretions, is not indicative of intoxication from such chemicals.”
“The large number of decedents in the one location (allegedly 40 to 45), most of whom were seen in videos and photos strewn on the floor of the apartments away from open windows, and within a few meters of an escape to un-poisoned or less toxic air, is at odds with intoxication by chlorine-based choking or blood agents, even at high concentrations.”
“The inconsistency between the presence of a putative chlorine-containing toxic chocking or blood agent on the one hand and the testimonies of alleged witnesses and symptoms observed from video footage and photographs, on the other, cannot be rationalised. The team considered two possible explanations for the incongruity:
a. The victims were exposed to another highly toxic chemical agent that gave rise to the symptoms observed and has so far gone undetected.
b. The fatalities resulted from a non-chemical-related incident.”
5. A doctor in Douma told journalist Robert Fisk that there was no gas poisoning.
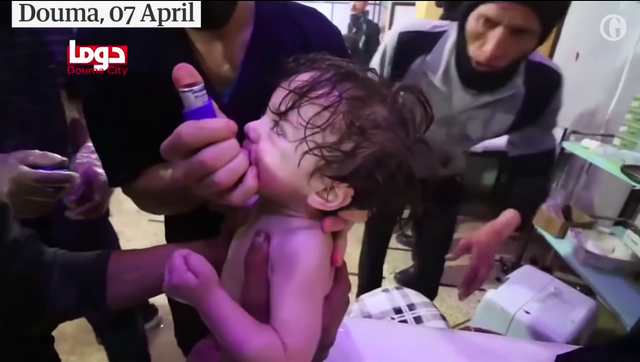
Shortly after the Douma incident a video was circulated online and redistributed on news media around the world featuring people being hosed down with water in a hospital and an infant receiving a respiratory treatment. A doctor who worked in the hospital Assim Rahaibani gave the following account to journalist Robert Fisk days after the incident, saying those in the video were actually just suffering from hypoxia due to dust inhaled after a conventional bombing:
“I was with my family in the basement of my home three hundred metres from here on the night but all the doctors know what happened. There was a lot of shelling [by government forces] and aircraft were always over Douma at night – but on this night, there was wind and huge dust clouds began to come into the basements and cellars where people lived. People began to arrive here suffering from hypoxia, oxygen loss. Then someone at the door, a ‘White Helmet’, shouted ‘Gas!’, and a panic began. People started throwing water over each other. Yes, the video was filmed here, it is genuine, but what you see are people suffering from hypoxia – not gas poisoning.”
Lest anyone accuse Fisk of having any special loyalties to the Syrian government, in this same report he says it “is indeed a ruthless dictatorship.”
6. A BBC reporter said he has proof that the hospital scene was staged.
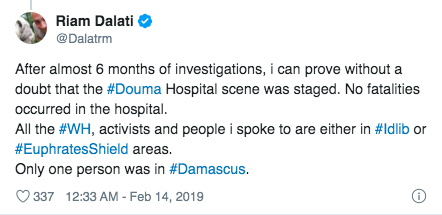
https://twitter.com/Dalatrm/status/1095677403198906369?s=20
The BBC, another establishment that can hardly be accused of Assad loyalism, saw its Syria producer Riam Dalati claiming earlier this year that he had proof beyond a doubt the aforementioned hospital scene was staged. While holding to the establishment line that the attack did happen, Dalati expressed uncertainty as to what if any chemical would have been used and said “everything else around the attack was manufactured for maximum effect.” Emphases mine:
“The ATTACK DID HAPPEN, Sarin wasn’t used, but we’ll have to wait for OPCW to prove Chlorine or otherwise,” Dalati tweeted. However, everything else around the attack was manufactured for maximum effect. After almost 6 months of investigations, i can prove without a doubt that the Douma Hospital scene was staged.”
“No fatalities occurred in the hospital,” Dalati continued. “All the White Helmets, activists and people i spoke to are either in Idlib or Euphrates Shield areas. Only one person was in Damascus. Russia and at least one NATO country knew about what happened in the hospital. Documents were sent. However, no one knew what really happened at the flats apart from activists manipulating the scene there. This is why Russia focused solely on discrediting the hospital scene.”
In other words, Russia knew that these “activists” were staging the scene for the news media, and understandably focused on discrediting their work.
“I can tell you that Jaysh al-Islam ruled Douma with an iron fist,” Dalati added. “They coopted activists, doctors and humanitarians with fear and intimidation.”
Dalati set his account to private for an extended period after these extremely controversial statements got him a flood of attention, but the thread is up on Twitter as of this writing (here’s an archive in case they vanish again).
7. More evidence the Douma scene was knowingly staged for media.
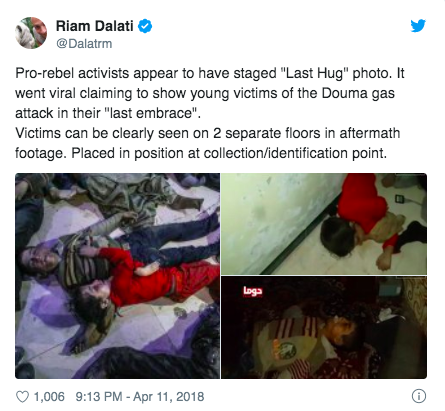
https://twitter.com/Dalatrm/status/984011488938643456?s=20
Riam Dalati also tweeted evidence after the attack that people had staged the corpses of two children to make it appear as though they died hugging each other for the purpose of emotional manipulation. If you’ve got a strong stomach (seriously think hard about whether this is something you want in your head before diving in), Stephen McIntyre also compiled some disturbing proof of dead infants being physically placed on top of other corpses in between video shoots of the Douma incident’s aftermath.
Whoever was positioning these bodies for the cameras clearly had a goal of generating an emotional response from the outside world. Which would be precisely the goal of staging a false chemical weapons attack.
8. Witness testimony at The Hague.
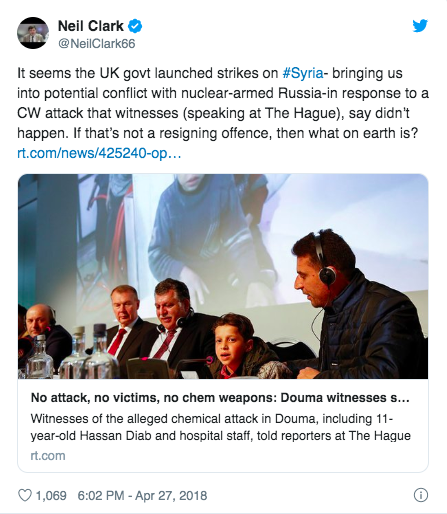
https://twitter.com/NeilClark66/status/989761664680521728?s=20
Seventeen Syrian civilians, including medical personnel and some of the “victims” seen in the aforementioned hospital footage, spoke at the OPCW headquarters in The Hague saying that no chemical weapons attack took place. RT reports:
“There were people unknown to us who were filming the emergency care, they were filming the chaos taking place inside, and were filming people being doused with water. The instruments they used to douse them with water were originally used to clean the floors actually,” Ahmad Kashoi, an administrator of the emergency ward, recalled. “That happened for about an hour, we provided help to them and sent them home. No one has died. No one suffered from chemical exposure.”
The briefing was boycotted by the US and 16 of its allies and was smeared as an unconscionable Russian hoax by media outlets ranging from Sky News to Al Jazeera to The Guardian to The Intercept, apparently for no other reason than that what these Syrians were saying didn’t match the unsubstantiated claims being promoted by the political/media class of the US-centralized empire. If you want to just listen to what the Syrians themselves say and make up your own mind, RT has an English translation video here:
9. The first OPCW Director General finds the glaring irregularities and omissions from the OPCW’s Douma report “very disturbing”.
After the aforementioned Courage Foundation presentation given by Alex this past October, the aforementioned former OPCW Director General Jose Bustani (the one whose kids John Bolton threatened) had this to say:“The convincing evidence of irregular behaviour in the OPCW investigation of the alleged Douma chemical attack confirms doubts and suspicions I already had. I could make no sense of what I was reading in the international press. Even official reports of investigations seemed incoherent at best. The picture is certainly clearer now, although very disturbing”
“I have always expected the OPCW to be a true paradigm of multilateralism. My hope is that the concerns expressed publicly by the Panel, in its joint consensus statement, will catalyse a process by which the Organisation can be resurrected to become the independent and non-discriminatory body it used to be.”
10. This OAN reporter literally just walking around asking people in Douma what they saw.
11. MIT Professor Emeritus Theodore Postol speaking about the plot holes and irregularities in scientific protocol with the Douma investigation.
12. Common sense: Assad stood nothing to gain from launching a chemical attack, while Jaysh al-Islam fighters stood everything to gain by faking one.
This is the initial reason why critical thinkers were so skeptical of the establishment Douma narrative: from the very beginning, it made no sense at all.Click this hyperlink to read a BBC article dated five days before the Douma incident, describing how the Syrian government “appears poised to regain control” of the town and how Jaysh al-Islam fighters were already evacuating. The battle was won. Assad would have stood absolutely nothing to gain from tempting a retaliation from western powers (which could have been far more severe than it ended up being) all to drop a couple of cylinders of chlorine gas, which incidentally is a highly ineffective weapon that ordinarily takes a very long time to kill.
Jaysh al-Islam (and whoever else they may have been working with), on the other hand, would have stood everything to gain by murdering a few of the civilians they had been holding captive in the town they’d invaded in the hopes that western forces would become their airforce for a bit and hold off the Syrian Arab Army from reclaiming Douma.
“Why would Assad use chemical weapons at this time? He’s won the war,” Major General Jonathan Shaw told The Mail on Sunday at the time. “That’s not just my opinion, it is shared by senior commanders in the US military. There is no rationale behind Assad’s involvement whatsoever. He’s convinced the rebels to leave occupied areas in buses. He’s gained their territory. So why would he be bothering gassing them?”
“The jihadists and the various opposition groups who’ve been fighting against Assad have much greater motivation to launch a chemical weapons attack and make it look like Assad was responsible,” the ex-SAS and Parachute Regiment commander added. “Their motivation being that they want to keep the Americans involved in the war – following Trump saying the US was going to leave Syria for other people to sort out.”
Admiral Lord West made similar comments on the BBC around the same time, prompting BBC host Annita McVeigh to flip into frantic narrative management mode suggesting that he’s “muddying the waters” during an “information war with Russia”.
“President Assad is in the process of winning this civil war, and he was about to take over Douma, all that area,” West said. “He’d had a long, long, long slog slowly capturing that area of the city, and there just before he goes in and takes it all over, apparently he decides to have a chemical attack. It just doesn’t ring true. It seems extraordinary, because clearly he would know that there’s likely to be a response from the allies. What benefit is there for his military? Most of the rebel fighters, this disparate group of Islamists, had withdrawn, there were a few women and children left around. What benefit was there militarily in doing what he did? I find that extraordinary.”
“Whereas we know that in the past some of the Islamo groups have used chemicals, and of course there’d be huge benefit in them labeling an attack as coming from Assad, because they would guess quite rightly that there would be a response from the US as there was last time, and possibly from the UK and France,” West added.
“If I were advising some of the Islamist groups, many of whom are worse than Daesh,” West said, “I would say look, we’ve got to wait until there’s another attack by Assad’s forces, particularly if they’ve got a helicopter overhead or something like that and they’re dropping barrel bombs, and we set off some chlorine. Because we’ll get the next attack from the allies. And there’s no doubt that if we believe he’s done a chemical attack we should do that. And those attacks will get bigger, and it’s the only way they’ve got, actually, of stopping the inevitable victory of Assad.”
These are not Assad sympathizers or Kremlin assets saying this. These are not a bunch of hippie dippie anti-imperialists. These are lifelong military men, thinking in military terms, describing what they were seeing. And what they were seeing is the thing that a false flag is.
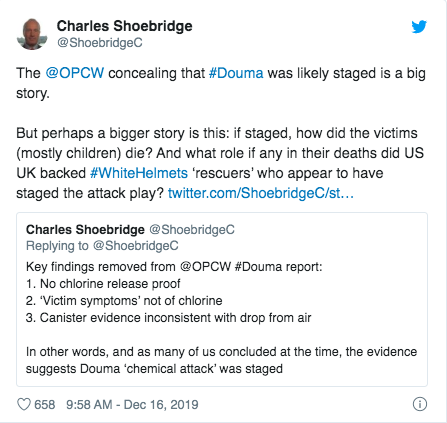
https://twitter.com/ShoebridgeC/status/1206347865729183746?s=20
And now here we are. The US is still illegally occupying Syria in spite of Trump’s repeated verbiage about getting out, and those children are still dead.
This isn’t just some idle philosophical question. People died. A massive war crime occurred and the more minutes tick by before a legitimate investigation is launched–with full transparency and accountability this time–the less available evidence there will be. Which is why establishment narrative managers on Syria go full dead-weight when asked if they support a full criminal investigation into what happened. They don’t actually believe it will go their way, and rightly so.
Meanwhile the illegal occupation of Syria drags on, perhaps until Trump can be replaced with a more compliant puppet, and we’re all basically just sitting around waiting to be deceived again.
This cannot continue. This must not continue.
UN reiterates that it can’t verify US allegations against Iran in Aramco attacks
Press TV – December 20, 2019
The UN Under-Secretary-General for Political Affairs Rosemary DiCarlo has reiterated earlier remarks by the UN General Secretary that the body cannot verify US claims blaming Iran for attacks on Saudi Arabia’s Aramco oil facilities.
DiCarlo made remarks during a UN Security Council briefing on the eighth report of the Secretary General on the implementation of resolution 2231 which endorsed the Iran nuclear deal in 2015.
“At this time, we are unable to independently corroborate that the cruise missiles, or the recovered components we inspected, are of Iranian origin,” she said speaking of alleged missile debris related to the September 14 attack on the oil facilities.
“We have recently received confirmation that some of the cruise missile components were, in fact, not made by the identified manufacturers but could have been copies,” she added.
DiCarlo also said the Secretariat is “unable to independently corroborate” whether drones used in the operation were of “Iranian origin”.
The attacks, which successfully halved the Saudi kingdom’s oil production, were claimed by Yemen’s Houthi Ansarullah movement and were in response to Riyadh’s nearly five-year onslaught against the country.
The operation displayed a significant advancement in Yemeni military capabilities, successfully striking one of Riyadh’s most important and also most heavily protected assets.
Washington, however, which has provided the bulk of Saudi Arabia’s air defense systems, was quick to blame Iran following the attack without providing any conclusive evidence to back up its claims.
Washington’s allegations against Tehran came at a time when Saudi officials had said that they lacked enough information to identify the perpetrator of the attack.
Washington’s jump to blame Tehran for the attack came as the operation, conducted by Yemen’s ragtag military forces, was widely seen to be undermining the efficiency of Washington’s much-prized Patriot surface-to-air missile systems deployed in Saudi Arabia.
Two days following the attack, Russian President Vladimir Putin pointed to the utter failure of the US defense systems, mockingly suggesting that Saudis may be better off buying Russian-made missile defense systems.
Washington insists on blaming Iran
On Thursday, Washington claimed that it had obtained new evidence blaming Iran for the attack.
A US report, cited by Reuters, said Washington “assessed that before hitting its targets, one of the drones traversed a location approximately 200 km to the northwest of the attack site”.
“This, in combination with the assessed 900 kilometer maximum range of the Unmanned Aerial Vehicle (UAV), indicates with high likelihood that the attack originated north of Abqaiq,” the report said, referring to the location of one of the oil facilities.
Speaking with Reuters, US Special Representative for Iran Brian Hook said the newly-declassified information proved that Iran was behind the operation.
“As many nations have concluded, there are no plausible alternatives to Iranian responsibility,” he said.
Hook’s comments come despite the fact that Washington’s own report stopped short of claiming that Iran was the origin of the attack.
“At this time, the US Intelligence Community has not identified any information from the recovered weapon systems used in the 14 September attacks on Saudi Arabia that definitively reveals an attack origin,” Reuters quoted the report as saying.
Addressing the Security Council on Thursday, Iran’s Ambassador to the United Nations Majid Takht-Ravanchi vehemently rejected Washington’s accusations regarding the Aramco operation.
He also described US sanctions on Iran as being “economic terrorism” targeting ordinary people as well as different sectors of the Iranian economy.
UN slams US JCPOA withdrawal
Speaking on Thursday, DiCarlo also urged for the full and effective implementation of the Joint Comprehensive Plan of Action (JCPOA) to “secure tangible economic benefit to the Iranian people”.
“We therefore regret the withdrawal of the United States from the JCPOA in May 2018,” she added.
Washington reimposed economic sanctions which had been lifted under the deal after withdrawing from the deal last year.
“Certain actions taken by the United States, since its withdrawal from the Plan, are contrary to the goals of the Plan,” she said.
“The reimposition of its national sanctions lifted under the Plan, as well as its decision not to extend waivers for the trade in oil with Iran and certain non-proliferation projects, may also impede the ability of Iran and other Member States to implement the Plan and 2231,” she added.
The UN official said Iran has stated that the suspension of its JCPOA commitments in response to the failure of signatories of the JCPOA to uphold the agreement, “are reversible and that it intends to remain in the Plan”.
“In this regard, the recent decisions by Belgium, Denmark, Finland, the Netherlands, Sweden and Norway to also join the Instrument in Support of Trade Exchanges (INSTEX) are positive developments,” she added.
Why Western Media Ignore OPCW Scandal
Strategic Culture Foundation | December 20, 2019
The credibility of the Organization for the Prohibition of Chemical Weapons is on the line after a series of devastating leaks from whistleblowers has shown that the UN body distorted an alleged CW incident in Syria in 2018. The distortion by the OPCW of the incident suggests that senior directors at the organization were pressured into doing so by Western governments.
This has grave implications because the United States, Britain and France launched over 100 air strikes against Syria following the CW incident near Damascus in April 2018. The Western powers rushed to blame the Syrian government forces, alleging the use of banned weapons against civilians. This was in spite of objections by Russia at the time and in spite of evidence from independent investigators that the CW incident was a provocation staged by anti-government militants.
Subsequent reports by the OPCW later in 2018 and 2019 distort the incident in such a way as to indict the Syrian government and retrospectively exculpate the Western powers over their “retaliatory” strikes.
However, the whistleblower site Wikileaks has released more internal communications provided by 20 OPCW experts who protest that senior officials at the organization’s headquarters in The Hague engaged in “doctoring” their field reports from Syria.
Copies of the doctored OPCW reports are seen to have suppressed important evidence casting doubt on the official Western narrative claiming that the Syrian government was to blame. That indicates the OPCW was engaged in a cover-up to retrospectively “justify” the air strikes by Western powers. This is a colossal scandal which implies the US, Britain and France wrongly attacked Syria and are therefore guilty of aggression. Yet, despite the gravity of the scandal, Western media have, by and large, ignored it. Indicating that these media are subordinated by their governments’ agenda on Syria, rather than exposing the truth as independent journalistic services.
An honorable exception is Fox News anchor Tucker Carlson who has given prominence to the scandal on US national TV. So too has veteran British journalist Peter Hitchens who has helped expose the debacle in the Mail on Sunday newspaper.
Apart from those sources, the mainstream Western media have looked away. This is an astounding dereliction of journalistic duty to serve the public interest and to hold governments to account for abusing power.
Major American news outlets have been engrossed in the Trump impeachment case over his alleged abuse of power. But these same media have ignored an arguably far more serious abuse of power with regard to launching missiles on Syria over a falsehood. That says a lot about the warped priorities of such media.
However, their indifference to the OPCW scandal also reflects their culpability in fomenting the narrative blaming the Assad government, and thereby setting up the country for military strikes. In short, the corporate media are complicit in a deception and potentially a war crime against Syria. Therefore they ignore the OPCW scandal.
That illustrates how Western news media are not “independent” as they pompously claim but rather serve as propaganda channels to facilitate their governments’ agenda.
An enlightening case study was published by Tareq Haddad who quit from Newsweek recently because the editors censored his reports on the unfolding OPCW scandal. Haddad explained that he had important details to further expose the OPCW cover-up, but despite careful deliberation on the story he was inexplicably knocked back by senior editors at Newsweek who told him to drop it. There is more than a hint in Haddad’s insider-telling that senior staff at the publication are working as assets for Western intelligence agencies, and thus able to spike stories that make trouble for their governments.
Given the eerie silence among US, British and European media towards the OPCW scandal it is reasonable to posit that there is a systematic control over editorial policies about which stories to cover or not to. What else explains the blanket silence?
The scandal comes as Western powers are attempting to widen the powers of the OPCW for attributing blame in such incidents. Russia has objected to this move, saying it undermines the authority of the UN Security Council. Given the scandal over Syria, Russia is correct to challenge the credibility of the OPCW. The organization has become a tool for Western powers.
Russian envoy to the OPCW and ambassador to the Netherlands Alexander Shulgin says that Moscow categorically objects to expanding the OPCW’s functions and its powers of attributing blame. The extension of powers is being recommended by the US, Britain and France – the three countries implicated in abusing the OPCW in Syria to justify air strikes against that country.
The Russian envoy added: “The OPCW’s attribution mechanism is a mandate imposed by the US and its allies, which has nothing to do with international law and the Chemical Weapons Convention’s provisions. Any steps in this direction are nothing more than meddling in the UN Security Council’s exclusive domain. We cannot accept this flagrant violation of international law.”
Thus, the OPCW – a UN body – is being turned into a rubber-stamp mechanism by Western powers to legalize their acts of aggression. And yet despite the mounting evidence of corruption and malfeasance, Western corporate media studiously ignore the matter. Is it any wonder these media are losing credibility? And, ironically, they have the gall to disdain other countries’ media as “controlled” or “influence operations”.
Democrat advice for ‘combating online disinformation’ is common sense buried under hypocrisy and censorship
By Nebojsa Malic | RT | December 19, 2019
There is actually some good advice in the Democratic National Committee’s five suggestions for avoiding “disinformation” online. Too bad it’s buried in hypocrisy and promotion of literal disinformation shops, grifters and frauds.
On Tuesday, as Democrats launched their final impeachment push in the House of Representatives, the DNC posted a set of recommendations to its followers to protect themselves from “disinformation.” While the jokes about flogging the dead horse of ‘Russiagate’ write themselves at this point, some of the advice offered is actually quite solid.
For instance, it makes perfect sense to actively seek out information from multiple sources. The DNC spoils it, however, by insisting the sources have to be “authoritative.” As in what, approved by the Party? Well, no, merely by the self-appointed gatekeepers such as MediaBiasFactCheck and NewsGuard.
We’ve written about NewsGuard before. As for MBFC, it lists the Alliance for Securing Democracy – operators of the ridiculous Hamilton68 dashboard – and Bellingcat as “least biased” news sources. Enough said.
“Ask yourself who the author of online content is,” also amounts to good advice. That too is tempered by the realization that in its more commonplace, lazy form it amounts to identity politics: stuff “our” people create has to be correct, while anything done by “them” is suspect.
The third point is perhaps the strongest: “When you share, make sure you are sharing content that is true and helpful to others, not as a knee-jerk reaction to content that angers or scares you.”
One only wishes the Democrats would take their own advice, given how widespread the “woke rage clickbait” business model has become. A whole bunch of online outlets have catered to hate-clicks of Democrats perpetually aggrieved by Donald Trump’s presidency, until they went out of business and fired their staff.
The fourth piece of advice urges people to “try to inject truth into the debate” using fact-checkers like Snopes or PolitiFact. Leaving aside the proliferation of partisan fact-checkers and the whole industry of “arguments” based on redefining the meaning of words, this method is somewhat of a rare bird – mainly because of too many people following points two and three too literally, and generally launching personal attacks rather than debating the issues.
By far the worst offender, however, has to be the fifth point, urging DNC followers to “educate” themselves by reading a variety of articles, books and reports that actually peddle outrageous propaganda.
For example, one of the recommended resources is a report on disinformation by New Knowledge – a Democrat-funded shop that literally faked an army of Russian “bots” to sway a 2017 US Senate race in Alabama.
Another is a New York Times “documentary” on a Soviet conspiracy to “tear the West apart” that tells more about its authors than anything they claim.
Other recommendations include “smart civil society groups” that are literally disinformation shops run either by the Democrats themselves (Media Matters for America), or the Atlantic Council and NATO (Disinfo Portal). There is also Graphika, an outfit currently employing the Atlantic Council’s former chief troll-hunter Ben Nimmo, a disinformation story unto himself.
But wait, there’s more! Among the recommended authorities are Russiagate pushers Clint Watts and Malcolm Nance, CNN and MSNBC authorities on “disinformation” and “Russian bots” despite being repeatedly and colossally wrong on everything pretty much all the time.
Needless to say, DNC’s advice has attracted far more derision than appreciation on Twitter, with responses dominated by snark along the lines of “Tell us more about this and the Steele dossier,” or “disinformation [is] information that doesn’t lead to election of Democrats.”
Nor was all of the negative feedback from conservatives. “Coming from those who rigged the 2016 Democratic primary, no thanks. I don’t take advice from criminals,” quipped one diehard Bernie Sanders fan.
Tough luck, Democrats. Do better.
US Democratic Party Warns Supporters of ‘Disinformation’ from Russia’s RT and Sputnik
Sputnik – December 20, 2019
The US Democratic National Committee has published a list of recommendations on how to combat online disinformation.
This list of “tips and additional resources” mentions Russian “propaganda outlets like RT & Sputnik.”
“Don’t let yourself be manipulated. Be aware of Russian propaganda outlets like RT & Sputnik and educate yourself on Russian propaganda lines,” the text on the committee’s website says.Apart from this, the recommendations include “reading longer works documenting disinformation and propaganda”, such as George Orwell’s 1984 and Report On The Investigation Into Russian Interference In The 2016 Presidential Election by the US Department of Justice.
The authors of this list of recommendations name what they believe to be reliable sources of information: the Senate Intelligence Committee, reports on disinformation by Harvard and Oxford, and some others.
Earlier this month, the European Values Centre for Security Policy think tank unveiled a report headlined Kremlin Watch Strategy for Countering Hostile Russian Interference, calling on European countries not to view RT and Sputnik as “free press” outlets and to ban its journalists from attending press conferences.
In October 2017, the organisation published a list of 2,327 US, British and European politicians, diplomats and military officials who had previously talked to RT. The list features Donald Trump, John McCain and Boris Johnson. According to Sputnik and RT Editor-in-Chief Margarita Simonyan, the publication of that list changed absolutely nothing. She added that the organisation was founded in the Czech republic and receives donations from different sources, including the British Foreign Ministry and the US embassy in Prague.
Featured Video
Thomas Fazi: NATO’s Hybrid Warfare – Deception & Permanent War
or go to
Aletho News Archives – Video-Images
Book Review
UAE tortured, killed journalist for opposing Israel normalization
The Cradle | October 31, 2026
UAE security officers detained, tortured, and killed Emirati poet and news editor Habib al-Sayegh in August 2019, shortly after he published a column opposing UAE normalization with Israel, according to a newly published book.
“Princes and Thieves,” a book by investigative journalist Matthew Cole published on 25 October, alleges that UAE security officers raided Sayegh’s Abu Dhabi home shortly after the publication of the column, hooded him in front of his wife and took him to a detention facility where he was tortured to death.
His interrogators reportedly pulled out several of his teeth with pliers and beat him repeatedly with a sharp metal object.
On 11 August 2019, Sayegh criticized the UAE’s plan to normalize relations with Israel as part of the Abraham Accords in his weekly column for Khaleej newspaper. The column was titled “Israel Is Our Real Enemy and A Dangerous Project.”
Sayegh described Israel as “a real and natural enemy” while questioning “who authorized the normalizers to speak on behalf of everyone?”
Nine days after the column was published, Emirati state media announced his death, without stating a cause. … continue
Blog Roll
 Aletho News
- US Approves Sale of 500 Patriot Missiles to Ukraine, Deliveries May Take Years
- German Imperialism: An Urgent Explainer
- Backed by AAP, West Virginia Proposal Would Allow Dental Hygienists to Give HPV Vaccine to 9-Year-Olds
- Poland Is the Symptom and Europe Is the Patient
- UAE security forces tortured, killed journalist for opposing Israel normalization: Report
- They Compared the Spice to the Drug. The Spice Won — Again. (Part 2)
- Thomas Fazi: NATO’s Hybrid Warfare – Deception & Permanent War
- Wrong, AP and NPR: Europe’s 50,000 Heat Deaths Are a Computer-Model Estimate, Not a Real Body Count
- Questioning Your Doctor Is Now Considered A Psychological Problem (Seriously)
- London tourism expo promotes Israeli agency linked to theft of Palestinian land
- If Americans Knew
- DAILY UPDATE: Latest essential news on Palestine, Israel, & region
- 1,300 will gather in Palo Alto on Nov. 1 for Z3 Conference on Zionism
- DAILY UPDATE: Latest essential news on Palestine, Israel, & region
- The Long Arm of AIPAC
- Genocidal intent behind Hebron assault, rights group says
- This week, Israel killed 8-year-old who survived bombing that wiped out her family
- DAILY UPDATE: Latest essential news on Palestine, Israel, & region
- Israeli soldier poses at damaged Lebanon church, sparking anger
- New Report. Manufacturing the Great Replacement: Is Israel behind one of the largest racist influence campaigns ever documented?
- ‘Arab voice doesn’t count’: Jewish Israeli blocs reject Palestinian support
- No Tricks Zone
- Germany’s Green Energy Transition Becoming Increasingly Expensive…Another 6 Trillion Euros!
- Sudden Stratospheric Warming, Powerful El Niño Combination May Lead To Extreme Europe Cold, Energy Crisis!
- Two New Studies Find Thwaites Glacier Melt Cannot Be Driven By Human Activity Or A Warming Ocean
- E-Cars Reduce CO2 Emissions By Only 41% Compared To Internal Combustion Engine Vehicles
- Predictions Made By Renowned Climate Professor Over Past Decades Have Been Proven To Be Poor
- New Study Suggests Large Regions Of The Pacific Ocean Have Been Cooling For The Last 80 Years
- Germany’s Green Energy Debacle: High Energy Costs Force Kahla Porzellan to Close After 182 Years!
- New Study: 50 Years Of The Most Aggressive ‘Net Zero’ Policies Can Only Affect The Global Climate By 0.03°C
- US September “Heat” Was No Record…Many Records Set Decades Ago
- Latest European Green Energy Debacle; Portugal’s Largest Flagship Solar Park Insolvent!

