Skripal in Prison — The First Book to Report the Truth

Editor’s note: John Helmer of Dances With the Bears is one of the two people who have done the most work on Her Majesty’s Skripal fiasco (the other being Rob Slane of The Blogmire). He’s the longest-serving foreign reporter in Russia (arrived to cover the Perestroika and simply never left) and with unnerving regularity manages to know more than you would think would be possible for one Australian in Moscow. Now he has a book out on the whole thing.
By John Helmer | Anti-Empire | February 14, 2020
It is exactly two years since the case of two Russians, Sergei and Yulia Skripal, began with their collapse on a park bench in the middle of England on the afternoon of March 4, 2018.
On their anniversary it is necessary to tell this story. But it isn’t the story of what happened. This is because the only people who can tell that one, the Skripals, are locked away in isolation, guarded by determined men under secret government orders.
Instead, this is the story of what didn’t happen – provably didn’t happen because it was quite impossible circumstantially; and because the legal papers warranting that it did have not been signed by a judge, tested in a court of law, or released in public.
The facts which you have seen, heard or read about the incident of March 4, 2018, have been falsified. Everything that has flowed from them is false too. Understanding this is a start to the other story, and so something solid to work from – not missed until now; more like seen but disbelieved. As if the truth were fiction, and the fiction truth.
This is the story of how the largest and longest criminal investigation in modern British history ended in a prosecution without evidence of the crime, the weapon, the crime scene, and even of the crime victims. Allegations there are; evidence admissible in a British court of law there is not. That’s to say, a prosecution which will not be presented in court, before no judge and jury; with no witnesses on oath; and no verdict. That is no prosecution at all.
To say otherwise, as do the British Government, its allies abroad, and every one of its mass-circulation media without exception, is a lie. The victims, it turns out, are held in a British prison, at a secret location, incommunicado, without access to lawyers to defend them, without contact with their families, or the consular representatives of the state whose passports they hold. No court has judged them or sentenced them to this punishment.

The Prime Ministers, Theresa May & Boris Johnson, lied.
MI6, the Secret Intelligence Service, lied.
The BBC lied.
The coroner broke the law.
The police and prosecutors faked the evidence.
Russian intelligence agents tried to rescue Sergei Skripal but were foiled in the attempt.
This is the story of what didn’t happen, and the truth of what did.

WHAT THE CRITICS ARE SAYING
- “You’ve lost me John” — Mark Urban, BBC
- “Other books will follow on the Skripals, but they will struggle to match the texture of Urban’s research, its knowledgeable hinterland” — The Times
- “There are people out there who know exactly what happened and who are biding their time before revealing all. I am not such a person, nor would I want to be, but I believe that such people do exist” — Rob Slane, The Blogmire
- “One of the most experienced foreign journalists in Moscow, John Helmer has lived in Russia for the last 30 years and knows more about it than necessary” — Andrei Shitov, Chief Political Observer, Tass
- “The book explains why the truth, though known, has not been told” — Katrina van den Heuvel, Editor, The Nation, New York.
- “You are picking on a dead man who can’t answer for himself” – Joe Lauria, Editor, Consortium News
- “[John Helmer is] a notorious conspiracy theorist” — Jeremy Kinsman, former Canadian ambassador to Russia, foreign policy advisor to Prime Minister Justin Trudeau.
NYC Taxpayers Spending Millions on Cyber Center with Controversial Ties to Israeli Intelligence
Graphic by Claudio Cabrera
By Whitney Webb | MintPress News | February 14, 2020
Early last week, the city of New York launched — with little media scrutiny — one of two new massive cybersecurity centers that will be run by private Israeli firms with close ties to Israel’s government, the so-called “Mega Group” tied to the Jeffrey Epstein scandal and prominent pro-Israel lobby organizations operating in the United States. The centers were first announced in 2018 as was the identity of the firms who would run them: Israel-based Jerusalem Venture Partners and SOSA.
As MintPress has reported on several occasions, all three of these entities have a history of aggressively spying on the U.S. federal government and/or blackmailing top American politicians, raising concerns regarding why these companies were chosen to run the new centers in the heart of Manhattan. The news also comes as Israeli cybersecurity companies tied to Israeli military intelligence Unit 8200 were revealed to have access to the U.S. government’s most classified systems and simulating the cancellation of the upcoming 2020 presidential election.
The new cybersecurity centers are part of a new New York City public-private partnership called “CyberNYC” that is valued at over $100 million and officially aims to “spur the creation of 10,000 cybersecurity jobs and make New York City a global leader in cyber innovation.” CyberNYC is an initiative of New York City’s Economic Development Corporation.
However, the companies that will be responsible for creating those cybersecurity jobs will benefit foreign companies, namely Israeli and most of the jobs to be created will go to foreigners as well, as media reports on the partnership have quietly noted. Those reports also stated that, while the stated purpose of the centers is to create new jobs, the Israeli firms chosen to run them — Jerusalem Venture Partners (JVP) and SOSA — view it as an opportunity to provide Israeli cybersecurity companies with a foothold into the American market and to see Israeli cybersecurity products adopted by both small and medium-sized American businesses, not just large corporations and government agencies.
For example, the founder of JVP and former Knesset member, Erel Margalit, told the Jerusalem Post that “the center we are setting up [in New York] will assist Israeli hi-tech companies in collaborating with customers and companies in the US and around the world.” More recently, ahead of the opening of the cybersecurity center that Margalit’s firm will manage, he told the Times of Israel that “New York is about something else, it’s about the drama of taking investors from Israel and Spain or Paris and other places and taking them to the next business level.” In other words, the companies set to benefit from these new centers will be foreign and mainly Israeli, as JVP invests the vast majority of its funds in Israeli start-ups.
Given that Wilson Lin, the head of CyberNYC, explained the reason behind the initiative is the fact that “there are not enough well-trained people in cyber security to fill the jobs that are required for a safer, more thriving commercial sector,” the statements of JVP’s founder strongly suggests that those “well-trained people” will not be Americans in New York, but will be brought in from abroad, namely Israel’s cybersecurity sector.
Of the companies chosen by CyberNYC to run its new cybersecurity centers, both have clear and demonstrable ties to Israel’s government and military intelligence as well as controversial groups of pro-Israel donors with considerable political clout in the United States.
For instance, Jerusalem Venture Partners was founded by Erel Margalit in 1993, with funding from the Yozma Program, an Israeli government program to “incentivize venture capital investment” in Israel. Since then, it has been a driving force in the development of Israel’s hi-tech sector and regularly collaborates with the Israeli Ministry of Economy and Industry and the EISP (Entrepreneurship and Innovation Support Program) alumni organization of Unit 8200. Today, it is the second largest venture capital fund in Israel.
JVP was also the sole venture capital fund chosen to partner with Israel’s government and military to establish the public-private “cyber hub” in Beersheba. This “hub” not only houses the IDF’s technology campus, but also the Israel National Cyber Directorate, which reports directly to Israel’s Prime Minister, as well as a high-tech corporate park that mostly houses tech companies with ties to Israel’s military intelligence apparatus. The area has been cited in several media reports as a visible indicator of the public-private merger between Israeli technology companies, many of them started by Unit 8200 alumni, and the Israeli government and its intelligence services.

A composite image of the future JVP-funded New York City cyber center. Photo | JVP Press Release
In addition to JVP’s close ties to Israel’s government and its key role in the merging of Israel’s private cybersecurity sector with Israeli military intelligence, JVP also has close ties to the Bronfman family through its Chief Operating Officer and general partner, Fiona Darmon. Prior to working with JVP, Darmon worked for Claridge Israel, the investment arm of the Bronfman family that was founded by Charles Bronfman in 1987.
Charles Bronfman was a one-time business partner of Mossad agent Robert Maxwell, father of Jeffrey Epstein’s alleged madam Ghislaine Maxwell, and co-founded the “Mega Group”, a group of pro-Israel oligarchs with clear and direct ties to organized crime, alongside Leslie Wexner, the main financier of Jeffrey Epstein’s operation that involved the sex trafficking of minors on behalf of Israeli military intelligence.
SOSA was founded much more recently than JVP, yet also has close ties to Israel’s government and military. Created in 2014, SOSA has grown rapidly by connecting mostly Israeli start-ups with investors and through its partnerships with the IDF. This partnership first became clear in 2018, when SOSA created the Homeland Security (HLST) Innovation Hub, which the Times of Israel described as “a first of its kind program that aims to create a defense and security innovation community that will match homeland security and defense industry firms with startups, to help industry giants maintain their leading edge.”
Last year, SOSA became one of two companies to manage the Israeli Ministry of Defense’s program INNOFENSE, an innovation program for civilian tech start-ups in the country’s defense industry. SOSA’s collaboration with the IDF also involves the creation of “joint business activities between international companies, [government] security organizations, investors and startups,” making SOSA a key player in the blurring of the line between Israeli military intelligence and its private tech sector.
SOSA is also directly partnered with two of Israel’s top weapons manufacturers, Rafael Advanced Defense Systems, as well as defense electronics companies ELTA Systems and Elron Electronics, the former parent company of another Israeli weapons manufacturer Elbit Systems. It is also partnered with the Unit 8200 alumni-founded tech company CheckPoint Systems and Leumi Tech, the hi-tech subsidiary of one of Israel’s largest banks, Leumi. Leumi Tech exists only in the U.S. and specifically aims to “provide a comprehensive suite of products and services to Israeli high-tech companies operating in the US.” The bank was recently forced to pay $400 million to the U.S. government for assisting U.S. citizens, most of them dual U.S.-Israeli citizens, in preparing false tax returns and hiding their assets in offshore accounts.
SOSA’s General Manager Guy Franklin is of particular interest, due to his close ties to the Israeli American Council (IAC), a pro-Israel lobby group created by convicted felon and ultra-Zionist millionaire Adam Milstein and largely funded by Sheldon and Miriam Adelson. The Adelsons are also the largest donors to both President Trump and the Republican Party in the United States.

In this photo posted on SOSA’s Facebook page, SOSA execs Uzi Scheffer and Guy Franklin pose in New York’s Time Square
Of the $100 million in funding for the CyberNYC initiative, $30 million comes from New York taxpayers and the remaining funds coming from the program’s partners, which includes Goldman Sachs and the Israeli military intelligence Unit 8200 incubator Team8, a start-up accelerator which has been discussed at length in several past MintPress News reports, including the recent MintPress investigation into the Israeli company Cybereason — a partner of Team8.
Team8, particularly its presence in New York, has long been associated with the push by pro-Israel political donor and American hedge fund manager Paul Singer and Israel’s government to make Israel the global cybersecurity leader as a means of preventing countries from boycotting Israel over human rights violations and war crimes. Team8’s role in CyberNYC will see them not only finance part of the initiative but also training cybersecurity workers who will be hired as part of the partnership.
Singer, who is based in Manhattan, created Start Up Nation Central in 2012 to specifically outsource American tech jobs to Israel in collaboration with top AIPAC officials and Israel’s government. Meanwhile, in parallel, Israel’s government and intelligence apparatus began a policy that same year that involved outsourcing intelligence and military intelligence operations to private companies created for that very purpose, particularly in the field of cybersecurity.
Thus, much as Israel’s cybersecurity industry has long been fused to Israel’s military and intelligence apparati, the Paul Singer-funded and Israel-backed policy has openly sought to bring American companies and government agencies into the fold in order to prevent boycotts of Israel. Though the so-called “anti-BDS laws” that have been passed in several U.S. states are one facet of this push, the use of Israeli tech, namely cybersecurity, sector to pursue this same end has received decidedly less coverage.
New York City has long been a major focus on this policy, with the growth of Israel hi-tech start-ups present in New York and run by former members of Unit 8200 exploding since this policy officially began in 2012. Indeed, Haaretz noted that, between 2013 and 2017 alone, the number of Israeli tech start-ups in New York City grew by fivefold and the number of Unit 8200 alumni working in NYC tech start-ups has also spiked in that same time frame.
The number of Unit 8200 alumni working in NYC’s tech sector has grown so much that they host an annual gala closed to the press where the goal, per Haaretz, is “to try to connect startups and early stage entrepreneurs from 8200 EISP (the Israeli accelerator for Unit 8200 alumni) with clients and venture capital funds in the United States.” One of the main players at that gala is Guy Franklin, the CEO of SOSA, which was chosen to run the other NYC cybersecurity sector.
The decision to create expensive, new cybersecurity centers run by JVP and SOSA, two Israeli firms with clear ties to controversial pro-Israel lobby organization and donors as well as Israel’s government and intelligence apparatus, reveals that not only is this Singer and Israel-backed policy continuing to develop and expand at a rapid pace, but now the money of New York City taxpayers is now being used to propel it to new heights even though that very policy benefits Israel’s economy at the U.S.’ expense.
Whitney Webb is a MintPress News journalist based in Chile. She has contributed to several independent media outlets including Global Research, EcoWatch, the Ron Paul Institute and 21st Century Wire, among others. She has made several radio and television appearances and is the 2019 winner of the Serena Shim Award for Uncompromised Integrity in Journalism.
Why Washington is paranoid about Huawei
By Alex Lo | South China Morning Post | February 12, 2020
The past illuminates the present. This bombshell of a story dropped by The Washington Post certainly explains a lot about America’s current war against Chinese 5G supplier Huawei.
For more than half a century after the second world war, the Swiss company Crypto, whose products the governments of more than 100 countries have relied on to send secure encrypted messages, was secretly owned and operated by the CIA and its West German intelligence counterpart, the BND.
This has enabled American intelligence to read the top secrets of friends and foes alike, and to share them with other members of the so-called Five Eyes, the intelligence services of four other English-speaking countries.
But given the close working relationship with West German intelligence, maybe it should have been called the Six Eyes, despite the language differences.
Washington has kept insinuating that Huawei poses a security risk to all companies and governments that use its 5G infrastructures. Yet, it has never provided actual evidence despite having searched high and low for it, including illegally hacking into Huawei’s mainframes at its Shenzhen headquarters.
What Americans are afraid of, or paranoid about, is that the 5G pioneer will be to Chinese intelligence what Crypto was to the CIA. It takes one to know one.
As George Yeo, former minister of foreign affairs for Singapore, said in a recent speech, “a key reason for the US campaign against Huawei is the fear that China may not only develop a similar surveillance capability but Chinese equipment and Chinese systems will make it harder for the US to maintain the same surveillance reach.”
Americans are afraid if Huawei is dirty. But as Yeo explains, it’s just as bad for US intelligence if it is clean: it won’t have flaws and back-door vulnerabilities so readily available to exploit.
And of course, thanks to Edward Snowden, we know that other US agencies such as the FBI and National Security Agency have exploited such back doors with large US tech companies, including Apple, Google, Facebook, Microsoft, and others.
Yeo makes a third important point: “The only safe assumption is that all systems expose us to external intelligence penetration. We have to find ways to protect ourselves and accept that nothing is foolproof.”
If all systems are penetrable, the only answer is to be extra vigilant. Picking on one company or one country just distracts you from being alert to threats from elsewhere.
Alex Lo has been a Post columnist since 2012, covering major issues affecting Hong Kong and the rest of China. A journalist for 25 years, he has worked for various publications in Hong Kong and Toronto as a news reporter and editor. He has also lectured in journalism at the University of Hong Kong.
Last Week’s Cyberattack Against Iran Originated in the US – Iranian Civil Defence Chief
Sputnik – February 14, 2020
The United States government reportedly carried out a number of cyberattacks targeting Iran’s internet infrastructure over the past year, in response to Tehran’s shootdown of a US drone over Iranian airspace in the Hormuz Strait, and other actions in the Middle East which Washington has blamed on the Islamic Republic.
Iran foiled a ‘large-scale’ attack on the country’s cyber infrastructure on February 8, with the denial of service (DDOS) attack believed to have been launched by the US, Brig. Gen. Gholam Reza Jalali, chief of Iran’s Civil Defence Organization, has said.
“It’s very difficult and time-consuming to trace the source of a cyberattack. The Telecommunication Infrastructure Company is currently studying and looking for the source of the recent cyberattack against the country… but our analysis is that the US was the origin,” Jalali said, his comments cited by Press TV.
“The Americans’ cyberattack has been foiled by our cyber defence unit,” the commander said, but warned that the attack may be just a test ahead of larger planned attacks.
The February 8 DDoS attack caused widespread internet outages across Iran. Deputy Information and Communications Technology Minister Hamid Fattah said Sunday that the attack targeted communications infrastructure, and called it “the biggest attack” of its kind in Iran’s history. The disruption was said to have continued for about an hour before being dealt with by Iran’s DEJFA ‘Digital Fortress’ system.
“Since Americans failed to give a military response to our recent shoot-down of their unmanned aerial vehicle in Iranian waters as well as our missile attack on the [al-Asad Airbase in Iraq], they are responding to our country through continued economic pressure and cyberattacks,” Jalali suggested.
According to Jalali, the US attack failed to cause any damage.
He noted that last week’s attacks were further cause for Iran to accelerate its efforts to complete the construction of a National Information Network (NIN) in case further attacks are impending. The national infrastructure project, to which the Iranian government has already committed the equivalent of about $200 million, foresees the creation of a secure and stable communications internet network serving as a backup national intranet, providing information services, government e-services and other crucial data to citizens.
Last year, Iran’s Information and Communications Technology Ministry reported that the country had thwarted some 33 million cyberattacks against sensitive sites last year. In November, Jalali accused the US of declaring a cyberwar against Iran.
Gen. Soleimani assassinated to sabotage Iran’s talks with Saudis, UAE following Israeli briefing: NYT
Press TV – February 14, 2020
Washington ordered the assassination of top Iranian General Qassem Soleimani to sabotage de-escalation talks between Iran, Saudi Arabia and the United Arab Emirates following a report by Israel’s Mossad spy agency, according to the New York Times.
The paper reported on Thursday that General Soleimani had been arranging talks in Saudi Arabia and United Arab Emirates in order to de-escalate tensions with Tehran.
The Times wrote that the talks happened after Saudi Arabia and the UAE, which are central to the Trump administration’s so-called regional alliance seeking to pressure Iran, began to question the efficiency of Washington’s anti-Iran campaign.
According to the report, one such meeting took place last September in Abu Dhabi, the capital of the United Arab Emirates where a plane carrying “senior Iranian officials” landed for talks.
News of the meeting, which reached Washington only after it was notified by reports from American spy agencies, “set off alarms inside the White House”, according to the report.
The report added that a similar mediation attempt, also arranged by Gen. Soleimani, was underway between Tehran and Riyadh using Iraqi and Pakistani intermediaries.
The report wrote that the developments had greatly concerned Israel, which had been trying to push the Trump administration to exert more pressure on Tehran.
According to the Times, US Secretary of State Mike Pompeo met Mossad chief Yossi Cohen on October during a trip to Israel where he was briefed on Iran’s attempted de-escalation talks with Saudi Arabia and the UAE.
Cohen warned Pompeo that Tehran was effectively on the verge of achieving its “primary goal” of breaking up the so-called “anti-Iran” alliance.
A few months later in early January, General Soleimani was assassinated by Washington’s order while on a formal visit to Baghdad.
According to former Iraqi prime minister Adel Abdul-Mahdi, General Soleimani was due to formally meet the Iraqi premier during the trip and was carrying Tehran’s response to a message from Riyadh regarding the de-escalation talks.
Following the attack, the Trump Administration claimed that the assassination had taken place after a reported rocket attack on a US base in Iraq killed a “US civilian contractor” and that Gen. Soleimani was an “imminent threat” to US citizens.
Many US political figures have rejected the claims and have questioned why the Trump administration has failed to provide any evidence backing its actions.
The New York Times’ Thursday report, however, reveals that entirely different considerations, such as Israel’s push to undermine Iran’s attempts at peace with its regional neighbors, were behind the assassination.
‘Months of miscalculations’
According to the report, the assassination marks yet another miscalculation by the Trump administration which has failed to bend Iran through its “maximum pressure” campaign.
Following its unilateral withdrawal from the 2015 Iran nuclear deal in 2018, the US imposed unilateral sanctions against Tehran in a bid to goad Tehran to accept new terms dictated by Washington.
The Times, however, reported that a recent analysis conducted by the Central Intelligence Agency (CIA) shows that the sanctions have had little effect in fulfilling Washington’s goals.
The US has also sought to pressure Iran militarily by deploying troops to the region and creating a regional anti-Iran alliance in the region as part of if its anti-Iran campaign.
Washington called for the formation of a naval coalition in the region following a string of suspicious attacks on oil tankers in the Persian Gulf.
Iran has vehemently denied the accusations, saying the incidents appear to be false flag operations meant to frame the Islamic Republic and push US interests.
Citing instances such as the major Yemeni attack on Saudi oil facilities last September and Iran’s downing of a US Global Hawk spy craft in June, the New York Times report said stepped-up US military presence also failed to achieve its objectives.
Witnessing the Trump administration’s faltering policy in the Middle East, Saudi Arabia and the UAE were convinced to open direct talks with Tehran, the report noted.
Crypto CIA spy op revelations makes us see US’ Huawei objections in a new light
© Global Look Press/www.imago-images.de/MANUEL GEISSE; © REUTERS/Arnd Wiegmann
By Neil Clark | RT | February 13, 2020
The revelation that the CIA (and German Intelligence) was in secret control of the Swiss cryptography firm Crypto AG highlights the hypocrisy of US ‘security concerns‘ over the advance of Huawei and other firms.
The very wise old saying that if you point one finger at someone there are three fingers pointing back at you, was classically illustrated by this week’s bombshell revelations — published in the Washington Post and on ZDF and SRF – that the CIA and BND (West Germany’s secret service) secretly owned and controlled the Swiss cryptography company Crypto. The real owners of Crypto installed ‘backdoor vulnerabilities’ in its products which allowed the US and West Germany to eavesdrop on communications — from enemies and allies alike — which the senders believed had been successfully encrypted. We’re talking here about top secret communications between leading government officials, spies, diplomats and military figures.
Just imagine that back in the 1970s or 80s you had claimed that the Crypto was a CIA front. You’d have been dismissed as a ‘crank conspiracy theorist, ’and/or ‘totally paranoid‘ by the gatekeepers of that time. But the rumours were true. Once again a ‘conspiracy theory’ has turned out to be not as barmy as once depicted. Truth again proved to be stranger than fiction.
How much intelligence was gathered via Crypto is quite staggering. As RT has reported: “Throughout the 1980s — around 40% of all government transmissions analysed by the US National Security Agency (NSA) ran through Crypto‘s devices.”
What a neat little racket. Over 120 governments of the world, but not the former Soviet Union and Communist China who, to their great credit were distrustful, made use of Crypto’s products. These governments, which included Iran, Libya, Argentina and Egypt were effectively paying the Americans and West Germans to spy on them!
The Germans bowed out of the operation in 1993, but for the next 25 years, the CIA kept it running. Which begs the question: what other US Intelligence fronts of the past and present don’t we know about?
In her 1999 book Who Paid the Piper?: The CIA and the Cultural Cold War, Frances Stonor Saunders detailed how the CIA funded a whole range of publications and artistic enterprises often through the ’Congress for Cultural Freedom’.
Literary journals (who conveniently had a pop at communism) were funded by the CIA. Modern artists were funded by the CIA. Writers, poets and philosophers were funded by the CIA.
And under ‘Operation Mockingbird’ leading journalists were basically recruited to the agency.
According to Carl Bernstein, the CIA had over 400 journalists working for them in the old Cold War.
“In many instances, CIA documents show, journalists were engaged to perform tasks for the CIA with the consent of the managements of America’s leading news organizations,” the American journalist writes.
The CIA‘s own records show that, by 1991, they had relationships with “every major wire service, newspaper, news weekly and television network in the country”.
Now we know they were even behind Crypto too!
Given the organisation’s modus operandi, it is scarcely believable that the CIA doesn’t have similar ‘relationships’ and control mechanisms working today. Why wouldn’t it?
Not only should the Crypto revelations make us more aware of the CIA’s very wide reach, they should also make us see the American objections to the involvement of firms from China and Russia with developing telecommunications infrastructure and new technology in a completely different light.
The Russian anti-virus firm Kaspersky, has seen its software banned from use on US government networks, while the Chinese giant Huawei has been hit with sanctions — and warnings given to other countries about letting it build their 5G networks.
Taking the moral high ground (as always), US officials have said that Huawei could covertly access mobile-phone networks through ‘back doors’.
OMG! You mean like the US did with Crypto?
The Wall Street Journal cites the same US officials saying that “Huawei has had this secret capability for more than a decade.”
What ‘intelligence’ would that be I wonder? The CIA’s?
What seems to be the objection here is that China might end up doing what the US has been doing for years, namely spying on countries through ‘back doors’. How dare they! The hypocrisy as I’m sure you’ll agree is off the scale.
The strength of the objections — and indeed the sanctions already imposed in the US against the company tell us one thing. Huawei, unlike Crypto, Encounter magazine, the ‘National Committee for a Free Europe’, and lots of organisations we probably still don’t know about, is no CIA front.
State-backed Alliance for Securing Democracy disinfo shop falsely smears The Grayzone as ‘state-backed’
By Alex Rubinstein | The Grayzone | February 13, 2020
The Alliance for Securing Democracy, an online censorship initiative of the Western government-funded German Marshall Project, falsely and hypocritically characterized The Grayzone and independent journalist Jordan Chariton as “state-backed media,” smearing them for their factual reporting on the shadowy network behind the controversial app that undermined the integrity of the Iowa caucuses.
The Grayzone has exposed the Alliance for Securing Democracy (ASD) in a series of investigative reports as a neo-McCarthyite outfit prone to spreading disinformation, staffed by counter-terror cranks and national security hustlers.
The ASD’s parent organization also happens to be bankrolled by the US government, numerous European governments, and the European Union, at the tune of millions of dollars — making these false accusations against The Grayzone and Jordan Chariton actual state-backed smears.
Chariton, who founded the independent progressive news outlet Status Coup, hit back at the ASD’s outrageous claims. “The days of faux democracy gladiators defaming journalists – whose factual work they seek to discredit – as part of a Kremlin syndicate are over. It’s time to fight back,” he told The Grayzone.
On February 10, the ASD published a dubious analysis of a supposed Russian effort to spread conspiracies and disinformation around the Iowa caucuses. It honed in on the Russian-funded Sputnik News and three shows broadcast by RT. Those programs included “Going Underground,” which is hosted by British journalist Afshin Rattansi.
The post continued: “In addition, all the most popular tweets about Iowa retweeted in this time period by at least one monitored account pushed a narrative that the Democratic National Committee and/or the Democratic establishment more broadly seeks to undermine Sanders via nefarious means. Monitored accounts ‘Redacted Tonight’ (@redactedtonight) and ‘Watching the Hawks’ (@watchinghawks) are the primary accounts engaging directly with this material.”
“Watching the Hawks” is hosted by American journalist and son of former Minnesota Governor Jesse Ventura, Tyrel Ventura. “Redacted Tonight” is a political satire show hosted by American comedian Lee Camp. Camp opens each show by welcoming his live studio audience to “the comedy show where Americans in America covering American news are called foreign agents.”
The social media managers for both “Watching the Hawks” and “Redacted Tonight” are US citizens.
Nonetheless, the retweeting by these shows of factual reporting by The Grayzone and Jordan Chariton set off national security alarm bells among the disinformation warriors of the Alliance for Securing Democracy.
The Grayzone article that the ASD took issue with exposed the role of pro-Israel billiionaire Seth Klarman in pouring his money into the Super PAC behind the faulty Iowa vote results app, while at the same time donating directly to candidate Pete Buttigieg – the candidate who benefited the most from the sabotage of the caucus results.
The Klarman Family Foundation also happens to be a major funder of the ASD.
On Twitter, the ASD muddled the distinction between The Grayzone, Chariton, and the RT-sponsored Twitter accounts that retweeted them. The outfit claimed that “state-backed media accounts spread various conspiracy theories about the Iowa caucuses, many of which claimed the DNC, news media, and other candidates used “dirty tricks” to steal the victory from Sen. Bernie Sanders.” Attached to the tweet was a screenshot of tweets by The Grayzone and Chariton, making no mention of either “Watching the Hawks” or “Redacted Tonight.”
The false accusation was subsequently retweeted by ASD founder Clint Watts.
The Grayzone editor Max Blumenthal responded to the smear with indignation: “Neither Jordan Chariton nor The Grayzone are state-backed media, unlike your fiscal parent. And our reporting is 100% factual, unlike yours,” Blumenthal wrote on Twitter. “We are currently exploring options for holding your McCarthyite operation fully accountable for spreading malicious disinformation.”
After enduring a withering barrage of online criticism for its malicious falsehood, the ASD issued a weasely “clarifying point.”
The Alliance for securing media citations and grants from oligarchs
The Alliance for Securing Democracy is the most prominent of an array of information warfare initiatives that exploited public hysteria over supposed Russian meddling in the 2016 presidential elections.
The group’s Hamilton 68 Dashboard claimed to have tracked 600 Twitter accounts supposedly “linked to Russian influence operations.” In the mainstream press, that dubious claim was stretched even further as the dashboard was touted as a tool for keeping tabs on “Russian bots.”
Among the widely cited claims of Russian covert influence campaigns was the #taketheknee trend inspired by blacklisted NFL quarterback Colin Kaepernick’s high-profile protest of police brutality. The ASD’s cynical accusation, that a domestic protest movement against racism was being manipulated by the Kremlin, was reported uncritically by the New York Times.
The ASD has even claimed that Stars and Stripes, a military publication operated out of the Department of Defense, was an outlet “relevant to Russian messaging themes.” It has made similar accusations against The Intercept.
Oddly enough, the sole proprietor of The Intercept is billionaire Pierre Omidyar, whose Democracy Fund is a major financial backer of the Alliance for Securing Democracy.
An ASD fellow who helped design its bogus bot tracker, Andrew Weisburd, has publicly fantasized about the murder of Intercept editor Glenn Greenwald, whom he branded a “traitor.”
Aside from Omidyar’s Democracy Fund, the ASD is backed by Craig Newmark, the namesake of Craigslist, and the Klarman Family Foundation. As The Grayzone recently reported, Seth Klarman is a major funder of pro-settler Israel lobby organizations. He is also a prominent debt vulture strangling Puerto Rico with austerity. And, again, Klarman is a top donor to Buttigieg, the self-declared winner of the Iowa caucuses.
Ascertaining a full picture of just who is backing the ASD is not possible, however, as the organization’s public list of funders “does not include any donors who do not wish to disclose their charitable giving.”
But besides the centrist billionaires that fund it, the group’s fiscal parent rakes in money from Western governments, including the US State Department.
Meet the real state-backed disinfo shop
While the Alliance for Securing Democracy claims to be independently funded, it shares major backers with the German Marshall Fund (GMF), including the Sandler Foundation.
Likewise, Omidyar’s Democracy Fund gave somewhere between $500,000 and $1 million to the GMF, while Klarman Family Foundation chipped in between $250,000 and $499,999.

According to the ASD website, the group is “housed at the German Marshall Fund.”
Unlike The Grayzone and Jordan Chariton, the GMF is a state-backed entity that faithfully pursues the agenda of its government funders.
In the 2019 fiscal year, the German Marshall Fund received $1 million or more from both the German and Swedish foreign offices, at least $1 million from the US State Department, and $1 million or more from the United States Agency for International Development (USAID), a primary arm of the US government for fomenting regime change abroad.
The European Commission — which is the executive branch of the European Union — supported the German Marshall Fund to the tune of between $500,000 and $999,999.
Additional supporters of the German Marshall Fund include branches of the German and US government, anti-communist billionaire George Soros’ Open Society Foundations, NATO, internet giants like Google, the European Parliament, oil companies like Exxon, big agro companies like Bayer, large banks, and an array of global arms dealers such as Raytheon and Boeing.
The Theranos nanotainer of Russiagate online initiatives
The Alliance for Security Democracy’s bogus dashboard was undoubtedly the most-cited authority on Russian bot activity in the media. But its credibility suffered a major blow following a series of revealing remarks by founder Clint Watts, who confessed to Buzzfeed, “We don’t even think [all the accounts we monitor are] all commanded in Russia — at all. We think some of them are legitimately passionate people that are just really into promoting Russia.”
Having banked his credibility on fighting the supposedly pernicious presence of Russian bots, Watts went on to concede, “I’m not convinced on this bot thing.”
The ASD’s faulty methodology was developed by J.M. Berger and Jonathon Morgan. The latter was involved in orchestrating a false flag influence campaign targeting Alabama’s Senate elections, and was banned from Facebook after it was exposed. New York Times reporter Scott Shane, who reported on the disinformation campaign, was also responsible for hyping up the ASD’s supposed findings on the “take the knee” hashtag.
But among the ASD’s cadre of national security hacks, Clint Watts is perhaps the most shameless hustler. As The Grayzone’s Max Blumenthal previously reported, “Watts appears to speak no Russian, has no record of reporting or scholarship from inside Russia, and has produced little to no work of any discernible academic value on Russian affairs.”
In his published work, Watts has not only called for the US to “befriend” the “al-Qaeda linked group” Ahrar al-Sham; he also urged Washington to support “jihadi[s]” in order to deliver “payback” to Russia.
In testimony to Congress in 2017, Watts claimed Russia organized a massive bot attack on his Twitter account after his article urging support for al-Qaeda was published. The tale was not just hyperbole; it appeared to have been a fabrication. He also regaled Congress with a story about RT’s and Sputnik’s coverage of a stand-off at Turkey’s Incirlik Airbase that was completely false.
Clint Watts has admitted to running an influence operation for 15 years aimed at improving approval for US foreign policy in the Middle East, which he has said “had almost no success,” and came at a cost of “billions a year in tax dollars.”
While he hypes his work for the FBI, where he spent at most one year, Watts has spent much of his career at the Foreign Policy Research Institute, a hardline neoconservative think tank founded by an open white supremacist.
And left unmentioned in Watts’ bio is his affiliation with the Central Intelligence Agency: the Agency has published an article he co-authored with former CIA director and current CNN contributor John Brennan.
Besides producing dubious analysis, Clint Watts has exhibited a tendency for paranoid Cold War fantasies. In 2017, he warned an audience that Russia was “trying to knock us down and take us over,” then claimed that his colleagues had seen their computers “burned up by malware” after they criticized Russia.
In response to supposed Russian meddling, Watts has called for interfering in Russia’s elections, “but do[ing] it in line with the founding principles of democracy and America.”
He has also called for a government-imposed censorship campaign inside the United States, demanding it “quell information rebellions that can quickly lead to violent confrontations and easily transform us into the Divided States of America.”
Even as the Alliance for Securing Democracy was exposed by The Grayzone and others as the Russiagate version of the phony Theranos nanotainer – with Clint Watts playing the Cold Warrior analog to Elizabeth Holmes – the state-backed neo-McCarthyite operation has forged ahead, rebranding its dashboard as “Hamilton 2.0” and rolling out an “Authoritarian Interference Tracker.”
Currently, the ASD is hyping up claims by NATO vassal state Estonia about Russian interference in their country, according to its “Authoritarian Interference Tracker.” Coincidentally, former Estonian president Toomas Hendrik Ilves sits on ASD’s advisory council.
He is joined on the ASD board by Michael Chertoff, the notoriously self-dealing former Department of Homeland Security chief; and by John Podesta, who workshopped ways to “stick the knife” into Bernie Sanders while leading Hillary Clinton’s presidential campaign in 2016. Podesta was recently nominated to the 2020 Democratic Convention Rules Committee.
Also on the ASD advisory council is neoconservative extraordinaire turned liberal media’s favorite Never-Trumper Bill Kristol, who is widely acknowledged as the leading media and think tank influencer behind the US invasion of Iraq. Kristol has called for a deep state coup to depose Trump, and is rolling out a wave of ads to undermine Bernie Sanders.
Former CIA director Michael Morell, who offered unsolicited advice on killing Russians and Iranians in Syria during a televised interview, and the obsessively anti-Russian former US ambassador to Russia Michael McFaul also occupy seats on the council.
While the ASD couches its work as an attempt to counter Russian disinformation, a clear pattern has emerged of efforts to suppress domestic reporting in the US that doesn’t conform to the imperial foreign policy consensus.
As The Grayzone previously reported, senior German Marshall Fund fellow and neocon movement veteran Jamie Fly appeared to take credit for a purge of popular Facebook accounts of alternative media outlets including The Free Thought Project, Anti-Media, and Cop Block. He promised it was “just the beginning.”
Now, the Alliance for Securing Democracy has trained its guns on The Grayzone. And with its latest falsehood, this malign organization has targeted an independent journalistic organization that has done more than any other to hold it accountable.
Alexander Rubinstein has covered foreign policy, police, prisons, and protests for a variety of publications including The Grayzone and Mint Press News. Follow him on Twitter at @RealAlexRubi.
The Washington Mandarins and Veteran Disinformation Spooks Behind Stanford’s Internet Observatory
By Morgan Artyukhina | Sputnik | February 13, 2020
Stanford University’s Internet Observatory (SIO) is the latest in a growing network of cybersecurity groups policing the activities of social media users, pushing a pro-State Department line about Washington’s adversaries, and spreading the fear of disinformation that’s driving popular support for renewed conflict with Russia and other nations.
This article will pull back the veil on one of the fastest-growing institutions in the US Security State’s information war. Some of the observatory’s central figures include Facebook’s security chief during the Cambridge Analytica scandal, leading academic champions of Western triumphalism and US policy advisers, and even a lead researcher from a cybersecurity group previously exposed as being itself a disinformation outfit.
‘Rebuilding the Arsenal of Democracy’
Formed just this past summer, the observatory is attached to Stanford University’s Cyber Policy Center instead of a think tank like the Atlantic Council’s Digital Forensic Research Lab or operating as a for-profit cybersecurity company, like FireEye. In line with its more academic focus, SIO offers cybersecurity courses for students, such as program Director Alex Stamos’ popular “HackLab” course, “Trust & Safety Engineering,” and “Online Open Source Investigation,” as well as grants for full-time researchers and post-doctoral students, counting among its staff senior Stanford academics.
Startup funding for the Observatory came from Craig Newmark Philanthropies, a $5 million gift to fund nearly a dozen researchers for two years. Newmark, the billionaire founder of the website Craigslist, has quietly established a name for himself as another bankroller of State Department-approved media organs, alongside eBay founder Pierre Omidyar, oil tycoons the Koch brothers, and investor George Soros. Sputnik’s inquiries to Stamos about potential future funding sources were not returned by the time this story went to publication.
Newmark’s justification for supporting the Observatory serves as an effective summary of his efforts in this field:
“What we’re doing is rebuilding the arsenal of democracy,” he told Reuters in July 2019. On another occasion, Stanford quoted him as saying: “The strength of our democracy depends on ensuring that all people have access to accurate information. The Internet Observatory has a vision for a trustworthy Web, and I’m proud to support their mission-critical work to grapple with disinformation and other ways that bad actors use tech against the common good.”
Who’s Who at SIO
Heading up the outfit is Alex Stamos, the former security chief at Facebook and a visiting fellow at the conservative Hoover Institution think tank. Not only was Stamos in charge of Facebook’s cybersecurity during the Cambridge Analytica scandal in which some 87 million users had their personal information collected and used, most without their knowledge or consent, by companies intending on helping candidates like Donald Trump shape elections, but when he left Facebook in the summer of 2018 to form the SIO, Stamos’ departure was based primarily in his disagreement with other Facebook executives’ apprehension at surrendering so much user data to cybersecurity firms in their effort to track down supposed Russian political meddling on the site.
Meanwhile, its research team is headed up by Renée DiResta, a Mozilla fellow who’s lectured at events hosted by the arch-conservative Federalist Society. DiResta was also the research director at New Knowledge, ostensibly a cybersecurity outfit that disbanded after it was revealed they had played a deep role in an online disinformation campaign designed to influence the December 2017 Alabama special election in favor of Democratic candidate Doug Jones.
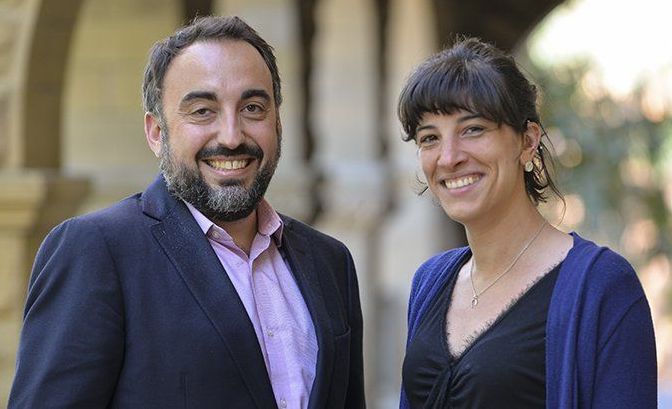
Stanford Internet Observatory Director Alex Stamos (left) and Research Manager Renée DiResta (right), Rod Searcey
While DiResta has sworn up and down that she knew nothing about the disinformation campaign being waged by New Knowledge chief Jonathon Morgan, at the time of the campaign she was also an Advisor on Policy at Data for Democracy, an informal cybersecurity brainstorming and collaboration network set up and coordinated by Morgan.
Other Stanford academics who’ve joined the SIO milieu include “end of history” proponent Francis Fukuyama and Hoover Institute fellows Amy Zegart and Michael McFaul, the latter of whom was also US Ambassador to Russia.
Further, the Stanford Cyber Policy Center’s codirector is Nate Persily, who founded Social Science One in April 2018 to do much the same as the SIO hopes to now: sort through petabytes of privacy-protected data on Facebook users to “investigate the spread of information and misinformation on Facebook, and their impact on elections and democracy,” as Wired put it in July 2018. Indeed, Wired noted Stamos hoped in setting up the Observatory to gain access to Facebook data via SSO.
“There’s an enormous number of questions you can ask about what 2 billion people around the world are clicking and reading and sharing,” Harvard University Institute for Quantitative Social Science director Gay King, who co-founded SSO with Persily, told Wired. The group receives funding from Omidyar-connected groups such as the Knight Foundation, Democracy Fund and the Omidyar Network, as well as the Charles Koch Foundation of conservative oil tycoon fame.
DiResta’s Proximity to Disinformation Electioneering
DiResta became embroiled in this disinformation cauldron as early as November 2016, when she met Mikey Dickerson, a former Obama administration official who served as the first head of the US Digital Service, which managed US government websites and who, according to the Washington Post, “expressed a desire to fight back” against Trump’s election victory.
“There was a feeling after the Trump election that Democrats hadn’t prioritized tech, that Republicans had built this amazing juggernaut machine,” DiResta told the Post in January 2019. “The right wing was running a meme war, and there were these crazy dirty tricks. People wanted to build countermeasures.”
Facebook banned the account of Jonathon Morgan, the CEO of New Knowledge, a cyber firm that meddled in Alabama’s 2017 special election.
Soon after, Dickinson founded American Engagement Technologies (AET), which later played a pivotal role in the Alabama special election, coordinating a massive effort to impersonate Republicans in an effort to discourage Alabamans from voting for Republican candidate and slavery and pedophilia defender Roy Moore. AET was bankrolled by LinkedIn founder Reid Hoffman, who sunk $750,000 into AET, $100,000 of which was used by Dickinson to hire New Knowledge. New Knowledge, in turn, coordinated Project Birmingham, the name of the disinformation effort, as documents obtained by the Washington Post show.
Hoffman has emerged again in recent news as the money behind ACRONYM, the group who sabotaged the February 2020 Iowa Democratic Caucus results in an operation noted by observers to be very similar to that concocted by New Knowledge, including attempting to frame Russians for the interference.
DiResta, in turn, advised AET before it obtained Hoffman’s backing, migrating to New Knowledge in the aftermath of the Alabama campaign, pledging to the Post she knew only of “an experiment in Alabama” but disavowing knowledge of their tactics.
However, DiResta had also joined Morgan startup group Data for Democracy as the group’s Policy Lead in August 2017, a nonprofit network of roughly 1,200 hackers founded by Morgan the previous December to “use data and technology for social impact,” according to its LinkedIn profile, especially “election integrity, disinformation & social network manipulation, transparency, and policy initiatives.” Between these three connections, it seems increasingly unlikely she knew nothing of the tactics behind Project Birmingham – indeed, she had already professed sympathy with just such efforts to “fight back” against Trump.
The Pesky Problem of Privacy
Stamos, in an interview with Reuters, said pressures on Facebook to protect user privacy are making it harder to see and combat misuses on the platform, such as disinformation and election interference.
“The ability to do academic research on what’s happening online has never been worse,” Stamos told Reuters in a July 2019 interview. “What you get is everything encrypted and everything locked up and not available to researchers.”
He specifically blasted the Federal Trade Commission settlement requiring Facebook’s board to create an independent privacy committee and to have greater oversight over third-party apps on its platform, saying the skittishness it creates around sharing users’ data with research groups would be “a blow for the public’s understanding of social media manipulation,” as Reuters summarized it.
Building a ‘Data Clearinghouse’
Indeed, now that Stamos has moved from security chief to academic, he’s renewed his pressure on tech giants to hand over user data for “academic” purposes, successfully winning backdoor access to user and ad data via API gateways from Facebook, Google, and Bing, turning the SIO into what Wired called “his data clearinghouse.”
At the time this article went to publication, Stamos had not answered inquiries by Sputnik about the other social media giants Wired noted the Observatory was courting for API access, including Twitter, YouTube and Reddit.
‘For $5,000 I Can Buy A Whole Lot of Speech’
Like Stamos, DiResta has a history of distrusting online people-to-people networks. In September 2018, she appeared on a panel titled, “Is Social Media a Threat to Democracy? Fake News, Filter Bubbles, and Deep Fakes,” at which she blasted Twitter for enabling “more speech” with its autofill retweet function, noting that “for $5,000 I can buy a whole lot of speech.”
That event, the Reboot 2018 Conference in San Francisco, was hosted by the Federalist Society, perhaps the country’s premier elite club for the Establishment Right, counting so many leading DC policymakers, diplomats and federal judges – including more than half of the Supreme Court – that in January 2019, Washington Post Magazine opined that the Federalist Society had reached an “unprecedented peak of power and influence.”
In describing the panel’s focus, the event handout noted that “Social media companies are under increasing scrutiny for their effect on American society. According to critics, these platforms promote hyper-partisanship, disinformation, extremism and even violence. They are also blamed for facilitating Russian-sponsored voter manipulation during the 2016 election. Our panel of experts will discuss these challenges as well as their implications for the upcoming election.”
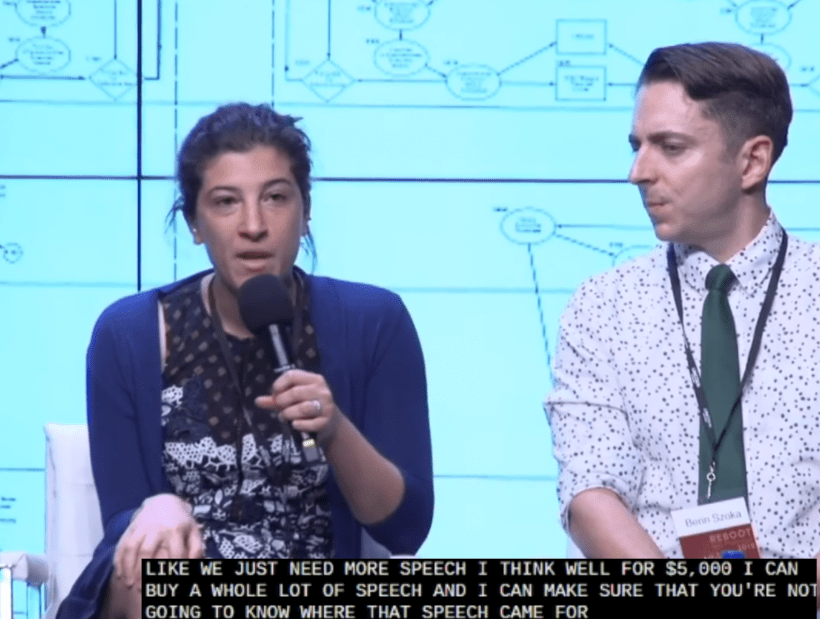
Renee DiResta speaking at Reboot 2018 Conference in San Francisco, October 2, 2018, Sputnik Screenshot
Pruning Facts: Be More Like Google!
Since its formation, the Observatory has rushed to embrace the standard of “Russian disinformation campaigns,” turning out several reports ostensibly documenting such efforts in Africa, and also attacking Bing for failing to prune their search results of pro-Russian links.
While the SIO purports to have identified “Evidence of Russia-Linked Influence Operations in Africa,” as the title of an October 2019 report suggests, in truth they offer nothing but insinuation and supposition. The report itself admits they “cannot independently verify” their most contentious claim, that the Russian security contractor “Wagner Group” is behind a supposed “Facebook operation” in Libya.
Further, the extent of their proof of “Russia-linked organizations likely operating at least in part at the behest of a state actor” that shared “tactical similarities to Internet Research Agency activities” extends to little more than native-speakers speaking well of local initiatives tied to the Russian government and Facebook pages that “often re-posted Sputnik articles.” Quelle horreur!
This is the same kind of suggestive wording obfuscating ignorance that FireEye and the Atlantic Council’s DFRL have employed in claiming to identify disinformation campaigns by US targets for regime change, including Russia but also Venezuela, Iran, and China, among others.
For example, as Sputnik has reported, during the regular purges carried out by Twitter and Facebook, the cybersecurity reports used to justify the purges routinely enjoyed only moderate or low confidence by the researchers, and in at least one instance in May 2019, Twitter Site Integrity chief Yoel Roth was forced to admit they never looked at FireEye’s report before summarily deleting 2,800 accounts “linked to Iran.”
In another report in December 2019, the SIO faulted Microsoft default search engine Bing for failing to prune its search results as efficiently as Google does, specifically naming higher-ranked links to Sputnik and RT stories on search terms like “novichok,” “Skripal,” and “MH17” as a problem.
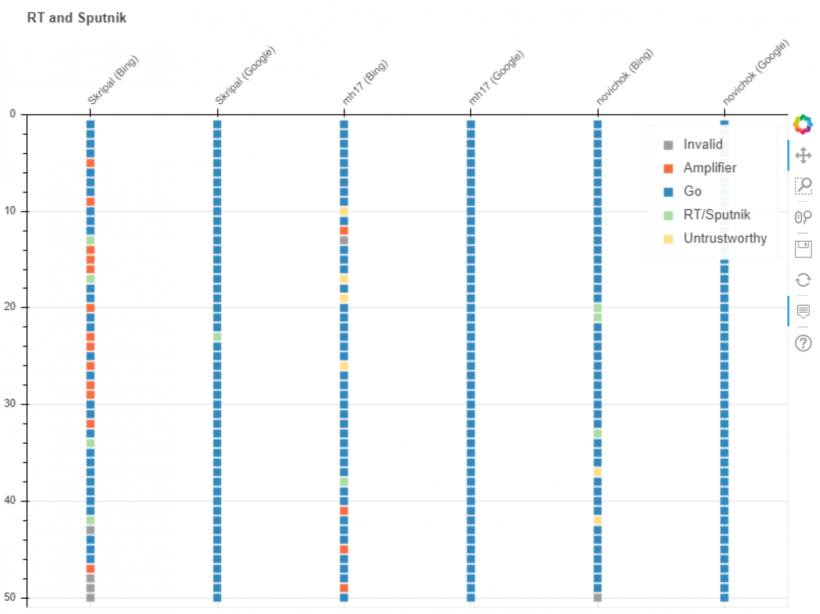
A graphic from a December 2019 report by the SIO showing RT and Sputnik in search results for “skripal” “MH17” and “novichok” on Bing and Google, Stanford Internet Observatory
In an interesting moment of frankness, the SIO admits that Google does, in fact, manually prune its search results – something the tech giant has long maintained it doesn’t do. A November 2019 report by the Wall Street Journal confirmed what documents leaked to the Daily Caller the previous April had hinted at: that Google intervenes directly to “correct” algorithms that yield politically undesirable search results.
“Over time, Google has increasingly re-engineered and interfered with search results to a far greater degree than the company and its executives have acknowledged,” the WSJ wrote, noting the efforts had increased sharply since the 2016 US elections. The litany of manipulations range from “algorithmic changes to its search results that favor big businesses over smaller ones” to making “behind-the-scenes adjustments” to “auto-complete suggestions, boxes called ‘knowledge panels’ and ‘featured snippets,’ and news results, which aren’t subject to the same company policies limiting what engineers can remove or change.”
“Despite publicly denying doing so, Google keeps blacklists to remove certain sites or prevent others from surfacing in certain types of results,” the WSJ report continues. “These moves are separate from those that block sites as required by US or foreign law, such as those featuring child abuse or with copyright infringement, and from changes designed to demote spam sites, which attempt to game the system to appear higher in results.”
From ‘Fake News’ to ‘Disinformation’
The language deployed in the SIO report is also interesting, in that it categorizes stories forwarding a point of view differing from the US State Department’s line alongside conspiracy theory links about Pizzagate, links between vaccines and autism, and white supremacist content, as if they were all just flavors of “fake news” to be purged in the defense of “real” news.
Although US President Donald Trump is credited with popularizing the slander, “fake news” is a narrative swallowed hook, line and sinker in recent years by both tech giants and the billionaire investors who bankroll their growing media networks. For example, in 2015, Craig Newmark Philanthropies joined the Omidyar-backed Knight Foundation, the George Soros-funded Open Society Foundations and the Ford Foundation to back Google’s First Draft News and the Google News Lab, projects that aimed to coordinate “efforts between newsrooms, fact-checking organizations, and academic institutions to combat mis- and disinformation.”
As MintPress News documented, these efforts are just drops in the bucket of a much larger project involving every major US-based tech giant to shape media narratives around the globe to reflect the US State Department line, adopting common definitions of disinformation that dismiss alternative points of view as assaults upon reality.
“Fake news” has dovetailed with “disinformation” to provide a convenient excuse to extend state control over the realm of cyberspace, and the SIO is just the latest instrument in a growing symphony of thought policing.
Are DNC insiders weaponizing ‘election security’ to seize control of 2020 primaries?
By Helen Buyniski | RT | February 12, 2020
Google and a dodgy “election security” nonprofit are reaching out to Democratic campaigns with free security tools, even offering to activate them. After the Iowa debacle, campaigns should be wary of DNC insiders bearing gifts.
Election security nonprofit Defending Digital Campaigns (DDC) has partnered with Google to offer free Titan security keys to Democratic presidential campaigns. Not only will these benevolent guardians of the democratic process let the candidates have the keys, part of Google’s Advanced Protection security program, free of charge – they’ll even install and activate the new security systems themselves! What could go wrong?
Candidates would be wise to think twice about accepting the seemingly-generous offer, or any other “free election security” bait, especially after the disaster of the Iowa caucuses. That vote collapsed not because of a foreign hack, but because Shadow Inc., an organization staffed almost entirely by former Hillary Clinton operatives, sold Iowa Democrats a difficult-to-use app that mangled vote counts. While Shadow was supposedly “vetted for cybersecurity and technical considerations” by “third-party experts,” many of the security “experts” peddling their services to the Democrats are veterans of the same Clinton and Obama campaigns as Shadow’s staff. And of course the 2020 Democratic National Committee, which insisted Iowa use an app to report results instead of calling them in by phone for security reasons, is positively bristling with insiders left over from 2016.
Defending Digital Democracy, the “security experts” Iowa Democrats were already paying to train volunteers in electoral “worst case scenarios,” is – unsurprisingly, given the name – run by the same Clinton and Romney staffers who sit on Defending Digital Campaigns’ board, Robby Mook and Matt Rhoades. Founded by former Obama Pentagon Chief of Staff Eric Rosenbach and advised by top Clinton lawyer Marc Elias, DDD has been “protecting” elections with the help of CrowdStrike founder (and Russiagate Patient Zero) Dmitri Alperovich since 2017. The Fear of Russian Meddling industry appears to be one big happy family, none of whom, it seems, have ever heard of paper ballots – one sure-fire way to avoid outside interference in an election.
The links between the various groups are extensive and complex enough to fill several articles, but looking at their financial backers is instructive. Shadow and DDC were both bankrolled by LinkedIn co-founders – Reid Hoffman provided the startup capital for Shadow’s parent corporation Acronym, while DDC’s treasurer and largest donor is Allen Blue. Hoffman also provided the financing for “disinformation experts” New Knowledge’s phony Russian bot operation in Alabama in 2017, which – if its own numbers are to be believed – handed the traditionally-red state’s open Senate seat to Democrat Doug Jones by weaponizing fear of Russian meddling.
There’s no stronger proof that all this “election security” talk is mere pageantry than in the DNC’s appointment of former Clinton campaign director John Podesta to the 2020 convention’s Rules Committee. Podesta has no business being anywhere near election security – it was his inability to recognize “phishing” that led to the Clinton campaign’s emails being spread all over the internet by Wikileaks in the runup to the 2016 election. Podesta, like Mook, has been aggressively pushing the threat of Russian election interference ever since, absent a shred of proof that the dreaded “meddling” is coming from anywhere but inside the country.
Some naive individuals might question whether party insiders would really try to steal another primary after the catastrophe of 2016 handed Trump his victory. But those responsible for that trainwreck were never punished, defending themselves in court with the rationale that party bylaws allowed them to pick candidates in smoke-filled rooms should they so desire. Moreover, nothing has come of the revelation former South Bend mayor Pete Buttigieg’s campaign paid $40,000 to Shadow before the company’s app nearly handed him victory in Iowa, or that parent company Acronym’s CEO is happily married to a Buttigieg staffer. Worse, last week it emerged that Buttigieg staffer Emily Goldman has signed on to the Nevada Democratic Party as “voter protection director” – a full-time position – now that Nevada has dropped the Shadow app for its own caucus.
Yet calls for DNC chair Tom Perez to resign, motivated by all these scandals and more, have fallen on deaf ears. Knowledge of the metastasizing conflicts of interest within the party has merely circulated on social media to the point where few in its progressive wing believe a fair election is possible. Inviting Google – which was 100 percent in the bag for Clinton in 2016, according to whistleblowers and researchers alike – and yet another Russia-obsessed, insider-heavy “election security” group to install free “protection” in one’s campaign infrastructure is inviting the local foxes to install security for one’s shiny new henhouse. Unless a candidate is secure in being the establishment’s pick, they would be wise to leave this Trojan horse outside the gates.
New leaks shatter OPCW’s attacks on Douma whistleblowers
By Aaron Maté | The Grayzone | February 11, 2020
For the past year, the Organization for the Prohibition of Chemical Weapons (OPCW) has been roiled by allegations that it manipulated an investigation to falsely accuse the Syrian government of a chemical weapons attack. An OPCW report released in March 2019 lent credence to claims by Islamist militants and Western governments that the Syrian military killed around 40 civilians with toxic gas in the city of Douma in April 2018. The accusation against Damascus led to U.S.-led military strikes on Syrian government sites that same month.
But leaked internal documents published by WikiLeaks show that OPCW inspectors who deployed to Douma rejected the official story, and complained that higher-level officials excluded them from the post-mission process, distorted key evidence, and ignored their findings.
After months of virtual silence, the OPCW has responded with an internal inquiry that lambasts two veteran officials who raised internal objections, attacking their credibility and qualifications. The OPCW’s self-described “independent investigation” describes the pair as rogue, low-level actors who played minor roles in the Douma mission and lacked access to crucial evidence. In a briefing to member states, OPCW Director General Fernando Arias dismissed them as disgruntled ex-employees. The two “are not whistle-blowers,” Arias said. “They are individuals who could not accept that their views were not backed by evidence.”
But a leaked document calls Arias’s assertions into serious question. Ian Henderson, one of the two inspectors, recently addressed a special session of the United Nations Security Council with his concerns about the Douma mission. Henderson submitted a supplemental written account that was distributed among participating UN member states and obtained by The Grayzone. It offers the most extensive and detailed account of the internal dispute over the OPCW’s Douma investigation to date.
The full leaked testimony can be read here (PDF).
Henderson provides a thorough timeline that bolsters suspicions that the OPCW leadership covered up a staged deception in Douma. Combined with the available record – which includes other OPCW leaks, as well as Arias’s and the OPCW’s own statements – Henderson’s account firmly demonstrates that he and a fellow dissenting colleague occupied veteran leadership roles inside the organization, including during the Douma fact-finding mission.
Henderson also exposes key gaps in the OPCW’s inquiry, which fails to specifically address the revelations that critical evidence was kept out of the OPCW’s published reports; that key findings were manipulated – and that all of this occurred under sustained U.S. government pressure.
In addition to Henderson’s complete testimony, The Grayzone has obtained a chilling email from a third former OPCW official. The former official, who worked in a senior role, blamed external pressure and potential threats to their family for their failure to speak out about the corruption of the Douma investigation.
This official was not among the pair of dissenting inspectors targeted by the inquiry. The email corroborates complaints by Henderson and his colleague about senior management’s suppression of evidence collected by the team that deployed to Syria.
‘I Fear Those Behind the Crimes’
In his briefing about the investigation of the inspectors, Arias, the OPCW director-general, described the pair as stubborn actors “who took matters into their own hands and committed a breach of their obligations to the Organization.” He characterized their behavior as “egregious.”
But leaked documents and testimony point to an OPCW leadership that has committed egregious acts of its own, including intimidating internal dissenters.
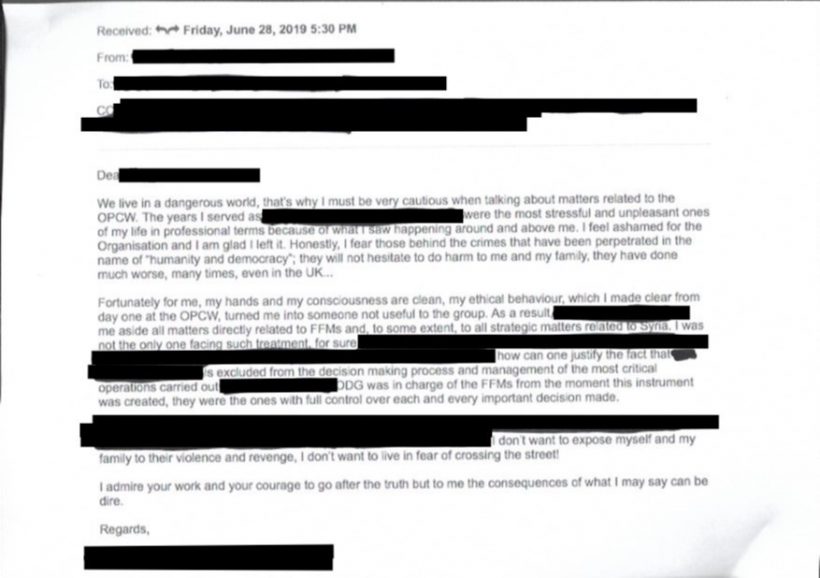
In an email obtained by The Grayzone,a former senior OPCW official described their tenure at the OPCW as “the most stressful and unpleasant ones of [their] life,” and expressed deep shame about the state of the organization they departed in disgust.
“I fear those behind the crimes that have been perpetrated in the name of ‘humanity and democracy,’” the official confided, “they will not hesitate to do harm to me and my family, they have done worse, many times, even in the UK… I don’t want to expose myself and my family to their violence and revenge, I don’t want to live in fear of crossing the street!”
The former OPCW senior official went on to denounce the removal of members of the original fact-finding team to Syria “from the decision making process and management of the most critical operations…” This tracks with complaints expressed in leaked OPCW documents that superiors who had not been a part of the investigation in Douma marginalized those who had.
The atmosphere of intimidation was confirmed by a second member of the OPCW’s original fact-finding mission to Douma. The whistleblower, identified by the pseudonym “Alex,” spoke to the journalist Jonathan Steele and to a panel convened by the Courage Foundation in October 2019. Alex revealed that a delegation of three U.S. officials visited the OPCW at The Hague on July 5, 2018. They implored the dissenting inspectors to accept the view that the Syrian government carried out a gas attack in Douma and chided them for failing to reach that conclusion. According to Steele, Alex and the other inspectors saw the meeting as “unacceptable pressure.” In his statement to the UN Security Council, Henderson confirmed that he attended the meeting.
The U.S. intervention at the OPCW could possibly violate the chemical weapons convention, which forbids state parties from attempting to influence investigations. It would not be the first time Washington has attempted to bully the OPCW into submission. In 2002, during the run-up to the invasion of Iraq, the George W. Bush administration engineered the ouster of the OPCW’s first director-general, Jose Bustani. The Bush administration was concerned that Bustani’s negotiations with Iraq about allowing international inspectors could undermine its plans for war.
Bustani later revealed that John Bolton, then an under secretary of state, had personally threatened him and his family with violent retaliation. The U.S. pressure on the OPCW over Douma also took place under Bolton’s watch. When the U.S. bombed Syria in April 2018 and pressured OPCW officials just three months later, Bolton was in the midst of his first months as President Donald Trump’s national security adviser. (Bustani, meanwhile, was among a group of panelists who heard direct testimony from Alex at a gathering convened by the Courage Foundation in October 2019.)
OPCW’s Inconsistency on ‘Inspector A’
The OPCW’s internal inquiry goes to great lengths to denigrate and discredit the two former staffers who challenged the official story on Douma. It refers to its two targets as “Inspector A” and “Inspector B.” The latter’s identity has not been publicly confirmed. “A” is Ian Henderson, a South African engineer and veteran OPCW official with extensive military experience.
Henderson’s written testimony to the United Nations, obtained by The Grayzone, undercuts the negative portrayal of his former managers, and offers a window into the pressure campaign and cover-up that he and his colleagues faced.
A suppressed internal study by Henderson first brought the OPCW scandal to public attention. In May 2018, an engineering assessment bearing Henderson’s name was leaked to a group of British academics, the Working Group on Syria, Propaganda and Media. The document is a detailed engineering analysis of two gas cylinders found at the scene of the alleged attacks in Douma. Whereas the OPCW’s final March 2019 report concluded that the cylinders were likely dropped from the air, Henderson found that there is “a higher probability that both cylinders were manually placed… rather than being delivered from aircraft.” The OPCW’s final report made no mention of this conclusion.
The inference of Henderson’s study is that the attack was staged by the armed opposition. At the time, Douma was under the control of the extremist Saudi-backed militia, Jaysh Al-Islam, and was on the brink of being re-taken by Syrian government forces.
From a political and military standpoint, a chemical weapons attack was the most self-destructive and unnecessary action the Syrian military could possibly take. From the standpoint of a foreign-backed militia on the verge of defeat, however, staging a chemical attack was a desperate Hail Mary operation that offered the hope of U.S. military invention in accordance with Washington’s “red line” policy. The suspected gambit by Jaysh Al-Islam appeared to have paid off when the Trump administration accepted its claims that a chemical attack had killed dozens of civilians in Douma, and initiated cruise missile strikes in response. Yet the U.S.-led attacks failed to prevent the Syrian government from retaking Douma and the whole of eastern Damascus. Within days, Western reporters had entered the area and were able to access local eyewitnesses who claimed that the chemical attack was a staged deception.
Henderson was among the first OPCW staffers to visit the site of the alleged attack in Douma. However, the OPCW inquiry dismissed Henderson’s role in the Douma probe, characterizing his engineering study as a personal, rogue operation. Henderson, the inquiry said, “was not a member of the FFM [Fact Finding Mission]” that deployed to Douma, and only “played a minor supporting role.”
There is ample evidence that contradicts this characterization. In his written UN testimony, Henderson revealed that he served in five Douma deployments as part of the FFM. This includes three instances as a sub-team leader for critical operations: visiting a suspected chemical weapons production site in Douma; conducting interviews and taking chemical samples at the Douma hospital; taking detailed measurements at one of the sites; and inspecting, itemizing, and securing the two cylinders that were removed from the sites of the alleged gas attack. The notion that he “was not a member” of the mission that he played such an active role in strains credulity.
A leaked email shows that at least one of Henderson’s colleagues protested a previous instance in which the OPCW leadership attempted to minimize his role. The “falsehood… that Ian did not form part of the Douma FFM team,” the colleague complained, was “patently untrue” and “pivotal in discrediting him and his work.”
The inquiry also falsely insinuated that Henderson was a low-level official. While acknowledging that Henderson served as an OPCW team leader during his first tenure with the OPCW from 1997 to 2005, the inquiry said that he was “rehired at a lower level” when he returned in 2016, and remained there until his departure in May 2019. Yet the OPCW’s own documents from that latter period showed that Henderson was described as an “OPCW Inspection Team Leader” as late as February 2018, just two months before his deployment to Douma as part of the OPCW’s Fact-Finding Mission (FFM). According to his UN testimony, Henderson served as an inspection team leader for multiple inspections of Syrian laboratory facilities at Barzaeh and Jamrayah in November 2017 and in November 2018, after the U.S. bombed Barzeh on dubious grounds.
After casting doubt on Henderson’s status within the organization, the OPCW inquiry dismissed his engineering report as “a personal document created with incomplete information and without authorisation.” Henderson, the investigators said, defied higher-level officials’ orders and conducted a study on his own with outside contractors.
In his briefing to member states on the inquiry’s findings, OPCW Director General Fernando Arias echoed this conclusion, describing Henderson’s report as “a purported document disseminated outside the Organisation.”
But Arias’ statements today contradict his own words from less than a year ago. Just days after Henderson’s report was leaked in May 2019, Arias delivered an extensive briefing and announced that an inquiry into the disclosure was underway. Arias made no claims of Henderson going rogue, and described his report as an “internal document… produced by a staff member.” It is unclear how Henderson’s report went from an “internal document” by an OPCW staffer in May 2019 to a “purported document disseminated outside the Organisation” in February 2020. Arias has not explained this discrepancy.
In his latest missive, Arias has offered a completely new rationale for keeping Henderson’s report from the public. In May 2019, Arias stated that because Henderson’s report “pointed at possible attribution,” it was therefore “outside of the mandate of the FFM [Fact-Finding Mission] with regard to the formulation of its findings.” The FFM is prevented from assigning blame to parties involved in chemical attacks. However, the OPCW’s published conclusion suggested the Syrian government was to blame for the attack – an act of attribution – since the Syrian military (or its Russian ally) was the only warring party in Douma with aircraft. Even more curiously, by accusing Henderson of freebooting and “subterfuge,” Arias and his organization’s independent inquiry has now offered a completely different explanation than it previously had for the omission of Henderson’s report.
Why Was Critical Evidence Excluded?
In yet another highly dubious assertion, the OPCW inquiry claimed Henderson “did not have access to all of the information gathered by the FFM team, including witness interviews, laboratory results, and assessments by independent experts regarding the two cylinders — all of which became known to the team after [Henderson] had stopped providing support to the FFM investigation.”
But an important piece of context is missing from this salvo: by the time Henderson carried through on his study in summer 2018, he and other members of the FFM had already complained to the OPCW leadership that their findings were being manipulated and suppressed.
According to Henderson’s testimony, a draft interim report circulated in June 2018 was subjected to “last-minute unexpected modifications” that were “contrary to the consensus that had been reached within the team.” This included a change to “reflect a conclusion that chlorine had been released from cylinders,” which was not consistent with the findings at that stage. An intervention by one of the FFM team members, possibly Inspector B, forced FFM team leader Sami Barrek to revise the interim report before its eventual release on July 6, 2018.
Despite agreeing to hear his team’s objections, Barrek personally blocked critical evidence that conflicted with the official story of Syrian government responsibility. One email chain revealed that Barrek resisted pleas from an inspector to include the relatively low levels of chemicals found in Douma. Alex, the anonymous second OPCW whistleblower, told journalist Jonathan Steele that chlorinated organic chemicals at the scene “were no higher than you would expect in any household environment.”
Another leaked document showed the OPCW had consulted with toxicologists in June 2018 to determine whether symptoms observed in victims were consistent with exposure to chlorine. According to minutes of that meeting, “the experts were conclusive in their statements that there was no correlation between symptoms and chlorine exposure.” But these critical findings, which dramatically undercut the official narrative, were inexplicably omitted from both the interim and final report.
‘Core’ Cover-up Team
One day after U.S. officials attempted to bully OPCW staff into submission on July 5, 2018, an interim report on Douma was published that reflected some of the inspectors’ key objections, albeit with watered-down language and significant omissions. A critical change then took place. OPCW officials announced that the ensuing final report would be drafted by a “core team” that was separate from the one which deployed to Douma. That left the core team without any of the FFM members who had been on the ground at the site of the supposed attack, with the exception of one paramedic. Henderson told the UN that the move deprived the core team of anyone qualified to conduct the needed engineering assessments on the chlorine cylinders that were said to have been dropped in Douma.
With superiors omitting critical information, Douma inspectors excluded from the so-called “core” team, and U.S. officials applying direct pressure, Henderson attempted to carry on with his report. Despite the inquiry’s claims, Henderson presented evidence to the UN that his work was approved by his superiors. Henderson reported that he held several meetings with top OPCW officials beginning in late summer 2018, where he informed them of his study and relayed concerns about the methodologies of the then-FFM team leader. Henderson said he was told by the then-Chief of Cabinet Sebastien Braha: “I don’t see why both studies can’t be done.” Henderson took that as a green light.
Henderson completed his engineering study in January 2019 and submitted a “detailed executive summary” for peer review. OPCW colleagues, including members of the Douma FFM, an unidentified former “core team” former inspector, and other “trusted [Technical Secretariat] staff members who had expertise in specific areas,” studied Henderson’s work and offered written feedback.
“This review was considered necessary and responsible,” Henderson wrote, “in that I knew (after the analysis had been completed) that these would be unpopular findings; therefore, I wanted to make sure there were no objections to any of the facts, observations, methodology used or findings reported in the summary.”
In its bid to portray Henderson’s engineering study as the work of a disconnected freelancer, the OPCW’s inquiry strangely made no mention of this peer review.
When he met with FFM team leader Sami Barrek the following month, Henderson ran into more obstructions. Barrek flatly rejected Henderson’s report, “stating that he had been instructed not to accept it.” Alarmed by the possibility that the OPCW would soon release a final report without a sound engineering assessment, Henderson submitted a physical copy to the OPCW’s Documents Registry Archive, and alerted management by email.
It was then that another hostile response arrived from above. Braha, the chief of cabinet, emailed back an order: “Please get this document out of DRA (Documents Registry Archive) … And please remove all traces, if any, of its delivery/storage/whatever in DRA.”
Days later, on March 1, 2019, the OPCW’s final report was released. Omitting Henderson’s engineering findings, it reached a conclusion that contradicted that of its own inspectors. According to the report, the investigation found that there were “reasonable grounds that the use of a toxic chemical as a weapon took place…This toxic chemical contained reactive chlorine.” For its analysis of the cylinders, the report claims it relied on “three independent analyses” without specifying them and only directly citing one.
This raises an ineluctable question: why did the OPCW rely on three unspecified “independent analyses” from outside experts who never set foot in Douma, rather than on the evidence-based reports of a veteran OPCW staffer and his colleagues who investigated the site of the supposed attack? The OPCW has yet to offer an explanation.
“I was shocked by the decision to release the report without having taken into account the engineering report, as all the FFM management knew it had been submitted,” Henderson recounted in his UN testimony. “I had expected the report to reflect the situation that had been the consensus of the Douma FFM team after the deployments, and for the assessment of the cylinders to be consistent with the findings of the engineering assessment, but found the complete opposite. I saw what I considered to be superficial and flawed analysis in the section on the cylinders.”
Henderson tried to resolve his concerns internally. He met with at least six high-level officials, and sought a meeting with Arias. A senior manager angrily rebuffed that request, telling Henderson that “you will never get to the director-general, and if you try and go around me to get to him, there will be consequences.” Henderson also submitted a detailed dossier outlining his concerns to the acting director of the Office of Internal Oversight, which was later rejected.
Perhaps most critically, Henderson sought a meeting where the drafters of the FFM report – the “core” team that had excluded all but one member of the team that visited Douma – “would explain what new information had been provided or new analysis conducted, that had turned around the situation from what had appeared to be clear at the end of deployments to Douma.”
Henderson also requested an opportunity to hear from the “three experts” who had conducted the engineering studies cited by the FFM’s final report. “This would be a technical discussion, comparing the information and inputs used and methodology applied, and interpretation of results, and would very quickly identify any flawed approaches and would help clarify the situation,” Henderson recalled.
“Throughout this period, I acknowledged there was a possibility that I could be wrong, but stressed that I was not the only one with concerns,” he added. “Investigating the situation would bring things to light and potentially defuse the situation.”
But Henderson’s requests were denied. “Whilst many in management were shocked and concerned, and all expressed sympathy with my concerns,” Henderson told the UN, “the responses I received included ‘this is too big;’ ‘it’s too late now;’ ‘this would not be good for the [Technical Sectrariat’s] reputation;’ ‘don’t make yourself a martyr;’ and ‘but this would play into the Russian narrative.’”
A leaked memo written by Henderson to Arias, the OPCW director general, in March 2019, captures his contemporaneous objections. The final report, Henderson wrote, “does not reflect the views of all the team members that deployed to Douma,” a view he said was shared by about 20 inspectors. (Alex relayed a similar account to Jonathan Steele: “Most of the Douma team felt the two reports on the incident, the Interim Report and the Final Report, were scientifically impoverished, procedurally irregular and possibly fraudulent.”) On top of the fact the report was written by a “core” team that excluded all but one Douma inspector, Henderson complained that its authors “had only operated in Country X” – believed to be Turkey.
Arias instructed Henderson to submit his report to the newly formed Investigation and Identification Team, which had been mandated to further investigate the Douma attack. The IIT met with Henderson in March 2019 and accepted a copy of his report. But two months later, Henderson was suspended and removed from the OPCW building after a leaked copy of his engineering assessment was published on the internet. The OPCW’s inquiry does not accuse Henderson of responsibility for the leak.
Conspicuous Claims About ‘Inspector B’
Less is known about “Inspector B,” the second OPCW inspector targeted by the inquiry. It is possible, though unconfirmed, that B is the same person as “Alex,” the aforementioned Douma team member turned whistleblower. Like Henderson, B has been with the OPCW since its formation. The inquiry notes that B initially served from July 1998 to December 2011, including as Team Leader, and then again from September 2015 until August 2018.
As with Henderson, the inquiry attempted to portray Inspector B as a marginal figure in the Douma inquiry who went rogue after he had left the OPCW. While acknowledging that he was a member of the FFM team that deployed to Syria in April 2018, the report said that B “never left the command post in Damascus,” and therefore did not visit Douma.
By the OPCW’s own standards, however, that was hardly disqualifying: Sami Barrek, the FFM team leader, was only in Damascus for three days and departed before his team members – including Henderson – first reached Douma. Yet Barrek was tasked with drafting the final report, and, as leaked emails show, faced internal complaints that he excluded critical evidence.
According to the Working Group, the British academic collective that received and published Henderson’s leaked report, Barrek subsequently visited Turkey where he met with members of the White Helmets. The White Helmets are a Western government-funded organization known for carrying out rescue operations in areas under the control of foreign-backed anti-government militias. As The Grayzone has reported, the U.S.- and U.K.-funded White Helmets have operated alongside extremist militants during Syria’s proxy war, and been used for propaganda efforts to promote U.S. military intervention and sanctions on Syria. In the case of Douma, the White Helmets participated in a staged video to create the appearance that a local hospital was treating victims of a chemical attack.
Conspicuously, the inquiry offered no specifics on what “Inspector B” did in Damascus or his role in the FFM. This omission could be seen as an indication that an accurate description of his role would reveal that he played a significant one. The inquiry noted that he “was involved in the drafting of the interim report on the Douma incident” – but did not offer further details. It seems unlikely that someone with a limited role in the investigation would have been entrusted to participate in drafting the public report on its findings.
As with its portrayal of Henderson, the inquiry claimed that the FFM “undertook the bulk of its analytical work, examined a large number of witness interviews, and received the results of sampling and analysis,” in the months after Inspector B was no longer involved. But it had nothing to say about Inspector B departing only after raising concerns that the Douma team’s analytical work was manipulated and excluded, including on vital chemical samples. Accordingly, the fact that more work was done after B’s ouster did not resolve his concerns; if anything, it only raised further questions about the OPCW’s faulty final product.
Western Media Outlets Complicit in Cover-up
The OPCW’s unprecedented rebuke of two career officials has received a warm reception in mainstream media outlets that have carefully ignored the OPCW scandal to date, turning a blind eye as one explosive internal document after another appeared on WikiLeaks.
Though the scandal was itself a product of disclosures by the OPCW’s own staff, The Guardian bizarrely described it instead as “a Russia-led campaign” that has now “been dealt a blow” by the OPCW’s inquiry. The New York Times published reports by Reuters and the Associated Press that also aired the inquiry’s conclusions without a scintilla of critical scrutiny.
At a time when whistleblowing is supposed to be held in high esteem, the Western political and media establishment’s flagrant disinterest and disregard for the two dissenting inspectors and the explosive leaked documents is glaring. This carries significant dangers.
As the email by a “former senior official at the OPCW” – someone who was not among the pair of dissenting inspectors – made clear, fear within the organization is almost as profound as the pressure to self-censor and conform to the dominant narrative.
The experience of the OPCW’s first director-general, Jose Bustani – who was ousted from his position after direct threats from John Bolton to him and his family – attests to the threats these new whistleblowers face. When Bustani heard Alex’s testimony, he came away from the meeting firmly convinced that something had gone extremely wrong at the OPCW.
“The convincing evidence of irregular behaviour in the OPCW investigation of the alleged Douma chemical attack confirms doubts and suspicions I already had,” Bustani said after the session. “The picture is certainly clearer now, although very disturbing.” Bustani added that he hoped the Douma revelations “will catalyse a process by which the [OPCW] can be resurrected to become the independent and non-discriminatory body it used to be.”
In his statement to the United Nations, Henderson echoed this sentiment. The ousted expert called on the United Nations to allow for a scientific, peer review process to weigh his report against the three “independent experts” whom the OPCW claimed to rely on for its final report. The “method of scientific rigour,” Henderson wrote, “dictates that one side cannot profess to be the sole owner of the truth.
“Should an independent scientific panel be allowed, he concluded, “I have no doubt that this would successfully clarify what happened in Douma.”
With his explosive UN testimony and the leaks that preceded it, Ian Henderson and his colleagues have made clear that the OPCW experts who deployed to Syria are determined to bring the cover-up of an elaborate deception to light.
Why Clinton Foundation Whistleblowers’ Case Against IRS May Cause US Political Dynasties to Shiver
By Ekaterina Blinova – Sputnik – February 12, 2020
While the mainstream media in the US was preoccupied with Donald Trump’s impeachment another legal drama has been unfolding since March 2019, namely Lawrence W. Doyle and John F. Moynihan v Internal Revenue Service (IRS). Wall Street analyst Charles Ortel has explained why the case matters more than the impeachment saga.
Lawrence W. Doyle and John F. Moynihan, both graduates of the Catholic Jesuit College of the Holy Cross and independent expert forensic investigators, came to prominence on 13 December 2018 when they testified before the House Oversight and Government Reform Committee on the Clinton Foundation’s alleged fraud.
According to them, the charity does not operate as a tax-exempt 501(c)(3) organisation and has acted as nothing short of a foreign agent “throughout its existence”. Summarising their conclusions the two Jesuit alumni suggested that the Clinton Foundation owes between $400 million and $2.5 billion in taxes and informed US lawmakers that if the IRS refuses to consider their “tax claim” they would appeal to the US Tax Court. According to Zero Hedge, the ongoing litigation is apparently related to this very case.
Multinational Charities “Perfect” Disguise for Money Laundering
Charles Ortel, a Wall Street analyst and investigative journalist who has been conducting a private inquiry into the Clinton Foundation for several years opines that the aforementioned legal case may involve unprosecuted crimes by some “charities” operated by political dynasties and may even put the IRS itself under the microscope.
“I believe that Doyle and Moynihan, like most concerned citizens, want the IRS to enforce charity laws and regulations fairly, without regard to whether a given charity might be linked to a Republican, Democrat, or Independent person,” he says, specifying that the precise claim and details of the legal case in question are unknown since they’re sealed by the court.
According to Ortel, multinational charities have become “perfect” vehicles for disguising money laundering and influence peddling since regulators do not have enough resources to check their revenues and spending scrupulously especially when these non-profits are operating abroad.
“Compounding the above problems is the fact that numerous foreign actors including governments, companies, and individuals are eager to curry favour with sitting or rising politicians who, typically, are also hungry for financial support,” he suggests. “While foreign interests are barred from directly supporting or financing political candidates, they are allowed to ‘contribute’ to charities in which dynastic political families have interests or associations.”
Why IRS & FBI Turns a Blind Eye to Loosely Operated Charities
To illustrate his point Ortel referred to the Clinton Foundation that has repeatedly come under the spotlight being suspected of alleged “pay-to-play” schemes. Echoing Doyle and Moynihan, Ortel believes that the Clinton Foundation cannot be called a “charity” since its operations in the US and abroad go beyond charitable activities. Furthermore it is neither validly organised nor properly audited, he highlights. The Wall Street analyst raises the question as to why the supposed violations have remained unnoticed by the FBI and IRS for over a decade.
Referring to page 432 of the first IG Horowitz Report, Ortel notes that the FBI opened investigations into the Clinton Foundation in January 2016. By July 2016, the IRS too confirmed that they had opened a Clinton Foundation investigation, he points out. However, nothing has been heard since then about the cases.
The Washington Post reported on 10 January that John Huber, the US attorney in Utah, who was appointed by then-Attorney General Jeff Sessions in November 2017 to look into the FBI handling of possible corruption at the Clinton Foundation and Hillary Clinton’s alleged pay-to-play schemes during her tenure as secretary of state, “found nothing worth pursuing.” The media outlet specified, however, that “the assignment has not formally ended and no official notice has been sent to the Justice Department or to lawmakers”, citing knowledgeable sources.
“What I suspect is that bureaucrats and others in the IRS and Department of Justice have been reluctant to press into their investigations because high level current and former politicians and powerful donors, across the political spectrum are likely implicated in trafficking influence through these false-front charities, and others”, Ortel presumes.
US Debt is Soaring While “Charities” Sit on Trillions
The Wall Street analyst explains why financial violations and fraud on the part of charitable organisations are fraught with risks for national economies and societies.
“One hopes that the overwhelming majority of American charities abide by relevant laws”, he says. “This is likely true concerning charities that tackle local, state, or national challenges, but American charities and foreign charities that operate internationally are rife with potential for fraud and corruption.”
He points out that this is particularly true when it comes to disaster relief when “pocketbooks open instantly and large sums swarm” towards various “tax-exempt organisations” often connected to celebrities that say they are going to help.
Ortel bemoans that fact that “afterwards, too frequently as in the case of Haiti, for example, there is no rigorous accounting for the vast sums claimed as donations or expenses”. The Clinton Foundation’s role in fundraising to tackle the consequences of the 2010 Haiti earthquake is still triggering controversy and was addressed by Donald Trump during his 2016 campaign.
“In 2020, America has run up a mountain of government debt and we see little progress in paring back soaring annual government deficits that add to our monstrous debt pile”, the investigative journalist emphasises. “At the same time, loosely regulated charities, some funded by monopolists and near monopolists sit on trillions of dollars of unencumbered assets inside private foundations or public charities.”
According to him, if the IRS and Department of Justice did their best to enforce existing laws and regulations that prohibit certain tax-exempt organisations from enriching themselves “vast sums could be raised to help reverse erosion in [the US] national balance sheet”.
Ortel expresses hope that the effort spearheaded by Doyle and Moynihan will help restore confidence in the administration of justice.
Despite Iowa Caucus Fiasco, Nevada Democrats Plan to Use New Software “Tool”
By Whitney Webb | MintPress News | February 10, 2020
Even while the chaos of the recent Iowa Caucus remains fresh in voters’ minds, the Nevada State Democratic Party is setting itself up for more of the same by using a new software application for reporting results that is set to be coded and tested in less than a month. The application, still currently under development, will come preloaded onto iPads that will be distributed to precinct chairs during Nevada’s upcoming caucus, scheduled for February 22.
The scramble to create this new application followed revelations that the same company that had developed the software largely blamed for the Iowa debacle – known as Shadow Inc. – had also developed the two applications that Nevada Democrats had planned to use both for early voting and for Caucus Day.
Volunteers for Nevada’s upcoming caucus were told at a recent training session about the software’s existence and the rough details of how it will operate, but very little other information according to a report in the Nevada Independent. Notably, volunteers were urged not to refer to the application as an “app” but instead as a “tool,” likely due to the fact that Nevada Democrats said they would not use any apps for their upcoming caucus in light of what happened in Iowa. CBS News previously reported on the existence of this “tool” last Friday but was also short on specifics.
During the volunteer training session, a party staffer told participants the following:
What we’ve done after Iowa is consult with a group of tech and security folks who are helping us through this process and making sure that we’re doing this in a way that is simple and efficient and secure for all of you so that we’re giving you the best tools we can possible on Caucus Day. (emphasis added)”
Then the staffer, whose comments were recorded and were first reported by the Nevada Independent, described the function of this “tool” as “flow[ing] your precinct early vote data, so that you can have the information for your precinct caucus, so that when you do your viability calculations, you’re able to get the number of people who voted early and then when you see the results of your first alignment, you’re able to key in that early vote information so that you have every piece of information you need to run your precinct caucus.”
When a volunteer asked the staffer how the software “tool” would transmit results from one place to another, the staffer did not provide details but instead stated that “… We’re still working out some of the details around those so I’ll make sure that everyone has more information as we’re able to share it.”
Shadowy connections
Nevada’s decision to use a software program to be developed in less than a month is jarring considering that the failure of Iowa’s caucus was blamed on the rushed development of the Shadow Inc.-created app that resulted in only partial results of the caucus being reported. Yet, the Shadow Inc. app was reported to have been developed over a period of roughly two months, though the company’s CEO, Gerard Niemira, has since claimed that the app’s creation began last August. In contrast, Nevada Democrats are now slated to use a software application developed in less than half that time, thereby raising the likelihood of undiscovered coding errors and other functionality issues of this app significantly.
Another issue is the fact that Nevada Democrats decided to go this route after consulting “a group of tech and security folks” whose names and affiliations were not provided. As previously mentioned, after the Iowa debacle, several media reports quoted technology and cybersecurity experts as well as software developers who had cited the rushed development of the Shadow Inc. app as having largely led to the app’s failure and the resulting chaos in Iowa. It thus seems odd that a group of “tech and security folks” are urging Nevada Democrats to pay for the development of a new program in an even shorter time frame as a way to prevent Nevada’s caucus from repeating Iowa’s failures.
Though the identity of this group remains unknown, concerns have been raised that some may have links to the 2020 presidential campaign of Pete Buttigieg, given that the Shadow Inc.-developed app used in Iowa was found to have ties to the Buttigieg campaign and the Iowa caucus chaos clearly benefited the Buttigieg campaign.
Concerns about possible connections between these tech and security consultants and the Buttigieg campaign have only grown since it was revealed that Nevada Democrats recently hired an organizer for Pete Buttigieg’s 2020 presidential campaign, Emily Goldman, as the Caucus’ Voter Protection Director, just weeks before the caucus is set to take place. Goldman also previously interned at the Brookings Institute, whose chair recently authored a piece in the Wall Street Journal entitled “Stop Bernie Sanders Now.” After Goldman’s connections to the Buttigieg were revealed, she deleted her work history on LinkedIn and locked her Twitter account.
Goldman’s new position at the Nevada State Democratic Party tasks her with “ensur[ing] that all eligible Nevadans are able to cast their ballot.”
Given the rushed development of a new app, the lack of transparency regarding the Nevada Democrats’ technology consultants and Emily Goldman’s recent hire, concerns that Nevada’s upcoming caucus will repeat the chaos seen in Iowa have hardly been assuaged.
Worse still, the very volunteers who attended the recent caucus training workshop described the sentiment in the room as “frustration and confusion”, with one caucus site leader telling the Nevada Independent that “there was ‘not a bit of proof’ at the training that Nevada wouldn’t be another Iowa.” Another volunteer told the Nevada Independent that “the people participating in the training didn’t even seem to understand the basic details of how to carry out the caucus process and didn’t know that precinct chairs can’t also be precinct captains on behalf of a campaign,” while other volunteers said they were not told how to properly realign early voters’ preferences on Caucus Day should the new tool fail.
Though the fallout from the Iowa Caucus is still fresh, it appears that the technology-driven chaos and corruption seen in Iowa has not served as a warning to some in the Democratic Party, but instead a roadmap.
Whitney Webb is a MintPress News journalist based in Chile. She has contributed to several independent media outlets including Global Research, EcoWatch, the Ron Paul Institute and 21st Century Wire, among others. She has made several radio and television appearances and is the 2019 winner of the Serena Shim Award for Uncompromised Integrity in Journalism.
Featured Video
No Vote, No Representation, No State: Democracy, Israeli Style
or go to
Aletho News Archives – Video-Images
From the Archives
Sanctions, War and the Policy of Dual Containment
By SASAN FAYAZMANESH | March 17, 2008
It is now nearly three decades since the Unites States adopted the policy of dual containment of Iran and Iraq. While much has been written about the containment of Iraq, there has been very little in-depth analysis of this policy when it comes to Iran. In a book that is going to be released on March 31, 2008, entitled The United States and Iran: Sanctions, Wars and the Policy of Dual Containment (Routledge), I attempt to address this shortcoming by investigating when and why the US policy of containment of Iran came about, how it evolved, and where it stands today.[1] To the extent that Israel has been involved in US policy making, the study will also include the role that Israel has played in the containment of Iran. Also, since the fate of Iran has been inextricably linked to that of Iraq, occasionally the investigation will overlap with the containment of Iraq.
The policy of dual containment of Iran and Iraq originated during the Carter Administration, but it was not until the Clinton Administration that the expression “dual containment” became popular. … continue
Blog Roll
 Aletho News
- Europe’s Establishment Is Embracing War – and Losing Voters
- NATO chief advocates war of aggression
- No Vote, No Representation, No State: Democracy, Israeli Style
- Zionist Bought Senate Blocks Information About American Citizens Killed By Israel
- While Gaza dominates the UN, these are the people keeping it alive
- New Report: “Scholasticide and Genocide in Gaza: Assessment, Testimonies and Legal Analysis”
- ‘THAAD Delusion’: Iran war exposes US missile shield limits – The Atlantic
- Moscow issues warning to NATO over Russian exclave
- Yes, the Iran war has destroyed Trump’s presidency
- The fallacy of US delusions about Iran’s economic collapse
- If Americans Knew
- Mamdani releases plan to combat antisemitism and hate crimes in New York City
- Iran’s Revolutionary Guards Publish Letter to the American People
- DMFI launches $1 million ad campaign supporting Virginia’s Elaine Luria
- US Senate blocks resolution seeking report on Americans killed by Israel
- Israeli Attacks Kill Ten Palestinians in Gaza
- Massacre at Minab: The School That Became a Grave
- Israeli media: The IDF Shows It Doesn’t Turn a Blind Eye; It Actively Emboldens Settler Havoc
- As settlers ravage West Bank, Israeli forces kill 10 in Gaza – Daily Update
- New Report: “Scholasticide and Genocide in Gaza: Assessment, Testimonies and Legal Analysis”
- Ex-Biden officials are desperate for a Gaza scapegoat
- No Tricks Zone
- Green Energy Debacle: German Expert Professor Fritz Vahrenholt Warns Of Severe Economic And Social Consequences
- Two More Paleo Reconstructions Affirm Meters-Higher Sea Levels Across Ireland, Brazil 7000-6000 Years Ago
- New Study: Earth And Venus Surface Warmth Largely Explained By Convection And Lapse Rate, Not CO2 Or Radiation
- 2025 Nature Paper Claiming Worsening Global Drought Gets RETRACTED …Heavily Flawed
- New Study: ‘Global Drought Shows No Detectable Recent Acceleration Under Climate Warming’
- Economic Masterminds: German Socialists Suggest Taxing Productivity Gains Stemming From Using AI
- The South China Sea Has Not Been Cooperating With The Climate Change Narrative
- Energy Crisis: Germany Enters Heating Season With Historically Low Gas Reserve Fill Levels
- New Study: The Antarctic Ice Sheet Gained Mass From 2020-2024 Due To Staggering Snow And Ice Accumulation
- Study: Ocean Heating Rates From Thousands Of Years Ago ‘Dwarf’ Modern Ocean Heating Rates

