DNC Scrambles To Change Debate Threshold After Gabbard Qualifies
By Caitlin Johnstone | March 4, 2020
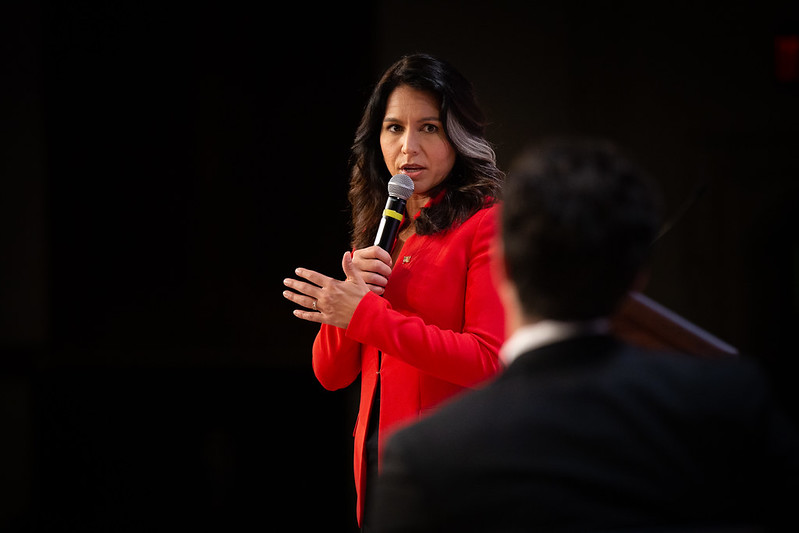
On a CNN panel on Monday, host John King spoke with Politico reporter Alex Thompson about the possibility of Democratic presidential candidate Tulsi Gabbard qualifying on Super Tuesday for the party’s primary debate in Phoenix later this month.
“I will note this, she’s from Hawaii,” King said of Gabbard. “She’s a congresswoman from Hawaii; American Samoa votes on Super Tuesday. The rules as they now stand, if you get a delegate, you’re back in the debates. As of now. Correct?”
“Yeah, they haven’t, I mean, that’s been the rule for every single debate,” Thompson replied. “And the DNC has not released their official guidance for the March 15 debate in Phoenix, but it would be very obvious that they are trying to cancel Tulsi, who they’re scared of a third party run, if they then change the rules to prevent her to rejoin the debate stage.”
And indeed, as the smoke clears from the Super Tuesday frenzy, this is precisely what appears to have transpired.
“The Gabbard campaign said it was informed that it would net two delegates from the caucuses in American Samoa, which will allocate a total of six pledged delegates,” The Hill reports today. “However, a report from CNN said that the candidate will receive only one delegate from the territory on Tuesday evening.”
“Tulsi Gabbard may have just qualified for the next Democratic debate thanks to American Samoa,” reads a fresh Business Insider headline. “Under the most recent rules, Rep. Tulsi Gabbard of Hawaii may have qualified for the next televised debate by snagging a delegate in American Samoa’s primary.”
“If Tulsi Gabbard gets a delegate out of American Samoa, as it appears she has done, she will likely qualify for the next Democratic debate,” tweeted Washington Post‘s Dave Weigel. “We don’t have new debate rules yet, but party has been inviting any candidate who gets a delegate.”
Rank-and-file supporters of the Hawaii congresswoman enjoyed a brief celebration on social media, before having their hopes dashed minutes later by an announcement from the DNC’s Communications Director Xochitl Hinojosa that “the threshold will go up”.
“We have two more debates– of course the threshold will go up,” tweeted Hinojosa literally minutes after Gabbard was awarded the delegate. “By the time we have the March debate, almost 2,000 delegates will be allocated. The threshold will reflect where we are in the race, as it always has.”
“DNC wastes no time in announcing they will rig the next debates to exclude Tulsi,” Journalist Michael Tracey tweeted in response.
This outcome surprised nobody, least of all Gabbard supporters. The blackout on the Tulsi 2020 campaign has reached such extreme heights this year that you now routinely see pundits saying things like there are no more people of color in the race, or that Elizabeth Warren is the only woman remaining in the primary. They’re not just ignoring her, they’re actually erasing her. They’re weaving a whole alternative reality out of narrative in which she is literally, officially, no longer in the race.
After Gabbard announced her presidential candidacy in January of last year I wrote an article explaining that I was excited about her campaign because she would severely disrupt establishment narratives, and, for the remainder of 2019, that’s exactly what she did. She spoke unauthorized truths about Syria, Afghanistan and Saudi Arabia, she drew attention to the plight of Julian Assange and Edward Snowden and said she’d drop all charges against both men if elected, she destroyed the hawkish, jingoistic positions of fellow candidates on the debate stage and arguably single-handedly destroyed Kamala Harris’ run.
The narrative managers had their hands full with her. The Russia smears were relentless, the fact that she met with Syrian president Bashar al-Assad was brought up at every possible opportunity in every debate and interview, and she was scoffed at and derided at every turn.
Now, in 2020, none of that is happening. There’s a near-total media blackout on the Gabbard campaign, such that I now routinely encounter rank-and-file liberals on social media who tell me they honestly had no idea she’s still running. She’s been completely redacted out of the narrative matrix.
So it’s unsurprising that the DNC felt comfortable striding forward and openly announcing a change in the debate threshold literally the very moment Gabbard crossed it. These people understand narrative control, and they know full well that they have secured enough of it on the Tulsi Problem that they’ll be able to brazenly rig her right off the stage without suffering any meaningful consequences.
The establishment narrative warfare against Gabbard’s campaign dwarfs anything we’ve seen against Sanders, and the loathing and dismissal they’ve been able to generate have severely hamstrung her run. It turns out that a presidential candidate can get away with talking about economic justice and plutocracy when it comes to domestic policy, and some light dissent on matters of foreign policy will be tolerated, but aggressively attacking the heart of the actual bipartisan foreign policy consensus will get you shut down, smeared and shunned like nothing else. This is partly because US presidents have a lot more authority over foreign affairs than domestic, and it’s also because endless war is the glue which holds the empire together.
And now they’re working to install a corrupt, right-wing warmongering dementia patient as the party’s nominee. And from the looks of the numbers I’ve seen from Super Tuesday so far, it looks entirely likely that those manipulations will prove successful.
All this means is that the machine is exposing its mechanics to the view of the mainstream public. Both the Gabbard campaign and the Sanders campaign have been useful primarily in this way; not because the establishment would ever let them actually become president, but because they force the unelected manipulators who really run things in the most powerful government on earth to show the public their box of dirty tricks.
Airbnb Gives Renters Secret Risk Assessments And Personality Tests
credit: Airbnb
MassPrivateI | March 3, 2020
What does the Church of Scientology and Airbnb have in common? If you answered secret risk assessments and personality tests, then give yourself a gold star.
If you have you rented an Airbnb in the past six years, the odds are pretty high that you have been given a secret risk assessment and personality score.
According to an Electronic Privacy Information Center (EPIC) complaint, Airbnb’s secret renter risk assessments are just as specious as the Church of Scientology’s personality tests.
“This complaint concerns Airbnb’s deployment of a risk assessment technique that assigns secret ratings to prospective renters, based on behavior traits using an opaque, proprietary algorithm. Airbnb has failed to show that its technique meets the fairness, transparency, and explainability standards for AI-based decision-making set out in the OECD AI Principles and the Universal Guidelines for AI.”
According to EPIC, Airbnb uses a secret algorithm to generate renter “risk scores.”
“Airbnb generates a risk assessment score for consumers before their reservations are confirmed. As the company explains on their website: Risk scoring. Every Airbnb reservation is scored for risk before it’s confirmed. We use predictive analytics and machine learning to instantly evaluate hundreds of signals that help us flag and investigate suspicious activity before it happens.”
For six years, Airbnb has been using their “Determining Trustworthiness and Compatibility of a Person” algorithm to create risk scores of every renter.
Airbnb also uses their secret algorithm to rate renters personalities.
“Personality comprises the emotional and cognitive characteristic of a person. Behavior is how a person acts or reacts, sometimes toward another person, in a certain situation. A person with positive personality or behavior traits such as conscientiousness and openness, for example, is often perceived as more reliable and trustworthy. A person with negative personality or behavior traits such as neuroticism and involvement in crimes, for example, is often perceived as untrustworthy.”
Airbnb does not want people who are “shy, anxious or depressed” to rent their apartments, condominiums or homes because those types of people are likely to leave negative comments.
But Airbnb will rent to people with a “high trustworthiness score” because they are more likely to leave positive comments.
Airbnb uses their secret algorithm to check renters social network profiles, email address, telephone number, geographic location, date of birth, social connections, employment history, education history, driver’s license number, financial account information, Internet Protocol (IP) address, and device identifier.
EPIC’s complaint claims Airbnb uses their algorithm to score a renters’ trustworthiness based on their social media profiles.
“According to the patent application, machine learning inputs include personal data collected from web pages, information from databases, posts on the person’s social network account, posts on a blog or a microblog account of the person, a comment made by the person on a website, or a directory listing for a company or association.”
Airbnb’s algorithm is also used to identify renters with Machiavellianism and negative personalities.
“A particular personality trait can be badness, anti-social tendencies, goodness, conscientiousness, openness, extraversion, agreeableness, neuroticism, narcissism, Machiavellianism, or psychopathy or is involved in pornography, has authored online content with negative language, or has interests that indicate negative personality or behavior traits.”
By identifying so-called negative personality or behavior traits of their renters, Airbnb has essentially turned property owners into untrained psychiatric and behavioral therapists.
Airbnb also reviews renters emails, phone conversations and in-person encounters with owners and adds them to their secret risk assessment.
“The method provides the behavior trait metrics and the personality trait metrics of the first person and corresponding metrics for a second person as input to a scoring system and obtaining as output from the system a compatibility score between the two persons.”
Airbnb’s algorithm considers derogatory or angry words an anti-social personality trait. This is horrifying, everything a renter says and does goes towards their personal risk assessment.
Airbnb’s risk assessments and personality tests are about as accurate as the Church of Scientologists E-Meter which purports to identify a person’s negative traits using “a box; a needle; one battery; two cans; and a bunch of copper wire.”
Airbnb has one more trick up their sleeve so to speak: they are also checking renters’ names against secret U.S. government watchlists.
Airbnb has turned a once innocuous thing like renting an apartment, condominium or home into a corporate surveillance nightmare replete with secret risk assessments and anti-social personality scores
Fighting the Canadian Media Crackdown – Dan Dicks on The Corbett Report
Corbett • 03/02/2020
The Canadian government has recently considered a proposal to require all Canadian media to be licensed by the government. The proposal has been rejected for now, but how long can independent media continue to function in the increasingly draconian Canadian police state? Dan Dicks of PressForTruth.ca joins us to discuss the issue.
Watch this video on BitChute / Flote.app / Minds.com / YouTube or Download the mp4
SHOW NOTES:
PressForTruth.ca
Trudeau’s Digital Charter And The $600M Media Bailout Explained
Ezra Levant of Rebel News Interrorgated For His Book Exposing Justin Trudeau
Licensing The Global News Circuit Soon To Be A Reality in Canada Despite Claims They Won’t Do It
Into the Fire – Dan Dicks on The Corbett Report
Dan Dicks on BitChute / Flote.app / Minds / Steemit / YouTube
Report details Israel’s February violations against Palestinian media
MEMO | March 2, 2020
The Journalists’ Support Committee (JSC) reported on Sunday that Israel committed 84 violations against Palestinian media during February.
The JSC said that Israeli occupation forces wounded 24 Palestinian journalists by shooting steel-coated rubber bullets at them while they were carrying out their work.
Israel also tried to prevent Palestinian journalists from covering the violations committed by its occupation forces.
As part of these efforts, the Israeli occupation forces arrested eight Palestinian journalists. Although four were released, the other four are still in prison.
The detention of five other journalists was extended by the occupation authorities during February.
The JSC pointed out that at least six Palestinian journalists being held by Israel have been prevented from meeting their lawyers and subjected to harsh interrogation, including verbal and physical abuse.
In the report, it was revealed that the Israeli occupation imposed very high fines on four Palestinian journalists before putting them under house arrest or expelling them from their home cities.
Journalists have been beaten by security forces and prevented from travelling in the course of their work.
Employment and Press accreditation documents have been confiscated by Israel.
Meanwhile, Israel is continuing to put pressure on social media sites to censor anything remotely pro-Palestine. Many journalists’ and media accounts have been suspended or closed accounts.
Ironically, three Palestinian journalists from the occupied West Bank, said the JSC, were taken before Israeli courts on the day that the Committee’s report was issued.
According to rights groups, there are 22 Palestinian journalists inside Israeli jails. There are around 5,500 Palestinians prisoners being held by Israel, including 42 women and girls, 250 children, 450 under administrative detention and around 1,000 in need of urgent medical care.
Coronavirus: The “Cures” Will Be Worse Than the Disease
By James Corbett – corbettreport.com – February 29, 2020
It’s spreading. It’s mutating. It’s going viral.
Am I talking about coronavirus? No! I’m talking about theories about coronavirus.
It’s a natural virus. / No, it’s a manmade bioweapon!
It’s less deadly than the regular flu. / It’s worse than the Spanish Flu! / It’s flying bat AIDS!!
The numbers are being underreported. / The numbers are being inflated!
It was patented in 2015! / No, it really wasn’t.
It was unleashed by accident. / It was unleashed on purpose. / It doesn’t even exist!
Yes, there are as many theories about coronavirus disease 2019 (Covid-19) as there are people talking about it. The reality is that I don’t know the truth about what this virus really is or where it came from and neither do you.
But there’s something that we do know for sure regardless of where this virus came from or whether it even really exists. The hype and fear and panic and pandemonium surrounding this (supposed) outbreak is going to be far worse than the disease could ever be. Because, as I’ve been screaming about for over a decade now, a bioweapon attack (real or manmade, false flag or otherwise) is the perfect cover for a slew of agenda items on the globalist checklist. And the more the population panics, the more they play into the globalists’ hands.
Here are five items on The Powers That Shouldn’t Be’s wishlist that are being delivered on a silver platter as people scurry around panicking about coronavirus.
1) Unprecedented surveillance and control of population
As Corbett Reporteers will know by now, China is in many ways the model for the technocratic Brave New World of the 21st century. Social credit scores and facial recognition CCTV networks and government-controlled internet are just the most obvious examples of how governments will seek to surveil and control their populations in the future. So it shouldn’t be surprising that China, as the epicenter of this new coronavirus outbreak, is pioneering new and hitherto undreamt of ways to keep their population in line during the crisis.
The first thing to note is the sheer scale of what the Chinese government is attempting here. The quarantine imposed in Wuhan last month, encompassing a city of 11 million people, was already the largest quarantine in human history. But when that quarantine expanded to include the entire province of Hubei—a population of 57 million people—the scope of the lockdown became nearly unimaginable. How can such a quarantine possibly be maintained?
Well, as we’ve all seen, it can be done by good old-fashioned brute force. When in doubt, just weld the sick person’s door shut so they can’t leave their room!
But to really manage millions of people, you need technological help. And so the Chinese government has been deploying every tool in its arsenal to monitor and maintain restrictions on citizens and their movements.
Flying drones to harass anyone walking around without a mask? Check.
A nationwide video surveillance system called—you can’t make this up—Skynet to help spot quarantine evaders? Check.
A color-coded rating on a smartphone payment app to identify people as low or high-risk for carrying the virus based on their payment and travel history? Check.
If you can think of a creepy and invasive way of tracking and controlling the population, you can bet your bottom dollar that the Chinese government has already thought of it (and is likely already using it).
But here’s the real question: When this is all over, do you think the government will simply shelve these technologies and systems? Or do you think that once this level of control becomes normalized that the authoritarians in the Chinese Communist Party will continue using it?
And here’s the even realer question: Do you think there’s a government anywhere around the world that wouldn’t use this technology on its own population if given a convenient excuse (like, say, a freakout over a novel coronavirus)?
The answers to these questions are obvious, but just look at the prisoner conditioning that has been taking place at the airports for the past two decades. Even people like myself who grew up pre-9/11 can scarcely believe there was a time where you could hop on a plane with little more than a step through a metal detector. What? You want to bring a water bottle through security!? What are you, crazy? In just two decades, the entire experience of air travel has been utterly transformed, and no declaration of victory in the so-called “War on Terror” will ever bring back the old security screening practices. For the average American, the TSA is just a fact of life now.
And for those who live for long enough in a quarantine crackdown, complete government surveillance of every citizens movements, purchases and interactions will just be a fact of life. These tools of control are here to stay, and the longer these quarantines last and the greater the areas effected, the further it will go in conditioning the public to accept it.
2) A blank check for Big Pharma and the WHO
When a detective is looking to solve a crime, it’s important to ask cui bono. Although it may be circumstantial, establishing who benefits from a crime at least points you to some suspects.
In this case, though, the question of who benefits has a simple answer: WHO benefits, of course. The World Health Organization, that is. As the United Nations body tasked with directing international health and leading the response to global health concerns, the WHO always grows in power in the wake of every crisis.
During the swine flu non-crisis and the ebola non-crisis and the zika non-crisis the WHO was led by Director-General Margaret Chan. It was under Chan’s watch, remember, that the WHO declared the 2009 swine flu outbreak a “global pandemic,” a move that automatically triggered billions of dollars of vaccine purchases by various governments. This was a blatant cash grab, of course, and even the Council of Europe was compelled to note that the members of the WHO council that made the pandemic declaration were also sitting on the boards of the vaccine manufacturers who stood to benefit from that decision.
With the Covid-19 outbreak, too, the WHO is playing a game with the pandemic declaration, only this time its motivation is precisely the opposite. In 2017, the World Bank issued a $425 billion bond in support of its Pandemic Emergency Financing Facility. Investors in that bond issue will lose everything if a global pandemic is declared before July . . . a key reason, some suggest, why the WHO is refusing to call coronavirus a pandemic despite it quite clearly meeting the criteria.
So who is heading the WHO this time around? Well, it’s not Margaret Chan anymore. She stepped down in 2017 and was replaced by Tedros Adhanom Ghebreyesus, an Ethiopian politician and academic who, William Engdahl notes, is the first WHO director-general who isn’t even a medical doctor. Instead, after earning his degree in biology at the University of Asmara in Eritrea and serving in a junior position at the Ministry of Health under the Marxist dictatorship of Mengistu, he:
“[. . .] then went on to become Minister of Health from 2005 to 2012 under Prime Minister Meles Zenawi. There he met former President Bill Clinton and began a close collaboration with Clinton and the Clinton Foundation and its Clinton HIV/AIDS Initiative (CHAI). He also developed a close relation with the Bill and Melinda Gates Foundation. As health minister, Tedros would also chair the Global Fund to Fight AIDS, Tuberculosis and Malaria that was co-founded by the Gates Foundation. The Global Fund has been riddled with fraud and corruption scandals.”
Oh, you mean the Gates Foundation and their GAVI Alliance for vaccination that are the WHO’s biggest donors? The Gates Foundation that helped host the Event 201 “high-level pandemic exercise” in New York last October that war gamed out the entire coronavirus scenario we’re currently living through? Right.
And how are WHO going to save the day? With Big Pharma drugs, naturally! Governments are already lining up to pledge tens of millions of dollars to fund the effort to develop a coronavirus vaccine. And that’s just the funding to develop the vaccine. There are many more billions waiting for the big pharma manufacturers who can deliver the first vaccine to market.
Yes, coronavirus is going to be a big payday for some rich and well-connected people in the international medical mafia. But don’t worry, the politicians are going to get in on the fun, too . . .
3) An excuse to implement medical martial law
A decade ago, in the midst of the swine flu hype, I released an episode of The Corbett Report podcast on medical martial law. In that episode I laid out the various ways that governments around the world (including, of course, the US government) have been quietly passing legislation that would enable them to implement martial law in the event of a global pandemic. This would allow them to quarantine and incarcerate citizens suspected of infection, and would allow the government to administer whatever medications (including vaccinations) it deemed necessary to stop the spread of the infection.
In the US specifically, this legislation took the form of The Model State Emergency Health Power Act, a piece of legislation that was drafted by the Center for Disease Creation (CDC). The act grants government the power to quarantine, force vaccinate, and mobilize the military to help implement emergency procedures as deemed necessary to contain the outbreak. It is designed to be forwarded in each state legislature so that the states could harmonize their emergency pandemic plans, essentially creating a federal system enabling medical martial law. As the ACLU notes:
“The Act lets a governor declare a state of emergency unilaterally and without judicial oversight, fails to provide modern due process procedures for quarantine and other emergency powers, it lacks adequate compensation for seizure of assets, and contains no checks on the power to order forced treatment and vaccination.”
Regardless, at last count the act has been the basis for 133 pieces of legislation in 33 different states.
And, sure enough, the citizens of the developed, Western world who thought that martial law was only for banana republics and exotic Eastern countries are about to get a taste of this bitter medicine on the back of the coronavirus hype.
Australia just activated its emergency pandemic plan despite not having a reported case of human-to-human transmission of Covid-19. The plan grants the government the power to cancel public events, force people to work from home, close childcare centers and otherwise impose mandates and restrictions on the daily lives of its citizens as it sees fit.
Not to be outdone, the Swiss Federal Council has just declared a “special situation” which allows the council to issue emergency police ordinances “without a basis in federal law.” Some of the powers explicitly assumed by the council include the power to mandate vaccinations, order quarantines and ban events or close institutions.
Now Britain, the US, and other countries are dusting off their own emergency plans and preparing to get in on the martial law bonanza.
Of course, this is not only the perfectly predictable response to the current outbreak hype, it was the predicted response. That’s right, as noted above, the high-level exercise dubbed Event 201 that was held last October and which simulated a global coronavirus pandemic featured extensive discussion about the need to implement medical martial law in order to bring the virus in check.
Thus we saw Stephen Redd of the CDC opining during the exercise that “governments need to be willing to do things that are out of their historical perspective [sic] . . . It’s really a war footing that we need to be on.”
Likewise, Brad Connett of medical supply manufacturer Henry Schein Inc declared that “it can happen quickly. A martial [law]-type plan–they may not say that, exactly–but a martial [law]-type plan can go into effect and stimulate change very quickly.”
It certainly can. And what room do you believe the governments that implement martial law are going to leave for dissent on the issue? Why, none, of course. But how are they going to stop the spread of information in this age of 24/7 always-connected social media?
Funny you should ask, because that leads us to our next New World Order agenda item.
4) An excuse to crack down on the internet
In New World Next Year 2020—the annual year-end New World Next Week wrap up episode—I predicted that 2020 was going to be The End of the Internet As We’ve Known It! At the time I formulated that prediction, the 2020 (s)election circus and the inevitable wave of censorship that it would bring about weighed heavily on my mind. As it is, it’s quite possible that coronavirus will be the convenient excuse for governments to flex their internet censorship muscles.
Zero Hedge has already had its Twitter account suspended for posting the details of a particular Chinese scientist working in the Wuhan bio lab that some suspect was the origin of the outbreak. This was done in the name of Twitter’s policy about “abuse and harassment,” but given that the website did nothing more than post the already publicly available contact information for the scientist, it seems more likely that this is part of a campaign to control the narrative on coronavirus from the get go.
As I write this editorial, the front page of Google News (which I strongly advise against using as a source of information, for the record) is filled with “Fact Checks” about various coronavirus theories that are floating around the internet.
Given the current state of online censorship, can there be any doubt that governments around the world will jump at the excuse to scrub dissenting voices from the internet? As alternative information about the virus, its origins, and the vaccines that are intended to “cure it” flood the net, a propaganda campaign unlike any we have seen before will be waged to portray the purveyors of this information as a threat to public order. They will be purged from the internet accordingly, with (no doubt) the approval of a large proportion of the population. And with that precedent set, it will only be a matter of time before any information that challenges the ruling power is deemed a “threat to public order” and wiped from the internet.
Lest there be any doubt that the online purge is an aspect of the pandemic scenario that is particularly important to TPTSB, it should be noted that Event 201 dwelled extensively on how to “stop the spread of misinformation.” Their answer: Internet shutdowns and censorship, of course!
5) Precipitating economic crisis
Given that I make my living online, the prospect of internet shutdowns and censorship crackdowns are worrying to me. But before you become too distraught over the plight of the poor podcaster, let’s put this crisis into perspective: Assuming that the virus does go pandemic, it is quite likely that this will be the largest economic disruption of our lifetime.
This is the point where I would put forward some facts to back up such a bold statement, but given that we just saw the worst week in the markets since the financial crisis, including the worst two day point drop in Dow Jones history, I doubt that it’s really necessary to elaborate.
As mass quarantines expand, public events are canceled, businesses are shuttered, and economic activity generally grinds to a halt, it doesn’t take a genius to deduce that we are in for a global economic crisis of nearly unthinkable proportions. But the real disruptions are going to start long before we get to that point.
Given that the mass quarantines have started in China, a.k.a. the most important link in the global just-in-time supply chain, we are going to see significant difficulties for many manufacturers producing basic consumer goods in the very near future. Smartphones. Cars. Even, in a perverse bit of irony, medical supplies. So much of the global economy that depends on Chinese manufacturing is already experiencing shutdowns and shortages. And this is only the razor thin edge of what promises to be a gigantic wedge.
Here’s the worst part: These disruptions are already baked into the cake. Even if everyone on the planet was suddenly cured of their disease overnight and all quarantines were lifted, the effects of these last few weeks of lockdowns and closures would still continue to ripple their way through the global economy for months. But as the fear and hype spreads from continent to continent and the mass disruptions expand, these effects will get worse and worse.
I would expand on this point, but I have a feeling this is going to become a dominant and recurring topic of review in these editorials in the future. Let me just say this for now: Regardless of whether coronavirus is natural or manmade or even whether it exists at all, the economic effects of this event are going to be very real and very profound. Given that I write for the International Forecaster and have been documenting the Ponzi scheme that is the modern global economy for over a decade now, I’m often asked when the scam will collapse and the long-predicted global financial crisis will hit. Well, it’s very possible that the crisis has now officially hit and the decades of pie-in-the-sky negative-interest-rate helicopter-funny-money insanity that has papered over our grim economic reality is about to come crashing down all at once.
Conclusion: Coronavirus panic is a giant boost for the globalist agenda
I recently heard a suggestion that if this does eventuate into a global pandemic then it will set the globalist agenda back by decades. After all, an event like this will surely teach us all a hard lesson in national self-sufficiency and the inherent danger of an overextended, just-in-time global supply chain, right?
Of course not. No, that’s the conclusion that a rational person thinking about the crisis in a rational way would come to. So of course the globalists are going to force feed us the exact opposite idea: That a crisis like this will demonstrate how we need even more global integration amongst all levels of public and private society.
Don’t believe me? Just read the press release that Johns Hopkins and the Event 201 participants put out last month just before “Wuhan” and “coronavirus” became topics of daily conversation:
“The next severe pandemic will not only cause great illness and loss of life but could also trigger major cascading economic and societal consequences that could contribute greatly to global impact and suffering. Efforts to prevent such consequences or respond to them as they unfold will require unprecedented levels of collaboration between governments, international organizations, and the private sector.”
Oh, that’s right. This is another chance to “fail forward.” After all, as that great globalist soothsayer Rahm Emanuel told us during the last financial catastrophe, the global elitists’ mantra is to “never let a good crisis go to waste.” Do you really think this “crisis” (whether real or imaginary) would be any exception?
Rohrabacher, Mueller, and Assange
By Daniel Lazare | Strategic Culture Foundation | February 26, 2020
Reports that Donald Trump offered to pardon WikiLeaks founder Julian Assange if he could prove that Russia didn’t hack Democratic National Committee caused a good-sized media storm when they came out in a British court last week. But then Dana Rohrabacher, the ex-US congressman supposedly serving as a go-between, issued an all-points denial, and the tempest blew over as fast as it arose.
But that doesn’t mean that the Russia-WikiLeaks story is kaput. To the contrary, it’s still brimming with unanswered questions no matter how much the corporate media wishes they would go away.
The most important question is the simplest: why didn’t Special Prosecutor Robert Mueller sit down with Julian Assange and ask him about the 20,000 DNC emails himself?
It’s not as if Assange would have said no. According to Craig Murray, the former British diplomat who serves as an unofficial WikiLeaks spokesman, he “was very willing to give evidence to Mueller, which could have been done by video-link, by interview in the [Ecuadorean] Embassy, or by written communication.” While Assange refuses as a matter of policy to disclose his sources, he had already made a partial exception in the case of the DNC by declaring, “Our source is not a state party.” Conceivably, he had more to say along such lines, information that Mueller might have then used to determine what role, if any, Russia played in the email release.
But he didn’t bother. Without making the slightest effort to get Assange’s side of the story, he assembled page after page of evidence purporting to show that WikiLeaks had collaborated with Russian intelligence in order to disseminate stolen material. Rather than an organization dedicated to exposing official secrets so that voters could learn what their government was really up to, WikiLeaks, in the eyes of the special prosecutor, was the opposite: an organization seeking to help Russia pull the wool over people’s eyes so they would vote for Donald Trump.
This is the super-sensational charge that has roiled US politics since 2016. Yet there is little to back it up.
Even though Mueller is confident that the Russian military intelligence agency known as the GRU routed the emails to WikiLeaks, for instance, he still hasn’t figured out how. “Both the GRU and WikiLeaks sought to hide their communications, which has limited the [Special Prosecutor’s] Office’s ability to collect all of the communications between them,” his report confesses on page 45. “The Office cannot rule out that stolen documents were transferred to WikiLeaks through intermediaries who visited during the summer of 2016,” it adds on page 47. “For example, public reporting identified Andrew Müller-Maguhn as a WikiLeaks associate who may have assisted with the transfer of these stolen documents to WikiLeaks.”
But Müller-Maguhn, a German cyber-expert who has worked with WikiLeaks for years, dismisses any such suggestion as “insane,” a claim the Mueller report makes no effort to rebut. The public is thus left with a blank where a dotted trail the GRU and WikiLeaks ought to be. Then there’s the issue of chronology. The Mueller report says that a GRU website known as DCLeaks.com reached out to WikiLeaks on June 14, 2016, with an offer of “sensitive information” related to Hillary Clinton. Considering that WikiLeaks would release a treasure trove of DNC emails on July 22, less than seven weeks later, the implication that the GRU was the source does not, at first glance, seem implausible.
But hold on. Although the report doesn’t mention it, Assange told a British TV station on June 12: “We have upcoming leaks in relation to Hillary Clinton, which is great.” Either he was amazingly clairvoyant in foreseeing an offer that the GRU would make two days hence or he got the material from someone else.
To be sure, the Mueller report adds that an alleged Russian intelligence “cutout” known as Guccifer 2.0 sent WikiLeaks an encrypted data file on July 14, which is to say eight days prior to publication. But since WikiLeaks didn’t confirm opening the file until July 18, this means that it would have had just four days to vet thousands of emails and other documents to insure they were genuine and unaltered. If just one had turned out to be doctored, its hard-earned reputation for accuracy would have been in shreds. So the review process had to be painstaking and thorough, and four days would not be remotely enough time.
Nothing about the Mueller account – timing, plausibility, the crucial question of how the stolen DNC emails made their way to WikiLeaks – adds up. Yet Mueller went public with it regardless. Which leads to another question: why?
One reason is because he knew he could get away with it, at least temporarily, since it was clear that corporate media howling for Trump’s scalp would accept whatever he put out as gospel. But another is that he’s a dutiful servant of the ruling class. After all, Mueller is the person who, as FBI director from 2001 to 2013, spent much of his time covering up Saudi Arabia’s not-inconsiderable role in 9/11, as investigative reporter James Ridgeway has pointed out on a number of occasions. Mueller is also the man who assured the Senate Intelligence Committee in February 2003 that “Iraq’s WMD program poses a clear threat to our national security,” a claim that the upcoming Iraqi invasion would reveal as fraudulent to the core.
Toeing the official line is therefore more important in his book than telling the truth. This is why he didn’t sit down with Assange – because he was afraid of what he might tell him. In January 2017, the CIA, NSA, and FBI officially reported that “Russian President Vladimir Putin ordered an influence campaign in 2016” and “that Russian military intelligence … used the Guccifer 2.0 persona and DCLeaks.com” to relay stolen computer data to WikiLeaks. Four months later, then-CIA Director Mike Pompeo went even farther by describing WikiLeaks as “a non-state hostile intelligence service often abetted by state actors like Russia.”
This was the official narrative that Mueller felt dutybound to defend when he was appointed special prosecutor a month after Pompeo made his remarks. Even though the CIA account would not hold up to close inspection, his self-perceived mission was to disregard certain facts and cherry-pick others in order to convince the public that it was true.
This leads us to a third question: how do Americans get themselves out of the hole that Mueller has dug for them? Not only does Assange face 170 years in prison for espionage, but the impact in terms of freedom of the press will be devastating. The prosecution’s case rests on an explosive theory that receiving inside information is effectively the same thing as supplying it. Just as a fence encourages people to steal, the idea is that a journalist encourages insiders to hack computers and rifle through file cabinets by offering to publish what they come up with. If upheld, it means that journalists would have to think twice before even talking to an inside for fear of incurring a similar penalty. Armed with such a legal instrument, Richard Nixon would have had no trouble dealing with Bob Woodward and Carl Bernstein. He would merely have charged them with espionage and locked them away until the break-in was forgotten.
If Assange goes down, in other words, democracy will take a major hit. Yet by labeling him a Russian agent, Mueller has seen to it that liberals are as unsympathetic to his plight as the most militant conservative, if not more so. He transformed Assange into the perfect scapegoat for Democrats and Russians to bash with bipartisan glee.
This is why a defense based purely on the First Amendment will not do. Rather, it’s important to deal with the charge of Russian collaboration that – completely unjustly – has turned him into an object of public opprobrium. It’s time to give the Mueller report the scrutiny it deserves before its collective falsehoods undermine democracy even more than they already have.
Russia isn’t only behind election hacking! They’re also trying to smear US over coronavirus … according to State Department
RT | February 22, 2020
Not satisfied with just blaming Russia for election meddling, US officials are now claiming Moscow is trying to “sow discord” by spreading disinformation about the coronavirus and the US’ role in its creation and global response.
US State Department officials are claiming Moscow is behind an internet campaign to blame the coronavirus on the US government.
Without citing specific examples, officials told AFP that the foreign nation is using “false personas” to spread conspiracy theories about the virus, including that the virus is the US’ attempt to “wage economic war on China” and that it could be a biological weapon deployed by the CIA to “spread anti-China messages.”
The messages are apparently spread through thousands of online accounts, run by people and not bots, which post similar messages in multiple languages and can be “linked back to Russian proxies.” The unknown number of accounts all received “carte blanche” from the Russian government to say whatever they can to damage the US’ reputation, the report claims.
Philip Reeker, the acting Assistant Secretary of State for Europe and Eurasia, says Russia’s intent in this loosely-detailed effort is to “undermine US institutions and alliances from within.”
The disinformation campaign was supposedly flagged in mid-January, with even media companies like RT and Sputnik being named as part of the effort to push anti-US messages in relation to the virus.
“The Russian strategy is to very cheaply but very effectively take advantage of the information environment to sow discord between us and China, or for economic purposes,” said Special Envoy Lea Gabrielle, head of the Global Engagement Center, which is supposed to identify and combat propaganda. Why Russia needs to “sow discord” between the US and China, when Washinton has been doing it successfully over recent years was not explained. Relations between the two countries have already soured due to Trump’s trade negotiations, imposed tariffs and even labeling the country a “threat to the world” before the coronavirus ever became a situation.
The State Department also blamed this campaign of “Russian talking points” for slower responses to the coronavirus in Africa and Asia.
All this information is supposedly gathered in a report by the Global Engagement Center (GCE) and seen by AFP. The State Department’s GCE has a sketchy history of being accused of spreading its own propaganda, like a $1.5 million program that was deployed to discredit any and all critics of Trump’s policies in Iran. The account @IranDisinfo was running smear campaigns against anyone, including journalists, who dared to challenge the president’s hawkish policies, despite the account supposedly being meant to only combat Islamic State (IS, formerly ISIS) propaganda.
For those keeping track at home, US officials have now blamed Russia for not only using the coronavirus to try and hurt the US’ “reputation,” but they have also conspired with Trump to win the 2016 election – a narrative House and Senate Dems are still pushing even after the two-plus year Mueller investigation came up limp – and worked to build up the campaigns of non-mainstream Democrats like Tulsi Gabbard, whom Hillary Clinton previously claimed is a “Russian agent,” and Bernie Sanders. It’s difficult to tell how Russia is functioning as a country if they are behind all of these elaborate campaigns US officials blame them for.
Israeli court orders Facebook to unblock account of NSO Group employee
MEMO | February 18, 2020
A Tel Aviv court ordered Facebook Inc to unblock the private account of a worker at Israeli surveillance company NSO Group, and similar rulings are expected for other employees in the coming days, an NSO spokeswoman said on Tuesday.
A group of NSO employees filed suit against Facebook in November, saying the social media giant had unfairly blocked their private accounts when it sued NSO in October.
Facebook-owned messaging service WhatsApp accused the Israeli firm of helping government spies break into the phones of about 1,400 users in a hacking spree targeting diplomats, political dissidents, journalists and senior government officials across the globe.
The NSO employees said their Facebook and Instagram accounts, and also those of former workers and family members, had been blocked.
Ruling on their complaint, Tel Aviv District Court ordered the account of one employee to be restored by Wednesday afternoon.
“We are certain that following the court’s unequivocal statements, Facebook will reverse the action it took against other employees,” the NSO spokeswoman said.
Facebook officials could not immediately comment.
The company said in November it had disabled “relevant accounts” after attributing a “sophisticated cyber attack” to the NSO Group and its employees, saying the measure was necessary for security reasons.
Read also:
UK to help controversial Israel spyware firm to sell product
The Death Of Free Speech: Zuckerberg Asks Governments For Instructions On “What Discourse Should Be Allowed”
By Jonathon Turley | February 17, 2020
I have written for years on the effort of European countries to expand their crackdown on free speech globally through restrictions on social media and Internet speech. It appears that Facebook chief executive Mark Zuckerberg has relented in what may prove the death knell for free speech in the West. Zuckerberg seems to relent in asking governments for regulations stipulating what speech will be permitted on Facebook and other platforms. It is the ultimate victory of France, Germany, and England in their continuing attack on free expression though hate speech laws and speech regulation.
Zuckerberg told an assembly of Western leaders Saturday at the Munich Security Conference that “There should be more guidance and regulation from the states on basically — take political advertising as an example — what discourse should be allowed?” He did add: “Or, on the balance of free expression and some things that people call harmful expression, where do you draw the line?” The problem is that his comments were received as accepting that government will now dictate the range of free speech. What is missing is the bright line rule long maintained by the free speech community.
As tragically demonstrated in France, Germany, and the United Kingdom, speech regulations inevitably expand with time. The desire to silence one’s critics becomes insatiable for both governments and individuals.
Zuckerberg is facing great pressure, including from Democratic leaders in the United States, to regulate political speech and he seems to be moving away from the bright-line position against such regulation as a principle. Instead, he is accepting the fluid concept of “balanced” regulations that has always preceded expanding speech codes and criminalization:
“There are a lot of decisions in these areas that are really just balances between different social values. It’s about coming up with an answer that society feels is legitimate and that they can get behind and understand that you drew the line here on the balance of free expression and safety. It’s not just that there’s one right answer. People need to feel like, ‘OK, enough people weighed in, and that’s why the answer should be this, and we can get behind that.’”
NYC Taxpayers Spending Millions on Cyber Center with Controversial Ties to Israeli Intelligence
Graphic by Claudio Cabrera
By Whitney Webb | MintPress News | February 14, 2020
Early last week, the city of New York launched — with little media scrutiny — one of two new massive cybersecurity centers that will be run by private Israeli firms with close ties to Israel’s government, the so-called “Mega Group” tied to the Jeffrey Epstein scandal and prominent pro-Israel lobby organizations operating in the United States. The centers were first announced in 2018 as was the identity of the firms who would run them: Israel-based Jerusalem Venture Partners and SOSA.
As MintPress has reported on several occasions, all three of these entities have a history of aggressively spying on the U.S. federal government and/or blackmailing top American politicians, raising concerns regarding why these companies were chosen to run the new centers in the heart of Manhattan. The news also comes as Israeli cybersecurity companies tied to Israeli military intelligence Unit 8200 were revealed to have access to the U.S. government’s most classified systems and simulating the cancellation of the upcoming 2020 presidential election.
The new cybersecurity centers are part of a new New York City public-private partnership called “CyberNYC” that is valued at over $100 million and officially aims to “spur the creation of 10,000 cybersecurity jobs and make New York City a global leader in cyber innovation.” CyberNYC is an initiative of New York City’s Economic Development Corporation.
However, the companies that will be responsible for creating those cybersecurity jobs will benefit foreign companies, namely Israeli and most of the jobs to be created will go to foreigners as well, as media reports on the partnership have quietly noted. Those reports also stated that, while the stated purpose of the centers is to create new jobs, the Israeli firms chosen to run them — Jerusalem Venture Partners (JVP) and SOSA — view it as an opportunity to provide Israeli cybersecurity companies with a foothold into the American market and to see Israeli cybersecurity products adopted by both small and medium-sized American businesses, not just large corporations and government agencies.
For example, the founder of JVP and former Knesset member, Erel Margalit, told the Jerusalem Post that “the center we are setting up [in New York] will assist Israeli hi-tech companies in collaborating with customers and companies in the US and around the world.” More recently, ahead of the opening of the cybersecurity center that Margalit’s firm will manage, he told the Times of Israel that “New York is about something else, it’s about the drama of taking investors from Israel and Spain or Paris and other places and taking them to the next business level.” In other words, the companies set to benefit from these new centers will be foreign and mainly Israeli, as JVP invests the vast majority of its funds in Israeli start-ups.
Given that Wilson Lin, the head of CyberNYC, explained the reason behind the initiative is the fact that “there are not enough well-trained people in cyber security to fill the jobs that are required for a safer, more thriving commercial sector,” the statements of JVP’s founder strongly suggests that those “well-trained people” will not be Americans in New York, but will be brought in from abroad, namely Israel’s cybersecurity sector.
Of the companies chosen by CyberNYC to run its new cybersecurity centers, both have clear and demonstrable ties to Israel’s government and military intelligence as well as controversial groups of pro-Israel donors with considerable political clout in the United States.
For instance, Jerusalem Venture Partners was founded by Erel Margalit in 1993, with funding from the Yozma Program, an Israeli government program to “incentivize venture capital investment” in Israel. Since then, it has been a driving force in the development of Israel’s hi-tech sector and regularly collaborates with the Israeli Ministry of Economy and Industry and the EISP (Entrepreneurship and Innovation Support Program) alumni organization of Unit 8200. Today, it is the second largest venture capital fund in Israel.
JVP was also the sole venture capital fund chosen to partner with Israel’s government and military to establish the public-private “cyber hub” in Beersheba. This “hub” not only houses the IDF’s technology campus, but also the Israel National Cyber Directorate, which reports directly to Israel’s Prime Minister, as well as a high-tech corporate park that mostly houses tech companies with ties to Israel’s military intelligence apparatus. The area has been cited in several media reports as a visible indicator of the public-private merger between Israeli technology companies, many of them started by Unit 8200 alumni, and the Israeli government and its intelligence services.

A composite image of the future JVP-funded New York City cyber center. Photo | JVP Press Release
In addition to JVP’s close ties to Israel’s government and its key role in the merging of Israel’s private cybersecurity sector with Israeli military intelligence, JVP also has close ties to the Bronfman family through its Chief Operating Officer and general partner, Fiona Darmon. Prior to working with JVP, Darmon worked for Claridge Israel, the investment arm of the Bronfman family that was founded by Charles Bronfman in 1987.
Charles Bronfman was a one-time business partner of Mossad agent Robert Maxwell, father of Jeffrey Epstein’s alleged madam Ghislaine Maxwell, and co-founded the “Mega Group”, a group of pro-Israel oligarchs with clear and direct ties to organized crime, alongside Leslie Wexner, the main financier of Jeffrey Epstein’s operation that involved the sex trafficking of minors on behalf of Israeli military intelligence.
SOSA was founded much more recently than JVP, yet also has close ties to Israel’s government and military. Created in 2014, SOSA has grown rapidly by connecting mostly Israeli start-ups with investors and through its partnerships with the IDF. This partnership first became clear in 2018, when SOSA created the Homeland Security (HLST) Innovation Hub, which the Times of Israel described as “a first of its kind program that aims to create a defense and security innovation community that will match homeland security and defense industry firms with startups, to help industry giants maintain their leading edge.”
Last year, SOSA became one of two companies to manage the Israeli Ministry of Defense’s program INNOFENSE, an innovation program for civilian tech start-ups in the country’s defense industry. SOSA’s collaboration with the IDF also involves the creation of “joint business activities between international companies, [government] security organizations, investors and startups,” making SOSA a key player in the blurring of the line between Israeli military intelligence and its private tech sector.
SOSA is also directly partnered with two of Israel’s top weapons manufacturers, Rafael Advanced Defense Systems, as well as defense electronics companies ELTA Systems and Elron Electronics, the former parent company of another Israeli weapons manufacturer Elbit Systems. It is also partnered with the Unit 8200 alumni-founded tech company CheckPoint Systems and Leumi Tech, the hi-tech subsidiary of one of Israel’s largest banks, Leumi. Leumi Tech exists only in the U.S. and specifically aims to “provide a comprehensive suite of products and services to Israeli high-tech companies operating in the US.” The bank was recently forced to pay $400 million to the U.S. government for assisting U.S. citizens, most of them dual U.S.-Israeli citizens, in preparing false tax returns and hiding their assets in offshore accounts.
SOSA’s General Manager Guy Franklin is of particular interest, due to his close ties to the Israeli American Council (IAC), a pro-Israel lobby group created by convicted felon and ultra-Zionist millionaire Adam Milstein and largely funded by Sheldon and Miriam Adelson. The Adelsons are also the largest donors to both President Trump and the Republican Party in the United States.

In this photo posted on SOSA’s Facebook page, SOSA execs Uzi Scheffer and Guy Franklin pose in New York’s Time Square
Of the $100 million in funding for the CyberNYC initiative, $30 million comes from New York taxpayers and the remaining funds coming from the program’s partners, which includes Goldman Sachs and the Israeli military intelligence Unit 8200 incubator Team8, a start-up accelerator which has been discussed at length in several past MintPress News reports, including the recent MintPress investigation into the Israeli company Cybereason — a partner of Team8.
Team8, particularly its presence in New York, has long been associated with the push by pro-Israel political donor and American hedge fund manager Paul Singer and Israel’s government to make Israel the global cybersecurity leader as a means of preventing countries from boycotting Israel over human rights violations and war crimes. Team8’s role in CyberNYC will see them not only finance part of the initiative but also training cybersecurity workers who will be hired as part of the partnership.
Singer, who is based in Manhattan, created Start Up Nation Central in 2012 to specifically outsource American tech jobs to Israel in collaboration with top AIPAC officials and Israel’s government. Meanwhile, in parallel, Israel’s government and intelligence apparatus began a policy that same year that involved outsourcing intelligence and military intelligence operations to private companies created for that very purpose, particularly in the field of cybersecurity.
Thus, much as Israel’s cybersecurity industry has long been fused to Israel’s military and intelligence apparati, the Paul Singer-funded and Israel-backed policy has openly sought to bring American companies and government agencies into the fold in order to prevent boycotts of Israel. Though the so-called “anti-BDS laws” that have been passed in several U.S. states are one facet of this push, the use of Israeli tech, namely cybersecurity, sector to pursue this same end has received decidedly less coverage.
New York City has long been a major focus on this policy, with the growth of Israel hi-tech start-ups present in New York and run by former members of Unit 8200 exploding since this policy officially began in 2012. Indeed, Haaretz noted that, between 2013 and 2017 alone, the number of Israeli tech start-ups in New York City grew by fivefold and the number of Unit 8200 alumni working in NYC tech start-ups has also spiked in that same time frame.
The number of Unit 8200 alumni working in NYC’s tech sector has grown so much that they host an annual gala closed to the press where the goal, per Haaretz, is “to try to connect startups and early stage entrepreneurs from 8200 EISP (the Israeli accelerator for Unit 8200 alumni) with clients and venture capital funds in the United States.” One of the main players at that gala is Guy Franklin, the CEO of SOSA, which was chosen to run the other NYC cybersecurity sector.
The decision to create expensive, new cybersecurity centers run by JVP and SOSA, two Israeli firms with clear ties to controversial pro-Israel lobby organization and donors as well as Israel’s government and intelligence apparatus, reveals that not only is this Singer and Israel-backed policy continuing to develop and expand at a rapid pace, but now the money of New York City taxpayers is now being used to propel it to new heights even though that very policy benefits Israel’s economy at the U.S.’ expense.
Whitney Webb is a MintPress News journalist based in Chile. She has contributed to several independent media outlets including Global Research, EcoWatch, the Ron Paul Institute and 21st Century Wire, among others. She has made several radio and television appearances and is the 2019 winner of the Serena Shim Award for Uncompromised Integrity in Journalism.
State-backed Alliance for Securing Democracy disinfo shop falsely smears The Grayzone as ‘state-backed’
By Alex Rubinstein | The Grayzone | February 13, 2020
The Alliance for Securing Democracy, an online censorship initiative of the Western government-funded German Marshall Project, falsely and hypocritically characterized The Grayzone and independent journalist Jordan Chariton as “state-backed media,” smearing them for their factual reporting on the shadowy network behind the controversial app that undermined the integrity of the Iowa caucuses.
The Grayzone has exposed the Alliance for Securing Democracy (ASD) in a series of investigative reports as a neo-McCarthyite outfit prone to spreading disinformation, staffed by counter-terror cranks and national security hustlers.
The ASD’s parent organization also happens to be bankrolled by the US government, numerous European governments, and the European Union, at the tune of millions of dollars — making these false accusations against The Grayzone and Jordan Chariton actual state-backed smears.
Chariton, who founded the independent progressive news outlet Status Coup, hit back at the ASD’s outrageous claims. “The days of faux democracy gladiators defaming journalists – whose factual work they seek to discredit – as part of a Kremlin syndicate are over. It’s time to fight back,” he told The Grayzone.
On February 10, the ASD published a dubious analysis of a supposed Russian effort to spread conspiracies and disinformation around the Iowa caucuses. It honed in on the Russian-funded Sputnik News and three shows broadcast by RT. Those programs included “Going Underground,” which is hosted by British journalist Afshin Rattansi.
The post continued: “In addition, all the most popular tweets about Iowa retweeted in this time period by at least one monitored account pushed a narrative that the Democratic National Committee and/or the Democratic establishment more broadly seeks to undermine Sanders via nefarious means. Monitored accounts ‘Redacted Tonight’ (@redactedtonight) and ‘Watching the Hawks’ (@watchinghawks) are the primary accounts engaging directly with this material.”
“Watching the Hawks” is hosted by American journalist and son of former Minnesota Governor Jesse Ventura, Tyrel Ventura. “Redacted Tonight” is a political satire show hosted by American comedian Lee Camp. Camp opens each show by welcoming his live studio audience to “the comedy show where Americans in America covering American news are called foreign agents.”
The social media managers for both “Watching the Hawks” and “Redacted Tonight” are US citizens.
Nonetheless, the retweeting by these shows of factual reporting by The Grayzone and Jordan Chariton set off national security alarm bells among the disinformation warriors of the Alliance for Securing Democracy.
The Grayzone article that the ASD took issue with exposed the role of pro-Israel billiionaire Seth Klarman in pouring his money into the Super PAC behind the faulty Iowa vote results app, while at the same time donating directly to candidate Pete Buttigieg – the candidate who benefited the most from the sabotage of the caucus results.
The Klarman Family Foundation also happens to be a major funder of the ASD.
On Twitter, the ASD muddled the distinction between The Grayzone, Chariton, and the RT-sponsored Twitter accounts that retweeted them. The outfit claimed that “state-backed media accounts spread various conspiracy theories about the Iowa caucuses, many of which claimed the DNC, news media, and other candidates used “dirty tricks” to steal the victory from Sen. Bernie Sanders.” Attached to the tweet was a screenshot of tweets by The Grayzone and Chariton, making no mention of either “Watching the Hawks” or “Redacted Tonight.”
The false accusation was subsequently retweeted by ASD founder Clint Watts.
The Grayzone editor Max Blumenthal responded to the smear with indignation: “Neither Jordan Chariton nor The Grayzone are state-backed media, unlike your fiscal parent. And our reporting is 100% factual, unlike yours,” Blumenthal wrote on Twitter. “We are currently exploring options for holding your McCarthyite operation fully accountable for spreading malicious disinformation.”
After enduring a withering barrage of online criticism for its malicious falsehood, the ASD issued a weasely “clarifying point.”
The Alliance for securing media citations and grants from oligarchs
The Alliance for Securing Democracy is the most prominent of an array of information warfare initiatives that exploited public hysteria over supposed Russian meddling in the 2016 presidential elections.
The group’s Hamilton 68 Dashboard claimed to have tracked 600 Twitter accounts supposedly “linked to Russian influence operations.” In the mainstream press, that dubious claim was stretched even further as the dashboard was touted as a tool for keeping tabs on “Russian bots.”
Among the widely cited claims of Russian covert influence campaigns was the #taketheknee trend inspired by blacklisted NFL quarterback Colin Kaepernick’s high-profile protest of police brutality. The ASD’s cynical accusation, that a domestic protest movement against racism was being manipulated by the Kremlin, was reported uncritically by the New York Times.
The ASD has even claimed that Stars and Stripes, a military publication operated out of the Department of Defense, was an outlet “relevant to Russian messaging themes.” It has made similar accusations against The Intercept.
Oddly enough, the sole proprietor of The Intercept is billionaire Pierre Omidyar, whose Democracy Fund is a major financial backer of the Alliance for Securing Democracy.
An ASD fellow who helped design its bogus bot tracker, Andrew Weisburd, has publicly fantasized about the murder of Intercept editor Glenn Greenwald, whom he branded a “traitor.”
Aside from Omidyar’s Democracy Fund, the ASD is backed by Craig Newmark, the namesake of Craigslist, and the Klarman Family Foundation. As The Grayzone recently reported, Seth Klarman is a major funder of pro-settler Israel lobby organizations. He is also a prominent debt vulture strangling Puerto Rico with austerity. And, again, Klarman is a top donor to Buttigieg, the self-declared winner of the Iowa caucuses.
Ascertaining a full picture of just who is backing the ASD is not possible, however, as the organization’s public list of funders “does not include any donors who do not wish to disclose their charitable giving.”
But besides the centrist billionaires that fund it, the group’s fiscal parent rakes in money from Western governments, including the US State Department.
Meet the real state-backed disinfo shop
While the Alliance for Securing Democracy claims to be independently funded, it shares major backers with the German Marshall Fund (GMF), including the Sandler Foundation.
Likewise, Omidyar’s Democracy Fund gave somewhere between $500,000 and $1 million to the GMF, while Klarman Family Foundation chipped in between $250,000 and $499,999.

According to the ASD website, the group is “housed at the German Marshall Fund.”
Unlike The Grayzone and Jordan Chariton, the GMF is a state-backed entity that faithfully pursues the agenda of its government funders.
In the 2019 fiscal year, the German Marshall Fund received $1 million or more from both the German and Swedish foreign offices, at least $1 million from the US State Department, and $1 million or more from the United States Agency for International Development (USAID), a primary arm of the US government for fomenting regime change abroad.
The European Commission — which is the executive branch of the European Union — supported the German Marshall Fund to the tune of between $500,000 and $999,999.
Additional supporters of the German Marshall Fund include branches of the German and US government, anti-communist billionaire George Soros’ Open Society Foundations, NATO, internet giants like Google, the European Parliament, oil companies like Exxon, big agro companies like Bayer, large banks, and an array of global arms dealers such as Raytheon and Boeing.
The Theranos nanotainer of Russiagate online initiatives
The Alliance for Security Democracy’s bogus dashboard was undoubtedly the most-cited authority on Russian bot activity in the media. But its credibility suffered a major blow following a series of revealing remarks by founder Clint Watts, who confessed to Buzzfeed, “We don’t even think [all the accounts we monitor are] all commanded in Russia — at all. We think some of them are legitimately passionate people that are just really into promoting Russia.”
Having banked his credibility on fighting the supposedly pernicious presence of Russian bots, Watts went on to concede, “I’m not convinced on this bot thing.”
The ASD’s faulty methodology was developed by J.M. Berger and Jonathon Morgan. The latter was involved in orchestrating a false flag influence campaign targeting Alabama’s Senate elections, and was banned from Facebook after it was exposed. New York Times reporter Scott Shane, who reported on the disinformation campaign, was also responsible for hyping up the ASD’s supposed findings on the “take the knee” hashtag.
But among the ASD’s cadre of national security hacks, Clint Watts is perhaps the most shameless hustler. As The Grayzone’s Max Blumenthal previously reported, “Watts appears to speak no Russian, has no record of reporting or scholarship from inside Russia, and has produced little to no work of any discernible academic value on Russian affairs.”
In his published work, Watts has not only called for the US to “befriend” the “al-Qaeda linked group” Ahrar al-Sham; he also urged Washington to support “jihadi[s]” in order to deliver “payback” to Russia.
In testimony to Congress in 2017, Watts claimed Russia organized a massive bot attack on his Twitter account after his article urging support for al-Qaeda was published. The tale was not just hyperbole; it appeared to have been a fabrication. He also regaled Congress with a story about RT’s and Sputnik’s coverage of a stand-off at Turkey’s Incirlik Airbase that was completely false.
Clint Watts has admitted to running an influence operation for 15 years aimed at improving approval for US foreign policy in the Middle East, which he has said “had almost no success,” and came at a cost of “billions a year in tax dollars.”
While he hypes his work for the FBI, where he spent at most one year, Watts has spent much of his career at the Foreign Policy Research Institute, a hardline neoconservative think tank founded by an open white supremacist.
And left unmentioned in Watts’ bio is his affiliation with the Central Intelligence Agency: the Agency has published an article he co-authored with former CIA director and current CNN contributor John Brennan.
Besides producing dubious analysis, Clint Watts has exhibited a tendency for paranoid Cold War fantasies. In 2017, he warned an audience that Russia was “trying to knock us down and take us over,” then claimed that his colleagues had seen their computers “burned up by malware” after they criticized Russia.
In response to supposed Russian meddling, Watts has called for interfering in Russia’s elections, “but do[ing] it in line with the founding principles of democracy and America.”
He has also called for a government-imposed censorship campaign inside the United States, demanding it “quell information rebellions that can quickly lead to violent confrontations and easily transform us into the Divided States of America.”
Even as the Alliance for Securing Democracy was exposed by The Grayzone and others as the Russiagate version of the phony Theranos nanotainer – with Clint Watts playing the Cold Warrior analog to Elizabeth Holmes – the state-backed neo-McCarthyite operation has forged ahead, rebranding its dashboard as “Hamilton 2.0” and rolling out an “Authoritarian Interference Tracker.”
Currently, the ASD is hyping up claims by NATO vassal state Estonia about Russian interference in their country, according to its “Authoritarian Interference Tracker.” Coincidentally, former Estonian president Toomas Hendrik Ilves sits on ASD’s advisory council.
He is joined on the ASD board by Michael Chertoff, the notoriously self-dealing former Department of Homeland Security chief; and by John Podesta, who workshopped ways to “stick the knife” into Bernie Sanders while leading Hillary Clinton’s presidential campaign in 2016. Podesta was recently nominated to the 2020 Democratic Convention Rules Committee.
Also on the ASD advisory council is neoconservative extraordinaire turned liberal media’s favorite Never-Trumper Bill Kristol, who is widely acknowledged as the leading media and think tank influencer behind the US invasion of Iraq. Kristol has called for a deep state coup to depose Trump, and is rolling out a wave of ads to undermine Bernie Sanders.
Former CIA director Michael Morell, who offered unsolicited advice on killing Russians and Iranians in Syria during a televised interview, and the obsessively anti-Russian former US ambassador to Russia Michael McFaul also occupy seats on the council.
While the ASD couches its work as an attempt to counter Russian disinformation, a clear pattern has emerged of efforts to suppress domestic reporting in the US that doesn’t conform to the imperial foreign policy consensus.
As The Grayzone previously reported, senior German Marshall Fund fellow and neocon movement veteran Jamie Fly appeared to take credit for a purge of popular Facebook accounts of alternative media outlets including The Free Thought Project, Anti-Media, and Cop Block. He promised it was “just the beginning.”
Now, the Alliance for Securing Democracy has trained its guns on The Grayzone. And with its latest falsehood, this malign organization has targeted an independent journalistic organization that has done more than any other to hold it accountable.
Alexander Rubinstein has covered foreign policy, police, prisons, and protests for a variety of publications including The Grayzone and Mint Press News. Follow him on Twitter at @RealAlexRubi.
The Washington Mandarins and Veteran Disinformation Spooks Behind Stanford’s Internet Observatory
By Morgan Artyukhina | Sputnik | February 13, 2020
Stanford University’s Internet Observatory (SIO) is the latest in a growing network of cybersecurity groups policing the activities of social media users, pushing a pro-State Department line about Washington’s adversaries, and spreading the fear of disinformation that’s driving popular support for renewed conflict with Russia and other nations.
This article will pull back the veil on one of the fastest-growing institutions in the US Security State’s information war. Some of the observatory’s central figures include Facebook’s security chief during the Cambridge Analytica scandal, leading academic champions of Western triumphalism and US policy advisers, and even a lead researcher from a cybersecurity group previously exposed as being itself a disinformation outfit.
‘Rebuilding the Arsenal of Democracy’
Formed just this past summer, the observatory is attached to Stanford University’s Cyber Policy Center instead of a think tank like the Atlantic Council’s Digital Forensic Research Lab or operating as a for-profit cybersecurity company, like FireEye. In line with its more academic focus, SIO offers cybersecurity courses for students, such as program Director Alex Stamos’ popular “HackLab” course, “Trust & Safety Engineering,” and “Online Open Source Investigation,” as well as grants for full-time researchers and post-doctoral students, counting among its staff senior Stanford academics.
Startup funding for the Observatory came from Craig Newmark Philanthropies, a $5 million gift to fund nearly a dozen researchers for two years. Newmark, the billionaire founder of the website Craigslist, has quietly established a name for himself as another bankroller of State Department-approved media organs, alongside eBay founder Pierre Omidyar, oil tycoons the Koch brothers, and investor George Soros. Sputnik’s inquiries to Stamos about potential future funding sources were not returned by the time this story went to publication.
Newmark’s justification for supporting the Observatory serves as an effective summary of his efforts in this field:
“What we’re doing is rebuilding the arsenal of democracy,” he told Reuters in July 2019. On another occasion, Stanford quoted him as saying: “The strength of our democracy depends on ensuring that all people have access to accurate information. The Internet Observatory has a vision for a trustworthy Web, and I’m proud to support their mission-critical work to grapple with disinformation and other ways that bad actors use tech against the common good.”
Who’s Who at SIO
Heading up the outfit is Alex Stamos, the former security chief at Facebook and a visiting fellow at the conservative Hoover Institution think tank. Not only was Stamos in charge of Facebook’s cybersecurity during the Cambridge Analytica scandal in which some 87 million users had their personal information collected and used, most without their knowledge or consent, by companies intending on helping candidates like Donald Trump shape elections, but when he left Facebook in the summer of 2018 to form the SIO, Stamos’ departure was based primarily in his disagreement with other Facebook executives’ apprehension at surrendering so much user data to cybersecurity firms in their effort to track down supposed Russian political meddling on the site.
Meanwhile, its research team is headed up by Renée DiResta, a Mozilla fellow who’s lectured at events hosted by the arch-conservative Federalist Society. DiResta was also the research director at New Knowledge, ostensibly a cybersecurity outfit that disbanded after it was revealed they had played a deep role in an online disinformation campaign designed to influence the December 2017 Alabama special election in favor of Democratic candidate Doug Jones.
Stanford Internet Observatory Director Alex Stamos (left) and Research Manager Renée DiResta (right), Rod Searcey
While DiResta has sworn up and down that she knew nothing about the disinformation campaign being waged by New Knowledge chief Jonathon Morgan, at the time of the campaign she was also an Advisor on Policy at Data for Democracy, an informal cybersecurity brainstorming and collaboration network set up and coordinated by Morgan.
Other Stanford academics who’ve joined the SIO milieu include “end of history” proponent Francis Fukuyama and Hoover Institute fellows Amy Zegart and Michael McFaul, the latter of whom was also US Ambassador to Russia.
Further, the Stanford Cyber Policy Center’s codirector is Nate Persily, who founded Social Science One in April 2018 to do much the same as the SIO hopes to now: sort through petabytes of privacy-protected data on Facebook users to “investigate the spread of information and misinformation on Facebook, and their impact on elections and democracy,” as Wired put it in July 2018. Indeed, Wired noted Stamos hoped in setting up the Observatory to gain access to Facebook data via SSO.
“There’s an enormous number of questions you can ask about what 2 billion people around the world are clicking and reading and sharing,” Harvard University Institute for Quantitative Social Science director Gay King, who co-founded SSO with Persily, told Wired. The group receives funding from Omidyar-connected groups such as the Knight Foundation, Democracy Fund and the Omidyar Network, as well as the Charles Koch Foundation of conservative oil tycoon fame.
DiResta’s Proximity to Disinformation Electioneering
DiResta became embroiled in this disinformation cauldron as early as November 2016, when she met Mikey Dickerson, a former Obama administration official who served as the first head of the US Digital Service, which managed US government websites and who, according to the Washington Post, “expressed a desire to fight back” against Trump’s election victory.
“There was a feeling after the Trump election that Democrats hadn’t prioritized tech, that Republicans had built this amazing juggernaut machine,” DiResta told the Post in January 2019. “The right wing was running a meme war, and there were these crazy dirty tricks. People wanted to build countermeasures.”
Facebook banned the account of Jonathon Morgan, the CEO of New Knowledge, a cyber firm that meddled in Alabama’s 2017 special election.
Soon after, Dickinson founded American Engagement Technologies (AET), which later played a pivotal role in the Alabama special election, coordinating a massive effort to impersonate Republicans in an effort to discourage Alabamans from voting for Republican candidate and slavery and pedophilia defender Roy Moore. AET was bankrolled by LinkedIn founder Reid Hoffman, who sunk $750,000 into AET, $100,000 of which was used by Dickinson to hire New Knowledge. New Knowledge, in turn, coordinated Project Birmingham, the name of the disinformation effort, as documents obtained by the Washington Post show.
Hoffman has emerged again in recent news as the money behind ACRONYM, the group who sabotaged the February 2020 Iowa Democratic Caucus results in an operation noted by observers to be very similar to that concocted by New Knowledge, including attempting to frame Russians for the interference.
DiResta, in turn, advised AET before it obtained Hoffman’s backing, migrating to New Knowledge in the aftermath of the Alabama campaign, pledging to the Post she knew only of “an experiment in Alabama” but disavowing knowledge of their tactics.
However, DiResta had also joined Morgan startup group Data for Democracy as the group’s Policy Lead in August 2017, a nonprofit network of roughly 1,200 hackers founded by Morgan the previous December to “use data and technology for social impact,” according to its LinkedIn profile, especially “election integrity, disinformation & social network manipulation, transparency, and policy initiatives.” Between these three connections, it seems increasingly unlikely she knew nothing of the tactics behind Project Birmingham – indeed, she had already professed sympathy with just such efforts to “fight back” against Trump.
The Pesky Problem of Privacy
Stamos, in an interview with Reuters, said pressures on Facebook to protect user privacy are making it harder to see and combat misuses on the platform, such as disinformation and election interference.
“The ability to do academic research on what’s happening online has never been worse,” Stamos told Reuters in a July 2019 interview. “What you get is everything encrypted and everything locked up and not available to researchers.”
He specifically blasted the Federal Trade Commission settlement requiring Facebook’s board to create an independent privacy committee and to have greater oversight over third-party apps on its platform, saying the skittishness it creates around sharing users’ data with research groups would be “a blow for the public’s understanding of social media manipulation,” as Reuters summarized it.
Building a ‘Data Clearinghouse’
Indeed, now that Stamos has moved from security chief to academic, he’s renewed his pressure on tech giants to hand over user data for “academic” purposes, successfully winning backdoor access to user and ad data via API gateways from Facebook, Google, and Bing, turning the SIO into what Wired called “his data clearinghouse.”
At the time this article went to publication, Stamos had not answered inquiries by Sputnik about the other social media giants Wired noted the Observatory was courting for API access, including Twitter, YouTube and Reddit.
‘For $5,000 I Can Buy A Whole Lot of Speech’
Like Stamos, DiResta has a history of distrusting online people-to-people networks. In September 2018, she appeared on a panel titled, “Is Social Media a Threat to Democracy? Fake News, Filter Bubbles, and Deep Fakes,” at which she blasted Twitter for enabling “more speech” with its autofill retweet function, noting that “for $5,000 I can buy a whole lot of speech.”
That event, the Reboot 2018 Conference in San Francisco, was hosted by the Federalist Society, perhaps the country’s premier elite club for the Establishment Right, counting so many leading DC policymakers, diplomats and federal judges – including more than half of the Supreme Court – that in January 2019, Washington Post Magazine opined that the Federalist Society had reached an “unprecedented peak of power and influence.”
In describing the panel’s focus, the event handout noted that “Social media companies are under increasing scrutiny for their effect on American society. According to critics, these platforms promote hyper-partisanship, disinformation, extremism and even violence. They are also blamed for facilitating Russian-sponsored voter manipulation during the 2016 election. Our panel of experts will discuss these challenges as well as their implications for the upcoming election.”
Renee DiResta speaking at Reboot 2018 Conference in San Francisco, October 2, 2018, Sputnik Screenshot
Pruning Facts: Be More Like Google!
Since its formation, the Observatory has rushed to embrace the standard of “Russian disinformation campaigns,” turning out several reports ostensibly documenting such efforts in Africa, and also attacking Bing for failing to prune their search results of pro-Russian links.
While the SIO purports to have identified “Evidence of Russia-Linked Influence Operations in Africa,” as the title of an October 2019 report suggests, in truth they offer nothing but insinuation and supposition. The report itself admits they “cannot independently verify” their most contentious claim, that the Russian security contractor “Wagner Group” is behind a supposed “Facebook operation” in Libya.
Further, the extent of their proof of “Russia-linked organizations likely operating at least in part at the behest of a state actor” that shared “tactical similarities to Internet Research Agency activities” extends to little more than native-speakers speaking well of local initiatives tied to the Russian government and Facebook pages that “often re-posted Sputnik articles.” Quelle horreur!
This is the same kind of suggestive wording obfuscating ignorance that FireEye and the Atlantic Council’s DFRL have employed in claiming to identify disinformation campaigns by US targets for regime change, including Russia but also Venezuela, Iran, and China, among others.
For example, as Sputnik has reported, during the regular purges carried out by Twitter and Facebook, the cybersecurity reports used to justify the purges routinely enjoyed only moderate or low confidence by the researchers, and in at least one instance in May 2019, Twitter Site Integrity chief Yoel Roth was forced to admit they never looked at FireEye’s report before summarily deleting 2,800 accounts “linked to Iran.”
In another report in December 2019, the SIO faulted Microsoft default search engine Bing for failing to prune its search results as efficiently as Google does, specifically naming higher-ranked links to Sputnik and RT stories on search terms like “novichok,” “Skripal,” and “MH17” as a problem.
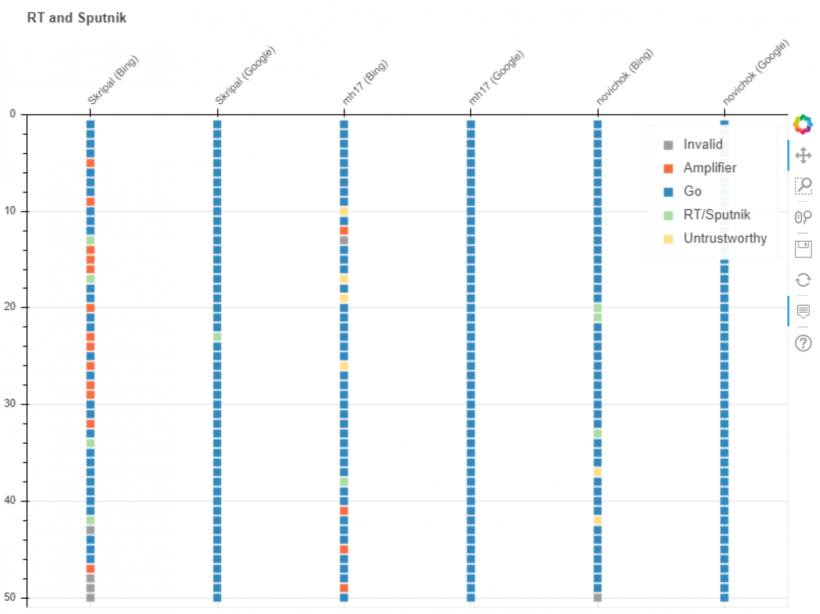
A graphic from a December 2019 report by the SIO showing RT and Sputnik in search results for “skripal” “MH17” and “novichok” on Bing and Google, Stanford Internet Observatory
In an interesting moment of frankness, the SIO admits that Google does, in fact, manually prune its search results – something the tech giant has long maintained it doesn’t do. A November 2019 report by the Wall Street Journal confirmed what documents leaked to the Daily Caller the previous April had hinted at: that Google intervenes directly to “correct” algorithms that yield politically undesirable search results.
“Over time, Google has increasingly re-engineered and interfered with search results to a far greater degree than the company and its executives have acknowledged,” the WSJ wrote, noting the efforts had increased sharply since the 2016 US elections. The litany of manipulations range from “algorithmic changes to its search results that favor big businesses over smaller ones” to making “behind-the-scenes adjustments” to “auto-complete suggestions, boxes called ‘knowledge panels’ and ‘featured snippets,’ and news results, which aren’t subject to the same company policies limiting what engineers can remove or change.”
“Despite publicly denying doing so, Google keeps blacklists to remove certain sites or prevent others from surfacing in certain types of results,” the WSJ report continues. “These moves are separate from those that block sites as required by US or foreign law, such as those featuring child abuse or with copyright infringement, and from changes designed to demote spam sites, which attempt to game the system to appear higher in results.”
From ‘Fake News’ to ‘Disinformation’
The language deployed in the SIO report is also interesting, in that it categorizes stories forwarding a point of view differing from the US State Department’s line alongside conspiracy theory links about Pizzagate, links between vaccines and autism, and white supremacist content, as if they were all just flavors of “fake news” to be purged in the defense of “real” news.
Although US President Donald Trump is credited with popularizing the slander, “fake news” is a narrative swallowed hook, line and sinker in recent years by both tech giants and the billionaire investors who bankroll their growing media networks. For example, in 2015, Craig Newmark Philanthropies joined the Omidyar-backed Knight Foundation, the George Soros-funded Open Society Foundations and the Ford Foundation to back Google’s First Draft News and the Google News Lab, projects that aimed to coordinate “efforts between newsrooms, fact-checking organizations, and academic institutions to combat mis- and disinformation.”
As MintPress News documented, these efforts are just drops in the bucket of a much larger project involving every major US-based tech giant to shape media narratives around the globe to reflect the US State Department line, adopting common definitions of disinformation that dismiss alternative points of view as assaults upon reality.
“Fake news” has dovetailed with “disinformation” to provide a convenient excuse to extend state control over the realm of cyberspace, and the SIO is just the latest instrument in a growing symphony of thought policing.
Featured Video
AIDS Inc. by Gary Null (2007)
or go to
Aletho News Archives – Video-Images
From the Archives
Clash of Civilization, Iran Part II
By Jamal Kanj – Intifada-Palestine.com – January 14, 2011
Israel’s survival kit is: perpetuate conflict, insecurity to rationalize collective hate and finally playing victim.
Devoid of conflict, Israel implodes internally; without hate, Zionism loses its justification; and playing eternal victim to continue blackmailing the West. Absence of this holy trinity, Israel ceases to exist.
From its inception, the house of Zion has mastered exploiting adversarial powers to advance Israel’s cause. For instance, their influence over the Democratic Party in the US began with President Truman’s bid for 2nd term election in 1948.
Responding to strong opposition from Secretary of State General George Marshall and Department experts urging against recognition of Israel, President Truman replied: “I’m sorry gentlemen but I have to answer to hundreds of thousands [Jewish voters] who are anxious for the success of Zionism. I do not have hundreds of thousands of [voting] Arabs among my constituents”
Zionists influence over liberal American politics was matched with the doctrinal school of Conservative theoreticians aligning the Republican Party’s platform with Israel’s objectives. The Neoconservative Zionists, coined Zioncons, invented the “Clash of Civilization” concept to fight Israel’s wars. … continue
Blog Roll
 Aletho News
- Pro-Palestine protesters arrested outside UK’s ruling Labour Conference in Liverpool
- Mauritius denies landing permit to flight from Israel, forcing cancellation: Tour operator
- Israeli finance minister calls for genocidal war on West Bank, annexation of south Lebanon
- 12 Things Your Psychiatrist Was Trained Not to Tell You
- From Unipolar Universalism to Multipolar Civilizational Distinctiveness
- RSF military group defects, joins Sudanese army: State media
- Ireland goalkeeper refuses to play ‘Israel’ as squad weighs boycott
- China pushes back against US on Cuba, Iran
- Ukrainian Soldiers, Potential Mercenaries: Have Gun, Will Travel!
- Burnham’s UN debut… A masterclass in British disinformation
- If Americans Knew
- Israel forces Gazans to live in constant peril – Daily Update
- Deconstructing Netanyahu’s pants-on-fire UN rant – Daily Update
- Trump betrayed voters with his campaign lies and prioritized a foreign country once he took office
- Netanyahu calls Israel’s war in Gaza ‘opposite of genocide’ in UN speech to near-empty hall
- Settler Kidnappings: Torture, Sexual Abuse and Terrorisation of Palestinian Abductees as Israel Deepens Annexation of West Bank
- Gaza winter nears as 162,000 tents become unusable, raising fears of humanitarian crisis
- Netanyahu says, “It’s the opposite of genocide”; UN says Gaza economy is world’s ‘most severe crisis on record’ – Daily Update
- Israel’s US-Backed Assault on Gaza Has Created the ‘World’s Most Severe Economic Crisis on Record’: UN
- ‘Protecting U.S. Citizens’… From Israel
- ‘This is where I live now, the back of a truck’: a day in the life of a grandmother in Gaza
- No Tricks Zone
- New Study: Earth And Venus Surface Warmth Largely Explained By Convection And Lapse Rate, Not CO2 Or Radiation
- 2025 Nature Paper Claiming Worsening Global Drought Gets RETRACTED …Heavily Flawed
- New Study: ‘Global Drought Shows No Detectable Recent Acceleration Under Climate Warming’
- Economic Masterminds: German Socialists Suggest Taxing Productivity Gains Stemming From Using AI
- The South China Sea Has Not Been Cooperating With The Climate Change Narrative
- Energy Crisis: Germany Enters Heating Season With Historically Low Gas Reserve Fill Levels
- New Study: The Antarctic Ice Sheet Gained Mass From 2020-2024 Due To Staggering Snow And Ice Accumulation
- Study: Ocean Heating Rates From Thousands Of Years Ago ‘Dwarf’ Modern Ocean Heating Rates
- Climate Extremists Target, Attack Large-Scale Power Grid Infrastructure In Germany!
- New Study: Antarctic Ice Melt Has Contributed Less Than 1 Centimeter To Sea Level Rise In The Last 30 Years

