‘All the Evidence’ Suggests Guccifer 2.0 is Linked to CIA, Not Russia, NSA Whistleblower Says

© Photo : Bill Binney
Sputnik | August 13, 2020
The internet is not capable of accommodating the download speeds necessary to validate the claims by Guccifer 2.0, that they hacked documents from across the Atlantic, according to a former technical director at the National Security Agency.
Guccifer 2.0, the cyber personality which claimed to have hacked documents belonging to members of the Democratic National Committee in 2016, is likely to be a front for the CIA, according to analysis conducted by members of Veteran Intelligence Professionals for Sanity (VIPS).
Bill Binney, a cryptogropher and former technical director at the US National Security Agency (NSA), blew the whistle on the agency’s mass surveillance programmes after serving with them for 30 years. Mr Binney explains to Sputnik that despite Guccifer 2.0 claiming to have hacked documents which the cyber criminal later published, the download speeds necessary to have obtained the documents simply are not available across the World Wide Web.
Sputnik: What were the conclusions that you came to regarding a cyber personality known as Guccifer 2.0 and his claims that he had hacked a trove of documents?
Bill Binney: Guccifer 2.0, posted files from the 5th of July [2016], the 1st of September [2016] in batch mode. He also put files out in the 15th of June that had Russian fingerprints. So to go straight at those, we had some collaborating analysts looking in the UK, looking at the data also. And they came up with a match of five files out of the Guccifer 2.0 batch on the 15th of June, they found five of those files also posted by Wikileaks in the Podesta emails, the same files. Now, the difference is the Guccifer 2.0 posts had Russian fingerprints. You know, Cyrillic characters and things like that implanted in the file. The WikiLeaks files posted, of those same five emails, did not have Russian signature prints in it. So that told us that Guccifer 2.0 was inserting these Russian fingerprints. And we had some other fingerprint evidence of them using that.
Then, when we looked at the 5th of July 2016 and the September 2016 data that was posted by Guccifer 2.0, he would give a bio, we had extracted file names, number of characters and the timestamp at the end of the file. And he did the batch. So there was one file after the other. It was timestamped at the end of each file. So all we had to do was [assess the] difference in time between the files and see how many characters were passed and we calculate the transfer rate. And when we did that we got rates between 14 and 49.1 megabytes per second. That’s between 19 and 49.1 million characters per second. And we knew that the international web across the Atlantic to Europe, somewhere in Eastern Europe could not handle that kind of rate transfer.
Some people here thought we could. So we said, okay, we’ll try it. And we tried it from Albania, Serbia, Netherlands and the UK. The fastest we got with between two data centres, one in New Jersey and one in the United Kingdom in London. And that was 12 megabytes per second, which is slightly less than one fourth necessary capacity to transfer just the data, not counting overhead that goes with it and all of that… So all of that said to us, it was not there.
Sputnik: Was there anything else?
Bill Binney: There was another factor. We looked at the files again and if you ignored the date and the hour, the two [batches] shuffled together like a deck of cards. That is the times, [if you] looked only at a minutes, seconds and milliseconds, the data from the 1st of September merged into the time holes of the 5 July data. Which meant it was shuffling like one of cards. You have one file, he separated in two, then they had a range change on the date and the hour. You can’t do it on minutes and seconds because they keep changing. I mean, you’d have to go up there every minute and every second you got to know it’s not possible to do that, without extreme effort I’d say. What that said to us was this guy is fabricating the data, he’s playing with the data, he’s playing with us…
Vault 7
Then we went back and looked at the Vault 7 material (descriptions of CIA hacking tools published by WikiLeaks), which said that there’s a programme called Marble Framework, which [the CIA can use to] modify an attack and make it look like someone else did the attack, and the countries they had the capability to do that [to] were Russia, China, North Korea, Iran and Arab countries. Also [Vault 7] said that the Marble Framework programme was [used] one time in 2016. Well, we think we found that one time. That one time came up and that fit very well with what was going on which we were finding out with the Guccifer 2.0 material. He was fabricating it. So that suggested us all the evidence was pointing back to CIA as the originator Guccifer 2.0. And that Guccifer 2.0 was inside CIA.
Sputnik: Just to clarify, the documents Guccifer 2.0 was publishing weren’t what is known as the DNC leaks or DNC hacks that WikiLeaks published in three batches?
Bill Binney: [Yes]. [Gucifer 2.0] claimed to have hacked [the documents he published].
The Hammer
There’s another whistleblower that we’re working with also and they’ve talked to us about a programme called The Hammer. This programme was set up inside CIA by, according to the whistleblower, by [former Director of National Intelligence James] Clapper and [former CIA chief John] Brennan. And it was done so that they could spy on anybody they wanted to, without anybody in the intelligence community or the US government or any other government knowing they were doing it. The programme actually goes… back to 2003, I believe, with you when they first set it up. But [the whistleblower] also said that after that they had a secret operation inside CIA, by this group of people inside CIA looking at the Trump campaign and anybody else they wanted to sign on.
And it was done in that way, because, see, if you go into the NSA data and which the Five Eyes can do that as well, if you do that, anybody going in there, you’re tracked and recorded [when you use the surveillance system]. It’s wherever you go and what you do. And that’s based on the network logs. And also if you do an unmasking, you have to make a request and that’s recorded, who did it, what time, what the subject was and what the justification was and what person they were after. So, you know, all that stuff is recorded to go there. But if you set up your own separate one, nobody knows what you’re doing. And that’s exactly what this [whistleblower] is claiming. I’m pointing to that group as the group that was probably the originator of Guccifer 2.0 and also this fabrication of the entire story of Russiagate.
This interview has been edited for clarity and concision.
‘We Have Absolute Proof’ DNC Leaks Were Not Hacked, NSA Whistleblower Says
Sputnik – 12.08.2020
Because the National Security Agency is tapped into data transfer points throughout the United States, via its mass surveillance programmes, if there was any evidence that the DNC servers were hacked then they would have the evidence to prove it, a former technical director at the agency explains.
Documents published by WikiLeaks that belonged to the Democratic National Committee (DNC) could not have been hacked via the internet and must have been initially downloaded from within the US, according to an investigation by members of Veteran Intelligence Professionals for Sanity (VIPS).
Bill Binney, a cryptogropher and former technical director at the US National Security Agency (NSA), blew the whistle on the agency’s mass surveillance programmes after serving with them for 30 years. Mr Binney detailed for Sputnik why the forensic evidence proves that key claims of Russiagate (regarding Russian officials hacking the DNC servers) are a “farce”.
© Photo : Bill Binney
Sputnik: A recent investigation by you and some of your colleagues at Veteran Intelligence Professionals for Sanity determined that the Democratic National Committee documents published by WikiLeaks in 2016 could not have been hacked by actors outside the US and instead had to have been downloaded onto a USB or CD-ROM.
Bill Binney: Yes, that’s right. And we have forensic evidence to prove it.
Sputnik: Could you please break down, for the average layperson, exactly how you came to this conclusion?
Bill Binney: Well, we did it by looking at the published DNC emails by WikiLeaks. In other words, the original assertion was that the DNC data was hacked externally, from Russia or by the Russians in Europe or something, and then transferred to WikiLeaks to publish so they could influence the election.
We looked at the DNC emails that were documented by WikiLeaks on the web. And that came down in three groups. One came down on 23rd of May 2016 and the other 25th of May 2016 and then one on the 26th of August of 2016. All of those three batches of emails had last modified times ending in an even number and even second, rounding up to the second, not including milliseconds. So, that meant to us that that was the property of the FAT (file allocation table) format. It’s a programme that when you read data to a thumb drive or CD ROM, and the programme indexes stuff on the [CD] and the thumb drive, for example, it then also rounds off the last modified time to an even number. That tells us very simply that there is 35,813 emails, all with the same property FAT file formatting saying that hey this was read [ie downloaded] to a thumb drive or a CD ROM before WikiLeaks got it to publish. Which meant it was physically transported to WikiLeaks. So, for us, that meant it was not a hack. Period.
We also had [CEO of cyber security firm Crowdstrike] Shawn Henry give testimony, I think it was the 7th of January of 2017, the secret testimony that just came out, where he said ‘we had indications that the data was exfiltrated, but we didn’t see the data exfiltrated’. Well, the indications that it was [exfiltrated], is this a FAT file format, to my mind. I mean, Shawn Henry never said specifically why his people were saying that. So for us, the only thing he could be [basing] it on what was last modified time.
Sputnik: So, just to be clear, when information is downloaded onto a CD roam or thumb drive, you’re saying that there’s a particular process, which means that, the last modified time will be recorded in such a way onto those files that is different than if those files were hacked and taken from a server across international boundaries or across a very long distance.
Bill Binney: Right. And we had provided all this data to the courts. Also we’ve included the Podesta emails, which show how a hack could occur and what the last modified times looked like. And that’s a, that’s also published by WikiLeaks, I think on the 21st of September [2016], that’s the date for that, that they put it out there. And the modified times of those files… close to 10,000 of them I think, run through even and odd numbers and various times, including milliseconds, things of that nature. So all that stuff, all that data, we provided to several courts, and several sets of lawyers to introduce as evidence in court and we were prepared to testify to that in court.
Sputnik: And is it not possible for the last modified time to be changed somehow or modified itself?
Bill Binney: Sure, but I don’t know of a programme that does, other than FAT, I mean, keeping in mind, you’re talking about 35,813 files. If you want to change them, you can go in and do them individually one at a time. I don’t know of any other programme that does it automatically, which is what what’s happened here, because it’s just a straightforward consistency. Humans make errors. If they go in and do something like that, they’ll make errors somewhere in the files. We didn’t see any errors at all. So that’s a program doing [it].
Sputnik: How many people from VIPs would you say were involved in this investigation that you conducted?
Bill Binney: Probably about six and a couple of auxiliaries, as we call them, in the UK cooperating with us. And we had a couple other people from outside VIPS helping us because they were also interested in getting to it too. Also, people who retired from commercial companies, running fiber lines and things like that.
Sputnik: If you were still working at the NSA and you were tasked to investigate an alleged hack would you have additional technical resources if you worked for the government, then if you’re doing it independently?
Bill Binney: Yeah, absolutely. This is one of the reasons why I started in August of 2016 saying that this entire Russiagate story was a farce. And that basically came out by knowing the capacity of NSA. The capabilities of them being able to capture stuff on the web. I mean, [the NSA] have over almost a hundred tap points inside the United States, all loaded up with fiber optic lines… You know, it can take everything off those lines and capture it. [A]nd that was true across the US as well as all the external points exiting and entering where you exit and enter the US.
And you’ll notice that NSA never said they saw any of the data transferring anywhere on any line. And that’s because it didn’t, it went on a thumb drive, you know, that’s the difference. That was one of the main reasons I said that this was not a hack. Because if it was NSA would have it. Like they did when the Chinese hacked one of the places over here in the US about six years ago. The government said, the hack came from this building in Shanghai.
Sputnik: And is there any kind of a practical or legal consideration as to why the NSA can’t publish its findings regarding the DNC servers?
Bill Binney: Actually, there isn’t, if the president approves, I mean, he can declassify anything he wants.
Sputnik: So where do you go from here? Is there more to investigate in relation to this subject or is this the end of the matter for you?
Bill Binney: As far as I’m concerned, we have absolute proof that this whole thing […] Russiagate, is a fabrication. It was a fabrication of the FBI, CIA and the DOJ primarily, but also included the State Department and [Department for Homeland Security] and a number of other departments.
Sputnik: There are those that argue Julian Assange will have a fair trial in the US should he be extradited. What can you tell us about the U.S. District Court for the Eastern District of Virginia, where Mr Assange would be tried?
Bill Binney: That’s a court that’s pro CIA because it’s in that jurisdiction of CIA. This is why they picked that court because it’s pro CIA and whatever national security issues come up, they will always go with that national security. So, you have a prejudiced judge in a court to begin with.
Sputnik: Would there be a jury with 12 men and women?
Bill Binney: Pulled from the area and most of them work for the government. So, you know, you just look at it. I mean, that should be a disqualifier as a jury from my point of view. But also think of it this way: Julian Assange published data he was given. So has the New York Times, The Guardian, all the major publications, the Washington Post, they’ve all done that. So why aren’t they being charged also?
Sputnik: Well, the US government is claiming that the first amendment does not apply to foreign journalists.
Bill Binney: Well then why don’t they go after The Guardian ?
Sputnik: Maybe they’re next?
Bill Binney: [I]f you accept their premise – of the US government – that means that any journalist anywhere in the world, publishing any article that exposes crimes by the US government, the US government can charge them with conspiracy to violate national security. So, every reporter in the world is now liable based on that [premise].
This interview has been edited for concision and clarity
Why Immunity for the CIA?
By Jacob G. Hornberger | FFF | August 11, 2020
Amidst the controversy over the doctrine of qualified immunity for cops, no one is talking about the full immunity accorded to the Central Intelligence Agency, an agency within the national-security establishment that wields omnipotent power.
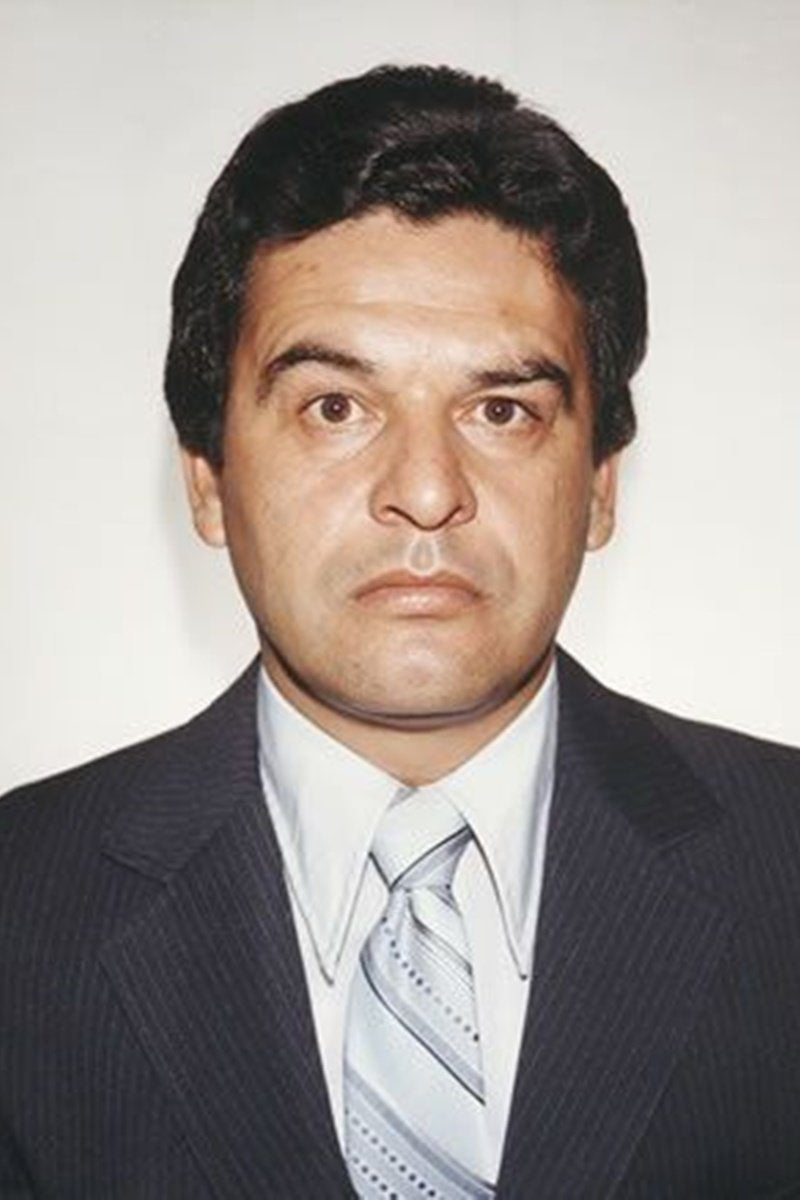 Among the most interesting lines in the new Amazon Prime series The Last Narc is what a CIA official says to DEA investigator Hector Berrellez, who was charged with leading the investigation into the kidnapping, torture, and murder of DEA agent Enrique “Kiki” Camarena. The official tells Berrellez that the CIA is not a law-enforcement agency and, therefore, doesn’t have to comply with the Constitution. Its mission, he said, is to protect the United States. Therefore, the implication is that the Constitution cannot be permitted to serve as a barrier to that end.
That’s the way it’s been since the beginning. The CIA has had omnipotent power to do whatever it deems necessary to protect “national security.” That includes, of course, the power of assassination, a power that the CIA assumed practically since its inception. In fact, as early as 1952, the CIA was developing a formal assassination manual for its assassins.
The CIA also wields the power of torture, the power to record its torture sessions, and the power to destroy such recordings to prevent Congress or the public from listening to them or viewing them.
The CIA also wields the power to lie, at least if it’s in the interest of “national security.”
No one jacks with the CIA. Not the Justice Department, including every U.S. Attorney in the land. Not the Congress. Not the president. Not the military. Who is going to mess with an organization that wields the omnipotent power to destroy or kill people and is more than willing to exercise that power in the name of protecting “national security”?
The kidnapping, torture, and execution of Kiki Camarena
A good example of this phenomenon is found in The Last Narc, which I wrote about in a blog post last week.
In 1985, 37-year-old DEA agent Enrique “Kiki” Camarena was kidnapped on the streets of Guadalajara, Mexico, and brutally tortured for 36 hours before finally being executed.
It was commonly believed that the crime had been committed by the Guadalajara drug cartel, which was headed by Rafael Caro Quintana, Ernesto Fonseca Carrillo, and Miguel Ángel Félix Gallardo, all of whom are featured in Netflix’s series Narcos: Mexico. But Mexican officials steadfastly refused to extradite the three drug lords to the United States for trial.
The DEA assigned Berrellez to take charge of the investigation. Berrellez, who felt as comfortable operating in Mexico as he did in the United States, found three former members of the Jalisco State Police who were willing to talk. They came to the United States and told Berrellez that back in 1985, they had been working double jobs — as state policemen and also as bodyguards for Caro, Fonseca, and Gallardo.
Berrellez interviewed them separately to ensure the integrity of their statements. They each pointed toward complicity of high Mexican officials with the cartel in the distribution of drugs into the United States, which I don’t think would surprise anyone.
The three former cops and bodyguards told Berrellez that they were in the room while Camarena was being tortured. Each of them stated that there were several high Mexican officials present in the house in which Camarena was being tortured while he was being tortured.
The heroism of Hector Berrellez
But then Berrellez discovered something else. According to the three former Mexican state policemen, a man named Max Gomez, also known as Felix Rodriguez, was inside the torture room and taking an active role in the brutal interrogation of Camarena. Berrellez investigated and determined that Rodriguez was a “retired” CIA agent.
Among the principal questions that was being addressed to Camarena was the extent to which he had discovered, in the course of his investigation, the nexus between the drug cartel, the CIA, and the Mexican government in the drug trade.
It was later learned that the interrogation was being recorded, which is something that one would not expect drug lords to do but that one would expect a CIA agent to do.
At that point, Berrellez was in trouble. It’s one thing to conduct an investigation that leads to the Mexican government’s involvement in Camarena’s torture and murder. It’s another thing to conduct an investigation that leads to the U.S. government’s involvement in the torture and murder of a DEA agent who is also an American citizen.
As Berrellez states in The Last Narc, he was warned to back off and let sleeping dogs lie. He was warned that if he didn’t, his life would be in jeopardy. If he didn’t back off, U.S. officials even threatened to forcibly return him to Mexico to face criminal charges that the Mexican government had leveled against him.
But Berrellez refused to back off, and so U.S. officials removed him from the investigation. Even though he could have remained silent, he instead decided to go public with his findings and cooperated in the making of The Last Narc. He comes across as a heroic figure in the series.
For his part, Rodriguez denies that he was in the torture room or that he has had anything to do with Guadalajara cartel and with drug dealing. The problem, however, is that CIA agents will lie if they believe that it is in the interest of “national security.” And they all know that they have immunity when it comes to lying and anything else that touches on “national security.”
Full immunity for the CIA
Here you have a prima facie case of U.S. governmental involvement in the torture and assassination of a U.S citizen, one who was an agent of the DEA. The alleged purpose of the torture was to determine if Camarena had uncovered evidence of CIA complicity with the Guadalajara Cartel and the Mexican government in the drug trade. Three witnesses, all giving their testimony separately, identified Rodriquez as one of Camarena’s interrogators.
That’s clearly enough evidence to launch a formal investigation into the matter. Perhaps it’s worth mentioning that Camarena’s murder took place during Iran Contra, when U.S. officials were breaking the law to raise the money to give to the Nicaraguan contras.
Has any of this caused any U.S. Attorney or the U.S. Congress to launch an aggressive investigation into the matter?
Don’t make me laugh. This is the CIA we are talking about. No one investigates the CIA, which makes the U.S. government as crooked and corrupt as the Mexican government. If you want to get a good sense of how both governments operate, I highly recommend watching The Last Narc.
Jacob G. Hornberger is founder and president of The Future of Freedom Foundation. He was born and raised in Laredo, Texas, and received his B.A. in economics from Virginia Military Institute and his law degree from the University of Texas. He was a trial attorney for twelve years in Texas. He also was an adjunct professor at the University of Dallas, where he taught law and economics.
Political Legitimacy Dies in 2020
By James Bovard | American Institute for Economic Research | July 28, 2020
The American political system may be on the eve of its worst legitimacy crisis since the Civil War. Early warning signals indicate that many states could suffer catastrophic failures in counting votes in November. The election will occur amidst the vast economic devastation inflicted by a political class that responded to COVID by seizing almost unlimited power. And Deep State federal agencies have already proven that they will trample the law to sabotage election results.
America could soon see a hundred-times worse replay of the Florida presidential balloting 20 years ago in the Bush-Gore showdown. Some Florida counties had antiquated voting equipment while others had harebrained ballot designs that confounded voters. The Florida Supreme Court ordered a manual recount of disputed votes but the Supreme Court, in a 5-to-4 decision, stopped the recount because it could result in “a cloud upon what [George W. Bush] claims to be the legitimacy of his election,” Justice Antonin Scalia wrote. Two days, the same Supreme Court majority blocked any subsequent recounting because it was “not well calculated to sustain the confidence that all citizens must have in the outcome of elections.” Unfortunately, “legitimacy via blocked recounts” may also be the epithet for the 2020 presidential election.
Because of the pandemic, many states are switching primarily to mail-in voting even though experiences with recent primaries were a disaster. In New York City, officials are still struggling to count mail-in ballots from the June primary. Up to 20% of ballots “were declared invalid before even being opened, based on mistakes with their exterior envelopes,” the Washington Post noted, thanks largely to missing postmarks or signatures. In Wisconsin, more than 20,000 “primary ballots were thrown out because voters missed at least one line on the form, rendering them invalid.”
Some states are mailing ballots to all the names on the voting lists, providing thousands of dead people the chance to vote from the grave. President Trump claims that the shift to mail-in voting could result in “the most corrupt vote in our nation’s history.” Trump is often wrong on issues but even a New York Daily News article tagged the recent primary results a “dumpster fire.” Delayed election results and potentially millions of disputed ballots could minimize support for whoever is designated the next president.
Elections supposedly choose which candidates are selected to follow the law and uphold the Constitution, but COVID shutdown dictates vividly how political power is now practically unlimited. Michigan governor Gretchen Whitmer prohibited “all public and private gatherings of any size” (prohibiting people from visiting friends) and also prohibited purchasing seeds for spring planting in stores after she decreed that a “nonessential” activity. Oregon Governor Kate Brown banned the state’s four million residents from leaving their homes except for essential work, buying food, and other narrow exemptions, and also banned all recreational travel – even though much of her state had almost zero COVID cases.
In the name of reducing risks, politicians entitled themselves to destroy tens of millions of jobs. Permitting governors to shut down churches was not on the ballot but that didn’t stop many states from banning worship services at the same time politicians cheered mass protests that scorned “stay-at-home” orders.
The media has often whitewashed the damage from COVID power grabs in part because every restriction was supposedly justified by “science.” After New York Gov. Andrew Cuomo dictated that nursing homes must admit COVID patients, more than 6,000 elderly nursing home residents were killed by the coronavirus. Cuomo has yet to reveal which “science” textbook spawned this policy (which several other states also imposed). Were those state governments grossly incompetent or were they murderous? It doesn’t matter because Trump made rude comments about N.I.H. honcho and media darling Anthony Fauci. What’s the point of voting for politicians who merely need to invoke dubious statistical extrapolations to sow death and economic devastation?
Finally, does the presidential election even matter? Deep State federal agencies are a Godzilla that have established their prerogative to undermine if not overturn election results. The FBI has achieved saint-like status among many liberals for its efforts to topple Trump. For almost three years, the nation’s political life was roiled by an investigation driven by false allegations that the Trump campaign colluded with Russia in the 2016 election. As George Washington University professor Jonathan Turley observed last week, the media continues to ignore “one of the biggest stories in decades. The Obama administration targeted the campaign of the opposing party based on false evidence.” Obama officials who exploited the CIA and other intelligence agencies to illicitly target Trump campaign officials have laughed all the way to million-dollar book advances.
During the Trump impeachment effort, the establishment media openly cheered the Deep State. New York Times columnist James Stewart assured readers that the secretive agencies “work for the American people,” New York Times editorial writer Michelle Cottle hailed the Deep State as “a collection of patriotic public servants,” and Washington Post columnist Eugene Robinson captured the Beltway’s verdict: “God bless the Deep State!” The media has almost completely abandoned its watchdog role, and its veneration will make it easier for the FBI, CIA, and National Security Agency to ravage not just elections but also Americans’ rights and liberties in the coming years.
Even before the voting starts, surveys show that for the first time “a majority of Americans (55 percent) are dissatisfied with their system of government,” the Atlantic reported. The percentage of Americans who “expressed trust in government in Washington” has fallen from 73% in 1958 to only 17% now, according to the Pew Research Center. But those numbers could quickly become far more ominous for our political ruling class.
What happens if Trump continues to repel many if not most potential voters, and then Biden comes across in the presidential debates as clueless and doddering as did Special Counsel Robert Mueller in a congressional hearing last July? How many Americans will feel forced to choose between a scoundrel and an idiot?
Many pundits and professors presume that a Biden victory in November will magically re-legitimize the American political system. But almost all the problems of recent years will continue or intensify. The Centers for Disease Control and the Food and Drug Administration, both of which horribly botched the nation’s response to COVID, will continue bollixing public health crises. U.S. foreign policy will continue to be reckless and self-defeating, with American pretensions to global hegemony becoming ever more ludicrous. Deficit spending will continue to spin out of control, spiraling closer to the day when the Federal Reserve’s sorcery fails to entrance financial markets. Unfortunately, both Democrats and Republicans appear willing to bankrupt the nation to perpetuate their own power.
Federal legitimacy hinges on the Constitution, but there is not a snowball’s chance in hell that either Trump or Biden will “make America constitutional again.” As Thomas Jefferson declared in 1786, “An elective despotism was not the government we fought for.” What’s the point of voting if “government under the law” is not a choice on Election Day? American political legitimacy will continue plummeting as long as politicians scorn any legal and constitutional limits on their power.
James Bovard is the author of ten books, including Public Policy Hooligan, Attention Deficit Democracy, The Bush Betrayal, and Lost Rights: The Destruction of American Liberty. He has written for the New York Times, Wall Street Journal, Playboy, Washington Post, New Republic, Reader’s Digest, and many other publications. He is a member of the USA Today Board of Contributors, a frequent contributor to The Hill, and a contributing editor for American Conservative.
Cybereason Announces New Plans to “Accelerate” Access to US Govt Networks Ahead of 2020 Election
By Whitney Webb | The Last American Vagabond | July 27, 2020
A cybersecurity firm tied to Israeli intelligence’s Unit 8200 that simulated a series of terrorist attacks occurring on the U.S. 2020 election has announced a new hire with deep ties to the U.S. intelligence and defense communities with the goal of gaining greater access to U.S. government networks.
A cybersecurity company tied to Israeli intelligence and a series of unnerving simulations regarding cyber-terrorist attacks on the upcoming U.S. elections has recently announced a new hire who plans to aid the company in further penetrating the U.S. public sector. Last Wednesday, the company Cybereason announced that it had hired Andrew Borene as its Managing Director for its recently launched U.S. public sector business. Borene, who boasts longstanding ties to the U.S. intelligence community and the Pentagon, “will accelerate Cybereason’s partner and customer presence in the U.S. public sector,” according to a Cybereason press release.
“My goal is to build a strong business for Cybereason within the U.S. public sector and I am planning to recruit a group of direct support executives, veterans and alumni of the elite [U.S.] military units and agencies that have defended our nation in the information age. I’ll also work to establish a network of the best channel and delivery partners for federal, state and local governments,” Borene said per the press release.
Eric Appel, Cybereason’s General Manager for North American Sales, stated that “We’re excited about Andrew joining Cybereason and the opportunity in the U.S. public sector for Cybereason to make a profound impact on helping the nation’s federal civilian, military, state and local government agencies…”
Borene will likely be successful in his ability to recruit a sales team of prominent alumni from the U.S. intelligence and defense communities to market Cybereason’s products throughout the U.S. government. Prior to joining Cybereason, Borene was a senior advisor to the Intelligence Advanced Research Projects Activity (IARPA), the intelligence community’s “DARPA” equivalent that is housed within the Office of the Director of National Intelligence (ODNI). He served in that capacity on behalf of intelligence contractor Booz Allen Hamilton. Prior to that, Borene served as Associate Deputy General Counsel to the Pentagon and was previously a military intelligence officer for the U.S. Marine Corps.
Borene’s private sector experience is also significant, as he was a senior executive at IBM. Notably, the current Chief Information Officer for the CIA, Juliane Gallina, had served alongside Borene as a top IBM executive prior to taking her current position at the agency. In addition, Borene also boasts ties to Wall Street as a veteran of Wells Fargo’s investment banking division.
In addition, Borene has deep ties to Washington’s foreign policy establishment as a “life member” of the Council on Foreign Relations (CFR) and to the national security-think tank nexus through his senior fellowship at the National Security Institute (NSI). NSI’s board includes former NSA directors, Keith Alexander and Michael Hayden (also a former CIA director); former Deputy Defense Secretary and “architect” of the Iraq War, Paul Wolfowitz; former director of the Defense Intelligence Agency, David Shedd; and a variety of other former top intelligence and defense officials as well as Silicon Valley executives and venture capitalists.
Notably, Borene is the latest addition to Cybereason with ties to the U.S. intelligence and defense communities as the company’s advisors include Robert Bigman, former Chief Information Security Officer for the CIA as well as Peter Sherlock, the former Chief Operating Officer of MITRE corporation, a major intelligence and defense contractor connected to the Ptech-9/11 controversy.
Cybereason: a front for Israeli Military Intelligence
Cybereason’s announcement of its hire of Andrew Borene coincided with its launch of its new “U.S. public sector business,” meaning that Cybereason now seeks to have its cybersecurity software running on even more of the U.S. government’s most classified networks. Cybereason, for years, has already been running on several sensitive U.S. government networks through its partnerships with IT contractors for intelligence and defense, such as Lockheed Martin (also a Cybereason investor), WWT and Leidos. However, Borene’s hire and this new publicly announced pivot towards the U.S. public sector clearly demonstrates the company’s interest in further deepening its presence on U.S. government networks.
Cybereason’s pivot is concerning for several reasons. First, its co-founders are alumni of Israel’s Unit 8200, an elite unit of the Israeli Intelligence corps that is part of the IDF’s Directorate of Military Intelligence and is involved mainly in signal intelligence, surveillance, cyberwarfare and code decryption. It is also well-known for its surveillance of Palestinian civilians and for using intercepted communications as blackmail in order to procure informants among Palestinians living under occupation in the West Bank.
In addition, all three Cybereason co-founders, after leaving Unit 8200, went on to work for two private Israel-based tech/telecom companies with a notorious history of aggressive espionage against the U.S. government: Amdocs and Comverse Infosys (the latter is now known as Verint Systems Inc.). This raises the possibility that Cybereason software could potentially be used as a backdoor by unauthorized actors, given that the company’s co-founders all previously worked for firms that have a history of placing backdoors into U.S. telecommunications and electronic infrastructure as well as aggressively spying on U.S. federal agencies.
Also notable is the fact that the company’s current CEO and co-founder Lior Div was much more than the average Unit 8200 officer during his time in the unit, as he “served as a commander [in Unit 8200] and carried out some of the world’s largest cyber offensive campaigns against nations and cybercrime groups. For his achievements, he received the Medal of Honor, the highest honor bestowed upon Unit 8200 members,” according to his biography. Troublingly, in an interview that Div gave to TechCrunch last year, Div stated that his work at Cybereason is “the continuation of the six years of training and service he spent working with the Israeli army’s 8200 Unit.”
This is particularly noteworthy given that Israel’s government has openly admitted that an on-going intelligence operation, first initiated in 2012 – the year Cybereason was founded, involves Israeli military intelligence and intelligence operations that had previously done “in house” (i.e. as part of Unit 8200, Mossad, etc.) being spun off into private companies, specifically start-ups in the “cyber” realm.
This operation is part of Israeli Prime Minister Benjamin Netanyahu’s “deliberate policy” to have former members of Israel’s “military and intelligence units … merge into companies with local partners and foreign partners” in order to make it all but impossible for major corporations and foreign governments to boycott Israel and to also to ensure that Israel becomes the world’s dominant “cyber power.”
One notable report on this policy, published by Israeli outlet Calcalist Tech, interviewed dozens of Israeli military, intelligence and government officials and noted that “since 2012, cyber-related and intelligence projects that were previously carried out in-house in the Israeli military and Israel’s main intelligence arms are transferred to companies that in some cases were built for this exact purpose.” The article also states that beginning in 2012, Israel’s intelligence and military intelligence agencies began to outsource “activities that were previously managed in-house, with a focus on software and cyber technologies.”
“Simulating” the Cancellation of the 2020 Election
In light of Cybereason’s background and the “acceleration” of their presence on U.S. government networks, the timing of their redoubled efforts to court the U.S. public sector add additional layers of concern given that it precedes the U.S. 2020 election by a matter of months. Since last year, Cybereason has conducted multiple simulations focused on the 2020 election, which were attended by federal officials from the FBI, DHS and the U.S. Secret Service and all of which ended in disaster. In those simulations, the 2020 election was ultimately canceled and martial law was then declared due to the chaos created by a group of hackers led by Cybereason employees.
Notably, Cybereason stood to gain nothing financially from the simulations given that their software could not have prevented the attacks waged against the U.S.’ electoral infrastructure in the exercise and the company framed their hosting of the simulations as merely “altruistic” because of their professed desire to help “protect” U.S. election infrastructure. The attacks conducted in the simulations by Cybereason employees included creating power grid blackouts, the use of deep fakes to sow confusion, creating havoc with municipal sewage systems and crashing self-driving cars into voters waiting in line to cast their ballots, killing 32 and injuring over a hundred people.
In the months since I first wrote about Cybereason and their 2020 “doomsday” simulations back in January, U.S. government officials and mass media alike have been warning that these same types of attacks that Cybereason simulated are likely to come to pass on this upcoming election day, scheduled for November 3rd of this year. More recently, in less than a week, headlines like “Election Security Experts Expect ‘Chaos’ Unless Action Taken,” “New York’s Pandemic Voting ‘Chaos’ Set to Go Nationwide in November,” and “Foreign adversaries ‘seeking to compromise’ presidential campaigns, intel warns,” among others, have been published in major U.S. media outlets.
While these narratives have asserted that China, Russia and/or Iran will be to blame for such attacks, it is worth noting that a tight-knit web of Israeli state-owned and private companies tied to Israeli military intelligence now run the software controlling key parts of the power grid in New York, California and elsewhere in the U.S.; are the main global producers of deep fakes; and the main providers of “security” software for self-driving and semi-self-driving cars, the quantity of which on U.S. streets has grown dramatically as a result of the coronavirus crisis.
With Cybereason’s newly announced push to run its software on critical U.S. government networks at both the federal and state levels, the company’s history of simulating terror attacks on critical U.S. infrastructure and their openly admitted and on-going ties to Israeli military intelligence deserve more scrutiny than ever as the U.S. election draws closer.
War Crimes and War Criminals: Who Will Be Held Accountable?
By Philip Giraldi | Strategic Culture Foundation | July 23, 2020
There is something unique about how the United States manipulates the “terrorism” label to avoid being accused of carrying out war crimes. When an indigenous militia or an armed insurgency like the Taliban in a country like Iraq or Afghanistan attacks American soldiers subsequent to a U.S. invasion which overthrew the country’s government, it is considered by Washington to be an act of “terrorism.” Terror attacks de facto permit a carte blanche response, allowing virtually anything as retaliation against the parties involved or countries that support them, including the assassination of foreign government officials. But for the attacker, whose perspective is quite different, the incident often could reasonably be described as legitimate resistance to a foreign occupier and much of the world might agree with that assessment.
So, it all comes down to definitions. The United States covers its version of reality through liberal use of the Authorization for Use of Military Force (AUMF) which more-or-less gives a blanket approval to attack and kill “terrorists” anywhere at any time. And how does one become a terrorist? By being included on the U.S. government’s heavily politicized annual list of terrorist groups and material supporters of terrorism. That was the argument that was used by the United States when it killed Iranian General Qassem Soleimani in January, that his organization, the Qods Force, was on the “terrorist” lists maintained by State and the Treasury Department and he was therefore held to be guilty of any and all attacks on U.S. military carried out by Qods or by presumed Iranian surrogate militias.
The case made to justify killing Soleimani was considered deeply flawed at the time it took place. Because the United States says something is legal due to a law Congress has passed does not make it so, just as most of the world would consider the U.S. profile killings by drone in Afghanistan and elsewhere, based on nothing more than the assumption that someone on the ground might be a “terrorist,” to be little more than war crimes.
It has recently been revealed that the Trump Administration has issued a so-called “finding” to authorize the CIA to conduct more aggressive cyberattacks against infrastructure and other targets in countries that are considered to be unfriendly. The finding specifically named Iran, North Korea, China and Russia as approved targets and it is of particular interest because it basically left it up to the Agency to decide whom to attack and to what degree. As Washington is not at war with any of the countries named and is essentially seeking to damage their economies directly, the activity undertaken by CIA has constituted acts of war and, by widely accepted legal definition, attacks on countries that are not actually threatening are war crimes.
To counter the negative publicity about Trump Administration actions and to establish a possible casus belli, Washington has been floating numerous stories alleging Iranian, Russian and Chinese “aggression.” The ridiculous story about Russia paying Afghans bounties to kill American soldiers was quickly debunked, so the White House and the captive media are now alleging that Moscow hacker/spies are seeking to steal proprietary information dealing with the development of a coronavirus vaccine. The agitprop coming out of Washington to blame Russia for nearly everything notwithstanding, opinion polls suggest that most of the world considers Washington to be the primary source of global instability, rejecting the assertion by Secretary of State Mike Pompeo that the U.S. is a “force for good.”
So, it is reasonable to suggest that the United States has been guilty of many war crimes in the past twenty years and has only been shielded from the consequences due to its ability to control the message combined with its power in international fora and its unwillingness to cooperate with the International Criminal Court (ICC) in the Hague.
But the willingness of the international community to look the other way in support of the war crimes double standard appears to be changing. The ICC, which has had its investigators denied entry to the United States, has been investigating Israeli war crimes even as it also looks at developments in Afghanistan and Iraq involving U.S. forces. Trump’s ban on entry by ICC personnel includes their families even if they are American citizens and it also protects Israel in that ICC investigators looking into the possible war crimes committed by Israeli soldiers and officers as well as the relevant Jewish state’s government officials will also be sanctioned and denied entry into the U.S. In practical terms, the Trump Administration is declaring that Israeli and U.S. soldiers will be regarded as one and the same as they relate to dealings with the ICC, a conceit that is little known to the American public.
The Israelis have responded to the threat from the ICC by compiling a secret list of government officials and military officers who might be subject to ICC issued arrest warrants if they travel in Europe for war crimes committed in Lebanon and Syria as well as of crimes against humanity directed against Palestinians. The list reportedly includes between 200 and 300 names.
That Israel is making a list of people who might be vulnerable to accusations of having possibly committed war crimes is a de facto admission by the government that such crimes were in fact committed. The ICC will soon decide whether to move on the December request by ICC Prosecutor Fatou Bensouda to investigate both Israel and Hamas over suspicions of war crimes in Gaza and Jerusalem as well as on the occupied West Bank beginning in 2014. The investigation would include “crimes allegedly committed in relation to the use by members of the IDF of non-lethal and lethal means against persons participating in demonstrations beginning in March 2018 near the border fence between the Gaza Strip and Israel, which reportedly resulted in the killing of over 200 individuals, including over 40 children, and the wounding of thousands of others.”
Given the time frame, Israeli government officials and military officers would likely be the first to face scrutiny by investigators. According to Haaretz, the list would almost certainly include “Prime Minister Benjamin Netanyahu; former defense ministers Moshe Ya’alon, Avigdor Lieberman and Naftali Bennett; former Israel Defense Forces chiefs of staff Benny Gantz and Gadi Eisenkot, and current Chief of Staff Aviv Kochavi; and the former and current heads of the Shin Bet security service, Yoram Cohen and Nadav Argaman, respectively.”
One wonders who would be included on a comparable list for the United States. There are a lot of lying politicians and sly generals to choose from. As both Israel and the United States do not recognize the authority of the ICC and will almost certainly refuse to participate in any fashion if the charges of war crimes and crimes against humanity ever actually make it to the court, any discussion of lists are at this point merely travel advisories for war criminals. The United States will push back and will inter alia certainly attempt to discredit the court using whatever weapons are available, to include sanctions against the nations that support any investigation and trial.
One nevertheless has to hope that the court will persevere in its effort to expose the crimes that continue to be committed by the U.S. and Israel in both Palestine and Afghanistan. Embarrassing Washington and Jerusalem in a very visible and highly respected international forum might be the only way to change the direction of the two nations that more than any other insist that “might makes right.”
I Don’t Always Believe CIA Narratives. But When I Do, I Believe Them About China.
By Caitlin Johnstone | July 22, 2020
My social media notifications have been lighting up the last few days with virulent Chinagaters sharing a video which purports to show Uighur Muslims being loaded onto a train to be taken to concentration camps. It’s actually an old video that had already surfaced last year, but it is magically making the rounds again as a new and shocking revelation in 2020 now that western China hysteria has been officially kicked into high gear, at exactly the same time the US enacts one of the most dangerous and incendiary escalations of recent years in the South China Sea.
Everyone tagging me in this video presents it as a self-evident “gotcha” moment, in exactly the same way Russiagaters spent years tagging me in every HUGE BOMBSHELL WALLS ARE CLOSING IN item of thinly sourced narrative fluff in their debunked conspiracy theory that the Kremlin had infiltrated the highest levels of the US government.
They are one hundred percent certain that the video shows Uighurs being loaded onto a train to go to a concentration camp, solely because that is what the bit of text over the video tells them that that’s what they are seeing. They aren’t looking at the actual data and thinking critically about it, they’re looking at the narrative and believing it on blind faith. Which, in a post-Iraq invasion world, is an absolutely insane thing to do when presented with information about a nation that is targeted by the US-centralized empire.
In reality there’s nothing in the video which tells us that these are Uighur people being sent to a “re-education camp” and not merely a conventional prison transfer of convicted criminals, the likes of which take place in the far more populous US prison system all the time. It’s an unknown. We are told by the BBC’s Andrew Marr (the same Andrew Marr whose phony journalism Noam Chomsky derided years ago) that it has been “authenticated by western intelligence agencies and by Australian experts”, which in practice are the same thing, and that’s really the extent of the evidence. Again, this is an insane source to take on faith in a post-Iraq invasion world.
There are in fact an abundance of reasons to be highly skeptical of the establishment narrative about what is happening to Uighurs in Xinjiang. But that isn’t the point that I am trying to make here.
The point I am trying to make here is that the only sane response to any narrative that is being promoted by western intelligence agencies and their media stenographers about governments which have resisted absorption into the imperial blob is intense and unrelenting skepticism. These organizations have such an extensive and well-known history of lying about exactly this sort of thing that they have left us no choice but to withhold belief from anything they say absent a mountain of independently verifiable evidence if we want to have a fact-based relationship with reality.
None of this means that China has a wonderful government. It doesn’t even mean that all the bad things we’re being told about what the Chinese government is doing are false. It’s entirely possible that that video shows exactly what we’re being urgently told to believe it shows. There’s simply no way to be sure one way or the other in an information ecosystem that is so severely tainted by propagandistic narrative manipulation.
Surely the Chinese government is far from sinless. It seems to be a constant that power structures which keep secrets and use propaganda will always wind up doing ugly things. But this doesn’t mean you go believing whatever cold war-facilitating story we are fed by western power structures about it. Not if we want to avoid being duped into serving as pro bono CIA propagandists, unwitting tools of a murderous war machine.
There is a slow-motion third world war underway between the US-centralized power alliance and the nations like China which have resisted being absorbed into it, and that war is being largely facilitated by propaganda. If one doesn’t wish to become a propagandist themselves, one ought to withhold belief from the stories they are told about the terrible, awful things the unabsorbed nations are doing which require extensive sanctions, subversion and interventionism in response.
This doesn’t mean you believe the opposite of what you’re told, it simply means you refrain from believing either way and remain agnostic until presented with hard verifiable proof. Believing damaging narratives about US-targeted governments is exactly as stupid as believing the words of a known compulsive liar about someone you know he hates.
China is such a curious anomaly in the narrative matrix. Many who are normally skeptical of claims by western governments immediately swallow anything they’re told about China. They not only believe all such claims, it never even occurs to them to seriously question them. Like they seem to be genuinely unaware that skepticism of establishment China narratives is even an option. The claims just slide right into the “believe” file in their mind, completely unchecked by anything resembling critical thought.
I argue with people all over the political spectrum about China online, and an astonishing percentage of them have clearly put exactly zero research into critically examining these claims, even if they’re people who are normally relatively critical of western foreign policy. They’re often completely unaware that whatever claims they’re advancing are not just disputed but have large amounts of evidence against them. This is because they’ve done no research whatsoever into finding out what they were told is even true. They’ll do that research on Iran, they’ll do it about Russia, they’ll do it about Syria, but with China all skepticism immediately goes right now the window. It’s the weirdest thing.
Always be intensely skeptical of claims made about governments targeted by the known liars who run the US-centralized empire. Always, always, always, always. If you advance imperialist propaganda, then you are just as culpable for the bloodshed and suffering they help facilitate as the people who are actually launching the missiles.
Stay skeptical, my friends.
The Evil, Immoral, Vicious, and Hypocritical Embargo Against Cuba
By Jacob G. Hornberger | FFF | July 20, 2020
The banality of evil that characterizes the U.S. national security state is demonstrated perfectly by the continuation of its deadly economic embargo against Cuba, which has been ongoing for some 60 years.
What’s the point of the embargo? After all, the Pentagon’s, CIA’s, and NSA’s official enemy Fidel Castro died years ago. Why continue to intentionally inflict harm on the Cuban people?
And make no mistake about it: Inflicting harm on the Cuban people is the purpose of the embargo. Its aim is to impoverish or starve Cubans into ousting their post-Castro regime and installing another pro-U.S. right-wing brutal dictatorship similar to the one that Castro ousted from power in the Cuban revolution.
In fact, the first embargo that the U.S. implemented against Cuba was during the reign of the crooked, corrupt, and brutal pro-U.S. right-wing dictatorship of Fulgencio Batista. That was an arms embargo. U.S. officials didn’t want weaponry imported into Cuba because that might enable the Cuban people to oppose Batista in a violent revolution.
During his reign, Batista partnered with the Mafia, the premier criminal organization that was smuggling drugs into the United States. As part of their partnership agreement, Batista let the Mafia operate gambling casinos in Cuba. As part of that cozy relationship, Batista would have his henchmen kidnap under-aged girls in Cuba and turn them over to the Mafia, which would then provide them as perks to the high-rollers in its casinos. That’s one of the things that brought on the Cuban Revolution.
That’s the guy that the U.S. national-security state was hell-bent on keeping in power. Thus, it should surprise no one that the CIA, like Batista, later entered into partnership with the Mafia, knowing full well that the Mafia was engaged in massive criminal activity. The purpose of the CIA-Mafia partnership was assassination. They were working together to assassinate Castro.
It stands to reason that the Mafia would try to assassinate Castro. It has lost all its casinos to Castro’s nationalization. And it was in the business of killing people.
But the U.S. government? In the business of murder? And in partnership with the biggest criminal organization in the world?
Don’t forget something important here: Castro, Cuba, and the Cuban people have never attacked the United States or even threatened to do so. No invasion. No terrorist attacks. No assassinations.
In fact, it has always been the other way around. In the more than six decades of bad relations between Cuba and the U.S., it has always been the U.S. government that has been the aggressor. An invasion, terrorist attacks, assassination attempts, and the embargo, all on the part of the U.S. government.
U.S. national-security state officials always justified such actions under the notion that Cuba was the spearhead of a worldwide communist conspiracy to take over the United States, one that was supposedly based in Moscow. It was always a ridiculous notion but that was the mindset of CIA, NSA, and Pentagon officials during the Cold War — that Cuba’s communist regime posed a grave threat to U.S. “national security.”
But the Cold War ended more than 30 years ago. Do the CIA, NSA, and Pentagon still think that the United States is in danger of falling to the Cuban communists?
Of course not. Now, it’s just sheer viciousness. Now, it’s just a matter of doing everything possible to oust the current regime in Cuba from power and restoring a Batista-like dictatorship, one that will be loyal and deferential to the Pentagon, the CIA, and the NSA.
The viciousness is demonstrated by the fact that the embargo doesn’t just criminalize Americans who do business with Cuba. It also targets foreign companies who do so. If they are caught doing so, they are targeted for prosecution or economic banishment here in the United States. In the minds of U.S. officials, it’s more imperative than ever to squeeze as many Cubans as possible into death and suffering.
Needless to say, the embargo has made things significantly worse for the Cuban people during the COVID-19 crisis. That’s fine with U.S. officials. The more Cubans who die, the greater the chance of an internal regime-change operation.
Sure, there is no doubt that Cuba’s socialist economic system is a major factor in the economic suffering of the Cuban people. But there is also no doubt that the U.S. embargo has served as the other side of a vise that has squeezed the economic lifeblood out of the Cuban people.
A dark irony, of course, is that the embargo has enabled the U.S. government to wield and exercise the same type of economic control over the American people that the Cuban socialist regime exercises over the Cuban people. It’s called adopting socialism to oppose socialism.
When will the evil, immoral, vicious, and hypocritical U.S. embargo against Cuba be lifted? When a critical mass of the American people, including those who go to church every Sunday, have a crisis of conscience and demand that it be lifted.
Powell & Iraq—Regime Change, Not Disarmament: The Fundamental Lie
By Scott Ritter – Consortium News – July 18, 2020
The New York Times Magazine has published a puff piece soft-peddling former Secretary of State Colin Powell’s role in selling a war on Iraq to the UN Security Council using what turned out to be bad intelligence. “Colin Powell Still Wants Answers” is the title of the article, written by Robert Draper. “The analysts who provided the intelligence,” a sub-header to the article declares, “now say it was doubted inside the CIA at the time.”
Draper’s article is an extract from a book, To Start a War: How the Bush Administration Took America into Iraq, scheduled for publication later this month. In the interest of full disclosure, I was approached by Draper in 2018 about his interest in writing this book, and I agreed to be interviewed as part of his research. I have not yet read the book, but can note that, based upon the tone and content of his New York Times Magazine article, my words apparently carried little weight.
Regime Change, Not WMD
I spent some time articulating to Draper my contention that the issue with Saddam Hussein’s Iraq was never about weapons of mass destruction (WMD), but rather regime change, and that everything had to be viewed in the light of this reality—including Powell’s Feb. 5, 2003 presentation before the UN Security Council. Based upon the content of his article, I might as well have been talking to a brick wall.
Powell’s 2003 presentation before the council did not take place in a policy vacuum. In many ways, the March 2003 U.S.-led invasion and subsequent occupation of Iraq was a continuation of the 1991 Gulf War, which Powell helped orchestrate. Its fumbled aftermath was again, something that transpired on Powell’s watch as the chairman of the Joint Chiefs of Staff in the administration of George H. W. Bush.
Powell was part of the policy team that crafted the post-Gulf War response to the fact that Iraq’s president, Saddam Hussein, survived a conflict he was not meant to. After being labeled the Middle East equivalent of Adolf Hitler whose crimes required Nuremburg-like retribution in a speech delivered by President Bush in October 1990, the Iraqi President’s post-conflict hold on power had become a political problem for Bush 41.
Powell was aware of the CIA’s post-war assessment on the vulnerability of Saddam’s rule to continued economic sanctions, and helped craft the policy that led to the passage of Security Council resolution 687 in April 1991. That linked Iraq’s obligation to be disarmed of its WMD prior to any lifting of sanctions and the reality that it was U.S. policy not to lift these sanctions, regardless of Iraq’s disarmament status, until which time Saddam was removed from power.
Regime change, not disarmament, was always the driving factor behind U.S. policy towards Saddam Hussein’s Iraq. Powell knew this because he helped craft the original policy.
I bore witness to the reality of this policy as a weapons inspector working for the United Nations Special Commission (UNSCOM), created under the mandate of resolution 687 to oversee the disarming of Iraq’s WMD. Brought in to create an intelligence capability for the inspection team, my remit soon expanded to operations and, more specifically, how Iraq was hiding retained weapons and capability from the inspectors.
SCUDS
One of my first tasks was addressing discrepancies in Iraq’s accounting of its modified SCUD missile arsenal; in December 1991 I wrote an assessment that Iraq was likely retaining approximately 100 missiles. By March 1992 Iraq, under pressure, admitted it had retained a force of 89 missiles (that number later grew to 97).
After extensive investigations, I was able to corroborate the Iraqi declarations, and in November 1992 issued an assessment that UNSCOM could account for the totality of Iraq’s SCUD missile force. This, of course, was an unacceptable conclusion, given that a compliant Iraq meant sanctions would need to be lifted and Saddam would survive.
The U.S. intelligence community rejected my findings without providing any fact-based evidence to refute it, and the CIA later briefed the Senate that it assessed Iraq to be retaining a force of some 200 covert SCUD missiles. This all took place under Powell’s watch as chairman of the Joint Chiefs.
I challenged the CIA’s assessment, and organized the largest, most complex inspection in UNSCOM’s history to investigate the intelligence behind the 200-missile assessment. In the end, the intelligence was shown to be wrong, and in November 1993 I briefed the CIA Director’s senior staff on UNSCOM’s conclusion that all SCUD missiles were accounted for.
Moving the Goalposts
The CIA’s response was to assert that Iraq had a force of 12-20 covert SCUD missiles, and that this number would never change, regardless of what UNSCOM did. This same assessment was in play at the time of Powell’s Security Council presentation, a blatant lie born of the willful manufacture of lies by an entity—the CIA—whose task was regime change, not disarmament.
Powell knew all of this, and yet he still delivered his speech to the UN Security Council.
In October 2002, in a briefing designed to undermine the credibility of UN inspectors preparing to return to Iraq, the Defense Intelligence Agency trotted out Dr. John Yurechko, the defense intelligence officer for information operations and denial and deception, to provide a briefing detailing U.S. claims that Iraq was engaged in a systematic process of concealment regarding its WMD programs.
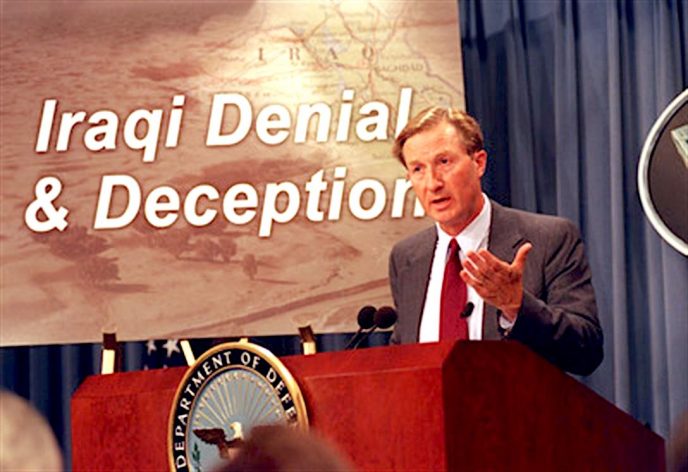
John Yurechko, of the Defense Intelligence Agency, briefs reporters at the Pentagon on Oct. 8, 2002 (U.S. Defense Dept.)
According to Yurechko, the briefing was compiled from several sources, including “inspector memoirs” and Iraqi defectors. The briefing was farcical, a deliberate effort to propagate misinformation by the administration of Bush 43. I know—starting in 1994, I led a concerted UNSCOM effort involving the intelligence services of eight nations to get to the bottom of Iraq’s so-called “concealment mechanism.”
Using innovative imagery intelligence techniques, defector debriefs, agent networks and communications intercepts, combined with extremely aggressive on-site inspections, I was able, by March 1998, to conclude that Iraqi concealment efforts were largely centered on protecting Saddam Hussein from assassination, and had nothing to do with hiding WMD. This, too, was an inconvenient finding, and led to the U.S. dismantling the apparatus of investigation I had so carefully assembled over the course of four years.
It was never about the WMD—Powell knew this. It was always about regime change.
Using UN as Cover for Coup Attempt
In 1991, Powell signed off on the incorporation of elite U.S. military commandos into the CIA’s Special Activities Staff for the purpose of using UNSCOM as a front to collect intelligence that could facilitate the removal of Saddam Hussein. I worked with this special cell from 1991 until 1996, on the mistaken opinion that the unique intelligence, logistics and communications capability they provided were useful to planning and executing the complex inspections I was helping lead in Iraq.
This program resulted in the failed coup attempt in June 1996 that used UNSCOM as its operational cover—the coup failed, the Special Activities Staff ceased all cooperation with UNSCOM, and we inspectors were left holding the bag. The Iraqis had every right to be concerned that UNSCOM inspections were being used to target their president because, the truth be told, they were.
Nowhere in Powell’s presentation to the Security Council, or in any of his efforts to recast that presentation as a good intention led astray by bad intelligence, does the reality of regime change factor in. Regime change was the only policy objective of three successive U.S. presidential administrations—Bush 41, Clinton, and Bush 43.
Powell was a key player in two of these. He knew. He knew about the existence of the CIA’s Iraq Operations Group. He knew of the successive string of covert “findings” issued by U.S. presidents authorizing the CIA to remove Saddam Hussein from power using lethal force. He knew that the die had been cast for war long before Bush 43 decided to engage the United Nations in the fall of 2002.
Powell Knew
Powell knew all of this, and yet he still allowed himself to be used as a front to sell this conflict to the international community, and by extension the American people, using intelligence that was demonstrably false. If, simply by drawing on my experience as an UNSCOM inspector, I knew every word he uttered before the Security Council was a lie the moment he spoke, Powell should have as well, because every aspect of my work as an UNSCOM inspector was known to, and documented by, the CIA.
It is not that I was unknown to Powell in the context of the WMD narrative. Indeed, my name came up during an interview Powell gave to Fox News on Sept. 8, 2002, when he was asked to comment on a quote from my speech to the Iraqi Parliament earlier that month in which I stated:
“The rhetoric of fear that is disseminated by my government and others has not to date been backed up by hard facts that substantiate any allegations that Iraq is today in possession of weapons of mass destruction or has links to terror groups responsible for attacking the United States. Void of such facts, all we have is speculation.”
Powell responded by declaring,
“We have facts, not speculation. Scott is certainly entitled to his opinion but I’m afraid that I would not place the security of my nation and the security of our friends in the region on that kind of an assertion by somebody who’s not in the intelligence chain any longer… If Scott is right, then why are they keeping the inspectors out? If Scott is right, why don’t they say, ‘Anytime, any place, anywhere, bring ‘em in, everybody come in—we are clean?’ The reason is they are not clean. And we have to find out what they have and what we’re going to do about it. And that’s why it’s been the policy of this government to insist that Iraq be disarmed in accordance with the terms of the relevant UN resolutions.” (emphasis added, Aletho News )
Of course, in November 2002, Iraq did just what Powell said they would never do—they let the UN inspectors return without preconditions. The inspectors quickly exposed the fact that the “high quality” U.S. intelligence they had been tasked with investigating was pure bunk. Left to their own devices, the new round of UN weapons inspections would soon be able to give Iraq a clean bill of health, paving the way for the lifting of sanctions and the continued survival of Saddam Hussein.
Powell knew this was not an option. And thus he allowed himself to be used as a vehicle for disseminating more lies—lies that would take the U.S. to war, cost thousands of U.S. service members their lives, along with hundreds of thousands of Iraqis, all in the name of regime change.
Back to Robert Draper. I spent a considerable amount of time impressing upon him the reality of regime change as a policy, and the fact that the WMD disarmament issue existed for the sole purpose of facilitating regime change. Apparently, my words had little impact, as all Draper has done in his article is continue the false narrative that America went to war on the weight of false and misleading intelligence.
Draper is wrong—America went to war because it was our policy as a nation, sustained over three successive presidential administrations, to remove Saddam Hussein from power. By 2002 the WMD narrative that had been used to support and sustain this regime change policy was weakening.
Powell’s speech was a last-gasp effort to use the story of Iraqi WMD for the purpose it was always intended—to facilitate the removal of Saddam Hussein from power. In this light, Colin Powell’s speech was one of the greatest successes in CIA history. That is not the story, however, Draper chose to tell, and the world is worse off for that failed opportunity.
Scott Ritter is a former Marine Corps intelligence officer who served in the former Soviet Union implementing arms control treaties, in the Persian Gulf during Operation Desert Storm, and in Iraq overseeing the disarmament of WMD.
The Russians are coming, again! Poorly understood cybercrimes play perfectly into political agendas
By Helen Buyniski | RT | July 16, 2020
Foreign hackers are determined as ever to steal technology, meddle in elections and skew foreign policy, but fear not! The CIA has apparently been authorized to deliver preemptive cyber-strikes based on partisan mythmaking.
US, UK and Canadian intelligence dropped a 16-page report on Thursday accusing “Russian hackers” – specifically APT29, the “Cozy Bear” hacking group of ‘Russiagate’ fame – of targeting unspecified entities involved in developing the (increasingly controversial) Covid-19 vaccine.
However, the report is fraught with the same factual pitfalls plaguing previous unsubstantiated “Russian hacking” tales, seemingly designed to capitalize on the general population’s ignorance about cyber-attacks – or vaccines, for that matter. While Democrat-linked cybersecurity firm CrowdStrike specializes in attributing state actors to malware attacks, more reputable companies avoid doing so based solely on the malware used, since hacking groups often exchange tools or even collaborate.
The best, or just best-funded hackers are able to not only cover their tracks effectively but create a fake trail leading to someone else. The WikiLeaks Vault 7 release in 2017 exposed the disturbing tools the CIA has at its disposal for simulating foreign cyberattacks, tools that allow the agency to make it seem like Moscow or Tehran is behind a hack when the real culprits are in Langley, Virginia.
Russia is far from the only country to be accused of such behavior, of course – China was accused of attempting to steal coronavirus vaccine research back in May, while US and UK intelligence agencies warned that same month that other “threat groups” were “actively targeting” local governments, pharmaceutical and research firms, healthcare facilities, and universities for virus-related hacking.
Nor is this latest outbreak of finger-pointing limited to the pandemic. On Thursday, UK foreign minister Dominic Raab denounced “Russian actors” for “almost certainly” seeking to meddle in the 2019 election – not by actually breaking any laws, but by “amplifying” documents leaked by other people on Reddit and circulated around social media in the run-up to December’s contest
Raab didn’t name any of the Russians responsible for circulating the material, perhaps mindful of the embarrassment that befell his ideological brother-in-arms, Atlantic Council bot-hunter Ben Nimmo, who accused several real people of being “Russian bots.” Further covering his bases, Raab in the same statement acknowledged that there was “no evidence of a broad-spectrum Russian campaign against the General Election.”
Even the most nonspecific shrieking about Russian hackers plotting to steal vaccine data, however, distracts from the inconvenient reality that the vaccines under development in the UK and US are performing abysmally. Neither the US company Moderna – initially hailed as the frontrunner despite never having brought a vaccine to market before – nor the UK’s collaboration between Oxford University and pharma giant AstraZeneca have produced any encouraging results in their clinical trials.
That didn’t stop the US from ordering 300 million doses of the Oxford jab, though the Trump administration’s coronavirus czar Anthony Fauci has already begun lamenting the “general anti-science, anti-authority, anti-vaccine feeling among some people in this country” he fears will keep Americans away from the needle.
With regard to hacking, however, the world might be more concerned about the CIA than the Russians – especially following Wednesday’s Yahoo News report that the agency had received carte blanche from Trump to wage preemptive (i.e. unjustified) cyber-warfare against any individual or organization it could link to a “handful of adversarial countries.”
According to several former US officials, the CIA has been wielding unprecedented offensive powers against American civilians only tenuously connected to Washington’s geopolitical rivals since 2018, checking off at least 12 cyber-attacks on its “wish list” already. Liberated from the tiresome need to provide “years of signals and dozens of pages of intelligence” justifying raining computer-borne chaos and destabilization on its victims, the CIA has wrought “a combination of destructive things – stuff is on fire and exploding – and also public dissemination of data: leaking or things that look like leaking.”
News of the CIA being given carte blanche appears at the same point in the US election cycle as the 2018 report about a similar measure that freed the hands of the Pentagon to conduct its own cyberattacks without interference from the State Department or any intelligence agencies.
With a hotly anticipated election coming up in November, it’s not hard to imagine how a few well-placed “leaks” or “destructive things” might convince voters to put aside their concerns about the administration’s response to the pandemic – or to place it front and center, depending on whether the CIA has decided it can live with four more years of Trump.
One thing is certain: the “Russian meddling” narrative isn’t going away anytime soon.
Helen Buyniski is an American journalist and political commentator at RT. Follow her on Twitter @velocirapture23
How an Israeli Spy-Linked Tech Firm Gained Access to the US Gov’t’s Most Classified Networks
By Whitney Webb |
Unlimited Hangout| July 15, 2020
If the networks of the U.S. military, the U.S. intelligence community and a slew of other U.S. federal agencies were running the software of a company with deep ties, not only to foreign companies with a history of espionage against the U.S. but also foreign military intelligence, it would — at the very least — garner substantial media attention. Yet, no media reports to date have noted that such a scenario exists on a massive scale and that the company making such software recently simulated the cancellation of the 2020 election and the declaration of martial law in the United States.
Earlier this month, MintPress News reported on the simulations for the U.S. 2020 election organized by the company Cybereason, a firm led by former members of Israel’s military intelligence Unit 8200 and advised by former top and current officials in both Israeli military intelligence and the CIA. Those simulations, attended by federal officials from the FBI, DHS and the U.S. Secret Service, ended in disaster, with the elections ultimately canceled and martial law declared due to the chaos created by a group of hackers led by Cybereason employees.
The first installment of this three part series delved deeply into Cybereason’s ties to the intelligence community of Israel and also other agencies, including the CIA, as well as the fact that Cybereason stood to gain little financially from the simulations given that their software could not have prevented the attacks waged against the U.S.’ electoral infrastructure in the exercise.
Also noted was the fact that Cybereason software could be potentially used as a backdoor by unauthorized actors, a possibility strengthened by the fact that the company’s co-founders all previously worked for firms that have a history of placing backdoors into U.S. telecommunications and electronic infrastructure as well as aggressive espionage targeting U.S. federal agencies.
The latter issue is crucial in the context of this installment of this exclusive MintPress series, as Cybereason’s main investors turned partners have integrated Cybereason’s software into their product offerings. This means that the clients of these Cybereason partner companies, the U.S. intelligence community and military among them, are now part of Cybereason’s network of more than 6 million endpoints that this private company constantly monitors using a combination of staff comprised largely of former intelligence operatives and an AI algorithm first developed by Israeli military intelligence.
Cybereason, thus far, has disclosed the following groups as lead investors in the company: Charles River Ventures (CRV), Spark Capital, Lockheed Martin and SoftBank. Charles River Ventures (CRV) was among the first to invest in Cybereason and has been frequently investing in other Israeli tech start-upsthat were founded by former members of the elite Israeli military intelligence Unit 8200 over the last few years. Spark Capital, based in California, appears to have followed CRV’s interest in Cybereason since the venture capitalist who co-founded Spark and led its investment in Cybereason is a former CRV partnerwho still has close ties to the firm.
While CRV and Spark Capital seem like just the type of investors a company like Cybereason would attract given their clear interest in similar tech start-ups coming out of Israel’s cyber sector, Cybereason’s other lead investors — Lockheed Martin and SoftBank — deserve much more attention and scrutiny.
Cybereason widely used by US Government, thanks to Lockheed
“A match made in heaven,” trumpeted Forbes at the news of the Lockheed Martin-Cybereason partnership, first forged in 2015. The partnership involved not only Lockheed Martin becoming a major investor in the cybersecurity company but also in Lockheed Martin becoming the largest conduit providing Cybereason’s software to U.S. federal and military agencies.
Indeed, as Forbes noted at the time, not only did Lockheed invest in the company, it decided to integrate Cybereason’s software completely into its product portfolio, resulting in a “model of both using Cybereason internally, and selling it to both public and private customers.”
Cybereason CEO and former offensive hacker for Israeli military intelligence — Lior Div — said the following of the partnership:
Lockheed Martin invested in Cybereason’s protection system after they compared our solution against a dozen others from the top industry players. The US firm was so impressed with the results they got from Cybereason that they began offering it to their own customers – among them most of the top Fortune 100 companies, and the US federal government. Cybereason is now the security system recommended by LM to its customers for protection from a wide (sic) malware and hack attacks.”
Rich Mahler, then-director of Commercial Cyber Services at Lockheed Martin, told Defense Daily that the company’s decision to invest in Cybereason, internally use its software, and include the technology as part of Lockheed Martin’s cyber solutions portfolio were all “independent business decisions but were all coordinated and timed with the transaction.”
How independent each of those decisions actually was is unclear, especially given the timing of Lockheed Martin’s investment in Cybereason, whose close and troubling ties to Israeli intelligence as well as the CIA were noted in the previous installment of this investigative series. Indeed, about a year prior to their investment in the Israeli military intelligence-linked Cybereason, Lockheed Martin opened an office in Beersheba, Israel, where the IDF has its “cyberhub”. The office is focused not on the sales of armaments, but instead on technology.
Marilyn Hewson, Lockheed Martin’s CEO, said the following during her speech that inaugurated the company’s Beersheba office:
The consolidation of IDF Technical Units to new bases in the Negev Desert region is an important transformation of Israel’s information technology capability… We understand the challenges of this move. Which is why we are investing in the facilities and people that will ensure we are prepared to support for these critical projects. By locating our new office in the capital of the Negev we are well positioned to work closely with our Israeli partners and stand ready to: accelerate project execution, reduce program risk and share our technical expertise by training and developing in-country talent.”
Beersheba not only houses the IDF’s technology campus, but also the Israel National Cyber Directorate, which reports directly to Israel’s Prime Minister, as well as a high-tech corporate park that mostly houses tech companies with ties to Israel’s military intelligence apparatus. The area has been cited in several media reports as a visible indicator of the public-private merger between Israeli technology companies, many of them started by Unit 8200 alumni, and the Israeli government and its intelligence services. Lockheed Martin quickly became a key fixture in the Beersheba-based cyberhub.
Not long before Lockheed began exploring the possibility of opening an office in Beersheba, the company was hacked by individuals who used tokens tied to the company, RSA Security, whose founders have ties to Israel’s defense establishment and which is now owned by Dell, a company also deeply tied to the Israeli government and tech sector. The hack, perpetrated by still unknown actors, may have sparked Lockheed’s subsequent interest in Israel’s cybersecurity sector.
Soon after opening its Beersheba office, Lockheed Martin created its Israel subsidiary, Lockheed Martin Israel. Unlike many of the company’s other subsidiaries, this one is focused exclusively on “cybersecurity, enterprise information technology, data centers, mobile, analytics and cloud” as opposed to the manufacture and design of armaments.
Haden Land, then-vice president of research and technology for Lockheed Martin, told the Wall Street Journal that the creation of the subsidiary was largely aimed at securing contracts with the IDF and that the company’s Israel subsidiary would soon be seeking partnership and investments in pursuit of that end. Land oversaw the local roll-out of the company’s Israel subsidiary while concurrently meeting with Israeli government officials. According to the Journal, Land “oversees all of Lockheed Martin’s information-systems businesses, including defense and civilian commercial units” for the United States and elsewhere.
Just a few months later, Lockheed Martin partnered and invested in Cybereason, suggesting that Lockheed’s decision to do so was aimed at securing closer ties with the IDF. This further suggests that Cybereason still maintains close ties to Israeli military intelligence, a point expounded upon in great detail in the previous installment of this series.
Thus, it appears that not only does Lockheed Martin use Cybereason’s software on its own devices and on those it manages for its private and public sector clients, but it also decided to use the company’s software in this way out of a desire to more closely collaborate with the Israeli military in matters related to technology and cybersecurity.
The cozy ties between Lockheed Martin, one of the U.S. government’s largest private contractors, and the IDF set off alarm bells, then and now, for those concerned with U.S. national security. Such concern makes it important to look at the extent of Cybereason’s use by federal and military agencies in the United States through their contracting of Lockheed Martin’s Information Technology (IT) division. This is especially important considering Israeli military intelligence’s history of using espionage, blackmail and private tech companies against the U.S. government, as detailed here.
While the exact number of U.S. federal and military agencies using Cybereason’s software is unknown, it is widespread, with Lockheed Martin’s IT division as the conduit. Indeed, Lockheed Martin was the number one IT solutions provider to the U.S. federal government up until its IT division was spun off and merged with Leidos Holdings. As a consequence, Leidos is now the largest IT provider to the U.S. government and is also directly partnered with Cybereason in the same way Lockheed Martin was. Even after its IT division was spun off, Lockheed Martin continues to use Cybereason’s software in its cybersecurity work for the Pentagon and still maintains a stake in the company.
The Leidos-Lockheed Martin IT hybrid provides a litany of services to the U.S. military and U.S. intelligence. As investigative journalist Tim Shorrock noted for The Nation, the company does “everything from analyzing signals for the NSA to tracking down suspected enemy fighters for US Special Forces in the Middle East and Africa” and, following its merger with Lockheed and consequential partnership with Cybereason, became “the largest of five corporations that together employ nearly 80 percent of the private-sector employees contracted to work for US spy and surveillance agencies.” Shorrock also notes that these private-sector contractors now dominate the mammoth U.S. surveillance apparatus, many of them working for Leidos and — by extension — using Cybereason’s software.
Leidos’ exclusive use of Cybereason software for cybersecurity is also relevant for the U.S. military since Leidos runs a number of sensitive systems for the Pentagon, including its recently inked contract to manage the entire military telecommunications infrastructure for Defense Information Systems Agency (DISA). In addition to maintaining the military telecom network, Cybereason is also directly partnered with World Wide Technologies (WWT) as of this past October. WWT manages cybersecurity for the U.S. Army, maintains DISA’s firewalls and data storage as well as the U.S. Air Force’s biometric identification system. WWT also manages contracts for NASA, itself a frequent target of Israeli government espionage, and the U.S. Navy. WWT’s partnership is similar to the Lockheed/Leidos partnership in that Cybereason’s software is now completely integrated into its portfolio, giving the company full access to the devices on all of these highly classified networks.
Many of these new partnerships with Cybereason, including its partnership with WWT, followed claims made by members of Israel’s Unit 8200 in 2017 that the popular antivirus software of Kaspersky Labs contained a backdoor for Russian intelligence, thereby compromising U.S. systems. The Wall Street Journal was the first to report on the alleged backdoor but did not mention the involvement of Unit 8200 in identifying it, a fact revealed by the New York Times a week later.
Notably, none of the evidence Unit 8200 used to blame Kaspersky has been made public and Kaspersky noted that it was actually Israeli hackers that had been discovered planting backdoors into its platform prior to the accusation levied against Kaspersky by Unit 8200. As the New York Times noted:
Investigators later discovered that the Israeli hackers had implanted multiple back doors into Kaspersky’s systems, employing sophisticated tools to steal passwords, take screenshots, and vacuum up emails and documents.”
Unit 8200’s claims ultimately led the U.S. government to abandon Kaspersky’s products entirely in 2018, allowing companies like Cybereason (with its own close ties to Unit 8200) to fill the void. Indeed, the very agencies that banned Kaspersky now use cybersecurity software that employs Cybereason’s EDR system. No flags have been raised about Cybereason’s own collaboration with the very foreign intelligence service that first pointed the finger at Kaspersky and that previously sold software with backdoors to sensitive U.S. facilities.
SoftBank, Cybereason and the Vision Fund
While its entry into the U.S. market and U.S. government networks is substantial, Cybereason’s software is also run throughout the world on a massive scale through partnerships that have seen it enter into Latin American and European markets in major ways in just the last few months. It has also seen its software become prominent in Asia following a partnership with the company Trustwave. Much of this rapid expansion followed a major injection of cash courtesy of one of the company’s biggest clients and now its largest investor, Japan’s SoftBank.
SoftBank first invested in Cybereason in 2015, the same year Lockheed Martin initially invested and partnered with the firm. It was also the year that SoftBank announced its intention to invest in Israeli tech start-ups. SoftBank first injected $50 million into Cybereason, followed by an additional $100 million in 2017 and $200 million last August. SoftBank’s investments account for most of the money raised by the company since it was founded in 2012 ($350 million out of $400 million total).
Prior to investing, Softbank was a client of Cybereason, which Ken Miyauchi, president of SoftBank, noted when making the following statement after Softbank’s initial investment in Cybereason:
SoftBank works to obtain cutting edge technology and outstanding business models to lead the Information Revolution. Our deployment of the Cybereason platform internally gave us firsthand knowledge of the value it provides, and led to our decision to invest. I’m confident Cybereason and SoftBank’s new product offering will bring a new level of security to Japanese organizations.”
SoftBank — one of Japan’s largest telecommunications companies — not only began to deploy Cybereason internally but directly partnered with it after investing, much like Lockheed Martin had done around the same time. This partnership resulted in SoftBank and Cybereason creating a joint venture in Japan and Cybereason creating partnerships with other tech companies acquired by SoftBank, including the U.K.’s Arm, which specializes in making chips and management platforms for Internet of Things (IoT) devices.
SoftBank’s interest in Cybereason is significant, particularly in light of Cybereason’s interest in the 2020 U.S. election, given that SoftBank has significant ties to key allies of President Trump and even the president himself.
Indeed, SoftBank’s Masayoshi Son was among the first wave of international business leaders who sought to woo then-president-elect Trump soon after the 2016 election. Son first visited Trump Tower in December 2016 and announced, with Trump by his side in the building’s lobby, that SoftBank would invest $50 billion in the U.S. and create 50,000 jobs. Trump subsequently claimed on Twitter that Son had only decided to make this investment because Trump had won the election.
Son told reporters at the time that the investment would come from a $100 billion fund that would be created in partnership with Saudi Arabia’s sovereign wealth fund as well as other investors. “I just came to celebrate his new job. I said, ‘This is great. The US will become great again,’” Son said, according to reports.
Then, in March of 2017, Son sent top SoftBank executives to meet with senior members of Trump’s economic team and, according to the New York Times, “the SoftBank executives said that because of a lack of advanced digital investments, the competitiveness of the United States economy was at risk. And the executives made the case, quite strongly, that Mr. Son was committed to playing a major role in addressing this issue through a spate of job-creating investments.” Many of SoftBank’s investments and acquisitions in the U.S. since then have focused mainly on artificial intelligence and technology with military applications, such as “killer robot” firm Boston Dynamics, suggesting Son’s interest lies more in dominating futuristic military-industrial technologies than creating jobs for the average American.
After their initial meeting, Trump and Son met again a year later in June 2018, with Trump stating that “His [Son’s] $50 billion turned out to be $72 billion so far, he’s not finished yet.” Several media reports have claimed that Son’s moves since Trump’s election have sought to “curry favor” with the President.
Through the creation of this fund alongside the Saudis, SoftBank has since become increasingly intertwined with Saudi Crown Prince Muhammad bin Salman (MBS), a key ally of President Trump in the Middle East known for his authoritarian crackdowns on Saudi elites and dissidents alike. The ties between Saudi Arabia and SoftBank became ever tighter when MBS took the reins in the oil kingdom and after SoftBank announced the launch of the Vision Fund in 2016. SoftBank’s Vision Fund is a vehicle for investing in hi-tech companies and start-ups and its largest shareholder is the Public Investment Fund of Saudi Arabia. Notably, Son decided to launch the Vision Fund in Riyadh during President Trump’s first official visit to the Gulf Kingdom.
In addition, the Mubadala Investment Company, a government fund of the United Arab Emirates (UAE), gave $15 billion to the Vision Fund. UAE leadership also share close ties to the Trump administration and MBS in Saudi Arabia.
As a consequence, SoftBank’s Vision Fund is majority funded by two Middle Eastern authoritarian governments with close ties to the U.S. government, specifically the Trump administration. In addition, both countries have enjoyed the rapid growth and normalization of ties with the state of Israel in recent years, particularly following the rise of current Saudi Crown Prince Muhammad bin Salman and Jared Kushner’s rise to prominence in his father-in-law’s administration. Other investments in the Vision Fund have come from Apple, Qualcomm and Oracle’s Larry Ellison, all tech companies with strong ties to Israel’s government.
The Saudi and Emirati governments’ links to the Vision Fund are so obvious that even mainstream outlets like the New York Times have described them as a “front for Saudi Arabia and perhaps other countries in the Middle East.”
SoftBank also enjoys close ties to Jared Kushner, with Fortress Investment Group lending $57 million to Kushner Companies in October 2017 while it was under contract to be acquired by SoftBank. As Barron’s noted at the time:
When SoftBank Group bought Fortress Investment Group last year, the Japanese company was buying access to a corps of seasoned investors. What SoftBank also got is a financial tie to the family of President Donald Trump’s senior advisor and son-in-law, Jared Kushner.”
According to The Real Deal, Kushner Companies obtained the financing from Fortress only after its attempts to obtain funding through the EB-5 visa program for a specific real estate venture were abandoned after the U.S. Attorney and the Securities and Exchange Commission began to investigate how Kushner Companies used the EB-5 investor visa program. A key factor in the opening of that investigation was Kushner Companies’ representatives touting Jared Kushner’s position at the White House when talking to prospective investors and lenders.
SoftBank also recently came to the aid of a friend of Jared Kushner, former CEO of WeWork Adam Neumann. Neumann made shocking claims about his ties to both Kushner and Saudi Arabia’s MBS, even asserting that he had worked with both in creating Kushner’s long-awaited and controversial Middle East “peace plan” and claimed that he, Kushner and MBS would together “save the world.” Neumann previously called Kushner his “mentor.” MBS has also discussed on several occasions his close ties with Kushner and U.S. media reports have noted the frequent correspondence between the two “princelings.”
Notably, SoftBank invested in Neumann’s WeWork using money from the Saudi-dominated Vision Fund and later went on to essentially bail the company out after its IPO collapse and Neumann was pushed out. SoftBank’s founder, Masayoshi Son, had an odd yet very close relationship with Neumann, perhaps explaining why Neumann was allowed to walk with $1.7 billion after bringing WeWork to the brink of collapse. Notably, nearly half of SoftBank’s approximately $47 billion investments in the U.S. economy since Trump’s election, went to acquiring and then bailing out WeWork. It is unlikely that such a disastrous investment resulted in the level of job creation that Son had promised Trump in 2016.
Given that it is Cybereason’s top investor and shareholder by a large margin, SoftBank’s ties to the Trump administration and key allies of that administration are significant in light of Cybereason’s odd interest in 2020 U.S. election scenarios that end with the cancellation of this year’s upcoming presidential election. It goes without saying that the cancellation of the election would mean a continuation of the Trump administration until new elections would take place.
Furthermore, with Cybereason’s close and enduring ties to Israeli military intelligence now well-documented, it is worth asking if Israeli military intelligence would consider intervening in 2020 if the still-to-be-decided Democratic contender was strongly opposed to Israeli government policy, particularly Israel’s military occupation of Palestine. This is especially worth considering given revelations that sexual blackmailer and pedophile Jeffrey Epstein, who targeted prominent U.S. politicians, mostly Democrats, was in the employ of Israeli military intelligence.
Notably, Cybereason’s doomsday election scenarios involved the weaponization of deep fakes, self-driving cars and hacking Internet of Things devices, with all of those technologies being pioneered and perfected — not by Russia, China or Iran — but by companies directly tied to Israeli intelligence, much like Cybereason itself. These companies, their technology and Cybereason’s own work creating the narrative that U.S. rival states seek to undermine the U.S. election in this way, will all be discussed in the conclusion of MintPress’ series on Cybereason and its outsized interest in the U.S. democratic process.
Featured Video
Benoit Paré: OSCE Whistleblower: The Ukraine War – Narratives vs. Reality
or go to
Aletho News Archives – Video-Images
Book Excerpt
How CIA used Ukraine as a platform for covert war against Russia
By Stephen KINZER | Responsible Statecraft | November 17, 2026
The following is an excerpt from Stephen Kinzer’s new book: Boiling Point: How America Brought War to Ukraine (Henry Holt and Company, November 2026)
Huddled beside an airstrip in southern Germany, a handful of anti-Communist warriors prepared to fire the first shots of the Cold War. A CIA officer from the Munich Operations Base was in charge. The Hungarian crewmen he had recruited stood nearby in flight suits. With them were two Ukrainian exiles who had volunteered to parachute into their homeland. They were code-named Apostle 1 and Apostle 2. Each carried forged identity papers, a miniature radio transmitter, a pistol, a machine gun, hand grenades, a purse full of gold coins, and a poison pill to be taken in case of capture. An unmarked C-47 transport plane was waiting.
The CIA officer overseeing this operation, a twenty-six-year-old Yale graduate named Stephen Tanner, watched the plane take off and disappear into the night. It flew over East Germany and Poland, then crossed into Soviet airspace. As it approached the Ukrainian city of Lviv, a cargo bay swung open. The two Ukrainians jumped into the darkness. Their mission was to link up with partisan fighters, seize territory, and establish a clandestine base through which the CIA could send them weapons.
That flight, on September 5, 1949, was the first American act of covert war in Ukraine. … continue
Blog Roll
 Aletho News
- The Food Book — First Edition, 2026, Paperback
- Benoit Paré: OSCE Whistleblower: The Ukraine War — Narratives vs. Reality
- UK forced to admit ordering backdoor access to Apple users’ data
- It’s not about China or national security. It’s about which foreign entity is allowed to spy on Americans
- Banning Palestine activists from the West will not save Israel’s image
- Iran rejects unlimited IAEA inspections amid continued military threats
- A Bridge Too Far
- David Barnea in the Bundestag – Mossad as a model for Germany’s Intelligence Services?
- Rome blasts Kiev after Italian lawmakers added to ‘kill list’
- Another €45 bn down the drain: Why the EU is desperate to waste more cash on Zelensky
- If Americans Knew
- An error has occurred; the feed is probably down. Try again later.
- No Tricks Zone
- Argentina’s Perito Moreno Glacier Joins Antarctica and Arctic In Defying Doomsday Melt Claims
- New Study: Barents Sea Temperatures Were Warmer And Sea Ice Less Extensive In The 1700s Than Today
- German Authorities Start Initiative To Evaluate Public Register For Climate “Disinformation” Spreaders!
- Zonal Asymmetry of Temperature Change in the Antarctic Circumpolar Current
- New Study: The Net Fossil Fuel Contribution To Rising Atmospheric CO2 Has Been Zero For 500 Years
- Germany’s Green Energy Transition Becoming Increasingly Expensive…Another 6 Trillion Euros!
- Sudden Stratospheric Warming, Powerful El Niño Combination May Lead To Extreme Europe Cold, Energy Crisis!
- Two New Studies Find Thwaites Glacier Melt Cannot Be Driven By Human Activity Or A Warming Ocean
- E-Cars Reduce CO2 Emissions By Only 41% Compared To Internal Combustion Engine Vehicles
- Predictions Made By Renowned Climate Professor Over Past Decades Have Been Proven To Be Poor

