‘Utter contempt for human life’: Iranian FM Zarif slams US for hitting Tehran with new sanctions amid Covid-19 crisis
RT | March 20, 2020
Iranian foreign minister Javad Zarif accused the US of taking its policy of “maximum pressure” on Tehran to a “new level of inhumanity” by imposing new sanctions on Iran as it struggles to cope with a huge surge of Covid-19 cases.
Zarif tweeted on Friday that The Trump administration was “gleefully” taking pride in “killing Iranian citizens” on Nowruz, the Persian New Year, celebrated on March 20 this year. He said US policy betrayed an “utter contempt for human life.”
His rebuke comes shortly after the US blacklisted five companies based in the United Arab Emirates for trading in Iranian petrochemicals. Three companies in China, three in Hong Kong and one in South Africa were also added to the list this week, as Washington attempts to choke off Tehran’s oil revenues.
“Washington’s increased pressure against Iran is a crime against humanity… all the world should help each other to overcome this disease,” Reuters quoted an Iranian official as saying on Friday.
“Our policy of maximum pressure on the regime continues,” US special representative for Iran Brian Hook told reporters, even though Iran is the worst-hit country in the Middle East by the Covid-19 coronavirus outbreak and may face economic catastrophe as a result.
Secretary of State Mike Pompeo said on Friday that the US has imposed “no sanctions” on medication or humanitarian assistance going into Iran. However, US financial sanctions have in effect prevented Tehran from buying the necessary supplies, while shipping sanctions have interfered with humanitarian deliveries.
China has called on the US to offer sanctions relief to Iran, with the Ministry for Foreign Affairs in Beijing tweeting on Wednesday that the policy was “against humanitarianism and hampers Iran’s epidemic response,” as well as deliveries of aid by the UN and other organizations.
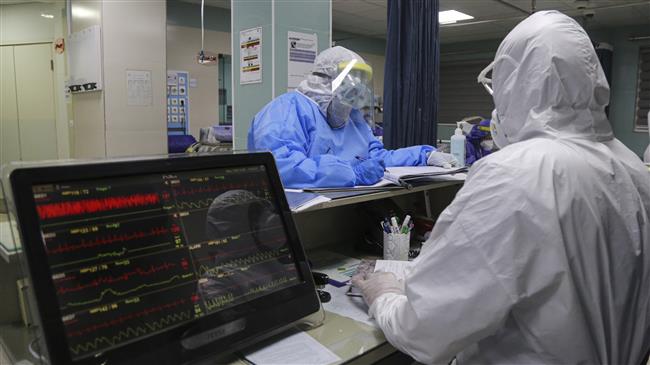
Iran has seen at least 1,400 deaths from Covid-19 so far, with more than 19,000 confirmed cases. A health ministry spokesperson said on Wednesday that one person in Iran was now dying “every 10 minutes” from the virus, with 50 new infections every hour.
US urged to explain military lab shutdown
By Leng Shumei – Global Times – 2020/3/15
Netizens and experts are calling for the US government to release information on the suspension of an infectious disease research lab under the US Army, as a petition on the White House website listed coincident events between the closure and the outbreak of COVID-19, urging the US government to clarify whether the lab was related to the deadly virus.
While the origin of the novel coronavirus is still unknown and conspiracy theories have caused widespread panic, experts said that timely information disclosure to the public would benefit global unity and cooperation against the pandemic, which had infected more than 150,000 people and killed 5,400 around the world as of Saturday.
The Fort Detrick laboratory that handles high-level disease-causing material, such as Ebola, in Fredrick, Maryland was shut after the US Centers for Disease Control and Prevention issued a cease and desist order to the organization in July, 2019 according to local media.
The suspension was due to multiple causes, including failure to follow local procedures and a lack of periodic recertification training for workers in the biocontainment laboratories. The wastewater decontamination system of the lab also failed to meet standards set by the Federal Select Agent Program, media reported.
The lab, which was closed more than half a year ago, recently caught public attention as a petition submitted to the White House website on March 10 listed some coincidences in time between the closure and the COVID-19 outbreak.
For example, “a large-scale ‘influenza’ killed more than 10,000 people” in the US in August 2019 following the closure; and the COVID-19 epidemic broke out globally in February 2020 after the US organized Event 201 – A Global Pandemic Exercise – in October 2019.
The petition also noted that many English-language news reports about the closure of Fort Detrick were deleted amid the worsening COVID-19 pandemic, raising suspicions over the lab’s relationship with the novel coronavirus.
Petitioners urged the US government to publish the real reason for the lab’s closure and to clarify whether the lab was related to the novel coronavirus and whether there was a virus leak.
The petition had received just more than 400 signatures as of Sunday.
Chinese netizens urged the US government to respond to the public’s appeals as soon as possible.
“It’s not a small issue, the truth should be published,” an internet user commented.
“The world deserves to know the truth,” said another.
Ni Feng, a deputy director of the Institute of American Studies of the Chinese Academy of Social Sciences, called on the US government to increase transparency in the COVID-19 pandemic related issues in response to wide-spread doubts.
The origin of the virus should be decided according to scientific research, but the urgent issue at the current stage is to cooperate in the global battle against the pandemic, Ni noted.
Wang Yiwei, a professor with the School of International Relations at Renmin University of China, agreed with Ni, noting that the US had behaved badly to China when the latter was struggling with the epidemic – accusing China of low transparency and blaming a Chinese lab for leaking the virus.
Now China has won the conviction of the world with practical efforts and improvements. The US should cooperate sincerely with China and the world against the virus, according to Wang.
Asleep at the wheel: Why didn’t Western politicians act quicker on Covid-19 spread?
By Neil Clark | RT | March 19, 2020
Western countries are in lockdown due to Covid-19, but if leaders, their advisers, and the political class in general had paid attention to what was going on in China at the turn of the year, the crisis might have been averted.
Imagine you’re a passenger on a ship. You’d expect, wouldn’t you, that the captain and his officers keep a very good look-out for dangers ahead? You’d expect them to have up-to-date weather information. You’d expect them to take corrective action before the ship hit an iceberg.
The sad truth – for Western citizens, the passengers of the ship – is that those whose job it was to watch out for gathering storms have let us down very badly.
The chronology is most important.
According to the South China Morning Post, the first case of someone suffering from what later came to be known as Covid-19 occurred in China on November 17. The number of cases grew in December, (the majority linked to the Huanan Seafood Market), but we didn’t know internationally what was going on until news began to come out that Wuhan had been hit by a new virus in very late December/early January. The Chinese informed the World Health Organization of new pneumonia cases of unknown etiology on December 31.
The Chinese delay in flagging up what was happening in Wuhan absolutely didn’t help, but there was still time – about a two-week window – for other countries to act.
As reported in the BMJ, on January 11 and 12, the Chinese authorities shared the virus’ genetic sequence for countries to use in “developing specific diagnostic kits.” 440 deaths had been confirmed by January 21. By the 22nd, seven cases had been confirmed OUTSIDE China, including one in the US. All were travelers from Wuhan.
That surely should have got alarm bells ringing in Western capitals, especially as Chinese New Year on January 25 was coming up. Western leaders, and their advisers, would surely know that many Chinese workers based in the West would return home to celebrate, greatly increasing the risk that the virus would be brought back to Europe and North America.
On January 22, the UK government announced that health teams would meet the three direct flights a week from Wuhan, China, the epicenter of the virus. At the same time, the risk level was raised from ‘very low’ to ‘low’. But as Neil Ferguson, director of the MRC Centre for Global Infectious Disease Analysis at Imperial College, London, pointed out, flight screening was no panacea.
“This measure will only identify people who have symptoms as they come off the plane. If someone was infected two days before they travelled, they will arrive without any symptoms at all.” He added, and I emphasize in bold: “It’s essential that the entire health system is alert to the possibility that there will be cases here.”
Lo and behold, the first British case was confirmed nine days later, on January 31, 2020, from Chinese nationals staying at a hotel in York. That very same day, the first cases were also confirmed in Italy. Guess what: they were two Chinese tourists in Rome. Italy is now the world’s number one coronavirus ‘hotspot’. Nearly 3,000 have died there and 60mn people are in quarantine.
Wouldn’t it have been better, if instead of ineffective flight screening, all flights to Western countries from China had been stopped in January – and all travelers who had recently visited China been quarantined? France, by the way, got its first three cases on January 24 (a week before Italy and the UK). All three people had just come back from China. You don’t have to be Sherlock Holmes to see the pattern, do you?
In the New Year, the number one priority of Western politicians should have been the new coronavirus and how best to protect their own populations from it. But their minds were clearly on other things.
Trump – egged on by Washington’s Endless War Lobby – was engaged in an utterly reckless escalation of tensions with Iran. While Covid-19 was spreading in China, the New Year began with the assassination of General Soleimani, a man who had been fighting ISIS, but who was now portrayed as the ‘worst terrorist in the world’. The ‘Iran crisis’ dominated the news cycle. Boris Johnson meanwhile began the year on holiday with his girlfriend in Mustique. The opposition Labour Party were focusing on a leadership election which needn’t have taken place for several months. Three of the four candidates declared on television on February 13 – a day after the UN had activated its WHO-led Crisis Management team to deal with a rapidly escalating problem –that their ‘number one priority’ was… tackling ‘anti-Semitism’ in the Labour Party. Yet after all the brouhaha about anti-Semitism being ‘rife’ in Labour, it was reported at the end of February that the police had ended up charging just one person, a former Labour member.
One person, that is, out of a membership of half a million.
It seemed in February that no one in the political class was very interested in Covid-19.
This is despite the publication in the leading medical journal The Lancet on January 24 of a report entitled ‘A novel coronavirus outbreak of global concern’.
Covid-19 only began to be taken with the seriousness it warranted when it was already too late to try and stop its entry.
By not acting in time to restrict travel to and from China – and later from other ‘hotspots’ like northern Italy and Madrid, Spain, the governments instead waited and waited, until the measures they did take were far more draconian that might otherwise have been the case. It’s true that Trump did bar foreigners who had recently visited China from entering the US on January 31, but as David Leonhardt pointed out in the New York Times, it was “not the sweeping solution that Trump portrayed it to be.”
The costs to the economies of the various lockdowns are incalculable. People’s livelihoods are going to be destroyed. Entire industries are threatened. Don’t forget lockdowns and ‘social distancing’ can actually cause deaths too. As John Pilger pointed out on Twitter, a 2012 study showed that isolation killed the elderly, but isolate is what they’re now being told to do.
We’re in a right old state at the moment, but how much of this could have been avoided if instead of dozing off, or looking elsewhere, those whose job it was to protect us had acted quickly, at the proper time?
COVID-19: All Truth Has Three Stages
By Larry Romanoff | Global Research | March 19, 2020
First, it is ignored.
Second, it is widely ridiculed.
Third, it is accepted as self-evident.
With COVID-19, we have now entered Stage 2. At first, the media ignored the claims and the analysis that the virus could have originated in the US. But the spread of information and restatements of evidence from all sides, including in the US itself, has become too intense and now the claims are being openly ridiculed in the Western media.
Briefly, Chinese virologists discovered conclusively that the original source of the virus was not China, nor Wuhan, nor the seafood market, but had been traced to the US, a possible scenario being that the virus might have originated at the US Military’s bio-weapons lab at Fort Detrick (which was shut down by the CDC in July, because of outbreaks), and brought to China during the World Military Games in October 2019.
Also, Japanese and Taiwanese virologists arrived independently at the conclusion that the virus could have originated in the US.
The Americans did their best from before the beginning to deflect culpability by crafting tales of bats, snakes, pangolins, the seafood market, the Wuhan University being a bio-weapons facility (which it is not), and the CIA tale leaked through the VOA and Radio Free Asia that the virus leaked from that university. They stated (factually) that Chinese researchers had participated (7 years ago) in similar virus research funded by the US NIH, thus somehow insinuating Chinese culpability, ignoring that the prior research was irrelevant to current events.
I must say the Americans have proven to be very skillful in grabbing the microphone first, to create an “official” narrative of a current event while flooding the media with sufficient finger-pointing to preclude a gullible public the time to logically assemble the pieces on their own.
They ignored the very real fact that few nations would either create or release a biological weapon that attacks primarily itself. They ignored too, the geopolitical likelihood of an ”end game” – that a virus is a powerful weapon of economic warfare, able to do to China’s economy what a trade war could not do.
Casual readers tend to ignore the fact that, in the American mentality, there are many solid geopolitical reasons to attack China, Iran, and Italy, the remaining countries merely constituting unfortunate collateral damage.
Many virus articles containing this and similar information had been published by second-tier internet news sites, some articles gaining enormous readership with hundreds of thousands of downloads and much re-posting. Many of these articles have been translated into 6 or 7 languages and published on websites all around the world. Simultaneously, many posts were made on Chinese social media speculating on the odd circumstances and long chain of unusual coincidences that led to the virus outbreak in Wuhan.
One of the articles referred to above, was translated and posted on Chinese social media and gathered 76,000 comments in the first 8 hours. Eventually, the major Chinese media outlets made the same claims – that the virus could have originated in the US and that the Americans were engaging in a massive cover-up.
Then, Zhao LiJian, a spokesman for China’s Foreign Ministry, made the story official, through a number of posts on US social media. One major media article, this in the NYT, noted that “Zhao’s remarks were spread on China’s most prominent social media platform, Weibo . . . [and] had been viewed more than 160 million times, along with screenshots of the original Twitter posts.
It seems LiJian’s Twitter posts, being essentially an official source that could not easily be ignored, claiming the virus was brought to China from the US during the Military Games, and demanding an explanation from the US, were receiving too much public attention to be ignored. All of the above created sufficient political pressure to force the Western media to respond. And of course they responded by ignoring the facts of the message and trashing the messenger.
On March 12, the UK Guardian ran a story claiming China was “pushing propaganda” about the virus coming from the US. (1) On March 13, the New York Times ran a similar story of a “China coronavirus conspiracy” of false claims about the source of the virus. (2) Then, on March 14, ABC News ran a story titled “False claims about sources of coronavirus cause spat between the US, China”, in which it ridiculed China and the claims of a US-virus. (3)
The Seattle Times published a version of the story, stating, “China is pushing a new theory about the origins of the coronavirus: It is an American disease . . . introduced by members of the U.S. Army who visited Wuhan in October. There is not a shred of evidence to support that, but the notion received an official endorsement from China’s Ministry of Foreign Affairs, whose spokesman accused American officials of not coming clean about what they know about the disease.” (4) The UK Independent published their own version of “China’s conspiracy theory” (5), as did CNN (6).
The ABC article claimed that “Assistant Secretary David Stilwell gave [Chinese] Ambassador Cui Tiankai a “very stern representation of the facts,” claiming Cui was “very defensive” in the face of this “official” American assault. The US State Department is quoted as having said, “We wanted to put the [Chinese] government on notice we won’t tolerate [conspiracy theories] for the good of the Chinese people and the world.”
Following that, the Washington Post, Bloomberg, and half a dozen other press wires and media outlets have contacted this author for interviews, eager for an opportunity to trash this ‘conspiracy theory’ at its source. The US Embassy in Beijing also “reached out” to the author “to talk about it”.
If the public information campaign and the resulting political pressure can continue, we will eventually enter stage three where the media will begin admitting first the possibility, then the likelihood, then the fact, of the US being the source of the “China” virus.
***
Larry Romanoff is a retired management consultant and businessman. He has held senior executive positions in international consulting firms, and owned an international import-export business. He has been a visiting professor at Shanghai’s Fudan University, presenting case studies in international affairs to senior EMBA classes. Mr. Romanoff lives in Shanghai and is currently writing a series of ten books generally related to China and the West. He can be contacted at: 2186604556@qq.com. He is a frequent contributor to Global Research.
Notes
(2) https://www.nytimes.com/2020/03/13/world/asia/coronavirus-china-conspiracy-theory.html
(3) https://abcnews.go.com/Politics/false-claims-sources-coronavirus-spat-us-china/story?id=69580990
(4) https://www.seattletimes.com/nation-world/china-spins-tale-that-the-u-s-army-started-the-coronavirus-epidemic/
https://www.ccn.com/did-coronavirus-originate-in-america-chinese-media-pushes-conspiracy/
(6) https://www.ccn.com/did-coronavirus-originate-in-america-chinese-media-pushes-conspiracy/
Copyright © Larry Romanoff, Global Research, 2020
Australia assigned to be the U.S. Policeman in the Pacific
By Paul Antonopoulos | March 19, 2020
The U.S. is ramping up pressure on Australia to support hostilities against China in Southeast Asia and the South Pacific. Last week in Sydney, the U.S. Ambassador to Australia, Arthur Culvahouse, said that “We’ll be pushing Australia to expand its step-up from the Pacific islands region to south-east Asia and to look north as well.” The U.S., Australia and like-minded countries need to win in this strategic competition, the diplomat said. The Ambassador emphasized that in consultations between American and Australian foreign and defense ministers, the two sides will focus their efforts to further strengthen the Pacific step-up strategy.
The US Ambassador told the gathering of business leaders last Tuesday that Australia “sits on the frontline of the great strategic competition of our time.” “If the security and prosperity enjoyed by our countries and the region is to continue, this is a competition that we must win,” he said in indirect reference to China being the competition that must lose.
Australia’s Pacific strategy was adopted in 2016 under Prime Minister Malcolm Turnbull to assert Australia’s position as the policeman for the U.S. in the South Pacific and Southeast Asia. The Pacific step-up strategy defines the Australian government’s approach to economic and strategic interaction with Pacific Island nations. However, this is just the friendly face of the strategy and rather it is primarily aimed at maintaining regional balance to counter China’s growing influence in the region. China signed an Action Program with eight Pacific Island nations at the October 2019 3rd China Economic Development Cooperation Forum and Pacific Islands held in Samoa. These countries’ support for China’s Belt and Road Initiative was confirmed.
As the U.S. is dealing with the growing influence of China and attempting to counter it all over the globe, Washington is relying on Australia to serve as a counterbalance to China in the South Pacific and Southeast Asia. However, as the coronavirus continues to grow out of control in the U.S., it is likely that Washington is going to take its focus off the South Pacific for a long while. This will give Australia autonomy to act on Washington’s behalf and it appears that U.S. President Donald Trump immensely trusts the Australians in this role, so-much-so that he honored the fellow Anglo-settler state by naming a new navy ship the USS Canberra, the only U.S. Navy warship named after a foreign city.
Australia wilfully wants to play a role that the U.S. assigned to them in Southeast Asia and the South Pacific so that it can more strongly assert its power on the region. Australia considers the small island countries of the South Pacific as an area within its sphere of influence. Canberra has a need to expand its weight in Southeast Asia, but finds this challenging as the region includes countries of larger populations and economies, such as Thailand and Indonesia.
Although Canberra wants to serve Washington’s interests in the region, Australia is a completely deindustrialized neoliberal country that does not have the means or capacity to challenge rising Southeast Asian countries and rather serves as a raw resource marketplace for the world. The U.S. is losing influence in Southeast Asia to China, and therefore Washington is relying on Australian support, hedging its bet on a common Anglo colonial-settler history to make Canberra receptive.
In this situation, Australia faces a very difficult choice as there is a clear divide between the economic community and the political class in regards to China policy. China is Australia’s most important economic partner, while the U.S. is Canberra’s most important security partner, so-much-so that Australia followed the U.S. to adventurist wars of aggression in Korea, Vietnam, Afghanistan and Iraq. China and Australia have established free trade areas and this agreement allows them to quickly increase the volume of bilateral trade. Therefore, the political will of Canberra is certain to face resistance from capitalist interests in the country as it wholly relies on China and other Southeast Asian countries for trade.
However, Australia is bound by the U.S. Indo-Pacific Strategy that aims to use American allies like Australia, Japan, India and others, to counter China’s increasing influence. This is done by enhancing military cooperation between these countries and does not serve any economic role like the Belt and Road Initiative. As China finds the Indo-Pacific Strategy as an aggressive force aimed against it, it is likely that under economic pressure, Australia will try to balance relations, despite the political will and determination of Canberra to act as the U.S’ policeman in Southeast Asia and the South Pacific.
Paul Antonopoulos is a Research Fellow at the Center for Syncretic Studies.
The indictment of Concord was meant to prove Russia interfered in the US presidential election. But it was just a political sham
By Scott Ritter | RT | March 17, 2020
Now that the Department of Justice has rightly dismissed the case, it just shows that the allegations were aimed at shaping public opinion – and that it’s all about the politicization of the US Justice System
It was the indictment that shook America. Or at least, it was supposed to. For months, prosecutors working for Robert Mueller – the special prosecutor charged with investigating allegations of collusion between the campaign of then-candidate Donald Trump and various Russian actors to tip the scales of the 2016 US presidential election in Trump’s favor – had been slaving away behind a wall of secrecy. Set up in May 2017, the Mueller team had little to show for its efforts save for a handful of guilty pleas by Trump associates for lying to federal agents. No evidence had been provided to an increasingly skeptical public to sustain the notion that the Russians had actively interfered in the election.
That changed in February 2018, when the Mueller team unveiled an indictment of thirteen Russian citizens and three Russian companies, including Concord Management, spelling out in detail an assortment of acts that, on the surface, looked damning. “From in or around 2014 to the present,” the indictment read, “defendants knowingly and intentionally conspired with each other (and with persons known and unknown to the Grand Jury) to defraud the United States by impairing, obstructing and defeating the lawful functions of the Government through fraud and deceit for the purpose of interfering with the US political and electoral processes, including the presidential election of 2016.”
From that point on, “thirteen individuals and three companies” became the mantra of the pro-“Russia did it” brigade, repeated over and over again on TV news, Twitter, Facebook and other platforms where they and their ilk gathered to promote the theory that President Trump had colluded with the Russians to secure his electoral victory in 2016. Whenever anyone questioned the validity of the investigation, like clockwork the supporters of Mueller and his work would religiously cite the existence of this indictment, as if, in and of itself, it proved Mueller’s case.
It was a pure numbers game, inflated further when Mueller and his team indicted twelve serving Russian Military Intelligence officers for allegedly hacking the Democratic National Committee server, among other alleged crimes, in the spring of 2016. What had Mueller accomplished with these indictments? The reality was that they were little more than a publicity stunt, a public relations game that allowed Mueller supporters to respond that “he indicted 25 Russians and three Russian companies” any time the accomplishments of the investigation were brought into question.
While these statistics sounded impressive, creating as they did the impression of irrepressible, righteous momentum, they represented little more than grand theater designed to create an impression of guilt that wasn’t backed up by fact. The Mueller indictment targeting Concord Management grew out of a grand jury investigation where the government had total control of the evidence presented. There’s an old saying about the US grand jury system, that “a prosecutor can indict a ham sandwich” – the implication being you can make anyone look guilty for anything at any time. The ham sandwich isn’t given the chance to present its case.
Normally, an indictment would compel a defendant, presented with overwhelming evidence of his or her guilt, to seek a plea arrangement. Or, seeing that the evidence was insufficient, they would take the case to trial where, through discovery, the prosecutor would be compelled to hand over any and all evidence so that the defense could mount a counterargument. In this light, a prosecutor would normally craft the grand jury case in a way that maximized its impact at trial. But the Concord Management case, like the case against the Russian intelligence officers, was never meant to go to trial. No one expected the Russians to mount a defense, because to do so would require their presence in the court, on American soil, where they would be subject to arrest and confinement.
Concord Management, however, took everyone by surprise, hiring a US-based legal team to defend it against the plethora of fantastic allegations that underpinned the indictment. In doing so, Concord Management put the Mueller team in a position where they would have to disclose how they obtained all the extraordinary details about the alleged Russian activities, including internal emails, travel itineraries, and specific details about the thirteen Russian men and women.
Confronted with the reality that Concord was ultimately prepared to take the case to trial, the Department of Justice pulled the plug on the indictment, hiding behind the claim that sensitive law enforcement techniques would be revealed if it was required to present its case. Oh, really?
This revelation only underscores how ill-prepared the Mueller team was to take the Concord case to trial – normally, questions about what evidence can and cannot be presented at trial are worked out before the indictment is published. But when an indictment is more about manipulating public perception by putting forth unsustained allegations, rather than proving actual fact-based guilt, issues about evidentiary classification don’t matter. But in this case, however, they do matter – and the US government, its bluff called, was compelled to dismiss the charges.
Under normal circumstances, the announcement that the indictment used to underpin the credibility of an investigation into whether the now-President of the United States colluded with Russia to win an election had been dismissed would not only be headline news, but would also generate public outrage and demands that those who brought the indictment forward be investigated for politicizing the American justice system.
But there is nothing normal about the present circumstance. The combined impact of the Mueller investigation (which stalled far short of its goal of indicting the president) and the related impeachment trial process (which likewise failed) left the American public sharply divided on the issue of Trump-Russian collusion, facts be damned. The dismissal of the Concord indictment should be further evidence that the allegations of Russian interference in the 2016 presidential election have been vastly overblown. The other indictments are similarly unsustainable at trial.
It’s just disappointing that the coronavirus news cycle will probably drown out this story, leaving the ramifications of the abuse of the US legal system by politically motivated prosecutors unexplored, and the American public worse off for it.
Scott Ritter is a former US Marine Corps intelligence officer. He served in the Soviet Union as an inspector implementing the INF Treaty, in General Schwarzkopf’s staff during the Gulf War, and from 1991-1998 as a UN weapons inspector. Follow him on Twitter @RealScottRitter
WHY IS CROWDSTRIKE CONFUSED ON ELEVEN KEY DETAILS ABOUT THE DNC HACK?
By Larry C Johnson | Sic Semper Tyrannis | March 17, 2020
Here is the bottom-line—despite being hired in late April (or early May) of 2016 to stop an unauthorized intrusion into the DNC, CrowdStrike, the cyber firm hired by the DNC’s law firm to solve the problem, failed abysmally. More than 30,000 emails were taken from the DNC server between 22 and 25 May 2016 and given to Wikileaks. Crowdstrike blamed Russia for the intrusion but claimed that only two files were taken. And CrowdStrike inexplicably waited until 10 June 2016 to reboot the DNC network.
CrowdStrike, a cyber-security company hired by a Perkins Coie lawyer retained by the DNC, provided the narrative to the American public of the alledged hack of the DNC, But the Crowdstrike explanation is inconsistent, contradictory and implausible. Despite glaring oddities in the CrowdStrike account of that event, CrowdStrike subsequently traded on its fame in the investigation of the so-called Russian hack of the DNC and became a publicly traded company. Was CrowdStrike’s fame for “discovering” the alleged Russian hack of the DNC a critical factor in its subsequent launch as a publicly traded company?
The Crowdstrike account of the hack is very flawed. There are 11 contradictions, inconsistencies or oddities in the public narrative about CrowdStrike’s role in uncovering and allegedly mitigating a Russian intrusion (note–the underlying facts for these conclusions are found in Ellen Nakashima’s Washington Post story, Vicki Ward’s Esquire story, the Mueller Report and the blog of Crowdstrike founder Dmitri Alperovitch):
- Two different dates—30 April or 6 May—are reported by Nakashima and Ward respectively as the date CrowdStrike was hired to investigate an intrusion into the DNC computer network.
- There are on the record contradictions about who hired Crowdstrike. Nakashima reports that the DNC called Michael Sussman of the law firm, Perkins Coie, who in turn contacted Crowdtrike’s CEO Shawn Henry. Crowdstrike founder Dmitri Alperovitch tells Nakashima a different story, stating our “Incident Response group, was called by the Democratic National Committee (DNC).
- CrowdStrike claims it discovered within 24 hours the “Russians” were responsible for the “intrusion” into the DNC network.
- CrowdStrike’s installation of Falcon (its proprietary software to stop breaches) on the DNC on the 1st of May or the 6th of May would have alerted to intruders that they had been detected.
- CrowdStrike officials told the Washington Post’s Ellen Nakashima that they were, “not sure how the hackers got in” and didn’t “have hard evidence.”
- In a blog posting by CrowdStrike’s founder, Dmitri Alperovitch, on the same day that Nakashima’s article was published in the Washington Post, wrote that the intrusion into the DNC was done by two separate Russian intelligence organizations using malware identified as Fancy Bear (APT28) and Cozy Bear (APT29).
- But, Alperovitch admits his team found no evidence the two Russian organizations were coordinating their “attack” or even knew of each other’s presence on the DNC network.
- There is great confusion over what the “hackers” obtained. DNC sources claim the hackers gained access to the entire database of opposition research on GOP presidential candidate Donald Trump. DNC sources and CrowdStrike claimed the intruders, “read all email and chat traffic.” Yet, DNC officials insisted, “that no financial, donor or personal information appears to have been accessed or taken.” However, CrowdStrike states, “The hackers stole two files.”
- Crowdstrike’s Alperovitch, in his blog posting, does not specify whether it was Cozy Bear or Fancy Bear that took the files.
- Wikileaks published DNC emails in July 2016 that show the last message taken from the DNC was dated 25 May 2016. This was much more than “two files.”
- CrowdStrike, in complete disregard to basic security practice when confronted with an intrusion, waited five weeks to disconnect the DNC computers from the network and sanitize them.
Let us start with the very contradictory public accounts attributed to Crowdstrke’s founder, Dmitri Alperovitch. The 14 June 2016 story by Ellen Nakashima of the Washington Post and the October 2016 piece by Vicki Ward in Esquire magazine offer two different dates for the start of the investigation:
When did the DNC learn of the “intrusion”?
Ellen Nakashima claims it was the end of April:
DNC leaders were tipped to the hack in late April. Chief executive Amy Dacey got a call from her operations chief saying that their information technology team had noticed some unusual network activity. . . . That evening, she spoke with Michael Sussmann, a DNC lawyer who is a partner with Perkins Coie in Washington. Soon after, Sussmann, a former federal prosecutor who handled computer crime cases, called Henry, whom he has known for many years. Within 24 hours, CrowdStrike had installed software on the DNC’s computers so that it could analyze data that could indicate who had gained access, when and how.
Ward’s timeline, citing Alperovitch, reports the alert came later, on 6 May 2016:
At six o’clock on the morning of May 6, Dmitri Alperovitch woke up in a Los Angeles hotel to an alarming email. . . . late the previous night, his company had been asked by the Democratic National Committee to investigate a possible breach of its network. A CrowdStrike security expert had sent the DNC a proprietary software package, called Falcon, that monitors the networks of its clients in real time. Falcon “lit up,” the email said, within ten seconds of being installed at the DNC: Russia was in the network.
This is a significant and troubling discrepancy because it marks the point in time when CrowdStrike installed its Falcon software on the DNC server. It is one thing to confuse the 30th of April with the 1st of May. But Alperovitch gave two different reporters two different dates.
What did the “hackers” take from the DNC?
Ellen Nakashima’s reporting is contradictory and wrong. Initially, she is told that the hackers got access to the entire Donald Trump database and that all emails and chats could be read. But then she is assured that only two files were taken. This was based on Crowdstrike’s CEO’s assurance, which was proven subsequently to be spectacularly wrong when Wikileaks published 35,813 DNC emails. How did Crowdstrike miss that critical detail? Here is Nakashima’s reporting:
Russian government hackers penetrated the computer network of the Democratic National Committee and gained access to the entire database of opposition research on GOP presidential candidate Donald Trump, according to committee officials and security experts who responded to the breach.
The intruders so thoroughly compromised the DNC’s system that they also were able to read all email and chat traffic, said DNC officials and the security experts. . . .
The DNC said that no financial, donor or personal information appears to have been accessed or taken, suggesting that the breach was traditional espionage, not the work of criminal hackers.
One group, which CrowdStrike had dubbed Cozy Bear, had gained access last summer (2015) and was monitoring the DNC’s email and chat communications, Alperovitch said.
The other, which the firm had named Fancy Bear, broke into the network in late April and targeted the opposition research files. It was this breach that set off the alarm. The hackers stole two files, Henry said. And they had access to the computers of the entire research staff — an average of about several dozen on any given day. . . .
CrowdStrike is continuing the forensic investigation, said Sussmann, the DNC lawyer. “But at this time, it appears that no financial information or sensitive employee, donor or voter information was accessed by the Russian attackers,” he said.
The DNC emails that are posted on the Wikileaks website and the metadata shows that these emails were removed from the DNC server starting the late on the 22nd of May and continuing thru the 23rd of May. The last tranche occurred late in the morning (Washington, DC time) of the 25th of May 2016. Crowdstrike’s CEO, Shawn Henry, insisted on the 14th of June 2016 that “ONLY TWO FILES” had been taken. This is demonstrably not true. Besides the failure of Crowdstrike to detect the removal of more than 35,000 emails, there is another important and unanswered question—why did Crowdstrike wait until the 10th of June 2016 to start disconnecting the DNC server when they allegedly knew on the 6th of May that the Russians had entered the DNC network?
Crowdstrike accused Russia of the DNC breach but lacked concrete proof.
Ellen Nakashima’s report reveals that Crowdstrike relied exclusively on circumstantial evidence for its claim that the Russian Government hacked the DNC server. According to Nakashima:
CrowdStrike is not sure how the hackers got in. The firm suspects they may have targeted DNC employees with “spearphishing” emails. These are communications that appear legitimate — often made to look like they came from a colleague or someone trusted — but that contain links or attachments that when clicked on deploy malicious software that enables a hacker to gain access to a computer. “But we don’t have hard evidence,” Alperovitch said.
There is a word in English for the phrases, “Not sure” and “No hard evidence”–that word is, “assumption.” Assuming that the Russians did it is not the same as proving, based on evidence, that the Russians were culpable. But that is exactly what CrowdStrike did.
The so-called “proof” of the Russian intrusions is the presence of Fancy Bear and Cozy Bear?
At first glance, Dmitri Alperovitch’s blog posting describing the Fancy Bear and Cozy Bear “intrusions” appears quite substantive. But cyber security professionals quickly identified a variety of shortcomings with the Alperovitch account. For example, this malware is not unique nor proprietary to Russia. Other countries and hackers have access to APT28 and have used it.
Skip Folden offers one of the best comprehensive analyses of the problems with the Alperovitch explanation:
No basis whatsoever:
APT28, aka Fancy Bear, Sofacy, Strontium, Pawn Storm, Sednit, etc., and APT29, aka Cozy Bear, Cozy Duke, Monkeys, CozyCar,The Dukes, etc., are used as ‘proof’ of Russia ‘hacking’ by Russian Intelligence agencies GRU and FSB respectively.
There is no basis whatsoever to attribute the use of known intrusion elements to Russia, not even if they were once reverse routed to Russia, which claim has never been made by NSA or any other of our IC.
On June 15, 2016 Dmitri Alperovitch himself, in an Atlantic Council article, gave only “medium-level of confidence that Fancy Bear is GRU” and “low-level of confidence that Cozy Bear is FSB.” These assessments, from the main source himself, that either APT is Russian intelligence, averages 37%-38% [(50 + 25) / 2].
Exclusivity:
None of the technical indicators, e.g., intrusion tools (such as X-Agent, X-Tunnel), facilities, tactics, techniques, or procedures, etc., of the 28 and 29 APTs can be uniquely attributed to Russia, even if one or more had ever been trace routed to Russia. Once an element of a set of intrusion tools is used in the public domain it can be reverse-engineered and used by other groups which precludes the assumption of exclusivity in future use. The proof that any of these tools have never been reverse engineered and used by others is left to the student – or prosecutor.
Using targets:
Also, targets have been used as basis for attributing intrusions to Russia, and that is pure nonsense. Both many state and non-state players have deep interests in the same targets and have the technical expertise to launch intrusions. In Grizzly Steppe, page 2, second paragraph, beginning with, “Both groups have historically targeted …,” is there anything in that paragraph which can be claimed as unique to Russia or which excludes all other major state players in the world or any of the non-state organizations? No.
Key Logger Consideration:
On the subject of naming specific GRU officers initiating specific actions on GRU Russian facilities on certain dates / times, other than via implanted ID chips under the finger tips of these named GRU officers, the logical assumption would be by installed key logger capabilities, physical or malware, on one or more GRU Russian computers.
The GRU is a highly advanced Russian intelligence unit. It would be very surprising were the GRU open to any method used to install key logger capabilities. It would be even more surprising, if not beyond comprehension that the GRU did not scan all systems upon start-up and in real time, including key logger protection and anomalies of performance degradation and data transmissions.
Foreign intelligence source:
Other option would be via a foreign intelligence unit source with local GRU access. Any such would be quite anti-Russian and be another nail in the coffin of any chain of evidence / custody validity at Russian site.
Stated simply, Dmitri Alperovitch’s conclusion that “the Russians did it” are not supported by the forensic evidence. Instead, he relies on the assumption that the presence of APT28 and APT29 prove Moscow’s covert hand. What is even more striking is that the FBI accepted this explanation without demanding forensic evidence.
Former FBI Director James Comey and former NSA Director Mike Rogers testified under oath before Congress that neither agency ever received access to the DNC server. All information the FBI used in its investigation was supplied by CrowdStrike. The Hill reported:
The FBI requested direct access to the Democratic National Committee’s (DNC) hacked computer servers but was denied, Director James Comey told lawmakers on Tuesday.
The bureau made “multiple requests at different levels,” according to Comey, but ultimately struck an agreement with the DNC that a “highly respected private company” would get access and share what it found with investigators.
The foregoing facts raise major questions about the validity of the Crowdstrike methodology and conclusions with respect to what happened on the DNC network. This is not a conspiracy theory. It is a set of facts that, as of today, have no satisfactory explanation. The American public deserve answers.
U.S. Forces Withdraw From Key Base Near Syrian Border. More Rocket Attacks On U.S. Targets In Iraq
South Front | March 18, 2020
Late on March 17, at least three rockets struck the area near the US embassy in Baghdad’s fortified Green Zone. This was the fourth such attack in the span of a week. A day earlier, a pair of rockets struck the Besmaya base south of Baghdad. This military facility is the second largest military base operated by the US-led coalition in Iraq after Camp Taji.
The threat of rocket attacks already forced the US military to announce that it is evacuating some of its bases in the country. The al-Qaim base, near the Syrian-Iraqi border, is among them. The al-Qaim facility has been an important logistical and operational hub employed by US forces for operations in western Iraq and eastern Syria. Its presence there, as well as in Syria’s al-Tanf, has allowed the US to project its power along the Syrian-Iraqi border more effectively and to support Israeli military actions against Iranian-backed forces in the area.
Al-Qaim is located on the highway between the Iraqi capital of Baghdad and the Syrian city of Deir Ezzor. The town of al-Bukamal, which Israeli and US media often label as a stronghold of Iranian-backed forces, is located on the Syrian side of the border.
The withdrawal from al-Qaim is a signal that the US has been forced to admit that its attempts to cut off the land link between Syria, Iraq and Iran have failed. Washington was seeking to prevent a free movement of troops, weapons and other supplies from one country to another.
Meanwhile in Syria, the Idlib zone remains the main focus of tensions. Idlib armed groups and their supporters continue blocking efforts to create a security zone along the M4 highway in southern Idlib, as had been agreed by Turkey and Russia. These actions are accompanied by a fierce war propaganda campaign against the Damascus government, Iran and Russia. If the situation develops in this direction and further, the only remaining option to implement the new de-escalation deal and neutralize the terrorist threat will be a new military operation.
Forced displacement and the US-Israel special relationship
By Ramona Wadi | MEMO | March 18, 2020
Democrats in the US House of Representatives have sent a letter to Secretary of State Mike Pompeo, asking the government to ensure that Israel is not using military equipment supplied or financed by America to perpetuate the forced displacement of Palestinian civilians.
“As supporters of the US-Israel special relationship and in light of the longstanding use of US-origin and supplied equipment by Israeli security forces,” they wrote, “we specifically request an examination of Israeli compliance with the requirements.” This was a reference to the US Arms Export Control Act which does not permit recipient countries to use such equipment unless for “legitimate self-defence” purposes.
The US said the Representatives, “should work to prevent unlawful home demolitions and the forcible transfer of civilians everywhere in the world and prevent the use of US-origin equipment in this destructive practice.”
Politically, though, the US-Israel relationship will take precedence over any human rights concerns. A letter by supporters of this relationship is already compromised in terms of upholding the colonial narrative and separating the recent statistics regarding home demolitions from the historical ethnic cleansing of Palestine which paved the way for colonial Israel’s establishment.
In light of the US “deal of the century” and the impending annexation of more Palestinian land, there is an inherent futility in this exercise of demanding answers from the government. It might satisfy some uneasy consciences but it will not contribute anything to the Palestinian people in terms of safeguarding their legitimate rights.
The deal of the century has demonstrated that what Israel has been doing all along — imposing unilateral measures to expand its colonial project — has given the Zionist state perpetual impunity. Israel, now aided by the US overtly, is ahead of the international community and its stagnant practices when it comes to human rights violations and international law. The US, like other countries, should be working towards eradicating forced displacement. Instead, it has chosen to support Israel’s expansion and penned a deal which will increase the number of people displaced.
Asking for clarification as a means to preserve US support for Israel defeats the purpose of trying to ensure that the end use of US aid is lawful. This contradictory approach must not be construed as a step forward in protecting Palestinians’ rights. It is a perfunctory exercise that detracts from the international law violation at hand, which is America’s political support for Israel’s annexation plans.
The letter shows how human rights concerns are being subjected to political allegiances. It does not call for a suspension of the “special relationship” between the US and Israel, but rather selectively targets a sliver of cooperation which facilitates Israel’s colonial expansion. It is well known that Israel manipulates its self-declared “exceptionalism” to prolong its violations against the Palestinian people and that the US is happy to play along with this.
“My hope is that Israel will stop the home demolitions and will see that there are many supporters of the US-Israel relationship on this letter,” explained US Representative Rohit Khanna. Such emphasis clarifies the underlying intent; the signatories may oppose forced displacement, but the political relationship will continue to take precedence, rather than make Israel reflect upon the consequences of what the International Criminal Court has clearly defined as war crimes.
Sheldon Adelson keeps casinos open despite coronavirus danger
By Alison Weir | If Americans Knew | March 17, 2020
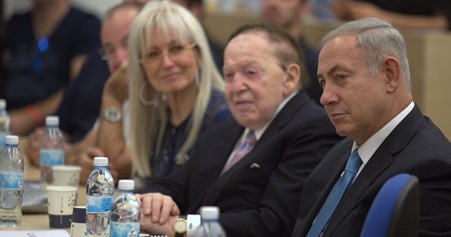
Bloomberg news reports that while other major Las Vegas casinos have closed to protect employees and the public from the coronavirus pandemic, Sheldon Adelson is keeping his casinos open.
According to Casino.org : “From the Strip to New England to the Midwest to California, commercial and tribal operators announced over the weekend they’d either voluntarily close casinos or do so to comply with state government orders barring large gatherings.”
On Monday President Trump called for Americans to avoid gatherings of more than 10 people, and the Nevada governor ordered schools and state offices to close.
Unlike governors elsewhere, the order did not include casinos, a powerful force in Nevada. However, the governor asked local governments to enforce a new Centers for Disease Control and Prevention guideline that all events with attendance above 50 be canceled or postponed.
Adelson’s billions used on behalf of Israel
Adelson is known for using his casino profits to obtain US policies beneficial for Israel by donating to American candidates for office. Adelson’s net worth is in the range of $37 billion.
In recent years, Adelson and his wife Miriam, an Israeli citizen, gave $205.83 million to Republican campaign efforts.
The Adelsons are credited with Trump’s decision to move the US Embassy to Jerusalem (after both Republican and Democratic presidents had long kept it in Tel Aviv), Trump’s decision to withdraw from the Iran nuclear deal, and the recent Trump-Kushner “peace plan.”
Adelson is a fervent advocate for Israel despite its long record of human rights violations and violations of U.S. laws, documented by Human Rights Watch, the Red Cross, Foreign Service Journal, and others.
He once infamously announced that he regretted serving in the U.S. army rather than the Israeli military.
Similarly, Miriam Adelson has said that her heart has always remained in Israel, but she got “stuck” in America after meeting Adelson.
In 2018 Trump bestowed the Presidential Medal of Freedom on the couple for their “philanthropic work.”
While the Adelsons have donated to medical research and programs addressing drug addiction (but apparently not gambling addiction, disastrous for many Americans), it appears that the bulk of their philanthropy involves Israel. Inside Philanthropy reports:
“The Adelson Family Foundation, one of Adelson’s philanthropic vehicles, is concerned with Jewish causes around the world. Adelson takes a decidedly pro-Israel stance, which is reflected in his and his wife Miriam’s philanthropy. The foundation supports charitable organizations located primarily in Israel and the United States, with funds going to Israel Advocacy and Defense, Israel Studies, Holocaust and Anti-Semitism Awareness, among others.
“Birthright Israel is a major grantee. The couple via their foundation have given tens of millions to the organization. Another youth outfit that the Adelsons have funded is B’nai B’rith Youth Organization. The Adelsons founded the Dr. Miriam and Sheldon G. Adelson Educational Campus in Las Vegas, “the only school in Nevada built on the Jewish ethos of community, service, innovation and discourse.” The school offers classes for students aged 18 months through 12th grade. Other education grantees include a mix of Israel and U.S. outfits, including American Friends of Ariel University, which supports Ariel University in Israel, and Rashi School in the Boston Area. Adelson funds a number of agencies that aim to shift policy and attitudes around Israel and the Jewish people, including Christians United for Israel, “an American pro-Israel Christian organization that defines itself as “a national grassroots movement focused on the support of Israel.” Sheldon and Miriam have also given millions to SpaceIL, an Israeli nonprofit founded by three young engineers at the end of 2010, answering the Google Lunar XPRIZE challenge.”
Trump had been scheduled to attend a fundraiser at the Adelsons’ Las Vegas mansion on Thursday, but called this off due to the pandemic. He had also been planning to address the Republican Jewish Coalition’s annual leadership meeting at Adelsons’ Sands’ Venetian casino resort.
Scheduled for Adelson’s Venetian and Palazzo resorts, the three-day meeting was expected to include numerous conservative politicians and leaders. Tickets began at $1,00 and were only available for current members of the RJC National Leadership. Adelson is on the RJC board.
The RJC announces that it “stands with Israel.” While the RJC states, “Hamas has sent hundreds of missiles from Gaza against Israeli civilians in recent days,” it fails to report that these mostly homemade rockets came after massive Israeli violence. Rockets from Gaza have killed about 29 Israelis in total, while Israeli airstrikes have killed over 3,500 Gazans.
Alison Weir is executive director of If Americans Knew, president of the Council for the National Interest, and author of Against Our Better Judgment: The Hidden History of How the U.S. Was Used to Create Israel.
US Military Accuses North Korea of Lying About Coronavirus Infection Rate of Zero
Sputnik – March 17, 2020
North Korea, whose contacts with the outside world remain limited even in a normal situation, was one of the first countries to introduce tough inspection and quarantine measures, canceling tourist visits, cutting off flights and rail travel and quarantining all workers coming home from abroad.
Nearly three months into the COVID-19 outbreak, North Korean health officials maintain that the country has zero cases of the virus.
The Korean Central News Agency reported last week that it there were no cases of COVID-19 in the country, but urged the public to remain vigilant. The agency reported that the country has enforced “strict, top-class anti-epidemic measures,” to intensify its coronavirus response, including the tightening of inspection and quarantine of imports from abroad. The measures are said to include comprehensive “inspection and disinfection of vehicles, vessels and goods,” and a 10-day quarantine of imports.
The World Health Organization too has indicated that it’s not aware of any cases of the virus in the self-isolating country, although the organization does plan to send equipment and supplies to help Pyongyang battle COVID-19. North Korea had previously asked the WHO for material assistance including disposable gowns, gloves and hazmat suits.
The popular Coronavirus Resource Center map run by Johns Hopkins’ University School of Medicine, which depends on credible sources including the WHO and the US Centers for Disease Control and Prevention, also reports zero cases for North Korea thus far.
However, US officials believe Pyongyang, which is required to report on any outbreak of contagious viruses as part of its WHO membership obligations, is lying.
Speaking to reporters last week, US Forces Korea commander Gen. Robert Abrams said the Pentagon was “fairly certain” that the country had coronavirus cases given the lack of noticeable military activity. According to the US commander, the North Korean military only recently restarted training following a month-long lockdown.
Keith Luse, executive director of the National Committee on North Korea, a Washington-based think tank, told Bloomberg that it “it’s hard to imagine that North Korea could dodge the COVID-19 bullet.”
Western media have similarly spread stories suggesting that the virus was quietly raging throughout the country, with one report by the US National Endowment for Democracy-sponsored Daily NK online newspaper claiming that as many as 200 soldiers had already died, and that another 4,000 people were in quarantine. These claims, citing anonymous sources, were never verified, but have been spread widely by English-language media.
North Korea, which is thought to have successfully weathered both the SARS and Ebola outbreaks in 2003 and 2014, became one of the first countries in the world to mount a nation-wide emergency response to COVID-19 amid rising infection rates in neighbouring China, South Korea and Japan.
These measures included a ban on all foreign tourists in late January, quarantine for travellers from China exhibiting potential symptoms of the virus in Sinuiju in the country’s west, and the declaration of a “state emergency” to deal with the epidemic on January 30, including the creation of a special ‘Central Emergency Anti-Epidemic Headquarters’.
North Korea’s presumed infection rate stands in sharp contrast to those of its neighbours, with China, where the virus originated, reporting over 81,000 cases, including some 218 cases in the North-Korea neighbouring regions of Liaoning and Jilin. South Korea has 8,320 confirmed cases. Japan has reported 833 cases. Russia, meanwhile, has 93 confirmed cases.
‘Reciprocal measures’: Beijing tells NYT, WSJ, WaPo journalists to hand in credentials as US-China media war rolls on
RT | March 17, 2020
China is pulling the press credentials of US journalists from outlets including the New York Times and the Washington Post whose passes expire in 2020, in the latest move of an ongoing tit-for-tat with America over media access.
In a statement about China’s “countermeasures against US suppression of Chinese media organizations in the United States,” Beijing announced that American reporters working for the NYT, Wall Street Journal, Voice of America, Time and the Washington Post whose credentials are due to expire by the end of this year must hand them over within 10 days.
These reporters will also not be allowed to work in China – including Hong Kong and Macau – in the future, and other US journalists will face new visa restrictions similar to those Washington recently introduced for Chinese reporters.
“In view of the US’ discriminatory restrictions on visas, administrative review, and interviews of Chinese journalists, China will take reciprocal measures against US journalists,” it added.
The back-and-forth expulsions of journalists started in February, when Chinese authorities gave three Wall Street Journalists five days to leave the country after Beijing objected to an opinion piece in the outlet calling China the “real sick man of Asia.” The paper refused to apologize for the piece.
Shortly afterwards, the US dramatically reduced the number of journalists it would permit to work for four Chinese state-owned media companies inside the US, cutting the number allowed from 160 to 100. They also reduced the length of time those permitted entry could remain in the US.
Beijing condemned the move as reflecting a “Cold War mindset” and warned of retaliation.
Featured Video
Weaponized Journalism: 2021 Sayer Ji Interview with NPR
or go to
Aletho News Archives – Video-Images
From the Archives
How Rothschild Banking Clan Uses Its Vast Wealth to Influence World Events and Control Governments
By Ilya Tsukanov – Sputnik – 15.09.2024
How powerful is the Rothschild banking family? How did they amass their fortune? Just how rich are they? Do they secretly control the world? Sputnik explores. … continue
Blog Roll
 Aletho News
- London tourism expo promotes Israeli agency linked to theft of Palestinian land
- Dockworkers launch global strike against Israeli and US military shipments
- Europe facing gas price shock – Gazprom chief
- Ukraine continues recruiting people with disabilities
- Weaponized Journalism: 2021 Sayer Ji Interview with NPR
- Beyond Netanyahu: what Israel’s election means for Palestinians
- Lithuania plans universal conscription
- Lies, Damn Lies, and Ukraine News
- Financial Times rejects Nordic demands to correct Putin call story – media
- The Case for Less Unity in Europe
- If Americans Knew
- An error has occurred; the feed is probably down. Try again later.
- No Tricks Zone
- Germany’s Green Energy Transition Becoming Increasingly Expensive…Another 6 Trillion Euros!
- Sudden Stratospheric Warming, Powerful El Niño Combination May Lead To Extreme Europe Cold, Energy Crisis!
- Two New Studies Find Thwaites Glacier Melt Cannot Be Driven By Human Activity Or A Warming Ocean
- E-Cars Reduce CO2 Emissions By Only 41% Compared To Internal Combustion Engine Vehicles
- Predictions Made By Renowned Climate Professor Over Past Decades Have Been Proven To Be Poor
- New Study Suggests Large Regions Of The Pacific Ocean Have Been Cooling For The Last 80 Years
- Germany’s Green Energy Debacle: High Energy Costs Force Kahla Porzellan to Close After 182 Years!
- New Study: 50 Years Of The Most Aggressive ‘Net Zero’ Policies Can Only Affect The Global Climate By 0.03°C
- US September “Heat” Was No Record…Many Records Set Decades Ago
- Latest European Green Energy Debacle; Portugal’s Largest Flagship Solar Park Insolvent!

