American Pravda: How the CIA Invented “Conspiracy Theories”
BY RON UNZ • UNZ REVIEW • SEPTEMBER 5, 2016
A year or two ago, I saw the much-touted science fiction film Interstellar, and although the plot wasn’t any good, one early scene was quite amusing. For various reasons, the American government of the future claimed that our Moon Landings of the late 1960s had been faked, a trick aimed at winning the Cold War by bankrupting Russia into fruitless space efforts of its own. This inversion of historical reality was accepted as true by nearly everyone, and those few people who claimed that Neil Armstrong had indeed set foot on the Moon were universally ridiculed as “crazy conspiracy theorists.” This seems a realistic portrayal of human nature to me.
Obviously, a large fraction of everything described by our government leaders or presented in the pages of our most respectable newspapers—from the 9/11 attacks to the most insignificant local case of petty urban corruption—could objectively be categorized as a “conspiracy theory” but such words are never applied. Instead, use of that highly loaded phrase is reserved for those theories, whether plausible or fanciful, that do not possess the endorsement stamp of establishmentarian approval.
Put another way, there are good “conspiracy theories” and bad “conspiracy theories,” with the former being the ones promoted by pundits on mainstream television shows and hence never described as such. I’ve sometimes joked with people that if ownership and control of our television stations and other major media outlets suddenly changed, the new information regime would require only a few weeks of concerted effort to totally invert all of our most famous “conspiracy theories” in the minds of the gullible American public. The notion that nineteen Arabs armed with box-cutters hijacked several jetliners, easily evaded our NORAD air defenses, and reduced several landmark buildings to rubble would soon be universally ridiculed as the most preposterous “conspiracy theory” ever to have gone straight from the comic books into the minds of the mentally ill, easily surpassing the absurd “lone gunman” theory of the JFK assassination.
Even without such changes in media control, huge shifts in American public beliefs have frequently occurred in the recent past, merely on the basis of implied association. In the initial weeks and months following the 2001 attacks, every American media organ was enlisted to denounce and vilify Osama Bin Laden, the purported Islamicist master-mind, as our greatest national enemy, with his bearded visage endlessly appearing on television and in print, soon becoming one of the most recognizable faces in the world. But as the Bush Administration and its key media allies prepared a war against Iraq, the images of the Burning Towers were instead regularly juxtaposed with mustachioed photos of dictator Saddam Hussein, Bin Laden’s arch-enemy. As a consequence, by the time we attacked Iraq in 2003, polls revealed that some 70% of the American public believed that Saddam was personally involved in the destruction of our World Trade Center. By that date I don’t doubt that many millions of patriotic but low-information Americans would have angrily denounced and vilified as a “crazy conspiracy theorist” anyone with the temerity to suggest that Saddam had not been behind 9/11, despite almost no one in authority having ever explicitly made such a fallacious claim.
 These factors of media manipulation were very much in my mind a couple of years ago when I stumbled across a short but fascinating book published by the University of Texas academic press. The author of Conspiracy Theory in America was Prof. Lance deHaven-Smith, a former president of the Florida Political Science Association.
Based on an important FOIA disclosure, the book’s headline revelation was that the CIA was very likely responsible for the widespread introduction of “conspiracy theory” as a term of political abuse, having orchestrated that development as a deliberate means of influencing public opinion.
During the mid-1960s there had been increasing public skepticism about the Warren Commission findings that a lone gunman, Lee Harvey Oswald, had been solely responsible for President Kennedy’s assassination, and growing suspicions that top-ranking American leaders had also been involved. So as a means of damage control, the CIA distributed a secret memo to all its field offices requesting that they enlist their media assets in efforts to ridicule and attack such critics as irrational supporters of “conspiracy theories.” Soon afterward, there suddenly appeared statements in the media making those exact points, with some of the wording, arguments, and patterns of usage closely matching those CIA guidelines. The result was a huge spike in the pejorative use of the phrase, which spread throughout the American media, with the residual impact continuing right down to the present day. Thus, there is considerable evidence in support of this particular “conspiracy theory” explaining the widespread appearance of attacks on “conspiracy theories” in the public media.
But although the CIA appears to have effectively manipulated public opinion in order to transform the phrase “conspiracy theory” into a powerful weapon of ideological combat, the author also describes how the necessary philosophical ground had actually been prepared a couple of decades earlier. Around the time of the Second World War, an important shift in political theory caused a huge decline in the respectability of any “conspiratorial” explanation of historical events.
For decades prior to that conflict, one of our most prominent scholars and public intellectuals had been historian Charles Beard, whose influential writings had heavily focused on the harmful role of various elite conspiracies in shaping American policy for the benefit of the few at the expense of the many, with his examples ranging from the earliest history of the United States down to the nation’s entry into WWI. Obviously, researchers never claimed that all major historical events had hidden causes, but it was widely accepted that some of them did, and attempting to investigate those possibilities was deemed a perfectly acceptable academic enterprise.
However, Beard was a strong opponent of American entry into the Second World War, and he was marginalized in the years that followed, even prior to his death in 1948. Many younger public intellectuals of a similar bent also suffered the same fate, or were even purged from respectability and denied any access to the mainstream media. At the same time, the totally contrary perspectives of two European political philosophers, Karl Popper and Leo Strauss, gradually gained ascendancy in American intellectual circles, and their ideas became dominant in public life.
Popper, the more widely influential, presented broad, largely theoretical objections to the very possibility of important conspiracies ever existing, suggesting that these would be implausibly difficult to implement given the fallibility of human agents; what might appear a conspiracy actually amounted to individual actors pursuing their narrow aims. Even more importantly, he regarded “conspiratorial beliefs” as an extremely dangerous social malady, a major contributing factor to the rise of Nazism and other deadly totalitarian ideologies. His own background as an individual of Jewish ancestry who had fled Austria in 1937 surely contributed to the depth of his feelings on these philosophical matters.
Meanwhile, Strauss, a founding figure in modern neo-conservative thought, was equally harsh in his attacks upon conspiracy analysis, but for polar-opposite reasons. In his mind, elite conspiracies were absolutely necessary and beneficial, a crucial social defense against anarchy or totalitarianism, but their effectiveness obviously depended upon keeping them hidden from the prying eyes of the ignorant masses. His main problem with “conspiracy theories” was not that they were always false, but they might often be true, and therefore their spread was potentially disruptive to the smooth functioning of society. So as a matter of self-defense, elites needed to actively suppress or otherwise undercut the unauthorized investigation of suspected conspiracies.
Even for most educated Americans, theorists such as Beard, Popper, and Strauss are probably no more than vague names mentioned in textbooks, and that was certainly true in my own case. But while the influence of Beard seems to have largely disappeared in elite circles, the same is hardly true of his rivals. Popper probably ranks as one of the founders of modern liberal thought, with an individual as politically influential as left-liberal financier George Soros claiming to be his intellectual disciple. Meanwhile, the neo-conservative thinkers who have totally dominated the Republican Party and the Conservative Movement for the last couple of decades often proudly trace their ideas back to Strauss.
So, through a mixture of Popperian and Straussian thinking, the traditional American tendency to regard elite conspiracies as a real but harmful aspect of our society was gradually stigmatized as either paranoid or politically dangerous, laying the conditions for its exclusion from respectable discourse.
By 1964, this intellectual revolution had largely been completed, as indicated by the overwhelmingly positive reaction to the famous article by political scientist Richard Hofstadter critiquing the so-called “paranoid style” in American politics, which he denounced as the underlying cause of widespread popular belief in implausible conspiracy theories. To a considerable extent, he seemed to be attacking straw men, recounting and ridiculing the most outlandish conspiratorial beliefs, while seeming to ignore the ones that had been proven correct. For example, he described how some of the more hysterical anti-Communists claimed that tens of thousands of Red Chinese troops were hidden in Mexico, preparing an attack on San Diego, while he failed to even acknowledge that for years Communist spies had indeed served near the very top of the U.S. government. Not even the most conspiratorially minded individual suggests that all alleged conspiracies are true, merely that some of them might be.
Most of these shifts in public sentiment occurred before I was born or when I was a very young child, and my own views were shaped by the rather conventional media narratives that I absorbed. Hence, for nearly my entire life, I always automatically dismissed all of the so-called “conspiracy theories” as ridiculous, never once even considering that any of them might possibly be true.
To the extent that I ever thought about the matter, my reasoning was simple and based on what seemed like good, solid common sense. Any conspiracy responsible for some important public event must surely have many separate “moving parts” to it, whether actors or actions taken, let us say numbering at least 100 or more. Now given the imperfect nature of all attempts at concealment, it would surely be impossible for all of these to be kept entirely hidden. So even if a conspiracy were initially 95% successful in remaining undetected, five major clues would still be left in plain sight for investigators to find. And once the buzzing cloud of journalists noticed these, such blatant evidence of conspiracy would certainly attract an additional swarm of energetic investigators, tracing those items back to their origins, with more pieces gradually being uncovered until the entire cover-up likely collapsed. Even if not all the crucial facts were ever determined, at least the simple conclusion that there had indeed been some sort of conspiracy would quickly become established.
However, there was a tacit assumption in my reasoning, one that I have since decided was entirely false. Obviously, many potential conspiracies either involve powerful governmental officials or situations in which their disclosure would represent a source of considerable embarrassment to such individuals. But I had always assumed that even if government failed in its investigatory role, the dedicated bloodhounds of the Fourth Estate would invariably come through, tirelessly seeking truth, ratings, and Pulitzers. However, once I gradually began realizing that the media was merely “Our American Pravda” and perhaps had been so for decades, I suddenly recognized the flaw in my logic. If those five—or ten or twenty or fifty—initial clues were simply ignored by the media, whether through laziness, incompetence, or much less venial sins, then there would be absolutely nothing to prevent successful conspiracies from taking place and remaining undetected, perhaps even the most blatant and careless ones.
In fact, I would extend this notion to a general principle. Substantial control of the media is almost always an absolute prerequisite for any successful conspiracy, the greater the degree of control the better. So when weighing the plausibility of any conspiracy, the first matter to investigate is who controls the local media and to what extent.
Let us consider a simple thought-experiment. For various reasons these days, the entire American media is extraordinarily hostile to Russia, certainly much more so than it ever was toward the Communist Soviet Union during the 1970s and 1980s. Hence I would argue that the likelihood of any large-scale Russian conspiracy taking place within the operative zone of those media organs is virtually nil. Indeed, we are constantly bombarded with stories of alleged Russian conspiracies that appear to be “false positives,” dire allegations seemingly having little factual basis or actually being totally ridiculous. Meanwhile, even the crudest sort of anti-Russian conspiracy might easily occur without receiving any serious mainstream media notice or investigation.
This argument may be more than purely hypothetical. A crucial turning point in America’s renewed Cold War against Russia was the passage of the 2012 Magnitsky Act by Congress, punitively targeting various supposedly corrupt Russian officials for their alleged involvement in the illegal persecution and death of an employee of Bill Browder, an American hedge-fund manager with large Russian holdings. However, there’s actually quite a bit of evidence that it was Browder himself who was actually the mastermind and beneficiary of the gigantic corruption scheme, while his employee was planning to testify against him and was therefore fearful of his life for that reason. Naturally, the American media has provided scarcely a single mention of these remarkable revelations regarding what might amount to a gigantic Magnitsky Hoax of geopolitical significance.
To some extent the creation of the Internet and the vast proliferation of alternative media outlets, including my own small webzine, have somewhat altered this depressing picture. So it is hardly surprising that a very substantial fraction of the discussion dominating these Samizdat-like publications concerns exactly those subjects regularly condemned as “crazy conspiracy theories” by our mainstream media organs. Such unfiltered speculation must surely be a source of considerable irritation and worry to government officials who have long relied upon the complicity of their tame media organs to allow their serious misdeeds to pass unnoticed and unpunished. Indeed, several years ago a senior Obama Administration official argued that the free discussion of various “conspiracy theories” on the Internet was so potentially harmful that government agents should be recruited to “cognitively infiltrate” and disrupt them, essentially proposing a high-tech version of the highly controversial Cointelpro operations undertaken by J. Edgar Hoover’s FBI.
Until just a few years ago I’d scarcely even heard of Charles Beard, once ranked among the towering figures of 20th century American intellectual life. But the more I’ve discovered the number of serious crimes and disasters that have completely escaped substantial media scrutiny, the more I wonder what other matters may still remain hidden. So perhaps Beard was correct all along in recognizing the respectability of “conspiracy theories,” and we should return to his traditional American way of thinking, notwithstanding endless conspiratorial propaganda campaigns by the CIA and others to persuade us that we should dismiss such notions without any serious consideration.
For Further Reading:
Netanyahu to dispatch Mossad chief to meet Biden & outline Israel’s demands for Iran nuclear deal overhaul
RT | January 24, 2021
Mossad chief Yossi Cohen may become the first top Israeli official to meet new US president Joe Biden amid concerns in Tel Aviv that his administration is set to revive the Obama-era international nuclear pact with Iran.
The head of Israeli secret service and one of PM Benjamin Netanyahu’s most trusted allies, Cohen, is heading to Washington sometime next month to brief the Biden administration on a set of terms regarding any potential nuclear deal with Tehran, Channel 12 reported on Saturday, citing “communications” between Israel and the new US administration.
Cohen is also expected to meet with the CIA chief and once again present an intelligence assessment of Iran’s nuclear program, which according to Israelis is secretly aimed at obtaining nukes.
Cohen’s team is reportedly set to demand a “radical overhaul” of the agreement, far more strict for Tehran, including a full halt of uranium enrichment and production of advanced centrifuges. On top of that, Israel wants Iran to stop “supporting terror groups” and “end its military presence in Iraq, Syria and Yemen.”
Iran’s president this week reiterated his country’s willingness to return to the terms of deal, but said it’s up to the Biden administration to make the necessary concessions. Cohen’s team is reportedly set to demand a “radical overhaul” of the agreement, with far more strict commitments from Tehran.
The Joint Comprehensive Plan of Action (JCPOA) was signed between Iran and the six major global powers in 2015 and put constraints on Tehran’s nuclear ambitions [the Western signatories never honored their commitments since 2015]. Israel lobbied the Obama administration hard against joining the JCPOA, and once Donald Trump took office, continued this effort, this time succeeding in getting Trump to withdraw and reintroduce crippling sanctions against Iran.
Since then, amid ever-escalating tensions with the US while criticizing other JCPOA signatories for their failure to bring Washington to its senses, Tehran chose to gradually renege on their side of the deal too.
In January, Iran began enriching uranium to 20 percent, drifting further away from the parameters of the deal. While higher than the 3.67 percent level agreed in the 2015 pact, the new figure is still below the 90 percent level that is considered weapons-grade.
Iran has also issued a symbolic ultimatum, with an Iranian spokesperson stating that the Biden administration will have one month, until February 21 to reverse sanctions. The director general of the International Atomic Energy Agency, which is tasked with monitoring Iran’s compliance, warned that time is running out with “only weeks left” to save JCPOA.
President Biden’s New Administration, Old Aggression
Strategic Culture Foundation | January 22, 2021
The day after President Joe Biden’s inauguration this week the White House announced that it was seeking a five-year extension of the New START treaty with Russia. The treaty was set to expire on February 4 after a 10-year run. Russia in recent months repeatedly urged the United States to renew the accord, which the former Trump administration had ignored.
Therefore, the new administration’s willingness to save New START is welcome. (But it is not clear cut, as explained below.) If the treaty had expired, there was a grave risk of relapse into a nuclear arms race. Given that the U.S. has already pulled out of several arms controls treaties, it is of paramount importance to maintain the last remaining pact, which specifically limits the bilateral arsenal of intercontinental warheads.
In announcing the Biden administration’s decision on extending New START, Pentagon spokesman John Kirby stated: “Just as we engage Russia in ways that advance American interests, we in the Department will remain clear-eyed about the challenges Russia poses and committed to defending the nation against their reckless and adversarial actions.” (Our emphasis.)
White House spokeswoman Jan Psaki articulated a similar testy rationale, saying that despite the extension proposal the Biden administration would hold Russia to “account for reckless and adversarial actions”. (Our emphasis.)
Please note the casual assertion of provocative claims as if they are proven facts. And this, ironically, from a new administration that has piously proclaimed to bring “facts” to public announcements in place of the Trumpian habit of peddling falsehoods and “alternate facts”.
It was then announced that President Biden has ordered his top intelligence officers to carry out a review into allegations of Russian malign conduct. In particular, allegations of a massive cyber attack – the so-called SolarWinds hack – on American government departments and commerce; the alleged poison assassination of Russian dissident figure Alexei Navalny; allegations of Russian interference in the 2020 presidential election; and, lastly, the allegations of Russian military intelligence running bounty-hunter plots in Afghanistan to murder U.S. soldiers. (We can be sure the conclusions are already foregone, only awaiting new media spin.)
Curiously though, the allegation of Russian interference in the 2020 election seems to be a new one for the archive of outlandish anti-Russian accusations. It is not clear what it refers to specifically. Earlier this week, Biden’s Democratic allies House Speaker Nancy Pelosi and former presidential candidate Hillary Clinton made ludicrous assertions that Russian President Vladimir Putin may have helped Donald Trump in trying to overthrow the electoral process with the violent assault on the Capitol by Trump supporters on January 6.
In any case, Russia has refuted all these absurd allegations as “baseless” and without evidence. This charade of accusing Russia has been intensifying since the 2016 election when Trump was elected. It now looks set to continue under the Biden presidency. Kremlin spokesman Dmitry Peskov says such fables betray a Cold War mentality of Russophobia which seems to be endemic in the American political establishment.
So Biden’s proposed extension of New START is not the offer of an olive branch to Russia, as it may first appear. It is being done with a cold hand of raw self-interest and in a wider context of continuing and intensifying antagonism towards Russia.
Indeed, in reporting the move on the nuclear pact, the New York Times quoted Biden aides saying that the new administration had no interest in establishing a “reset” in American relations with Russia.
This week also revealed other indications of aggressive mindset in the new administration. During confirmation hearings in the Senate for Biden’s Cabinet and national security team, the recurring theme was how the United States would stand up to purported adversaries. Russia, China and Iran were chief among the targets for American power interest, all described in pejorative terms as enemies.
Avril Haines was confirmed as Director of National Intelligence. Ridiculously, she declared that she would “speak truth to power” and ensure that “intelligence would not be politicized”. This is the same Avril Haines who helped mastermind drone assassinations while formerly serving as deputy director of the CIA and who this week vowed to take a more aggressive stance towards China. Antony Blinken and Lloyd Austin are set to become Secretaries of State and Defense. Other members of the Biden team, Victoria Nuland, Wendy Sherman and William Burns (who is to head the CIA) are also alumni of the past Obama administrations (2008-2016) in which Biden himself served as vice president.
All of them are indelibly complicit in propagating illegal wars, regime-change operations and the disastrous 2014 coup d’état in the Ukraine. In fact, Blinken during his Senate hearings this week affirmed that he is in favor of increasing lethal U.S. military supplies to Ukraine.
Joe Biden has a long and sordid record as a former Senator of supporting dozens of U.S. wars and aggressions, going back to the bloody invasions of Grenada in 1983 and Panama in 1989 and the bombing of former Yugoslavia in 1999, among others. But it was his pivotal support for the U.S. war on Iraq in 2003 which marks his most vile act as a warmonger and surrogate for American imperialism.
Biden has indulged the Russophobic fantasies of “Russiagate”, alleging collusion between the Kremlin and former president Trump, which have poisoned U.S.-Russia relations. Biden has even resorted to cheap ad hominem attacks on Putin calling the Russian leader a “thug”. How rich is that for someone who caused over one million deaths in his sponsorship of one war alone in Iraq, never mind dozens of others.
Alas, unfortunately, what we are seeing in Washington is a new administration with old aggression.
The cognitive dissonance afflicting America is something to behold. U.S. media this week were swooning over the inauguration of Democrat President Joe Biden as a “return to normal” after four years of turmoil under Donald Trump. The “adults have returned” goes the saying among pundits. More accurately, that should be the adult psychopaths and imperialist warmongers have returned.
In other matters, Biden announced a “war-time effort” to control the coronavirus pandemic which has devastated the United States. The American death toll from the disease [allegedly] stands at over 400,000 as of this week and is set to reach half a million by next month. The U.S. has the biggest [contrived] death toll in the world, accounting for 20 per cent of all Covid-19 deaths. Concurrent with the U.S. public health crisis is an economic crisis of poverty, unemployment, homelessness and inequality. It makes you wonder how it is that the Biden administration can devote so much interest on “foreign enemies” amid such catastrophe at home.
One dubious blessing perhaps is that United States will be so preoccupied with salvaging its own domestic woes that its warmongering politicians might not have the stomach nor nerve for overseas adventurism and wars. Although, don’t bet on it.
‘Sanctions guru’ involved in creating Russiagate saga to return as CIA’s deputy director under Biden
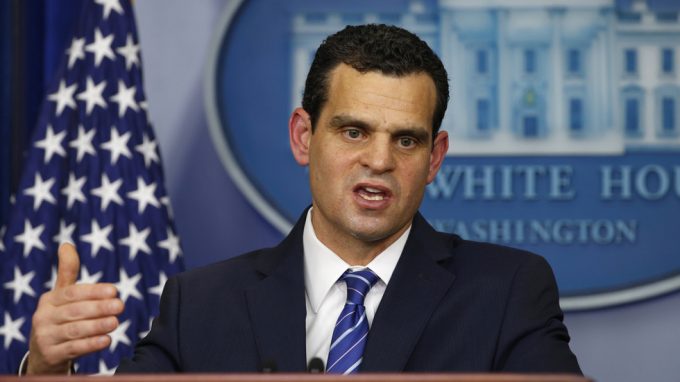
David Cohen in 2014. ©REUTERS / Kevin Lamarque
RT | January 15, 2021
Joe Biden’s transition team has picked David Cohen, the former deputy director of the CIA, to reprise his role and help smooth things out for his future boss, career diplomat and intelligence outsider William Burns.
Cohen was considered a frontrunner to become CIA director himself, but Biden chose Burns instead. Cohen’s return to the office he held between 2015 and 2017 was announced on Friday, and since his candidacy does not require a Senate confirmation, he will be able to start on inauguration day.
As deputy for then-CIA Director John Brennan, Cohen was involved in creating the infamous US intelligence assessment of alleged Russian interference in the 2016 election. The document was widely touted as a consensus opinion of 17 agencies, but later turned out to be a product of officials from only three of them – the CIA, FBI, and NSA – “hand-picked” for the task by then-Director of National Intelligence James Clapper (technically, his office is an agency of its own and could be counted as the fourth one vouching for the document).
The assessment, which was released in the final days of the Obama administration, claimed that Russia ran a sophisticated interference and influence campaign to help Donald Trump beat Hillary Clinton in the 2016 presidential election. It primed the US public for the sequel theory that accused the Trump campaign of “colluding” with the Kremlin, setting the tone for the entire presidency of the Republican winner. Russia denied any involvement in the election and said it was used as a scapegoat in US partisan fights.
In 2017, Cohen famously rebuked then-CIA Director Mike Pompeo, when he claimed the US intelligence community believed the outcome of the election was not affected by the purported Russian campaign. In fact, the scope of the report was not wide enough to make such an assessment.
Interestingly, after going private, Cohen worked at WilmerHale, a law firm that also employs Robert Mueller, the former FBI director and special counsel who investigated the Russiagate allegations and found no evidence of collusion. He also spent time as a national security contributor at NBC News, rubbing shoulders then with his ex-boss, Brennan.
Cohen is said to be respected and loved in the intelligence community. Brennan called him “a great listener” and “an ardent supporter and defender of the agency.”
Before becoming the second most senior official in the CIA, Cohen worked in the US Treasury, specializing in tracing financial streams and enforcing US economic sanctions, which won him the nickname “sanctions guru.” Early in his government career under George W. Bush, he was credited for his contribution to writing the section of the Patriot Act that deals with money laundering and financing of terrorism.
Silicon Valley and WEF-Backed Foundation Announce Global Initiative for COVID-19 Vaccine Records

Multiple airlines are now testing a digital health passport, called CommonPass, that will store health information needed for travel on a secure, easy-to-update app. The Commons Project
By Whitney Webb |
Unlimited Hangout| January 15, 2021
Silicon Valley’s most influential companies, alongside healthcare companies, US intelligence contractors and the Commons Project Foundation, recently launched the Vaccination Credential Initiative. The initiative’s ambitions reach far beyond vaccines and will have major implications for civil liberties.
On Thursday, tech giants with deep ties to the US national-security state—Microsoft, Oracle, and the MITRE corporation—announced that they had partnered with several health-care companies to create the Vaccination Credential Initiative (VCI) to advance the implementation of digital COVID-19 vaccination records.
According to a Reuters report, the VCI “aims to help people get encrypted digital copies of their immunization records stored in a digital wallet of their choice” because the “current system [of vaccination records] does not readily support convenient access and sharing of verifiable vaccination records.”
The initiative, on its website, notes that the VCI is a public-private partnership “committed to empowering individuals with digital vaccination records” so that participants can “protect and improve their health” and “demonstrate their health status to safely return to travel, work, school and life while protecting their data privacy.” The initiative is essentially built on a common framework of digital vaccination “wallets” called SMART Health Cards that are meant to “work across organizational and jurisdictional boundaries” as part of a new global vaccination-record infrastructure.
The host of the VCI website and one the initiative’s key backers is the Commons Project Foundation. That foundation, in partnership with the World Economic Forum (WEF), runs the Common Trust Network, which has three goals that are analogous to those of VCI. As listed on the WEF website, the network’s goals are (1) to empower individuals by providing digital access to their health information; (2) to make it easier for individuals to understand and comply with each destination’s requirements; and (3) to help ensure that only verifiable lab results and vaccination records from trusted sources are presented for the purposes of cross-border travel and commerce.
To advance these goals, the Common Trust Network is powered by “a global registry of trusted laboratory and vaccination data sources” as well as “standard formats for lab results and vaccination records and standard tools to make those results and records digitally accessible.”

How CommonPass works, thecommonsproject.org
Another, and related, Commons Project Foundation and WEF partnership is CommonPass. CommonPass, which is also supported by the Rockefeller Foundation, is both a framework and an app that “will allow individuals to access their lab results and vaccination records, and consent to have that information used to validate their COVID status without revealing any other underlying personal health information.” Current members of CommonPass, including JetBlue, Lufthansa, Swiss International Airlines, United Airlines, and Virgin Atlantic, are also members of the Common Trust Network.
This overlap between the Commons Project Foundation/WEF partnerships and the VCI illustrates that the WEF itself is involved with the VCI, albeit indirectly through their partners at the Commons Project Foundation. The Commons Project Foundation itself is worth exploring, as its cofounders, Paul Meyer and Bradley Perkins, have long-standing ties to the RAND Corporation, the US’ Centers for Disease Control and Prevention, and the International Rescue Committee, as noted in this article published last year by MintPress News. The IRC, currently run by Tony Blair protégé David Milliband, is developing a biometric ID and vaccination-record system for refugees in Myanmar in cooperation with the ID2020 Alliance, which is partnered with CommonPass backer, the Rockefeller Foundation. In addition, the ID2020 Alliance funds the Commons Project Foundation and is also backed by Microsoft, one of the key companies behind the VCI.
Wearable IDs for your Health and your Wallet
Overlap between digital vaccination records, promoted via initiatives such as CommonPass and VCI, and the push for a new global digital-identity system is no coincidence. Indeed, the developer of VCI’s SMART Health Cards framework at Microsoft Health, Josh C. Mandel, noted in his overview presentation on that framework that digital identity is integral to the digital vaccination-record effort. SMART Health Cards, as of now, are expected to include a person’s complete name, gender, birth date, mobile phone number, and email address in addition to vaccination information, though it is possible and likely that more personal information will be required as the initiative advances, given that VCI states that these identifiers are merely a starting point.
While advertised as digital vaccination records, SMART Health Cards are clearly intended to be used for much more. For instance, public information on the framework notes that SMART Health Cards are “building blocks that can be used across health care,” including managing a complete immunization record that goes far beyond COVID-19 vaccines, sharing data with public-health agencies, and communication with health-care providers.

Vaccine Credential Initiative partners, vaccinationcredential.org
Yet, this framework will not be limited to health-care information, as Mandel has said. In his presentation, he notes the application of SMART Health Cards could soon be used as IDs for commercial activity, such as renting a car. The VCI framework’s use of the term “digital wallet” to refer to its digital vaccination record is also suggestive of future connectivity to economic activity. Efforts to link digital identity, not just to economic activity but also to health data, have recently escalated, for example with the piloting of Gavi, the Vaccine Alliance (aka GAVI)–Mastercard–Trust Stamp partnership in Africa. That program, first launched in 2018, links Trust Stamp’s digital-identity platform with the GAVI-Mastercard Wellness Pass, a digital vaccination record, and Mastercard’s click-to-pay system run on AI technology called NuData. Mastercard and GAVI are both partnered with the ID2020 Alliance, which includes VCI member Microsoft.
Given the reasonable speculation that such platforms would utilize digital currency, specifically cryptocurrency, for financial activity, it is worth noting that VCI member Microsoft filed a patent in 2019 that would allow “human body activity,” including brain waves and body heat, to mine (i.e., generate) cryptocurrency. This, of course, would link biometrics to financial activity, among other things.
Such a system, as laid out in the Microsoft patent, would likely require the introduction of wearables in order to be implemented. Notably, numerous wearables for contactless identity, digital travel passes, and payment devices have recently been launched. Examples include DigitalDNA, Proxy, and FlyWallet. FlyWallet is particularly notable as their latest product, Keyble, is a wearable that combines digital identity through fingerprint authentication, which enables both contactless payments and health applications, such as vital-sign monitoring and data sharing with insurance companies and health-care providers.
Sponsored by Spooks and Silicon Valley
The SMART Health Cards framework was developed by a team led by the chief architect of Microsoft Healthcare, Josh Mandel, who was previously the Health IT Ecosystem lead for Verily, formerly Google Life Sciences. Verily is currently heavily involved in COVID-19 testing throughout the United States, particularly in California, and links test recipients’ results to their Google accounts. Their other COVID-19 initiatives have been criticized due to still-unresolved privacy concerns, something that has also plagued several of Verily’s other efforts pre-COVID-19, including those involving Mandel.
Of particular concern is that Verily, and by extension Google, created Project Baseline, which has been collecting “actionable genetic information” with a focus on “population health” from participants since 2017. Yet, during the COVID-19 process, Project Baseline has become an important component of Verily’s COVID-19 testing efforts, raising the unsettling possibility that Verily has been obtaining Americans’ DNA data through its COVID-19 testing activities. While Verily has not addressed this possibility directly, it is worth noting that Google has been heavily involved in amassing genomic data for several years. For instance, in 2013, Google Genomics was founded with the goal of storing and analyzing DNA data on Google Cloud servers. Now known as Cloud Life Sciences, the Google subsidiary has since developed AI algorithms that can “build your genome sequence” and “identify all the mutations that an individual inherits from their parents.”
Google also has close ties with the best-known DNA testing companies in the United States, such as Ancestry.com. Ancestry, recently purchased by private-equity behemoth Blackstone, shares data with a secretive Google subsidiary that uses genomic data to develop lifespan-extending therapies. In addition, the wife of Google cofounder Sergey Brin, Anne Wojcicki, is the cofounder and CEO of DNA testing company 23andMe. Wojcicki is also the sister of the CEO of Google-owned YouTube, Susan Wojcicki.
Google and the majority of VCI’s backers—Microsoft, Salesforce, Cerner, Epic, the Mayo Clinic, and MITRE Corporation, Change Healthcare—are also prominent members of the MITRE-run COVID-19 Healthcare Coalition. Other members of that coalition include the CIA’s In-Q-Tel and the CIA-linked data-mining firm Palantir, as well as a myriad of health-care and health-record companies. The coalition fits well with the ambitions of Google and like-minded companies that have sought to gain access to troves of American health data under the guise of combatting COVID-19.
The COVID-19 Healthcare Coalition describes itself as a public-private partnership that has enabled “the critical infrastructure to enable collaboration and shared analytics” on COVID-19 through the sharing of health-care and COVID-19 data among members. That this coalition and VCI are intimately involved with MITRE Corporation is significant, given that MITRE is a well-known, yet secretive, contractor for the US government, specifically the CIA and other intelligence agencies, which has developed Orwellian surveillance and biometric technologies, including several now focused on COVID-19.
Just three days before the public announcement of VCI’s establishment, Microsoft Healthcare and Google’s Verily announced a partnership along with MIT and Harvard’s Broad Institute to share the companies’ cloud data and AI technologies with a “global network of more than 168,000 health and life sciences partners” to accelerate the Terra platform. Terra, originally developed by the Broad Institute and Verily, is an “open data ecosystem” focused on biomedical research, specifically the fields of cancer genomics, population genetics, and viral genomics. The biomedical data Terra amasses includes not only genetic data but also medical-imaging, biometric signals, and electronic health records. Google, through its partnership with the Pentagon, which was announced last September, has moved to utilize the analysis of such data in order to “predictively diagnose” diseases such as cancer and COVID-19. US military contractors, such as Advanced Technology International (ATI), have been developing wearables that would apply that AI-driven predictive diagnosis technology to COVID-19 diagnoses.
Predictive COVID-19 diagnosis is also an ambition of another company that backs VCI, Salesforce. Salesforce is one of three companies that created COVID 360, which Salesforce senior vice president Bob Vanstraelen describes as a “free full Coronavirus treatment solution for patients and citizens at risk” that is hosted on Salesforce Health Cloud and was by Deloitte’s Israel branch and the Israeli intelligence-linked AI firm Diagnostic Robotics. COVID 360 uses the Diagnostic Robotics clinical-predictions platform and applies it to COVID-19 so that “government agencies or caretakers” can identify individuals “in proximity to a potential positive coronavirus case” and mandate coronavirus testing and/or treatment regimes, based on a risk profile generated by COVID 360. Diagnostic Robotics and Salesforce are both members of the MITRE-run COVID-19 Healthcare Coalition.
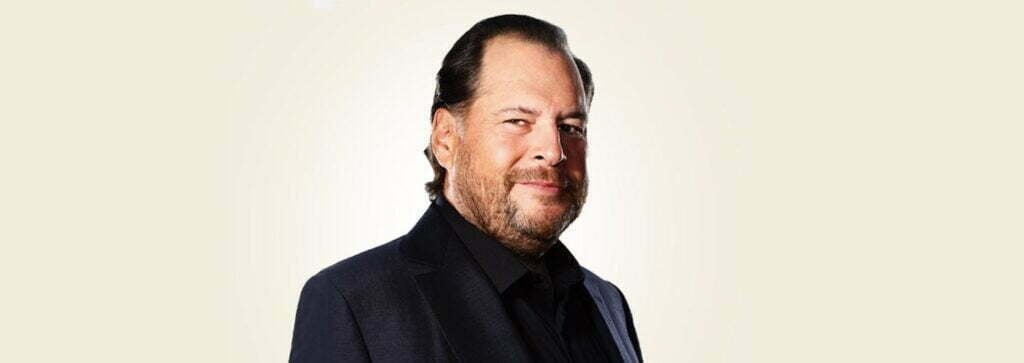 Salesforce founder and CEO Marc Benioff, inclusivecapitalism.com
Salesforce founder, chair, and CEO Marc Benioff was previously a vice president at Oracle. Oracle, another VCI backer, was created as a spin-off of a CIA project of the same name, and its top executives have close ties to the outgoing Trump administration and also to Israel’s government. While Benioff’s pre-Salesforce history to a CIA-linked company like Oracle is significant, Benioff’s close ties to the World Economic Forum also deserve greater scrutiny.
Benioff is not only a member of the WEF’s board of trustees, but he is also the inaugural chair of the forum’s Centre for the Fourth Industrial Revolution, a “revolution” that its architect and WEF founder Klaus Schwab defines as a merging of humans’ physical, digital, and biological identities. Benioff is also the owner and cochair of Time magazine, which recently ran an entire issue focused on promoting the Fourth Industrial Revolution and the WEF-backed Great Reset.
Benioff also serves on the Council for Inclusive Capitalism, a collaboration between the Vatican and oligarchs to create a “more inclusive, sustainable and trusted economic system” for the twenty-first century. Alongside Benioff on the council are well-known figures such as Lynn Forester de Rothschild (close associate of Jeffrey Epstein and the Clintons), Mark Carney (UN special envoy for Climate Action and former Governor of the Bank of England), and William Lauder (executive chairman of Estée Lauder, nephew of Mega Group member Ronald Lauder) as well as the top executives of MasterCard, Visa, Dupont, Merck, Johnson & Johnson, BP, and Bank of America. Also present are the heads of the Ford and Rockefeller Foundations.
Benioff and others mentioned in this article are perfect examples of the cross-pollination between groups of oligarchs and their associated foundation and organizations and how these networks are working together to pursue a common agenda. While the push for combining digital identity with vaccination records and economic activity appears, superficially, to be the efforts of various organizations and groups, the same individuals and entities appear time and again, pointing to a coordinated push to not only implement such a system, but manufacture consent for such a system among the global population.
The effort to manufacture consent for an all-encompassing digital identification system is notable given that its main “selling point” thus far has been coercion. We have been told that such a system is necessary, or we will never be able to return to work or school, we will never be able to travel and we will be prohibited from participating normally in the economy. While this system is being introduced in this way, it is essential to point out that coercion is a built-in part of this infrastructure and will be used to modify human behavior to great effect, reaching far beyond just the issue of COVID-19 vaccines if implemented.
Whitney Webb has been a professional writer, researcher and journalist since 2016. She has written for several websites and, from 2017 to 2020, was a staff writer and senior investigative reporter for Mint Press News. She currently writes for The Last American Vagabond.
Felony Murder and Gen. Rene Schneider
By Jacob G. Hornberger | FFF | January 14, 2021
 Some legal experts are speculating about the possibility that people who participated in the January 6 Capitol melee could be charged with murdering Capitol police officer Brian Sicknick, even though they did not participate in his killing. The felony-murder rule holds that if a person is involved in the commission of a felony in a conspiracy with others, he can be charged with murder even though others in the conspiracy did the killing.
When I read that, I immediately thought about the kidnapping and murder of Chilean General Rene Schneider, who was killed in 1970. In fact, it’s interesting that while the members of Congress and the mainstream press express shock and outrage over recent events in the Capitol, they have long been non-plussed by the shocking and outrageous violence that U.S. government officials instigated and in which they participated in 1970.
Schneider was the overall commander of Chile’s armed forces. He was a man of deep integrity, had a family, and believed that it was the duty of the military to support and defend the constitution of the country.
In the 1970 presidential election, the Chilean people delivered a plurality of votes to a man named Salvador Allende, who U.S. officials reviled because he was a socialist. Like President Kennedy ten years before, Allende was interested in establishing friendly relations with the communist world, including the Soviet Union and Cuba, two official Cold War enemies of the U.S. national-security establishment. Keep in mind that in 1970, the Cold War was still continuing and that the communists were defeating U.S. military and CIA forces in the Vietnam War.
U.S. officials determined that Allende posed a grave threat to “national security” — not only the “national security” of the United States but also the “national security” of Chile. They decided to prevent his accession to the presidency, either through bribes to the Chilean congress or through a U.S.-supported coup that would install a right-wing military dictatorship in the country.
There was one big obstacle to a coup: Gen. Rene Schneider.
The Chilean constitution provided for only two ways to remove a duly elected president from office: by impeachment (and conviction) or through the next election. The Chilean constitution did not provide for a coup as a third way to remove a president from office.
The Chilean congress had been unable to secure enough votes to remove Allende from office through impeachment. That left the next election, which would have meant that Allende would stay in office for the next 6 years.
Schneider’s position was very simple: Since the Constitution did not provide for a coup to remove the president, the military could not act to remove him.
The U.S. national-security establishment’s position was different: While it too favored supporting and defending the U.S. Constitution, it held that there was an implicit exception to the rule, which was: Whenever a country’s president is determined to be a grave threat to the “national security” of his own country, it becomes the the moral duty of the national-security establishment to protect “national security” by removing the president from office. (As I point out in an upcoming article in FFF’s monthly journal Future of Freedom, this mindset has clear ramifications in the Kennedy assassination, which occurred ten years prior to Allende’s election.)
In order to achieve the coup, it was necessary to remove Schneider as an obstacle. Thus, U.S. officials within the CIA and other parts of the U.S. government entered into a conspiracy to kidnap Schneider.
Now, before a go further, I know what some of you are thinking: “Conspiracy theory, Jacob! Conspiracy theory! There is no way that officials of the U.S. government would ever conspire to violently kidnap an innocent man! It’s outrageous that you would even suggest such a thing about our government!”
But the fact is that that this conspiracy did in fact occur, notwithstanding the fervent mindset that some might have to deny its existence. The CIA secretly hired the kidnappers, paid them money, including hush money after the fact, and even smuggled high-powered weapons into the country, which they gave to their Chilean co-conspirators.
When the kidnappers attempted to kidnap Schneider on the streets of Santiago, he was armed and fought back. The kidnappers shot him and Schneider died three days later from his wounds.
The CIA claimed that it never intended to murder Schneider. It said that it just wanted to kidnap him. However, that claim has the word “lie” written all over it. After all, what could they have done with him after kidnapping him? They couldn’t return him, given that would have restored him as the obstacle to the coup. Moreover, if they returned him, he might have been able to lead law-enforcement personnel to the kidnappers and ultimately to the CIA. Thus, it is a virtual certainty that Schneider would have been killed by one of the kidnappers and that the CIA would have dutifully expressed shock.
Nonetheless, enter the felony-murder rule. Kidnapping is a felony. So is conspiracy to kidnap. Under the felony-murder rule, the U.S. conspirators were as responsible for Schneider’s murders as the actual killers.
The CIA and other U.S. officials who participated in the conspiracy tried desperately to keep their involvement in the conspiracy secret. People who suspected their complicity in the plot were undoubtedly labeled “conspiracy theorists.” But investigators in the private sector kept pushing and ultimately the truth came out: The CIA and other U.S. officials had participated in a felony, with the conspiracy taking place in both Virginia and Washington, D.C.
Nonetheless, the Justice Department has never charged any of the conspirators with kidnapping or murder or conspiracy to commit kidnapping and murder. Keep in mind that there is no statute of limitations for murder. But even if a federal grand jury were to return a criminal indictment, it is a virtual certainty that the federal judiciary would immediately dismiss it on grounds of “national security.”
It’s probably worth mentioning that when the family of Rene Schneider sued in federal district court for Schneider’s wrongful death, the federal courts threw them out on their ears, without even permitting them to take depositions that could have determined the full extent of the conspiracy. When it comes to extraordinary measures to protect “national security,” including kidnapping and assassination, secrecy in a national-security state is always paramount.
But that’s the nature of any national-security state: omnipotent power to inflict violence on innocent people with immunity and impunity, even while decrying violence committed by others.
Jacob G. Hornberger is founder and president of The Future of Freedom Foundation. He was born and raised in Laredo, Texas, and received his B.A. in economics from Virginia Military Institute and his law degree from the University of Texas. He was a trial attorney for twelve years in Texas. He also was an adjunct professor at the University of Dallas, where he taught law and economics. In 1987, Mr. Hornberger left the practice of law to become director of programs at the Foundation for Economic Education.
William Burns, ex-envoy to Russia who accused Putin of using judo-like tactics to ‘sow chaos’ in US, named as Biden’s CIA director
RT | January 11, 2021
[Proclaimed] President-elect Joe Biden has nominated career diplomat William Burns to serve as director of the Central Intelligence Agency, claiming that Americans will “sleep soundly” with Burns at the helm of the shadowy intel service.
Burns, who is currently president of the Carnegie Endowment for International Peace, an international affairs think tank based in Washington, DC, retired from the US Foreign Service in 2014 after a 33-year career in diplomacy. He served as deputy secretary of state in the Obama administration from 2011-2014, and as ambassador to Russia from 2005 to 2008. Before his assignment in Moscow, Burns was US envoy to Jordan from 1998 to 2001, and was appointed assistant secretary of state for Near Eastern affairs from 2001 to 2005.
In a press release, Biden described Burns as a “exemplary diplomat with decades of experience on the world stage keeping our people and our country safe and secure.” The statement said that Burns understood the alleged threats facing the United States, whether they be “attacks emanating from Moscow, the challenge China poses,” or plots being hatched by terrorists and other non-state actors.
Like many other State Department veterans, Burns has repeatedly accused Moscow of interfering in the 2016 presidential elections.
In a 2017 op-ed published by the New York Times, the retired diplomat accused Russia of “aggressive” and “deeply troubling” election meddling. Burns predicted that Washington’s relationship with Moscow will remain competitive and “often adversarial” for the foreseeable future, claiming that Russian President Vladimir Putin is seeking greater influence in the world “at the expense of an American-led order.” He alleged that Russia is dreaming of a dominant position in global affairs unconstrained by “Western values and institutions.”
He called on the US to focus on the conflict in Ukraine, predicting that the country’s fate will determine the “future of Europe, and Russia, over the next generation.”
Tellingly, he also dismissed the “superficially appealing notions” like cooperation against Islamic terrorism. He claimed that Russia’s efforts to help the Syrian government defeat Islamic State (IS, formerly ISIS) has made the terrorist threat “far worse.”
His animosity towards Russia was again revealed in an interview with the Atlantic magazine in 2019. He told the outlet that Putin had been able to “sow chaos” in the United States by “acting like [a] good judo expert, which he is.” According to Burns, the Russian leader took advantage of a “stronger opponent” by leveraging the “polarization and dysfunction” in the US political system.
Burns even suggested that the now-debunked claims of “collusion” between Moscow and the Trump campaign in 2016 had merit, hinting that Special Counsel Robert Mueller could potentially uncover a larger conspiracy behind Putin’s alleged judo-like interference.
Mueller’s probe ultimately found no evidence of collusion, despite years of salacious media reports alleging overwhelming proof of a vast conspiracy between Trump and the Kremlin.
The diplomat appears to have a more reconciliatory approach towards China. Although he has identified Beijing as a long-term competitor with Washington, he has argued that China was more focused on “adapting” to the US-led world order, rather than “undermining it,” which he accused Russia of doing. However, he expressed support for at least some aspects of the Trump administration’s trade war with China, describing the hardline economic policy as “overdue.”
Data giant Palantir’s murky track record raises alarming questions about secret, potentially illegal £23 million NHS deal
By Kit Klarenberg | RT | December 23, 2020
Palantir has won a huge contract to continue its work on the NHS Covid-19 Data Store. But the British public will have no way of knowing how the private information the company has been granted access to will be used.
The potentially illegal two-year deal, which began on December 12, was awarded under the Crown Commercial Services G-Cloud 11 Framework, a ‘streamlined’ – i.e. much-accelerated – system typically used for minor contracts, which doesn’t require a tender to be published. Under the terms of the agreement, the store will rely on Palantir’s Foundry data until at least December 2022.
The store was established in March to manage Covid-19 data and inform the government’s response to the virus. Palantir was one of several tech firms hired for the project, for the princely sum of £1, and ever since has been granted access to sensitive data such as patients’ ages, addresses, health conditions, treatments and whether they smoke or drink, among other private information.
Such information is clearly a highly valuable commodity, exclusive oversight of which is fraught with opportunity for abuse, but Whitehall insists any personally-identifying details are aggregated or anonymized prior to being shared with Palantir et al.
Despite these reassurances, the deal did not go unchallenged – not least because the contracts underpinning the deal weren’t published until June, mere hours before a legal action brought by political campaigning website openDemocracy and law firm Foxglove to secure their release was due to commence.
A very secret weapon
An even cursory review of Palantir’s operations starkly underlines why so many should be concerned about its involvement with the NHS, and its access to such intimate patient particulars.
Co-founder Peter Thiel’s inspiration for the company was a desire to repurpose the fraud recognition systems of PayPal – which he also co-founded – for defense and security applications. Most established investors weren’t interested in his pitch, but it caught the attention of In-Q-Tel, the little-known venture capital wing of the US Central Intelligence Agency (CIA), which gifted the start-up US$2 million in 2004.
A decade later, Palantir was valued in the billions and pulling in hundreds of millions of dollars annually, primarily from US government agencies, including the CIA, Departments of Defense and Homeland Security, Federal Bureau of Investigation, Air Force, Marine Corps, and Special Operations Command.
The company’s ‘Gotham’ platform pools these entities’ disparate and sprawling databases and allows for the effective sorting, management and cross-referencing of information contained therein.
These capabilities can be put to predictive purposes – for example, soldiers in Afghanistan used the tool to combine maps, intelligence reports, and reports of roadside bombings to plan missions. As a result, Bloomberg dubbed Palantir the War on Terror’s “secret weapon,” and Gotham also became of intense interest to law enforcement agencies the world over.
Due to the veil of secrecy surrounding Palantir’s commercial activities, the total number of forces employing the technology globally is unknown – although the company isn’t only opaque about what services it provides to which clients, but has been outright dishonest at the nature of its government partnerships in the past.
Usage metrics
In 2018, it was revealed police in New Orleans utilized Palantir software to trace targets’ ties to gang members, link suspects’ criminal histories, analyze social media, and forecast the likelihood individuals would commit crimes or become a victim thereof.
Several high-profile convictions of violent, murderous drug gangs were secured in the process, although it was operated in total secrecy for five years until exposure by tech website the Verge, with even the city council totally unaware.
The tendency toward concealment may at least in part be attributable to public outcry over predictive policing programs, which exhibit seemingly invariable racial bias. Even algorithms that do not specifically use race as a metric have been found prone to this prejudice, due to the inclusion of ancillary variables such as socio-economic background, education, and location.
Still, significant light was shed on how authorities use Gotham, and what information it collates, in September 2020, when two Los Angeles Police Department training documents – ‘Intermediate Course’ and ‘Advance Course’ – used to instruct officers on the workings of the system were leaked.
The data collected on citizens – both law-abiding and those with criminal records, or suspected of having committed a crime, or even being connected in any way to individuals who have – includes sex, race, names, contact details, addresses, prior warrants, mugshots, surveillance photos, personal relationships, past and current employers, and even tattoos, scars, piercings and other identifying features.
According to an ‘LAPD Palantir Usage Metrics’ document, in excess of 5,000 officers – accounting for half the Department’s members – had access to Gotham in 2016, and in that year, they collectively ran around 60,000 searches through the system in support of over 10,000 cases.
Such a cutting-edge service doesn’t come cheap, with subscriptions running to millions of dollars annually. This sizable investment comes despite questions hanging over Palantir’s predictive policing effectiveness, which may suggest the software’s value to authorities doesn’t necessarily lie in its crime-fighting prowess.
Official figures indicate violent crime rates remained virtually unchanged in Los Angeles from 2009 to 2019, while aggravated assaults increased. However, non-violent crime did fall over the same period, in particular burglary and vehicle theft.
‘Without any safeguards
Troublingly, crucial portions of Palantir’s NHS contract are entirely redacted, including sections titled “limit of parties’ liability,”“authorised user groups,” and “data integration and analytics capability for self-service” – which covers how many “authorised users” are permitted to create and modify tools designed using the data, and the data sets involved.
In other words, the public presently has no way of knowing precisely what private information Palantir has been granted access to, how it will be used, and with who and what it can be shared with.
Shocking stuff indeed, yet the mainstream UK media and lawmakers alike have been almost entirely silent on what should at the very least be the subject of intense national debate. Amazingly, the company’s name has been mentioned a grand total of twice in parliamentary debates over the course of 2020, and only once in a critical context.
This wall of establishment silence stands in stark contrast to the US, where legislators – including Senator Elizabeth Warren – have prominently raised privacy concerns over Palantir’s participation in ‘HHS Protect’, a program launched by the Department of Health and Human Services to track the spread of coronavirus. Under its auspices, the company harvests data from a variety of federal, state and local government sources, healthcare facilities, colleges, and more.
“The inclusion of Protected Health Information in this database raises serious privacy concerns,” a coalition of Democratic senators wrote in July. “Neither HHS nor Palantir has publicly detailed what it plans to do with this, or what privacy safeguards have been put in place, if any. We are concerned that, without any safeguards, data in HHS Protect could be used by other federal agencies in unexpected, unregulated, and potentially harmful ways.”
While ministers claim life in the UK will begin returning to “normal” around Easter 2021, the length of the deal places Palantir in a position of immense and entirely unaccountable privilege at the heart of an institution which theoretically provides vital services to every British citizen, for the next two years and potentially beyond.
Readers may wish to ask themselves who or what their elected representatives are truly working for, and which interests they ultimately serve – or better yet, pose these queries to parliamentarians directly.
Kit Klarenberg is an investigative journalist exploring the role of intelligence services in shaping politics and perceptions.
Featured Video
Benoit Paré: OSCE Whistleblower: The Ukraine War – Narratives vs. Reality
or go to
Aletho News Archives – Video-Images
Book Excerpt
How CIA used Ukraine as a platform for covert war against Russia
By Stephen KINZER | Responsible Statecraft | November 17, 2026
The following is an excerpt from Stephen Kinzer’s new book: Boiling Point: How America Brought War to Ukraine (Henry Holt and Company, November 2026)
Huddled beside an airstrip in southern Germany, a handful of anti-Communist warriors prepared to fire the first shots of the Cold War. A CIA officer from the Munich Operations Base was in charge. The Hungarian crewmen he had recruited stood nearby in flight suits. With them were two Ukrainian exiles who had volunteered to parachute into their homeland. They were code-named Apostle 1 and Apostle 2. Each carried forged identity papers, a miniature radio transmitter, a pistol, a machine gun, hand grenades, a purse full of gold coins, and a poison pill to be taken in case of capture. An unmarked C-47 transport plane was waiting.
The CIA officer overseeing this operation, a twenty-six-year-old Yale graduate named Stephen Tanner, watched the plane take off and disappear into the night. It flew over East Germany and Poland, then crossed into Soviet airspace. As it approached the Ukrainian city of Lviv, a cargo bay swung open. The two Ukrainians jumped into the darkness. Their mission was to link up with partisan fighters, seize territory, and establish a clandestine base through which the CIA could send them weapons.
That flight, on September 5, 1949, was the first American act of covert war in Ukraine. … continue
Blog Roll
 Aletho News
- The Food Book — First Edition, 2026, Paperback
- Benoit Paré: OSCE Whistleblower: The Ukraine War — Narratives vs. Reality
- UK forced to admit ordering backdoor access to Apple users’ data
- It’s not about China or national security. It’s about which foreign entity is allowed to spy on Americans
- Banning Palestine activists from the West will not save Israel’s image
- Iran rejects unlimited IAEA inspections amid continued military threats
- A Bridge Too Far
- David Barnea in the Bundestag – Mossad as a model for Germany’s Intelligence Services?
- Rome blasts Kiev after Italian lawmakers added to ‘kill list’
- Another €45 bn down the drain: Why the EU is desperate to waste more cash on Zelensky
- If Americans Knew
- An error has occurred; the feed is probably down. Try again later.
- No Tricks Zone
- Argentina’s Perito Moreno Glacier Joins Antarctica and Arctic In Defying Doomsday Melt Claims
- New Study: Barents Sea Temperatures Were Warmer And Sea Ice Less Extensive In The 1700s Than Today
- German Authorities Start Initiative To Evaluate Public Register For Climate “Disinformation” Spreaders!
- Zonal Asymmetry of Temperature Change in the Antarctic Circumpolar Current
- New Study: The Net Fossil Fuel Contribution To Rising Atmospheric CO2 Has Been Zero For 500 Years
- Germany’s Green Energy Transition Becoming Increasingly Expensive…Another 6 Trillion Euros!
- Sudden Stratospheric Warming, Powerful El Niño Combination May Lead To Extreme Europe Cold, Energy Crisis!
- Two New Studies Find Thwaites Glacier Melt Cannot Be Driven By Human Activity Or A Warming Ocean
- E-Cars Reduce CO2 Emissions By Only 41% Compared To Internal Combustion Engine Vehicles
- Predictions Made By Renowned Climate Professor Over Past Decades Have Been Proven To Be Poor

